
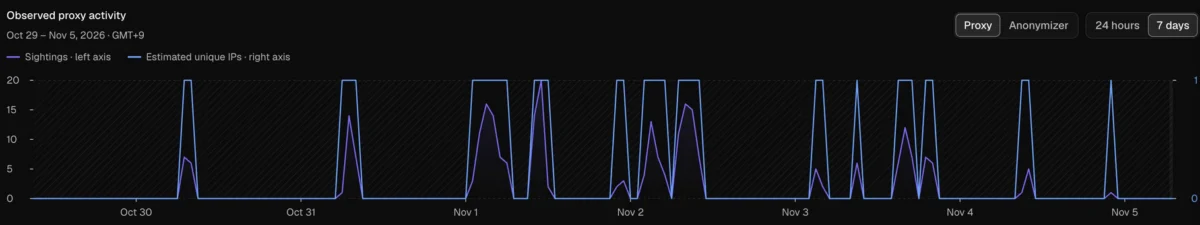
Multiple computers and mobile devices connected to the secure network of the Executive Office of the President have been inadvertently functioning as active residential proxy nodes, allowing external users to route internet traffic through the heart of the United States government. According to findings released by cybersecurity researchers, these devices—likely operated by White House staffers—were running consumer applications integrated with commercial proxy software. This oversight effectively rendered portions of the official government internet address block available for public rent, creating a critical cybersecurity loophole that leaves one of the world’s most sensitive networks exposed to exploitation, data scraping, and anonymous cyber activity.
The discovery highlights a pervasive and rapidly growing blind spot in modern enterprise and government security: the inadvertent integration of residential proxy software through seemingly harmless mobile and desktop applications. Security firms monitoring global internet infrastructure revealed that this unauthorized proxy traffic was not an isolated glitch, but a persistent and measurable operational vulnerability occurring inside official government facilities over a multi-week monitoring window.
Detection and Technical Findings
The alarming security posture was first brought to light by the specialized threat intelligence firm Layer3 Intel. Analysts reported that they detected multiple residential proxy nodes beaconing outward from internet address block AS2650, which is officially reserved and assigned exclusively to the Executive Office of the President.
According to Layer3 Intel’s telemetry, this unauthorized proxy activity was relatively persistent between October 5 and November 3. A comprehensive review of the active proxies available through the AS2650 block showed that connection exit nodes routed traffic directly out of the White House network on 236 separate occasions during that specific timeframe. Further analysis revealed that the activity originated from six distinct internet addresses within the government network. Crucially, this traffic was not observed as a continuous, 24-hour stream; rather, it manifested on 26 of the 30 monitored days, with the vast majority of the proxy routing activity concentrated during evening hours, specifically between 5:00 p.m. and midnight local time.
Simultaneously, proxy-tracking and threat-intelligence firm Synthient corroborated these findings, publishing network telemetry pointing directly to Windows 11 installations running a commercial service known as Infatica. Infatica operates as a residential proxy program that is frequently bundled or covertly integrated into "free" consumer-facing mobile and desktop applications, browser extensions, and utility tools.
The Connection to Infatica and Historical Cyberattacks
The involvement of Infatica brings a significant geopolitical and historical dimension to the incident. Infatica was founded by Vladimir Fomenko, a Russian national whose previous web hosting venture, King Servers, played a central and well-documented role in past cyber operations targeting American democratic infrastructure.
Back in 2016, King Servers served as the foundational infrastructure—described by investigators as ground zero—for state-sponsored cyberattacks that breached voter registration and election administration databases in Arizona and Illinois. During those attacks, six of the eight specific internet addresses utilized by Russian state security services
to compromise the U.S. election systems were traced directly back to Fomenko’s King Servers hosting infrastructure.
While the current presence of Infatica nodes within the White House network does not inherently indicate a targeted state-sponsored cyber offensive from the same actors, security experts emphasize the severe inherent risks. Allowing software linked to individuals with such backgrounds to operate on a secure government network presents an unacceptable counterintelligence and operational security hazard.
The Scale of the Problem: Public Access to Government Assets
Perhaps most startling to security professionals is the sheer accessibility of the White House network through these commercial channels. Layer3 Intel discovered that Infatica was not an isolated anomaly operating within the Executive Office of the President’s infrastructure. In total, the security firm identified 28 separate residential proxy services that were capable of routing traffic and exiting through the AS2650 network block.
In a published technical analysis, the Layer3 Intel research team underscored the trivial nature of gaining access to these privileged endpoints, writing that the network had effectively been turned into a public resource. According to the firm, anyone could obtain access simply by signing up for a public residential proxy service, paying a nominal fee of a few dollars, and routing web requests through it.
The researchers stressed that they did not selectively target the White House network or deliberately attempt to force their network probes to exit through government infrastructure. Instead, the exposure was discovered entirely by chance while requesting global rotating access through standard, commercially available proxy networks.
Broad Ecosystem Risks and Prior Vulnerabilities
The exposure of government infrastructure via residential proxies is symptomatic of a broader, systemic failure in how modern organizations manage endpoint security and software procurement on corporate and government devices. Residential proxy services operate by turning ordinary consumer internet connections—typically residential broadband lines—into commercial exit nodes. Customers of these proxy services pay to route their web traffic through these residential IPs to mask their true locations, evade anti-bot detection systems, bypass geographic content blocks, or execute coordinated web scraping operations.
However, the ecosystem surrounding residential proxy providers is notoriously opaque. Many of these services engage in aggressive monetization schemes, paying software developers to integrate Software Development Kits (SDKs) into consumer applications. Unsuspecting users install games, VPNs, or utility apps, unknowingly granting the software permission to share their device’s internet bandwidth with third parties.
This architecture introduces profound cybersecurity vulnerabilities. In late 2025, security researchers uncovered a widespread flaw wherein cybercriminals aggressively targeted vulnerabilities within residential proxy services. Attackers leveraged these proxy endpoints to pivot inward, scanning the local networks of unsuspecting users for unpatched systems, vulnerable Internet of Things (IoT) devices, and internal corporate assets to infect with malware.
In January 2026, dozens of residential proxy providers were forced to rush emergency security patches after Ben Brundage, founder of Synthient, publicly demonstrated how malicious actors were actively abusing proxy vulnerabilities to execute unauthorized code and seize control of local network devices.
Speaking to cybersecurity journalists, Brundage highlighted the terrifying economics of the threat landscape. He noted that certain proxy resellers sell bandwidth for as little as 60 cents per gigabyte, meaning an attacker can spend less than a dollar to gain a foothold inside some of the most confidential and trusted networks in the world. Furthermore, the fragmented reseller ecosystem frequently allows bad actors to bypass standard Know Your Customer (KYC) and identity verification protocols completely anonymously.
Corporate and Government Blind Spots
The presence of residential proxies on the White House network is indicative of a widespread blind spot across both the public and private sectors. Because these proxy nodes are typically installed via employee-owned devices brought into the workplace, or through personal applications installed on agency-issued hardware, traditional perimeter defenses often fail to flag them as immediate malware infections. Instead, the software operates under the guise of legitimate application traffic.
Data from other cybersecurity organizations underscores the sheer magnitude of this enterprise risk. During a comprehensive industry webinar in January 2026, proxy-tracking service Spur revealed alarming statistics regarding the prevalence of residential proxy nodes across critical infrastructure. Spur’s analysis detected active residential proxies residing within nearly 300 government-owned and operated networks across the United States. Additionally, the tracking firm identified proxy nodes inside 318 utility companies, 166 healthcare organizations and hospitals, and 141 institutions operating within the banking and financial sectors.
Reinforcing these findings, a comprehensive threat report published earlier this year by security firm Infoblox revealed that a staggering 65% of its entire enterprise customer base had corporate or organizational networks querying one or more domains associated with residential proxy services. This widespread corporate contagion demonstrates that organizations of all sizes struggle to maintain visibility over the software supply chain running on endpoints connected to their internal networks.
Implications and Official Response
As of press time, the White House has not formally responded to media requests for comment regarding the detection of residential proxy exit nodes within the Executive Office of the President’s network. The lack of an immediate public statement leaves open questions regarding how many devices were ultimately compromised, whether any sensitive data was accessed or exfiltrated by third parties utilizing the proxy network, and what remediation steps the administration’s Office of Administration and Chief Information Officer are taking to purge the unauthorized software.
The implications of this security lapse extend far beyond simple bandwidth theft or network congestion. When government networks act as commercial exit nodes, malicious actors can leverage those highly trusted, government-owned IP addresses to conduct sophisticated cybercrimes, launch credential-stuffing attacks against financial institutions, commit large-scale advertising fraud, or orchestrate targeted espionage operations while entirely masking their digital footprints behind the federal government’s digital perimeter.
For federal agencies and enterprise organizations alike, the incident serves as a stark reminder of the urgent need for enhanced endpoint visibility, strict application whitelisting, and robust monitoring of outbound network telemetry. As long as employees continue to introduce consumer-grade software and unvetted applications onto hardware connected to high-value networks, trusted infrastructure will remain dangerously susceptible to exploitation by the very commercial proxy ecosystems designed to obscure the digital underworld.

