• Home
  • About Us
  • Contact Us
  • Cookies Policy
  • Disclaimer
  • DMCA
  • Privacy Policy
  • Terms and Conditions
Dr Crypton
Secure Your Future in Crypto
NFT & Digital Assets

Life After Blur: A Comprehensive Guide for NFT Collectors Navigating the New Marketplace Landscape

by admin November 16, 2026
written by admin

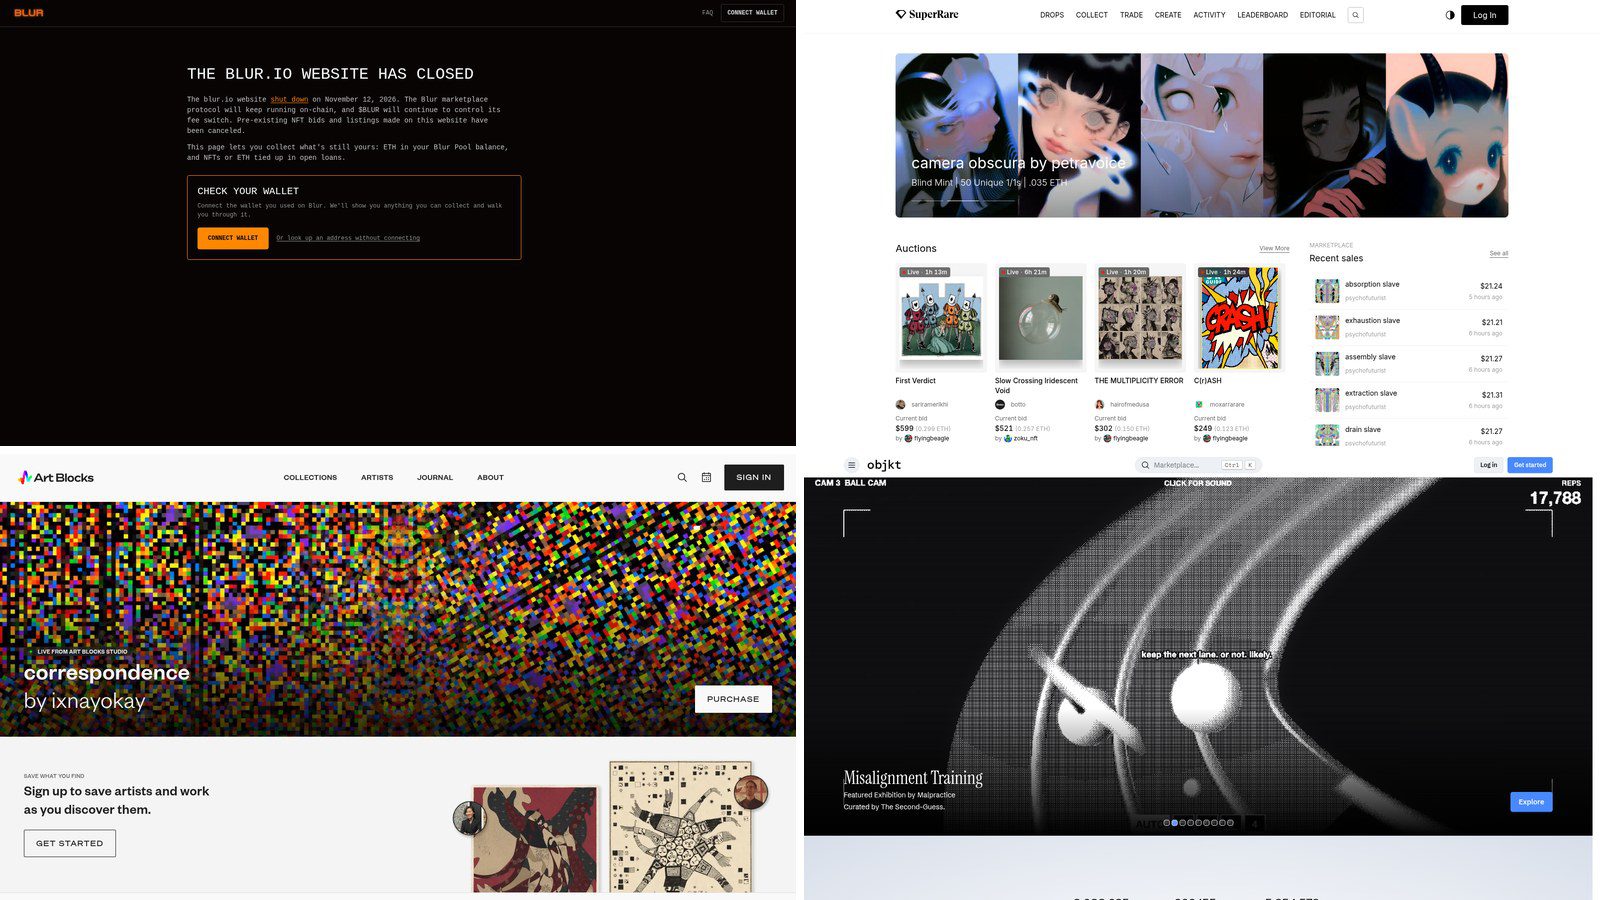
The permanent closure of Blur.io on November 12, 2026, marks the end of a transformative era in the digital asset space, forcing a broad migration of NFT traders, liquidity providers, and collectors to alternative venues. For years, Blur functioned as the primary engine for high-volume, professional-grade NFT trading on Ethereum, pioneering sophisticated bidding pools and lending protocols that prioritized speed and efficiency over creator-royalty enforcement. With the platform now shuttered, there is no single successor to fill the void, prompting a shift toward specialized marketplaces that emphasize community, curation, and varying approaches to artist compensation.

The shutdown of the Blur website does not mean the underlying protocol has vanished; however, the shift in user experience is significant. Blur’s marketplace protocol continues to function on-chain, but the interface that facilitated seamless bulk-buying and automated bidding is no longer active. For the average collector, this necessitates a transition to new platforms—a move that requires a strategic assessment of where one’s specific assets fit best. Whether one holds 1/1 digital art, generative projects, or high-volume profile pictures (PFPs), the post-Blur landscape requires a nuanced understanding of fee structures, royalty enforcement, and platform-specific liquidity.
After Blur Shutdown: Where NFT Collectors Go Next

A Chronology of the Transition

The sunsetting of Blur.io was not an overnight decision but rather the culmination of a broader market shift that began in early 2026. The platform’s decline in market share was accelerated by changes in consumer sentiment regarding creator royalties and the increased regulation of decentralized finance (DeFi) components within NFT ecosystems.

  • March 9, 2026: Magic Eden officially terminated its EVM (Ethereum Virtual Machine) marketplace support, effectively pivoting its operations exclusively to the Solana blockchain. This served as an early indicator of a market consolidation trend, where platforms began focusing on specific chains to remain viable.
  • November 12, 2026: Blur.io officially closed its primary web interface. All pre-existing bids and listings were canceled to prevent potential exploits or orphan transactions.
  • November 12, 2027: This date marks the final window for users to access the dedicated withdrawal page for recovering Blur Pool ETH and collateral locked in Blend (Blur Lending) positions. After this, while funds remain on the blockchain, the administrative interface for recovery will be unavailable.

The State of the Market: Where to Go Next

For collectors, the decision of where to move is fundamentally an ideological one. The market has effectively split into four distinct tiers based on the type of asset and the priority placed on creator royalties.

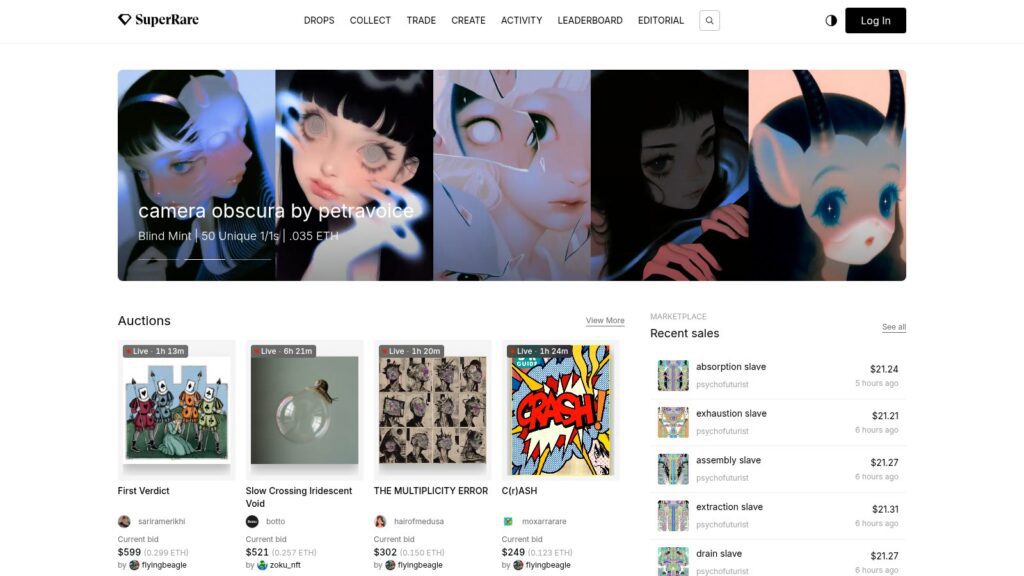
The Curated 1/1 Sector: SuperRare

SuperRare remains the premier destination for collectors of 1/1 fine art. Its model is built on exclusivity and structural support for artists. Unlike Blur, which was an open-access aggregator, SuperRare requires an invitation for creators. Its fee structure is highly standardized: a 3% marketplace fee paid by the buyer to the DAO treasury, with artists receiving a guaranteed 10% royalty on all secondary sales. For the serious collector, this provides a predictable environment where artist compensation is not subject to the whims of the seller.
After Blur Shutdown: Where NFT Collectors Go Next

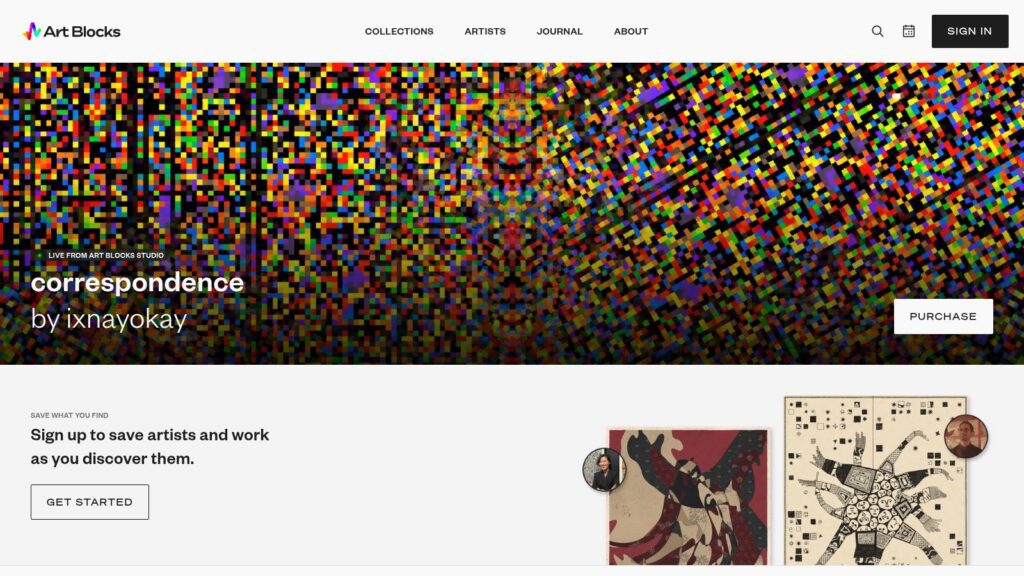
The Generative Art Frontier: Art Blocks

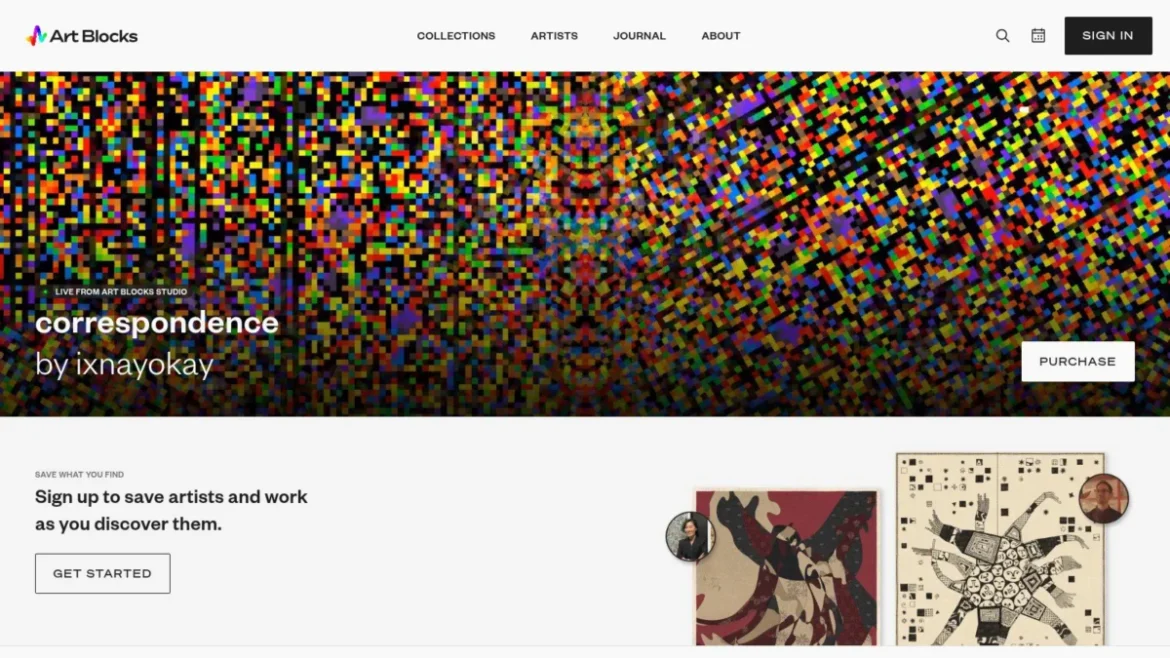
Generative art collectors have increasingly moved toward Art Blocks. The platform provides a unique environment for long-form generative projects where the art is rendered on-chain. Art Blocks enforces a royalty structure through the ERC-2981 standard, ensuring that artists receive their share of secondary sales automatically. The split—typically two-thirds to the artist and one-third to the platform—creates a sustainable ecosystem for algorithmic artists. Its integration with the Royalty Registry ensures that these rights are honored across most secondary market touchpoints.

The Generalist Ecosystem: OpenSea

OpenSea remains the most robust general-purpose marketplace for those who hold a diversified portfolio of PFPs, utility tokens, and mixed-chain assets. While its history with creator royalties has been contentious, the platform currently offers a 1% selling fee. Its handling of royalties is now highly granular: creators can mandate royalties for collections using specific modern standards like ERC721-C or ERC1155-C. For collectors, the onus is now on the individual to verify the settings of a collection before listing or purchasing, as "optional" royalty settings remain a feature of the platform’s legacy architecture.

The Tezos Alternative: objkt

While Blur never serviced the Tezos blockchain, many collectors hold assets across both Ethereum and Tezos. For these users, objkt remains the definitive venue. Charging a straightforward 5% marketplace fee paid by the seller, objkt integrates royalty payments directly into its smart contracts. This simplicity has made it a favorite for artists who prefer a "set it and forget it" approach to secondary revenue.
After Blur Shutdown: Where NFT Collectors Go Next

Fact-Based Analysis of Implications

The migration away from Blur is not merely a change in user interface; it represents a fundamental change in the "culture" of NFT trading. Blur’s rise in 2022 and 2023 was built on the premise that NFTs were financial instruments first and collectibles second. By allowing sellers to bypass royalties, Blur squeezed the margins for artists while maximizing liquidity for traders.

The current landscape, by contrast, favors "sustainability" over "velocity." Marketplaces that thrive today are those that have aligned themselves with the creators. This shift has significant implications for asset valuation. Collections that have moved to platforms enforcing mandatory royalties often see more stable price floors, as the artist is incentivized to continue building, thereby maintaining the value of the asset for the collector.

Furthermore, the "liquidity fragmentation" caused by the absence of a central aggregator means that collectors must be more vigilant. Without the unified view that Blur once provided, price discovery is becoming more localized to each platform. Data suggests that this has led to a slight increase in price volatility across smaller collections, as buyers are less likely to sweep the floor across multiple exchanges simultaneously.
After Blur Shutdown: Where NFT Collectors Go Next

Managing Your Assets Post-Shutdown

Collectors who still have funds tied to the Blur ecosystem should prioritize the following actions:

  1. Wallet Reconciliation: Your NFTs are stored in your wallet, not on a marketplace. You do not need to "move" your assets to list them on OpenSea or other venues. However, you must revoke legacy approvals you granted to Blur’s smart contracts. This is a crucial security step that many users overlook.
  2. Liquidity Recovery: If you were active in Blur’s lending protocols (Blend) or the Blur Pool, visit the official legacy portal immediately. The FAQ provided by the Blur team confirms that while assets will not be lost after November 2027, the recovery process will become significantly more complex, requiring direct interaction with Ethereum smart contracts rather than a user-friendly web interface.
  3. Royalty Verification: Before listing an asset on a new platform, verify the collection’s metadata and royalty settings. If you value the artist’s work, choose a venue that honors their specific royalty requirements. The power has shifted from the platform to the individual, and the collective choice of where to trade will determine the viability of future NFT projects.

The Road Ahead

As the industry moves into 2027, the focus is shifting toward interoperability. Projects that utilize standardized royalty protocols are proving more resilient than those that relied on marketplace-specific enforcement. While the convenience of a one-stop-shop like Blur is missed by high-frequency traders, the current environment offers a more stable and artist-aligned future for the long-term collector.

The closure of Blur serves as a reminder that in the decentralized web, no interface is permanent. The longevity of an asset lies in its smart contract and its community, not the website where it happens to be listed at a given moment. Collectors should approach this transition not as a loss of utility, but as an opportunity to migrate to platforms that better reflect their values as patrons of digital art. The market continues to evolve, and for those who take the time to understand the new rules of engagement, the ecosystem remains as active and diverse as ever.
November 16, 2026 0 comment
0 FacebookTwitterPinterestEmail
Tech & Startup News

The Disconnect Between Humanoid Robot Hype and the Reality of Modern Robotic Warfare

by admin November 16, 2026
written by admin

The promise of humanoid robotics in military applications has long occupied the space between science fiction and venture capital pitch decks. However, recent developments concerning Foundation, a startup claiming to deploy humanoid robots to the frontlines of the conflict in Ukraine, have highlighted a stark discrepancy between marketing narratives and the operational realities of modern warfare. Independent journalist and host of the Eye on AI podcast, Craig Smith, has shed light on the logistical failures surrounding Foundation’s claims, casting doubt on the company’s assertion that its "Phantom" robots have successfully reached the Ukrainian theater.

According to Smith, who documented his attempt to track the delivery of these systems, the Foundation robots never actually crossed the border into Ukraine. Instead, the shipment was halted at the Polish-Ukrainian border, leaving the robots stranded in a logistical limbo that contradicts the company’s public-facing narrative. When confronted with these findings, Foundation’s leadership, including spokesperson LeBlanc, failed to provide verification of arrival. Furthermore, LeBlanc retreated from previous assertions that the company had conducted formal demonstrations for Brave1, the Ukrainian government’s cluster for defense technology. This retraction suggests that the integration of humanoid platforms into the Ukrainian defense ecosystem is significantly less advanced—or perhaps non-existent—than promotional materials have implied.

The Marketing vs. Mechanics Gap

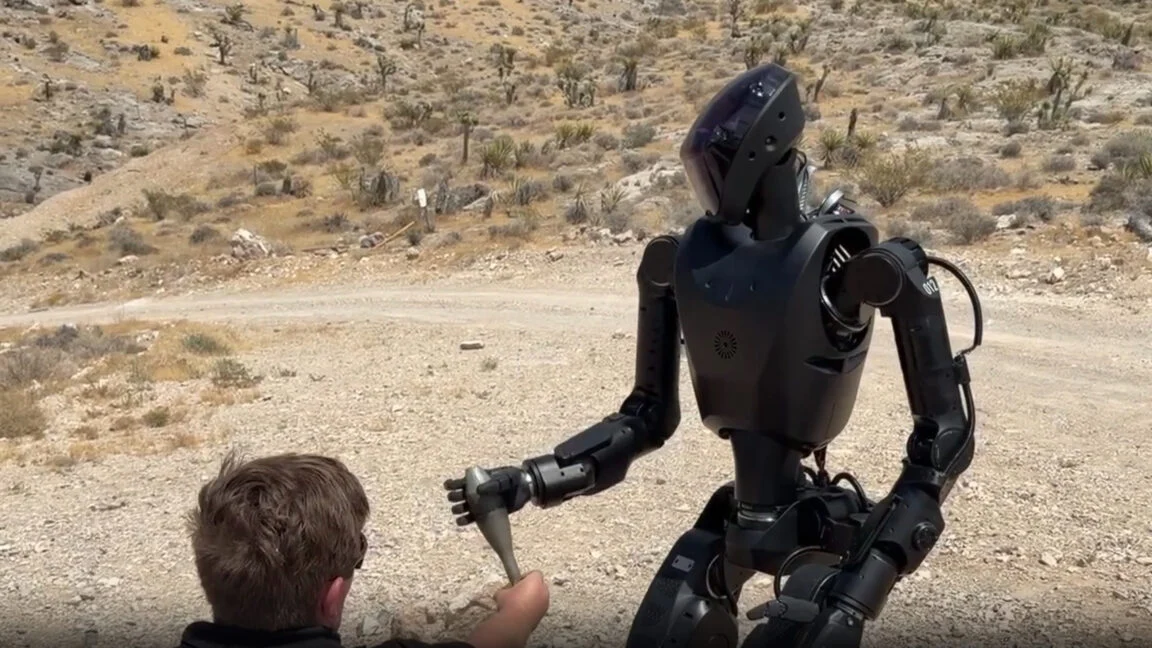
The promotional media released by Foundation serves as a case study in the current disconnect between robotics R&D and combat utility. A video released by the company in May 2026, labeled a "mortar demo," depicts a humanoid robot performing the task of loading a mortar shell. The movement is notably slow and deliberate, highlighting a fundamental issue: humanoids, while visually impressive, lack the speed, stability, and ruggedization required for high-intensity combat zones.

In a battlefield environment, where seconds translate to life or death, the deliberate, controlled motions of current humanoid hardware are liabilities. The "mortar demo" showcases a controlled, static environment that bears no resemblance to the chaotic, mud-filled, and explosive-heavy reality of the Donbas or southern frontlines. The mechanical complexity of a humanoid robot—which requires thousands of actuators, intricate sensors, and high-energy battery systems—makes it inherently fragile compared to the simplified, hardened chassis of established military hardware.

The Evolution of Unmanned Ground Vehicles (UGVs)

While startups chase the humanoid dream, the Ukrainian military has pioneered a more pragmatic and effective approach to robotic warfare. The actual "robots" making an impact on the frontlines are not bipedal figures, but Unmanned Ground Vehicles (UGVs). These platforms, characterized by their robust caterpillar tracks or high-traction wheels, represent the current apex of combat robotics.

The tactical utility of these UGVs is defined by their modularity and durability. Unlike humanoids, which are optimized for human-scale environments and balance, UGVs are engineered for heavy lifting, traverse, and survivability. As the Ukrainian military continues to face a significant personnel deficit compared to the Russian armed forces, these systems have become essential force multipliers.

Data from the 2026 tactical reports indicate that ground robots are now being used for a wide spectrum of operations:

  • Logistical Resupply: Autonomous or remotely operated vehicles carrying ammunition, food, and water to forward operating bases (FOBs) that are too dangerous for human drivers.
  • Casualty Evacuation (CASEVAC): Specially modified UGVs capable of carrying wounded soldiers from the "zero line" to triage points, significantly reducing the exposure of medical personnel to enemy fire.
  • Combat Engagement: Armed variants, often mounted with remote weapon stations (RWS), are utilized to provide suppressing fire or serve as mobile, expendable "loitering" explosive platforms.

Chronology of Robotic Deployment in Ukraine

The integration of unmanned systems into the Ukrainian counteroffensive has followed a rapid, iterative timeline.

  • Early 2024: Ukraine begins experimenting with small, commercial off-the-shelf (COTS) ground robots for mine clearing and basic surveillance.
  • Late 2024–2025: The shift toward dedicated, military-grade UGVs accelerates. The Ukrainian Ministry of Defense formalizes partnerships with local tech startups to mass-produce reliable, low-cost tracked vehicles.
  • April 2026: A surge in robotic deployment is observed, with ground robots being used in conjunction with aerial drone swarms to conduct reconnaissance and localized attacks.
  • July 2026: Advanced tactics emerge, including the delivery of UGVs behind enemy lines via amphibious landings and heavy-lift drone airdrops.
  • September 2026: During tactical offensives, the use of airdropped robots to breach minefields and neutralize fortified Russian positions proves to be a turning point in breaking through pincer movements.

Analysis: Why Humanoids Struggle in Combat

The failure of the humanoid model to gain traction in the Ukrainian war effort is rooted in engineering physics. A humanoid robot must maintain a complex center of gravity, which is easily disrupted by uneven terrain, debris, or the impact of concussive shockwaves from nearby artillery. Conversely, a UGV with a low center of gravity and a wide wheelbase is inherently stable.

Furthermore, the "general-purpose" claim often leveled by humanoid manufacturers fails to account for the specialization required on the frontlines. A robot in a factory, where floors are level and lighting is consistent, can rely on high-fidelity sensors and pre-mapped environments. On a battlefield, the environment is dynamic, unpredictable, and saturated with electronic warfare (EW) signals that can disrupt the wireless communication links upon which these robots depend.

The current military standard, therefore, favors "dumb" but reliable automation over "smart" but fragile humanoids. The Ukrainian military’s success is a direct result of selecting platforms that can be mass-produced, easily repaired in the field, and effectively operated by personnel with minimal training.

Official Responses and Industry Implications

The ambiguity surrounding Foundation’s claims serves as a warning for investors and military planners alike. When questioned by reporters, industry analysts noted that the "Brave1" certification process is rigorous and transparent. By failing to substantiate their claims or provide evidence of official integration, Foundation has inadvertently exposed the fragility of the "Silicon Valley" approach to defense contracting.

The broader implication is that the defense industry is entering a new era of scrutiny. As states continue to integrate robotics into their national defense strategies, the premium will be placed on verifiable performance metrics rather than aesthetic appeal. Companies that pivot away from the "humanoid hype" and toward the "utility-first" engineering model—focusing on ruggedized, task-specific, and cost-effective ground vehicles—are likely to see the greatest success in securing long-term government contracts.

Conclusion: The Future of the Robotic Battlefield

The battlefield of the future will almost certainly be dominated by autonomous and semi-autonomous systems, but it will not look like the humanoid-filled landscapes depicted in speculative fiction. It will be characterized by a diverse ecosystem of specialized machines: aerial swarms providing constant surveillance, tracked ground vehicles handling the brunt of logistical and frontline combat, and high-speed sensors processing data in real-time.

For Foundation and other startups in the humanoid sector, the path forward requires a shift in priorities. If these companies wish to contribute to modern defense, they must move beyond the marketing videos that show robots performing choreographed tasks in safe, interior environments. They must instead address the harsh realities of front-line duty: the need for rapid repair in the field, the requirement for high-level resistance to electronic jamming, and the necessity of navigating the literal and metaphorical terrain of modern, high-intensity conflict. Until then, the "Phantom" robots—and the hype surrounding them—will remain largely confined to the borderlands, while the real work of robotic warfare continues on the frontlines, performed by machines that prioritize function over form.

November 16, 2026 0 comment
0 FacebookTwitterPinterestEmail
Bitcoin & Altcoins

South Korea Proposes Major Legislative Overhaul to Tighten Cryptocurrency Exchange Regulations and Curb Financial Crime

by admin November 16, 2026
written by admin

South Korea’s financial regulatory landscape is poised for a significant transformation as the National Assembly considers a comprehensive amendment to the Act on Reporting and Use of Specific Financial Transaction Information. Spearheaded by Kim Hyun-jung, a Democratic Party representative for Pyeongtaek-B in Gyeonggi Province, the proposed bill seeks to institutionalize rigorous oversight mechanisms for cryptocurrency exchanges. The primary objective of this legislative push is to dismantle avenues used for money laundering and the illicit movement of funds, effectively closing regulatory gaps that have persisted as the digital asset sector has matured. If enacted, these provisions would mark a pivotal shift from reliance on presidential decrees to a more rigid, statutory framework for the nation’s multi-billion dollar virtual asset market.

Chronology of South Korea’s Regulatory Evolution

The movement toward tighter control of digital assets in South Korea did not occur in a vacuum; it is the culmination of years of escalating regulatory scrutiny. In 2021, the nation first introduced the "Travel Rule," which required virtual asset service providers (VASPs) to collect and share identifying information for transactions exceeding a specific threshold. However, these requirements were largely dictated by executive orders and regulatory guidelines issued by the Financial Services Commission (FSC), leaving ambiguity regarding legal enforcement.

In July 2024, the government took a massive step forward with the implementation of the Virtual Asset User Protection Act, which focused on protecting investor deposits and preventing unfair trading practices. Kim Hyun-jung’s new bill serves as a direct successor to these efforts, aiming to codify the "Travel Rule" into the primary statute itself. By moving these mandates from secondary orders into the primary Act, the government intends to provide a clear, indisputable legal basis for compliance, thereby minimizing the room for interpretation that exchanges have previously exploited.

Strengthening Transactional Integrity and Transparency

At the heart of the proposed legislation is the formalization of information-sharing protocols. Currently, while exchanges are tasked with identifying the origins and destinations of transferred assets, the lack of a uniform, statutory enforcement mechanism has led to inconsistent data collection. The new bill empowers receiving exchanges with the authority to mandate the disclosure of complete sender and receiver information.

Crucially, the proposal introduces a "refusal and return" mechanism. Under the new rules, if a transaction lacks sufficient detail or if the provided data appears suspicious, the receiving exchange is legally authorized—and indeed obligated—to freeze the deposit or return the funds to the source. This is designed to act as a barrier against "peel chains" or complex layering schemes often used in money laundering. Furthermore, the bill creates a collaborative security network: if an exchange repeatedly fails to comply with information-sharing standards, peer exchanges are encouraged to terminate liquidity and transactional relationships with the non-compliant entity. This peer-policing model essentially forces compliance through the threat of market isolation.

Risk Mitigation for External Wallets and Third-Party Exchanges

A significant portion of the proposed legislation targets the interaction between licensed exchanges and external entities, including personal (unhosted) wallets and foreign-based platforms. The bill mandates that before any collaborative arrangement or transaction processing occurs, a domestic exchange must conduct comprehensive "due diligence" on the counterparty. This includes verifying the existence and licensing status of the partner exchange, as well as an assessment of their history regarding sanctions, anti-money laundering (AML) violations, and regulatory penalties.

The inclusion of personal, unhosted wallets in this scope is particularly noteworthy. Previously, transfers to private, self-custody wallets were often subject to less stringent scrutiny compared to exchange-to-exchange transfers. Under the new bill, exchanges would be required to verify the identity of the user behind the personal wallet before allowing the transfer of assets. This represents a significant administrative burden, as it necessitates the integration of identity verification technologies that can bridge the gap between centralized exchange databases and decentralized wallet addresses.

Governance and Accountability: The Outsourcing Clause

The bill also addresses the growing trend of exchanges outsourcing their "Know Your Customer" (KYC) and AML verification processes to third-party firms. While such outsourcing is common for operational efficiency, the proposed amendment clarifies that the legal liability remains solely with the exchange. If a third-party provider fails to execute a check correctly, the registered exchange will be held accountable for the oversight.

Furthermore, the bill mandates that exchanges report significant structural or legal changes to the Financial Intelligence Unit (FIU). This includes, but is not limited to, the emergence of criminal allegations against high-level executives or major shareholders. This ensures that the FIU remains aware of the "fitness and propriety" of those running the nation’s financial infrastructure. Failure to comply with these disclosure requirements or any of the aforementioned transaction rules could result in administrative fines reaching up to 100 million won per infraction.

Broader Context: The Role of the National Police Agency

Parallel to the legislative efforts in the National Assembly, the National Police Agency (NPA) has been drafting its own operational guidelines for the management of seized cryptocurrencies. This initiative is a response to the increasing frequency of digital asset confiscation in criminal investigations, including cases involving privacy coins—digital assets designed to obfuscate transaction trails.

The coordination between the NPA’s enforcement protocols and the legislative framework proposed by Kim Hyun-jung reflects a synchronized "whole-of-government" approach. By managing hot wallets and digital asset custody under strict, standardized procedures, the government is effectively creating a closed-loop system where illegal assets, once seized, are managed with the same level of security and transparency that the law now demands of private exchanges.

Economic Implications and Market Analysis

Industry analysts observe that while these measures may increase the operational costs for small-to-medium-sized crypto exchanges, they are likely to enhance the long-term credibility of the South Korean market. By forcing a higher standard of transparency, the bill may encourage institutional investors—who have historically been wary of the crypto space due to volatility and security concerns—to enter the market with greater confidence.

However, the cost of compliance remains a concern. The requirement to verify identity for private wallet transfers and the potential for increased legal liability when outsourcing KYC tasks could lead to market consolidation. Smaller exchanges that lack the capital to invest in sophisticated compliance software may find the regulatory environment untenable, potentially leading to a market dominated by a few large, well-funded players.

Official Stance and Future Outlook

Representative Kim Hyun-jung has been vocal about the necessity of this bill, arguing that the explosive growth of cryptocurrency trading necessitates a robust legal infrastructure that is commensurate with traditional financial services. In her statements regarding the bill, she emphasized that the goal is not to stifle innovation, but to create a "transparent and trustworthy" environment. She intends to leverage her influence in the National Assembly to fast-track the bill, positioning it as a vital component of the nation’s broader financial stability strategy.

As of mid-October 2024, the bill is in the review phase. Should it pass, South Korea will solidify its status as one of the world’s most stringent jurisdictions for virtual assets. This move aligns with international trends, such as the European Union’s Markets in Crypto-Assets (MiCA) regulation, which also emphasizes consumer protection and the prevention of financial crime. For South Korean exchanges, the message is clear: the era of light-touch regulation is over, and the future of the industry will be built on the bedrock of legislative compliance, rigorous reporting, and uncompromising accountability. The coming months will be critical as stakeholders, lawmakers, and regulatory bodies engage in the final negotiations that will define the future of the digital asset economy in South Korea.

November 16, 2026 0 comment
0 FacebookTwitterPinterestEmail
FinTech Innovations

Starling Bank Launches Talk to Transact Feature as Agentic AI Transforms Digital Banking in the United Kingdom

by admin November 16, 2026
written by admin

The landscape of retail banking is undergoing a seismic shift as Starling Bank, the prominent UK-based digital financial institution, officially announced the introduction of its new "Talk to Transact" capability. This innovative feature, integrated into the bank’s mobile application, empowers customers to initiate payments and transfers through natural language prompts, marking a significant milestone in the integration of agentic AI within consumer finance. By leveraging the bank’s proprietary Starling Intelligence platform, the feature effectively reduces the friction associated with traditional mobile banking, moving the industry closer to a future defined by conversational commerce.

The rollout of Talk to Transact represents the latest evolution in Starling’s aggressive AI-driven product roadmap. By allowing users to issue voice or text commands—such as "Pay the plumber £200" or "Send money to my savings account"—the bank is actively streamlining the administrative burden of money management. While the technology is sophisticated, Starling has maintained a "human-in-the-loop" security protocol, requiring users to review and authorize every transaction via a screen tap before funds are moved. This design choice underscores the bank’s commitment to balancing operational efficiency with robust security standards.

The Chronology of Starling’s AI Integration

Starling Bank’s journey into advanced automation did not occur in a vacuum; it is the culmination of a multi-year strategy focused on digital-first banking infrastructure. Founded in 2014 by Anne Boden, the bank was built on a cloud-native architecture that allowed for rapid iteration and the deployment of modular financial tools.

The recent evolution of the Starling Assistant can be tracked through the following timeline:

  • 2014–2022: Establishment of core banking services, focusing on mobile-first user interfaces, real-time transaction notifications, and the development of the "Engine" banking-as-a-service platform.
  • August 2024: Launch of the "Smart Tools" program, a centralized hub within the mobile app designed to house AI-powered utilities.
  • Late 2024: Introduction of 14 distinct AI-driven tools, including holiday spending analyzers, cost calculators, and 50/30/20 budget planners.
  • November 2026: Announcement of the "Talk to Transact" voice and natural language payment capability, marking the bank’s entry into agentic payment processing.
  • End of 2026 (Projected): Full deployment of the Talk to Transact feature to all retail customers, followed by the introduction of specialized business-oriented AI tools.

The Mechanics of Agentic Payments

At its core, the Talk to Transact feature functions by bridging the gap between natural language processing (NLP) and the bank’s backend transaction engine. When a user taps the Assistant icon and speaks or types a request, the Starling Intelligence platform performs a series of rapid calculations.

The process is structured into four distinct stages:

  1. Intent Recognition: The AI parses the natural language prompt to identify the recipient, the specific amount, and the desired timing of the payment.
  2. Execution Preparation: The Assistant identifies the necessary payee details from the user’s history or directory. If a new payee is involved, it initiates the setup process within the secure environment.
  3. Verification: The system generates a summary of the transaction, ensuring that the AI has correctly interpreted the user’s instructions.
  4. Authorization: The user performs a final, manual confirmation, which serves as a security safeguard against both AI hallucinations and accidental input.

Harriet Rees, Starling Group CIO, characterized this shift as a fundamental change in the user experience. "Agentic payments are following mobile wallets as the next evolution of payments here in the UK," Rees noted. "Gone is the need for multiple payment screens and laboriously inputting payment details. Now, payments and transfers can happen with a simple natural language conversation."

Supporting Data and Industry Context

The banking industry is currently seeing an unprecedented level of investment in Generative AI and agentic systems. According to recent market analysis from major financial research firms, banks that implement AI-driven personalization and automation tools can expect to reduce customer service operational costs by as much as 20% to 30% over the next three years.

For Starling, the focus on "agentic" capabilities—systems that do not just provide information but actively perform tasks—is a strategic differentiator. While most retail banks currently utilize chatbots primarily for FAQ support, Starling’s approach aims to embed the AI directly into the transactional flow.

The necessity for such tools is driven by the increasing complexity of financial lives. With the proliferation of digital subscriptions, peer-to-peer payment apps, and fluctuating interest rates, consumers are struggling to manage their finances in real-time. Starling’s strategy of releasing one new "Smart Tool" every week is a deliberate attempt to maintain high user engagement and ensure that the bank remains the primary interface for its customers’ financial decision-making.

Addressing Security and Regulatory Oversight

One of the primary concerns for any institution deploying agentic AI is the risk of unauthorized transactions or algorithmic bias. By requiring manual authorization for every payment, Starling is navigating the regulatory landscape carefully. The UK’s Financial Conduct Authority (FCA) has been increasingly vocal about the need for robust governance frameworks regarding AI in financial services, emphasizing that firms remain fully responsible for the actions of their automated systems.

Industry experts suggest that Starling’s "Assistant" approach is a prudent middle ground. By keeping the human in the loop, the bank mitigates the risk of "black box" banking, where automated systems make decisions that are opaque or potentially detrimental to the user. This approach aligns with the growing global trend of "Responsible AI," which prioritizes transparency and user agency over total automation.

Broader Implications for the UK Banking Sector

The introduction of Talk to Transact by a major player like Starling is likely to trigger a competitive response from traditional "Big Four" banks in the UK. As the digital banking market reaches a state of saturation, the battle for market share is shifting from basic interest rates to the quality of the user experience.

If Starling’s initiative proves successful, it will likely set a new industry standard. We can expect to see:

  • Standardization of Voice Banking: As consumers become accustomed to voice-activated payments, other institutions will be pressured to adopt similar natural language processing (NLP) capabilities.
  • Expansion of Banking-as-a-Service (BaaS): Through its Engine platform, Starling is positioning itself not just as a retail bank, but as a technology provider. The success of these AI tools could be licensed to other institutions globally, creating a new revenue stream for the bank.
  • Increased Personalization: The long-term vision of agentic commerce—where AI agents negotiate on behalf of the user to find the best deals or automatically shift funds into high-yield accounts—is the next frontier. Starling’s commitment to allowing customers to eventually create their own tools suggests a future where banking becomes highly personalized and modular.

Future Outlook and Strategic Vision

As Starling looks toward the next year, the company’s roadmap suggests a deepening of its AI capabilities. The planned rollout of tools for small business customers, which will enable them to instruct the Assistant to manage invoices and payroll, could be a significant value-add for the SME sector. Small businesses, which often lack the administrative resources of larger corporations, stand to benefit most from the efficiency gains provided by agentic AI.

The broader promise of this technology, as described by the bank’s leadership, is a transformation in how people relate to money. By providing "deep insight and resources," the Assistant aims to move beyond simple transaction processing to become a holistic financial advisor.

However, the success of this vision will depend on sustained user trust. As AI becomes more deeply integrated into the financial fabric of the UK, the bank must balance the speed and convenience of its new tools with the unwavering necessity of security. Starling Bank’s decision to phase in these features, rather than pushing for total automation, suggests that the leadership understands that in the world of finance, utility is secondary to reliability.

In summary, the Talk to Transact feature is more than a novelty; it is a clear indicator of the direction in which digital banking is heading. By reducing the number of manual steps required to manage money, Starling is not only improving the daily experience of its customers but is also cementing its position as a pioneer in the era of agentic banking. Whether this leads to a permanent change in consumer behavior remains to be seen, but the intent from one of the UK’s leading digital banks is clear: the future of banking will be spoken, not typed.

November 16, 2026 0 comment
0 FacebookTwitterPinterestEmail
NFT & Digital Assets

Justin Aversano Moments of the Unknown: 7 Floors in NYC

by admin November 16, 2026
written by admin

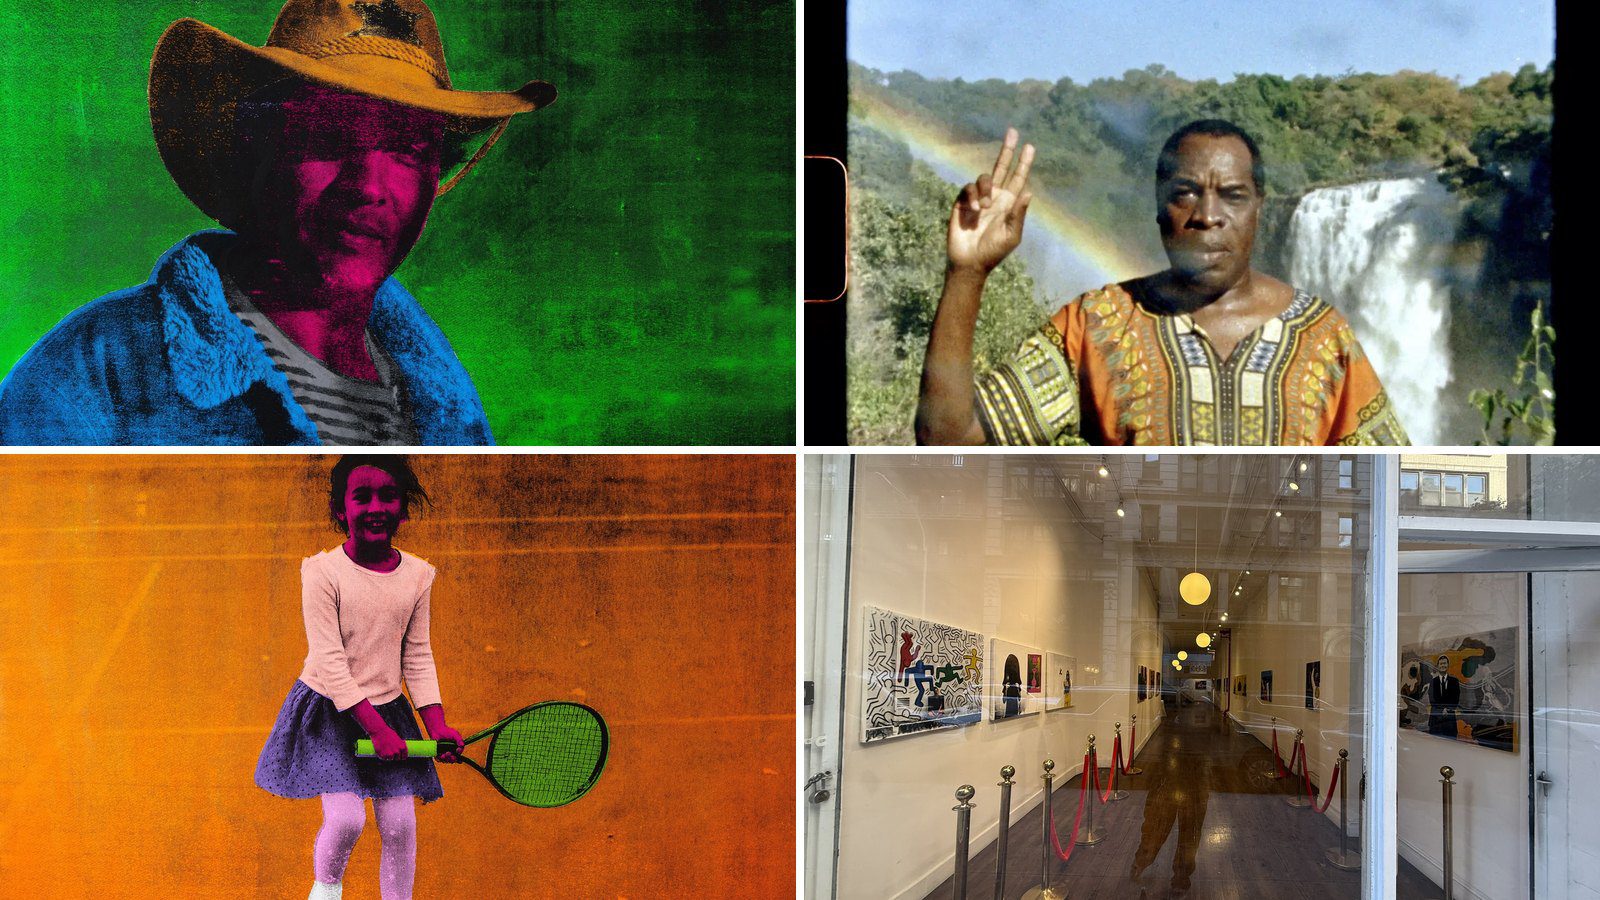
This ambitious exhibition, titled Enter Through the Thrift Shop and co-curated by Aversano and Viktoria Nagibina, represents a departure from the traditional gallery-represented model of contemporary art. By seizing control of an entire 19th-century building, Aversano has constructed a multi-sensory environment that serves as both a physical gallery and a temporal archive. The exhibition, which opened on November 11, serves as the culmination of a year-long global odyssey that saw the artist filming a unique portrait every single day across all seven continents.

The Genesis of a Global Portraiture Project

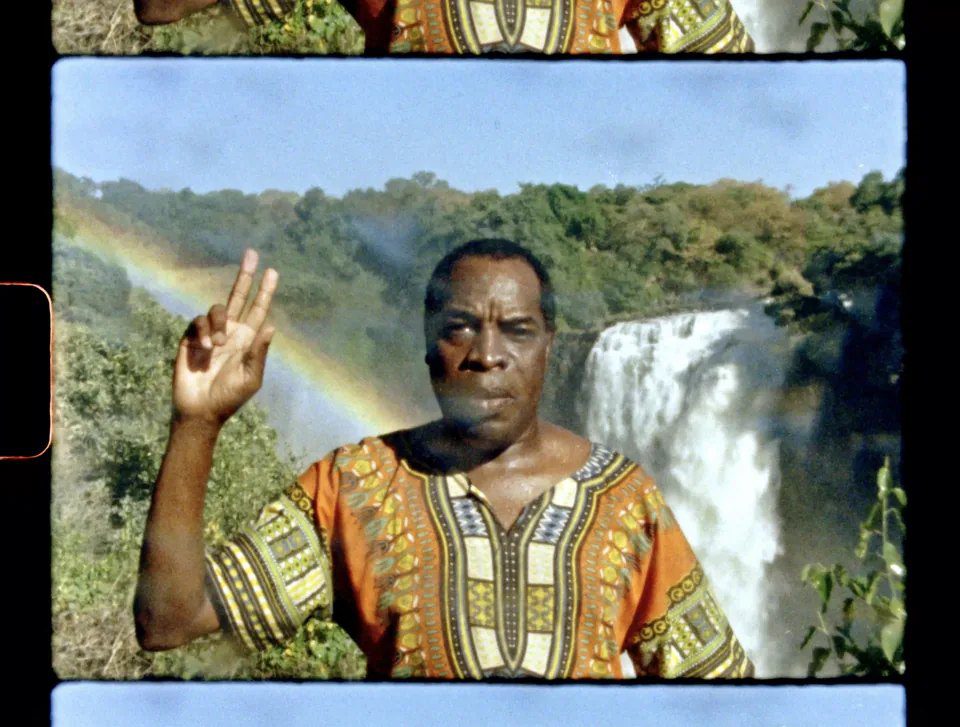
The scale of the project is anchored in a rigorous, self-imposed set of rules. Between April 8, 2023, and April 7, 2024, Aversano committed to capturing a ten-second Super 8 film clip of a different individual in a different city every day. This daily ritual, intended to serve as a “cinematic portrait of humanity,” mirrors the archival ambition of historical projects like Edward Steichen’s 1955 exhibition, The Family of Man, and the cross-cultural reach of the Voyager Golden Record.

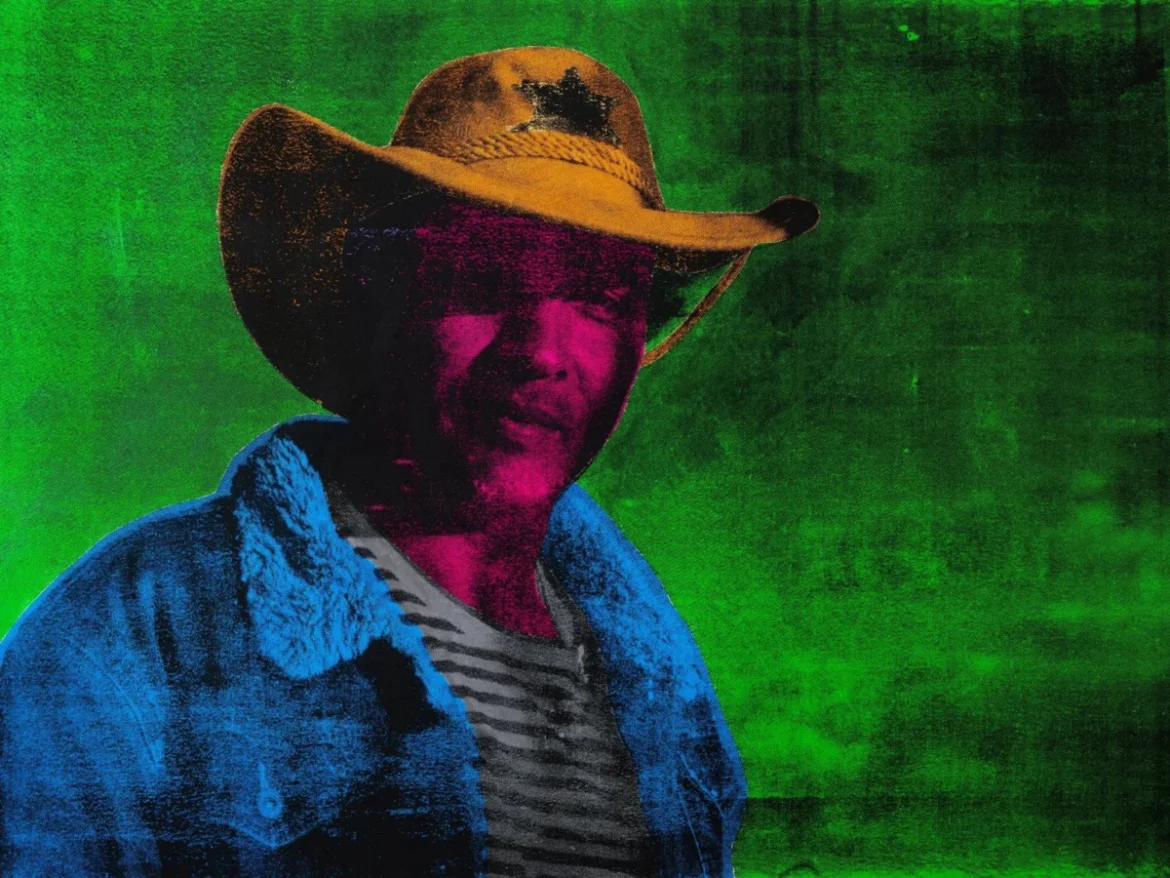
The transition from film to canvas was a meticulous process. Each of the 366 paintings on display began with a singular frame extracted from the daily footage. This frame was then fed into a generative AI model—a process the artist describes as “a machine’s reading of a memory”—before being painstakingly translated onto canvas by hand. The physical application of paint, layered and finished with a distinct black silkscreen, introduces a tactile element that bridges the gap between digital processing and human craftsmanship. The variations in the silkscreen printing are preserved as intentional artifacts, ensuring that each of the 366 works remains unique.

Justin Aversano Moments of the Unknown: 7 Floors in NYC

The Architectural Narrative of 60–62 East 11th Street

The venue itself is as much a participant in the narrative as the artwork. Designed by architect Louis Korn in 1895, the building originally served as the headquarters for the Scovill & Adams Company, a pivotal firm in the history of American photography. The space previously housed editorial offices, darkrooms, and a north-facing rooftop skylight designed for the specific purpose of capturing natural light for photographic experiments.

Aversano and Nagibina, who established their studio in the building in June 2026, discovered this rich photographic lineage only after committing to the lease. The exhibition layout is chronologically and conceptually layered: the journey begins on the lower floors representing “The Past,” moves through the “Present” in the building’s mid-section, and concludes with “The Future” on the upper levels.

The integration of Bijan Royal Antiques, a working shop operating on the ground floor since 1965, provides a literal and metaphorical threshold for the visitor. By requiring guests to pass through a functioning, historic antique store, Aversano forces a collision between the curated, static history of the past and the dynamic, digitally-integrated art of the present.

Augmented Reality and the Loop of Memory

A central feature of the exhibition is the integration of augmented reality (AR) to collapse the distance between the physical canvas and the original source material. Visitors are encouraged to use their personal mobile devices to scan the paintings. Upon doing so, a custom AR application—developed using Claude Code—animates the painting, revealing the original ten-second Super 8 clip from which it was derived.

Justin Aversano Moments of the Unknown: 7 Floors in NYC

The auditory experience is equally curated. Each portrait is paired with an AI-generated audio track trained on Aversano’s own voice, which performs the journal entries written at the time of the initial filming. These entries were revisited and annotated a year later, creating a dialogue between the artist’s immediate impression and his subsequent reflection. This loop—from analog film to digital synthesis, back to physical canvas, and finally to interactive screen—proposes a new methodology for how digital-native art can exist within a physical space.

Economic Strategy and the Rejection of “Flipper” Culture

Perhaps the most disruptive aspect of Moments of the Unknown is its sales strategy. In an era where digital art is frequently associated with rapid-fire, speculative minting cycles, Aversano has adopted a counter-intuitive approach. Only 10% of the 366 paintings were made available via the project’s website at a fixed price of 1.111 ETH.

The vast majority of the inventory is reserved for visitors who physically attend the exhibition. This strategy functions as a mechanism for community building, ensuring that collectors are vetted and aligned with the long-term vision of the project. By prioritizing in-person engagement over immediate online liquidity, Aversano is attempting to bypass the volatility of the 2021-era NFT market, opting instead for a model of “slow acquisition.”

The exhibition is entirely self-funded, a testament to the artist’s reinvestment of previous earnings and the support of a dedicated network of patrons. This model draws clear parallels to recent initiatives by figures like Dave Krugman, who have utilized physical New York spaces to build localized, high-intent collector bases. It reflects a broader shift within the digital art community: the realization that the long-term value of an asset is tied to the strength of the social and physical infrastructure surrounding it.

Justin Aversano Moments of the Unknown: 7 Floors in NYC

Institutional Context and Broader Implications

The timing of this exhibition is significant within the wider context of New York’s digital art ecosystem. Moments of the Unknown runs concurrently with the lead-up to the Whitney Museum’s artport: A History of Internet Art, which opens on November 21. While the Whitney’s exhibition provides a historical overview of how the internet has influenced artistic practice, Aversano’s project acts as an empirical study of the current moment, where the boundaries between “online” and “offline” have become virtually indistinguishable.

The project also provides a meaningful counterpoint to other contemporary efforts to translate screen-native imagery into physical mediums. Whereas some artists focus on the material texture of the output—such as the transformation of pixel art into woven rugs—Aversano insists that the screen remain an essential, albeit secondary, layer of the experience. The painting is the object, but the film is the truth; by requiring the viewer to hold a phone to the canvas, the artist forces the physical and the digital to coexist in the viewer’s hand.

Accessibility and Logistics

For those interested in viewing the collection, private visits can be scheduled directly through the artist. The exhibition remains open to the public through November 26, 2026. Because the building functions as a living archive, visitors are encouraged to allocate significant time to move through the seven floors, allowing for the immersive experience of the film trilogy at the heart of the installation.

The legacy of this project will likely be defined by its refusal to conform to the traditional gallery-museum-auction house pipeline. By internalizing the entire lifecycle of the art—from production and exhibition to curation and sales—Aversano has demonstrated a viable, albeit labor-intensive, blueprint for the future of independent artistic practice. Whether this model can be scaled remains to be seen, but for the duration of the show in Greenwich Village, it stands as one of the most rigorous examinations of memory, technology, and human connection currently on view in New York.

November 16, 2026 0 comment
0 FacebookTwitterPinterestEmail
Web3 & DApps

Outlier Ventures and Injective Unveil the Injective Ecosystem Builder Catalyst Cohort to Accelerate Next-Generation Institutional DeFi

by admin November 15, 2026
written by admin

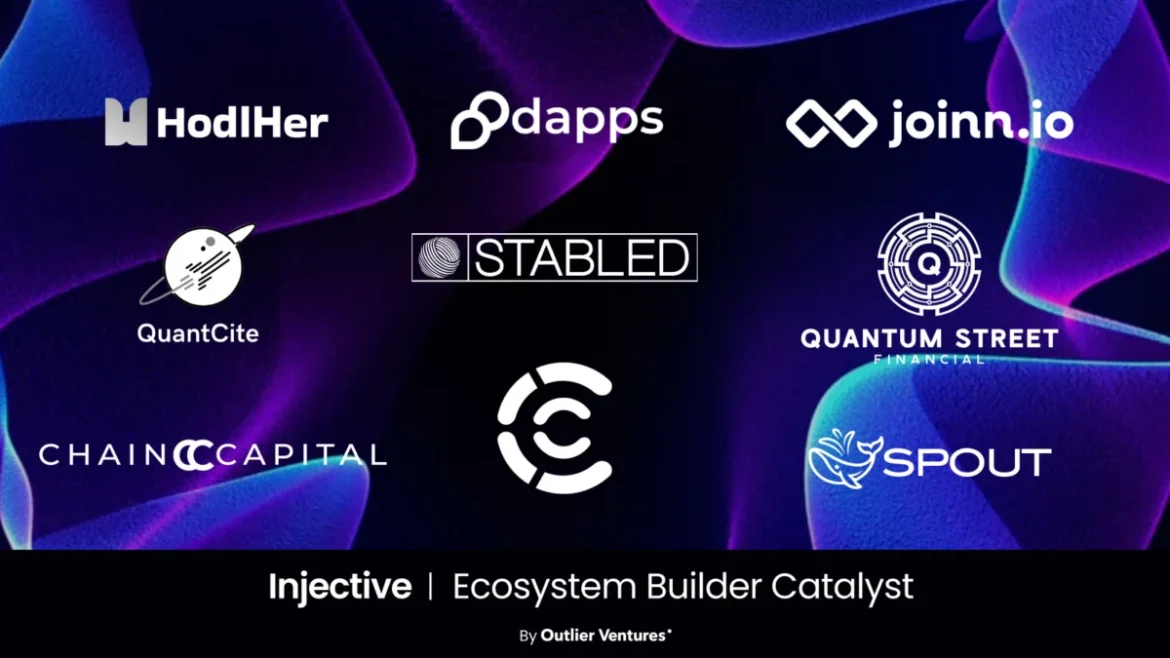
Outlier Ventures, a globally recognized Web3 accelerator and venture capital firm, has officially announced its partnership with Injective, a layer-1 blockchain optimized for finance, to launch the latest cohort of the Injective Ecosystem Builder Catalyst. This intensive, nine-week virtual accelerator program has been meticulously designed to identify, mentor, and fund high-growth decentralized finance (DeFi) and institutional infrastructure startups building natively within the Injective ecosystem.

The launch arrives at a critical juncture for the broader digital asset economy. As decentralized finance continues to mature, the industry is transitioning away from rudimentary token-swapping mechanisms toward sophisticated, institutional-grade financial layers. Modern financial applications increasingly demand sub-second transaction finality, gasless execution layers, and MultiVM interoperability to bridge the gap between traditional financial systems and decentralized rails. By leveraging Injective’s high-performance, purpose-built infrastructure, the newly selected cohort aims to bridge this divide, establishing a robust foundation for the next decade of programmable capital markets.

Background Context and Market Dynamics

The broader decentralized finance landscape has experienced a profound resurgence and structural evolution over recent years. According to industry metrics, total value locked (TVL) across the DeFi sector has surged toward the $140 billion threshold, signaling renewed confidence from both retail and institutional participants. Concurrently, the tokenization and integration of Real-World Assets (RWAs)—ranging from Treasury bills to private debt and equities—have expanded by more than 380% since 2022. This exponential growth highlights a fundamental shift in how global capital seeks yield, liquidity, and operational efficiency through blockchain technology.

Despite these advancements, legacy financial systems continue to suffer from fragmentation, high administrative overhead, and sluggish settlement times. Traditional finance (TradFi) heavily relies on siloed ledgers and fragmented liquidity pools that inhibit optimal capital allocation. In response, infrastructure providers like Injective have engineered specialized blockchains equipped with native financial modules—such as built-in order books, risk management frameworks, and cross-chain execution capabilities—allowing developers to construct financial primitives that were previously impossible on generic smart contract platforms.

The Injective Ecosystem Builder Catalyst accelerator operates as a direct response to this demand for high-performance infrastructure. By combining Outlier Ventures’ extensive venture scaling methodology with Injective’s technical architecture, the program aims to fast-track startups capable of challenging legacy market inefficiencies.

Chronology of the Accelerator Program

The journey of the Injective Ecosystem Builder Catalyst cohort is structured as a rigorous, nine-week operational sprint designed to take early-stage founders from the product-refinement phase to venture-scale execution.

Week 1 through Week 3 focus heavily on product architecture, technical stress-testing, and alignment with Injective’s native financial modules. During this initial phase, founders work closely with core contributors and technical advisors to optimize their smart contracts, enhance execution speed, and ensure seamless integration with Injective’s shared liquidity layers.

Weeks 4 through 6 pivot toward legal structuring, regulatory compliance, and tokenomics design. Given that many of the participating startups deal with institutional-grade products, cross-border payments, and real-world asset tokenization, navigating the complex global regulatory environment is a primary focus. Mentors from Outlier Ventures and legal experts specializing in digital assets provide tailored guidance to ensure long-term viability across multiple jurisdictions.

9 Startups Selected for the Injective Ecosystem Builder Catalyst: Scaling the DeFi-First Future

Weeks 7 through 8 concentrate on go-to-market strategies, community building, and institutional partnership development. Startups refine their pitch decks, conduct beta testing with institutional partners, and prepare for capital-raising milestones.

The culmination of this intensive nine-week program is the upcoming Injective Ecosystem Builder Catalyst Demo Day, scheduled for February 25, 2026. This flagship event serves as the primary gateway for founders to present their finalized products to a global audience of venture capitalists, angel investors, liquidity providers, and prospective enterprise partners.

Detailed Overview of the Selected Cohort Startups

The newly unveiled cohort comprises nine pioneering companies spanning various sectors of financial technology, institutional trading, real-world asset tokenization, and Web3 social infrastructure. Each project utilizes Injective’s underlying architecture to achieve superior capital efficiency and performance.

QuantCite operates as an institutional-grade Order and Execution Management System (OEMS) integrated with advanced smart-routing technology. Designed specifically for quantitative trading funds and professional market makers, QuantCite unifies execution venues across both centralized exchanges and decentralized protocols, ensuring seamless liquidity access and high-performance execution.

Joinn addresses the financial inclusion gap in emerging markets by offering a fintech application that enables everyday users to safeguard and grow their savings through yield-generating, tokenized financial assets. Providing a Web2-like user experience powered by secure blockchain rails, Joinn facilitates gasless, cross-chain transactions coupled with a 24/7 Visa card experience and an integrated artificial intelligence agent designed to automate compounding strategies.

Choice functions as a decentralized exchange and liquidity aggregation layer specifically optimized for the Injective network. By deploying a proprietary routing algorithm capable of tapping into liquidity pools across multiple venues, Choice guarantees optimal swap execution while minimizing slippage for traders.

Stabled tackles the complexities of international trade by providing a compliant cross-border payments platform for businesses. The platform facilitates instant stablecoin transactions that bypass traditional banking intermediaries, substantially reducing foreign exchange losses and settlement delays.

Quantum Street bridges traditional capital markets and decentralized finance by bringing cash-flowing off-chain assets on-chain. Comprising seasoned financial engineers, the project structures transactions for income-generating enterprises, injecting tangible economic utility into stablecoins and accelerating Total Value Locked (TVL) expansion.

Spout introduces a paradigm shift to the equity markets by enabling the peer-to-peer borrowing and lending of U.S. public equities. Through tokenized equities and a collateralized debt position (CDP) model, Spout facilitates 0% APR margin loans alongside attractive lending yields averaging around 10% APY.

Dapps.co reimagines Web3-native social networking by restoring creative agency through tokenized communities and vibrant on-chain economies. The network incorporates an advanced AI provenance layer designed to combat low-quality synthetic media while empowering creators to monetize directly via micro-transactions, direct messaging, and tipping mechanisms.

9 Startups Selected for the Injective Ecosystem Builder Catalyst: Scaling the DeFi-First Future

Chain Capital transforms illiquid private debt into highly tradable digital securities. By tokenizing commercial invoices and corporate receivables, the platform automates complex securitization workflows, cutting middle-office administrative costs by up to 75% while providing institutional investors with compliant access to high-yield investment exposures.

HodlHer represents the world’s first AI-driven Web3 operating system built natively on Injective. Utilizing intelligent AI personas, the platform assists users, creators, and decentralized projects through a complete operational loop encompassing market perception, analytical reasoning, and automated on-chain execution.

Statements and Industry Perspectives

While specific direct quotes from individual founders remain integrated within their ongoing venture presentations, leadership teams from both Outlier Ventures and Injective have emphasized the strategic importance of this collaboration. Representatives from Outlier Ventures noted that the caliber of teams in this cohort reflects a maturing industry that is no longer content with merely replicating traditional financial models. Instead, founders are aggressively architecting novel economic primitives made possible exclusively by high-speed, interoperable layer-1 networks.

Similarly, ecosystem advocates within Injective have underscored that the integration of institutional-grade tooling, RWA tokenization, and AI-driven agents marks a definitive turning point for decentralized applications. By offering functional parity with traditional financial order books alongside decentralized composability, Injective aims to position itself as the undisputed destination for developers seeking uncompromising technical performance.

Fact-Based Analysis of Implications

The launch of the Injective Ecosystem Builder Catalyst cohort carries several significant implications for the broader blockchain and financial technology sectors.

First, the strong emphasis on institutional-grade infrastructure—exemplified by projects like QuantCite, Chain Capital, and Stabled—suggests a continued convergence between decentralized finance and traditional institutional capital markets. As regulatory frameworks around the globe gradually accommodate tokenized assets and stablecoin settlements, platforms capable of offering institutional compliance alongside decentralized transparency are positioned to capture substantial market share.

Second, the integration of artificial intelligence agents into financial and social layers, as demonstrated by Joinn and HodlHer, points toward an emerging trend of autonomous on-chain finance. By delegating complex trading, yield-compounding, and administrative tasks to intelligent software personas, user friction is significantly reduced, potentially accelerating mainstream consumer adoption of Web3 applications.

Finally, the geographical and economic diversity of the cohort highlights the global reach of modern financial technology. By addressing localized pain points such as cross-border payments in emerging markets and illiquid private debt in traditional sectors, these startups demonstrate tangible utility that extends far beyond speculative token trading.

As the nine-week accelerator program progresses toward its culmination at the Demo Day on February 25, 2026, industry observers will closely monitor how these startups scale their operations, secure institutional partnerships, and deploy their infrastructure to the broader public. Stakeholders, investors, and community members interested in tracking the cohort’s evolution can access additional event details and registration links via the official Outlier Ventures and Luma event platforms.

November 15, 2026 0 comment
0 FacebookTwitterPinterestEmail
Cybersecurity & Hacking

White House Staffers Unknowingly Turn Official Network into Open Proxy Nodes for Rent, Security Experts Warn

by admin November 15, 2026
written by admin

Multiple computers and mobile devices connected to the secure network of the Executive Office of the President have been inadvertently functioning as active residential proxy nodes, allowing external users to route internet traffic through the heart of the United States government. According to findings released by cybersecurity researchers, these devices—likely operated by White House staffers—were running consumer applications integrated with commercial proxy software. This oversight effectively rendered portions of the official government internet address block available for public rent, creating a critical cybersecurity loophole that leaves one of the world’s most sensitive networks exposed to exploitation, data scraping, and anonymous cyber activity.

The discovery highlights a pervasive and rapidly growing blind spot in modern enterprise and government security: the inadvertent integration of residential proxy software through seemingly harmless mobile and desktop applications. Security firms monitoring global internet infrastructure revealed that this unauthorized proxy traffic was not an isolated glitch, but a persistent and measurable operational vulnerability occurring inside official government facilities over a multi-week monitoring window.

Detection and Technical Findings

The alarming security posture was first brought to light by the specialized threat intelligence firm Layer3 Intel. Analysts reported that they detected multiple residential proxy nodes beaconing outward from internet address block AS2650, which is officially reserved and assigned exclusively to the Executive Office of the President.

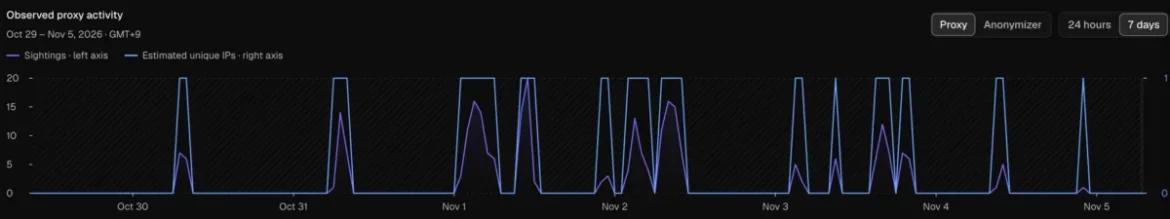
According to Layer3 Intel’s telemetry, this unauthorized proxy activity was relatively persistent between October 5 and November 3. A comprehensive review of the active proxies available through the AS2650 block showed that connection exit nodes routed traffic directly out of the White House network on 236 separate occasions during that specific timeframe. Further analysis revealed that the activity originated from six distinct internet addresses within the government network. Crucially, this traffic was not observed as a continuous, 24-hour stream; rather, it manifested on 26 of the 30 monitored days, with the vast majority of the proxy routing activity concentrated during evening hours, specifically between 5:00 p.m. and midnight local time.

Simultaneously, proxy-tracking and threat-intelligence firm Synthient corroborated these findings, publishing network telemetry pointing directly to Windows 11 installations running a commercial service known as Infatica. Infatica operates as a residential proxy program that is frequently bundled or covertly integrated into "free" consumer-facing mobile and desktop applications, browser extensions, and utility tools.

The Connection to Infatica and Historical Cyberattacks

The involvement of Infatica brings a significant geopolitical and historical dimension to the incident. Infatica was founded by Vladimir Fomenko, a Russian national whose previous web hosting venture, King Servers, played a central and well-documented role in past cyber operations targeting American democratic infrastructure.

Back in 2016, King Servers served as the foundational infrastructure—described by investigators as ground zero—for state-sponsored cyberattacks that breached voter registration and election administration databases in Arizona and Illinois. During those attacks, six of the eight specific internet addresses utilized by Russian state security services

to compromise the U.S. election systems were traced directly back to Fomenko’s King Servers hosting infrastructure.

While the current presence of Infatica nodes within the White House network does not inherently indicate a targeted state-sponsored cyber offensive from the same actors, security experts emphasize the severe inherent risks. Allowing software linked to individuals with such backgrounds to operate on a secure government network presents an unacceptable counterintelligence and operational security hazard.

The Scale of the Problem: Public Access to Government Assets

Perhaps most startling to security professionals is the sheer accessibility of the White House network through these commercial channels. Layer3 Intel discovered that Infatica was not an isolated anomaly operating within the Executive Office of the President’s infrastructure. In total, the security firm identified 28 separate residential proxy services that were capable of routing traffic and exiting through the AS2650 network block.

In a published technical analysis, the Layer3 Intel research team underscored the trivial nature of gaining access to these privileged endpoints, writing that the network had effectively been turned into a public resource. According to the firm, anyone could obtain access simply by signing up for a public residential proxy service, paying a nominal fee of a few dollars, and routing web requests through it.

The researchers stressed that they did not selectively target the White House network or deliberately attempt to force their network probes to exit through government infrastructure. Instead, the exposure was discovered entirely by chance while requesting global rotating access through standard, commercially available proxy networks.

Broad Ecosystem Risks and Prior Vulnerabilities

The exposure of government infrastructure via residential proxies is symptomatic of a broader, systemic failure in how modern organizations manage endpoint security and software procurement on corporate and government devices. Residential proxy services operate by turning ordinary consumer internet connections—typically residential broadband lines—into commercial exit nodes. Customers of these proxy services pay to route their web traffic through these residential IPs to mask their true locations, evade anti-bot detection systems, bypass geographic content blocks, or execute coordinated web scraping operations.

However, the ecosystem surrounding residential proxy providers is notoriously opaque. Many of these services engage in aggressive monetization schemes, paying software developers to integrate Software Development Kits (SDKs) into consumer applications. Unsuspecting users install games, VPNs, or utility apps, unknowingly granting the software permission to share their device’s internet bandwidth with third parties.

This architecture introduces profound cybersecurity vulnerabilities. In late 2025, security researchers uncovered a widespread flaw wherein cybercriminals aggressively targeted vulnerabilities within residential proxy services. Attackers leveraged these proxy endpoints to pivot inward, scanning the local networks of unsuspecting users for unpatched systems, vulnerable Internet of Things (IoT) devices, and internal corporate assets to infect with malware.

In January 2026, dozens of residential proxy providers were forced to rush emergency security patches after Ben Brundage, founder of Synthient, publicly demonstrated how malicious actors were actively abusing proxy vulnerabilities to execute unauthorized code and seize control of local network devices.

Speaking to cybersecurity journalists, Brundage highlighted the terrifying economics of the threat landscape. He noted that certain proxy resellers sell bandwidth for as little as 60 cents per gigabyte, meaning an attacker can spend less than a dollar to gain a foothold inside some of the most confidential and trusted networks in the world. Furthermore, the fragmented reseller ecosystem frequently allows bad actors to bypass standard Know Your Customer (KYC) and identity verification protocols completely anonymously.

Corporate and Government Blind Spots

The presence of residential proxies on the White House network is indicative of a widespread blind spot across both the public and private sectors. Because these proxy nodes are typically installed via employee-owned devices brought into the workplace, or through personal applications installed on agency-issued hardware, traditional perimeter defenses often fail to flag them as immediate malware infections. Instead, the software operates under the guise of legitimate application traffic.

Data from other cybersecurity organizations underscores the sheer magnitude of this enterprise risk. During a comprehensive industry webinar in January 2026, proxy-tracking service Spur revealed alarming statistics regarding the prevalence of residential proxy nodes across critical infrastructure. Spur’s analysis detected active residential proxies residing within nearly 300 government-owned and operated networks across the United States. Additionally, the tracking firm identified proxy nodes inside 318 utility companies, 166 healthcare organizations and hospitals, and 141 institutions operating within the banking and financial sectors.

Reinforcing these findings, a comprehensive threat report published earlier this year by security firm Infoblox revealed that a staggering 65% of its entire enterprise customer base had corporate or organizational networks querying one or more domains associated with residential proxy services. This widespread corporate contagion demonstrates that organizations of all sizes struggle to maintain visibility over the software supply chain running on endpoints connected to their internal networks.

Implications and Official Response

As of press time, the White House has not formally responded to media requests for comment regarding the detection of residential proxy exit nodes within the Executive Office of the President’s network. The lack of an immediate public statement leaves open questions regarding how many devices were ultimately compromised, whether any sensitive data was accessed or exfiltrated by third parties utilizing the proxy network, and what remediation steps the administration’s Office of Administration and Chief Information Officer are taking to purge the unauthorized software.

The implications of this security lapse extend far beyond simple bandwidth theft or network congestion. When government networks act as commercial exit nodes, malicious actors can leverage those highly trusted, government-owned IP addresses to conduct sophisticated cybercrimes, launch credential-stuffing attacks against financial institutions, commit large-scale advertising fraud, or orchestrate targeted espionage operations while entirely masking their digital footprints behind the federal government’s digital perimeter.

For federal agencies and enterprise organizations alike, the incident serves as a stark reminder of the urgent need for enhanced endpoint visibility, strict application whitelisting, and robust monitoring of outbound network telemetry. As long as employees continue to introduce consumer-grade software and unvetted applications onto hardware connected to high-value networks, trusted infrastructure will remain dangerously susceptible to exploitation by the very commercial proxy ecosystems designed to obscure the digital underworld.

November 15, 2026 0 comment
0 FacebookTwitterPinterestEmail
Cybersecurity & Hacking

Meta hit with 805 million euro fine by Italian regulators over intrusive Android photo gallery access practices

by admin November 15, 2026
written by admin

The Italian Data Protection Authority, known as the Garante per la protezione dei dati personali, has imposed a substantial penalty of 805 million euros on Meta Platforms Inc. The fine follows a rigorous investigation into the company’s data processing practices within its Facebook application for Android. At the heart of the controversy is a feature designed to suggest photos and videos from users’ local device storage for potential social media posts. The Garante concluded that this mechanism was enabled by default and systematically accessed private gallery metadata and files without obtaining the explicit, informed consent required under European privacy law.

A Breach of Privacy Code and ePrivacy Directive

The investigation centered on a violation of Article 122 of Italy’s Privacy Code, which serves as the national implementation of the European Union’s ePrivacy Directive. Under this legal framework, a mobile device is considered a protected extension of an individual’s private life. Consequently, any digital access to the contents of a smartphone—such as personal photos, videos, and associated EXIF metadata—requires the user to provide "free and informed" consent.

The Garante’s technical analysis revealed that the Facebook application employed a "catch-all" permission structure. When users granted the app permission to access their device storage, the application utilized that singular authorization for multiple functions, including the controversial photo-suggestion tool. The authority determined that the general notices presented to users at the time of installation or app updates were insufficient. These notices failed to clearly delineate that enabling standard app permissions would also grant the company access to scan and analyze the user’s entire photo archive on an ongoing basis. Because the scope of the data collection was opaque, the authority ruled that users could not have provided valid consent, rendering the feature’s operation unlawful regardless of whether the data was transferred to external servers or resulted in measurable harm to the individual.

Chronology of the Investigation

The regulatory scrutiny began following a formal complaint filed by the Centro Tutela Consumatori Utenti (CTCU), a consumer protection group based in Bolzano, Italy. The group’s advocacy, which gained significant momentum in mid-2025, highlighted the privacy risks associated with the automatic scanning of personal media.

Italy Fines Meta €805 Million Over Facebook's Android Gallery Access Without Explicit Consent
  • 2023: Meta introduces the "Gallery Suggestion" feature for Android users, designed to prompt users to share content stored on their local devices.
  • July 11, 2025: The Centro Tutela Consumatori Utenti publishes official consumer advice, urging users to manually disable gallery access and review app permissions, citing unauthorized processing of unpublished photos.
  • July 2025: The Garante formally launches an investigation into the feature, deploying its own technical teams to audit the Facebook Android application’s data processing activities.
  • November 2026: The Garante concludes the investigation, issuing an 805 million euro fine and ordering Meta to cease the default-enabled status of the feature within 60 days.

Supporting Data and Regulatory Weighing

The penalty of 805 million euros represents approximately 0.47% of Meta’s global revenue, a figure calculated based on several aggravating factors identified by the Garante. The authority noted that the breach affected approximately 20 million Android users in Italy. Furthermore, the duration of the infringement was a critical factor; the violation remained ongoing for users who had not updated their application or who had previously granted broad permissions without awareness of the secondary use of their data.

The authority also cited Meta’s limited cooperation during the investigative process and a historical precedent—a 2019 regulatory decision against the company—as reasons for the severity of the fine. While the Garante acknowledged that Meta had made some remedial changes to its interface following the initial consumer complaints, it deemed these adjustments "late and limited," noting that they only applied to users who actively updated their software.

Meta’s Defense and Legal Strategy

Meta has signaled its intent to appeal the ruling, characterizing the fine as "disproportionate" in a public statement released via a spokesperson. The company maintains that the feature functions exclusively after a user provides permission on their device, asserting that users retain full control over their privacy settings.

In its defense during the investigative phase, Meta argued that the case should fall under the jurisdiction of the Irish Data Protection Commission (DPC), which typically acts as the lead supervisory authority for Meta’s European operations under the General Data Protection Regulation (GDPR). However, the Garante rejected this "one-stop-shop" argument, noting that the case concerns the ePrivacy Directive, which operates under a different legal framework that does not facilitate a centralized, single-authority mechanism for enforcement.

Broader Implications for Tech Governance

The ruling sets a significant precedent for how mobile applications handle local device content. By emphasizing that "convenience features" cannot bypass the requirement for explicit, informed consent, the Garante has signaled a tougher stance on the "dark pattern" design practices often used to secure broad permissions from unsuspecting users.

Italy Fines Meta €805 Million Over Facebook's Android Gallery Access Without Explicit Consent

Furthermore, while the current investigation did not conclude whether the gallery content was used for training artificial intelligence models—an accusation Meta denies—the ruling hints at future regulatory friction. The Garante indicated that it may launch a separate inquiry into newer cloud-based processing features introduced by Meta, which could potentially expose the company to further legal challenges regarding the scope of AI data harvesting.

The Impact on Users and Future Compliance

The Garante’s order imposes strict requirements on Meta. Within 60 days, the company must:

  1. Disable the gallery suggestion feature by default for all users, including those who have already provided permissions.
  2. Implement a separate, explicit consent process for the feature, ensuring users understand exactly what they are authorizing.
  3. Ensure that failure to meet this deadline results in the feature remaining permanently disabled for any user who has not provided valid, specific consent.

For the 20 million affected users in Italy, the ruling serves as a reminder of the importance of auditing smartphone permissions. Consumer groups continue to advise that users regularly navigate to their device settings to check which applications possess "read" access to photo libraries and to revoke such access for apps that do not require it for core functionality.

The implications for the wider technology industry are profound. Companies that rely on local device data to drive engagement metrics must now reconcile their product design with the reality of increasing regulatory intervention. As privacy authorities across the European Union watch this case closely, the precedent established by the Garante may inform future enforcement actions across the bloc, potentially forcing a global shift in how social media platforms interact with personal digital archives.

As of mid-November 2026, the tech industry remains in a state of watchful waiting. The eventual outcome of Meta’s appeal will clarify the legal boundaries of the ePrivacy Directive in the context of modern app ecosystems, but the immediate message from the Italian regulator is clear: privacy by design is no longer a suggestion, but a prerequisite for operation in the European market.

November 15, 2026 0 comment
0 FacebookTwitterPinterestEmail
Cybersecurity & Hacking

FBI Warns Hackers Are Weaponizing AI Penetration Framework ARTEX to Automate Global Cyberattacks

by admin November 15, 2026
written by admin

Federal law enforcement authorities have issued an urgent, cross-sector advisory warning that malicious cyber actors are aggressively weaponizing an autonomous artificial intelligence penetration testing framework known as ARTEX. According to a joint intelligence assessment, the open-source platform is being utilized to orchestrate high-speed, multi-tiered cyberattacks against critical infrastructure, government networks, financial institutions, and major corporate environments worldwide. The advisory highlights a worrying evolution in the threat landscape, demonstrating how threat actors are successfully leveraging large language models to compress timelines for complex network intrusions down to mere hours.

The exploitation of ARTEX represents a paradigm shift in modern cybersecurity. Where traditional advanced persistent threat (APT) campaigns required meticulous, manual enumeration and days or weeks of reconnaissance, agentic AI frameworks allow attackers to automate the entire attack lifecycle. From initial target discovery and vulnerability scanning to privilege escalation and data exfiltration, ARTEX executes these operations with minimal human intervention. Cybersecurity analysts, incident responders, and national security agencies are now racing to understand the full scope of campaigns tied to the framework, implement robust detection mechanisms, and shore up defences against AI-accelerated cyber assaults.

Mechanics and Capabilities of the ARTEX Framework

ARTEX is an autonomous penetration testing framework authored primarily in the Go programming language. Its core architecture relies on artificial intelligence agents designed to accept high-level operational directives from human operators, translate those goals into specific technical tasks, and autonomously execute them against target networks. Rather than depending on proprietary neural networks, ARTEX integrates seamlessly with a broad array of commercially available and open-source large language models. These include prominent architectures such as Anthropic’s Claude, OpenAI’s GPT models, DeepSeek, GLM, Grok, and Kimi.

By interfacing with these advanced LLMs, ARTEX can dynamically adapt its tactics based on real-time feedback from target environments. If an initial exploitation attempt fails or encounters a defensive barrier, the AI agents automatically pivot, analyze alternative pathways, and deploy secondary techniques. According to intelligence compiled by the Federal Bureau of Investigation, this capability drastically reduces the temporal footprint of an intrusion. The agency noted that several recorded operations progressed smoothly from initial target acquisition to total privileged domain compromise in less than three hours.

Furthermore, the framework excels at identifying vulnerabilities in overlooked perimeter assets and third-party integrations. Rather than focusing solely on heavily guarded core infrastructures, ARTEX actively probes legacy services, employee portals, partner integrations, and cloud administration interfaces. This operational efficiency enables attackers with minimal specialized technical knowledge to conduct sophisticated, multi-target operations simultaneously, effectively democratizing advanced cyber espionage and mass exploitation capabilities.

Chronology and Evolution of the Threat

The proliferation and subsequent weaponization of ARTEX unfolded rapidly over a matter of months, highlighting the speed at which dual-use security tools can be co-opted by malicious actors.

FBI warns ARTEX AI hacking tool is powering global cyberattacks
  • July 2026: The ARTEX framework is initially published on GitHub by an independent developer operating under the alias Autumn-27, ostensibly intended as an advanced, automated penetration testing utility for security professionals.
  • August 2026: Multiple distinct threat groups, including state-sponsored entities and financially motivated cybercriminal syndicates, begin weaponizing the open-source codebases for active cyber operations targeting global infrastructure.
  • October 8, 2026: Amid mounting reports of widespread abuse and active exploitation campaigns, the original developer removes the GitHub repository, though copies, forks, and localized variants continue to circulate within underground forums.
  • October 2026: High-profile supply-chain attacks and regional breaches—most notably the ConnectWise Cloud Backup compromise and attacks against South Korean financial institutions—are publicly linked to ARTEX and agentic AI tools.
  • November 2026: Security researcher MalwareMustDie releases an open-source detection signature pack, while the FBI releases a comprehensive 13-page Flash Advisory detailing indicators of compromise and urging immediate remediation across vulnerable sectors.

Despite the removal of the official repository, the framework remains highly accessible through decentralized channels. Security researchers scanning global internet-facing assets in early November identified more than 1,600 publicly exposed ARTEX control consoles, though intelligence analysts believe the actual number of localized, private deployments is significantly higher.

High-Profile Incidents and Campaign Attribution

The operational efficacy of ARTEX has been demonstrated in several major, highly publicized cyber incidents over recent months. Security firms and government investigators have successfully attributed multiple sprawling campaigns to specific threat groups utilizing the AI framework.

The ConnectWise Cloud Backup and Microsoft 365 Supply-Chain Breach

In October 2026, cybersecurity researchers and Microsoft uncovered a sophisticated supply-chain attack targeting ConnectWise Cloud Backup (formerly SkyKick Cloud Backup). The campaign was attributed by Microsoft Threat Intelligence to a China-state-aligned actor tracked as Storm-0940.

The attackers successfully compromised application identities utilized by the backup service, granting them authorized pathways into downstream customer environments. Using ARTEX to automate and accelerate their operations, the actors attempted authentication against more than 2,250 separate Microsoft 365 tenant environments. The AI agents managed to infiltrate at least 162 distinct customer tenants, modifying credentials and establishing persistent access before defenders could successfully isolate the compromised tokens.

Targeting of South Korean Financial Institutions

Simultaneously, financial sectors in East Asia experienced a wave of automated intrusions. A Chinese-speaking threat actor combined ARTEX with Claude Code agents to execute coordinated attacks against major South Korean banking institutions, including Shinhan Bank, KB Kookmin Bank, and Hana Bank.

The operation resulted in the exposure of sensitive personal data belonging to approximately 67,000 individuals. CrowdStrike researchers later discovered exposed attacker infrastructure containing detailed ARTEX configuration files and session logs. In a related domestic crackdown, South Korean law enforcement authorities arrested seven suspects connected to a wider cybercriminal ring that utilized ARTEX to breach over 90 organizations, stealing roughly 8.2 million records from hospitals, educational entities, and private businesses.

Vapor Panda Cyberespionage Operations

CrowdStrike also documented a sprawling espionage campaign conducted by a Chinese threat group tracked as Vapor Panda. The group deployed ARTEX in automated assaults against more than 200 organizations distributed across 14 countries. Successful compromises were confirmed in at least nine distinct organizations, where autonomous AI agents performed deep reconnaissance, exploited edge-case vulnerabilities, deployed web shells, and systematically harvested corporate credentials.

FBI warns ARTEX AI hacking tool is powering global cyberattacks

Official Responses and Defensive Recommendations

In response to the escalating threat posed by autonomous attack frameworks, regulatory bodies, law enforcement agencies, and independent security researchers have mobilized to provide actionable defensive guidance.

The FBI’s advisory stresses that while automated AI attacks frequently generate a high volume of telemetry and suspicious traffic alerts, their sheer velocity often leaves human security operations centers (SOCs) with insufficient reaction time. To counter this, the bureau recommends a multi-layered defensive posture focusing on identity management, perimeter hardening, and behavioral anomaly detection.

Organizations are strongly advised to:

  • Secure and audit all internet-facing applications, legacy services, and partner integration portals.
  • Strictly restrict and monitor administrative access to cloud management consoles and API endpoints.
  • Implement rigorous rate-limiting policies on sensitive web applications and APIs to stymie automated enumeration and brute-force attempts.
  • Continuously review application permissions, OAuth tokens, and authentication logs for anomalous privilege escalations or unexpected modifications.
  • Deploy behavior-based monitoring tools designed to detect abnormal bursts of automated requests, rapid lateral movement patterns, and large-scale data staging.

Complementing the government advisory, independent researcher MalwareMustDie released a comprehensive, open-source detection signature pack. The package includes specialized rules tailored for popular security monitoring and threat-detection platforms, providing rules to identify suspicious network traffic, cloud-native API abuse, anomalous identity management actions, and known file signatures associated with ARTEX deployments.

Broader Implications for Enterprise Security

The widespread operational deployment of ARTEX marks a definitive turning point in the asymmetric warfare of cyberspace. For decades, cybercriminals and state-sponsored espionage units maintained an advantage in scale and persistence, while defenders relied on automation primarily for threat hunting and incident response. The integration of agentic artificial intelligence into offensive toolkits completely flips this dynamic, giving attackers the ability to scale sophisticated, individualized attacks globally with minimal operational overhead.

As large language models continue to evolve and autonomous frameworks become more resilient, organizations can expect automated reconnaissance and exploitation to become the baseline standard for sophisticated threat actors. Cybersecurity strategies must similarly evolve, shifting away from manual log review toward real-time, automated defensive orchestration capable of matching the speed and precision of artificial intelligence-driven attacks. Enterprises failing to adapt to this AI-accelerated threat landscape risk finding their traditional perimeter defenses outpaced by autonomous adversaries operating at machine speed.

November 15, 2026 0 comment
0 FacebookTwitterPinterestEmail
Bitcoin & Altcoins

Kraken Expands Its Digital Asset Offerings with the Official Listing of Pearl (PEARL) Layer-1 Blockchain Token

by admin November 15, 2026
written by admin

Major cryptocurrency exchange Kraken has officially announced the integration of Pearl (PEARL), the native coin of the Pearl network, onto its trading platform. Going live on November 13, 2026, the listing marks a significant milestone for both the exchange and the emerging sector of decentralized artificial intelligence infrastructure. The inclusion of PEARL allows users worldwide to deposit, trade, and manage the asset directly through Kraken and Kraken Pro, offering broader market liquidity to a network bridging traditional blockchain consensus mechanisms with high-performance artificial intelligence computing.

The rollout of PEARL on Kraken opens up new avenues for crypto traders and institutional investors interested in the convergence of decentralized finance (DeFi) and artificial intelligence (AI). As the digital asset ecosystem continues to mature, exchanges are increasingly vetting projects that offer tangible utility beyond conventional speculative instruments. Pearl’s unique positioning within the Layer-1 blockchain landscape makes it a noteworthy addition to Kraken’s growing catalog of supported cryptocurrencies.

Background Context of the Pearl Network and Proof of Useful Work

To understand the significance of PEARL’s listing, one must examine the fundamental architecture of the Pearl network. Unlike traditional Layer-1 blockchains that rely heavily on energy-intensive Proof of Work (PoW) algorithms involving abstract cryptographic hashing—such as Bitcoin—or stake-based validation models like Proof of Stake (PoS), the Pearl network is secured by an innovative consensus mechanism known as Proof of Useful Work (PoWoW).

In a standard PoW system, vast amounts of computational power are expended solving complex mathematical puzzles that serve no direct purpose outside of network security. In stark contrast, Pearl miners perform matrix multiplication, which is recognized as the core graphical processing unit (GPU) operation driving modern artificial intelligence training and inference workloads. By aligning blockchain security with practical computational needs, the Pearl network ensures that the energy and hardware power dedicated to mining are simultaneously channeled into powering AI models.

Under this model, valid mining proofs are generated organically from the exact computations that a GPU is already executing for AI applications. New PEARL tokens are subsequently issued as block rewards to miners who successfully discover valid blocks, supplemented by standard transaction fees. This dual-utility framework aims to address two critical global bottlenecks simultaneously: the escalating energy consumption of blockchain verification and the chronic shortage of accessible GPU infrastructure required for large-scale artificial intelligence development.

Timeline and Chronology of the Listing

The integration of PEARL onto Kraken follows a rigorous internal review process typical of top-tier digital asset exchanges. Although the listing went live on November 13, 2026, preparations for asset integration span months of technical coordination between Kraken’s engineering teams and the core developers of the Pearl network.

Leading up to the launch date, Kraken maintained its strict policy of non-disclosure regarding upcoming listings, preserving market integrity and preventing speculative volatility prior to the official announcement. On November 13, trading pairs opened simultaneously across Kraken and Kraken Pro, accompanied by the immediate activation of deposit and withdrawal channels. Users seeking to acquire the asset were directed to navigate to the platform’s funding portal, select the PEARL asset, and generate a deposit address, with strict advisories issued regarding the necessity of utilizing exclusively supported networks to prevent permanent loss of funds.

Market Data and Tokenomics Integration

The valuation and market reception of PEARL are closely tied to the broader trends dictating the decentralized physical infrastructure network (DePIN) and AI compute sectors. Analysts note that tokens bridging blockchain technology with generative AI and machine learning infrastructure have experienced heightened demand throughout 2025 and 2026.

PEARL is available for trading!

By integrating PEARL, Kraken provides its global user base with direct exposure to this high-growth niche. Tokenomics on the Pearl network are structured around incentivizing hardware providers—primarily GPU owners and data center operators—to contribute their idle or dedicated processing power to the network. As AI adoption accelerates globally, the demand for matrix multiplication operations is projected to scale exponentially, potentially driving organic transactional and computational activity across the Pearl blockchain. Financial market observers emphasize that while the asset’s inclusion on a major exchange like Kraken typically enhances liquidity and price discovery, its long-term viability will depend heavily on sustained enterprise and developer adoption of the underlying Pearl network infrastructure.

Official Responses and Exchange Policies

Kraken’s leadership has consistently emphasized a disciplined, compliance-first approach to asset listings. While the exchange frequently expands its portfolio to include innovative digital assets, it maintains a strict firewall between its listings committee and client-facing support staff.

In its official launch communication, Kraken reiterated its long-standing policy regarding future asset additions: the company does not reveal details or potential candidates for listing prior to an official, coordinated rollout. All future token additions are slated to be announced exclusively through the official Kraken Listings Roadmap and verified corporate social media channels, such as their dedicated announcements profile on X (formerly Twitter). Client engagement representatives remain strictly constrained from answering inquiries regarding unreleased or rumored asset integrations, ensuring an equitable information ecosystem for all market participants.

Broader Industry Impact and Strategic Implications

The listing of Pearl on Kraken underscores a broader paradigm shift within the cryptocurrency industry. As the boundarylines between traditional technology sectors and Web3 continue to blur, Layer-1 networks that offer verifiable, real-world utility are commanding increased attention from both retail and institutional capital.

Projects like Pearl represent a direct challenge to the critique that blockchain technology operates in an economic and environmental vacuum. By repurposing the computational heavy lifting of blockchain consensus to fuel AI training and inference, the network addresses mounting environmental and efficiency concerns associated with decentralized ledgers. For Kraken, supporting such assets aligns with a strategic vision of fostering a more mature, utility-driven digital asset economy.

Furthermore, the integration provides valuable market data regarding investor appetite for decentralized AI compute tokens. As regulatory frameworks surrounding digital assets continue to evolve across global jurisdictions, exchanges are placing a premium on tokens with clear operational use cases and transparent tokenomics. The successful debut of PEARL on a regulated, globally compliant venue like Kraken serves as a bellwether for how utility-centric Layer-1 chains can successfully transition from specialized developer ecosystems into mainstream financial markets.

Future Outlook for Kraken and the Pearl Ecosystem

Looking ahead, the collaboration between Kraken and the Pearl network is expected to foster deeper integration as both platforms scale. For the Pearl network, access to Kraken’s robust liquidity pools and vast international user base provides the foundational market depth required to attract larger enterprise clients and independent GPU miners alike. Increased liquidity typically correlates with tighter bid-ask spreads and more stable price discovery, which are essential prerequisites for institutional participation.

Meanwhile, Kraken continues to cement its reputation as a premier venue for discovering cutting-edge blockchain technologies. By maintaining rigorous technical standards for asset onboarding while aggressively expanding into high-utility sectors such as decentralized AI, the exchange positions itself at the forefront of the next wave of financial and technological innovation. As the digital asset markets absorb the introduction of PEARL, industry analysts will closely monitor network hash rates, GPU contribution metrics, and trading volume trends to gauge the sustained momentum of this unique intersection between blockchain infrastructure and artificial intelligence.

November 15, 2026 0 comment
0 FacebookTwitterPinterestEmail
Newer Posts
Older Posts

Recent Posts

  • Life After Blur: A Comprehensive Guide for NFT Collectors Navigating the New Marketplace Landscape
  • The Disconnect Between Humanoid Robot Hype and the Reality of Modern Robotic Warfare
  • South Korea Proposes Major Legislative Overhaul to Tighten Cryptocurrency Exchange Regulations and Curb Financial Crime
  • Starling Bank Launches Talk to Transact Feature as Agentic AI Transforms Digital Banking in the United Kingdom
  • Justin Aversano Moments of the Unknown: 7 Floors in NYC

Recent Comments

No comments to show.
  • Facebook
  • Twitter

@2021 - All Right Reserved. Designed and Developed by PenciDesign


Back To Top
Dr Crypton
  • Home
  • About Us
  • Contact Us
  • Cookies Policy
  • Disclaimer
  • DMCA
  • Privacy Policy
  • Terms and Conditions

We are using cookies to give you the best experience on our website.

You can find out more about which cookies we are using or switch them off in .

Dr Crypton
Powered by  GDPR Cookie Compliance
Privacy Overview

This website uses cookies so that we can provide you with the best user experience possible. Cookie information is stored in your browser and performs functions such as recognising you when you return to our website and helping our team to understand which sections of the website you find most interesting and useful.

Strictly Necessary Cookies

Strictly Necessary Cookie should be enabled at all times so that we can save your preferences for cookie settings.