The digital landscape is littered with the digital ghost towns of abandoned applications, but few carry the latent, systemic risk of a forgotten media-streaming client discovered by cyber defense specialists. Security researchers at Eye Security have successfully neutralized a critical vulnerability within the update mechanism of Time4Popcorn—an abandoned fork of the infamous Popcorn Time BitTorrent streaming application. Tracked as CVE-2026-30612, the security flaw exposed millions of Windows and macOS devices worldwide to remote code execution (RCE) attacks with elevated privileges. Rather than exploiting the vulnerability for malicious purposes or leaving the loophole open for cybercriminal exploitation, the researchers executed a high-stakes, proactive remediation campaign, systematically disabling the vulnerable updaters across millions of dormant installations before the infrastructure could fall into hostile hands.
The Genesis and Architecture of the Flaw
To understand the magnitude of the threat averted by Eye Security, it is necessary to examine the architectural flaws inherent in the Time4Popcorn application. Popcorn Time originally gained global notoriety as a peer-to-peer BitTorrent client wrapped in a polished, Netflix-style user interface, allowing users to stream pirated movies and television shows seamlessly. Although the original developers abandoned the project due to intense legal pressure, the open-source nature of the software meant that numerous unofficial forks quickly emerged. Among these, Time4Popcorn amassed a massive user base, capitalizing on the brand recognition of its predecessor.
However, many of these derivative applications were built with inadequate attention to long-term software maintenance and secure coding practices. The core vulnerability stemmed from the way the desktop applications handled software updates. Both the Windows and macOS variants of Time4Popcorn were configured to periodically ping an abandoned domain—specifically, popcorntimeupd.xyz—to check for new software versions.
Critically, these communication requests were transmitted entirely over unencrypted HTTP rather than secure HTTPS. Furthermore, the updater binary lacked any cryptographic verification mechanisms, meaning it accepted and executed incoming executable files without validating digital signatures. Any malicious actor who managed to acquire or spoof the abandoned domain could easily intercept the unencrypted HTTP traffic, inject malicious payloads, and force the client applications to execute arbitrary code. Because of how the applications were originally deployed and granted permissions on host operating systems, successful exploitation would grant attackers absolute control: SYSTEM-level privileges on Windows machines and root-level access on macOS systems. If weaponized by threat actors, this architectural oversight could have birthed an unprecedented botnet capable of massive distributed denial-of-service (DDoS) attacks, ransomware distribution, or corporate espionage.
Uncovering the Scale: Millions of Dormant Installations
The discovery of CVE-2026-30612 occurred almost by accident during routine domain analysis and threat intelligence monitoring. Specialists at Eye Security identified that the primary update domain associated with Time4Popcorn had lapsed and was available for registration. Recognizing the latent danger, the researchers proactively registered popcorntimeupd.xyz to observe incoming traffic and assess the potential exposure.
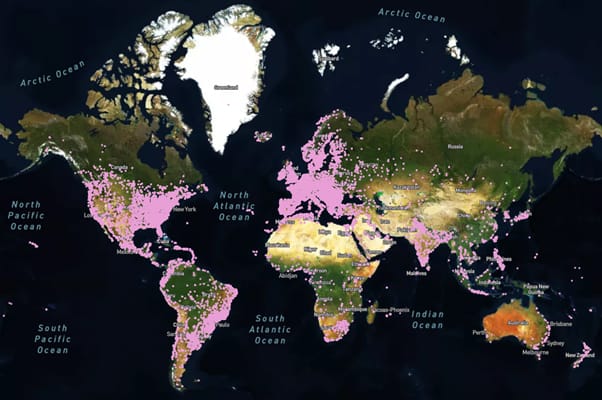
The telemetry data collected following the domain registration astonished the research team. Within a remarkably short window, the infrastructure recorded connection requests from approximately 3 million Windows clients and 350,000 macOS clients. A geographic and network analysis of these connections revealed a startling breadth of distribution. Requests flooded in not only from standard residential Internet Service Providers (ISPs) but also from enterprise corporate networks, government institutions, and even sensitive military environments.
A deeper forensic analysis of the connecting clients provided a crucial silver lining: despite the massive volume of connections, telemetry indicated that none of the users appeared to be actively running or streaming content through the application. This behavioral pattern strongly suggested that the software had been installed years prior, forgotten by users, and left lingering in the background of their operating systems long after the service itself had ceased functioning. Nevertheless, the presence of the software on these systems meant that a dormant ticking time bomb remained embedded within critical and sensitive networks globally.

Recognizing that control of a single domain was insufficient to secure the entire ecosystem, the researchers expanded their intelligence-gathering efforts and successfully registered 14 additional domains historically linked to the Time4Popcorn infrastructure.
A Novel Remediation Chronology
Faced with millions of vulnerable systems communicating with infrastructure under their temporary control, Eye Security faced a unique ethical and operational dilemma. Standard security protocols usually dictate disclosing vulnerabilities to software vendors and allowing them to patch the issue. However, because Time4Popcorn was entirely abandoned, no vendor existed to issue a patch. Leaving the systems exposed until users manually uninstalled the software was deemed unacceptably risky, as any lapsed domain could theoretically be scooped up by financially motivated cybercriminals or state-sponsored APT groups.
To mitigate the threat permanently without causing collateral damage, the researchers devised a meticulously planned remediation operation, carried out between November 2025 and March 2026.
Using the very update mechanism that posed the security threat, Eye Security deployed a customized, benign remediation payload to the connecting client applications. Rather than installing malware, the payload was engineered strictly to stop and permanently disable the vulnerable updater service, cutting off future communication with the server and eliminating the RCE vector.
The execution of this operation required extreme technical precision. During initial deployment and testing phases, the researchers discovered that mainstream commercial antivirus products frequently flagged their remediation payload as suspicious or malicious because the script deliberately terminated and disabled a persistent background service. To ensure that endpoint detection and response (EDR) solutions did not erroneously block the life-saving patch, Eye Security iteratively modified the payload to comply with security software heuristics while successfully achieving its remediation goals.
Importantly, the payload was designed with strict privacy boundaries: it collected zero host telemetry, harvested no user data, and deleted no personal files on the host computers. By keeping their actions strictly confined to neutralizing the update loop, the researchers operated within a fully authorized and defensive legal framework.
The results of the campaign were swift and definitive. Following the deployment of the remediation script, Eye Security recorded over 2 million update downloads. By March 1, incoming requests to their update domain had plummeted by 98%, signaling that the vast majority of exposed systems had been successfully immunized against potential exploitation.
Upon the successful conclusion of the remediation phase, Eye Security transitioned ownership of the recovered domains to The Shadowserver Foundation, a respected non-profit security organization dedicated to improving the security of the Internet, ensuring that the infrastructure would remain permanently neutralized and out of malicious hands.
Lingering Risks: Mobile Platforms and Legacy Architecture
Despite the resounding success of the desktop remediation operation, security experts emphasize that the threat landscape surrounding abandoned legacy forks of Popcorn Time has not been entirely eradicated. Users of the software still face significant residual security risks that require manual intervention.
First and foremost, the remediation effort was limited to desktop operating systems. Android users who installed mobile variants of Time4Popcorn remain vulnerable. Because the Android platform architecture requires explicit user interaction to install application updates and manage local packages, researchers were technically unable to deploy a remote remediation payload to mobile devices.
Second, desktop and mobile iterations of Time4Popcorn alike suffer from deep architectural rot. Forensic evaluations revealed that the application relies on an extensively outdated version of the Google Chrome rendering engine originally released in 2014. This ancient engine lacks modern browser sandbox protections and contains numerous publicly known, unpatched zero-day vulnerabilities. If exploited by a creative adversary, these legacy browser flaws could still serve as an entry point for system compromise, entirely independent of the updater mechanism.
Consequently, security professionals and industry analysts have issued a unified recommendation: the only definitive safeguard against CVE-2026-30612 and its associated risks is the immediate and complete removal of the application from all systems. Users are urged to audit their personal and corporate devices to ensure that legacy streaming software remnants are thoroughly purged.
Implications for Enterprise Security and Software Lifecycle Management
The Popcorn Time incident serves as a profound case study in the broader implications of shadow IT, software abandonment, and the complexities of modern digital hygiene. While the primary victims of such vulnerabilities are often individual consumers seeking free media content, the presence of these applications on corporate, government, and military networks highlights a persistent blind spot in enterprise asset management.
Modern organizations invest heavily in perimeter defenses, endpoint detection, and vulnerability management systems to protect against active threats. However, passive, dormant applications left behind by employees—often referred to as lingering shadow IT—frequently escape routine vulnerability scanning if they do not communicate actively with recognized enterprise servers. When an external third party or an abandoned domain changes hands, organizations can find themselves exposed to critical remote code execution flaws through software that IT administrators did not even know was present on the network.
Furthermore, the operation conducted by Eye Security and handed over to The Shadowserver Foundation underscores the growing importance of proactive defensive interventions in cyberspace. As cyber threat actors increasingly weaponize abandoned infrastructure—a tactic known as "domain shadowing" or exploiting dead switches—the security community faces difficult questions regarding active defense. While unauthorized interference with third-party software typically crosses legal and ethical boundaries, interventions executed purely to disarm critical vulnerabilities in abandoned, unmaintainable software demonstrate how cooperative, non-malicious actors can sometimes avert systemic digital disasters.
Ultimately, the Popcorn Time updater crisis has been safely defused, averting what could have been a catastrophic botnet deployment affecting millions of systems globally. Yet, the episode remains a stark reminder that in an interconnected digital ecosystem, forgotten software is never truly dead—it simply waits quietly until someone else knocks on the door.

