
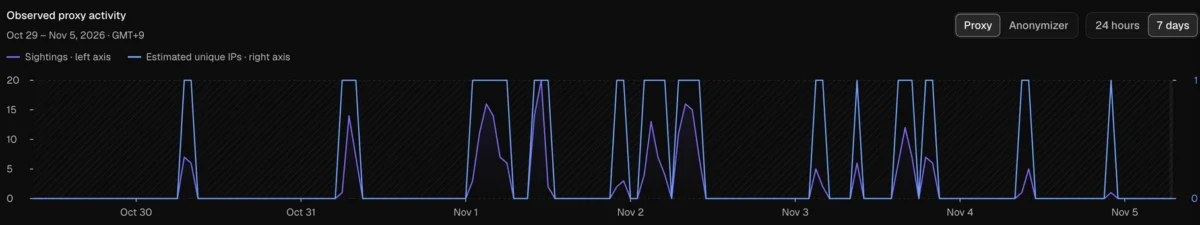
In a shocking oversight that has laid bare the vulnerabilities of government cybersecurity, security experts have revealed that multiple devices within the White House are actively participating in commercial residential proxy networks. This alarming configuration inadvertently allows unknown global users to rent the Internet Protocol (IP) addresses assigned to the Executive Office of the President, routing external traffic directly through the highest levels of the United States government.
The security firms Layer3 Intel and Synthient independently discovered the breach, which persisted across multiple weeks in late 2025 and early 2026. The compromise stems not from a sophisticated nation-state cyberattack on government infrastructure, but rather from the everyday digital habits of individuals operating within secure facilities—specifically, the installation of seemingly innocuous mobile or desktop applications containing hidden monetization software development kits (SDKs).
Among the residential proxy services identified as operating within the White House’s dedicated network block (AS2650) is Infatica, a proxy provider founded by Vladimir Fomenko. Fomenko is a Russian national whose previous web hosting company, King Servers, was famously identified by US intelligence as the launchpad for cyberattacks targeting state election databases in Arizona and Illinois in 2016. The revelation that proxy nodes linked to actors with historical ties to Russian state-sponsored operations have managed to bridge the network perimeter of the Executive Office of the President has ignited severe concern among cybersecurity professionals.
Chronology and Detection of the Breach
The discovery of the proxy nodes was not the result of targeted reconnaissance or invasive government probing, but rather the accidental byproduct of routine global Internet scanning.
Between October 5 and November 3, cybersecurity researchers at Layer3 Intel noticed unusual and persistent telemetry beaconing out from AS2650, the Autonomous System Number officially reserved for the Executive Office of the President. Upon closer examination of the traffic patterns, analysts discovered that the network’s IP addresses were functioning as residential proxy exit nodes—meaning external users could pay a nominal fee to route their web traffic through the White House’s network, masking their true geographic locations and identities.
According to Layer3 Intel’s telemetry, proxy exit activity originating from the White House network was recorded 236 times during the observation window. The activity was highly systematic, appearing on 26 out of 30 days, with the vast majority of connections concentrated during evening and nighttime hours—specifically between 5:00 p.m. and midnight Eastern Time. Six distinct IP addresses within the government allocation block were found to be actively participating in these proxy pools.
Further investigation by the threat intelligence platform Synthient corroborated these findings. Synthient founder Ben Brundage tracked the anomalous traffic back to multiple Windows 11 installations running Infatica services. The software utilized by these machines transformed the official government-issued devices into commercial relay stations, effectively monetizing the White House’s high-trust network bandwidth for external buyers.
The Scale of the Problem: Beyond a Single Provider
While Infatica’s presence on the White House network is particularly concerning due to its founder’s background, security analysts emphasize that the scope of the issue is far broader than any single company.
Layer3 Intel reported that its probes identified a staggering 28 separate residential proxy services capable of routing traffic through the Executive Office of the President’s network. This indicates that multiple staffers or devices brought into the workplace have downloaded various consumer applications embedded with proxy-sharing SDKs.
"This is public access," the Layer3 Intel research team wrote in a public disclosure. "Anybody can obtain it by signing up to a public residential proxy service, paying a few dollars and sending requests through it. We did not selectively target this network or try to make our probes exit from it. We caught this by chance, simply by requesting global rotating access through these services."
Residential proxy networks operate on a simple yet dangerous premise: companies recruit everyday users to share their residential or corporate internet connections by offering "free" VPNs, ad-blockers, weather applications, or browser extensions. In exchange for utilizing these applications, the user’s device becomes a node in a massive peer-to-peer proxy network. Third-party customers—ranging from digital marketers to cybercriminals—then pay the proxy provider to route their web traffic through these endpoints, making their activities appear as though they originate from legitimate home or corporate networks rather than data centers.
The Underground Market and Criminal Exploitation
The commercial market for residential proxies has exploded in recent years, driven by a high demand for IP rotation to bypass anti-bot defenses, scrape web data for artificial intelligence training models, and perpetrate ad fraud. However, security researchers have repeatedly warned that the underlying architecture of these networks represents a massive, unmitigated security risk.
Because many residential proxy providers enforce lax Know Your Customer (KYC) protocols, malicious actors can easily purchase access to high-value networks for pennies.
"Some of these resellers sell bandwidth for as low as 60 cents a gigabyte," Ben Brundage, founder of Synthient, explained to security journalists. "That means for less than a dollar, you can gain access into some of the most confidential and trusted networks."
The dangers associated with residential proxies extend far beyond passive traffic routing. In late 2025 and early 2026, security analysts uncovered widespread campaigns by cybercriminals actively weaponizing residential proxy nodes. By exploiting software vulnerabilities inherent in proxy client applications, malicious actors were able to pivot from the proxy node into the local networks of infected devices—a tactic famously demonstrated by the Kimwolf botnet. This allowed unauthorized third parties to scan local corporate or government subnets, probe for internal vulnerabilities, and potentially deploy secondary malware payloads.
When these compromised devices are brought inside high-security environments like the White House, the threat profile escalates dramatically. An open proxy node inside a government facility does not merely risk the integrity of a single workstation; it creates a trusted bridgehead inside a heavily defended perimeter, potentially exposing internal routing tables, unencrypted local communications, and sensitive organizational infrastructure to external bad actors.
Institutional Blind Spots Across Government and Industry
The revelation that White House networks are harboring residential proxy nodes highlights a pervasive blind spot in modern enterprise and government cybersecurity: the inability to fully monitor and control employee endpoint behavior.
Government and corporate networks are traditionally hardened against external intrusions through rigorous firewalls, intrusion detection systems, and strict perimeter defenses. However, these security models often struggle to account for insider threats born of convenience and ignorance. Employees working long hours in high-pressure environments frequently install consumer-grade utilities, browser extensions, or mobile applications onto their work-issued or personal devices without realizing that these programs contain embedded monetization kits that trade away their network integrity.
The scope of this vulnerability across the broader institutional landscape is staggering. Data compiled by the proxy tracking service Spur during a January 2026 industry webinar revealed that residential proxy nodes were actively beaconing out from nearly 300 government-owned and operated networks. Furthermore, Spur identified proxy activity within 318 utility companies, 166 healthcare organizations and hospitals, and 141 financial institutions.
Reinforcing these findings, a comprehensive study published earlier this year by the security firm Infoblox reported that a startling 65 percent of its enterprise customer base had internal devices querying one or more residential proxy-related domains. These statistics demonstrate that endpoint-based proxy leakage is an endemic crisis affecting virtually every sector of critical infrastructure, defense, and commerce.
Response and Future Implications
As of the publication of this report, the White House has not issued an official response or public comment regarding the security findings released by Layer3 Intel and Synthient. The lack of an immediate statement underscores the delicate nature of disclosing vulnerabilities tied directly to the Executive Office of the President, where federal IT and cybersecurity teams are now likely conducting urgent internal audits to identify and isolate the compromised endpoints.
The incident is expected to accelerate regulatory and technical scrutiny of the residential proxy industry. Cybersecurity advocates have long called for stricter oversight, mandatory KYC enforcement, and harsher legal penalties for proxy operators whose infrastructure facilitates unauthorized access to critical government and corporate networks. Furthermore, enterprise security vendors are increasingly updating their signature databases and Endpoint Detection and Response (EDR) tools to aggressively flag and block software development kits associated with proxy monetization.
For government agencies and defense contractors, the White House breach serves as a stark wake-up call. It demonstrates that advanced firewalls and multi-factor authentication are insufficient if an employee can inadvertently punch a hole in the network perimeter simply by installing a free browser extension or mobile utility. Moving forward, robust endpoint hygiene, strict application whitelisting, and continuous network telemetry monitoring will be vital to ensuring that the most trusted networks in the world are not unknowingly rented out to the highest bidder on the dark web.

