
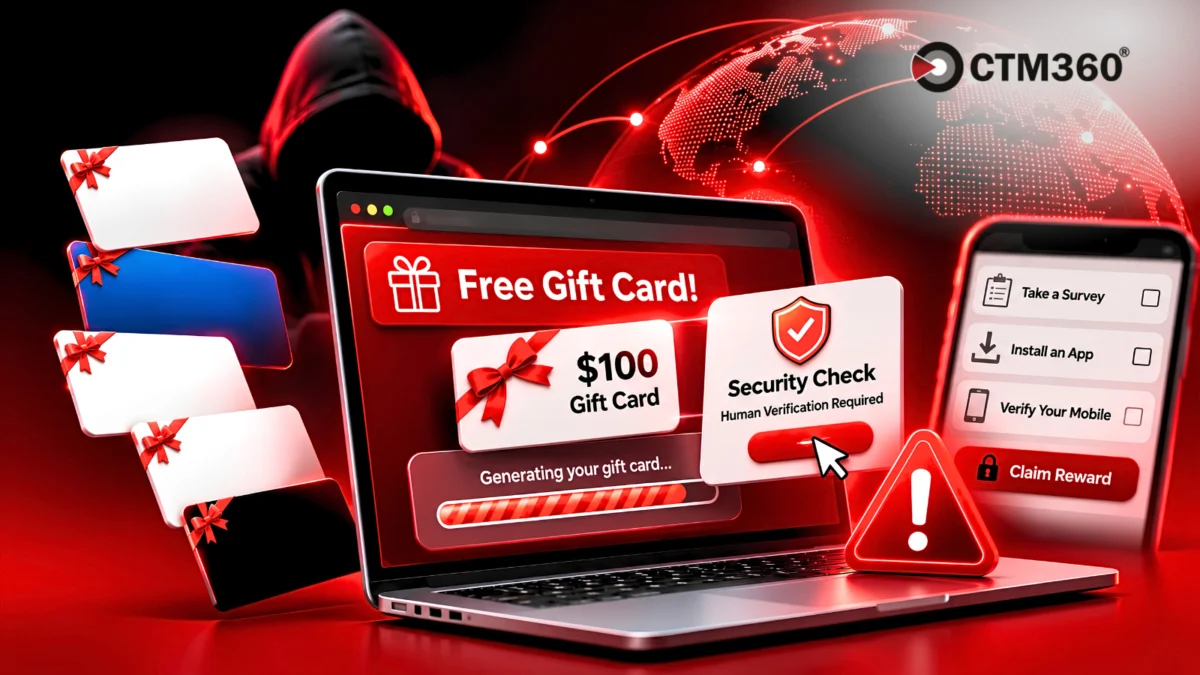
The digital landscape is currently witnessing an unprecedented global surge in sophisticated fraudulent reward portals and deceptive gift card giveaways. Cyber threat intelligence analysts have tracked a massive influx of campaigns that lure unsuspecting internet users with the promise of high-value complimentary vouchers from household-name brands. Behind polished visual interfaces, fake progress bars, and fabricated endorsements, these operations are designed not to deliver rewards, but to ensnare victims in endless verification loops, harvest personal data, and enroll them in unauthorized, recurring mobile subscriptions.
Recent telemetry and security reports published by digital risk protection firms, including comprehensive studies by CTM360, highlight a sprawling cybercriminal infrastructure. This ecosystem relies on modular frameworks, allowing threat actors to rapidly adapt their campaigns, pivot across popular consumer brands, and exploit public trust on a massive, industrialized scale.
The Anatomy of the Trap: Hook, Line, and Sinker
The lifecycle of these fraudulent gift card campaigns has been meticulously mapped by security researchers, revealing a calculated psychological progression designed to shepherd victims from initial curiosity to blind urgency. The attack vector typically begins on social media feeds, messaging platforms, or via malicious display advertisements. These promotional units frequently leverage unauthorized celebrity endorsements, deepfakes, or high-profile public figures holding popular retail items to instantly capture attention.
The core pitch is disarmingly simple: click the advertisement, claim a free gift card worth hundreds of dollars from a premier global brand, and complete a brief "human verification" check to unlock the funds.
Once a user interacts with the ad, they are seamlessly redirected to a meticulously crafted rogue landing page. To establish immediate credibility, these malicious portals incorporate professional graphic design, live activity tickers showing recent winners, and responsive user-interface elements. Victims are invited to select their preferred retailer and gift card denomination—often ranging from $100 to $1,000.
Upon selection, the website initiates a scripted, highly convincing visual animation. A fake progress bar ticks upward accompanied by status logs indicating backend database connections, security handshakes, and code generation. Eventually, the portal displays a partially masked voucher code, such as XXXX-XXXX-7F3A-XXXX. This psychological trigger convinces the victim that the reward is genuine and merely seconds away from being fully revealed.
However, before the final digits are unlocked, the user hits the ultimate barrier: a deceptive "Security Check" or "Human Verification" gate.
The Infinite Verification Loop and "Trap 10" Monetization
Far from protecting the platform against automated bots, the "human verification" stage serves as the primary revenue-generation engine for the cybercriminals. Security analysts refer to this phase as an entry point into predatory affiliate monetization loops—frequently categorized in threat intelligence frameworks as "Trap 10."
Instead of granting access to the promised gift card, the verification process diverts victims through a convoluted series of third-party offers, surveys, and app installation prompts. Users are systematically pushed to:
- Download unverified, potentially adware-laden mobile applications from official or third-party app stores.
- Complete lengthy marketing questionnaires that harvest Personally Identifiable Information (PII) including home addresses, email addresses, and phone numbers.
- Submit mobile phone numbers to authorize premium-rate SMS billing services or enroll in recurring subscription models.
If a victim diligently completes these assigned tasks, they find that the reward remains permanently out of reach. The portal either reports the step as incomplete due to a "session timeout" or immediately redirects them to yet another monetization offer. Across extensive testing environments evaluated by cybersecurity researchers, a zero-percent delivery rate for actual gift cards has been recorded. The carrot is perpetually pulled away just as the user attempts to bite.
Industrial-Scale Brand Impersonation and Modular Infrastructure
The scale of this threat is staggering. Analysts have cataloged over 1,000 distinct incidents linked to this specific recurring campaign framework within a relatively compressed observation window. Threat actors heavily exploit public familiarity with established global entities, routinely impersonating major consumer platforms, technology giants, and fast-fashion retailers. Among the most frequently abused brand identities are retail behemoths like Amazon and Walmart, entertainment ecosystems like PlayStation, and consumer lifestyle brands such as Sephora and SHEIN.
What makes this campaign particularly resilient against traditional law enforcement and domain-takedown efforts is its underlying architecture. The threat actors utilize a modular scam engine. Rather than hardcoding a single brand or landing page, the infrastructure separates the front-end lure from the back-end redirection logic. This means operators can swap out the impersonated brand, change the celebrity endorsement video, and migrate to entirely new domain names within minutes, all without altering the core affiliate monetization mechanism.
From a technical standpoint, these operations function primarily as volume-driven affiliate marketing schemes gone rogue. When a victim is redirected from the fake reward portal to a third-party offer, the URL passes specific tracking parameters, such as unique offer identifiers (offer_id) and affiliate tags (aff_id). This technical hand-off ensures that every time a victim falls for a trick—such as entering their phone number for a recurring mobile subscription—the primary threat actor receives an immediate financial commission from the affiliate network hosting the downstream offer.
Financial, Operational, and Reputational Fallout
The consequences of these widespread fraudulent campaigns extend far beyond minor personal annoyance, impacting both everyday consumers and multinational corporations alike.
For the individual consumer, the fallout can be severe. Victims frequently experience:
- Financial Loss: Unwelcome charges appearing on mobile phone bills due to recurring SMS subscription traps.
- Privacy Invasion: Extensive harvesting and underground trading of personal data, leading to an immediate surge in targeted phishing emails, spam phone calls, and secondary scams.
- Device Compromise: Potential installation of grayware or aggressive adware through forced application downloads during the verification loops.
For the targeted brands, the implications center on severe reputational abuse and customer erosion. Major retailers invest billions of dollars in building consumer trust, brand equity, and secure digital shopping environments. When cybercriminals weaponize these brand names to deceive the public, consumer confidence is subtly eroded. Shoppers may grow wary of legitimate promotional emails, official seasonal giveaways, and authorized loyalty programs, mistakenly believing that major brands are associated with predatory marketing practices.
Industry Response and Digital Risk Protection Strategies
As fraudulent reward portals continue to proliferate across social media networks and ad-serving platforms, cybersecurity experts emphasize that traditional perimeter defenses are insufficient. Because these scams rely heavily on psychological manipulation, social engineering, and rapid domain rotation, mitigation requires a proactive, multi-layered approach to Digital Risk Protection (DRP).
Security organizations advise enterprises to continuously monitor their external digital landscape. By deploying automated threat intelligence tools, brands can identify unauthorized domain registrations, rogue social media advertisements, and phishing portals utilizing their intellectual property before those campaigns reach critical mass. Early detection allows brand protection teams to issue rapid takedown notices, work with domain registrars to suspend malicious infrastructure, and alert consumer bases to active impersonation campaigns.
Concurrently, consumer advocacy groups and cybersecurity educators continue to urge internet users to adhere to fundamental digital hygiene principles. Key defensive practices include:
- Exercising extreme skepticism toward unsolicited social media ads promising high-value gift cards, cash prizes, or luxury items for minimal effort.
- Verifying promotional offers directly through a brand’s official website or verified mobile application rather than clicking links embedded in social media posts or unsolicited messages.
- Recognizing that legitimate organizations rarely require users to complete endless third-party offers, install random applications, or pay hidden fees to claim a won or awarded prize.
- Monitoring mobile phone statements and credit reports regularly to catch unauthorized subscription charges or data leaks early.
As threat actors continue to refine their monetization models and exploit consumer trust in established brands, the fight against fraudulent reward portals remains an ongoing challenge for cybersecurity professionals, platform moderators, and legal authorities worldwide. Only through continuous technological vigilance, rapid cross-industry collaboration, and heightened public awareness can the digital ecosystem hope to dismantle these industrial-scale deceptive networks.

