
Federal law enforcement authorities have taken a significant step in one of the most high-profile cybercrime investigations of the decade, arresting a prominent Canadian cybersecurity executive in connection with the notorious ShinyHunters hacking syndicate. The federal probe escalated dramatically after the sophisticated cybercriminal organization successfully breached Federal Bureau of Investigation (FBI) digital infrastructure, compromising sensitive personnel records detailing thousands of agents, unit specializations, and confidential medical histories.
The arrest, which took place in Pennsylvania, highlights the increasingly blurred lines between corporate incident response firms, ransomware negotiation specialists, and the shadowy underworld of digital extortion. As federal prosecutors in the Eastern District of Texas take charge of the sprawling multi-jurisdictional case, the cybersecurity industry finds itself reckoning with profound questions regarding ethics, accountability, and the legal boundaries of managing extortion demands.
The Arrest in Pennsylvania and Court Proceedings
Federal Bureau of Investigation agents apprehended Edward Dubrovsky, a 54-year-old Canadian cybersecurity professional and author, during a visit to Pennsylvania where he was scheduled to participate in an industry gathering. According to federal court records indexed on legal databases, Dubrovsky was taken into custody on October 8, 2026, facing formal charges of conspiracy to threaten to impair the confidentiality of information with the intent to extort money, alongside interference with commerce by threats.
While initial court filings in Pennsylvania recorded the defendant’s last name slightly misspelled as Dobrovsky, subsequent documentation revealed the rapid acceleration of the judicial process. On October 9, federal authorities transferred jurisdiction of the case to the U.S. District Court for the Eastern District of Texas, which sources close to the investigation confirm has become the central command hub for the comprehensive federal probe into ShinyHunters.
At the time of his detention, Dubrovsky was held at a federal facility in Philadelphia operated by the U.S. Bureau of Prisons. Public court records indicate that he had not yet retained private counsel or been assigned a public defender immediately following his initial appearance before a magistrate judge. Representatives for the federal government and the FBI have largely declined to comment on active aspects of the indictment, citing the ongoing nature of the conspiracy investigation.

Chronology of an Escalating Cyber Crisis
The apprehension of the Canadian cybersecurity executive represents the culmination of a frantic, months-long international manhunt and digital counter-offensive launched in response to a series of devastating breaches orchestrated by ShinyHunters.
The timeline of key events leading up to the October arrests illustrates the rapid escalation of the threat landscape:
- Late 2025: ShinyHunters intensifies corporate targeting, employing sophisticated phishing campaigns and stolen credential harvesting to breach software-as-a-service providers and corporate environments. The group targets a navigation and digital aviation unit recently divested by aerospace giant Boeing.
- September 2026: Dutch National Police execute search and seizure operations, arresting reformed cybercriminal Pepijn van der Stap in the Netherlands. Investigators begin analyzing extensive digital hardware seized during the raid for operational ties to ShinyHunters.
- October 5–7, 2026: The annual Cyber Risk Summit takes place at the Loews Philadelphia Hotel. Cybersecurity executives, insurance providers, and advisory firms gather for panels on ransomware negotiation strategies. Among the attendees and primary corporate sponsors is CyberSteward, a firm associated with Edward Dubrovsky.
- October 8, 2026: Federal agents arrest Dubrovsky in Pennsylvania on cyber extortion and conspiracy charges.
- October 9, 2026: The federal case is officially transferred to the Eastern District of Texas. Media outlets, including The New York Times, report on the arrest of a Canadian national linked to the ShinyHunters inquiry. FBI Director Kash Patel issues a public statement acknowledging enforcement actions without explicitly naming the suspect.
- October 10, 2026: Cypfer, a Canadian security firm, issues a public clarification noting that Dubrovsky served as a managing director prior to his resignation in December 2025, disputing LinkedIn profile descriptions designating him as a company co-founder.
Industry Connections and Corporate Background
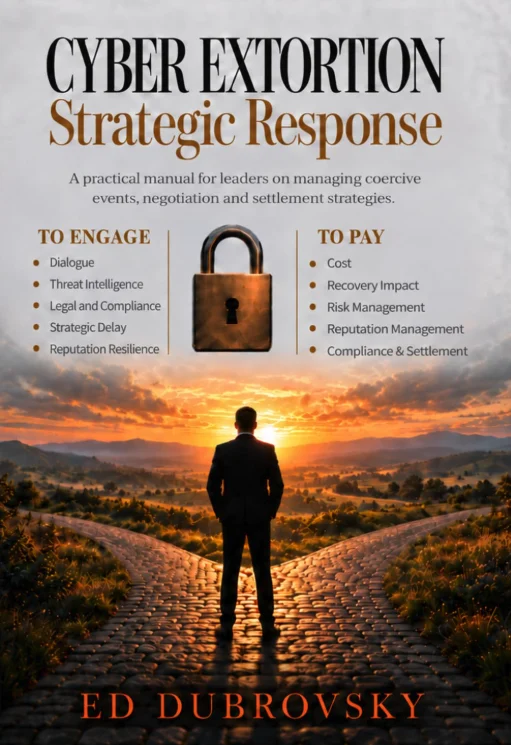
The suspect’s professional footprint within the cybersecurity sector has drawn intense scrutiny from investigators and industry peers alike. Prior to his arrest, Dubrovsky maintained a prominent profile as an authority on ransomware mitigation, authoring a 252-page textbook titled Cyber Extortion Strategic Response. The publication purports to guide organizations through the complex decision-making processes required during active extortion events, emphasizing the delicate distinction between establishing communication with malicious actors and authorizing illegal ransom payments.
Public records indicate that Dubrovsky previously held a leadership role at Cypfer, a prominent Canadian security vendor that served as a top-tier sponsor for the Philadelphia cyber insurance conference where he was detained. Cypfer representatives subsequently clarified his corporate timeline, noting that he departed the organization late last year before affiliating with CyberSteward, another security advisory firm that sponsored the same risk summit.
The intersection of specialized cyber firms and criminal enterprises has long been a subject of quiet concern among law enforcement agencies. Companies specializing in ransomware negotiation frequently operate in regulatory gray areas, acting as intermediaries between victimized corporations and extortion syndicates. While legitimate advisory firms assist organizations in minimizing operational disruption and evaluating legal liabilities, investigators are increasingly examining whether certain actors crossed ethical and legal boundaries by facilitating illicit transactions or maintaining undisclosed ties to threat groups.
The ShinyHunters Threat Matrix and FBI Data Breach
ShinyHunters has cemented its reputation as one of the most destructive and agile cyber extortion rings operating globally. The collective typically gains initial access through targeted credential theft and phishing attacks directed at cloud environments and corporate software-as-a-service platforms. Once inside, the group exfiltrates vast repositories of proprietary and confidential data, threatening public leaks unless exorbitant financial demands are satisfied. According to internal estimates cited by federal law enforcement, the syndicate has successfully extorted in excess of $70 million from corporate victims throughout the current calendar year.

The group’s audacity reached an unprecedented peak when operatives turned their sights on the FBI itself. Following the arrest of Dutch national Pepijn van der Stap in September, leadership of the hacking collective allegedly fell to an operative known online as "Rey." In an aggressive display of defiance, the faction taunted federal investigators by publishing sensitive data stolen from an FBI online recruitment portal. The compromised cache included highly confidential records detailing individual agent unit assignments, specialized operational capacities, and deeply private medical and psychiatric evaluations.
International journalism outlets subsequently identified "Rey" as a teenager named Saif Al-din Khader. Investigative reporting revealed that Khader was detained by authorities after the group attempted an extortion campaign against a digital aviation and navigation entity spun off from Boeing. Following his apprehension, Khader reportedly began cooperating with federal investigators, providing vital intelligence that accelerated the dragnet encompassing international associates and advisory intermediaries.
Broader Implications for the Cybersecurity Industry
The arrest of a high-ranking figures within the ransomware negotiation ecosystem signals a profound paradigm shift in how law enforcement approaches the mechanics of cyber extortion. For years, the prevailing commercial model relied heavily on discreet dialogue, risk mitigation, and, in many cases, the covert transfer of cryptocurrency to silence criminals.
Legal experts and industry analysts suggest that the ongoing federal inquiry could permanently alter the operational framework of incident response firms. By scrutinizing the financial flows, communication channels, and advisory practices of third-party negotiators, the Department of Justice is signaling a zero-tolerance policy toward any individual or entity suspected of aiding, abetting, or materially benefiting from digital extortion schemes.
As the Eastern District of Texas prepares to unseal further indictments and advance proceedings against additional targets, the fallout from the ShinyHunters investigation will likely resonate across boardrooms, insurance boardrooms, and specialized security consultancies worldwide. The case underscores a stark reality for the digital age: as cybercrime syndicates grow increasingly brazen, the protective barriers separating corporate defenders from criminal actors are coming under unprecedented judicial scrutiny.

