
The notorious ShinyHunters extortion syndicate has launched a renewed wave of widespread cyberattacks targeting vulnerable Oracle PeopleSoft servers worldwide. By employing a sophisticated URL-encoding trick, the threat actors are successfully bypassing web application firewall (WAF) rules that organizations previously relied upon as a temporary defense against the critical CVE-2026-35273 security flaw.
According to threat intelligence reports released by Google’s Mandiant and Threat Intelligence Group (GTIG), the bypass technique allows the group—tracked in telemetry as UNC6240—to target enterprises, academic institutions, and government agencies that applied network-level blocks rather than patching the underlying software vulnerability. This fresh campaign has resulted in the deployment of persistent web shells, data exfiltration toolkits, and sophisticated backdoors across multiple critical infrastructure sectors globally.
Evolution of the Campaign and the CVE-2026-35273 Zero-Day
The crisis began unfolding in mid-June when security researchers uncovered an active zero-day exploit chain targeting Oracle PeopleSoft architecture. On June 10, initial reports revealed that the ShinyHunters collective was actively exploiting unpatched servers, breaching roughly 100 high-profile organizations to siphon sensitive corporate and institutional data.
Recognizing the severity of the threat, Oracle moved rapidly, issuing an emergency security advisory and patch on June 11 to fix the unauthenticated remote code execution (RCE) vulnerability, which was formally cataloged as CVE-2026-35273. Simultaneously, Google’s threat intelligence division linked the exploitation activity directly to the UNC6240 actor cluster, noting a heavy concentration of attacks directed against the education sector.
Because immediate patch deployment can be operationally disruptive for large enterprises running legacy enterprise resource planning (ERP) systems, security vendors like Mandiant offered interim workarounds. System administrators who could not instantly install Oracle’s official updates or disable the vulnerable Environment Management Hub were advised to configure their perimeter defenses—specifically web application firewalls and reverse proxies—to block all external web traffic directed at the sensitive /PSEMHUB/* endpoint.
While this defensive posture provided a temporary safety net, the respite was short-lived. Threat actors quickly analyzed how perimeter devices processed HTTP requests, engineering a technique to slip past defensive filters without altering the fundamental attack payload.
Anatomy of the WAF Bypass Technique
The core mechanism of the new ShinyHunters exploit involves exploiting discrepancies in how perimeter security tools and backend application servers handle URI normalization and percent-encoding.
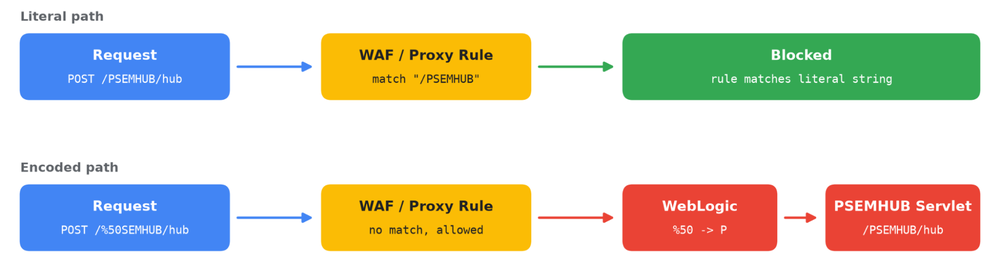
Standard WAF configurations designed to mitigate CVE-2026-35273 typically look for literal character strings matching /PSEMHUB/ in incoming HTTP requests. If a request contains this exact string, the WAF blocks it. However, Mandiant’s latest findings show that ShinyHunters has altered their operational scripts to send percent-encoded variants of the path.
Instead of sending traditional plaintext requests to /PSEMHUB/, the attackers are now routing their probes through strings such as /%50SEMHUB/, where the hexadecimal sequence %50 represents the percent-encoded version of the capital letter "P".
Many commercial WAFs and reverse proxy solutions evaluate the raw, literal request path before applying decoding logic, causing their rule sets to miss the encoded sequence entirely and permit the traffic through. Conversely, Oracle WebLogic—the underlying application server platform—subsequently decodes the percent-encoded characters during request processing, translating /%50 back into the literal "P" and correctly routing the payload to the vulnerable endpoint.
"This allows the threat actor to reach the endpoint on systems whose operators may have believed their WAF rules had mitigated the exposure," Mandiant explained in a detailed technical advisory. Furthermore, Google researchers warn that the %50 trick is merely one variation; the threat actors can easily rotate through mixed-case lettering, alternative percent-encoding combinations, or nested encoding schemes to continually evade static WAF signatures.
Global Impact Across Sectors and Deployment of Toolkits
The renewed wave of intrusions has successfully compromised dozens of systems across a diverse array of industries. Impacted sectors now span higher education, high-technology enterprises, IT services, healthcare providers, agricultural organizations, transportation networks, and government entities worldwide.
Forensic analysis of the attack lifecycle indicates a calculated, multi-stage methodology. Before launching a destructive or data-theft phase, ShinyHunters typically performs stealthy reconnaissance. The actors transmit between five and 15 HTTP POST requests to /%50SEMHUB/hub containing serialized Java objects. On vulnerable machines, these probe requests elicit specific responses detailing the host operating system without generating disk artifacts or service crashes. This allows the attackers to map out exploitable targets quietly.
Once a target environment is verified, the hackers leverage the vulnerability to execute arbitrary commands directly in system memory or drop persistent JSP web shells. Investigators have identified three primary web shells utilized in the campaign:
x.jsp: Deployed primarily for remote command execution.u.jspandu2.jsp: Utilized for uploading larger binaries and secondary operational payloads.
On compromised Microsoft Windows servers, the actors leverage these shells to install an executable named Ple64.exe. Although disguised to masquerade as a legitimate, digitally signed Light Alloy media player installer, the binary actually installs a sophisticated backdoor tracked by Google as SIDEEYE. The SIDEEYE malware functions as a multi-purpose Swiss Army knife, granting operators capabilities for credential theft, comprehensive process and file management, interactive reverse shell generation, and encrypted reverse proxy operations.
To establish persistent footholds and facilitate lateral movement across internal corporate networks, the syndicate also deploys the open-source Neo-reGeorg tunneling toolkit through files named tunnel.jsp and tunnel.jspx. This utility enables attackers to tunnel standard SOCKS5 proxy traffic directly over normal, encrypted HTTP and HTTPS connections, effectively blending malicious traffic with legitimate web communications. On compromised Linux infrastructure, Mandiant observed the actors installing legitimate MeshAgent remote management software to maintain persistent, out-of-band access.
The FBI Data Breach Claims and Escalated Scrutiny
The resurgence of the PeopleSoft exploitation campaign follows a high-profile escalation in late September, when ShinyHunters publicly claimed responsibility for breaching United States Federal Bureau of Investigation (FBI) systems. At the time, the extortion group asserted that they had leveraged a novel, previously undisclosed Oracle PeopleSoft zero-day vulnerability to compromise the FBI Jobs platform (FBIjobs.gov).
According to statements provided directly by the threat group to security journalists, the alleged breach allowed the actors to pivot laterally from the application layer into the bureau’s internal AWS GovCloud infrastructure. The syndicate claimed to have successfully exfiltrated between two and three terabytes of sensitive data containing personal and professional records belonging to current and former FBI personnel, employment applicants, and various internal administrative directories.
While independent verification of the claimed data volume and lateral movement remained difficult to establish at the time, federal authorities moved quickly to contain the situation. The FBI formally confirmed that it was actively investigating reports of unauthorized digital activity impacting the recruitment portal, though officials refrained from verifying specific claims regarding data theft or internal network infiltration.
In subsequent communications, members of ShinyHunters confirmed that they utilized the exact same URL-encoding WAF bypass technique against the FBI Jobs portal, while continuing to allege that they also deployed separate, undocumented vulnerabilities residing within the same PSEMHUB component architecture.
Industry Recommendations and Defense-in-Depth Analysis
The persistence of the ShinyHunters syndicate highlights a fundamental cybersecurity axiom: perimeter defenses such as web application firewalls and virtual patching mechanisms are never a permanent substitute for proper software patching. While WAF rules can buy critical time during the initial emergency response phase, sophisticated threat actors routinely adapt their tooling to exploit normalization discrepancies and encoding variations.
Security analysts and incident responders urge organizations operating Oracle PeopleSoft environments to abandon temporary network filters and immediately implement the following remediation actions:
- Apply Official Patches: Ensure that all Oracle security updates addressing CVE-2026-35273 are fully installed across all production and staging environments without delay.
- Comprehensive Log Review: System administrators should conduct forensic audits of historical and current Oracle WebLogic access logs. Queries should specifically search for incoming requests targeting
/PSEMHUB/alongside various encoded variants, including/%50SEMHUB/, mixed-case strings, and alternative URI-encoded sequences, to identify historical compromise or ongoing reconnaissance. - Endpoint Integrity Audits: Organizations must inspect application directories for unauthorized JSP files (
x.jsp,u.jsp,tunnel.jsp, etc.), unusual executable binaries in system directories, and unexpected outbound network connections indicative of reverse shells or tunneling utility activity. - Credential Rotation: Given the deployment of credential-stealing backdoors like SIDEEYE, any systems where exposure is suspected should undergo immediate credential resets, session invalidation, and a thorough review of privileged account access logs.
As cybercriminal groups continue to weaponize application-layer normalization flaws to bypass modern perimeter defenses, the latest campaign serves as a stark reminder of the necessity for rigorous asset discovery, rapid patch management, and comprehensive endpoint visibility in safeguarding enterprise infrastructure.

