The notorious cybercrime and extortion syndicate known as ShinyHunters has launched a renewed wave of widespread cyberattacks targeting enterprise infrastructure worldwide. By employing a sophisticated URL-encoding evasion technique, the threat group has successfully circumvented web application firewall (WAF) rules designed to mitigate the critical Oracle PeopleSoft remote code execution vulnerability cataloged as CVE-2026-35273. This development has alarmed cybersecurity researchers and exposed significant blind spots in perimeter defense strategies, particularly for organizations that relied on network-level filtering rather than applying official vendor patches.
Security intelligence provided by Google’s Mandiant and Threat Intelligence Group (GTIG)—which tracks the threat actor under the moniker UNC6240—reveals that the bypass technique tricks standard WAF configurations into ignoring malicious payloads directed at vulnerable servers. The campaign has already resulted in the deployment of persistent web shells, backdoors, and lateral movement toolkits across dozens of high-profile networks globally, spanning critical sectors such as higher education, technology, IT services, healthcare, agriculture, transportation, and government agencies.
The Resurgence of UNC6240 and the Mechanics of the WAF Bypass
The underlying vulnerability, CVE-2026-35273, centers on the Environment Management Hub component of Oracle PeopleSoft, specifically targeting the /PSEMHUB/* endpoint. When exploited, the flaw enables unauthenticated malicious actors to execute arbitrary code with the privileges of the underlying application server, paving the way for full system compromise and data exfiltration.
Following emergency disclosures and the release of patches by Oracle in June 2026, many enterprise administrators implemented temporary workarounds. Because applying emergency patches or disabling core management components can disrupt business continuity, numerous organizations opted to block external web traffic destined for the literal /PSEMHUB/ path using reverse proxies and WAFs.
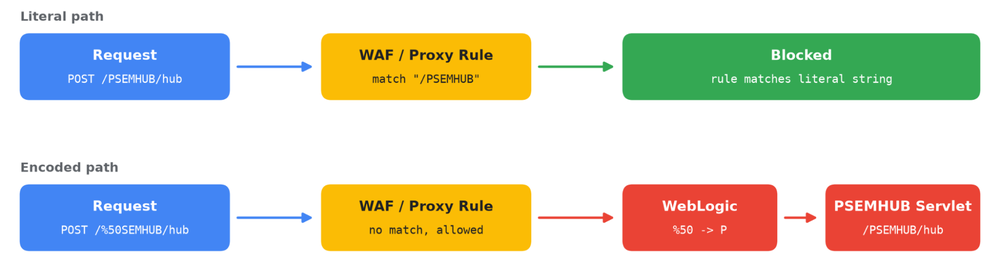
However, ShinyHunters quickly adapted their tactics. Instead of targeting the standard string, the extortion group began leveraging percent-encoded request paths. For example, rather than transmitting traditional requests to /PSEMHUB/, the attackers send requests formatted as /%50SEMHUB/, where the %50 sequence acts as the standard URL-encoded representation of the capital letter "P".
According to Mandiant’s analysis, many standard WAF implementations and reverse proxies evaluate the literal request path prior to normalization or decoding. Because the literal string does not match the blocklist rule for /PSEMHUB/, the security device permits the traffic to pass through. Once the packet reaches Oracle WebLogic, the application automatically decodes the percent-encoded characters, routing the request directly to the vulnerable endpoint and successfully executing the payload. This discrepancy between how edge security tools and backend application servers handle path normalization has left numerous organizations exposed despite believing their perimeter defenses were secure.
Chronology of a Zero-Day Campaign and Escalating Threats
The current exploitation phase represents the latest chapter in an aggressive campaign that first captured global attention in June 2026. The timeline of events highlights the speed at which threat actors operationalize critical vulnerabilities:
- June 10, 2026: Independent security reports emerge indicating that the ShinyHunters extortion group is actively exploiting an unknown PeopleSoft zero-day vulnerability, successfully breaching and stealing sensitive data from approximately 100 enterprise organizations.
- June 11, 2026: Oracle issues an emergency security update addressing the zero-day flaw, formally designating it as CVE-2026-35273. Concurrently, Google confirms that UNC6240 is weaponizing the vulnerability, particularly against institutions in the education sector. Security vendors issue interim mitigation guidance, suggesting WAF blocks on the
/PSEMHUB/*endpoint for organizations unable to immediately patch. - September 2026: ShinyHunters publicly claims responsibility for a high-profile breach of Federal Bureau of Investigation (FBI) systems, asserting they utilized a new PeopleSoft zero-day to compromise the FBI Jobs platform and pivot into internal AWS GovCloud infrastructure, allegedly stealing terabytes of employee data.
- Late 2026 / Early 2027: Google Mandiant detects the rollout of the URL-encoding WAF bypass technique (
/%50SEMHUB/), revealing that ShinyHunters has renewed mass exploitation efforts against systems that relied solely on perimeter blocking.
Anatomy of the Post-Exploitation Phase and Tooling
Once ShinyHunters successfully bypasses perimeter defenses, their operational playbook follows a structured, multi-stage methodology designed for stealth, persistence, and lateral movement. Mandiant researchers have detailed the exact mechanics observed during recent incident response engagements:
Before launching a full-scale assault, the attackers typically send a probing sequence of between five and 15 HTTP POST requests to /%50SEMHUB/hub containing serialized Java objects. On vulnerable hosts, these queries return operating system metadata without generating disk artifacts or causing service crashes. This allows the threat actors to silently inventory target environments and confirm exploitability before deploying heavier tooling.
Upon verifying vulnerability, ShinyHunters triggers the flaw to execute commands in memory or install specialized JSP web shells. Investigators have identified three primary web shells deployed in these attacks: ‘x.jsp’ for general command execution, alongside ‘u.jsp’ and ‘u2.jsp’ intended for the staging and uploading of larger payloads.
On compromised Windows servers, the actors utilize these web shells to drop an executable named ‘Ple64.exe’. This binary cleverly masquerades as a digitally signed installer for the legitimate Light Alloy media player, but its actual payload installs a sophisticated backdoor tracked by Google as SIDEEYE. SIDEEYE provides the threat actors with extensive capabilities, including credential harvesting, file and process management, interactive reverse shells, and built-in reverse proxy functionality.
To facilitate deeper penetration into target networks, ShinyHunters frequently deploys the open-source Neo-reGeorg tunneling toolkit via files named ‘tunnel.jsp’ and ‘tunnel.jspx’. This utility allows attackers to tunnel SOCKS5 proxy traffic over standard HTTP and HTTPS connections, effectively weaponizing the compromised PeopleSoft server as a bridgehead to move laterally across internal enterprise networks. Furthermore, on compromised Linux environments, researchers observed the deployment of legitimate remote management software, such as MeshAgent, to maintain long-term persistent access.
The FBI Incident and Continuing Attribution Claims
The severity of the ShinyHunters syndicate’s campaign was underscored by their controversial claims regarding federal infrastructure. In late September 2026, the group contacted security journalists asserting they had successfully breached FBI systems via a PeopleSoft vulnerability. The attackers claimed access to the FBI Jobs platform enabled them to migrate into internal AWS GovCloud environments, resulting in the alleged exfiltration of two to three terabytes of sensitive records concerning current personnel, applicants, and internal administrative databases.
While independent verification of the stolen data volume and the exact vector remained challenging in the immediate aftermath, the FBI acknowledged it was actively investigating unauthorized cyber activity targeting the FBIjobs.gov portal. Significantly, representatives for ShinyHunters later confirmed to security researchers that they applied their WAF-bypassing methodology during the course of the FBI intrusion, while continuing to assert that they also leveraged secondary, undisclosed flaws within the same PSEMHUB component.
Broader Implications for Enterprise Security and Perimeter Defense
The resurgence of the ShinyHunters extortion campaign through a basic URL-encoding evasion technique serves as a stark reminder of the limitations inherent in perimeter-only security controls. Relying on web application firewalls or reverse proxies to filter malicious traffic based on literal string matching is increasingly proving insufficient against disciplined, adaptable threat actors.
Security analysts emphasize that WAF rules must be regularly audited, normalized, and tested against modern evasion tactics, including various forms of percent-encoding, Unicode manipulation, and case-variation attacks. Furthermore, network defenders must recognize that perimeter blocks are merely temporary stopgaps intended to buy time for proper patch management, rather than permanent architectural solutions.
Actionable Remediation and Defense Recommendations
In response to the ongoing global campaign, Google Mandiant and other leading cybersecurity authorities have urged organizations operating Oracle PeopleSoft environments to undertake immediate remediation steps:
- Prioritize Patch Management: Organizations must immediately apply the official vendor security updates provided by Oracle for CVE-2026-35273, rather than relying on perimeter filtering workarounds.
- Comprehensive Log Analysis: Administrators should review WebLogic access logs for historical and ongoing indicators of compromise, specifically searching for suspicious requests targeting
/PSEMHUB/as well as encoded variants such as/%50SEMHUB/,/%70SEMHUB/, or mixed-case string permutations. - Network Segmentation and Monitoring: Implement strict egress filtering and monitor internal network segments for unauthorized lateral movement tools, unexpected SOCKS tunneling activity (such as Neo-reGeorg), and unauthorized administrative utilities like MeshAgent.
- Endpoint Detection and Response (EDR): Ensure robust EDR telemetry is active across all servers hosting Oracle infrastructure to detect anomalous child processes, unexpected script execution originating from web server directories, and known malicious binaries like the SIDEEYE backdoor (
Ple64.exe).
As threat groups continue to refine their evasion techniques against traditional enterprise defenses, the Oracle PeopleSoft incidents underscore the critical necessity of defense-in-depth strategies, timely vulnerability patching, and continuous behavioral monitoring across both perimeter and internal network assets.