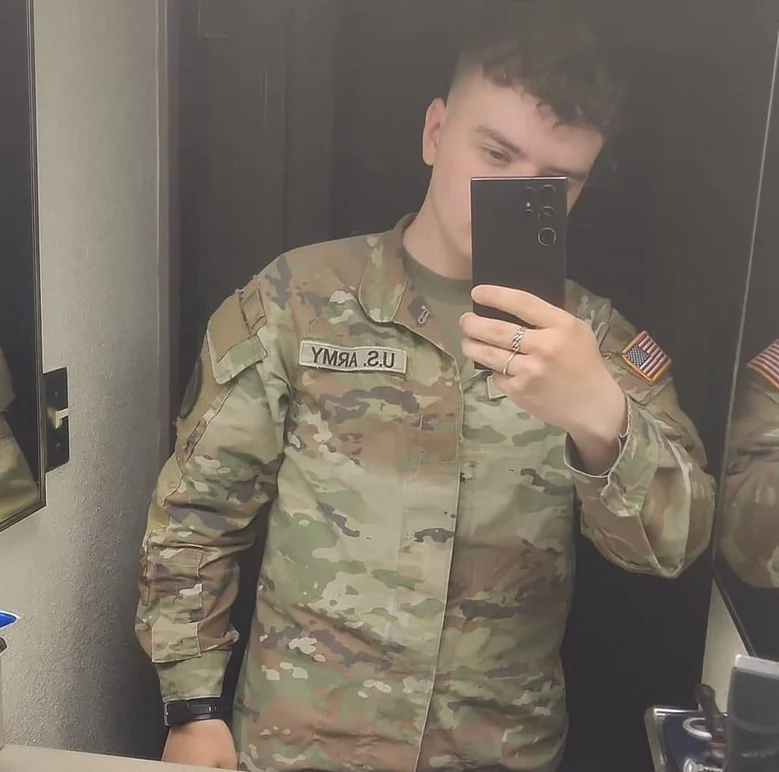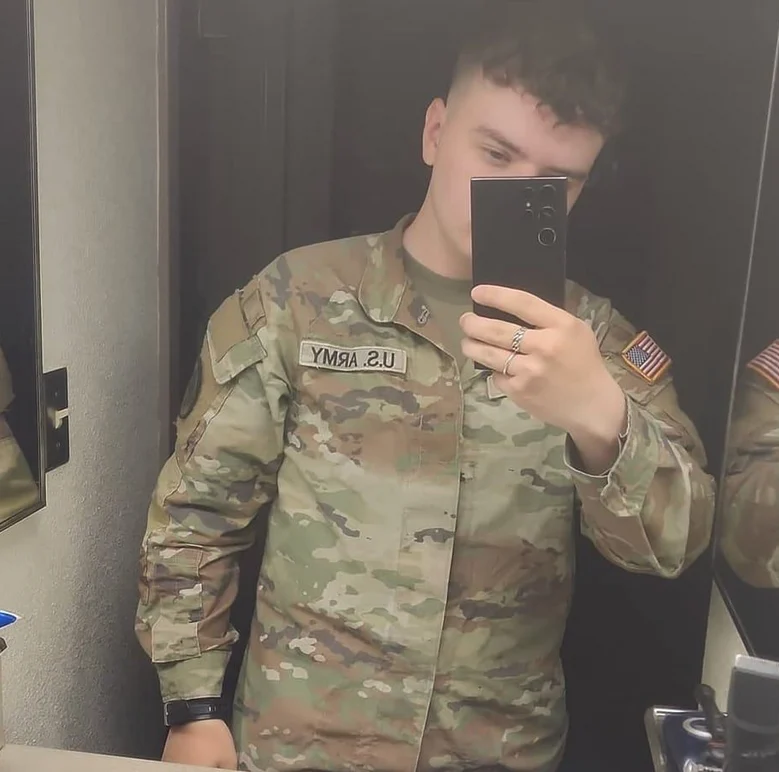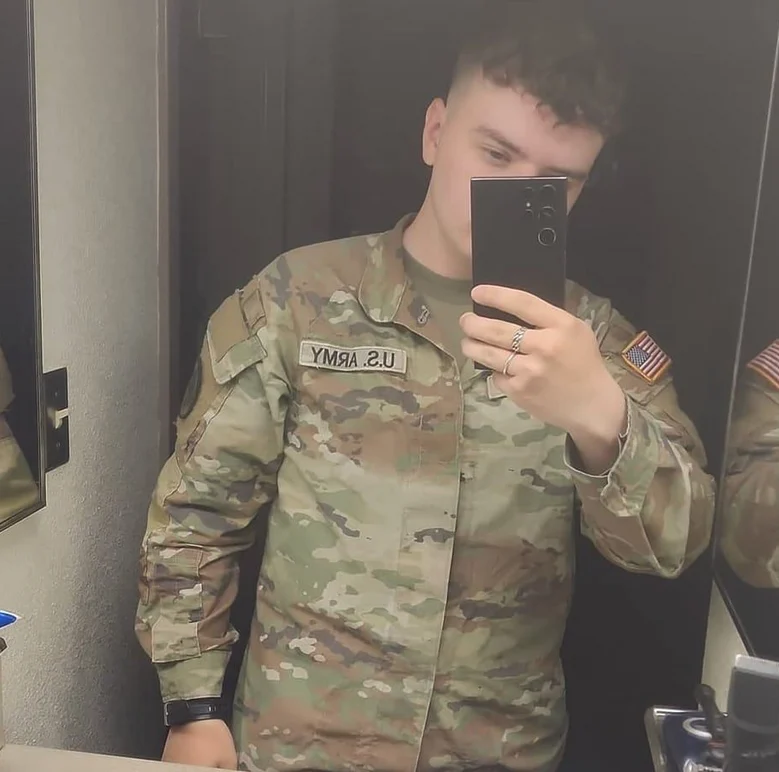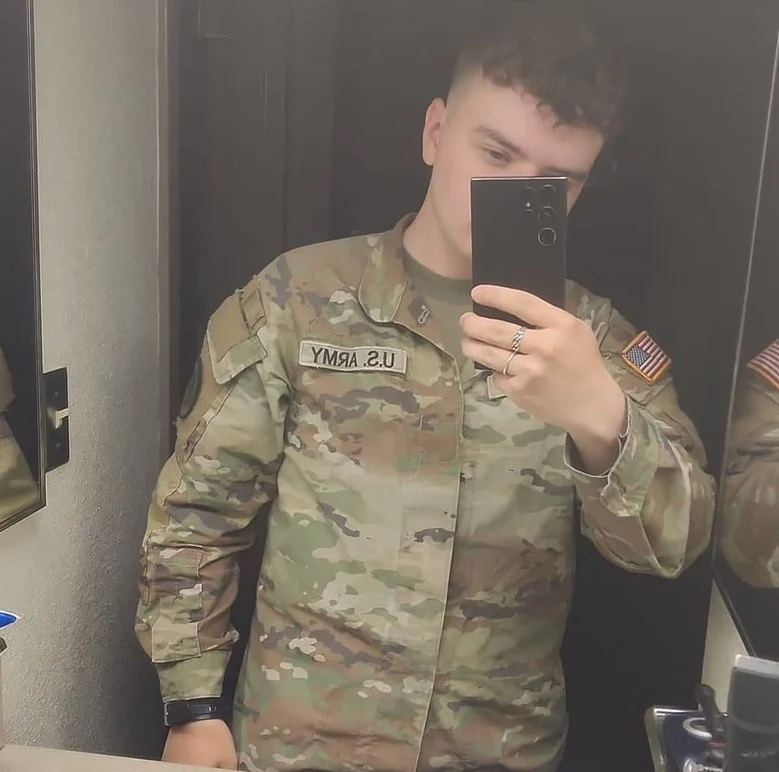
The intersection of national security, military insider threats, and global cybercrime was starkly highlighted in a federal courtroom in Seattle, where a 22-year-old active-duty U.S. Army soldier was sentenced to 70 months in federal prison. Cameron John Wagenius, who operated under the chilling cybercriminal alias "Kiberphant0m," stood before the judge to face the consequences of a sweeping cyber extortion campaign. Operating from a military base in South Korea, Wagenius carved a destructive path through corporate and telecommunications networks, compromising sensitive metadata for more than 100 million AT&T customers and targeting numerous other telecommunications giants worldwide.
In addition to the nearly six-year prison sentence, U.S. District Court authorities ordered Wagenius to pay $294,978 in direct restitution to his victims. The sentencing brings a temporary close to a high-profile case that shocked defense officials and cybersecurity professionals alike. Despite wielding a high level of security clearance and executing complex corporate infiltrations, Wagenius’s criminal enterprise yielded a meager financial return of roughly $1,500, exposing a chilling reality: catastrophic digital destruction and systemic corporate exposure can be driven by malicious actors seeking marginal financial gain, fueled instead by notoriety, ideological chaos, and ego.
Main Facts and the Core Conspiracy
The federal indictments against Wagenius outlined a campaign of unprecedented scale against major cloud infrastructure and telecom giants. Operating primarily through compromised credentials harvested from external sources, Wagenius and his co-conspirators targeted cloud data storage service Snowflake. The vulnerabilities exploited by the group largely stemmed from organizations failing to enforce multi-factor authentication (MFA) on enterprise accounts, an administrative oversight that Snowflake has since aggressively addressed by mandating MFA across all client directories.
Once inside the corporate cloud environments, the threat actors siphoned massive repositories of customer data. Most notably, Wagenius accessed and downloaded call and text message metadata belonging to tens of millions of AT&T customers. This trove of records—including source numbers, destination numbers, timestamps, and call durations—gave the young soldier immense leverage. Working alongside a network of seasoned international cybercriminals, Wagenius and his associates targeted more than a dozen major telecommunications providers globally, including Verizon’s specialized Push-to-Talk corporate infrastructure.
Rather than silently selling the data on underground forums or exploiting it for immediate financial fraud, the group engaged in brazen, public extortion. They contacted victim corporations directly, demanding substantial ransoms under the threat that millions of customer metadata records would be leaked to the public or sold to competing criminal factions.
A Detailed Chronology of the Cyber Onslaught
The unfolding of the "Kiberphant0m" case spans a meticulously documented timeline of digital investigation, public warnings, international cooperation, and judicial swiftness.
- Mid-2024: Wagenius, stationed in South Korea, begins actively exploiting enterprise cloud configurations via unauthenticated Snowflake tenant accounts. Collaborating with cybercriminals such as Conor Riley Moucka and Kenneth Schuchman, he orchestrates breaches across multiple telecommunications firms.
- October 2024: Operating under the moniker Kiberphant0m, Wagenius takes to underground cybercrime forums, publicly boasting about exfiltrating call and text metadata for more than 100 million AT&T customers. He initiates extortion demands, attempting to squeeze multinational corporations for millions of dollars in Bitcoin.
- November 2024: Cybersecurity research firm KrebsOnSecurity publishes an investigative warning suggesting that the elusive Kiberphant0m is likely a U.S. military service member stationed abroad in South Korea, raising alarms within the Department of Defense.
- Late November to December 2024: Swift inter-agency coordination leads to the identification and apprehension of Cameron John Wagenius. Federal prosecutors in Washington state file twin indictments, and Wagenius is swiftly transferred back to U.S. jurisdiction, where he immediately enters guilty pleas across all counts.
- August 2025: Co-conspirator Conor Riley Moucka, operating under the alias "Judische," formally pleads guilty to his role in the Snowflake extortion campaign following his earlier arrest in Canada.
- September 2025: While incarcerated and awaiting sentencing in a federal Bureau of Prisons (BOP) facility, Wagenius attempts to probe prison IT infrastructure. Prison officials uncover his use of fellow inmates’ accounts to prompt generative artificial intelligence tools for zero-day exploits, Windows privilege escalation vectors, and prison escape methodologies.
- Today: Wagenius receives his sentence of 70 months in federal prison and is ordered to pay nearly $300,000 in victim restitution.
An International Web of Co-Conspirators
Federal prosecutors assert that Wagenius did not operate in a vacuum. His digital syndicate included several notorious names within the global cybercriminal underground, each bringing distinct technical capabilities and operational histories to the enterprise.
Kenneth Schuchman, a 28-year-old resident of Vancouver, Washington, allegedly assisted Wagenius in the operational execution and extortion phases of the conspiracy. Schuchman is no stranger to federal law enforcement; in 2019, he pleaded guilty to operating the infamous "Satori" botnet, a vast, automated army of compromised Internet-of-Things (IoT) devices responsible for crippling distributed denial-of-service (DDoS) attacks worldwide.
Another key figure in the international indictment is Conor Riley Moucka of Kitchener, Ontario, who operated under the handle "Judische." Moucka was arrested in Canada in 2024 and formally entered a guilty plea in August 2026 for his integral role in the Snowflake cloud data extortion schemes.
Perhaps most internationally elusive is John Erin Binns, an American citizen currently residing in Turkey. Binns remains wanted by U.S. authorities for his alleged participation in the catastrophic 2021 T-Mobile data breach, which compromised the personal identifying information of at least 76 million current and former customers.
The dangerous synergy between these hardened cybercriminals and an active-duty U.S. Army soldier with security clearance transformed a standard corporate shakedown into a national security emergency.
Escalation, Ransom, and National Security Breaches
The extortion campaign transcended corporate financial data when the threat actors escalated their tactics following initial payoffs. Federal investigators revealed that even after AT&T reportedly paid a ransom totaling approximately $370,000 in Bitcoin to appease the extortionists and secure an agreement for data destruction, the syndicate engaged in double-dipping, or re-extortion.
Angered by the disruption of their network—specifically following the arrest of co-conspirator Moucka—Kiberphant0m retaliated online. Wagenius posted sensitive data directly to public hacker forums, including what he claimed were the call and text logs of prominent political figures, notably then-President-elect Donald Trump and then-Vice President Kamala Harris. Furthermore, the hacker threatened to release classified schematics allegedly stolen from the U.S. National Security Agency (NSA). This reckless dissemination of high-profile communications metadata and national security data elevated the investigation from a corporate hacking case to a critical threat against the integrity of the federal government.
Inter-Agency Task Force Response and Insider Threat Dynamics
The unique convergence of a military insider threat and cyber extortion mobilized a joint response from America’s premier investigative bodies. Paul Russell, the resident agent in charge at the Defense Criminal Investigative Service (DCIS)—the criminal investigative arm of the Department of Defense Office of Inspector General—detailed the immense pressure felt by law enforcement upon discovering the perpetrator’s identity.
"We don’t often get leads where there’s an active duty soldier with a secret clearance who’s creating hacking tools and trafficking in data," Russell noted. "That doesn’t happen every day, and so when that hits it really spins all of our partner organizations up. It was very serious from jump street, just because it was unique, it was an insider threat, and we weren’t sure what we were dealing with."
The multi-agency task force brought together the Federal Bureau of Investigation (FBI), the Army Criminal Investigative Division (CID), the U.S. Secret Service, and the DCIS. Investigators had to navigate the delicate challenge of containing an active-duty military member who possessed both advanced technical skills and institutional access to classified communications channels.
Incarceration Behavior and AI Exploitation Attempts
Even while locked behind bars awaiting trial, Wagenius demonstrated an inability to disconnect from his cybercriminal impulses. According to a sentencing memorandum filed by federal prosecutors in Seattle, Wagenius actively attempted to breach the operational security of the Bureau of Prisons (BOP) network while housed in a federal correctional facility.
Prison monitoring records from September 2025 revealed that Wagenius covertly used the email accounts of fellow inmates to query commercial artificial intelligence applications. Employing a sophisticated social engineering technique known as "prompt injection," Wagenius framed his malicious requests within the fictional context of writing a book. This semantic framing allowed him to bypass the safety guardrails programmed into commercial AI models to prevent the generation of malicious code.
Using these deceptive prompts, Wagenius solicited detailed step-by-step instructions and working script code for exploiting known vulnerabilities. These included Windows 10 Enterprise privilege escalation vectors, D-Link networking device command injection flaws (specifically tracking under CVE-2023-45208), and instructions on how to construct improvised radio antennas using prison commissary items to enhance radio reception and monitor local correctional staff communications. In addition to network exploitation queries, prison monitors discovered that the young soldier had prompted the AI for information regarding prison escape strategies.
When confronted by federal investigators regarding these searches, Wagenius claimed he was merely researching potential software vulnerabilities to voluntarily report them to BOP officials. Prosecutors, however, remained skeptical, noting that while there was no definitive evidence Wagenius successfully deployed exploits inside the prison network, his ongoing inquiries underscored a persistent, unyielding compulsion to probe digital perimeters.
Broader Implications for Corporate Cyber Resilience
The sentencing of Cameron John Wagenius serves as a watershed moment for both military justice and corporate cybersecurity. The case exposes glaring vulnerabilities in how major enterprises manage third-party cloud integrations and identity verification. The Snowflake data breaches demonstrated that even the most sophisticated multinational corporations remain highly vulnerable to supply chain disruptions if basic hygiene protocols—such as mandatory multi-factor authentication and strict credential management—are neglected.
Furthermore, the integration of generative artificial intelligence by incarcerated hackers signals a dangerous evolution in the cybercrime landscape. Threat actors are increasingly leveraging commercial AI tools as force multipliers, using prompt injection techniques to bypass safety filters and accelerate the discovery of zero-day exploits and privilege escalation vectors. For correctional authorities, the incident highlights the urgent need to monitor digital communications platforms within prison facilities closely, as motivated threat actors will continually seek out technological backdoors regardless of their physical confinement.
Ultimately, while the financial yield of Wagenius’s criminal empire amounted to a mere $1,500, the societal, corporate, and governmental fallout was astronomical. As federal prosecutors stated in their final sentencing memorandum, the true damage lies not in the profitability of the enterprise, but in the profound disruption, anxiety, and security risks inflicted upon individual citizens, corporate entities, and the United States government. With Wagenius now beginning his nearly six-year federal prison sentence, law enforcement hopes to send an unyielding message to military insiders and civilian hackers alike: the full weight of federal prosecution will bear down on those who compromise the digital infrastructure of modern society.