• Home
  • About Us
  • Contact Us
  • Cookies Policy
  • Disclaimer
  • DMCA
  • Privacy Policy
  • Terms and Conditions
Dr Crypton
Secure Your Future in Crypto
Tech & Startup News

Massive 75% Discount on One-Year BJ’s Wholesale Club Memberships Arrives Just in Time for the Holiday Shopping Rush

by admin September 24, 2026
written by admin

As autumn settles in and households begin shifting their focus toward seasonal festivities, cooler-weather cooking, and early holiday preparations, major warehouse clubs are rolling out aggressive membership promotions to capture budget-conscious consumers. Among the most competitive offers currently on the market is a newly launched deal that slashes the price of a standard one-year BJ’s Wholesale Club Membership down to just $15. Marking a substantial 75% markdown from the standard annual rate of $60, this limited-time promotion provides new members with full access to the retailer’s extensive network of wholesale goods, digital shopping conveniences, and specialized member perks.

The timing of the discount is strategically aligned with the calendar. Industry analysts frequently note that the final quarter of the year drives the highest volume of warehouse club acquisitions, as consumers prepare for large family gatherings, Thanksgiving dinners, winter holidays, and the stocking of pantry essentials. By reducing the barrier to entry to a mere $15, BJ’s Wholesale Club is positioning itself to attract shoppers who might otherwise hesitate to pay full price for an annual subscription they have yet to test.

Main Facts of the Promotion and Membership Structure

The $15 promotional rate applies strictly to new members who enroll using the designated digital redemption process. Purchasing the deal yields a unique redemption code that must be activated directly on BJs.com. As a condition of this heavily discounted rate, the membership automatically enrolls the user in BJ’s Easy Renewal program, a standard industry practice for introductory warehouse offers that ensures future renewals are billed at the standard annual rate unless canceled by the subscriber.

Once activated, the membership grants the cardholder full access to all physical club locations, online shopping platforms, and secondary services. According to corporate data published by BJ’s Wholesale Club, members can save up to 25% off traditional grocery store prices across a wide array of departments. This includes fresh produce, USDA Choice meats, deli platters, bakery goods, household paper products, cleaning supplies, consumer electronics, and rotating seasonal merchandise.

Furthermore, the membership extends beyond simple in-store shopping. Members are permitted to utilize a robust suite of digital and logistical conveniences, including Curbside Pickup and Same-Day Delivery options for those who prefer not to navigate crowded aisles. For in-store shoppers, the proprietary ExpressPay® feature within the BJ’s mobile app allows customers to scan item barcodes as they place them in their carts and pay digitally, bypassing traditional checkout lines entirely. Additionally, BJ’s maintains a unique pricing policy regarding coupons: the warehouse club accepts manufacturer coupons and permits shoppers to stack them alongside hundreds of in-house BJ’s digital coupons, maximizing potential savings on brand-name goods.

Background Context: The Evolution of Warehouse Clubs in the Retail Landscape

To fully understand the significance of steep membership promotions, one must examine the broader evolution of the warehouse club industry over the past several decades. Pioneered in the late 20th century, the warehouse club model relies on a membership-fee revenue structure that allows operators to sell merchandise at razor-thin profit margins. By limiting product variety—typically stocking only high-volume items and popular national brands rather than thousands of niche SKUs—clubs achieve immense purchasing power with manufacturers.

In recent years, macroeconomic pressures, including persistent inflation and fluctuating grocery costs, have driven a massive resurgence in consumer interest toward wholesale shopping. Households facing elevated grocery bills are increasingly looking for ways to stretch their disposable income. Buying in bulk has transitioned from a niche preference for large families to a strategic financial tool for households of all sizes aiming to lower their cost-per-unit spending on daily necessities.

Competitors such as Costco, Sam’s Club, and BJ’s Wholesale Club have all leveraged introductory discounts, gift card incentives, and digital app integrations to capture market share. BJ’s, with a strong historical footprint along the East Coast of the United States, has continuously expanded its digital infrastructure, refined its private-label offerings (such as Wellsley Farms and Berkley Jensen), and introduced fuel savings to remain competitive against its larger national rivals.

Chronology of Membership Incentives and Seasonal Retail Trends

The rollout of autumn membership promotions follows a predictable annual retail calendar that retailers have perfected over decades. Understanding this timeline highlights why discounts like the $15 BJ’s membership appear precisely when they do.

During the late winter and early spring months (January through April), warehouse clubs typically focus on health, fitness, organization, and early spring cleaning promotions. Membership drives during this quarter often target consumers seeking lifestyle resets or tax-season financial management.

As summer transitions into early fall (August and September), retail strategies pivot sharply. This period marks the back-to-school shopping rush, followed immediately by the arrival of autumn decorations, early Halloween inventory, and preparations for the final quarter’s major holidays. Retailers recognize that consumer spending velocity increases exponentially between October and December. By introducing a $15 promotional price point in September, BJ’s Wholesale Club captures consumers precisely at the psychological inflection point when shopping lists begin to expand.

Historically, warehouse club introductory rates fluctuate between free memberships, gift card bundles, and steep cash discounts. A flat $15 rate represents one of the most aggressive cash reductions offered by the brand, bypassing the need to wait for a promotional gift card to clear or meeting complex spending thresholds.

Detailed Analysis of Member Perks and Ancillary Services

Beyond the traditional savings found in grocery and household goods aisles, warehouse club memberships increasingly derive their value from ancillary services. For members who commute or travel frequently, these secondary perks often offset the cost of the membership entirely within the first few months of use.

Fuel Savings and Transportation Services
One of the most heavily utilized ancillary benefits of a BJ’s membership is access to BJ’s Gas stations. The company reports that members save an average of 20 cents per gallon compared to local average market fuel prices. For a standard commuter vehicle, these fuel savings accumulate rapidly over the course of a 12-month membership period.

In addition to fueling stations, BJ’s operates dedicated Tire Centers. Members can purchase major tire brands, receive complimentary tire rotation and balancing services for the life of tires purchased at the club, and utilize flat repair services.

Specialized In-Club and Partner Services
BJ’s operational footprint extends well beyond retail goods through partnerships and specialized in-house departments:

  • BJ’s Optical: Offers comprehensive eye exams (where available), designer frames, contact lenses, and prescription lenses at discounted member rates.
  • BJ’s Home Improvement: Provides members with vetted contractor services for major residential upgrades, such as roofing, siding, and window replacements, often backed by member-exclusive financing terms or gift card rebates.
  • BJ’s Travel: Functions as a full-service travel agency, offering members exclusive discounts on vacation packages, cruises, rental cars, and hotel bookings.

Economic Implications and Consumer Strategy

The strategy of offering a $15 annual membership carries distinct economic implications for both the retailer and the consumer. For BJ’s Wholesale Club, lower upfront membership fees serve as a customer acquisition engine. The primary goal of the business model is member retention; once a consumer becomes accustomed to bulk purchasing, digital coupon stacking, and same-day delivery services, they are statistically likely to renew their membership at the standard $60 rate upon expiration.

For the consumer, analyzing the utility of such an offer requires a basic calculation of household consumption patterns. Financial analysts note that a $15 investment carries virtually negligible financial risk. Even for single-person households or couples who do not purchase massive quantities of food, savings realized on household paper goods, gasoline, and occasional electronics purchases can easily surpass the $15 threshold within a single shopping trip.

However, consumers must remain cognizant of the automatic renewal mechanism attached to introductory offers. Because the promotion requires enrollment in BJ’s Easy Renewal, subscribers who do not wish to be billed the standard $60 rate for the subsequent year must proactively manage their account settings prior to the end of the 12-month term.

Statements and Industry Reactions Regarding Wholesale Membership Trends

While specific executive commentary regarding this exact $15 flash promotion reflects standard corporate promotional disclosures, broader retail industry consensus highlights the shifting demographics of warehouse club shoppers. Financial earnings reports released throughout the retail sector indicate that warehouse clubs are experiencing steady membership growth, driven heavily by younger demographics, including Millennials and Gen Z consumers setting up independent households.

Retail analysts point out that younger consumers are increasingly pragmatic regarding inflation, viewing warehouse clubs not merely as bulk-buying warehouses for large families, but as essential tools for household budgeting. The ability to purchase high-quality private-label goods—which often match national brand quality at a fraction of the cost—has become a cornerstone of modern consumer shopping strategy.

Furthermore, supply chain experts note that warehouse clubs have successfully insulated themselves against various supply disruptions by maintaining robust supplier relationships and focusing on high-velocity core items. This operational stability allows clubs to offer consistent pricing stability that traditional supermarkets struggle to match during inflationary cycles.

Conclusion and Actionable Information for Prospective Members

The availability of a one-year BJ’s Wholesale Club Membership for $15 represents a rare cost-reduction opportunity in an otherwise high-cost retail environment. With standard annual memberships normally priced at $60, the 75% discount lowers the financial barrier for households looking to test the benefits of wholesale shopping ahead of the holiday season.

The offer is strictly designated for new members. Interested individuals must purchase the redemption code through authorized promotional platforms, such as StackSocial, and subsequently complete the activation process on BJs.com. Because the promotion mandates enrollment in BJ’s Easy Renewal, users should keep track of their renewal timelines to maintain control over future subscription costs.

As the retail calendar moves deeper into the peak autumn and winter shopping season, promotional offers of this magnitude are typically subject to strict inventory or time limits. For consumers aiming to trim their grocery budgets, reduce fuel expenditures, and streamline holiday preparations, the $15 membership option provides an economically sound entry point into the world of wholesale retail.
September 24, 2026 0 comment
0 FacebookTwitterPinterestEmail
Artificial Intelligence & Tech

Model Context Protocol Explained: A Five-Minute Guide to AI Integration Standards

by admin September 24, 2026
written by admin

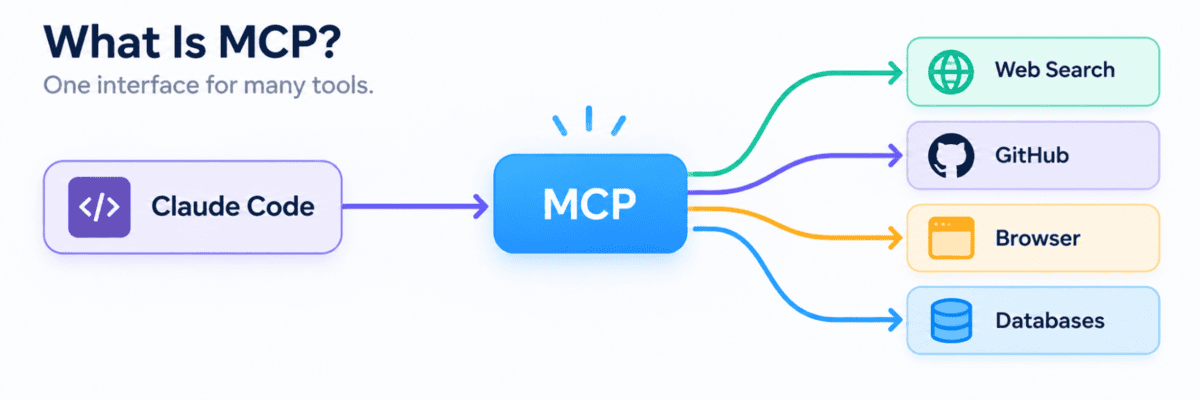
The rapid evolution of artificial intelligence has transitioned from simple text-based conversational interfaces to autonomous agents capable of performing complex, multi-step tasks. Central to this shift is the Model Context Protocol (MCP), an open-standard initiative that addresses one of the most significant bottlenecks in AI development: the fragmented ecosystem of data silos and incompatible tool integrations. By establishing a universal language for AI applications, MCP enables models like Claude to interact with external systems—such as databases, web browsers, and code repositories—without the need for bespoke, proprietary middleware for every connection.

The Problem of Fragmentation

Historically, integrating AI models with external tools has been an arduous, manual process. Each software vendor, database provider, or internal API required developers to write custom code, handle unique authentication flows, and manage specific data formatting. This "n-to-n" integration problem—where every AI application must build a unique bridge to every potential data source—has historically stifled the scalability of agentic workflows. If a developer wanted an AI to search the web, check a GitHub repository, and update a Jira ticket, they were forced to build three distinct integrations.

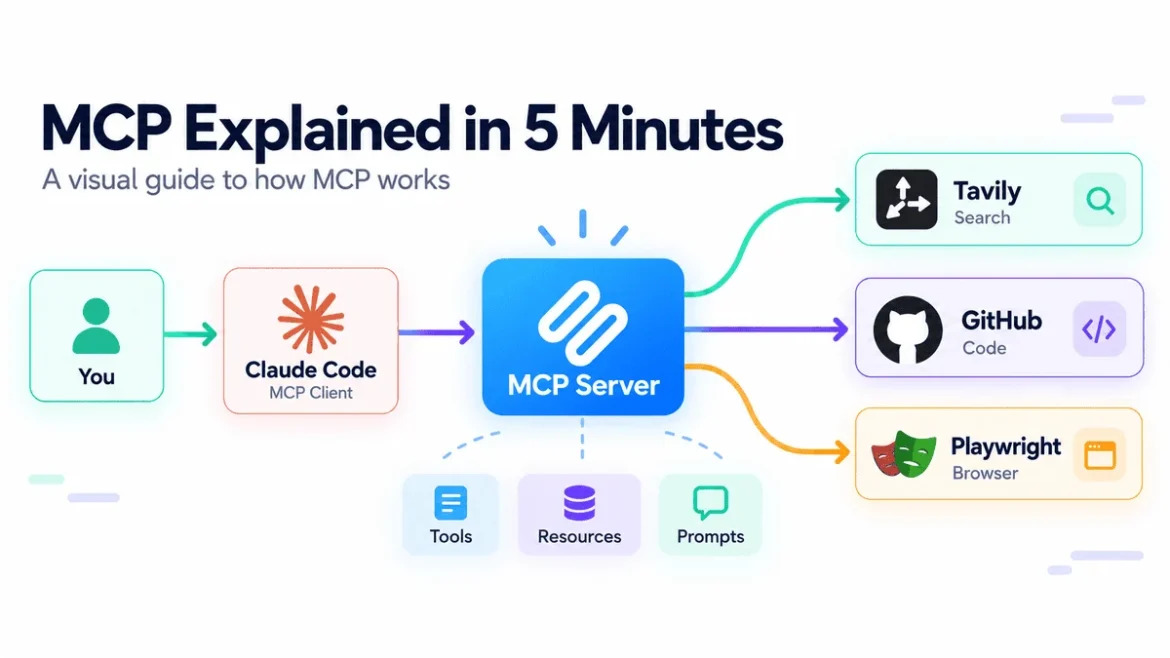
MCP Explained in 5 Minutes - KDnuggets

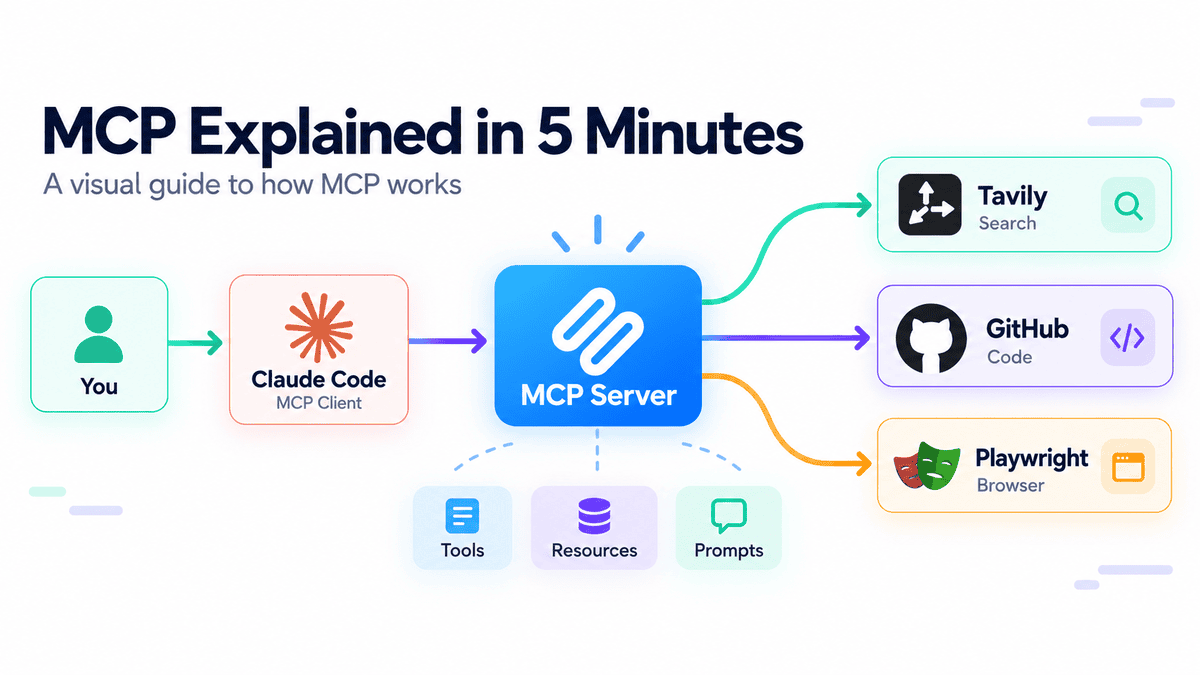
The Model Context Protocol solves this by introducing a standardized architecture that separates the AI application (the host) from the service providing the data or functionality (the server). In this framework, the host does not need to know the internal workings of the external tool; it only needs to know how to communicate via the MCP standard.

Chronology and Development

The concept of a standardized protocol for AI context gained significant momentum throughout 2024 as enterprises struggled to move AI agents beyond experimental, isolated environments. While early LLMs were largely "zero-shot" learners, the industry shift toward Retrieval-Augmented Generation (RAG) and agentic frameworks necessitated a more robust way to feed models high-fidelity, real-time data.

By late 2024 and early 2025, the industry saw the formalization of the MCP specification. Anthropic, which played a leading role in championing this standard, released documentation and support for MCP within its Claude Code environment. This was not merely a technical update but a strategic move to commoditize "tool-use," effectively turning the AI agent into an operating system for digital tasks. The release of the July 2026 specification marked a turning point, moving the protocol from a stateful, session-heavy architecture to a stateless, modular model capable of operating across distributed cloud infrastructure.

MCP Explained in 5 Minutes - KDnuggets

Architectural Components: How It Works

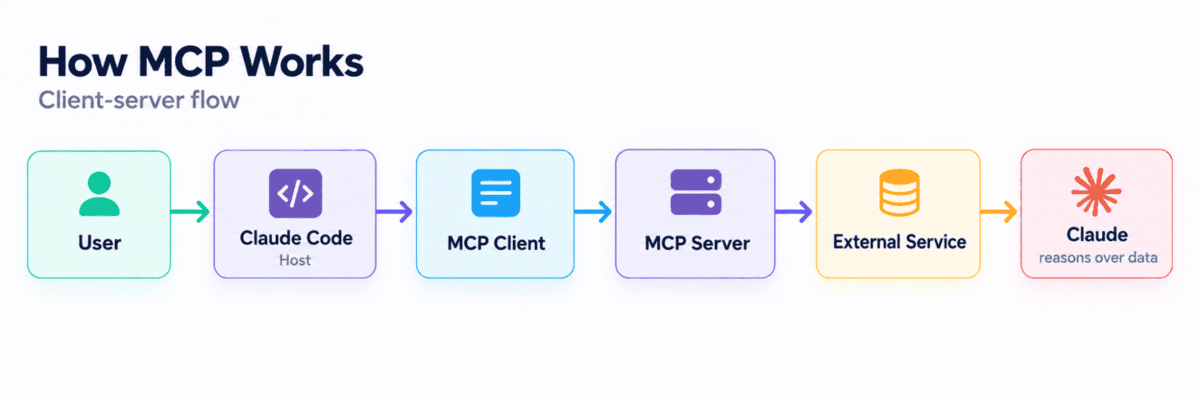
Understanding MCP requires dissecting its core architectural components. The protocol relies on three primary elements:

  1. The Host: This is the AI application or environment, such as Claude Code. The host initiates requests and manages the conversation with the user.
  2. The Client: Acting as the intermediary, the client resides within the host and facilitates communication with MCP servers.
  3. The Server: This is the lightweight wrapper around an external service. It exposes three specific capabilities:
    • Tools: Functions that the AI can execute (e.g., performing a web search or clicking a button).
    • Resources: Data that the AI can read (e.g., log files, database entries, or code documentation).
    • Prompts: Pre-defined templates that guide the AI’s behavior for specific tasks.

By utilizing a standard transport layer, usually JSON-RPC, the client and server can negotiate capabilities dynamically. When a user issues a prompt, the model evaluates its available tools and determines whether to invoke an MCP server to retrieve information or perform an action. This eliminates the need for the model to "guess" how to interact with an API; it simply queries the server for its capabilities and executes the command within the established parameters.

Practical Implementation: The Agentic Workflow

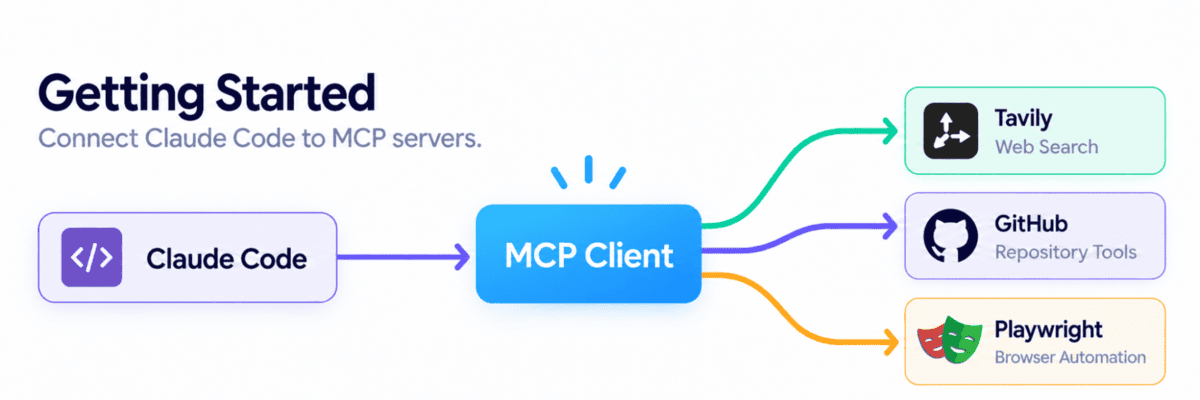
The efficacy of MCP is best illustrated through its practical application in professional developer workflows. By connecting Claude Code to specific MCP servers, developers can bridge the gap between intent and execution.

MCP Explained in 5 Minutes - KDnuggets

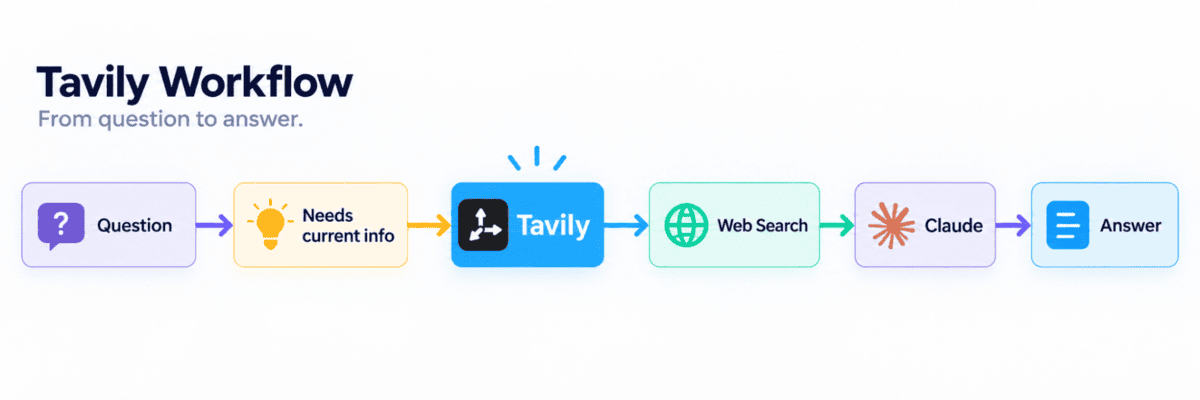
For instance, utilizing the Tavily MCP server allows an AI agent to bypass the "knowledge cutoff" limitations of LLMs. By providing a standardized interface for live web research, the agent can perform deep-web crawling and summarization, returning synthesized results to the user in seconds. Similarly, the GitHub MCP server enables an agent to authenticate via a Personal Access Token (PAT) to perform repository-wide audits, analyze pull requests, and identify bugs without the user ever leaving the command-line interface.

Furthermore, the integration of Playwright via MCP represents the frontier of browser-based automation. By transforming the browser into an API-accessible entity, the agent can interact with modern, dynamic websites, filling out forms or navigating UI-heavy applications that were previously inaccessible to pure-text models. These tools function not by overriding the underlying services but by acting as a universal translator that makes these systems "agent-ready."

Data and Implications

The transition to a stateless architecture in the 2026 specification has profound implications for enterprise adoption. Statelessness allows for horizontal scaling; as demand for agentic processing grows, organizations can deploy MCP servers across serverless architectures without worrying about session persistence or state synchronization. This shift lowers the barrier to entry for developers who are building high-concurrency AI systems.

MCP Explained in 5 Minutes - KDnuggets

Furthermore, industry analysis suggests that the widespread adoption of MCP could lead to a "standardization of tool-use," where the value of an AI platform is measured less by its base model performance and more by the breadth and depth of its MCP-compatible ecosystem. Just as the emergence of the HTTP protocol enabled the web to scale, MCP provides the foundation upon which an interoperable "AI Web" can be built.

Security and Governance

While MCP provides immense utility, it introduces new vectors for security and governance. Because an MCP server essentially gives an AI the ability to execute actions on behalf of a user, strict adherence to the "Principle of Least Privilege" is paramount. When configuring a GitHub MCP server, for example, developers are encouraged to use granular PATs that restrict the agent’s access to only the necessary repositories.

The protocol includes built-in mechanisms for security, such as standardized authentication headers and scoped access controls, ensuring that AI agents cannot inadvertently modify production databases or leak sensitive information unless explicitly granted permission. As the standard matures, the community is moving toward more robust identity and access management (IAM) integrations, which will allow enterprises to audit agent actions with the same level of scrutiny applied to human employees.

MCP Explained in 5 Minutes - KDnuggets

Future Outlook

The Model Context Protocol is not merely an incremental improvement; it is a foundational shift in how humans interact with machine intelligence. By decoupling the reasoning engine from the data source, MCP fosters a modular ecosystem where individual tools can be improved, replaced, or scaled independently of the AI model.

As we look toward the future, it is highly probable that major software platforms will begin shipping native MCP servers alongside their APIs. This would effectively turn every enterprise software tool into an "agent-native" application. For developers and businesses alike, the message is clear: the era of manual integration is coming to an end. The future of AI lies in the ability to connect disparate systems into a cohesive, intelligent whole, and MCP serves as the primary standard for achieving that connectivity.

September 24, 2026 0 comment
0 FacebookTwitterPinterestEmail
Cryptocurrency News

OpenZeppelin Brings Industry-Standard Smart Contract Security Suite to the TRON Network

by admin September 24, 2026
written by admin

LONDON, UK — September 24, 2026. In a landmark development for the decentralized finance and blockchain engineering sectors, OpenZeppelin has officially announced the integration of its premier smart contract libraries and secure development suite with the TRON network. This major technological convergence brings OpenZeppelin’s battle-tested security framework to one of the world’s most heavily utilized public blockchains, bridging the gap between institutional-grade development practices and TRON’s massive high-throughput ecosystem.

The integration addresses a critical scaling requirement for developers building sophisticated decentralized applications (dApps), stablecoin ecosystems, and enterprise-grade payment gateways on TRON. By introducing audited contract components, standardized upgrade workflows, and modern developer tooling, the collaboration aims to significantly reduce deployment friction while elevating the baseline of security across the network.

Bridging Institutional Security with High-Throughput Infrastructure

For years, OpenZeppelin has served as the gold standard for smart contract development across the broader blockchain industry. Since its inception in 2015, the organization’s flagship OpenZeppelin Contracts library has underpinned more than $37 trillion in total value transferred. Furthermore, its rigorous security team has conducted over 900 engagements, preemptively identifying and resolving more than 10,000 vulnerabilities prior to production deployment.

Until now, developers operating within the TRON ecosystem frequently had to navigate disparate security tooling or custom-built frameworks that lacked the universal standardization enjoyed by EVM-compatible networks. By bringing its comprehensive suite—including the widely popular Contracts Wizard, secure upgrade tools, and AI-assisted development support—to TRON, OpenZeppelin provides builders with a trusted, unified foundation.

The newly adapted suite is meticulously tailored to TRON’s specific network architecture. Beyond basic token creation and access control, the integrated tools support advanced, production-critical primitives such as passkey authentication, robust supply chain controls, decentralized permissions, and dynamic governance frameworks. These additions empower development teams to construct complex applications capable of safely evolving alongside user demand.

Strategic Perspectives from Industry Leaders

The integration has drawn enthusiastic responses from key stakeholders across both organizations, highlighting the mutual benefits of merging OpenZeppelin’s security pedigree with TRON’s unparalleled transaction volume.

Sam Elfarra, Community Spokesperson for the TRON DAO, emphasized the foundational role that robust security plays in the network’s ongoing evolution. "Security is fundamental to expanding what developers can build across the TRON ecosystem," Elfarra stated. "OpenZeppelin gives developers a trusted set of tools and standards that many already know from across the broader blockchain industry. Bringing that experience to TRON lowers friction for builders while giving teams stronger foundations for creating applications that can operate at scale."

Echoing this sentiment, Pepe Blasco, Engineering Manager at OpenZeppelin, underscored the importance of establishing reliability from the ground up. "Strong security starts at the foundation. Developers need primitives they can trust on the network they are deploying to," noted Blasco. "Bringing our contracts and tooling to TRON lets teams keep the assurances they know from other ecosystems, while accounting for the network-specific requirements that matter in production. The goal is a robust path from first line to production."

Context and Chronology: The Maturation of the TRON Network

To fully appreciate the significance of this integration, one must examine TRON’s trajectory since its inception. Founded in September 2017 by Justin Sun, the TRON blockchain achieved a major milestone with the launch of its MainNet in May 2018. Over the ensuing years, the network evolved from an ambitious content-sharing protocol into one of the dominant Layer-1 settlement layers for global decentralized transactions.

OpenZeppelin Integrates with TRON to Bring Its Security Standard to the Network

By late 2026, TRON had cemented its position as a primary global highway for digital dollars. The network currently hosts the largest circulating supply of USD Tether (USDT) of any blockchain, with figures exceeding $94 billion. Operational statistics compiled by TRONSCAN highlight the sheer scale of the network:

  • Total User Accounts: Surpassed 405 million globally.
  • Total Transactions: Exceeded 15 billion processed transfers.
  • Total Value Locked (TVL): Consistently maintains over $29 billion in ecosystem value.

Operating under the guiding ethos of "Moving Trillions, Empowering Billions," TRON has increasingly attracted traditional financial institutions, fintech enterprises, and sophisticated developers seeking high throughput and minimal transaction latency. However, as the network absorbs larger volumes of institutional capital and enterprise-grade financial instruments, the demand for uncompromising smart contract security has grown exponentially. The arrival of OpenZeppelin directly answers this call, providing the institutional assurance required to onboard the next wave of corporate and retail applications.

Implications for Decentralized Finance and Enterprise Adoption

The immediate implication of OpenZeppelin’s deployment on TRON is a marked reduction in development overhead and security vulnerabilities. Historically, smart contract bugs and faulty access controls have resulted in billions of dollars in exploits across the decentralized finance (DeFi) landscape. By standardizing the development lifecycle—from the initial writing of code to final deployment and ongoing upgrades—the integration mitigates human error and standardizes best practices.

Furthermore, the inclusion of AI-assisted development tools and automated security checks within the OpenZeppelin suite democratizes access to high-level engineering resources. Independent developers and small startup teams operating within the TRON ecosystem can now leverage the same structural guardrails previously reserved for heavily funded, enterprise-level protocols.

As TRON continues to expand its footprint across decentralized finance, cross-border payments, gaming, and tokenized real-world assets (RWAs), the presence of a trusted security framework will likely accelerate institutional participation. Financial institutions exploring blockchain integration frequently cite regulatory compliance, risk management, and smart contract auditability as non-negotiable prerequisites. By embedding OpenZeppelin’s proven architecture directly into its developer pipeline, TRON has substantially strengthened its value proposition for risk-averse corporate partners.

Looking Ahead

The partnership between OpenZeppelin and the TRON DAO marks a maturing milestone for the Web3 industry, demonstrating that platform interoperability and security standards can transcend individual blockchain architectures. As development teams begin leveraging the new suite to build the next generation of scalable dApps, the collective security posture of the TRON network is poised for a significant, measurable elevation.

With the tools now live and accessible to the global developer community, the focus shifts to execution—empowering builders to turn secure code into scalable, production-ready financial applications that serve hundreds of millions of users worldwide.


About OpenZeppelin

OpenZeppelin is recognized globally as the security standard for onchain finance. Since 2015, the organization has established the benchmark for blockchain and smart contract security through its industry-standard OpenZeppelin Contracts library, which has secured over $37 trillion in transferred value. Through more than 900 security engagements, OpenZeppelin has successfully identified and remediated over 10,000 vulnerabilities prior to production. The company routinely secures the world’s leading blockchain networks, decentralized finance protocols, and financial institutions.

  • Website: www.openzeppelin.com
  • Media Contact: Christian Santagata (Head of Marketing) | [email protected]

About TRON DAO

TRON DAO is a community-governed decentralized autonomous organization dedicated to accelerating the decentralization of the internet through blockchain technology and decentralized applications. Established in September 2017, the TRON network has grown into a premier global settlement layer characterized by massive user adoption, high transaction throughput, and deep liquidity, particularly in stablecoin markets.

  • Website: trondao.org / tron.network
  • Media Contact: Yeweon Park | [email protected]
September 24, 2026 0 comment
0 FacebookTwitterPinterestEmail
Blockchain Technology

MoonPay Expands Into Tokenized Assets With Acquisition of North Capital in All-Stock Deal Valued Over $60 Million

by admin September 24, 2026
written by admin

Crypto payments infrastructure giant MoonPay has officially entered the burgeoning market for tokenized real-world assets (RWAs) through a strategic all-stock acquisition of North Capital, a specialized financial services firm. According to industry reports, the transaction is valued at upwards of $60 million, contingent upon customary regulatory reviews and approvals. This major structural pivot marks a critical evolution for MoonPay, transitioning the company from a traditional fiat-to-crypto onboarding gateway into a fully integrated provider of regulated securities infrastructure.

By absorbing North Capital’s comprehensive suite of financial licenses and technological capabilities, MoonPay is positioning itself to capture institutional capital inflows looking to bridge traditional financial instruments with distributed ledger technology. The deal brings together MoonPay’s massive retail and institutional payment rails with North Capital’s robust compliance, brokerage, and alternative trading framework.

The Strategic Value of North Capital’s Infrastructure

Founded to streamline private capital formation and secondary market liquidity, North Capital has spent years establishing a formidable regulatory footprint in the United States. The firm is uniquely positioned in the fintech ecosystem due to its expansive compliance and operational licenses. North Capital operates the PPEX Alternative Trading System (ATS), a regulated platform that has successfully handled over $8.7 billion in total transaction volume. The PPEX ATS currently lists more than 1,250 eligible securities, providing a vital marketplace for private companies to issue and trade equity and debt instruments.

Beyond its alternative trading system, North Capital maintains critical regulatory registrations as a registered broker-dealer, transfer agent, and investment advisor. These components are notoriously difficult, time-consuming, and expensive to acquire independently, making North Capital an exceptionally attractive acquisition target for crypto-native enterprises seeking regulatory legitimacy.

For MoonPay, integrating these licenses means the company can legally bypass the traditional regulatory hurdles associated with handling securities. Rather than building a regulated securities stack from scratch—a process that can take years and encounter steep pushback from regulatory bodies like the Securities and Exchange Commission (SEC)—MoonPay can now leverage North Capital’s existing infrastructure. This allows MoonPay to offer tokenized equity, debt, and alternative assets directly to its extensive client base, opening new revenue streams well beyond conventional cryptocurrency purchasing.

MoonPay buys North Capital, including ATS for tokenized securities

Addressing Liquidity Fragmentation and the Agora Network Conundrum

One of the most consequential aspects of the acquisition involves North Capital’s recent strategic initiatives aimed at solving one of the tokenized asset sector’s most persistent challenges: liquidity fragmentation. Earlier, North Capital partnered with tZERO, another prominent tokenized securities venue, to launch Agora. Agora functions as a specialized network designed to connect disparate Alternative Trading Systems.

By linking these platforms, Agora allows qualified institutional participants to discover and route orders across multiple venues seamlessly, rather than being trapped in isolated liquidity silos. The network achieved a major milestone in July when it successfully executed its first routed order. However, the integration of North Capital into MoonPay introduces complex governance questions regarding Agora’s future.

With North Capital now absorbed into a vertically integrated financial group that concurrently owns its own transaction router and proprietary payment rails, industry observers are closely monitoring how Agora’s neutrality will be maintained. The success of multi-venue liquidity networks relies heavily on the perception of unbiased cooperation among founding members. Stakeholders in the tZERO-North Capital partnership will likely need to establish clear governance boundaries to ensure that MoonPay’s controlling stake in North Capital does not compromise the cooperative spirit of the Agora network.

The Broader Context: The Rise of Real-World Asset Tokenization

The acquisition of North Capital by MoonPay occurs against the backdrop of a broader, industry-wide race to tokenize real-world assets. Financial institutions, asset managers, and fintech pioneers are increasingly recognizing that blockchain technology offers unprecedented efficiencies for issuing, settling, and managing traditional financial instruments. From U.S. Treasury bills and commercial real estate to private equity and corporate debt, trillions of dollars in traditional assets are slowly migrating onto public and private ledgers.

Major global financial institutions—including BlackRock, Franklin Templeton, and JPMorgan—have launched proprietary tokenization initiatives to capitalize on the demand for instantaneous settlement, lower administrative overhead, and fractionalized ownership. For crypto infrastructure providers like MoonPay, participating in this macro trend is essential for long-term survival and growth. While retail crypto trading volumes remain cyclical, the market for tokenized securities represents a massive, sticky institutional opportunity that promises predictable, fee-based revenues.

MoonPay buys North Capital, including ATS for tokenized securities

By acquiring a licensed broker-dealer and ATS operator, MoonPay is effectively bridging the gap between Web3 native liquidity and traditional capital markets. This positioning makes MoonPay an appealing partner for legacy financial institutions that want to experiment with blockchain-based asset issuance without stepping outside the bounds of established regulatory frameworks.

Regulatory Realities and Future Outlook

As the transaction awaits final regulatory clearance, regulatory scrutiny remains a defining factor for both companies. The U.S. regulatory environment for digital assets and tokenized securities has historically been characterized by strict enforcement and a lack of bespoke legislative clarity. By acquiring an entity that already possesses SEC registration and FINRA membership, MoonPay is embedding compliance directly into its corporate DNA.

Market analysts view this move as a bellwether for future mergers and acquisitions within the fintech space. As crypto companies mature, many are discovering that raw technological innovation is insufficient without the regulatory permissions required to service institutional capital. Acquiring licensed legacy entities represents a fast-track solution to this dilemma.

Looking ahead, the integration of North Capital’s operations into MoonPay is expected to unfold over the coming months, pending the green light from relevant regulatory bodies. If successful, the combined entity will possess a rare combination of global consumer reach, frictionless fiat payment rails, and a fully compliant securities infrastructure. This positions MoonPay not merely as a gateway for buying digital currencies, but as a comprehensive financial utility capable of supporting the entire lifecycle of traditional and tokenized assets in the digital age.

September 24, 2026 0 comment
0 FacebookTwitterPinterestEmail
Cybersecurity & Hacking

OnePlus Security Vulnerability Allows Malicious Apps to Gain Full Root Access Without User Permissions

by admin September 24, 2026
written by admin

A critical security vulnerability affecting the latest iterations of OxygenOS, the proprietary Android-based operating system utilized by OnePlus and its parent company OPPO, has been publicly disclosed by security researcher Rasmus Moorats. The flaw allows a malicious application, requiring zero specific permissions, to escalate privileges to root access—the highest level of administrative control on an Android device. This discovery exposes a significant lapse in the security architecture of modern flagship smartphones, as it permits an attacker to bypass standard operating system protections, access sensitive user data, and execute arbitrary code at the kernel level.

The vulnerability stems from a sophisticated "chaining" of two distinct software flaws found within pre-installed OnePlus system services. By exploiting these weaknesses in tandem, an attacker can move from a low-privilege environment to absolute device ownership.

Chronology of the Disclosure and Corporate Tensions

The discovery process began in early 2026, leading to a strained period of communication between the independent researcher and the device manufacturer. According to the documented timeline provided by Moorats, the flaws were formally confirmed by OnePlus engineering teams in May 2026.

However, the path to resolution was hampered by significant disagreements regarding the disclosure process. In correspondence shared by the researcher, OnePlus management asserted that the company holds the "exclusive final right of vulnerability disclosure." The company explicitly warned the researcher that publishing the technical details without express authorization could result in legal action, citing European cybersecurity regulations as a basis for restricting independent reporting.

Despite these warnings and the absence of a patched version of OxygenOS, Moorats proceeded with a full public disclosure on September 24, 2026. At the time of publication, no Common Vulnerabilities and Exposures (CVE) identifier had been assigned, nor had a security patch been pushed to the affected devices. This move highlights a growing trend of friction between security researchers advocating for "responsible disclosure" and OEMs (Original Equipment Manufacturers) attempting to control the narrative surrounding product vulnerabilities.

Unpatched OnePlus Flaws Let Installed Android Apps Gain Root Without Permissions

Technical Breakdown: How the Chain of Vulnerabilities Works

The attack vector relies on the interaction between two specific components of the OxygenOS environment.

The first point of failure lies within a system service identified as "AtlasService." This service is designed to collect diagnostic and debugging data. Crucially, it operates with root-level privileges but fails to implement proper authentication checks, meaning it accepts requests from any application currently installed on the device, regardless of whether that application has been granted permissions by the user. An attacker can submit a specially crafted request to this service, which then passes the input to a secondary debugging tool. This tool executes the input as a system command without sufficient sanitization. While this initial exploit does not grant full system control, it does provide the attacker with root access within a restricted, sandboxed zone known as "dumpstate."

The second component of the attack involves a hardware-level helper service labeled "olc2." This service is intended to facilitate low-level hardware interactions. Under normal circumstances, the command structure of olc2 is guarded by a check that verifies the caller’s privilege level. Because the attacker has already gained root access via the AtlasService exploit, they successfully bypass this guard. Once the olc2 service is engaged, it executes the shell instruction provided by the attacker, effectively "breaking out" of the dumpstate sandbox and granting the malicious application full, unrestricted Linux kernel privileges.

Broader Implications and the OEM Ecosystem

The threat is not limited to a single model. While the testing was performed on a OnePlus 15, investigations suggest that the underlying codebase for OxygenOS is shared extensively across the OnePlus and OPPO product lines. The manufacturer has acknowledged that these vulnerabilities affect a wide range of devices, though it has remained opaque regarding the specific list of impacted models.

This incident is emblematic of a wider security crisis within the Android ecosystem known as "OEM-added vulnerabilities." While the Android Open Source Project (AOSP) undergoes rigorous security auditing by Google, the proprietary layers added by manufacturers to differentiate their products often introduce bespoke code that lacks the same level of scrutiny.

In August 2026, security firm Calif highlighted this systemic issue through their "OEMpocalypse" research. That study demonstrated that proprietary code added by major manufacturers—including Samsung, Xiaomi, OPPO, and OnePlus—frequently introduces paths for privilege escalation that allow third-party apps to gain root access on locked devices. These findings suggest that the security of a modern smartphone is increasingly dependent on the quality of code written by the manufacturer, rather than the core Android operating system alone.

Unpatched OnePlus Flaws Let Installed Android Apps Gain Root Without Permissions

User Risks and Mitigation Strategies

The primary constraint of the current exploit is that it requires a malicious application to be locally installed on the target device. This means the attack cannot be executed remotely via a webpage or a simple phishing link; a user must be tricked into installing an APK or a malicious application from a third-party source.

However, once installed, the malicious app operates entirely silently. Because the exploit uses pre-existing system services to escalate privileges, the application does not trigger the standard Android permission prompts that would normally alert a user to suspicious activity. There is currently no evidence that these vulnerabilities have been utilized in the wild by threat actors, but the public availability of the exploit code significantly increases the risk that malicious actors may develop automated tools to leverage these flaws.

Until OnePlus releases a comprehensive firmware update to address these vulnerabilities, the most effective defense remains traditional digital hygiene:

  1. Strict App Sourcing: Users should refrain from installing applications from outside the official Google Play Store. Sideloading applications from unverified sources remains the primary gateway for this exploit.
  2. Permission Auditing: While this specific exploit bypasses permission prompts, users should regularly review the list of installed applications and uninstall any software that is no longer required or originates from an untrusted developer.
  3. Firmware Updates: Owners of OnePlus and OPPO devices are urged to check for system updates frequently. While no fix was available at the time of the initial report, security patches are often bundled into monthly releases.

The Conflict Between Disclosure and Regulation

The dispute between Moorats and OnePlus underscores a critical debate in the cybersecurity community regarding the "Right to Disclose." OnePlus’s stance—that it possesses the sole right to determine when and how a vulnerability is made public—clashes with the industry-standard practice of coordinated disclosure. Industry norms typically allow a researcher to publish their findings after a set period (usually 90 days) if the vendor has failed to provide a fix or demonstrate progress toward one.

By threatening legal action, OnePlus is utilizing a strategy that critics argue stifles independent security research and leaves consumers at risk by suppressing information. The company’s reference to European cybersecurity regulations as a justification for silence is particularly contentious, as many cybersecurity experts interpret these regulations as a mandate for transparency and prompt remediation, rather than a tool for corporate obfuscation.

As the industry moves forward, the pressure on manufacturers to adopt more transparent security practices will likely increase. With the rise of sophisticated, proprietary "value-add" features in smartphones, the ability for manufacturers to rapidly identify, patch, and disclose flaws has become as important as the hardware specifications themselves. For now, users of OnePlus and OPPO devices remain in a vulnerable position, waiting for an official patch that addresses the core architectural weaknesses of their devices’ software.

September 24, 2026 0 comment
0 FacebookTwitterPinterestEmail
Cybersecurity & Hacking

MacSync Malware Evolves to Weaponize Public iCloud Calendars and Deliver Advanced macOS Payloads

by admin September 24, 2026
written by admin

Cybersecurity researchers have uncovered a sophisticated new iteration of the MacSync information-stealing malware that introduces an unconventional vector for command and control: public iCloud calendars. Initially spotted in early 2025 as a Swift-based variant loosely tied to the AMOS stealer family, MacSync has rapidly evolved into a modular, multi-stage threat targeting macOS environments. According to telemetry and analysis from Kaspersky, recent campaigns utilize elaborate social engineering—including deceptive ClickFix schemes and fraudulent cryptocurrency applications—to slip past user defenses. By leveraging legitimate cloud infrastructure such as Apple’s iCloud services, the operators of MacSync have demonstrated an increasing capacity to evade traditional endpoint detection systems, posing a renewed challenge for enterprise security teams and individual Mac users alike.

The Evolution of MacSync: From AMOS Offshoot to Advanced Multi-Stage Threat

To understand the current threat landscape surrounding MacSync, security analysts must examine its trajectory since it first emerged in April 2025. Initially characterized as a relatively straightforward Swift-based info-stealer derived from the notorious AMOS (Atomic macOS Stealer) family, the malware quickly caught the attention of threat intelligence researchers due to its rapid iteration cycle. Unlike early versions that relied solely on conventional payload delivery methods, the recent campaign analyzed by Kaspersky reveals a significant architectural overhaul.

The malicious operators behind MacSync have steadily modularized the malware, decoupling the initial downloader from the core infostealer modules and the newly introduced backdoor components. This modular design not only complicates the task of reverse-engineering the malware but also allows threat actors to dynamically provision payloads based on the compromised system’s profile. By separating the initial reconnaissance and delivery phases from data harvesting and remote administration capabilities, the creators of MacSync have mirrored the sophisticated tactics typically observed in advanced persistent threat (APTs) groups, bringing enterprise-grade stealth techniques to the macOS consumer and enterprise threat landscape.

Anatomy of an Attack: Social Engineering and iCloud Calendar C2

MacSync malware uses public iCloud calendars to deliver new payloads

The primary distribution vector for MacSync relies heavily on social engineering, capitalizing on user trust and the growing prevalence of browser-based deception tactics. Recent campaigns have heavily leveraged so-called ClickFix attacks, where users are manipulated into copying and pasting malicious terminal commands under the guise of fixing minor software errors or updating legitimate utilities such as Homebrew and disk space analyzers. Furthermore, threat actors have deployed bespoke fraudulent infrastructure, including dedicated promotional websites and social media campaigns advertising a fake cryptocurrency wallet application named "Toria."

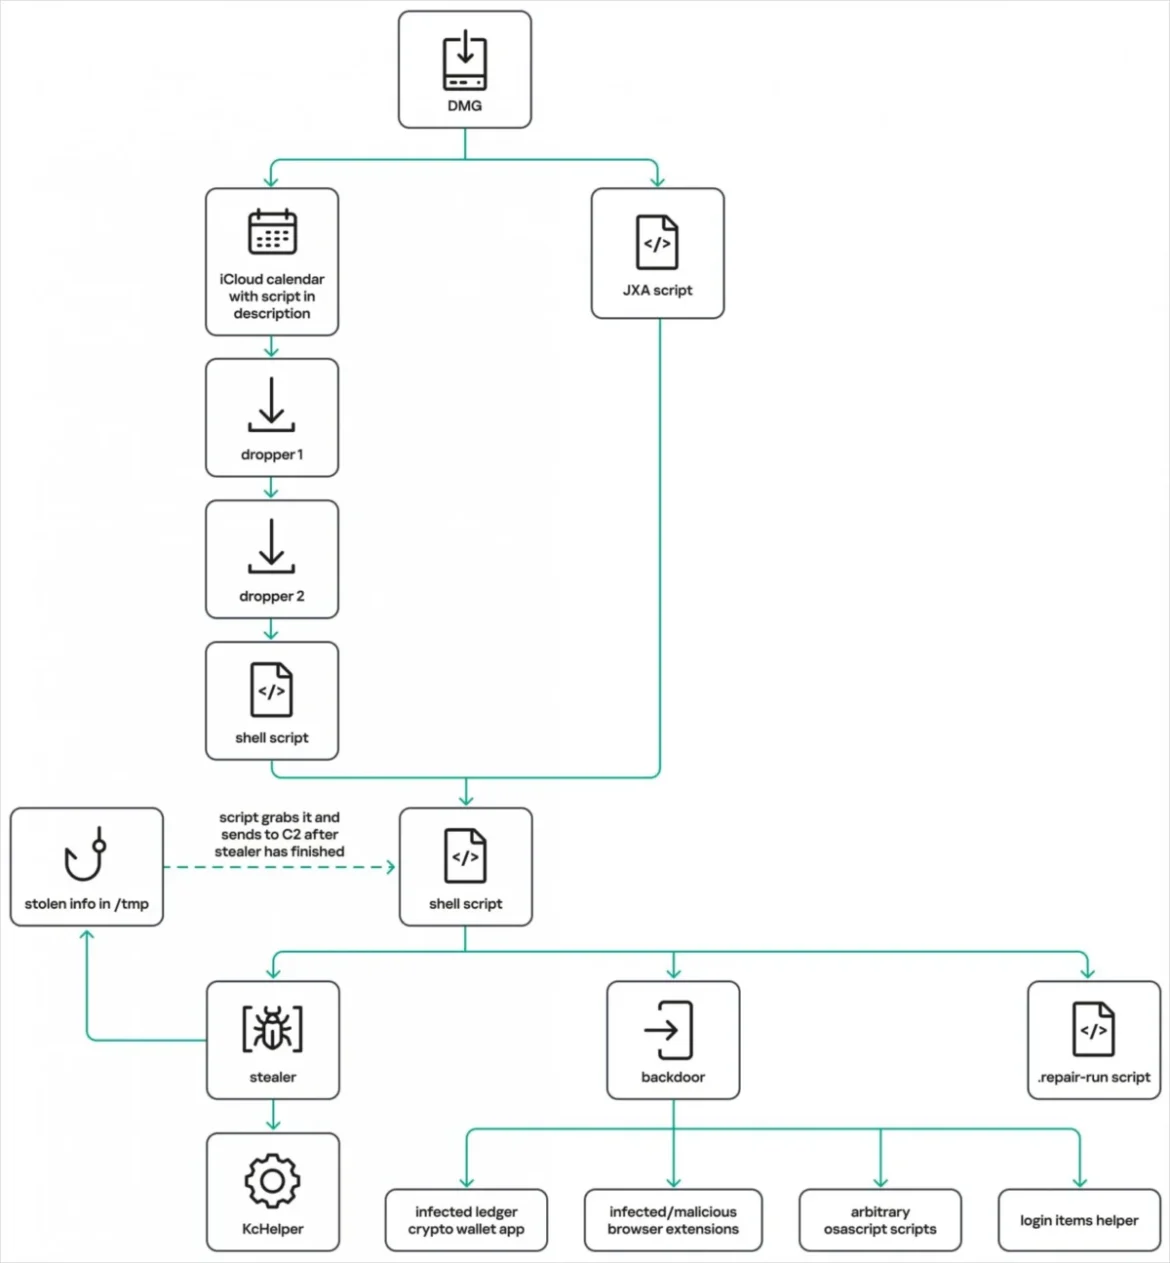
Once a victim is lured into interacting with these malicious assets, the infection chain bifurcates into standard and highly complex delivery mechanisms. In the more intricate variant identified by Kaspersky, a specialized downloader script fetches hidden commands embedded directly within the description field of a public iCloud calendar event.

The mechanics of this technique highlight a clever abuse of native macOS utilities and legitimate cloud services. The downloader feeds the retrieved calendar data directly into the system’s default interactive shell, the Z shell (zsh). Because the calendar description contains a mixture of unstructured text and hidden executable code, standard lines generate benign parsing errors. However, specific instructions placed immediately following the designated description delimiter (DESCRIPTION:) are executed by the shell. These commands orchestrate the fetching of a subsequent archive containing multi-stage malware components from iCloud. Ultimately, this leads to the deployment of an application bundle acting as a dropper, which unpacks and launches the core MacSync payloads.

Comprehensive Data Harvesting and the New Objective-C Backdoor

Once successfully established on a compromised macOS host, MacSync executes a comprehensive sweep of the system to extract sensitive information. The core infostealer module targets a vast repository of personal, professional, and financial data. This includes browser history, cookies, and saved authentication credentials from all major web browsers; data associated with cryptocurrency wallet browser extensions and desktop applications; local data stores from messaging platforms like Telegram; and the system’s native Keychain file.

In addition to user-level credentials, the malware performs aggressive reconnaissance of developer and administrative assets. It scans for Secure Shell (SSH) keys, AWS credentials, Kubernetes configuration files, Git repositories, and various shell initialization and configuration files. This makes MacSync particularly dangerous for software engineers, systems administrators, and corporate employees who handle elevated access tokens on their personal or work-managed Mac computers.

MacSync malware uses public iCloud calendars to deliver new payloads

Compounding the threat is a newly observed Objective-C backdoor module. Disguising itself as Finder—the fundamental file manager interface of macOS—this backdoor is designed to maintain persistent unauthorized access. Upon installation, the backdoor establishes persistence mechanisms by configuring a LaunchAgent, modifying local .zshrc profile files, and injecting global Git hooks. To ensure the user remains oblivious to the compromise during these automated operations, the backdoor actively terminates legitimate macOS notification processes, effectively silencing system alerts and preventing warning banners from appearing on the desktop.

Capabilities and Mystery Components of the Backdoor Module

While security researchers were unable to fully analyze the specific AppleScript payloads executed by the backdoor due to obfuscation and missing script components, they were able to infer the intended functions of various commands based on their internal naming conventions and status messages. The backdoor is equipped to execute remote management commands, manipulate file systems, and execute arbitrary scripts supplied by the command-and-control (C2) infrastructure.

Of particular note to analysts is a mysterious command identified in the backdoor’s codebase designated as live_browser. When invoked, this command downloads and executes an auxiliary component known as sn_relay. As of the latest Kaspersky reports, the precise functional objective of sn_relay remains undetermined, leaving researchers to monitor its behavior closely for signs of secondary payloads, lateral movement tools, or proxy capabilities. The inclusion of such obscure components underscores the fluid nature of the MacSync project and suggests that the threat actors are actively testing new functional modules in the wild.

Industry Implications and the Broader Threat to macOS

The weaponization of public iCloud calendars and the integration of sophisticated backdoors into MacSync highlight a broader, concerning trend within the threat landscape: the continuous expansion of malware targeting Apple’s macOS ecosystem. Historically, macOS users enjoyed a degree of immunity from widespread cybercrime due to the platform’s stringent security controls, sandboxing, and market share dynamics. However, as enterprise adoption of Macs grows and cryptocurrency wealth becomes increasingly centralized on desktop environments, cybercriminals have invested heavily in bypassing macOS-specific security barriers.

MacSync malware uses public iCloud calendars to deliver new payloads

Security analysts emphasize that techniques abusing cloud services—such as leveraging public calendar events for command and control—blur the lines between legitimate administrative traffic and malicious activity. Because connections to Apple’s iCloud domains are universally trusted by corporate firewalls and endpoint security solutions, they rarely trigger traditional network-level alerts. This makes cloud-abusing malware exceptionally difficult to detect using legacy signature-based defenses, placing a heavier burden on behavioral monitoring and proactive user awareness.

Defensive Recommendations and Best Practices for macOS Users

In light of the evolving capabilities demonstrated by the MacSync malware family, cybersecurity professionals and incident responders strongly urge users to adopt rigorous defensive habits. Chief among these recommendations is avoiding the execution of raw terminal commands found in online forums, social media posts, or unexpected pop-up windows—a primary vector exploited by ClickFix campaigns.

Furthermore, users should exercise extreme caution when downloading disk image (.DMG) files, installers, or software updates from untrusted third-party websites, peer-to-peer networks, or unsolicited social media advertisements. Whenever an application requests administrative password prompts or terminal execution rights, users should independently verify the authenticity of the software vendor. Organizations managing fleets of macOS endpoints are encouraged to deploy modern endpoint detection and response (EDR) solutions capable of monitoring shell behavior, unauthorized modifications to shell configuration files, and abnormal launch agent installations to catch multi-stage threats like MacSync before critical data can be exfiltrated.

September 24, 2026 0 comment
0 FacebookTwitterPinterestEmail
Web3 & DApps

Outlier Ventures and Injective Unveil the Next Cohort of High-Growth Startups for the Ecosystem Builder Catalyst Accelerator

by admin September 24, 2026
written by admin

The modern architecture of decentralized finance (DeFi) is undergoing a profound structural evolution, moving rapidly away from simplistic token-swapping mechanisms toward a sophisticated, institutional-grade financial layer. In response to this paradigm shift, prominent Web3 accelerator Outlier Ventures and Layer-1 blockchain protocol Injective have officially announced the latest cohort of startups selected for the Injective Ecosystem Builder Catalyst.

This intensive 9-week virtual accelerator program has been meticulously engineered to identify, fund, and scale the next generation of visionary founders who are constructing high-growth decentralized applications and core infrastructure natively on the Injective network. As the decentralized economy expands to encompass complex institutional financial instruments, high-performance execution environments have become an absolute necessity. The newly inducted cohort represents a diverse array of financial technology innovators targeting everything from cross-border institutional payments and real-world asset (RWA) tokenization to advanced agentic trading systems and decentralized equity markets.

The Macroeconomic Backdrop: A Maturing DeFi and RWA Landscape

To understand the strategic significance of the Injective Ecosystem Builder Catalyst cohort, one must examine the broader macroeconomic climate of the digital asset industry. The decentralized finance sector has experienced a remarkable resurgence, with Total Value Locked (TVL) hovering near the $140 billion threshold globally. Concurrently, the tokenization of Real-World Assets has emerged as one of the fastest-growing sectors within blockchain technology, scaling by more than 380% since 2022.

Traditional financial institutions, asset managers, and fintech enterprises are no longer viewing blockchain merely as an experimental sandbox. Instead, they are actively seeking high-throughput, low-latency execution environments that can rival—and occasionally surpass—legacy financial rails. Injective has positioned itself at the epicenter of this institutional migration by offering sub-second block finality, gasless transaction capabilities, and robust MultiVM interoperability.

Rather than merely porting legacy financial products onto decentralized ledgers, the founders in this current cohort are designing entirely new financial primitives. Leveraging Injective’s native financial modules, shared liquidity infrastructure, and technical edge, these teams are building systems that combine code, culture, and capital into a unified, highly programmable layer tailored specifically for the financial demands of 2026 and beyond.

Inside the Cohort: Nine Innovative Startups Redefining Digital Finance

The nine selected startups participating in the current 9-week virtual accelerator represent a cross-section of the most forward-thinking builders in the Web3 ecosystem. Each project utilizes Injective’s specialized infrastructure to maximize capital efficiency, reduce friction, and solve complex operational inefficiencies inherent in both traditional and decentralized finance.

9 Startups Selected for the Injective Ecosystem Builder Catalyst: Scaling the DeFi-First Future

1. QuantCite

QuantCite addresses a critical bottleneck for professional traders and quantitative hedge funds: fragmented liquidity. As an institutional-grade Order and Execution Management (OEM) and smart-routing platform, QuantCite unifies trade execution seamlessly across both centralized exchanges and decentralized venues. By providing high-performance infrastructure and deep liquidity access, the platform enables quants to execute complex, multi-venue strategies without suffering from prohibitive slippage or latency issues.

2. Joinn

Focusing on retail financial inclusion, Joinn operates as a fintech application designed to help everyday consumers in emerging markets protect and grow their savings. By granting users access to stable, yield-generating tokenized financial assets through a user-friendly Web2-like interface, Joinn abstracts away the complexities of blockchain interaction. The platform features gasless, signless transactions operating across multiple chains, 24/7 account access, an integrated Visa card experience, and a dedicated AI agent designed to automate and optimize the compounding of yields.

3. Choice

Choice serves as a specialized decentralized exchange (DEX) and aggregation layer optimized natively for the Injective network. By deploying a proprietary, advanced routing algorithm that taps into aggregate liquidity pools across diverse venues, Choice ensures that retail and institutional traders alike receive optimal swap execution with minimized price impact and reduced slippage.

4. Stabled

Targeting international trade and corporate treasury management, Stabled is an enterprise-grade cross-border payments platform. It enables businesses to execute compliant stablecoin transactions instantly, bypassing traditional correspondent banking networks entirely. By eliminating legacy intermediaries, Stabled significantly reduces foreign exchange (FX) losses and removes the multi-day settlement delays that traditionally plague international commerce.

5. Quantum Street

Quantum Street brings decades of capital markets and financial engineering expertise directly onto the blockchain. The team specializes in structuring transactions for cash-flowing businesses, effectively bridging off-chain assets into on-chain formats. By doing so, Quantum Street creates genuine, revenue-backed utility for stablecoins while actively contributing to the expansion of decentralized finance Total Value Locked (TVL).

6. Spout

Spout introduces an innovative approach to equity markets by enabling the seamless borrowing and lending of tokenized U.S. public equities. Utilizing a Collateralized Debt Position (CDP) model, Spout allows users to access 0% APR margin loans while simultaneously providing lenders with competitive approximate yields of around 10% APY, thereby bridging traditional equity markets with decentralized liquidity.

7. Dapps.co

Recognizing the economic pressures faced by digital content creators in the modern media landscape, Dapps.co has developed a Web3-native social network designed to restore financial agency to creators. The platform utilizes tokenized communities and on-chain economies, complemented by an advanced AI provenance layer engineered to combat low-quality generated content. Creators can monetize their work directly through native tipping mechanisms and paid direct messaging channels.

9 Startups Selected for the Injective Ecosystem Builder Catalyst: Scaling the DeFi-First Future

8. Chain Capital

Chain Capital addresses the massive illiquid private debt market by transforming traditional debt instruments into tradeable securities. Through the tokenization of corporate invoices and receivables, Chain Capital automates the end-to-end securitization workflow. This automation reduces traditional middle-office administrative costs by up to 75% while offering institutional investors a compliant, streamlined pathway to high-yield asset exposures.

9. HodlHer

Positioned at the intersection of artificial intelligence and decentralized systems, HodlHer introduces an AI-driven Web3 operating system built natively on Injective. Utilizing unique, intelligent AI personas, the platform assists individual users, creators, and project teams in navigating the complete lifecycle of on-chain operations—moving fluidly from market perception and analytical reasoning to automated transaction execution.

Program Structure, Mentorship, and the Road Ahead

The Injective Ecosystem Builder Catalyst is structured to provide these early-stage teams with comprehensive, hands-on support far beyond simple capital allocation. Over the course of the intensive nine-week program, founders receive specialized mentorship from industry veterans, rigorous legal and regulatory guidance, and direct access to ecosystem incentive programs designed to accelerate market entry and user acquisition.

Leadership from both Outlier Ventures and Injective emphasize that the ultimate objective of this cohort is not merely to increase the sheer volume of digital assets in circulation, but to enhance system fit, interoperability, and composability. Injective’s technical architecture offers functional parity with traditional finance (TradFi) order books and sophisticated collateral management systems, while simultaneously unlocking financial engineering strategies that remain entirely impossible within legacy banking frameworks.

As these startups refine their products and stress-test their infrastructures, the broader digital asset community anticipates their public debuts. The accelerator program will culminate in the highly anticipated Injective Ecosystem Builder Catalyst Demo Day, scheduled for February 25, 2026. This showcase event will provide founders with a direct platform to present their innovations to leading venture capitalists, angel investors, and strategic partners from across the global financial technology ecosystem. Industry observers and prospective participants can register for the upcoming Demo Day via the official Outlier Ventures Luma portal.

September 24, 2026 0 comment
0 FacebookTwitterPinterestEmail
Tech & Startup News

A rice farmer in the Philippines diagnosed with neuroschistosomiasis after experiencing sudden neurological tremors

by admin September 22, 2026
written by admin

The sudden onset of localized physical tremors in a seemingly healthy individual often signals an underlying systemic issue, yet few diagnoses are as unexpected as the one recently documented in the New England Journal of Medicine. A rice farmer residing in the rural Philippines presented to an emergency department after experiencing a terrifying, minute-long episode of involuntary, violent shaking in her right arm and leg. Despite the severity of the tremors, the patient remained conscious, displayed no cognitive confusion, and suffered no headaches or generalized weakness. This clinical presentation, characterized by focal motor seizures, prompted an immediate and thorough neurological investigation.

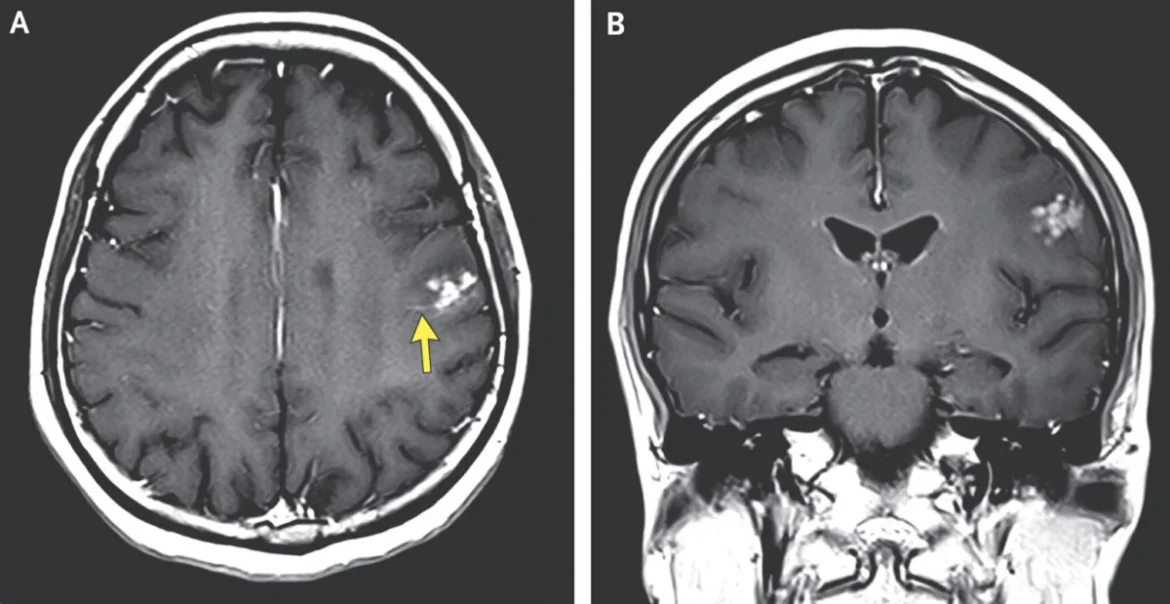
Following a standard physical examination that yielded unremarkable results, clinicians turned to advanced diagnostic imaging to uncover the source of the patient’s distress. Magnetic resonance imaging (MRI) of the brain revealed a cluster of bright, fluid-filled nodules localized within the left frontal lobe. The clinical team quickly identified these lesions as the hallmark of a rare but dangerous parasitic infection: neuroschistosomiasis, a cerebral complication stemming from the blood fluke Schistosoma japonicum.

The Pathological Timeline and Transmission

Schistosomiasis is a neglected tropical disease caused by parasitic flatworms. While the adult worms typically reside in the blood vessels surrounding the intestines or the liver, the migration of eggs can occasionally deviate from this path, leading to ectopic infections in the central nervous system. In this specific case, the patient’s occupation as a rice farmer provided the critical epidemiological link. The lifecycle of S. japonicum is intricately tied to freshwater environments, where the larvae thrive in irrigation systems, rice paddies, and canals.

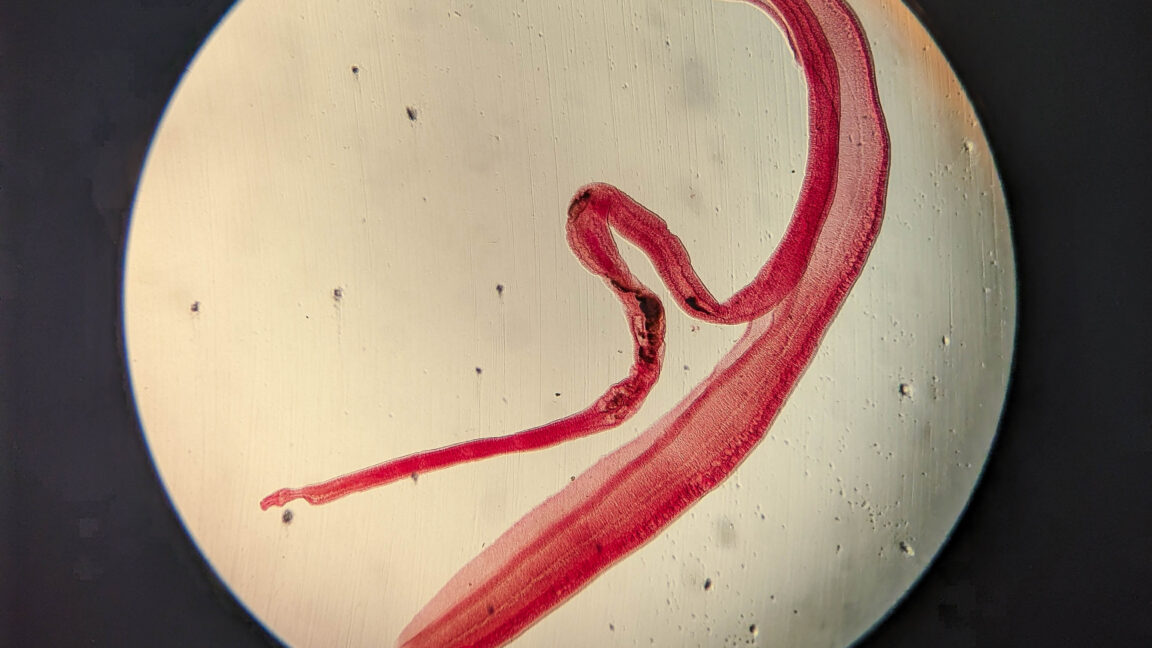
The infection process begins when eggs are shed into water sources through human or animal waste. These eggs hatch into miracidia, which must locate a specific intermediate host—an amphibious snail of the genus Oncomelania. Within the snail, the parasite undergoes significant asexual reproduction, eventually releasing thousands of cercariae—free-swimming, fork-tailed larvae—into the water. These cercariae possess the ability to penetrate intact human skin upon contact. Once inside the human host, they migrate through the circulatory system, passing through the lungs and heart before maturing into adult worms in the venous system of the abdomen.

The presence of these worms in the brain is an aberrant, yet well-documented, clinical anomaly. When the worms or their eggs deposit in the cerebral vasculature, they provoke an inflammatory response, leading to the formation of granulomas—the "bright nodules" observed in the MRI. These granulomas can exert pressure on the surrounding brain tissue, triggering focal seizures like those experienced by the patient.

Epidemiological Context of S. japonicum

The distribution of Schistosoma japonicum is geographically specific. While it has been successfully eradicated from Japan, the parasite remains endemic across large swaths of the Philippines, China, and parts of Indonesia. According to the World Health Organization (WHO), schistosomiasis affects more than 250 million people globally, with the vast majority of cases occurring in sub-Saharan Africa. However, the specific strain found in Southeast Asia presents unique challenges due to its wide range of animal reservoirs, including cattle, water buffalo, and pigs, which makes the cycle of transmission difficult to break.

In the Philippines, public health efforts have focused on mass drug administration (MDA) of praziquantel, the standard treatment for the infection. Despite these efforts, the persistence of the disease in agricultural communities remains a significant burden. The case reported in the New England Journal of Medicine serves as a stark reminder that even in regions where public health infrastructure exists, the risk of occupational exposure remains high for those working in flooded, contaminated environments.

Woman's brain worm infection confirmed after eggs grow tails in lab test

Clinical Management and Diagnostic Challenges

The medical team managing the rice farmer’s case faced a complex diagnostic path. Because the patient presented with no systemic symptoms—such as fever, eosinophilia, or abdominal pain, which are more common indicators of systemic schistosomiasis—the diagnosis was entirely dependent on neuroimaging. The identification of granulomas in the left frontal lobe necessitated a differential diagnosis that included brain tumors, tuberculosis, and neurocysticercosis (a tapeworm infection often mistaken for schistosomiasis).

The specific "nodular" appearance of the lesions, combined with the patient’s history of living and working in an endemic area, allowed clinicians to narrow their focus to S. japonicum. Neuroschistosomiasis is historically associated with higher morbidity rates if left untreated, as the chronic inflammation can lead to permanent neurological deficit or progressive intracranial pressure. The immediate administration of anti-parasitic medication, often paired with corticosteroids to reduce the inflammatory response surrounding the brain lesions, is the standard clinical approach.

Broader Implications for Public Health

This case highlights the ongoing necessity for surveillance and education in endemic agricultural sectors. While the patient was treated, her experience reflects a larger reality for millions of rural workers whose livelihoods depend on water-based agriculture. The intersection of environmental conditions and human behavior creates a high-risk scenario that is notoriously difficult to regulate.

Experts in tropical medicine emphasize that while neuroschistosomiasis is a "rare" complication, it is likely underreported. Patients in remote areas who experience single-episode seizures may not seek tertiary care or may be misdiagnosed with idiopathic epilepsy. The availability of advanced imaging, such as MRI, is often limited in the very areas where S. japonicum is most prevalent, creating a diagnostic gap that hinders accurate data collection and treatment.

Furthermore, the environmental impact of climate change and irrigation expansion may alter the habitats of the Oncomelania snail, potentially shifting the zones of transmission. Public health officials are now looking at integrated approaches that include not only the treatment of the human population but also the management of animal reservoirs and the modification of agricultural practices to reduce snail habitats.

Conclusion and Future Outlook

The case of the Philippine rice farmer is a poignant example of the complexities of global health in the 21st century. It underscores the vital role of specialized medical reporting in identifying rare complications that might otherwise be overlooked. As the international medical community continues to refine the treatment of parasitic diseases, the focus must remain on the intersection of human activity and environmental biology.

For the patient, the prognosis remains dependent on the success of the anti-inflammatory and anti-parasitic treatment in shrinking the granulomas and preventing further seizure activity. For the global health community, the case serves as a call to action: to improve diagnostic accessibility in rural settings and to continue the rigorous pursuit of environmental control measures that can protect agricultural workers from the unseen dangers lurking in their own fields. The "unfortunate fluke" of this infection, while medically fascinating, remains a tangible threat that requires ongoing vigilance, scientific investment, and sustained public health commitment. As research continues to advance, the goal remains clear: to ensure that the risks associated with essential agricultural labor are mitigated through science-led policy and improved medical literacy in endemic regions.

September 22, 2026 0 comment
0 FacebookTwitterPinterestEmail
Tech & Startup News

ShinyHunters claims it stole FBI employee data. Here’s what we know.

by admin September 22, 2026
written by admin

The landscape of federal cybersecurity was severely shaken as the notorious cybercrime syndicate known as ShinyHunters claimed responsibility for one of the most brazen data breaches in recent history, asserting that it successfully infiltrated the systems of the Federal Bureau of Investigation (FBI). The group’s primary objective, according to multiple cybersecurity reports and statements released by the hackers, is not financial extortion, but rather a direct retaliation against the bureau for public advisories issued earlier this year.

The unfolding crisis has raised critical questions regarding the vulnerability of federal digital infrastructure, the security of sensitive government personnel data, and the escalating aggression of elite cybercriminal organizations operating globally. As federal investigators scramble to verify the legitimacy of the breach, the potential ramifications extend far beyond a bureaucratic feud, posing severe security risks to thousands of government workers and their families.

The Genesis of the Conflict and the FBI Advisory

To understand the current standoff between ShinyHunters and the FBI, it is necessary to examine the events of May 2026. On May 15, the FBI’s Internet Crime Complaint Center (IC3) published a comprehensive public service announcement warning American institutions and organizations about an aggressive cybercriminal collective utilizing extortion tactics, harassment, and severe digital intimidation.

ShinyHunters says it stole FBI employee data. Here’s what we know.

The advisory specifically highlighted the methodologies of ShinyHunters, accusing the group of launching devastating cyberattacks on learning management systems and educational infrastructure, which subsequently disrupted schools and students nationwide. Furthermore, the FBI’s public warning detailed the psychological and physical tactics allegedly employed by the syndicate to pressure victims into paying ransoms. These tactics included persistent threatening phone calls, targeted harassment campaigns directed at victims and their families, and "swatting"—the dangerous practice of making false emergency calls to dispatch heavily armed police units to a target’s residential address.

Rather than remaining silent or absorbing the blow to their reputation, ShinyHunters chose to push back aggressively. The syndicate disputed the characterizations made in the FBI’s Flash report, claiming that the bureau’s advisory contained substantial false allegations and exaggerated descriptions of their operations. Setting a strict one-week ultimatum, the group demanded that FBI Director Kash Patel and Brett Leatherman, the assistant director of the FBI’s cyber division, formally retract or correct the statements made in the May advisory. To prove the validity of their threats, ShinyHunters escalated from verbal pushback to direct cyber warfare against the federal law enforcement agency itself.

The Mechanics of the Alleged Breach: Exploiting PeopleSoft

According to details provided by the hacking collective to prominent cybersecurity journalists and intelligence researchers, the breach was initiated through a targeted exploitation of the FBI’s job application portal, specifically the recruitment website FBIjobs.gov.

ShinyHunters asserted that they leveraged a zero-day vulnerability—a critical, previously unknown software flaw—embedded within Oracle PeopleSoft software utilized by the platform. By exploiting this unpatched vulnerability, the hackers claimed they were able to bypass standard authentication protocols and execute unauthorized commands directly on the host servers without requiring prior login credentials.

ShinyHunters says it stole FBI employee data. Here’s what we know.

Once inside the recruitment infrastructure, the threat actors allegedly pivoted to compromise FBI-managed servers hosted on Amazon Web Services (AWS) GovCloud. The syndicate claims to have siphoned between two and three terabytes of highly sensitive government data. Among the specific internal services reportedly compromised in the sweep are human resources databases, the MedLink system, and the Criminal Justice Information Services (CJIS) division, though the full extent of the penetration remains unconfirmed by independent technical audits.

The recruitment website itself visibly reflected the disruption. Screenshots captured by technology observers showed the FBI careers landing page displaying a "System Unavailable" banner. The message stated that Apply.fbijobs.gov and the Special Agent Applicant Portal were temporarily offline, hovering ominously above the agency’s standard recruitment slogan, "Set Yourself Apart."

Verification Efforts and Cybersecurity Analysis

In the wake of the claims, cybersecurity experts, open-source intelligence (OSINT) specialists, and investigative media outlets rushed to analyze the validity of the data samples provided by ShinyHunters.

To substantiate their claims, the group supplied 404 Media with a data sample purportedly containing personal identifiable information (PII) belonging to approximately 5,000 current FBI employees and prospective job applicants. The compromised data fields allegedly included full legal names, private home addresses, personal telephone numbers, dates of birth, and, in several instances, biographical details concerning the spouses and family members of the personnel.

ShinyHunters says it stole FBI employee data. Here’s what we know.

Investigative researchers employed OSINT Industries—an advanced open-source intelligence verification platform—to cross-reference the telephone numbers contained within the leaked sample. The analysis revealed that numerous phone numbers actively corresponded to the names of individuals listed alongside them. Furthermore, secondary checks utilizing Darkside, a specialized tool designed to search through historical databases of previously compromised credentials and corporate leaks, successfully linked several of the targeted phone numbers directly to personnel working within the United States Department of Justice.

Despite these alarming indicators, professional cybersecurity firms have urged caution regarding the completeness of ShinyHunters’ technical narrative. In a detailed post-incident analysis published by CyPro, researchers pointed out that the syndicate’s public statements lacked the rigorous technical disclosures typically required to independently verify a complex enterprise software exploit. Specifically, ShinyHunters failed to publicly identify a specific Common Vulnerabilities and Exposures (CVE) reference number, a precise PeopleSoft component, specific exploit request strings, or affected product version configurations. Furthermore, cybersecurity analysts noted that public reporting has yet to fully explain how the attackers successfully bridged the gap from the public-facing recruitment portal into highly secure internal AWS GovCloud environments.

A Pattern of Escalation: Recent Campaign History

The alleged FBI hack does not exist in a vacuum; rather, it is part of an aggressive, high-profile escalation by ShinyHunters across the global threat landscape throughout the autumn of 2026.

The group’s operational tempo has accelerated dramatically over the summer. In June, threat intelligence researchers at Google published a comprehensive report detailing a coordinated ShinyHunters campaign specifically targeting the education sector by weaponizing vulnerabilities within Oracle software products.

ShinyHunters says it stole FBI employee data. Here’s what we know.

More recently, on September 18, ShinyHunters executed a stunning power play within the cybercrime underworld by completely hijacking the official leak website of Cl0p, a rival and notorious ransomware gang. To rub salt in the wound, the syndicate plastered an eight-figure ransom demand across the hijacked portal, accompanied by a mock law enforcement seizure notice. This exact tactic—deploying fake federal seizure banners—was mirrored just days later when they defaced portions of the FBI’s online recruitment apparatus.

This aggressive branding and willingness to cross swords with both rival criminal syndicates and the world’s most powerful law enforcement agency underscore a significant shift in ShinyHunters’ operational posture. Moving away from purely financially motivated corporate extortion, the group appears increasingly driven by notoriety, ego, and ideological defiance against state-sponsored cybersecurity enforcement.

Broader Implications and National Security Fallout

The potential exposure of sensitive FBI employee data carries profound national security implications that stretch far beyond the immediate public relations embarrassment for the bureau.

If the stolen dataset is proven to be authentic and comprehensive, the personal exposure of federal law enforcement officers, special agent applicants, and their immediate families creates severe operational and safety vulnerabilities. Home addresses and private phone numbers in the hands of malicious actors—ranging from domestic criminal enterprises and extremist networks to hostile foreign intelligence services—provide a direct avenue for harassment, physical intimidation, surveillance, and targeted cyber-espionage against the very individuals tasked with upholding national security.

ShinyHunters says it stole FBI employee data. Here’s what we know.

Furthermore, this incident compounds a difficult year for the bureau’s digital defenses. The latest breach follows a high-profile security lapse in March, when Iran-linked hackers successfully compromised the personal email account of FBI Director Kash Patel, subsequently publishing historical photographs and documents online. While the DOJ and FBI maintained at the time that the compromised material contained no classified government secrets, the recurrence of high-level digital intrusions points to systemic challenges in securing the personal and professional digital footprints of top federal officials.

Official Response and the Path Forward

In an official statement responding to inquiries from technology publications like PCMag, the FBI acknowledged the unfolding situation: "The agency is aware of claims regarding unauthorized activity affecting FBIjobs.gov and is currently investigating."

Federal incident response teams, alongside cybersecurity contractors and cloud infrastructure partners, are working around the clock to audit affected servers, patch vulnerabilities, and determine the exact volume of data exfiltrated during the attack. Meanwhile, the bureau faces a difficult balancing act: managing an active criminal investigation into a defiant hacker collective while reassuring its workforce—and the broader public—that federal data infrastructure remains resilient against determined state and non-state adversaries.

As the one-week ultimatum issued by ShinyHunters ticks down, the immediate future remains uncertain. For the thousands of federal employees and job applicants whose private lives may now be exposed on dark web forums, the primary concern is no longer the political posturing between a cybercrime syndicate and federal law enforcement, but the very personal reality of securing their homes, families, and digital identities in the wake of an unprecedented breach.

September 22, 2026 0 comment
0 FacebookTwitterPinterestEmail
Artificial Intelligence & Tech

Bridging the Digital Divide: How AI Is Enabling Global Communication in Over 300 Languages

by admin September 22, 2026
written by admin

In a significant milestone for global digital equity, technology platforms now support over 300 languages, facilitating interactions for more than 7 billion people—a figure that accounts for approximately 86% of the world’s population. This achievement marks a critical shift in the evolution of artificial intelligence, moving away from a historically Western-centric focus toward a more inclusive, multilingual digital ecosystem. For decades, the digital world was largely confined to a handful of dominant languages, creating an exclusionary environment for thousands of dialects and lesser-represented languages. Today, the integration of advanced AI is systematically dismantling these barriers, aiming to ensure that technology understands the nuance, cultural context, and diverse modes of human expression.

The History of Language Technology: From Early Translation to Native AI

The journey toward global language inclusivity began in earnest in 2006 with the launch of Google Translate. At the time, the objective was straightforward: to provide a basic, functional bridge between speakers of different languages. While that initial service paved the way for cross-lingual communication, it relied on traditional machine translation models that often struggled with idiomatic expressions, cultural references, and the fluidity of spoken language.

For many years, the standard architecture for speech recognition followed a rigid, multi-step pipeline: converting audio to text, processing that text through a translation engine, and then synthesizing it back into audio. This method, while functional, often failed to capture the essence of human interaction. It stripped away essential components of communication—tone, pacing, emotional variance, and the messy, authentic reality of human speech. Human beings rarely speak in perfect, grammatical sentences; we laugh, interrupt, hesitate, and frequently weave multiple languages together, such as the common practice of speaking Spanglish or Hinglish.

Recognizing the limitations of text-based translation, researchers have shifted toward native audio intelligence. By training advanced models like Gemini to process audio directly, developers are now able to grasp both the acoustic properties of sound and the underlying intent of the speaker. This transition represents a fundamental change in AI development: the recognition that language is not merely a collection of words, but a sophisticated, culturally sensitive medium that requires a deeper, more empathetic computational approach.

Data Sovereignty and Local Partnerships

A primary challenge in training AI to understand diverse languages is the inherent bias in the data available on the web, which disproportionately favors dominant languages like English, Spanish, and Mandarin. To address this, the industry has shifted toward local, grassroots partnerships. This strategy prioritizes data sovereignty, ensuring that the languages are represented by the communities that actually speak them, rather than by external entities.

These open-data partnerships have paved the way for ambitious projects such as LinguaMeta, currently the world’s largest open-source language data repository. By mapping over 7,000 spoken, written, and signed languages, this project provides a foundation for developers worldwide to build tools that are linguistically accurate and culturally respectful. These efforts have received external recognition, including design innovation accolades, underscoring the importance of mapping the full spectrum of human language.

The impact of these initiatives is most visible when deployed in practical, community-facing roles. Projects like the Centre for Digital Language Inclusion and AI Singapore’s Project Aquarium represent a new wave of localized AI. By providing multilingual tools to farmers, healthcare workers, and educators in their native tongues, these organizations are ensuring that AI is not just a high-level research curiosity, but a functional utility that improves lives and provides access to information that was previously locked behind a language barrier.

Addressing Infrastructure Constraints in the Global South

Technological progress is only as impactful as its accessibility. Despite the rapid expansion of mobile technology, more than 3 billion people still lack reliable, high-speed internet access. For these populations, standard cloud-based AI models are ineffective. To bridge this digital divide, developers have introduced lightweight, on-device translation models, such as TranslateGemma. By running these models locally on hardware, users can benefit from high-quality translation without the need for constant, stable connectivity.

However, even lightweight models require hardware capable of running them, which poses a barrier for the hundreds of millions of people who still rely on basic feature phones. In regions like sub-Saharan Africa, where feature phones remain the primary communication tool, innovation has taken a different route. By partnering with organizations like Viamo, developers have launched services such as "Ask Viamo Anything" (AVA). This voice-based AI assistant leverages Gemini to answer queries via standard interactive voice response (IVR) systems. The success of this pilot in Rwanda, where it has already processed over 2 million queries, demonstrates that even in low-resource environments, voice-first AI can provide immediate, life-changing access to information.

Designing for Universal Accessibility

True inclusivity requires looking beyond regional dialects to accommodate the diverse ways humans communicate, including those with non-standard speech. Conventional speech-to-text tools have historically struggled to understand individuals with speech impairments, often forcing the user to adapt their behavior to the machine. This is being rectified through a design-first approach that prioritizes accessibility.

A notable advancement in this field is Sign Language-to-Text (SL2T) technology. With over 70 million people worldwide relying on sign language, the integration of SL2T into platforms like Gboard and live transcription services marks a significant milestone. By training these models on over 50 different sign languages, developers are finally moving toward a reality where digital platforms are as accessible to the deaf and hard-of-hearing community as they are to the hearing population.

The Importance of Cultural Nuance

Beyond functional translation, AI must also respect cultural identity. A recurring issue in navigation and mapping technology has been the mispronunciation of local landmarks, streets, and towns. While this may seem like a minor inconvenience, it effectively erases the cultural heritage of a place. By working directly with local experts—such as the collaboration with Māori language speakers in New Zealand to refine place-name pronunciations in Google Maps—tech companies are demonstrating that cultural sensitivity is a necessary component of technical development. When AI models incorporate authentic local pronunciations, they cease to be "foreign" tools and instead become reflections of the heritage of the communities they serve.

Broader Implications and Future Outlook

The scale of this progress is substantial. Today, AI-powered language tools are embedded across major ecosystems, including Search, Android, Chrome, and YouTube, connecting more than five billion users across multiple platforms. However, the future of this field lies in moving beyond the metrics of scale and focusing on the metrics of depth.

The implications for global commerce, education, and social equity are profound. As AI models become better at grasping context and respecting cultural differences, the barrier to participating in the global digital economy will continue to lower. For a teacher in a remote region, having access to educational materials in their own language, or for a farmer to receive real-time weather data and agricultural advice in a local dialect, the divide between the "connected" and "disconnected" will shrink.

As we look toward the next decade of development, the priority must remain on transparency, open data, and the continuous involvement of local communities. The objective is to build a digital architecture that does not force users to assimilate into a singular, dominant global culture, but rather one that expands the spectrum of human expression. By treating every language as an essential part of the global collective, the technology sector is finally working toward a promise made long ago: that the power of information should be accessible to everyone, everywhere, on their own terms. The ongoing collaboration between AI researchers, linguists, and grassroots organizations will be the defining factor in determining whether this digital future is truly inclusive, or simply a more efficient version of the same exclusionary past.

September 22, 2026 0 comment
0 FacebookTwitterPinterestEmail
Newer Posts
Older Posts

Recent Posts

  • The Evolution of the Web3 Wallet: From Private-Key Vault to the Command Center of the Agentic Web
  • Ethereum Foundation Announces Annual Protocol AMA Session Scheduled for September 16
  • Kraken Expands Its Digital Asset Offerings with the Official Listing of Doppler Finance (Xdp)
  • CSD BR and Ripple Collaborate to Integrate XRP Ledger into Brazilian Financial Market Infrastructure
  • Web3 Venture Funding Surges to Record $22 Billion in Third Quarter 2025 Driven by Institutional Adoption

Recent Comments

No comments to show.
  • Facebook
  • Twitter

@2021 - All Right Reserved. Designed and Developed by PenciDesign


Back To Top
Dr Crypton
  • Home
  • About Us
  • Contact Us
  • Cookies Policy
  • Disclaimer
  • DMCA
  • Privacy Policy
  • Terms and Conditions

We are using cookies to give you the best experience on our website.

You can find out more about which cookies we are using or switch them off in .

Dr Crypton
Powered by  GDPR Cookie Compliance
Privacy Overview

This website uses cookies so that we can provide you with the best user experience possible. Cookie information is stored in your browser and performs functions such as recognising you when you return to our website and helping our team to understand which sections of the website you find most interesting and useful.

Strictly Necessary Cookies

Strictly Necessary Cookie should be enabled at all times so that we can save your preferences for cookie settings.