• Home
  • About Us
  • Contact Us
  • Cookies Policy
  • Disclaimer
  • DMCA
  • Privacy Policy
  • Terms and Conditions
Dr Crypton
Secure Your Future in Crypto
NFT & Digital Assets

The Return to Artistic Provenance: Why the Argonauts Mint Signals a Fundamental Shift in the NFT Market

by admin September 25, 2026
written by admin

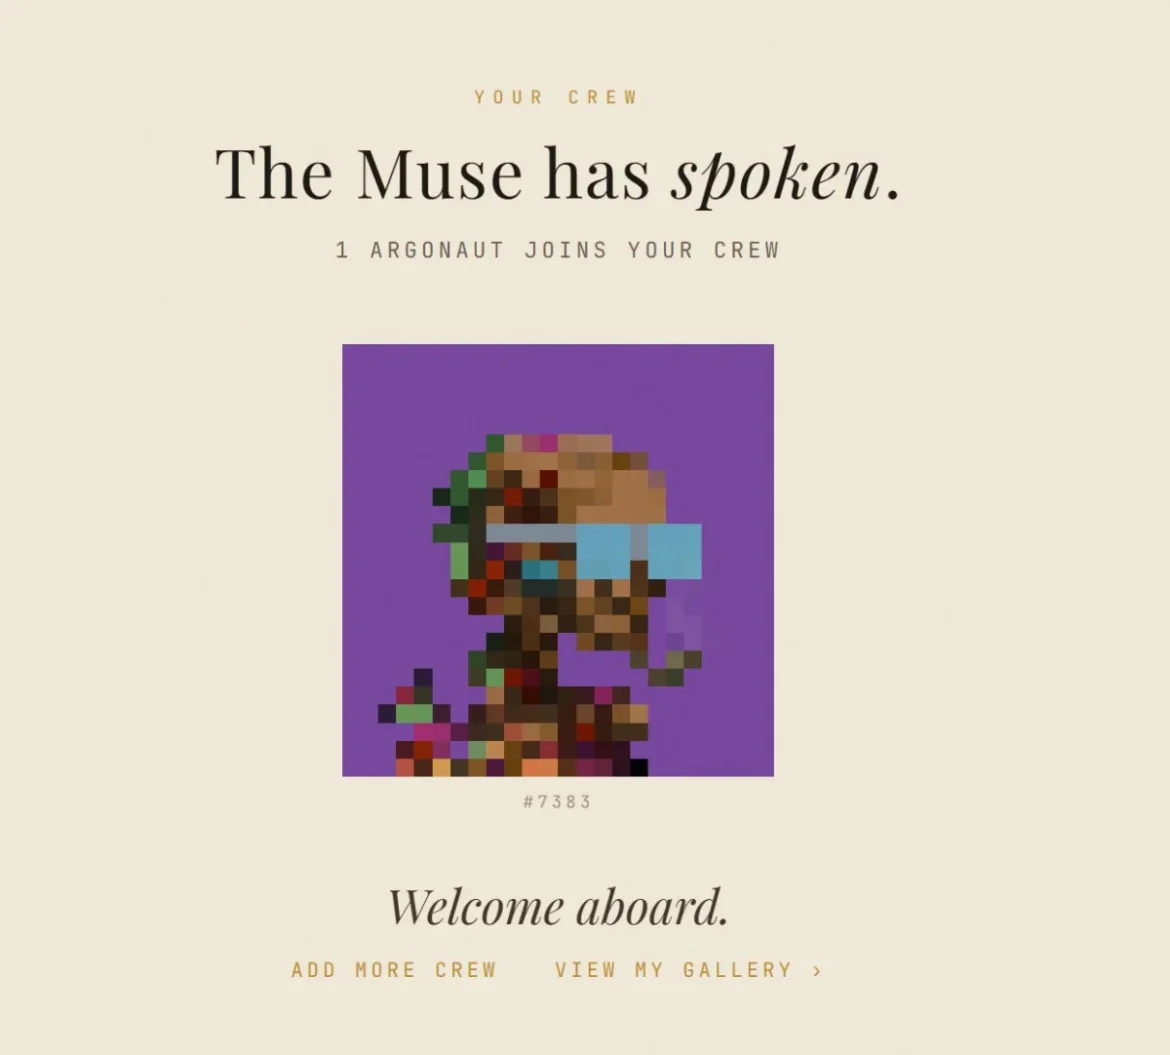
Today, the digital art community witnessed a significant milestone as Argonauts, the latest 10,000-piece collection by the crypto-native artist a.c.k. (@lphaCentauriKid), successfully minted out in a matter of minutes. Priced at approximately 0.12 ETH—roughly $300 at the time of transaction—the collection did not rely on the high-pressure sales tactics or the promise of extensive, vaporware-heavy "utility" that characterized the NFT market during the 2021-2022 speculative cycle. Instead, the rapid sell-out of Argonauts provides a compelling data point suggesting that the market for digital collectibles is undergoing a structural evolution, favoring artistic reputation and provenance over financial engineering.

The Mechanics of the Mint

The minting process for Argonauts was characterized by a steady, organic inflow of participants rather than the chaotic "gas wars" that once defined high-profile NFT drops. By setting a accessible mint price of 0.12 ETH, a.c.k. strategically lowered the barrier to entry for long-term collectors who had previously been priced out of the artist’s primary market, which typically consists of exclusive 1/1 digital works.

This decision to utilize a large-scale, accessible format represents a departure from the "whale-only" model that often limits the reach of high-end digital artists. By distributing 10,000 pieces, the artist effectively democratized ownership of his visual language, allowing a broader segment of the community to hold a stake in his body of work. The speed at which these tokens were claimed suggests that demand for high-quality, artist-led projects remains robust, even as the broader NFT ecosystem faces continued scrutiny and consolidation.

Chronology of a Shift

To understand the significance of this event, one must look at the trajectory of the NFT market over the last three years. In 2021, the market was defined by a rapid proliferation of generative collections, many of which were managed by teams with no prior artistic history. These projects frequently bundled art with elaborate "roadmaps" involving tokenomics, staking mechanisms, and promises of virtual real estate.

By 2023, the consequences of this model became apparent. As market liquidity tightened, projects that lacked fundamental artistic value or a clear creative vision struggled to maintain their floor prices. Conversely, artists who had been building consistent, long-term bodies of work—such as a.c.k.—began to see their reputations solidify. The Argonauts mint is the culmination of this maturation period. It follows a series of successful, artist-centric releases across the industry that have signaled a return to the medium’s original value proposition: the ability to own and verify digital provenance.

Data-Driven Analysis of Collector Behavior

Analysis of on-chain data surrounding the Argonauts launch reveals a distinct profile of the participating collectors. Rather than the transient, profit-seeking traders that dominated the previous cycle, the wallet addresses involved in this mint show a high degree of overlap with established art collectors and creators within the crypto-native space.

This phenomenon—"artists collecting artists"—is a critical indicator of a healthy, sustainable ecosystem. When a market is driven by creators, the value proposition is rooted in the history of the work rather than the expectation of a short-term secondary market flip. Data from major marketplaces indicates that the distribution of tokens in the Argonauts collection is widespread, suggesting that the supply has been absorbed by a committed base of supporters rather than concentrated in a few high-volume wallets. This decentralization of ownership is historically associated with lower volatility and longer-term asset retention.

The Role of Provenance and Artist Reputation

At the heart of the Argonauts success is the reputation of a.c.k. as a foundational figure in crypto-art. His visual language, which has been refined through years of digital creation, provides the project with an inherent narrative that does not require external marketing or "utility" fluff. In the art world, provenance is the history of ownership and the verified origin of a work; in the digital realm, blockchain technology provides this automatically.

The current market environment has become increasingly skeptical of projects that promise to "build" their way to value. Investors have shifted their focus toward "proven" entities—artists who have demonstrated a commitment to their craft over multiple years and through various market conditions. By leaning into this reality, a.c.k. has bypassed the need for manufactured hype, proving that artistic integrity remains the most reliable driver of demand in the NFT space.

Broader Implications for the NFT Industry

The implications of the Argonauts mint extend beyond the success of a single collection. If the market continues to prioritize art over utility-based gimmicks, the next phase of NFT development may look significantly more like the traditional fine art market than the tech-startup landscape of the past.

Industry analysts observe that this shift represents a return to the "Original Promise" of NFTs: providing a mechanism for digital artists to distribute their work directly to a global audience, with the added benefit of permanent, immutable ownership. When tokens are treated as digital assets rather than financial derivatives, the entire ecosystem benefits. The "community" surrounding such a project becomes a group of stakeholders interested in the preservation and appreciation of the artist’s work, rather than a cohort of speculators looking for an exit.

Reactions and Industry Sentiment

While no formal press release was issued by the artist regarding the sell-out, social media sentiment from prominent collectors and fellow artists has been overwhelmingly positive. The discourse has centered on the "health" of the mint, with many participants noting that the absence of artificial scarcity or complex mechanics was a refreshing change of pace.

Critics of the NFT space have long argued that the technology lacks a "use case" beyond speculation. Projects like Argonauts effectively counter this argument by demonstrating that the technology is, in itself, the utility. The ability to own a verified, immutable piece of an artist’s catalog is the functional purpose of the NFT. By focusing on this core capability, a.c.k. has effectively stripped away the layers of noise that have distracted the market for years.

Conclusion: A Path Toward Maturity

The success of Argonauts is not merely a financial achievement; it is a cultural signal. It indicates that the NFT market is entering a phase of maturity where artistic quality is once again the primary currency. For collectors, this means a shift away from the high-risk, high-volatility speculative environment of the past toward a more considered approach to building a digital collection.

For artists, the lesson is clear: the most sustainable path forward is one that prioritizes the work itself. By fostering deep, authentic relationships with a dedicated collector base, artists can insulate themselves from the boom-and-bust cycles that have plagued the sector. If the trajectory set by the Argonauts mint continues, the coming years could see a resurgence in high-quality digital art, characterized by sustained interest, stable ownership, and a renewed focus on the creative potential of the blockchain.

Ultimately, the market is not necessarily shrinking; it is refining. The participants in today’s mint have signaled that they are no longer interested in the "promises" of the past. They are interested in art, they are interested in the artist, and they are interested in the future of digital provenance. In that sense, the Argonauts collection serves as a blueprint for the next era of NFTs—an era where the art is the utility, and the community is built on the shared appreciation of digital creation. The industry, it seems, is finally coming home.
September 25, 2026 0 comment
0 FacebookTwitterPinterestEmail
Tech & Startup News

Early October Prime Day Discounts Bring Rare Savings to DJI Osmo Pocket 3 Creators and Videographers

by admin September 25, 2026
written by admin

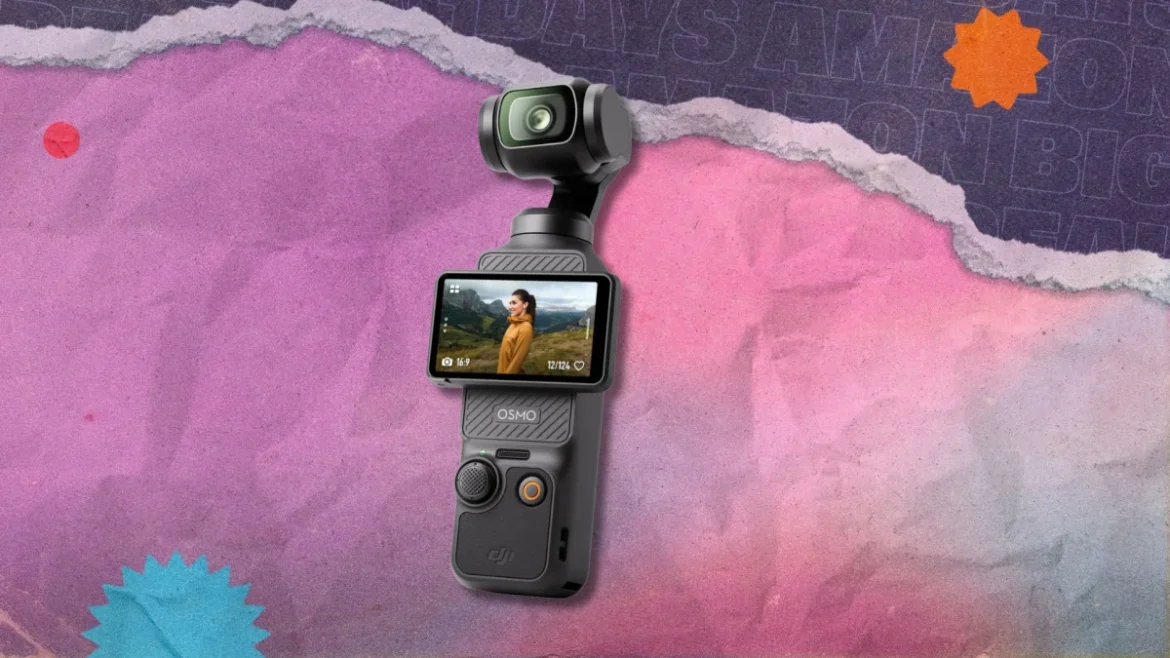
The retail landscape ahead of the upcoming autumn shopping events has begun to yield notable price reductions, highlighted by a significant discount on one of the most sought-after portable content creation tools on the market. As of late September, major online retailers, led by Amazon, have slashed the price of the DJI Osmo Pocket 3 to $439, down from its standard retail price of $499. This 12% markdown represents a $60 savings for consumers looking to upgrade their mobile videography kits without waiting for the official commencement of Amazon’s October Prime Day, which is scheduled to kick off on October 6.

While seasonal shopping events traditionally drive intense consumer activity during a compressed window in mid-autumn, modern e-commerce trends have increasingly shifted toward early-bird promotions. Retailers frequently introduce preliminary discounts days or even weeks prior to major tentpole sales to capture early demand, smooth out logistics, and secure consumer commitments before competitors can counter. For creators, vloggers, and independent journalists, these early-window markdowns provide a strategic opportunity to acquire high-demand hardware away from the frenetic rush and potential stock depletion of the official event days.

Technological Evolution and Core Specifications

The DJI Osmo Pocket 3 occupies a unique niche in the digital imaging ecosystem, bridging the gap between high-end professional cinema cameras and the ubiquitous convenience of smartphone video capture. Released to critical acclaim within the creator community, the device was engineered to address the persistent limitations of mobile journalism and handheld vlogging: stabilization, low-light performance, and quick deployment.

At the core of the Osmo Pocket 3 is a robust 1-inch CMOS sensor, a substantial hardware upgrade from previous iterations that significantly enhances light collection and dynamic range. This larger sensor allows the device to capture pristine 4K video at up to 120 frames per second, catering directly to videographers who require high-frame-rate slow-motion capabilities for dynamic action shots, sweeping landscapes, or moody nocturnal scenes.

Physical versatility remains a hallmark of the hardware. The camera features a rotating 2-inch touchscreen interface, a thoughtful design choice that enables users to effortlessly transition between traditional horizontal (landscape) shooting and vertical framing optimized for platforms like TikTok, YouTube Shorts, and Instagram Reels. Furthermore, the device incorporates advanced 3-axis mechanical stabilization. Unlike digital stabilization, which often results in image cropping and artifacts, mechanical gimbal stabilization physically compensates for hand tremors and movement in real time, yielding cinematic, fluid camera sweeps even while the operator is walking or running.

To maintain frame framing during solo shoots, the Osmo Pocket 3 is equipped with ActiveTrack 6.0 technology. This proprietary tracking software utilizes deep learning algorithms to recognize and lock onto subjects, ensuring that the creator remains centered in the frame without the assistance of a dedicated camera operator. Rapid focusing mechanisms complement the tracking suite, maintaining sharp focus on moving subjects across varying lighting conditions.

Audio Integration and Ecosystem Expansion

Beyond video fidelity, modern content creation heavily relies on clean, broadcast-quality audio. DJI has systematically integrated the Osmo Pocket 3 into its broader ecosystem of wireless audio peripherals. The device features native connectivity to up to two DJI Mic 2 or Mic Mini transmitters simultaneously. This capability allows independent creators, documentary filmmakers, and interviewers to bypass cumbersome external audio recorders, establishing a direct, low-latency wireless audio link that significantly streamlines field production workflows.

The ability to pair directly with professional-grade wireless microphones addresses a historical pain point for mobile creators, who traditionally had to rely on separate audio synchronization during post-production. By unifying high-bitrate visual capture with seamless multi-source audio recording within a pocket-sized form factor, DJI has positioned the Osmo Pocket 3 as an all-in-one production studio suitable for fast-paced journalism, travel blogging, and corporate digital communication.

Market Implications and the October Prime Day Landscape

The decision by retailers to discount the DJI Osmo Pocket 3 by $60 ahead of the official October Prime Day launch reflects broader economic strategies within the consumer technology sector. High-end creator hardware rarely sees aggressive price slashing outside of major shopping holidays like Black Friday, Cyber Monday, and Amazon Prime Day. Consequently, a pre-event discount of this magnitude serves as an indicator of heightened competition among digital marketplace platforms aiming to capture discretionary consumer spending during an economically sensitive period.

Industry analysts note that consumer electronics manufacturers and authorized distributors frequently subsidize these early promotional prices to stimulate unit volume. As smartphone cameras continue to improve, dedicated standalone vlogging cameras must offer undeniable value propositions to justify their purchase price to consumers. By lowering the financial barrier to entry by 12%, retailers can successfully convert fence-sitting buyers who might otherwise have settled for standard smartphone upgrades.

Furthermore, the timing of these deals aligns with the fourth-quarter retail cycle, a critical window during which electronics brands generate a disproportionate percentage of their annual revenue. Early October sales serve as a bellwether for consumer appetite heading into the heavily contested year-end holiday shopping season. If demand for creator-focused tech remains robust despite broader macroeconomic pressures, suppliers can anticipate stable or expanding market share in the burgeoning prosumer video segment.

Broader Context for Content Creators and Independent Media

The democratization of high-end video production equipment has fundamentally altered the media landscape. Tools like the DJI Osmo Pocket 3 enable solo operators, regional news outlets, and independent digital creators to produce broadcast-grade content that rivals traditional studio productions in terms of visual and auditory fidelity.

The accessibility of such technology has profound implications for how news and entertainment are gathered and disseminated. Field reporters can deploy rapidly into remote or volatile environments without the heavy, conspicuous footprint of traditional broadcast cameras. Similarly, educational creators, travel documentarians, and digital entrepreneurs can maintain high production values while operating on lean budgets.

However, the proliferation of advanced mobile imaging tools also introduces new challenges regarding content saturation and quality control. With high-resolution sensors and stabilization accessible to a wider demographic than ever before, the differentiator in digital media increasingly shifts toward storytelling, editorial integrity, and unique perspective rather than technical execution alone. Nevertheless, hardware reliability, ease of use, and efficient workflows remain critical bottlenecks for creators working under tight deadlines.

Purchasing Considerations and Availability

For prospective buyers evaluating the current Amazon promotion, market researchers advise verifying seller authenticity and warranty coverage, as third-party marketplace dynamics can occasionally introduce gray-market goods or unauthorized distribution channels. Purchasing directly from verified storefronts ensures access to standard manufacturer warranties and customer support.

As the October 6 start date for Amazon’s official Prime Day event approaches, consumers tracking high-end electronics will continue to monitor price fluctuations. While it remains uncertain whether the Osmo Pocket 3 will see deeper discounts during the peak of the sale, historical pricing trends suggest that a 12% markdown prior to the event represents a solid, reliable saving for immediate purchasers who require the hardware for upcoming autumn production schedules.

Ultimately, the combination of advanced stabilization, a 1-inch sensor, 4K capabilities, and seamless microphone integration cements the DJI Osmo Pocket 3 as a cornerstone device for modern visual storytelling. Whether utilized by seasoned journalists capturing breaking news on the move or lifestyle vloggers documenting daily narratives, the hardware continues to redefine the boundaries of what is possible within a pocket-sized digital camera footprint.

September 25, 2026 0 comment
0 FacebookTwitterPinterestEmail
Artificial Intelligence & Tech

Google Beam expands with new regions, partners, and customers

by admin September 25, 2026
written by admin

The Evolution of Distance Collaboration

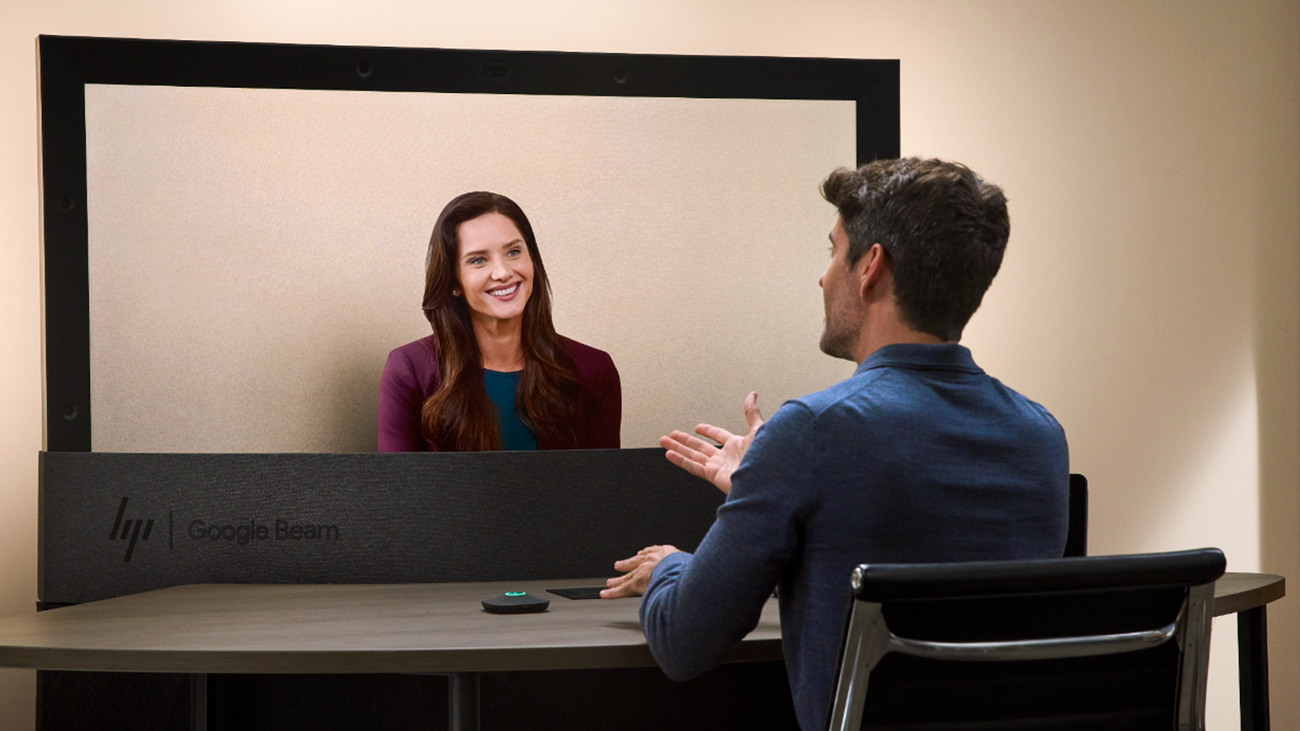
Since its inception, the Google Beam project has sought to eliminate the psychological and physical barriers inherent in standard digital meetings. The core philosophy rests on the belief that meaningful human connection—defined by nuance, body language, and eye contact—is often lost in the flat, grid-like interfaces of conventional video software. By integrating with established ecosystems such as Google Meet and Zoom, the Beam initiative is positioning itself as a hardware-agnostic, enterprise-grade tool designed to bridge the gap between distributed teams.

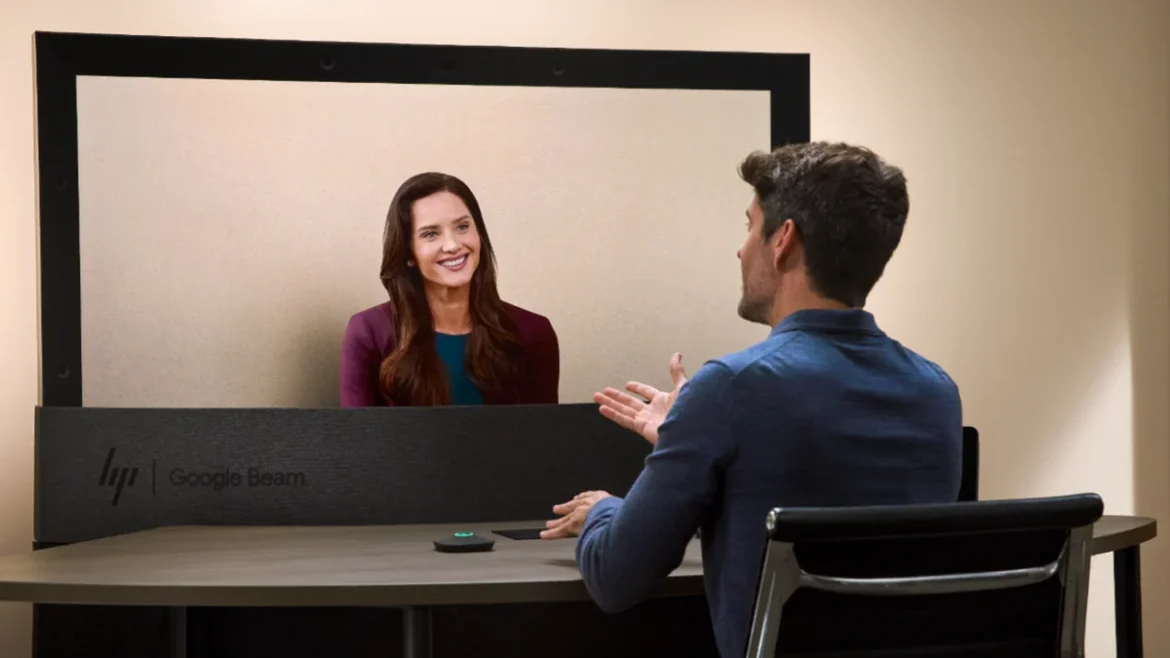
The technology utilizes specialized displays and cameras to create a life-sized projection of remote participants, effectively mimicking the sensation of being in the same room. This is a significant pivot from the 2020-2022 era of video conferencing, where the focus was primarily on connectivity and stability; the current era focuses on the quality and intimacy of those interactions.

Global Expansion and Infrastructure

The current expansion phase is not merely a regional pilot but a robust, multi-country deployment. Google is officially launching support in six major markets: the United States, Canada, the United Kingdom, France, Germany, and Japan. This footprint is supported by a network of 18 dedicated channel partners, specifically selected for their expertise in audiovisual integration. These partners are tasked with the installation, maintenance, and ongoing support of the hardware, ensuring that enterprises can scale their deployments without internal technical bottlenecks.

This rollout represents a major logistical investment. By providing local support in diverse regulatory and technical environments, Google is signaling that Beam is intended for permanent, daily use in high-stakes corporate environments, rather than as a novelty tool.

Quantifying the Impact: A Data-Driven Approach

To justify the capital expenditure required for such hardware, Google has released findings from an internal eight-week study. The data suggests that Beam addresses several key pain points of remote collaboration:

  • Enhanced Connectivity: Teams using the technology reported a 50% increase in feelings of interpersonal connection compared to traditional video platforms.
  • Communication Clarity: Users noted a 33% improvement in ensuring their feedback was clearly understood, reducing the friction often caused by digital misinterpretations.
  • Efficiency Gains: There was a 21% reduction in the necessity for follow-up meetings, suggesting that the "presence" offered by Beam allows for more decisive and effective communication during the initial engagement.

These statistics provide a compelling value proposition for corporations looking to optimize their real estate and travel budgets. If a technology can reduce the frequency of secondary meetings and improve decision-making speed, the cost of the hardware—while significant—can be offset by improved organizational velocity.

Case Study: Bain & Company

One of the most notable early adopters is the global consultancy Bain & Company. Their experience provides a template for how industries reliant on high-trust relationships can utilize telepresence. Keith Bevans, EVP and Partner at Bain, noted that the firm faced significant challenges in assessing candidate suitability during virtual interviews. The "nuance" of body language and the ability to maintain consistent eye contact are critical components of a consultant’s professional profile.

Google Beam expands with new regions, partners, and customers

Bain utilized HP Dimension with Google Beam to conduct candidate screenings, effectively bringing remote talent into a "virtual office" space. By doing so, the firm was able to maintain its rigorous assessment standards without requiring the carbon footprint or time commitment of physical travel. This application serves as a proof-of-concept for other sectors, including high-end sales, executive coaching, and legal consultations, where the "in-person" feel is non-negotiable.

The Industrious Partnership and the "Extended Network"

Perhaps the most ambitious aspect of this rollout is the partnership with Industrious. By integrating Google Beam into a premium, flexible workspace environment, Google is effectively creating a "Beam-as-a-Service" model. This move acknowledges that many small-to-medium-sized businesses, or even large enterprises with decentralized hubs, may not want to invest in the hardware for every office.

Starting this October, businesses will be able to book Beam-enabled suites at select Industrious locations in major economic hubs, including Atlanta, Chicago, New York City, and Palo Alto. This creates an "extended network" that democratizes access to high-end telepresence. For a startup or a remote-first company, the ability to rent a Beam-enabled room for a crucial client pitch or a sensitive HR negotiation represents a significant shift in how professional infrastructure is consumed.

Implications for the Future of Work

The implications of the Google Beam expansion are far-reaching. First, it challenges the narrative that the office is dead. Instead, it suggests a hybrid future where the "office" is defined not by a specific zip code, but by the quality of the communication tools available to the staff. If a remote worker in Tokyo can engage with a team in London with the same physical presence as someone sitting across the table, the traditional geographic limitations on talent acquisition are fundamentally altered.

Second, the hardware-as-a-service model via Industrious could disrupt the commercial real estate market. Landlords and workspace providers who offer high-fidelity collaboration tools may see higher occupancy rates, as companies seek out "collaboration-ready" spaces rather than just empty desk space.

Finally, the success of this project will likely spur competition. As Google, HP, and other hardware manufacturers refine these systems, we can expect a convergence of AI-driven enhancements—such as real-time language translation, automated note-taking, and AI-moderated interactions—all layered on top of the physical telepresence experience.

A Sustained Commitment

The overarching strategy for Google remains consistent: to embed itself as the backbone of modern work. Whether through cloud-based software or physical hardware like the HP Dimension, the goal is to make the technology invisible. By moving away from the "window-into-the-room" feeling of a monitor and toward the "being-in-the-room" feeling of Beam, Google is attempting to solve the last remaining hurdle of the remote work revolution.

As the program expands throughout late 2025 and into 2026, the industry will be watching closely to see if this technology reaches a tipping point of adoption. For now, the combination of empirical performance data, high-profile corporate partnerships, and a flexible, location-independent access model suggests that Google Beam is not merely a research project, but a cornerstone of the company’s enterprise strategy for the next decade. Organizations interested in exploring these capabilities can find further documentation and case studies via the official portal at beam.google.

September 25, 2026 0 comment
0 FacebookTwitterPinterestEmail
Cryptocurrency News

MEXC Dominates TokenInsight September 2026 Crypto Exchange Liquidity Report With Industry-Leading BTC and ETH Futures Depth

by admin September 25, 2026
written by admin

Global digital asset exchange MEXC has captured significant attention across the decentralized finance and traditional trading sectors following the publication of the TokenInsight Crypto Exchange Liquidity Report for September 2026. According to the comprehensive evaluation, MEXC secured the deepest combined Bitcoin (BTC) and Ethereum (ETH) futures order book depth within the critical 0.03% price band, outperforming eight other major international exchanges. Furthermore, the platform demonstrated stellar execution metrics across spot markets and alternative asset classes, notably achieving the lowest median slippage for a $300,000 silver futures sell order.

The TokenInsight report serves as a benchmark for institutional and retail traders alike, providing a systematic, data-driven assessment of liquidity performance across nine leading global cryptocurrency exchanges. By evaluating parameters such as order book depth, trading slippage, and bid-ask spreads across spot and derivatives markets—including tokenized precious metals like gold (XAU) and silver (XAG)—the report highlights the structural resilience and efficiency of top-tier trading venues. MEXC’s prominent standing in the September 2026 findings underscores its ongoing evolution into a multi-asset trading powerhouse capable of supporting high-volume, low-friction transactions.

Background and Context of Exchange Liquidity in 2026

To fully understand the significance of MEXC’s performance in the September 2026 TokenInsight report, it is essential to examine the broader macroeconomic and structural shifts shaping the digital asset landscape. By 2026, the cryptocurrency market has matured substantially, driven by increased institutional participation, clearer regulatory frameworks across multiple jurisdictions, and a rapid convergence between traditional finance (TradFi) and decentralized digital assets.

In this hyper-competitive environment, liquidity has become the ultimate differentiator for cryptocurrency exchanges. Liquidity refers to an asset’s ability to be bought or sold quickly without causing a significant change in its price. For high-volume traders, institutional funds, and algorithmic market makers, deep liquidity ensures that large orders can be executed efficiently, minimizing the impact of slippage—the difference between the expected price of a trade and the price at which the trade is actually executed.

Historically, liquidity fragmentation has plagued the digital asset sector, with trading volume scattered across dozens of centralized and decentralized platforms. However, leading exchanges have increasingly focused on optimizing their order book architecture, incentivizing professional market makers, and upgrading matching engines. MEXC’s strategic emphasis on a 0-fee trading model has played a pivotal role in attracting continuous order flow, thereby creating a self-reinforcing cycle of deep liquidity and tight spreads.

Detailed Breakdown of TokenInsight’s September 2026 Findings

The TokenInsight Crypto Exchange Liquidity Report utilizes rigorous methodologies to evaluate exchanges across various liquidity tiers and asset categories. MEXC’s performance across spot markets, crypto derivatives, and precious metals futures highlights its multifaceted strengths.

Near-Touch Futures Depth Leads the Industry

One of the most notable highlights from the September report is MEXC’s dominance in near-touch derivatives liquidity. Within the 0.03% price band, MEXC’s combined BTC and ETH futures order book depth reached an impressive $21.03 million. This figure represents the deepest liquidity among all nine surveyed exchanges in this specific category.

Near-touch depth is a critical metric for derivatives traders, as it measures the volume of resting limit orders positioned closest to the current mid-market price. High near-touch depth enables traders to execute sizeable positions rapidly without eroding their profit margins through excessive slippage. MEXC’s ability to concentrate executable liquidity near the market price demonstrates the effectiveness of its market-making partnerships and matching engine technology.

Top-Tier BTC and ETH Spot Liquidity Performance

While MEXC excelled in derivatives, its spot market performance remained robust. At the 0.01% price band, the exchange’s combined BTC and ETH spot order book depth touched approximately $1.35 million, placing it in a tie for the deepest spot liquidity reported. Widening the scope to the 0.03% price band, MEXC’s combined spot depth expanded to $3.58 million, securing a solid second-place ranking among global competitors.

Furthermore, execution quality for large-scale spot orders was exceptional. When testing a substantial $500,000 BTC spot sell order, MEXC recorded the lowest median slippage in the entire report, coming in at an exceptionally tight 0.005%. This metric proves that the platform can absorb significant sell pressure without destabilizing local market prices.

Consistent Ethereum Futures Execution Across Tiers

TokenInsight September Report: MEXC Posts Deepest BTC and ETH Futures Depth at $21.03M, Lowest Silver Slippage at 0.002%

Ethereum derivatives trading on MEXC showed remarkable stability across varying order sizes. TokenInsight’s stress-testing evaluated execution efficiency for both mid-tier and large-scale orders. For a $500,000 ETH futures sell order, MEXC registered a median slippage of just 0.003% and a P90 slippage of 0.007%. When order sizes were doubled to $1 million, the platform maintained its poise, recording a median slippage of 0.008% and a P90 slippage of 0.013%. These figures rank among the best-performing results in the September 2026 survey, reinforcing MEXC’s appeal to high-net-worth individuals and institutional participants seeking reliable execution for large-ticket strategies.

Pioneering Precious Metals Futures: Leading in Silver Liquidity

Beyond traditional cryptocurrency pairs, the TokenInsight report evaluated the integration of tokenized traditional financial assets, specifically gold (XAU) and silver (XAG) futures. As digital asset platforms increasingly bridge the gap between crypto and TradFi, performance in non-crypto instruments has become a key metric of diversification and infrastructural maturity.

MEXC distinguished itself significantly in the silver futures category. For a $300,000 silver futures sell order, the exchange recorded a median slippage of only 0.002%, representing the lowest slippage figure among all surveyed exchanges. Additionally, MEXC achieved a combined XAU and XAG futures depth of $2.39 million within the 0.01% band, taking the market lead in XAG-specific order book depth. This performance illustrates MEXC’s successful expansion into multi-asset tokenization, offering traders seamless access to safe-haven commodities alongside volatile digital assets.

Chronology of MEXC’s Growth and Strategic Milestones

Founded in 2018, MEXC has steadily scaled its operational infrastructure to become a dominant force in the global digital asset economy. The platform’s trajectory reflects a series of strategic milestones designed to eliminate friction for retail and professional traders alike:

  • 2018: MEXC is established, focusing on high-performance matching engines and a customer-centric expansion model across Asian and global emerging markets.
  • 2021–2022: Amid intense industry competition, MEXC pivots toward a highly aggressive fee structure, eventually pioneering a 0-fee trading model for spot and select derivative markets to aggressively capture market share.
  • 2023–2024: The exchange expands its asset offering beyond cryptocurrencies, introducing early-stage token discovery programs, broader derivatives products, and initial integrations for tokenized traditional financial (TradFi) assets.
  • 2025: MEXC surpasses key operational thresholds, expanding its user base across more than 170 countries and establishing robust partnerships with tier-one global market makers to deepen order book resilience.
  • September 2026: TokenInsight releases its comprehensive Crypto Exchange Liquidity Report, validating MEXC’s multi-year infrastructure investments by ranking the platform first in BTC/ETH futures near-touch depth and silver futures execution efficiency.

Industry Implications: What the September 2026 Report Means for Traders

The findings of the TokenInsight report carry profound implications for the broader cryptocurrency exchange ecosystem. As regulatory scrutiny increases and market participants demand higher standards of transparency and execution efficiency, exchanges can no longer rely solely on marketing or expansive token listings to attract volume. Liquidity architecture, execution speed, and cost efficiency are now the definitive pillars of exchange survival and growth.

For retail traders, MEXC’s deep order books and low slippage translate directly into a superior trading experience. Tighter spreads mean that traders retain more of their capital when entering and exiting positions, while minimal slippage on large orders ensures that sudden market volatility does not result in unexpected execution penalties.

For institutional and professional algorithmic traders, the validation provided by an independent research firm like TokenInsight offers essential assurance. The ability to execute $500,000 spot orders or $1 million derivatives positions with negligible slippage confirms that MEXC’s liquidity infrastructure is robust enough to handle institutional capital deployment. Furthermore, the successful integration of tokenized precious metals points toward a future where traders can hedge crypto portfolios with traditional commodities on a single, unified interface.

About MEXC: Building the Gateway to Infinite Opportunities

Operating as a leading global multi-asset trading platform, MEXC has positioned itself as a comprehensive gateway to modern financial opportunities. Serving an active user base across more than 170 markets, the platform provides streamlined access to cryptocurrencies, digital stocks, tokenized real-world assets (RWAs), derivatives, and TradFi-linked financial instruments.

Central to MEXC’s value proposition is its commitment to reducing barriers to entry. By maintaining a 0-fee trading environment, the platform empowers retail investors to discover emerging digital assets earlier, execute transactions faster, and maximize their trading potential without being burdened by excessive transaction costs. As the boundaries between decentralized finance and traditional capital markets continue to dissolve, MEXC remains dedicated to scaling its technical infrastructure, enhancing global liquidity, and providing users with secure, efficient access to worldwide financial markets.

Disclaimer and Forward-Looking Operations

Looking ahead, representatives from MEXC have indicated that the platform will continue to invest heavily in its core liquidity infrastructure, matching engine enhancements, and cross-asset product offerings. As digital asset adoption scales globally, maintaining superior order book depth and ultra-low slippage will remain central to the company’s long-term growth strategy.

Disclaimer: This article is for informational purposes only and does not constitute financial or investment advice. The financial markets, including digital assets, tokenized commodities, and derivatives, carry a high degree of volatility and risk. Investors and traders should conduct thorough independent research and assess their personal financial risk tolerance before engaging in any trading activities.

September 25, 2026 0 comment
0 FacebookTwitterPinterestEmail
Blockchain Technology

The Escalating Cyber Threat Landscape in the Middle East: A New Era of Digital Insecurity 2025-2026

by admin September 25, 2026
written by admin

The Middle East is currently navigating an unprecedented transformation in its digital threat environment, as a convergence of geopolitical volatility, rapid digital transformation, and the weaponization of artificial intelligence creates a fertile ground for cyber-adversaries. According to the Middle East Cyber Threat Landscape 2025-2026 analysis published by the AI-powered monitoring firm CloudSEK, the region has transitioned from a landscape dominated by localized hacktivism to one defined by sophisticated, financially motivated ransomware campaigns and state-aligned digital espionage. This shift poses a severe challenge to the region’s critical infrastructure, including its vital oil and gas sectors, maritime chokepoints, and burgeoning digital economies.

The data, spanning from April 2025 to August 2026, illustrates a region under siege. While earlier periods were marked by ideological protest—driven largely by regional military tensions involving Israel, Iran, and the United States—the latter half of the reporting period saw a pivot toward more damaging, profit-driven intrusions. Ransomware, in particular, has emerged as the primary tool of choice for criminal syndicates, with attack frequency increasing by more than twenty-fold within a seventeen-month window.

A Chronology of Escalation: From Hacktivism to Ransomware

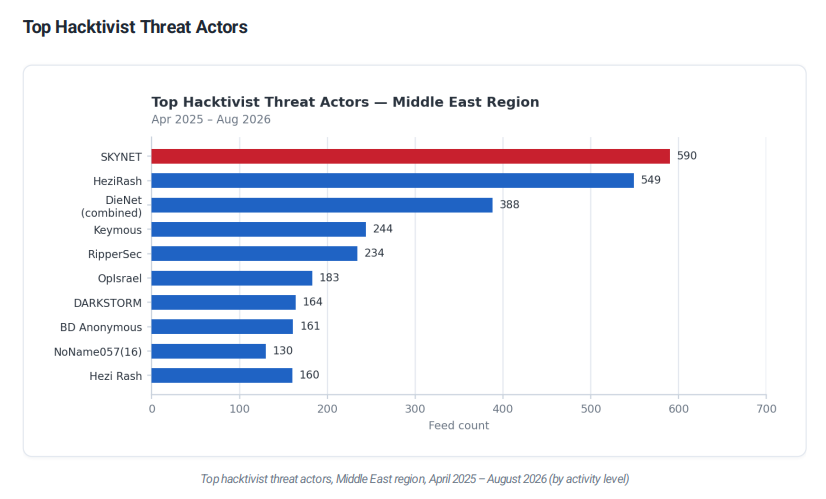
The timeline of cyber activity in the Middle East over the past year and a half reflects the broader geopolitical unrest of the period. In mid-2025, as military tensions reached a crescendo, the region saw a massive surge in hacktivist activity. Groups such as SKYNET, HeziRash, and DieNet orchestrated a sustained campaign of distributed denial-of-service (DDoS) attacks, website defacements, and SQL injection maneuvers. Israel bore the brunt of this activity, accounting for approximately 37.8% of all regional hacktivist events.

Latest Blockchain News, BSV Insights, and AI Web3 Trends from CoinGeek

By April 2026, however, the landscape began to shift. While politically motivated disruption did not vanish, it plateaued, ceding the spotlight to professionalized ransomware operations. The most significant spike in ransomware activity occurred in June 2026, when 357 distinct activity signals were recorded—a stark contrast to the 17 signals logged in April 2025. This rapid escalation suggests that threat actors are no longer merely seeking to make a statement; they are seeking to monetize vulnerabilities in sectors that are critical to the region’s stability.

The facility management sector has emerged as the primary victim of these attacks, followed closely by infrastructure, manufacturing, and property management. This prioritization indicates a strategic focus on entities that cannot afford downtime, thereby increasing the leverage held by extortionists.

Geographical Distribution and Threat Sources

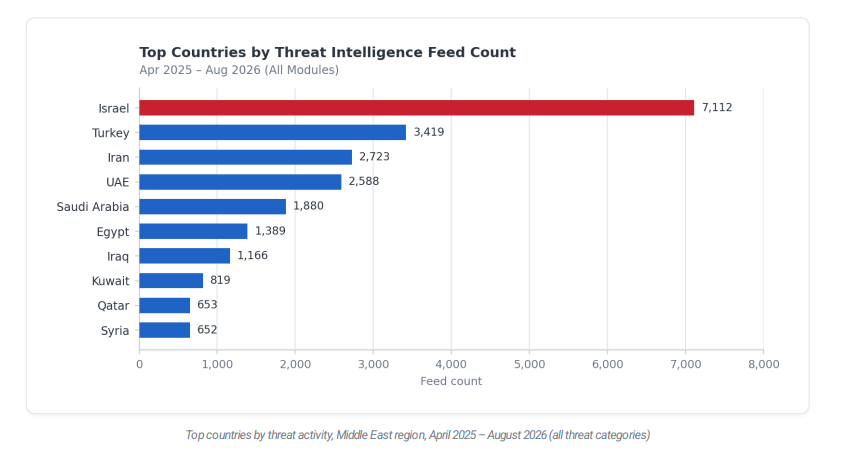
The geography of cyber risk in the Middle East is multifaceted. While Iran is often framed as a focal point of regional conflict, security analysts clarify that it serves primarily as a hub for threat actor development rather than the sole victim. Conversely, Türkiye has been identified as the most targeted nation for ransomware, followed by Israel, the United Arab Emirates, Egypt, and Saudi Arabia.

The dark web has become the backbone of this criminal ecosystem. In this hidden marketplace, stolen government credentials, financial data, and proprietary corporate intelligence are traded at a premium. Türkiye and the UAE exhibit the highest levels of darknet engagement, while Israel leads the region in total threat intelligence feed volume, with over 7,100 specific alerts documented in the study. The prominence of these nations reflects their high levels of digital adoption; as these economies modernize and integrate advanced e-commerce and banking systems, they inadvertently expand their attack surface.

Latest Blockchain News, BSV Insights, and AI Web3 Trends from CoinGeek

The Weaponization of Artificial Intelligence

Perhaps the most alarming development in the 2025-2026 threat landscape is the integration of artificial intelligence into the cybercrime toolkit. AI has significantly lowered the barrier to entry for novice hackers while drastically increasing the efficiency of established criminal groups.

Ram Narayanan, Middle East country manager at Check Point Software Technologies, has noted that AI is now influencing nearly every stage of the cyber-kill chain. The most critical shift is the acceleration of the vulnerability exploitation cycle. Previously, there was a window of several days between the disclosure of a software vulnerability and its active exploitation by bad actors. Today, that window has shrunk to mere hours. AI-driven automation allows attackers to scan networks, identify weaknesses, and deploy payloads at speeds that human-led security teams struggle to match.

The implications of this are profound. As AI tools become cheaper and more accessible, the "cost per attack" continues to plummet, encouraging a surge in smaller, highly targeted campaigns that are difficult to attribute and even harder to mitigate.

Official Responses and Strategic Resilience

In response to these mounting pressures, regional governments are prioritizing "cyber-resilience" over traditional, perimeter-based security models. The United Arab Emirates has led the charge with the introduction of its V7 cybersecurity model, a sophisticated framework designed to automate malware detection and support continuous penetration testing. This initiative is complemented by a national commitment to reskilling the workforce, acknowledging that human error remains the weakest link in any security architecture.

Latest Blockchain News, BSV Insights, and AI Web3 Trends from CoinGeek

However, the consensus among cybersecurity experts is that technological solutions alone are insufficient. The nature of modern threats—characterized by autonomy and rapid evolution—requires a fundamental change in corporate and government culture. Organizations are increasingly advised to adopt a "zero-trust" architecture, enforce rigorous identity and access controls, and maintain immutable, offline backups. The latter is considered essential in the face of ransomware attacks that specifically target cloud-based or networked backups to force a ransom payment.

Broader Economic and Geopolitical Implications

The persistence of cybercrime in the Middle East has tangible economic consequences. When critical infrastructure sectors like energy and manufacturing are targeted, the ripple effects can disrupt global supply chains, particularly given the region’s role as a major maritime corridor through the Straits of Hormuz and Bab el-Mandeb.

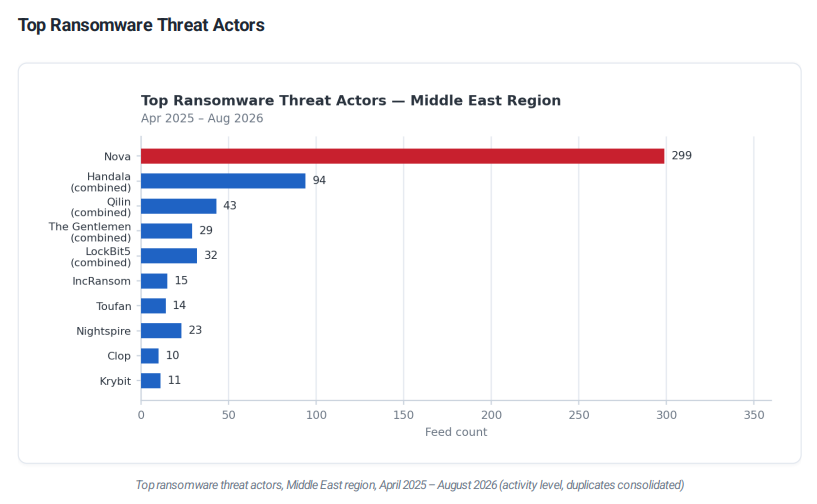
Moreover, the convergence of criminal and state-sponsored activity creates a complex attribution problem. When a ransomware group like Nova or Qilin attacks a government agency, it is often unclear whether the motive is purely financial or if the group is being utilized as a proxy for state-level interests. This ambiguity complicates international cooperation and legal response efforts, as traditional diplomatic channels are often ill-equipped to deal with decentralized, non-state actors operating from the dark web.

Looking Toward 2027: A Proactive Defense

As the region moves toward the end of 2026 and into 2027, the emphasis must remain on proactivity. The era of reactive security, where an organization waits for an alert before taking action, has passed. Proactive threat hunting, the use of AI to defend against AI, and the fostering of regional intelligence-sharing partnerships will be the defining factors of success.

Latest Blockchain News, BSV Insights, and AI Web3 Trends from CoinGeek

The message for enterprises and government agencies is clear: the threat environment is not a temporary anomaly, but a permanent feature of the modern digital economy. Organizations that fail to integrate security into their core operations risk not only financial loss but also the erosion of public trust and the compromise of national security. As the Middle East continues to innovate, its ability to secure its digital foundations will ultimately determine its capacity to thrive in a global market that is increasingly defined by the security of information.

Summary of Key Findings

  • Ransomware Surge: The most common form of attack, with a twenty-fold increase in activity signals recorded between early 2025 and mid-2026.
  • Targeted Sectors: Facility management, industrial systems, and infrastructure are the most frequently targeted, signaling a focus on critical, high-impact systems.
  • Leading Actors: Groups such as Nova, Handala, and Qilin continue to dominate the extortion landscape, often utilizing botnets and phishing as primary delivery mechanisms.
  • Technological Shift: The adoption of AI by criminal groups has drastically reduced the time-to-exploit, making rapid, automated defense mechanisms mandatory.
  • Strategic Imperative: Cyber-resilience is now an economic necessity, requiring a shift toward offline backups, constant threat monitoring, and robust identity management.

While the challenges are significant, the region’s commitment to building advanced, AI-driven defense models shows a recognition of the stakes. By fostering a culture of security and investing in both the technology and the talent required to manage it, the Middle East is positioning itself to withstand the next generation of digital conflict. The path forward is not to shun innovation, but to build it upon a foundation of absolute vigilance.

September 25, 2026 0 comment
0 FacebookTwitterPinterestEmail
Blockchain Technology

MoonPay to Acquire North Capital in Major Expansion into Tokenized Securities Infrastructure Valued at Over $60 Million

by admin September 25, 2026
written by admin

Crypto payments and infrastructure giant MoonPay has officially reached an agreement to acquire North Capital, a prominent player in private securities and alternative trading systems, in an all-stock transaction reportedly valued at upwards of $60 million, contingent upon customary regulatory approvals. This strategic acquisition marks a significant milestone for MoonPay as it aggressively broadens its operational scope beyond traditional cryptocurrency transactions and fiat-to-crypto on-ramps, diving deep into the rapidly growing market of tokenized real-world assets (RWAs) and regulated digital securities.

By absorbing North Capital, MoonPay acquires a comprehensive, fully compliant securities infrastructure stack. This integration provides the crypto native firm with critical regulatory licenses and operational frameworks, including broker-dealer capabilities, a registered transfer agent, and investment advisory registrations. These regulatory pillars are essential for navigating the complex legal landscape of digital asset securities in the United States and global jurisdictions. As the boundary lines between traditional finance (TradFi) and decentralized finance (DeFi) continue to blur, this transaction positions MoonPay to bridge the gap by offering institutional-grade compliance alongside its established consumer-facing payment rails.

Understanding the Target: North Capital’s Footprint in Alternative Markets

Founded with a vision to modernize private capital markets, North Capital has built a robust reputation for helping companies raise capital efficiently by leveraging regulatory exemptions. More importantly, the firm operates the Private Placement Exchange Alternative Trading System (PPEX ATS). The PPEX ATS is a powerhouse within the private securities ecosystem, boasting a catalog of more than 1,250 eligible securities and having successfully supported over $8.7 billion in cumulative transaction volume.

The platform provides a compliant venue for the issuance, trading, and settlement of private securities—an asset class historically plagued by illiquidity, manual paperwork, and fragmented market structures. By incorporating North Capital’s broker-dealer and advisory arms directly into its infrastructure platform, MoonPay is no longer merely a conduit for buying and selling cryptocurrencies like Bitcoin and Ethereum. Instead, it is transforming into a full-spectrum financial technology conglomerate capable of handling the entire lifecycle of tokenized equities, debt instruments, and alternative investment funds.

The Nexus of Liquidity: Agora and the tZERO Partnership

MoonPay buys North Capital, including ATS for tokenized securities

One of the most intriguing and complex dimensions of the North Capital acquisition involves its strategic partnerships within the tokenized securities landscape, most notably its collaboration with tZERO. Earlier, North Capital and tZERO joined forces to launch Agora, an innovative inter-market routing network designed specifically to connect alternative trading systems (ATSs).

Historically, tokenized and private securities markets have suffered from severe liquidity fragmentation. Different trading venues operate in isolated silos, meaning that buyers and participants on one platform cannot easily access liquidity or execute orders on another. Agora was built to solve this exact problem by establishing a unified routing network that allows qualified institutional participants to discover and route orders seamlessly across multiple venues.

The initiative achieved a major operational milestone in July when it successfully executed its very first routed order on the live network. However, the integration of North Capital into MoonPay’s corporate umbrella introduces new governance questions for Agora. With one of its two founding ATS platforms now absorbed by a vertically integrated corporate group that simultaneously owns transaction routing technology and consumer payment rails, industry observers are closely watching how Agora will manage neutrality, competitive dynamics, and institutional trust moving forward.

Strategic Implications for the Tokenized Asset Boom

The timing of MoonPay’s acquisition reflects a broader, industry-wide race toward the tokenization of real-world assets. Traditional financial institutions, asset managers, and fintech pioneers are increasingly recognizing that blockchain technology can drastically reduce settlement times, lower administrative overhead, and democratize access to asset classes that were once restricted to ultra-high-net-worth individuals and institutional giants.

Tokenization involves representing ownership of physical or traditional financial assets—such as commercial real estate, corporate bonds, private equity, and commodities—as cryptographic tokens on a distributed ledger. While the technological plumbing for tokenization has existed for years, widespread adoption has been severely bottlenecked by regulatory uncertainty and the lack of compliant, interconnected secondary markets.

By acquiring North Capital, MoonPay bypasses years of regulatory licensing hurdles. Rather than building a broker-dealer and an alternative trading system from scratch and waiting for approvals from regulatory bodies like the Financial Industry Regulatory Authority (FINRA) and the Securities and Exchange Commission (SEC), MoonPay instantly inherits a licensed, battle-tested compliance machine. This move allows the company to offer tokenization as a service to enterprise clients, enabling banks, fintechs, and issuers to tokenize assets and distribute them in full compliance with securities laws.

MoonPay buys North Capital, including ATS for tokenized securities

Navigating Regulatory Scrutiny and Future Outlook

While the all-stock deal valued at over $60 million represents a lucrative exit for North Capital’s stakeholders and a transformative growth catalyst for MoonPay, the transaction remains subject to rigorous regulatory review. Given the current regulatory climate surrounding digital assets and securities in the United States, regulators will likely scrutinize the transfer of broker-dealer registrations and alternative trading system ownership.

The convergence of crypto payment rails with regulated securities infrastructure also places MoonPay under a brighter regulatory spotlight. As the company expands its footprint from retail crypto onboarding into institutional-grade capital markets, compliance, anti-money laundering (AML) protocols, and know-your-customer (KYC) standards will become even more critical to its ongoing operations.

Market analysts view this acquisition as part of a larger consolidation wave within the digital asset sector. As standalone startups find it increasingly difficult to navigate high regulatory compliance costs and fragmented liquidity pools, well-capitalized infrastructure giants like MoonPay are stepping in to acquire regulated entities. This consolidation trend is expected to accelerate, ultimately shaping a more mature, institutionalized digital asset economy where compliance and innovation go hand in hand.

As the deal moves toward final approval, the industry will be monitoring how MoonPay integrates North Capital’s technology stack into its existing ecosystem. The success of this integration will not only determine MoonPay’s trajectory in the multi-trillion-dollar tokenized asset market but may also set a precedent for how crypto-native firms successfully transition into regulated traditional financial infrastructure.

September 25, 2026 0 comment
0 FacebookTwitterPinterestEmail
Blockchain Technology

SAP Is Taming the Wild West of AI Agents With Its New Enterprise Governance Hub

by admin September 25, 2026
written by admin

For the modern Chief Information Officer, the proliferation of autonomous AI agents has created a digital blind spot that threatens to eclipse the security challenges of the early cloud-computing era. While enterprises have spent the last two years rushing to integrate Large Language Models into their workflows, the result has been the emergence of "Shadow AI"—a landscape where thousands of independent agents operate across departments with little to no centralized oversight. SAP is now positioning itself to address this chaotic sprawl, leveraging its massive global footprint to introduce the first ERP-scale solution for agent discovery, inventory, and governance.

The SAP AI Agent Hub, built upon the foundation of SAP LeanIX, represents a significant shift in how organizations manage their technical debt. By providing a vendor-agnostic command center capable of cataloging not only SAP-native agents but also third-party LLMs and Model Context Protocol (MCP) servers, SAP is attempting to act as the primary cartographer for the uncharted territories of enterprise AI.

A Chronology of the Autonomous Enterprise Shift

The road to the AI Agent Hub’s Q3 2026 general availability has been marked by a deliberate, multi-phased rollout. The concept was first introduced to the public during the SAP Sapphire conference in May 2026, where the company outlined its vision for the "Autonomous Enterprise." At that stage, the hub was a conceptual framework designed to help enterprises move beyond experimental pilot programs into sustainable production environments.

Following the initial reveal, the summer of 2026 served as an incubation period for the technology. By September, the narrative shifted from theoretical potential to tangible market penetration. On September 22, 2026, SAP published a comprehensive roadmap detailing the practical integration of the hub into existing IT stacks. This was immediately followed by a series of technical demonstrations at the SAP Transformation Excellence Summit in Atlanta, where industry leaders began to engage with the tool’s capability to trace, monitor, and decommission agents that had drifted from their operational goals.

The Scale of the Shadow AI Problem

The urgency behind SAP’s release is backed by stark industry data regarding the failure rates of autonomous systems. According to research from IDC and Lenovo, a staggering 88% of custom agent builds fail to transition successfully from a controlled pilot environment to a production setting. This "pilot purgatory" often stems from a lack of visibility: if an IT department cannot see what is running, they cannot audit it, secure it, or scale it.

Further compounding the issue is the difficulty of tracking the economic impact of these agents. PYMNTS reported in September 2026 that only 23% of merchants currently possess the capability to accurately track agent-driven transactions. In an era where AI agents are increasingly tasked with executing procurement, supply chain logistics, and customer-facing interactions, this opacity represents a direct financial risk. Without a centralized "agent inventory," organizations are essentially running blind, vulnerable to security leaks, data hallucinations, and unintentional financial exposure.

The Competitive Landscape of Governance

SAP is not operating in a vacuum. The governance of AI agents has become the most contested frontier in enterprise software, with at least five major governance-focused products debuting in the two-week window surrounding the September summit. The market is witnessing a rapid consolidation of the "control layer," as vendors race to provide the guardrails necessary for enterprise adoption.

Dataiku has launched a standalone Agent Management product aimed at cross-platform monitoring, while NiCE’s $955 million acquisition of Cognigy underscores the high value placed on the routing and orchestration layer of AI agents. Meanwhile, Collibra has introduced "Guardian Agents" for runtime governance, and identity giant Okta has begun integrating agent-specific identity verification into its platform.

Despite this flurry of activity, SAP maintains a distinct competitive advantage: the sheer size of its installed base. With roughly 425,000 customers already utilizing its ERP infrastructure, SAP possesses a distribution channel that few, if any, of its competitors can match. While competitors may offer specialized features, SAP’s integration into the core transactional systems of the global economy provides a "home-field advantage" for compliance and governance tasks.

Technical Capabilities and the Promise of Interoperability

The AI Agent Hub is designed as a three-pillar architecture: discovery, observability, and behavior mining. The discovery phase uses the LeanIX backbone to identify agents across an entire IT landscape, regardless of whether they are hosted on AWS, Google Cloud, or Microsoft Azure. Once discovered, the observability component, integrated with SAP Cloud ALM, allows administrators to perform session tracing and monitor goal completion in real-time.

Perhaps most critically, the hub features the AI Agent Excellence framework, powered by SAP Signavio. This tool performs "behavior mining," a process that analyzes agent output against intended workflows to detect drift. If an agent begins to deviate from its operational parameters—potentially engaging in unauthorized tasks or inefficient processes—the hub alerts the administrator.

The platform is also bolstered by SAP Company Memory, a governed knowledge layer currently in beta. This layer is designed to ground agents in the specific, historical context of the enterprise, ensuring that AI responses are not just accurate to the LLM, but accurate to the business’s internal logic and regulations. Furthermore, SAP has solidified partnerships with major players including Microsoft, Google Cloud, AWS, Anthropic, and NVIDIA, ensuring that its Joule assistant can interoperate with external frameworks in a bidirectional manner.

The Reality Check: Heterogeneous Environments

While the preliminary numbers provided by SAP—150 organizations and 180,000 discovered agents—are impressive, industry analysts caution that the true test of the hub lies in its performance in "messy" environments. SAP’s internal metrics remain self-reported and have not been subject to independent audits. More importantly, the hub’s effectiveness in a "clean" SAP-centric environment is markedly different from its performance in a fragmented, multi-cloud architecture.

Most modern enterprises operate in a state of high technical heterogeneity. Different departments often employ different agent frameworks, data silos, and cloud providers, leading to a complex web of dependencies. The true value of the AI Agent Hub will only be realized if it can successfully bridge these divides. If the tool proves to be effective primarily within SAP-heavy environments, its impact will be limited to a portion of the enterprise market. If it truly acts as a universal governance layer, it could set the industry standard for the next decade of autonomous computing.

Implications for the Future of Enterprise AI

The rise of the AI Agent Hub signals that the "Wild West" phase of corporate AI adoption is drawing to a close. Organizations are moving away from a fascination with what agents can do, and toward a rigorous evaluation of how they should operate within the boundaries of enterprise compliance.

For the CIOs and CTOs currently struggling to manage a fleet of autonomous bots, the SAP AI Agent Hub offers a potential solution to a critical problem. However, it is essential to view this not as a plug-and-play panacea, but as a foundational attempt to bring discipline to a nascent field. Visibility is the first step toward governance, but true control will require a shift in organizational culture—one that prioritizes oversight and accountability alongside innovation.

Whether SAP succeeds in dominating this space depends on the transition from marketing rhetoric to widespread, cross-platform adoption. As the company moves past the September 2026 hype cycle and into the reality of long-term product support, the success of the hub will be measured by its ability to secure the diverse, messy, and rapidly evolving architectures that define the modern, autonomous enterprise. For now, the hub stands as a promising, distribution-backed attempt to turn the chaos of AI agent proliferation into a manageable, governed asset.

September 25, 2026 0 comment
0 FacebookTwitterPinterestEmail
Decentralized Finance (DeFi)

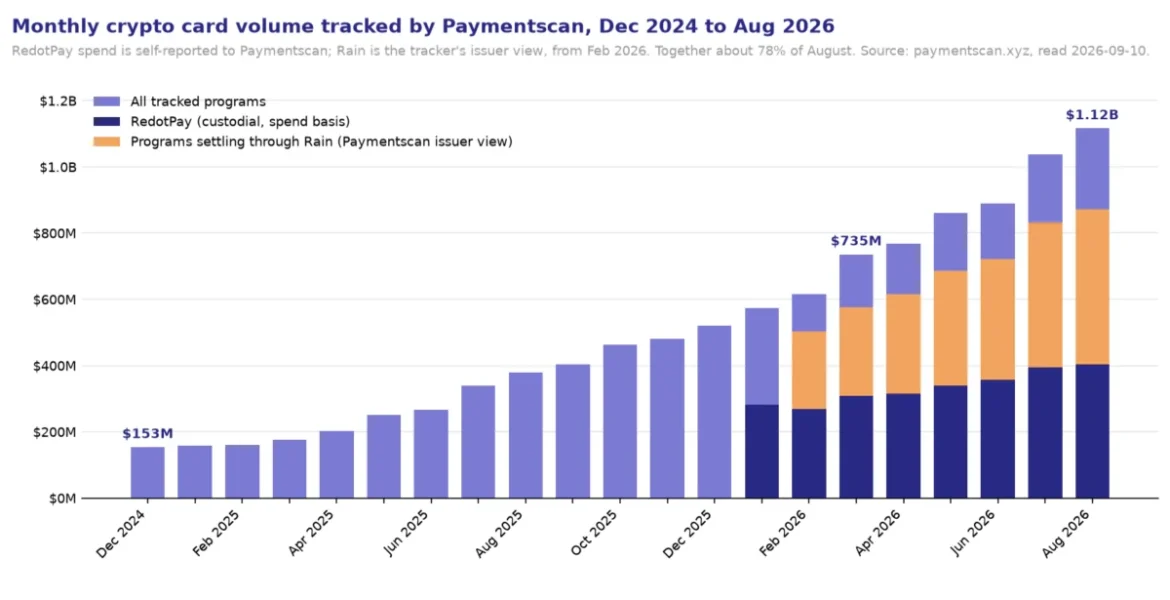
Crypto Card Volume in 2026: $1.1 Billion a Month, and What Is Inside It

by admin September 25, 2026
written by admin

At 16:49:48 UTC on Friday, August 28, 2026, a Solana wallet—funded just three hours prior with 1.79 SOL derived from $190 in USDC bridged from Ethereum—initiated a series of commands that began systematically draining card-balance accounts held by users of Avici, a prominent Solana-based neobank. By the time the exploit was neutralized, 1,685 users had seen their balances liquidated, totaling a loss of $500,859.22. This incident, while rapidly contained, has cast a harsh spotlight on the "non-custodial" crypto card market, a sector that has seen its monthly transaction volume explode to over $1.1 billion as of August 2026.

The vulnerability did not stem from stolen private keys or compromised user devices. Instead, it lay within a specific Solana card contract shared by Avici and several other programs. The underlying infrastructure belongs to Rain, a card-issuing company that has become the backbone of much of the self-custodial card market. While Avici’s terms of service, last updated in June 2025, assured users that neither the company nor the issuer held custody of their collateral, the technical reality of the smart contract architecture allowed for a systemic failure. The incident serves as a stark reminder that in the world of crypto-native finance, the definition of "non-custodial" is often dictated by the nuance of smart contract permissions rather than the absolute security of user assets.

A Chronology of the August Drain

The exploit was surgical and efficient. The attacker’s wallet, identified on-chain as 0xFVNFzqAny8spWdPmYw6RQ9TkYa29ueFFiqCFD1gQnCEj, remained dormant for 189 minutes after its initial funding before launching its first attack at 16:49:48 UTC. Over the next two and a half hours, the wallet executed approximately 21,405 transactions, with roughly 17,500 successfully interacting with the Rain-controlled Solana program.

The mechanics of the exploit relied on an authorization bug within the SubmitSignatures call. By manipulating the signature-verification instruction—pointing the signature, key, and message offsets back at one another—the attacker managed to satisfy a two-signature check with only a single signature. This granted the attacker administrative status over individual user collateral accounts, allowing for the immediate withdrawal of funds.

The fallout was swift. Between 19:03 and 19:49 UTC, as the drain was concluding, the stolen funds were bridged from Solana to Ethereum and moved through Tornado Cash. By 19:18 UTC, Rain had begun patching the affected programs. By September 5, all upgrade authorities for the involved contracts were successfully migrated to a Squads multisig vault, providing a long-term fix to the security architecture.

Market Growth and Concentration Risks

According to data from Paymentscan, the crypto card market has witnessed extraordinary growth, rising from $153 million in monthly volume in December 2024 to $1.116 billion by August 2026. This trajectory highlights a significant shift in consumer behavior, as users increasingly seek to bridge the gap between volatile digital assets and daily retail spending.

However, this growth is heavily concentrated. Paymentscan’s issuer mapping attributes approximately 42% of August’s total volume—$468 million—to programs settling through Rain. When combined with the self-reported figures from RedotPay, these two entities facilitate roughly 78% of the entire tracked crypto card market. This concentration presents a systemic risk: while the August exploit was limited to specific Solana contracts, the reliance on a narrow set of infrastructure providers means that a single architectural flaw can ripple across multiple independent brands simultaneously.

Crypto Cards 2026: Who Holds the Money Before the Swipe

Decoding Custody Models

The industry’s terminology often obscures the legal reality of where money resides. An analysis of 18 major crypto card programs reveals five distinct custody models, ranging from direct debt claims to fully on-chain vaults:

  1. Sale-to-Operator: Programs like KAST have adopted language that characterizes user deposits as a "sale" of assets to the company. In this model, the user holds a USD-denominated debt claim against the operator, often with limited liability protections and no guarantee of asset segregation in the event of bankruptcy.
  2. Nominee Custody: Platforms like Revolut act as a "nominee" for the user. While the platform holds legal title, the user is defined as the beneficial owner. This model relies on the robustness of the platform’s balance sheet and the clarity of its insolvency procedures.
  3. Fiat-Only Issuers: Many exchange-based cards, such as those from Crypto.com or Kraken, do not hold crypto assets on the card account at all. Crypto is held in exchange custody and converted to fiat only at the moment of a transaction. In the EU, this is governed by strict e-money safeguarding regulations.
  4. Shared Program Pools: This is the category that suffered the August exploit. In this model, user collateral is held in a smart contract. While the user technically owns the collateral, the contract is managed by an operator with administrative upgrade keys. If the authorization logic is flawed, the "non-custodial" nature of the account provides no protection.
  5. Self-Custodial Vaults: Programs like Gnosis Pay and Ether.fi Cash utilize sophisticated smart account architectures (such as Safe) where the user maintains control over their assets, often utilizing modules for spend permissions or time-delayed transactions. These are currently the most robust designs, though they are not immune to logic errors.

The Issuer Landscape: Beyond Traditional Banking

A significant finding in the current market structure is the role of "Third National." Seven of the programs analyzed—including Avici, KAST, and Ether.fi Cash—list Third National as their card issuer. Investigations reveal that Third National is not a chartered bank, but rather a Puerto Rico-based money transmitter operating under the corporate umbrella of Signify Holdings, Inc. (Rain).

This underscores a broader trend: many crypto-native card programs are built on non-bank infrastructure, utilizing stablecoin lending networks to facilitate settlement. When a user taps their card, Rain settles with the merchant via Visa and is subsequently repaid from the user’s collateral contract. This "charge card" model, financed by institutional stablecoin liquidity, is highly scalable but introduces dependencies on the creditworthiness and operational security of the underlying infrastructure provider.

The Regulatory Horizon and Future Outlook

The regulatory landscape is poised to change dramatically with the implementation of the EU’s Anti-Money Laundering Regulation (Regulation (EU) 2024/1624), effective July 2027. This framework will effectively prohibit anonymous crypto-asset accounts and limit the usage of anonymous prepaid cards. These impending rules are expected to force a consolidation in the market, favoring programs that maintain transparent KYC (Know Your Customer) and KYB (Know Your Business) compliance.

The recent failures of programs like Kulipa and the closure of Bit.Store following the revocation of its issuer’s license serve as reminders that card programs are fragile. Often, the decision to terminate a service is made by a sponsor bank or a network, leaving the consumer brand with little recourse.

Lessons from the August Incident

Despite the loss of $500,000, the August 28 incident had a relatively positive outcome for users. Rain and the affected programs, such as Avici and Tria, stepped in to refund all impacted users within 24 hours. This response highlights that, for now, the industry is operating on a model of "socialized risk," where venture-backed entities prioritize reputation and customer retention by covering losses out of their own balance sheets.

However, the event serves as a warning for the next phase of market development. As transaction volumes continue to grow, the industry can no longer rely on the promise of venture-backed refunds to mitigate smart contract risks. The path forward requires a transition toward more transparent, immutable, and fully audited on-chain vault architectures. For the end user, the lesson is clear: "non-custodial" is not a synonym for "invulnerable." Before topping up a card, users should look past the marketing, verify the issuer’s regulatory standing, and understand whether the smart contract holding their collateral is truly isolated or subject to the administrative whims of a single, centralized key.

As of September 2026, the sector stands at a crossroads. The integration of stablecoin-powered payments into the Visa network is a major technological milestone, but the infrastructure supporting this growth remains a work in progress. For the millions of users participating in this ecosystem, the security of their assets depends as much on the quality of the legal documentation and the strength of the multisig upgrade keys as it does on the underlying blockchain technology.

September 25, 2026 0 comment
0 FacebookTwitterPinterestEmail
Cybersecurity & Hacking

Court-Ordered Seizure of Radaris.com Domain Marks a Watershed Moment in the Enforcement of Daniel’s Law and the War on Data Brokers

by admin September 25, 2026
written by admin

The landscape of online consumer privacy and the murky world of commercial data brokers underwent a dramatic shift when a New Jersey court ordered the seizure and transfer of the high-traffic people-search domain, Radaris.com. For over a decade, Radaris operated as a pervasive fixture in the digital ecosystem, systematically scraping, compiling, and monetizing the personal dossiers of millions of Americans while routinely ignoring deletion requests and consumer complaints. That era of impunity slammed into a judicial roadblock following a relentless legal campaign spearheaded by Atlas Data Privacy Corp under New Jersey’s stringent Daniel’s Law.

The punitive domain transfer—which swept up Radaris.com alongside more than a dozen sister domains—was not merely a routine civil penalty. It represented the culmination of years of calculated obfuscation, international shell games, and aggressive legal posturing by the platform’s operators. As privacy advocates hail the ruling as a monumental victory for public safety officials, legal experts warn that the battle over commercial data harvesting is rapidly escalating into a constitutional showdown with far-reaching implications for the entire information broker industry.

Anatomy of a Lawsuit: The Battle Over Daniel’s Law

Passed in response to a horrific tragedy involving the family of a federal judge, New Jersey’s Daniel’s Law is designed to shield law enforcement personnel, judicial officers, prosecutors, and their immediate family members from targeted harassment and violence. The statute grants these public servants the absolute right to have their personal information completely expunged from commercial people-search engines and data broker databases. Crucially, the law carries teeth, imposing statutory fines of $1,000 per violation against companies that willfully ignore valid removal requests.

In February 2024, Atlas Data Privacy Corp—a private entity dedicated to enforcing privacy mandates—initiated legal action against Radaris, alleging systematic and flagrant violations of Daniel’s Law. Rather than engaging constructively with the judicial process, Radaris and its legal representation allegedly engaged in a familiar pattern of delay, stonewalling, and jurisdictional maneuvering.

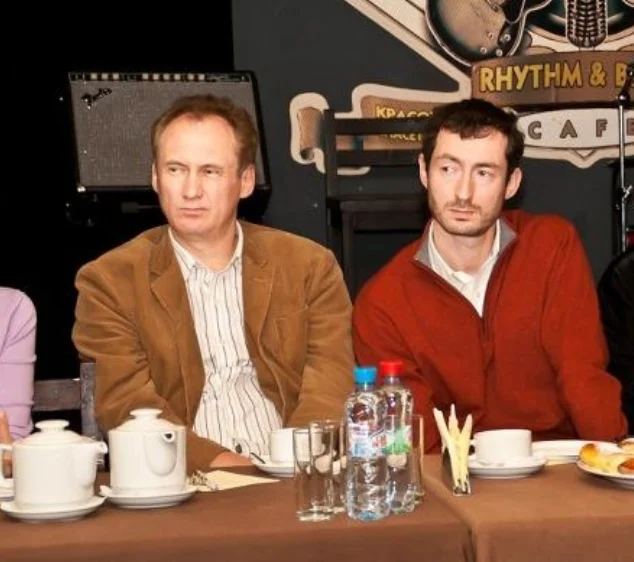
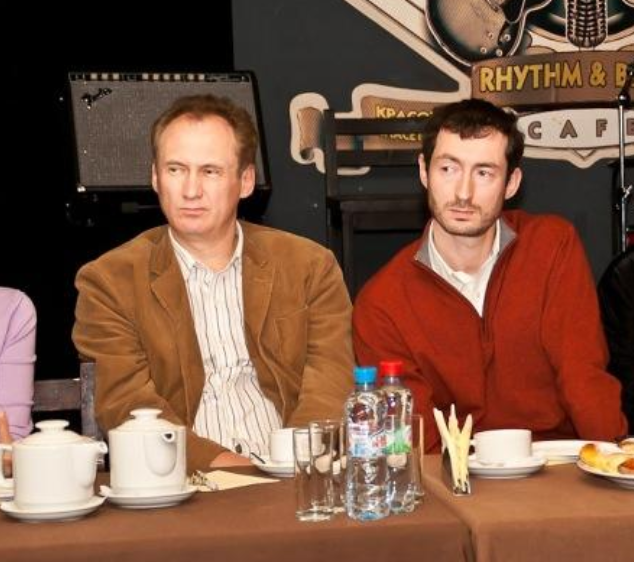
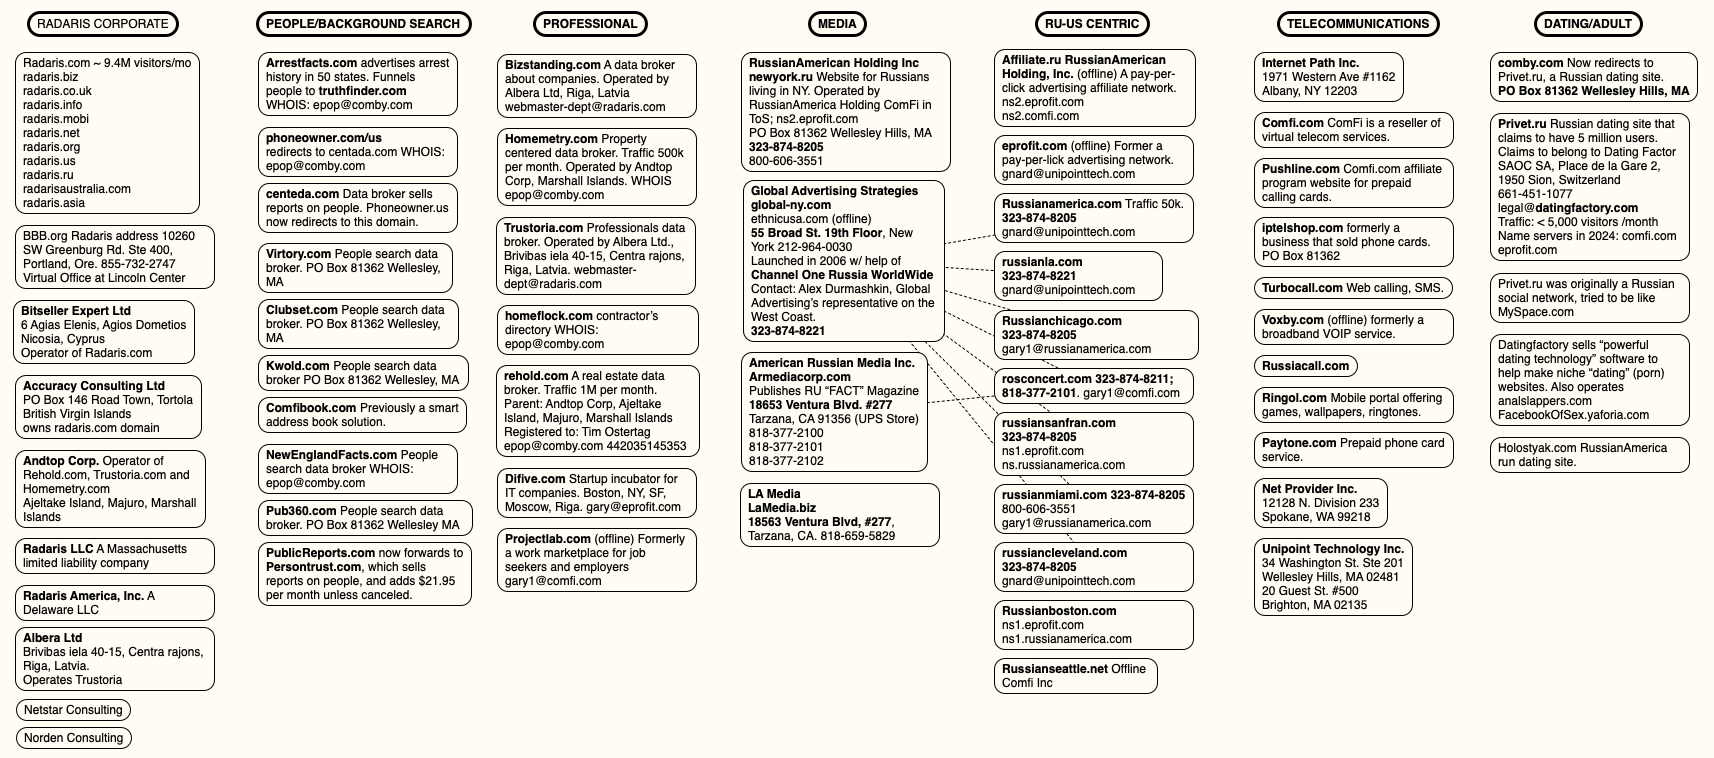
As the litigation progressed, investigative reporting by cybersecurity journalist Brian Krebs unmasked the true masterminds behind the sprawling enterprise: Igor and Dmitry (also known as Dan) Lubarsky, Russian-born brothers residing in Massachusetts. The investigation revealed that the brothers operated an intricate web of dozens of people-search subsidiaries, Russian-language dating portals, and affiliate marketing networks. Furthermore, court filings and investigative disclosures exposed that Radaris had historically utilized a fictitious chief executive officer named "Gary Norden" to front operations and court investors, an admission later confirmed by Boston-based attorney Val Gurvits during legal proceedings.

Data Broker Radaris Loses Domains in Privacy Fight – Krebs on Security

The Corporate Shell Game and International Evasion

The legal confrontation with Radaris exposed the sophisticated mechanics employed by modern data brokers to evade accountability. According to Matt Adkisson, president and CEO of Atlas, the defendants frequently engaged in what he characterized as an "island-hopping phase" designed to frustrate plaintiffs and exhaust judicial resources.

As legal pressure mounted across various jurisdictions, the corporate entities ostensibly owning and managing Radaris shifted continuously across offshore tax havens, including the Marshall Islands, the British Virgin Islands, Cyprus, and the Seychelles. Terms of service agreements were allegedly altered on the fly to reflect newly minted shell companies. In one notable instance, when Radaris updated its corporate documentation to claim management by a newly incorporated Marshall Islands entity, an Atlas-commissioned local investigator discovered that the alleged management firm did not even physically exist at the time of the claim.

This strategy of tactical attrition had served Radaris well for nearly ten years. Plaintiffs’ attorneys, worn down by complex jurisdictional challenges, opaque corporate structures, and the immense cost of pursuing foreign-shielded operators, typically abandoned their suits. However, recognizing the acute physical threat that exposed home addresses and personal records posed to New Jersey law enforcement officers, Atlas committed the requisite financial resources and investigative stamina to pierce the corporate veil.

Financial Interconnections and Industry Partnerships

Discovery materials obtained through the litigation—encompassing upwards of 10,000 internal emails, financial documents, and operational records—provided empirical proof of how the Radaris ecosystem functioned behind closed doors. The records reportedly validated that nominal legal entities such as Radaris America Inc., Bitseller Expert Limited, Digital Orbit Corp, Core Solutions Group, Lucky Solutions, and Veripages were centrally administered by a tight-knit cluster of individuals operating out of the Boston area.

These diverse corporate storefronts shared centralized banking channels, payment card processors, virtual office addresses, and core technical infrastructure routed through shared mail domains. The documentary evidence demonstrated that individual nodes within the network, such as Radaris.com and Veripages.com, generated substantial monthly revenues ranging between $42,000 and $45,000.

Data Broker Radaris Loses Domains in Privacy Fight – Krebs on Security

Moreover, the financial disclosures highlighted lucrative partnerships between the Radaris network and mainstream marketing conglomerates. Revenue streams were significantly augmented through data-sharing and affiliate arrangements with entities like the Lifetime Value Company—operator of consumer search brands such as PeopleLooker, PeopleSmart, and Bumper—as well as Onerep, a prominent privacy-management firm whose founder had similarly launched multiple people-search properties. The convergence of companies claiming to clean up personal data while simultaneously feeding the commercial data broker machine underscored the incestuous and contradictory nature of the modern surveillance economy.

Constitutional Challenges and the National Landscape

While the immediate fallout of the New Jersey court’s decision has crippled Radaris’s primary domain—which now redirects visitors to an informational notice managed by Atlas—the broader legal war is far from over. Victor Worms, legal counsel representing the defendants, moved to vacate the default judgment, arguing that Radaris.com is a non-entity lacking legal capacity to be sued, and asserting that the domain seizure constitutes an unconstitutional forfeiture.

Compounding the legal complexity, the broader data broker industry has launched a coordinated counter-offensive against Daniel’s Law. More than 70 parallel lawsuits initiated by Atlas have been removed to federal court by data broker defendants challenging the constitutionality of the New Jersey statute. Industry advocates argue that sweeping restrictions on publishing legally acquired public records infringe upon commercial free speech protections under the First Amendment of the U.S. Constitution.

The outcome of these challenges—which are widely anticipated to climb the judicial ladder to the Supreme Court of the United States—carries profound implications. While at least 14 other U.S. states have enacted legislation modeled after Daniel’s Law, parallel statutes face severe judicial scrutiny. Notably, a federal district court ruled West Virginia’s version of Daniel’s Law facially unconstitutional under the First Amendment, illustrating the friction between state-level privacy mandates and constitutional jurisprudence.

The Structural Deficit in American Data Privacy

Privacy experts point out that the protracted legal battles over Daniel’s Law highlight a glaring structural deficit in American governance: the enduring absence of a comprehensive federal consumer privacy framework.

Data Broker Radaris Loses Domains in Privacy Fight – Krebs on Security

According to privacy researcher and author Justin Sherman, state-level statutes—while well-intentioned—offer fragmented and incomplete protection because they almost universally exempt records categorized as "public" or "government" documents. Vital information including voting registries, property deeds, marriage licenses, motor vehicle registrations, criminal histories, and court documents remain legally accessible for commercial exploitation. Consequently, unless federal lawmakers enact robust baseline regulations governing data scraping and commercial surveillance, people-search enterprises will simply adapt their business models to harvest and repackage legally accessible public registries.

The systemic risks associated with unchecked data collection extend far beyond people-search directories. The ease with which sensitive personal information can be aggregated, monetized, and exposed was starkly demonstrated by high-profile breaches, such as the security failure at IDScan.net, which briefly exposed the driver’s license data of over 153 million Americans on the dark web. Despite repeated legislative wake-up calls and catastrophic corporate data leaks, comprehensive federal oversight remains paralyzed by intensive lobbying from big tech, social media platforms, cryptocurrency advocates, and artificial intelligence developers.

Conclusion: A Precedent With Limitations

The forced transfer of Radaris.com and its sister properties stands as a landmark tactical victory for privacy enforcement agencies and public safety officials. By systematically dismantling the corporate infrastructure of a notorious data broker through relentless litigation and exhaustive forensic accounting, Atlas Data Privacy Corp has demonstrated that even the most deeply entrenched commercial surveillance operations can be held accountable.

Yet, as the legal battleground shifts to federal appellate courts and the constitutional merits of Daniel’s Law are weighed, the case serves as a stark reminder of the limitations of piecemeal state regulation. Until the United States enacts comprehensive, 21st-century federal privacy legislation that restricts the commercial aggregation of public records, the multi-billion-dollar data broker industry will likely continue its high-stakes game of regulatory evasion.

September 25, 2026 0 comment
0 FacebookTwitterPinterestEmail
Cybersecurity & Hacking

Cloudflare Containers vulnerability exposed sensitive customer data due to thin provisioning flaw

by admin September 25, 2026
written by admin

A significant security vulnerability within Cloudflare’s containerization infrastructure has been identified, allowing a paying customer to inadvertently access residual data left behind by other tenants on shared servers. The flaw, which originated from the way Cloudflare managed disk space allocation, affected the company’s "Containers" and "Sandboxes" services, potentially exposing sensitive information ranging from database structures to environment variables and user credentials. While the vulnerability has since been fully mitigated, the incident highlights the complex security challenges inherent in multi-tenant cloud environments where resource isolation is paramount.

The Mechanism of the Flaw

The vulnerability centered on the implementation of "thin provisioning," a storage optimization technique used by Cloudflare to manage disk space across its global fleet of servers. In this architecture, storage is allocated to containers in discrete, 64-kilobyte blocks. When a customer’s container is terminated, these blocks are returned to a global pool, theoretically to be reallocated to future workloads.

Under normal circumstances, the Linux kernel’s device-mapper thin provisioning module is configured to "zero out" or wipe these blocks before they are assigned to a new user. However, a misconfiguration in Cloudflare’s infrastructure caused the system to skip this critical security step. Consequently, when a new container was provisioned, it would occasionally inherit a block that still contained data fragments from a previous tenant.

Because the system did not perform a secure wipe, an attacker could write a small amount of data to a block and then read the remainder of that block at a raw disk level. By doing so, they could recover up to 60 kilobytes of residual information from the preceding user. This data included sensitive directory structures, SQLite database pages, and configuration files, such as .env files and browser profiles, which often house highly sensitive credentials.

Timeline of Discovery and Remediation

The flaw was discovered by Oren Yomtov of the cybersecurity firm Accomplish. On September 4, 2024, the researchers utilized Cloudflare’s bug bounty program to formally report the vulnerability. The discovery process involved systematic testing across various servers, revealing that the issue was not isolated to a single machine but was systemic across Cloudflare’s global infrastructure.

The chronology of the incident and the subsequent cleanup are as follows:

Cloudflare Fixes Flaw That Let One Container Read Another Customer's Leftover Disk Data
  • September 4, 2024: Accomplish researchers report the vulnerability through the official bug bounty channel, providing a proof-of-concept that demonstrated the ability to read residual data.
  • September 14, 2024: Cloudflare implements a fix by re-enabling the block-wiping mechanism. The researchers verify that their proof-of-concept is no longer functional.
  • September 19, 2024: Recognizing that the initial fix did not address data already cached in active memory or existing image layers, Cloudflare completes a comprehensive, multi-day purge of all running container disks and clears associated caches. This process required draining and restarting servers during low-traffic periods to ensure zero downtime for clients.
  • September 24, 2024: Cloudflare officially discloses the vulnerability, detailing the scope and the steps taken to resolve it.

Empirical Scope and Data Analysis

The researchers conducted extensive testing to determine the prevalence of the issue. Across 24 production-level tests on servers selected by Cloudflare, they successfully recovered data on 18 occasions. Furthermore, the issue was validated across 22 underlying machines spanning four continents, suggesting that the misconfiguration was deeply embedded in the company’s global server provisioning scripts.

The recovered data was not merely fragmented noise; the researchers reported successfully capturing structurally complete SQLite databases and directory listings. Despite the sensitivity of the information, the researchers emphasized that their analysis scripts were strictly designed to perform format checks and count data snippets. They explicitly confirmed that no third-party names, credentials, or proprietary content were stored or transmitted beyond the verification required by Cloudflare’s security team.

In its official response, Cloudflare confirmed that the researchers handled the findings with high ethical standards. The company stated that the recovered data was kept private during the testing phase and subsequently destroyed in a secure manner.

Cloudflare’s Investigation and Forensic Audit

Following the report, Cloudflare initiated an internal forensic audit to determine whether the vulnerability had been exploited by malicious actors prior to the report. The company leveraged the researchers’ proof-of-concept to develop detection signatures, which were then applied to historical disk-activity logs.

According to Cloudflare, the audit uncovered no evidence of unauthorized access. The only recorded instances of the exploit were those generated by the Accomplish research team and Cloudflare’s own engineers during the verification phase. However, the company has not provided a definitive window for how long the unsafe "skip-wipe" configuration was in place, making it impossible to fully quantify the duration of the potential exposure.

Broader Implications for Cloud Security

This incident serves as a stark reminder of the "noisy neighbor" and data leakage risks inherent in shared infrastructure. As cloud providers move toward increasingly granular isolation—such as sandboxes designed specifically for AI agents and untrusted code—the complexity of managing storage and memory at the kernel level grows exponentially.

For enterprises relying on containerized environments, the reliance on the cloud provider’s "thin provisioning" security measures is a critical point of trust. The fact that a single flag in a configuration file could compromise the confidentiality of thousands of customers underscores the necessity for robust defense-in-depth strategies.

Cloudflare Fixes Flaw That Let One Container Read Another Customer's Leftover Disk Data

Furthermore, the Accomplish team noted that this was their sixth successful "sandbox escape" since July 2024. Their track record includes similar findings in platforms such as Anthropic’s Claude, Cursor, Docker, and OpenAI’s Codex. This trend indicates that as AI-integrated development environments become more prevalent, the sandboxes protecting these environments are becoming prime targets for security researchers and potential attackers alike.

The Role of Bug Bounty Programs

The successful resolution of this issue highlights the efficacy of bug bounty programs in modern cybersecurity. By incentivizing independent researchers to report vulnerabilities, companies can identify systemic flaws before they are weaponized by threat actors. Cloudflare’s decision to quickly validate the report, implement a global fix, and perform an extensive audit of their infrastructure demonstrates the standard operating procedure for major cloud service providers when dealing with high-severity disclosures.

However, the incident also raises questions about internal auditing processes. While the bug bounty program caught the issue, the fact that the vulnerability existed in a production environment suggests a gap in automated security regression testing. As providers scale their services globally, ensuring that infrastructure-as-code deployments strictly adhere to security defaults remains a significant operational challenge.

Moving Forward

For Cloudflare customers, no action was required, as the company performed the necessary remediation on the backend. Nevertheless, the incident serves as a catalyst for organizations to review their data handling practices in the cloud. Experts suggest that for highly sensitive data, customers should continue to rely on encryption-at-rest and strict access controls, as these measures provide a second layer of defense even if the underlying container infrastructure is compromised.

As for the industry at large, this case will likely prompt a re-evaluation of disk-provisioning standards. The trade-off between the performance gains of thin provisioning and the security requirements of multi-tenancy is now at the forefront of cloud engineering discussions. Cloudflare’s transparency in disclosing the nature of the "skip-wipe" configuration provides a valuable case study for other providers to audit their own storage allocation mechanisms.

The incident is now officially closed, with Cloudflare maintaining that no customer data was compromised beyond the controlled tests performed by the researchers. The company has moved to strengthen its monitoring tools, ensuring that any future deviation from standard security configurations is identified and mitigated in real-time.

September 25, 2026 0 comment
0 FacebookTwitterPinterestEmail
Newer Posts
Older Posts

Recent Posts

  • Ethereum Network Upgrade Update: Glamsterdam Activation on Hoodi Postponed
  • Kraken Expands Its Digital Asset Offerings With the Official Listing of NEXO
  • Cardano Price Faces Mounting Bearish Pressure as Whale Holdings Contract and Technical Indicators Signal Further Correction
  • Web3 Fundraising Surges to Record Highs in Third Quarter of 2025 as Institutional Capital Takes Center Stage
  • Beyond the Hype: Why Financial Institutions Are Rethinking Their AI Strategies in 2026

Recent Comments

No comments to show.
  • Facebook
  • Twitter

@2021 - All Right Reserved. Designed and Developed by PenciDesign


Back To Top
Dr Crypton
  • Home
  • About Us
  • Contact Us
  • Cookies Policy
  • Disclaimer
  • DMCA
  • Privacy Policy
  • Terms and Conditions

We are using cookies to give you the best experience on our website.

You can find out more about which cookies we are using or switch them off in .

Dr Crypton
Powered by  GDPR Cookie Compliance
Privacy Overview

This website uses cookies so that we can provide you with the best user experience possible. Cookie information is stored in your browser and performs functions such as recognising you when you return to our website and helping our team to understand which sections of the website you find most interesting and useful.

Strictly Necessary Cookies

Strictly Necessary Cookie should be enabled at all times so that we can save your preferences for cookie settings.