The rapid acceleration of artificial intelligence in software development and vulnerability research is poised to fundamentally disrupt the global balance between digital privacy, national security, and law enforcement investigations. While cybersecurity experts have long pursued the holy grail of perfectly secure software, a paradoxical consequence of AI-driven code auditing and vulnerability remediation is emerging. Major software ecosystems are rapidly closing decades-old security backlogs, creating an environment where high-end codebases may soon run entirely out of remotely exploitable bugs. This technical maturation threatens to render traditional law enforcement hacking techniques obsolete, potentially driving a resurgence in contentious legislative and regulatory battles over government-mandated encryption backdoors.
The Evolution of Electronic Surveillance: From Physical Wires to Encrypted Streams
To understand the magnitude of the impending shift, it is necessary to examine the trajectory of electronic surveillance over the past three decades. At the turn of the century, law enforcement interception largely mirrored classic investigative techniques centered around wiretapping analog communication lines, landlines, and early-generation mobile devices. The underlying infrastructure was centralized, telecommunication-dependent, and structurally porous.
The proliferation of smartphones in the late 2000s initially expanded the scope of accessible digital evidence. Unlike traditional voice calls, smartphones stored robust logs of user activity, text messages, and geolocation data. However, this era of unprecedented data accessibility proved exceptionally brief. In 2010, Apple introduced hardware-level encryption on iOS devices secured by user passcodes, a precedent quickly adopted by Google’s Android ecosystem.
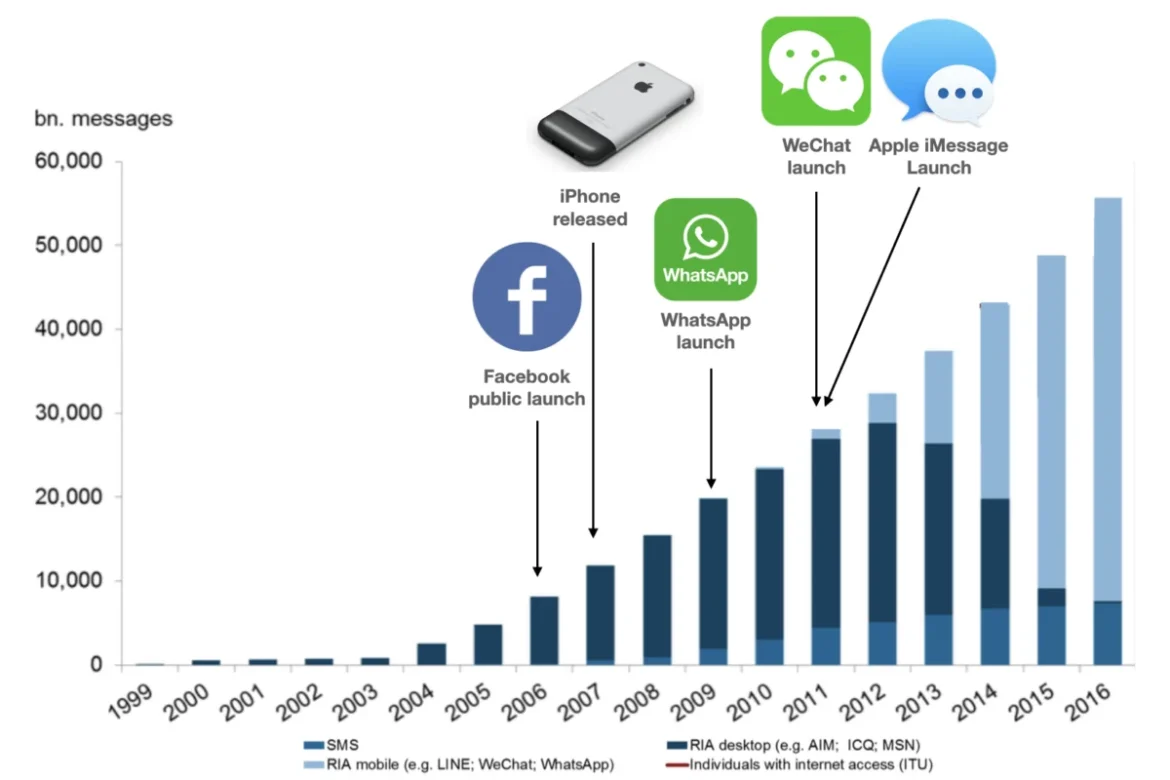
By the mid-2010s, consumer-facing communication shifted decisively toward end-to-end encryption. Platforms such as WhatsApp deployed encryption protocols that ensured messages could only be read by the communicating endpoints. By 2016, nearly one billion global users relied on default encrypted messaging and voice calls, effectively sealing private communications from the reach of traditional wiretaps and service provider compliance orders.
The Apple v. FBI Stalemate and the Era of Exploits

Faced with mounting encryption barriers, the United States Department of Justice and federal law enforcement agencies initiated a coordinated pushback, famously encapsulated by Federal Bureau of Investigation Director James Comey’s 2014 "Going Dark" initiative. This campaign sought to pressure technology companies into building exceptional access mechanisms—commonly known as backdoors—into commercial hardware and software.
The tension culminated in the high-profile 2016 legal battle between Apple and the FBI following a fatal terrorist attack in San Bernardino, California. The FBI formally demanded that Apple construct a specialized, weakened version of iOS to bypass the security features of a shooter’s locked iPhone. Apple steadfastly refused, arguing that creating such a tool would compromise the security of hundreds of millions of innocent users worldwide.
The legal stalemate dissolved not through judicial precedent or technological compromise, but via private enterprise. An undisclosed commercial third party stepped forward, demonstrating that it could bypass the iPhone’s security architecture using proprietary vulnerability exploits. This single event inaugurated a decade-long paradigm where intelligence and law enforcement agencies relied heavily on commercial offensive tools—such as automated device-unlocking hardware and remote zero-day exploitation frameworks—to maintain investigative access without legislative mandates for backdoors.
The Artificial Intelligence Disruption in Vulnerability Discovery
The delicate equilibrium established by commercial exploit procurement is now threatened by the commercialization of advanced artificial intelligence models trained specifically for cyber operations. In early 2026, artificial intelligence laboratories began unveiling frontier models demonstrating unprecedented capabilities in identifying subtle, deep-seated software vulnerabilities.
The public disclosure and subsequent export restrictions surrounding models such as Anthropic’s Mythos highlighted the strategic military and intelligence value of automated code auditing systems. Although the United States government initially restricted access to select domestic agencies and vetted defense contractors, subsequent developments by competitors—including OpenAI and foreign open-weight model laboratories such as China’s Z.ai and Moonshot—demonstrated that vulnerability-hunting capabilities cannot be monopolized by a single entity.
These advanced AI systems are currently being integrated directly into Continuous Integration and Continuous Deployment (CI/CD) software pipelines. As development teams deploy AI agents to scour legacy codebases, software vendors are systematically patching decades of accumulated vulnerabilities at an unprecedented velocity. While absolute software perfection remains theoretically unattainable, industry analysts project that major software ecosystems will soon exhaust the pool of accessible, remotely exploitable bugs.

Implications for National Security and Law Enforcement
The elimination of low-hanging software vulnerabilities carries severe implications for offensive cyber operations and domestic law enforcement. As commercial operating systems and enterprise applications achieve a historically high baseline of resilience, intelligence agencies and local police departments face a severe erosion of their capability to penetrate modern devices.
This technical blackout risks reigniting the dormant debate over exceptional access policies. Without reliable zero-day exploits or ambient software flaws to leverage during criminal investigations, state actors will likely exert intense regulatory and economic pressure on technology firms to integrate intentional cryptographic backdoors or key-escrow systems into consumer products.
Policy analysts warn that this dynamic introduces profound systemic risks. Mandated backdoors, by their technical nature, cannot be selectively restricted to authorized domestic agencies. Any vulnerability engineered into a communications platform for law enforcement use can theoretically be discovered and weaponized by foreign adversaries, organized crime syndicates, and hostile nation-states. Such a strategy risks undermining the foundational security of critical civilian infrastructure precisely as domestic software defenses reach peak maturity.
Future Outlook and Policy Challenges
As the cybersecurity community adapts to an AI-dominated landscape, policymakers and technical experts face difficult strategic choices. The transition toward uniformly secure software architecture represents a monumental victory for consumer privacy and digital infrastructure resilience, yet it simultaneously disrupts traditional paradigms of criminal investigation and national intelligence collection.
Navigating this transition will require a rigorous re-evaluation of how legal systems address investigative necessity in an era where technical circumvention is no longer feasible through conventional hacking. Without proactive international standards and robust institutional frameworks, the convergence of advanced artificial intelligence and universal encryption may force a permanent, structural realignment of global cybersecurity norms.