• Home
  • About Us
  • Contact Us
  • Cookies Policy
  • Disclaimer
  • DMCA
  • Privacy Policy
  • Terms and Conditions
Dr Crypton
Secure Your Future in Crypto
Decentralized Finance (DeFi)

Crypto Card Volume in 2026: $1.1 Billion a Month, and What Is Inside It

by admin September 26, 2026
written by admin

At 16:49:48 UTC on Friday, August 28, 2026, a Solana wallet—funded just three hours prior with 1.79 SOL derived from $190 in bridged USDC—began a systematic extraction of funds from card-balance accounts managed by Avici, a prominent Solana-based neobank. This event, which lasted roughly two and a half hours, served as a stark reminder of the underlying vulnerabilities within the rapidly expanding "non-custodial" crypto debit card sector. By the time the final transaction occurred at 19:18:52 UTC, 1,685 users had seen a combined $500,859.22 vanish from a smart contract infrastructure shared by several programs, including Avici and Tria.

The incident was not a result of compromised user keys or illicit wallet access. Rather, the vulnerability resided in the very architecture that proponents often cite as the hallmark of safety: a specialized smart contract designed for card collateral. These contracts, while ostensibly user-controlled, are frequently subject to administrative upgrade paths that rely on single signing keys. This centralized control, combined with a signature-verification flaw, allowed the attacker to grant themselves administrative privileges over individual user accounts, effectively bypassing the security models that users believed were protecting their assets.

The Chronology of the August 28 Exploit

The precision of the attack suggests a sophisticated understanding of the target’s technical debt. The attacker’s wallet, identified as FVNFzqAny8spWdPmYw6RQ9TkYa29ueFFiqCFD1gQnCEj, performed 21,405 transactions during the exploit window, with 17,500 succeeding. Each success followed a three-step sequence against a Rain-controlled Solana program: an initial SubmitSignatures call utilizing a native Ed25519 signature-verification instruction, followed by an AddCollateralAdmin call, and concluding with a WithdrawCollateralAsset command.

The critical failure involved a faulty verification instruction that directed signature and message offsets back at the initial call, allowing a single signature to satisfy a two-signature requirement. This oversight effectively turned the attacker into a "collateral admin" for thousands of accounts. By 19:03:18 UTC, while the exploit was ongoing, the attacker initiated a deBridge order to move over 1 million USDC from Solana to Ethereum, which was subsequently funneled through Tornado Cash in standard mixing increments.

Rain, the card-issuing infrastructure provider behind these programs, responded by patching the affected Solana programs between 19:18 UTC and 19:43 UTC. On September 5, 2026, Rain transitioned the upgrade authority for these programs to a Squads multisig vault, a critical security improvement that was not publicly announced but was verified via on-chain analysis on September 10.

The Scale of the Crypto Card Market

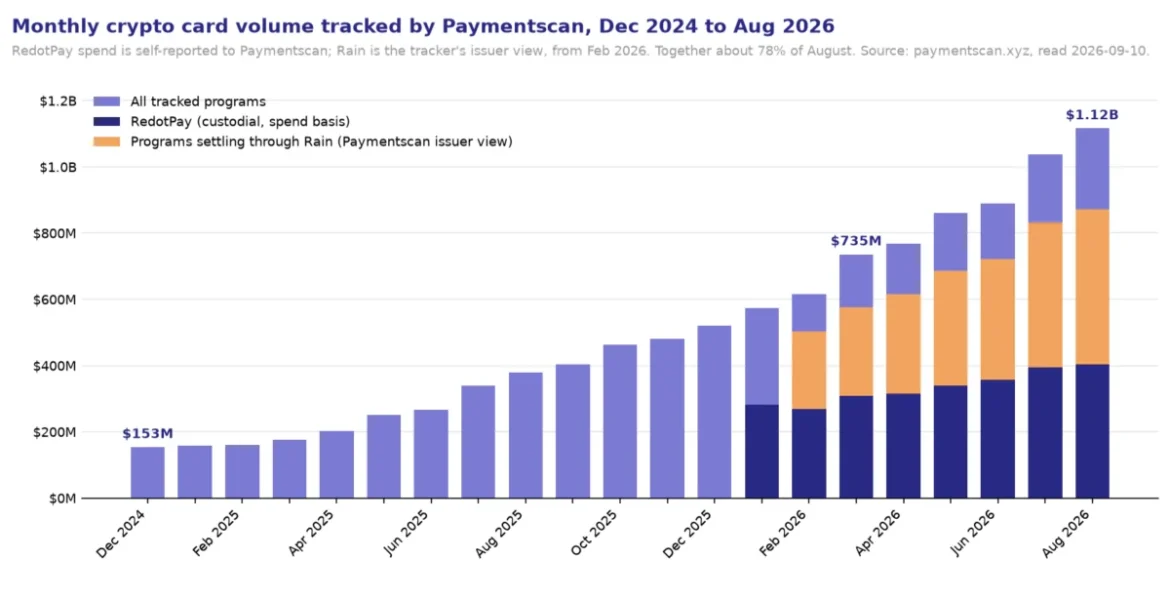
Data from Paymentscan indicates that the crypto card market has entered a period of hyper-growth, with August 2026 volume reaching $1.116 billion across 11 million transactions. This represents a significant shift from the $153 million recorded in December 2024. While these figures reflect a maturing industry, they also mask significant complexities regarding how funds are actually held.

Paymentscan identifies five distinct custody models, ranging from "Sold to the Operator"—where the user holds only a debt claim against the issuer—to "Your Own Vault," where funds remain in a self-custodial smart contract debited only at the moment of authorization. The industry remains highly concentrated; Rain alone facilitates settlement for roughly 42% of the market’s total volume. When combined with RedotPay’s self-reported figures, just two entities account for approximately 78% of the total tracked volume. This concentration creates a systemic risk profile where a single technical failure in a shared codebase can affect dozens of seemingly disparate brands simultaneously.

The Myth of Non-Custodial Security

The term "non-custodial" has become a marketing imperative in the crypto card space, yet its legal and technical definitions vary wildly. Avici’s terms of service, last updated in June 2025, assured users that the company would never hold custody of collateral. While legally accurate, this statement provided little comfort to the 1,685 users whose funds were drained due to a flaw in the underlying Rain-managed contract.

Crypto Cards 2026: Who Holds the Money Before the Swipe

This gap between marketing and mechanism is exemplified by programs like Solayer, which markets its Emerald card as "fully on-chain" while its internal security documentation reveals the use of offline, multisig-protected cold storage. This is, by definition, a custodial arrangement. The industry’s reliance on "Third National"—a Puerto Rican money transmitter and Rain affiliate—as an issuer for seven major programs further highlights the distance between the "DeFi" ethos and the reality of traditional financial infrastructure. These cards are effectively charge cards financed by borrowed stablecoins, not the seamless, on-chain experiences often depicted in promotional materials.

Regulatory and Institutional Implications

The regulatory landscape is set to undergo a fundamental shift with the implementation of the EU’s Anti-Money Laundering Regulation (Regulation (EU) 2024/1624) in July 2027. This regulation will effectively prohibit anonymous crypto-asset accounts and bar EU acquirers from processing payments from anonymous prepaid cards issued in third-party jurisdictions. For the "no-KYC" card sector, this presents an existential threat. Currently, these services exploit the gap between "Know Your Business" (KYB) verification for the issuer and the lack of individual KYC for the cardholder.

Recent infrastructure failures—such as the collapse of the Kulipa program in July 2026, which abruptly ended services for Ready, Argent, and Solflare—demonstrate that the primary risk to users is often not a hack, but rather the fragility of the underlying business relationships. When issuers like Paytend have their licenses revoked or programs like Fiat24 pause operations to address compliance gaps, the brand the consumer interacts with is often left powerless to assist.

Official Responses and Remediation

The response to the August 28 exploit was swift, if opaque. Avici and Tria, recognizing the reputational damage at stake, opted to cover the losses out of their own balance sheets, with Avici explicitly stating that Rain funded the refunds. The total impact, approximately $1.1 million, was mitigated for the end-user within 24 hours. However, the incident highlighted a dangerous lack of transparency regarding pre-deployment audits. While Rain claims to use Sherlock for audits, the drained contracts were older versions that remained live—a classic "legacy code" vulnerability that audit-at-deployment models fail to address.

Ether.fi Cash remains a notable outlier in the category. By utilizing a public, address-verified vault on Optimism and maintaining clear documentation on its CashModule contract, it offers a level of transparency that is currently the exception, not the rule. The contrast between Ether.fi’s architecture and the shared, opaque collateral pools of other programs is a lesson in the importance of technical due diligence over marketing claims.

Moving Forward: What Users Should Analyze

For the end-user, the August 2026 events suggest five critical questions that must be addressed before depositing funds into any crypto-linked card:

  1. Custody Classification: Does the contract transfer ownership to the operator, or is it a true self-custodial vault?
  2. Issuer Identity: Is the issuer a chartered bank, an EMI, or an offshore money transmitter? If the issuer is not clearly named, the program should be viewed as high-risk.
  3. Insolvency Protection: What happens if the service provider goes bankrupt? If the terms do not explicitly address the status of user funds in an insolvency event, users should assume they are unsecured creditors.
  4. Upgrade Authority: Who holds the keys to upgrade the contract? If a single private key controls the contract, the "non-custodial" nature of the product is largely performative.
  5. Transparency of Metrics: Are volume and spend metrics verifiable on-chain, or are they self-reported numbers that lack independent oversight?

The rapid expansion of the crypto card market in 2026 has provided users with unprecedented convenience, but it has also introduced a level of technical and systemic risk that the current marketing landscape fails to articulate. While the August 28 exploit ended with users being made whole, the next failure may not be supported by a $338 million venture-backed balance sheet. As the industry approaches the 2027 regulatory deadline, the divergence between robust, transparent platforms and those relying on "nuanced loopholes" will likely accelerate, forcing a consolidation that favors transparency and structural integrity over the current proliferation of proprietary, black-box solutions.

The reliance on a single company to manage nearly half of the market’s settlement volume creates a "too-big-to-fail" scenario that contradicts the decentralization tenets of the blockchain ecosystem. Ultimately, the stability of the crypto card market in the coming years will depend less on the cleverness of its smart contract marketing and more on the regulatory and technical rigor of the institutions standing behind the cards. Until that time, the user is left to navigate a landscape where "non-custodial" is a description of the current state of a contract, rather than a guarantee of future security.
September 26, 2026 0 comment
0 FacebookTwitterPinterestEmail
Cybersecurity & Hacking

U.S. Army Soldier Sentenced to Nearly Six Years in Federal Prison for Massive Telecommunications Hacks and Extortion Schemes

by admin September 26, 2026
written by admin

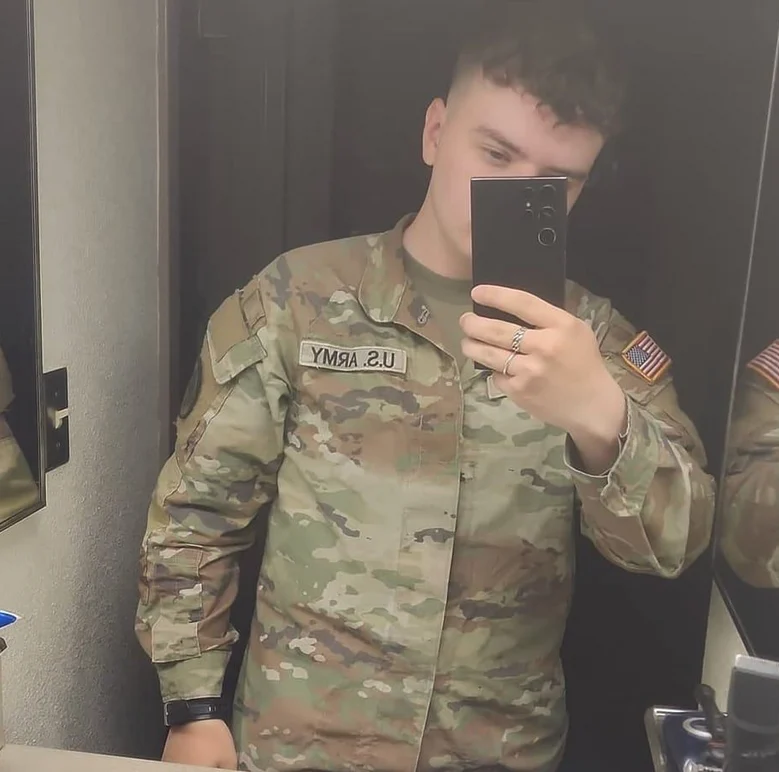
Cameron John Wagenius, a 22-year-old active-duty U.S. Army soldier stationed in South Korea, has been sentenced to 70 months in federal prison for orchestrating a series of sophisticated cyberattacks against major telecommunications companies, including a massive breach affecting more than 100 million AT&T customers. Operating under the cybercriminal moniker “Kiberphant0m,” Wagenius leveraged his high-level military security clearance and technical acumen to illicitly access, download, and attempt to monetize sensitive customer metadata. In addition to his nearly six-year prison sentence handed down in a Seattle federal court, Wagenius was ordered to pay $294,978 in restitution to his victims.

The sentencing marks a critical milestone in a sweeping international investigation involving multiple federal agencies, including the Federal Bureau of Investigation (FBI), the Army Criminal Investigation Division (CID), the U.S. Secret Service, and the Defense Criminal Investigative Service (DCIS). Despite the monumental scale of the data he compromised—which included call and text message metadata for the vast majority of AT&T subscribers, as well as intrusions into Verizon’s Push-to-Talk business and over a dozen other global telecommunications networks—prosecutors revealed that Wagenius reaped a mere $1,500 in direct financial profit from his illicit exploits.

The Genesis of the Breaches and the Snowflake Vulnerability

The cybercriminal enterprise spearheaded by Wagenius relied heavily on exploiting poorly secured enterprise cloud storage environments, most notably platforms provided by Snowflake. In 2024, Wagenius and a network of co-conspirators targeted large-scale corporate customers of the cloud data storage service that had left administrative credentials exposed and failed to enforce multi-factor authentication (MFA). By exploiting these security lapses, the threat actors gained unauthorized access to proprietary corporate databases, allowing them to extract vast quantities of proprietary records and customer metadata.

Operating from his duty station in South Korea, Wagenius adopted the alias Kiberphant0m and quickly established a notorious reputation within underground cybercrime forums. By October 2024, he publicly boasted about his acquisition of call and text metadata belonging to tens of millions of AT&T customers. This stolen data included highly sensitive transactional details, such as source and destination telephone numbers, timestamps, and call durations. Rather than keeping the data private, Wagenius and his associates engaged in aggressive extortion schemes, directly targeting vulnerable telecommunications giants and demanding substantial payouts in exchange for promises not to publish or auction the purloined data on the dark web.

Chronology of an Investigation and Arrest

The operation to unmask Kiberphant0m unfolded over several months through a combination of cybersecurity intelligence and federal law enforcement tracking. The chronology of the case underscores the rapid escalation of the threat and the coordinated response by global investigators:

  • Late November 2024: Cybersecurity publication KrebsOnSecurity published an investigative warning indicating that the threat actor operating as Kiberphant0m was likely an active-duty U.S. soldier stationed in South Korea.
  • December 2024: Federal authorities acted on intelligence and arrested Cameron John Wagenius. He was subsequently hit with two separate federal indictments in Washington state, swiftly pleading guilty to all counts.
  • August 2026: Conor Riley Moucka, an alleged Canadian co-conspirator known online as “Judische,” formally pleaded guilty to his role in the Snowflake extortion conspiracy following his earlier arrest in 2024.
  • September 2025 – September 2026: While incarcerated and awaiting sentencing at a federal facility, Wagenius attempted to exploit Bureau of Prisons (BOP) computer usage policies by engaging in prompt injection techniques against commercial AI tools, seeking unauthorized privilege escalation scripts and prison escape research.
  • Present Day: Wagenius is sentenced to 70 months in federal prison and ordered to pay nearly $300,000 in restitution.

An International Network of Co-Conspirators

Wagenius did not operate in a vacuum; federal prosecutors detailed a sprawling network of transnational cybercriminals who collaborated to execute the cloud storage breaches and subsequent extortion campaigns. Among those implicated alongside Wagenius is Kenneth Schuchman, a 28-year-old resident of Vancouver, Washington, with a notorious background in cybercrime. Schuchman previously pleaded guilty in 2019 to operating the Satori botnet, a vast infrastructure of compromised Internet-of-Things (IoT) devices responsible for launching massive distributed denial-of-service (DDoS) attacks against global internet infrastructure.

Another prominent co-conspirator is Conor Riley Moucka of Kitchener, Ontario, who pleaded guilty in August 2026 for his direct involvement in the Snowflake extortions. Meanwhile, American national John Erin Binns remains wanted by U.S. and international law enforcement. Binns, who has been residing in Turkey, is heavily implicated not only in the recent Snowflake-related campaigns but also in the monumental 2021 T-Mobile data breach that exposed the personal identifying information of at least 76 million customers.

The extortion tactics employed by this network reached unprecedented levels of audacity. Following the arrest of Conor Moucka—and even after AT&T had reportedly paid a $370,000 Bitcoin ransom to the extortion collective—Kiberphant0m engaged in a campaign of re-extortion. In an aggressive bid to pressure corporate and government entities, Wagenius posted what he alleged were call logs belonging to then-President-elect Donald Trump and then-Vice President Kamala Harris. Furthermore, he threatened to leak classified schematics allegedly stolen from the U.S. National Security Agency (NSA).

Inside the Federal Investigation: A Unique Insider Threat

The involvement of an active-duty U.S. service member possessing a secret security clearance presented an extraordinary challenge to federal law enforcement agencies. Paul Russell, the resident agent in charge at the Defense Criminal Investigative Service (DCIS)—the criminal investigative arm of the Department of Defense Office of Inspector General—emphasized the unprecedented nature of the case.

"We don’t often get leads where there’s an active duty soldier with a secret clearance who’s creating hacking tools and trafficking in data," Russell stated. "That doesn’t happen every day, and so when that hits it really spins all of our partner organizations up. It was very serious from jump street, just because it was unique, it was an insider threat, and we weren’t sure what we were dealing with."

The realization that a military insider was actively weaponizing his technical skills to compromise national telecommunications infrastructure triggered an immediate, multi-agency task force. The FBI, Army CID, U.S. Secret Service, and DCIS pooled their resources to track digital footprints, trace cryptocurrency transactions, and ultimately apprehend Wagenius before further classified or proprietary data could be disseminated to foreign actors.

Incarceration Misconduct and AI Prompt Injection Tactics

Even while stripped of his freedom and awaiting sentencing in a federal detention facility, Wagenius demonstrated a persistent inclination toward cyber reconnaissance and system exploitation. According to a sentencing memorandum filed by federal prosecutors in Seattle, Wagenius violated Bureau of Prisons computer use policies in late 2025 by orchestrating a series of indirect attempts to probe BOP network security.

Utilizing the email accounts of fellow inmates, Wagenius directed third parties to query commercial artificial intelligence tools. His prompts were carefully constructed to bypass safety filters designed to prevent AI models from generating malicious exploit code—a cybersecurity evasion technique known as "prompt injection." In one instance, Wagenius framed his queries within the context of researching a book he claimed to be writing, asking the AI tool to provide Common Vulnerabilities and Exposures (CVEs) related to Windows 10 Enterprise privilege escalation and bypasses, complete with unedited, real-world working scripts.

Weeks later, Wagenius utilized another inmate’s account to solicit step-by-step instructions and exploitation code for CVE-2023-45208, a command injection vulnerability affecting D-Link networking hardware. Alongside these cyber reconnaissance efforts, records indicate that Wagenius instructed the same proxy recipients to research methods for constructing contraband radio antennae using prison commissary items to enhance reception, as well as investigating strategies for escaping confinement.

When confronted by federal investigators regarding these prison-era digital inquiries, Wagenius claimed he was merely researching potential vulnerabilities to provide corrective feedback to the Bureau of Prisons. Prosecutors noted that while there was no concrete evidence indicating Wagenius successfully deployed these exploits within BOP networks, the behavioral pattern underscored his persistent malicious intent and technical fixation.

Broader Implications for Corporate Cybersecurity and National Security

The conviction and sentencing of Cameron John Wagenius serve as a watershed moment for both corporate accountability and the defense of critical national infrastructure. The incidents highlight critical vulnerabilities in how major enterprises manage cloud-based data storage and third-party vendor integrations. The ease with which cybercriminals accessed proprietary Snowflake environments due to neglected multi-factor authentication protocols prompted a widespread reckoning across the technology sector, forcing cloud providers and corporate clients alike to mandate strict, uncompromised MFA enforcement across all user tiers.

Furthermore, the case underscores the severe risks posed by insider threats within military and defense apparatuses. The convergence of military-grade security clearances, access to sensitive communications networks, and malicious cyber operations represents a complex threat matrix that traditional defense protocols are continually forced to adapt to. While Wagenius’s financial gains from his sprawling criminal enterprise were remarkably meager—totaling approximately $1,500—the collateral damage inflicted upon corporate trust, individual privacy, and national security institutions was immeasurable.

As federal authorities continue to pursue remaining co-conshrators such as John Erin Binns, the legal outcome for Kiberphant0m sends an unmistakable message to the global cybercrime underground: the cooperative enforcement machinery of the United States military and federal law enforcement agencies possesses the capability to pierce through pseudo-anonymous personas, dismantle transnational extortion rings, and bring malicious insiders to swift justice.

September 26, 2026 0 comment
0 FacebookTwitterPinterestEmail
Cybersecurity & Hacking

ShinyHunters Extortion Gang Bypasses Oracle PeopleSoft WAF Protections to Resume Mass Exploitation Campaigns

by admin September 26, 2026
written by admin

The notorious cybercrime and extortion syndicate known as ShinyHunters has launched a renewed wave of widespread cyberattacks targeting enterprise infrastructure worldwide. By employing a sophisticated URL-encoding evasion technique, the threat group has successfully circumvented web application firewall (WAF) rules designed to mitigate the critical Oracle PeopleSoft remote code execution vulnerability cataloged as CVE-2026-35273. This development has alarmed cybersecurity researchers and exposed significant blind spots in perimeter defense strategies, particularly for organizations that relied on network-level filtering rather than applying official vendor patches.

Security intelligence provided by Google’s Mandiant and Threat Intelligence Group (GTIG)—which tracks the threat actor under the moniker UNC6240—reveals that the bypass technique tricks standard WAF configurations into ignoring malicious payloads directed at vulnerable servers. The campaign has already resulted in the deployment of persistent web shells, backdoors, and lateral movement toolkits across dozens of high-profile networks globally, spanning critical sectors such as higher education, technology, IT services, healthcare, agriculture, transportation, and government agencies.

The Resurgence of UNC6240 and the Mechanics of the WAF Bypass

The underlying vulnerability, CVE-2026-35273, centers on the Environment Management Hub component of Oracle PeopleSoft, specifically targeting the /PSEMHUB/* endpoint. When exploited, the flaw enables unauthenticated malicious actors to execute arbitrary code with the privileges of the underlying application server, paving the way for full system compromise and data exfiltration.

Following emergency disclosures and the release of patches by Oracle in June 2026, many enterprise administrators implemented temporary workarounds. Because applying emergency patches or disabling core management components can disrupt business continuity, numerous organizations opted to block external web traffic destined for the literal /PSEMHUB/ path using reverse proxies and WAFs.

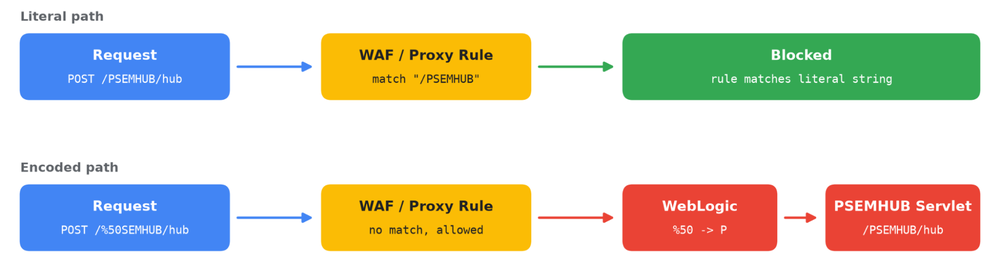
However, ShinyHunters quickly adapted their tactics. Instead of targeting the standard string, the extortion group began leveraging percent-encoded request paths. For example, rather than transmitting traditional requests to /PSEMHUB/, the attackers send requests formatted as /%50SEMHUB/, where the %50 sequence acts as the standard URL-encoded representation of the capital letter "P".

According to Mandiant’s analysis, many standard WAF implementations and reverse proxies evaluate the literal request path prior to normalization or decoding. Because the literal string does not match the blocklist rule for /PSEMHUB/, the security device permits the traffic to pass through. Once the packet reaches Oracle WebLogic, the application automatically decodes the percent-encoded characters, routing the request directly to the vulnerable endpoint and successfully executing the payload. This discrepancy between how edge security tools and backend application servers handle path normalization has left numerous organizations exposed despite believing their perimeter defenses were secure.

Chronology of a Zero-Day Campaign and Escalating Threats

ShinyHunters uses WAF bypass trick in Oracle PeopleSoft attacks

The current exploitation phase represents the latest chapter in an aggressive campaign that first captured global attention in June 2026. The timeline of events highlights the speed at which threat actors operationalize critical vulnerabilities:

  • June 10, 2026: Independent security reports emerge indicating that the ShinyHunters extortion group is actively exploiting an unknown PeopleSoft zero-day vulnerability, successfully breaching and stealing sensitive data from approximately 100 enterprise organizations.
  • June 11, 2026: Oracle issues an emergency security update addressing the zero-day flaw, formally designating it as CVE-2026-35273. Concurrently, Google confirms that UNC6240 is weaponizing the vulnerability, particularly against institutions in the education sector. Security vendors issue interim mitigation guidance, suggesting WAF blocks on the /PSEMHUB/* endpoint for organizations unable to immediately patch.
  • September 2026: ShinyHunters publicly claims responsibility for a high-profile breach of Federal Bureau of Investigation (FBI) systems, asserting they utilized a new PeopleSoft zero-day to compromise the FBI Jobs platform and pivot into internal AWS GovCloud infrastructure, allegedly stealing terabytes of employee data.
  • Late 2026 / Early 2027: Google Mandiant detects the rollout of the URL-encoding WAF bypass technique (/%50SEMHUB/), revealing that ShinyHunters has renewed mass exploitation efforts against systems that relied solely on perimeter blocking.

Anatomy of the Post-Exploitation Phase and Tooling

Once ShinyHunters successfully bypasses perimeter defenses, their operational playbook follows a structured, multi-stage methodology designed for stealth, persistence, and lateral movement. Mandiant researchers have detailed the exact mechanics observed during recent incident response engagements:

Before launching a full-scale assault, the attackers typically send a probing sequence of between five and 15 HTTP POST requests to /%50SEMHUB/hub containing serialized Java objects. On vulnerable hosts, these queries return operating system metadata without generating disk artifacts or causing service crashes. This allows the threat actors to silently inventory target environments and confirm exploitability before deploying heavier tooling.

Upon verifying vulnerability, ShinyHunters triggers the flaw to execute commands in memory or install specialized JSP web shells. Investigators have identified three primary web shells deployed in these attacks: ‘x.jsp’ for general command execution, alongside ‘u.jsp’ and ‘u2.jsp’ intended for the staging and uploading of larger payloads.

On compromised Windows servers, the actors utilize these web shells to drop an executable named ‘Ple64.exe’. This binary cleverly masquerades as a digitally signed installer for the legitimate Light Alloy media player, but its actual payload installs a sophisticated backdoor tracked by Google as SIDEEYE. SIDEEYE provides the threat actors with extensive capabilities, including credential harvesting, file and process management, interactive reverse shells, and built-in reverse proxy functionality.

To facilitate deeper penetration into target networks, ShinyHunters frequently deploys the open-source Neo-reGeorg tunneling toolkit via files named ‘tunnel.jsp’ and ‘tunnel.jspx’. This utility allows attackers to tunnel SOCKS5 proxy traffic over standard HTTP and HTTPS connections, effectively weaponizing the compromised PeopleSoft server as a bridgehead to move laterally across internal enterprise networks. Furthermore, on compromised Linux environments, researchers observed the deployment of legitimate remote management software, such as MeshAgent, to maintain long-term persistent access.

The FBI Incident and Continuing Attribution Claims

The severity of the ShinyHunters syndicate’s campaign was underscored by their controversial claims regarding federal infrastructure. In late September 2026, the group contacted security journalists asserting they had successfully breached FBI systems via a PeopleSoft vulnerability. The attackers claimed access to the FBI Jobs platform enabled them to migrate into internal AWS GovCloud environments, resulting in the alleged exfiltration of two to three terabytes of sensitive records concerning current personnel, applicants, and internal administrative databases.

ShinyHunters uses WAF bypass trick in Oracle PeopleSoft attacks

While independent verification of the stolen data volume and the exact vector remained challenging in the immediate aftermath, the FBI acknowledged it was actively investigating unauthorized cyber activity targeting the FBIjobs.gov portal. Significantly, representatives for ShinyHunters later confirmed to security researchers that they applied their WAF-bypassing methodology during the course of the FBI intrusion, while continuing to assert that they also leveraged secondary, undisclosed flaws within the same PSEMHUB component.

Broader Implications for Enterprise Security and Perimeter Defense

The resurgence of the ShinyHunters extortion campaign through a basic URL-encoding evasion technique serves as a stark reminder of the limitations inherent in perimeter-only security controls. Relying on web application firewalls or reverse proxies to filter malicious traffic based on literal string matching is increasingly proving insufficient against disciplined, adaptable threat actors.

Security analysts emphasize that WAF rules must be regularly audited, normalized, and tested against modern evasion tactics, including various forms of percent-encoding, Unicode manipulation, and case-variation attacks. Furthermore, network defenders must recognize that perimeter blocks are merely temporary stopgaps intended to buy time for proper patch management, rather than permanent architectural solutions.

Actionable Remediation and Defense Recommendations

In response to the ongoing global campaign, Google Mandiant and other leading cybersecurity authorities have urged organizations operating Oracle PeopleSoft environments to undertake immediate remediation steps:

  1. Prioritize Patch Management: Organizations must immediately apply the official vendor security updates provided by Oracle for CVE-2026-35273, rather than relying on perimeter filtering workarounds.
  2. Comprehensive Log Analysis: Administrators should review WebLogic access logs for historical and ongoing indicators of compromise, specifically searching for suspicious requests targeting /PSEMHUB/ as well as encoded variants such as /%50SEMHUB/, /%70SEMHUB/, or mixed-case string permutations.
  3. Network Segmentation and Monitoring: Implement strict egress filtering and monitor internal network segments for unauthorized lateral movement tools, unexpected SOCKS tunneling activity (such as Neo-reGeorg), and unauthorized administrative utilities like MeshAgent.
  4. Endpoint Detection and Response (EDR): Ensure robust EDR telemetry is active across all servers hosting Oracle infrastructure to detect anomalous child processes, unexpected script execution originating from web server directories, and known malicious binaries like the SIDEEYE backdoor (Ple64.exe).

As threat groups continue to refine their evasion techniques against traditional enterprise defenses, the Oracle PeopleSoft incidents underscore the critical necessity of defense-in-depth strategies, timely vulnerability patching, and continuous behavioral monitoring across both perimeter and internal network assets.

September 26, 2026 0 comment
0 FacebookTwitterPinterestEmail
Bitcoin & Altcoins

Bitget Faces Massive Security Breach as Unauthorized Transfers Exceed $351 Million in Sophisticated Backend Attack

by admin September 26, 2026
written by admin

On September 24, 2026, the global cryptocurrency exchange Bitget confirmed a major security incident involving unauthorized outflows from its infrastructure, resulting in a loss of approximately $351.6 million. The breach, which specifically targeted the exchange’s hot and warm wallet architecture, sent shockwaves through the digital asset industry, prompting immediate emergency protocols and an industry-wide response. Despite the significant scale of the theft, Bitget has maintained that its cold storage systems remain uncompromised and that the entirety of the losses will be covered by the exchange’s internal insurance reserves.

A Chronology of the Breach

The security incident began in the late afternoon of September 24. According to internal logs released by the exchange, Bitget’s real-time security monitoring systems flagged anomalous transaction patterns at 18:31 UTC. By the time the automated alerts triggered an emergency response from the internal security team, millions of dollars in assets had already been siphoned from the exchange’s multi-tier wallet infrastructure.

Early on-chain analysis provided by blockchain sleuths and independent researchers initially estimated the losses to be between $170 million and $183 million. However, as the forensic investigation deepened, it became clear that the scope was significantly broader. Bitget’s subsequent forensic review confirmed that the final tally of lost assets reached $351.6 million. The stolen funds were comprised of a diverse portfolio of assets, including Ethereum (ETH), Tether (USDT), USD Coin (USDC), Avalanche (AVAX), and Binance Coin (BNB).

One of the most notable maneuvers executed by the attackers involved the rapid laundering of stolen stablecoins. Forensic data indicated that a single address utilized approximately $19.67 million in USDT to acquire 7,111 ETH on the Arbitrum network within a six-minute window, a technique often used to obfuscate the origin of funds and bypass automated freezing mechanisms.

Anatomy of the Attack: Backend Compromise

Unlike many previous exchange hacks that involve the theft of private keys or phishing of high-level administrative credentials, Bitget’s investigation points to a more sophisticated vector. The exchange revealed that the attackers successfully compromised a backend system tasked with managing wallet operations.

By infiltrating this specific server, the perpetrators were able to inject malicious transaction data, effectively tricking the exchange’s internal systems into authorizing the unauthorized transfers. Crucially, Bitget clarified that the attackers did not gain access to the master private keys, which would have enabled them to drain the entire cold storage reserve. This distinction is vital for the exchange’s long-term recovery, as it confirms that the fundamental integrity of their offline security remains intact.

Bitget has engaged two prominent third-party cybersecurity firms—Mandiant and SlowMist—to conduct a comprehensive forensic audit. These firms are tasked with tracing the illicit flows of capital, identifying the exact point of entry into the backend system, and verifying the efficacy of the remedial measures implemented by Bitget’s engineering teams.

Financial Resilience and User Protection

In the immediate aftermath of the event, Bitget took the precautionary measure of suspending all withdrawal services. However, the exchange opted to keep deposit and trading functionalities active to maintain liquidity and market stability.

A central pillar of the exchange’s crisis management strategy has been its User Protection Fund. Established in 2022 with an initial capital injection of $300 million, the fund has been bolstered significantly over the years, reaching a reported valuation of over $464 million prior to the attack. Because the fund exceeds the $351.6 million loss, Bitget has formally guaranteed that no user account balances will be negatively impacted. The exchange has repeatedly emphasized that customer assets remain "intact," positioning the $464 million reserve as the ultimate buffer against the current shortfall.

This strategy serves as a critical test for the "proof of solvency" and insurance models that many centralized exchanges have adopted following the collapse of major platforms in recent years. By pledging to absorb the full loss, Bitget is attempting to prevent the "bank run" mentality that often exacerbates exchange failures during security crises.

Industry-Wide Cooperation and Support

The incident has triggered a collaborative response from across the decentralized finance (DeFi) and centralized exchange (CEX) sectors. In a public statement, Bybit CEO Ben Zhou extended his team’s support to Bitget, drawing parallels to previous industry incidents where competitors assisted in tracking stolen funds.

The collaborative effort extends to the integration of specialized tracking tools, such as the LazarusBounty initiative, which is being updated to monitor the movement of the stolen assets across decentralized protocols and bridges. Law enforcement agencies have also been notified, and the exchange has provided a list of flagged wallet addresses to major stablecoin issuers and centralized platforms to facilitate the potential freezing of any assets that attempt to move into regulated environments.

Implications for Exchange Architecture

The Bitget incident highlights a persistent vulnerability in the modern cryptocurrency exchange architecture: the "hot-to-warm" bridge. While cold wallets are the industry gold standard for security, the necessity of liquidity for day-to-day trading requires assets to be stored in hot and warm wallets, which are inherently more accessible.

The fact that the attacker manipulated the backend system to "fake" transaction data—rather than stealing the keys—is a worrying development for cybersecurity experts. It suggests that even with air-gapped storage and multi-signature security, the middleware that connects the exchange to the blockchain can become a target. This event will likely prompt a industry-wide review of "Authorized Transaction" protocols, with many exchanges expected to implement stricter hardware-based authentication for backend API calls.

Future Outlook and Operational Recovery

As of the latest updates provided by CEO Gracy Chen, Bitget remains in a high-alert state. The company has promised a full, transparent report within 24 hours of the incident’s conclusion, which is expected to outline the technical specifics of the breach and the permanent changes being made to their security infrastructure.

The path forward for Bitget involves three critical phases: containment, forensic verification, and the restoration of normal services. While trading and deposits are currently functional, the resumption of withdrawals is contingent upon the successful completion of the security audit by the third-party firms. Bitget has committed to providing hourly updates to its user base, attempting to maintain transparency in an environment where rumors and misinformation can easily cause market volatility.

The incident serves as a stark reminder of the risks inherent in holding assets on centralized exchanges. While the User Protection Fund provides a safety net for users, the technical complexity of the breach underscores that no system is entirely immune to sophisticated, state-level or high-tier criminal syndicates. For the broader crypto market, the successful mitigation of this incident—or the potential failure to fully recover the funds—will likely serve as a benchmark for how centralized entities handle large-scale systemic shocks in the years to come.

As investigations continue, the crypto industry is watching closely to see if the stolen assets can be recovered or if the incident will result in one of the largest capital write-offs in the history of the exchange sector. For now, the focus remains on ensuring that the backend vulnerability is patched and that the "three-tier" wallet structure is hardened against similar future manipulation.

September 26, 2026 0 comment
0 FacebookTwitterPinterestEmail
FinTech Innovations

Cambodia Emerges as a Critical Hub for Fintech Innovation and Global Security Cooperation

by admin September 26, 2026
written by admin

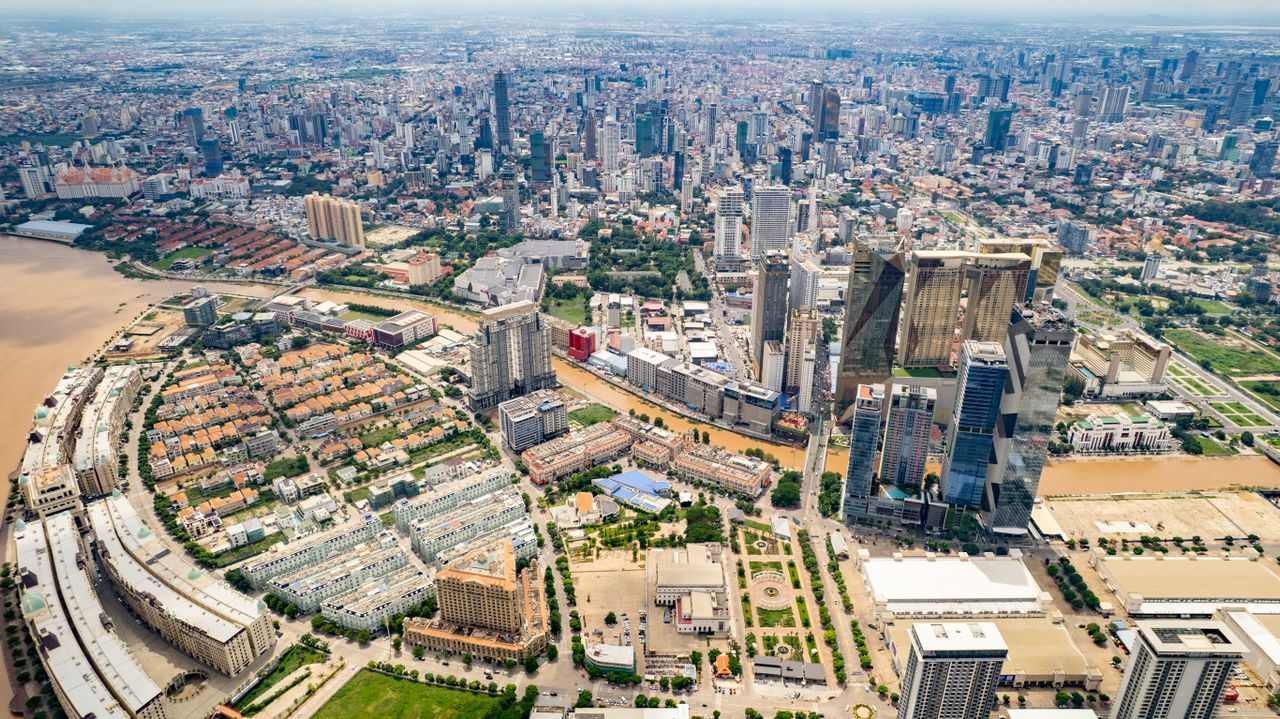
Cambodia is rapidly transforming its financial landscape through a dual-track strategy of aggressive digital payment integration and high-level international cooperation to combat transnational cybercrime. This week, the nation made significant strides on both fronts, securing a landmark security partnership with the United Kingdom to dismantle illicit scam networks while simultaneously launching a major cross-border payment initiative with India’s Unified Payments Interface (UPI). These developments underscore Cambodia’s evolving role within the global digital economy and its commitment to regulatory alignment with international standards.

The UK-Cambodia Security Pact: A New Front in Cybercrime

In a significant geopolitical shift, the United Kingdom and Cambodia have formalized a Memorandum of Understanding (MoU) aimed at neutralizing the growing threat of illegal online scam centers. This agreement represents the first structured, bilateral framework dedicated to dismantling criminal gangs that have utilized Southeast Asia as a base for large-scale financial fraud.

The prevalence of scam centers—which often employ human trafficking victims under the threat of violence—has become a major concern for global law enforcement. These operations frequently leverage sophisticated technological infrastructure to orchestrate romance scams, investment fraud, and pig-butchering schemes that target victims across the globe, including thousands of citizens in the UK.

UK Minister for Fraud, Lord Hanson, emphasized the borderless nature of these crimes during the signing. "Over two-thirds of fraud affecting the UK originates overseas," Hanson stated, noting that the agreement is essential for reducing the domestic threat to British citizens. The partnership is not merely a diplomatic gesture but a tactical alignment involving the Global Fraud Taskforce, established by the UK and INTERPOL.

Tactical Implementation and Capacity Building

The collaboration focuses on three core pillars: intelligence sharing, investigative capacity building, and financial disruption. By facilitating the exchange of data between the UK’s National Crime Agency and Cambodian law enforcement, both nations aim to map the networks that connect regional scam hubs to global financial systems.

Furthermore, the UK has committed to providing specialized training to Cambodian authorities in the realms of digital forensics, cybercrime investigative procedures, and the tracing of illicit digital assets. This capacity building is critical, as the financial flows supporting these scam centers often involve complex money laundering techniques that require advanced technical expertise to intercept. By disrupting the underlying financial architecture of these gangs, the joint task force intends to make the operations less profitable and more vulnerable to detection.

Finovate Global Cambodia: Partnerships in Fraud Fighting and Innovations in Payments

UPI Acceptance: Bridging Southeast Asian and Indian Markets

Parallel to its efforts in cyber-security, Cambodia is deepening its financial connectivity through a strategic partnership between NPCI International Payments Limited (NIPL) and ACLEDA Bank. This collaboration has successfully integrated India’s Unified Payments Interface (UPI) with Cambodia’s national QR code system, KHQR.

The integration, which went live this week, allows Indian travelers to make seamless, secure payments across more than 4.5 million merchant outlets in Cambodia. This initiative is part of a broader "Phase 1" rollout that prioritizes high-traffic retail, hospitality, and tourist sectors.

The technical architecture behind this launch relies on the interoperability of KHQR, which was launched by the National Bank of Cambodia in July 2022. By leveraging the existing Bakong payment system—Cambodia’s national mobile payment backbone—the new UPI integration allows for real-time settlement and reduced foreign exchange volatility for travelers.

A History of Digital Transformation

To understand the significance of the UPI launch, one must look at Cambodia’s rapid digital trajectory over the last decade. Founded in 1993 as a microfinance NGO, ACLEDA Bank has mirrored the nation’s growth, evolving into a commercial banking giant with assets exceeding $10 billion by 2025.

The timeline of Cambodia’s digital payment evolution is marked by several milestones:

  • 2020: The National Bank of Cambodia launches "Bakong," a blockchain-based payment system that serves as the foundation for the nation’s digital infrastructure.
  • 2022: The official launch of KHQR, a standardized QR code protocol designed to unify the fragmented payment landscape across the country.
  • 2024: National merchant adoption of KHQR reaches 4.5 million accounts, creating a robust, high-velocity digital economy.
  • 2026: Implementation of the NIPL-ACLEDA cross-border corridor, marking the first major international interoperability project for the KHQR network.

In Channy, President and Group Managing Director of ACLEDA Bank, highlighted the economic implications of this development. "By integrating the payment gateways of Cambodia and India, we are removing transactional friction," he noted. The move is expected to boost tourism revenue and provide local small-to-medium enterprises (SMEs) with direct access to one of the world’s fastest-growing digital consumer bases.

ABA Bank and the Resilience of the Cambodian Banking Sector

The modernization of Cambodia’s financial sector is further evidenced by the international recognition of its largest institutions. ABA Bank, a member of the nation’s "Big Four" alongside ACLEDA, Canadia Bank, and KB Prasac, was recently ranked as Cambodia’s top-performing bank in Forbes’ World’s Top Performing Banks 2026 report.

Finovate Global Cambodia: Partnerships in Fraud Fighting and Innovations in Payments

Ranking 31st globally among lower mid-size banks, ABA Bank has achieved this status through a massive scaling of its digital operations. Currently, the bank boasts assets of over $16 billion and serves more than five million mobile banking customers. Its strategy has centered on aggressive investment in self-service banking machines and a sprawling digital ecosystem that reaches deep into rural communities that were previously underbanked.

Askhat Azhikhanov, CEO of ABA Bank, attributed the ranking to a combination of institutional trust and technological foresight. "It is the result of the trust of millions of customers and our continued focus on building a strong, resilient, and forward-looking bank," Azhikhanov said. This success story reflects the broader trend in Cambodia, where banks are moving away from traditional branch-heavy models toward digital-first, high-tech financial services.

Implications for the Regional Financial Landscape

The convergence of these events suggests that Cambodia is positioning itself as a reliable and modernized financial hub within the ASEAN region. The security agreement with the UK signals that the country is shedding its past reputation as a haven for offshore criminal activity, choosing instead to align with international regulatory frameworks to protect its growing digital economy.

Simultaneously, the interoperability between KHQR and UPI signals a shift toward a more integrated regional payment architecture. By removing the need for cash and intermediary conversion, Cambodia is fostering a "frictionless" economic environment that is highly attractive to foreign investment and international tourism.

Future Outlook: Challenges and Opportunities

Despite the progress, the road ahead involves significant challenges. The technical integration of different national payment systems requires constant vigilance against cyber-threats, a point that is not lost on the government. The collaboration with the UK is a proactive measure to ensure that as Cambodia’s digital infrastructure grows, its defensive capabilities keep pace.

Furthermore, the success of the KHQR-UPI corridor will likely serve as a blueprint for future integrations with other nations. If successful, this could transform Cambodia into a central node for regional trade, utilizing its digital payment efficiency to facilitate easier commerce between South Asia and Southeast Asia.

As the country moves into the latter half of 2026, the focus will likely shift to "Phase 2" of the UPI-KHQR partnership: enabling Cambodian travelers to use their domestic apps in India. This move would complete the bilateral corridor, creating a seamless, two-way flow of capital and consumption. For global observers, Cambodia’s current trajectory offers a compelling case study on how emerging economies can leverage strategic international partnerships and aggressive digital adoption to leapfrog traditional development hurdles and emerge as robust, globally integrated financial players.

September 26, 2026 0 comment
0 FacebookTwitterPinterestEmail
FinTech Innovations

Mark Wahlberg to Discuss Strategic Investment and Entrepreneurial Evolution at TechCrunch Disrupt 2026

by admin September 26, 2026
written by admin

Mark Wahlberg is set to command the main stage at TechCrunch Disrupt 2026, marking a significant intersection between Hollywood celebrity and the sophisticated world of institutional-grade private equity. Joining him for this featured fireside chat is Bruce K. Lee, the founder and CEO of Keebeck Wealth Management. This session, scheduled for the upcoming October event in San Francisco, aims to deconstruct the transition of a high-profile entertainer into a diversified business mogul, focusing on the rigorous financial disciplines required to navigate the modern investment landscape.

The upcoming appearance underscores a broader industry trend wherein entertainers leverage their personal brands and capital to transition from passive celebrity endorsers to active, hands-on venture participants. For Wahlberg, this move is not a recent pivot but the culmination of a multi-decade trajectory that has seen him move from screen acting to the boardrooms of global corporations.

A Chronology of Entrepreneurial Expansion

Wahlberg’s journey into business began in the late 1990s, shortly after his critical breakthrough in Paul Thomas Anderson’s 1997 film Boogie Nights. While his acting career flourished—garnering two Academy Award nominations and a Golden Globe nod for The Fighter—Wahlberg simultaneously began laying the groundwork for a private investment portfolio.

By the early 2000s, Wahlberg established his production banner, which would eventually go on to produce hit television series such as HBO’s Entourage. This venture marked a transition from a salaried employee to an owner-operator. Following this, he expanded his footprint into the hospitality and retail sectors, launching the Wahlburgers restaurant chain and various fitness-related apparel and wellness ventures.

Mark Wahlberg is coming to TechCrunch Disrupt 2026, and he wants to talk about your work, not his

In 2001, he founded the Mark Wahlberg Youth Foundation, signaling an early commitment to corporate social responsibility that has remained a constant throughout his career. Over the past five years, however, his focus has shifted toward high-growth technology sectors, specifically health-tech and wellness, areas where he has increasingly sought the counsel of institutional experts like Bruce K. Lee. This shift represents a move toward a more disciplined, data-driven approach to asset allocation, distancing himself from the “celebrity investor” stereotype in favor of a more methodical methodology.

Building Institutional Discipline

The core of the discussion at TechCrunch Disrupt 2026 will center on the “institutionalization” of individual wealth. In many instances, high-net-worth individuals from the entertainment and athletic worlds struggle to bridge the gap between initial capital accumulation and long-term, sustainable wealth management.

Wahlberg’s partnership with Keebeck Wealth Management serves as a case study in this transition. Lee, whose firm manages complex portfolios for high-net-worth individuals, has reportedly been instrumental in helping Wahlberg navigate the intricacies of venture capital and private equity. According to preliminary insights, the session will focus on three key areas:

  1. Unlearning Old Instincts: Wahlberg has been candid about the necessity of abandoning the “gut-check” approach common in the entertainment industry in favor of the analytical rigor required to assess a startup’s scalability and market viability.
  2. Leveraging Social Capital for Deal Flow: The discussion will explore how established stars can use their reputation to gain access to exclusive investment rounds, while simultaneously ensuring that their presence adds value beyond mere capital.
  3. Sector-Specific Focus: With a growing interest in healthcare and wellness technology, Wahlberg is moving beyond generalist investing, aiming to understand the underlying infrastructure of the companies he backs.

The Broader Impact on Tech and Venture Capital

TechCrunch Disrupt, held at the Moscone West in San Francisco, acts as a bellwether for the technology sector. By inviting figures like Wahlberg, the event acknowledges the reality that the lines between cultural influence and venture capital are increasingly blurred.

The implications for the startup ecosystem are twofold. First, there is the democratization of capital. As celebrities become more sophisticated in their investment strategies, they provide an alternative source of funding that can be more patient and brand-conscious than traditional institutional venture capital. Second, the presence of such figures at technical conferences indicates a maturing of the "celebrity investor" asset class. It is no longer enough to attach a name to a company; stakeholders are now demanding that such investors provide measurable strategic value.

Mark Wahlberg is coming to TechCrunch Disrupt 2026, and he wants to talk about your work, not his

TechCrunch Disrupt 2026: The Landscape

The 2026 iteration of TechCrunch Disrupt is expected to draw over 10,000 attendees, including founders, venture capitalists, and technologists. The event agenda features more than 250 industry leaders across 200 sessions, with a heavy emphasis on AI-driven innovation, climate technology, and the future of the creator economy.

The choice of the Wahlberg-Lee session as a focal point of the conference highlights the organizer’s desire to bridge the gap between the high-level business strategy and the daily realities of startup development. As the technology industry faces a period of recalibration—characterized by higher interest rates and a move toward profitability over pure growth—the focus on disciplined, long-term wealth management is particularly salient.

Analytical Perspectives

Financial analysts observing the trend of celebrity-led venture capital note that there is a significant failure rate for those who do not adopt institutional discipline. The "celebrity halo effect" can often obscure poor fundamentals in the early stages of a company’s life. However, when paired with established financial advisors, celebrities often gain the ability to conduct proper due diligence, perform risk mitigation, and structure deals that are favorable to both the investor and the entrepreneur.

Wahlberg’s shift into the healthcare space is also indicative of a broader trend among high-net-worth individuals who are increasingly seeking "impact-driven" returns. By focusing on technologies that address chronic health issues or wellness, these investors align their portfolios with their personal interests, a strategy that often leads to higher engagement and better outcomes for the underlying businesses.

Looking Ahead

As the deadline for early-bird ticket pricing for TechCrunch Disrupt 2026 approaches at 11:59 p.m. PT tonight, the anticipation surrounding this specific fireside chat continues to grow. Attendees will have the opportunity to hear directly from Wahlberg regarding the mechanics of his investment playbook—an unvarnished look at the trial-and-error process that has defined his recent professional trajectory.

Mark Wahlberg is coming to TechCrunch Disrupt 2026, and he wants to talk about your work, not his

For those in the startup space, the value of this conversation lies in understanding how to engage with sophisticated, high-profile investors. For those in the financial sector, it serves as a masterclass in how to manage the expectations and the influence of a non-traditional client who has the power to disrupt markets simply through his involvement.

The session, which will take place on the Disrupt Stage, will be one of many critical touchpoints at this year’s gathering. With the tech sector continuing to navigate a volatile economic environment, the insights provided by practitioners who have successfully managed the transition from one high-stakes industry to another will prove invaluable for entrepreneurs looking to scale their own ventures in the years to come.

Ultimately, the story of Mark Wahlberg is one of professional reinvention. Whether on the set of a period piece or in the boardrooms of San Francisco, his ability to adapt to changing environments remains his most significant asset. At TechCrunch Disrupt 2026, that adaptability will be on full display, providing a blueprint for the next generation of business leaders who aspire to build, scale, and sustain a lasting impact in an ever-changing global economy.

September 26, 2026 0 comment
0 FacebookTwitterPinterestEmail
FinTech Innovations

Singapore Exchange Regulation Tightens Disclosure Standards for Listed Companies to Boost Long-Term Value and Transparency

by admin September 26, 2026
written by admin

Singapore Exchange Regulation (SGX RegCo) has unveiled a comprehensive overhaul of its listing requirements, mandating that listed companies provide significantly more granular disclosures regarding executive remuneration structures, formal dividend frameworks, and proactive investor relations practices. Designed to cement the financial hub’s reputation as a transparent, high-standard market, the regulatory shift aims to pivot corporate mindsets firmly toward sustainable, long-term value creation.

While the new rules will not officially take effect until January 1, 2027—with the inaugural wave of compliant annual reports scheduled for publication in 2028—the announcement marks a pivotal regulatory milestone for the local equity market. By establishing stricter benchmarks for corporate accountability, SGX RegCo is actively positioning Singapore to capture and retain increasingly selective global capital.

Executive Remuneration Overhaul and Alignment with Long-Term Value

Under the revised regulatory framework, annual reports covering financial years beginning on or after January 1, 2027, will require unprecedented transparency into how executive compensation is calculated. Issuers will be legally obligated to disclose the specific financial and non-financial performance metrics utilized to determine the remuneration packages of executive directors and key executive officers. Crucially, companies must explicitly demonstrate how these selected indicators align with broader corporate objectives centered around long-term value creation.

Historically, while a vast majority of Singaporean issuers incorporated financial indicators into their compensation frameworks, detailed public disclosures regarding those exact metrics remained sparse. Data from SGX RegCo reveals that while more than 90% of issuers utilized financial indicators in their remuneration models, only 47% transparently disclosed them in their published reports. This wide information gap has frequently drawn criticism from institutional investors and governance advocates seeking clear linkages between executive pay and shareholder returns. The forthcoming rules aim to dismantle this opacity, ensuring that executive enrichment directly mirrors corporate performance and stakeholder value.

Codifying Dividend and Investor Relations Policies

In tandem with executive remuneration reforms, the new SGX RegCo mandates require all listed entities to formally publish explicit dividend policies and structured investor relations (IR) guidelines.

The inclusion of a formal dividend policy, however, does not trap companies into rigid payout obligations. Recognizing that diverse firms require different capital allocation strategies, SGX RegCo explicitly clarified that issuers retaining capital to aggressively fund growth or R&D can readily outline these strategic rationales within their formal policies. The objective is not to dictate financial distributions, but rather to provide shareholders with predictable frameworks and clearer visibility into board-level capital management decisions.

Furthermore, companies must institute comprehensive investor relations policies that systematically define engagement channels and establish clear, accessible mechanisms for shareholders to communicate directly with corporate management. To operationalize this requirement, all listed issuers will be mandated to maintain either a dedicated website or a distinct investor engagement section on their existing web properties starting next year.

While SGXNET will firmly remain the official, primary channel for regulatory information dissemination, corporate websites will function as robust secondary hubs for stakeholder engagement. SGX RegCo has strongly encouraged issuers to host critical reference materials on these digital portals, including full annual reports, comprehensive minutes from annual general meetings (AGMs), investor presentation decks, and up-to-date calendars detailing upcoming corporate events.

Chronology and Regulatory Consultation Process

The path toward these enhanced disclosure standards is the culmination of months of meticulous regulatory deliberation, stakeholder engagement, and market consultation.

The consultative process kicked off in earnest in April, during which SGX RegCo published a formal consultation paper seeking comprehensive feedback from the broader financial ecosystem regarding proposed transparency enhancements. The feedback window remained open through May, yielding a diverse array of perspectives from 32 distinct respondents. This cohort included prominent asset managers, independent financial service providers, corporate representative bodies, listed issuers, and various market professionals.

Among the feedback received during the consultation period, several market participants advocated for an expansion of the disclosure scope beyond basic dividend policies to encompass a much broader spectrum of corporate capital management practices. In response, SGX RegCo confirmed that it would actively share these recommendations with the Corporate Governance Advisory Committee (CGAC). The committee will evaluate whether these broader capital management disclosures should be officially recommended and whether they are best integrated into the overarching Code of Corporate Governance or directly embedded within the formal listing rules.

Baseline Market Readiness: Where Issuers Stand Today

To gauge market readiness ahead of the 2027 implementation date, SGX RegCo conducted a comprehensive review of financial year 2025 annual reports published through May 31, 2026. The empirical findings indicate that while significant regulatory changes are ahead, the domestic corporate landscape is already organically trending toward these best practices.

The regulatory review demonstrated that more than 90% of listed issuers already maintained some form of website dedicated to investor engagement, successfully establishing rudimentary two-way communication channels for their investors. Additionally, roughly 80% of surveyed companies already disclosed the core objectives and guiding principles of their investor relations policies.

However, the data simultaneously exposed noticeable deficiencies in execution. While policies existed on paper, only a distinct minority of issuers provided granular, substantive details regarding the actual shareholder engagement activities they undertook throughout the year. Similarly, while compensation committees heavily relied on financial metrics, less than half bothered to explain them to their shareholders.

SGX RegCo’s leadership views these findings with a pragmatic eye. The data suggests that while there is ample room for qualitative improvement, the vast majority of issuers possess the foundational infrastructure required to adopt the new requirements without facing insurmountable operational friction.

Official Perspectives and Strategic Rationale

Addressing the strategic imperative behind the regulatory adjustments, SGX RegCo Chief Executive Tan Boon Gin underscored the critical nexus between corporate transparency and market attractiveness.

“Singapore’s equity market is benefiting from a resurgence of investor interest, but this interest will not last if boards and management do not increase investor engagement and demonstrate greater transparency—particularly transparency about how board or management decisions align with shareholder interests,” Tan remarked.

Tan further emphasized that the new rules are deliberately calibrated to strike a delicate balance between rigorous compliance and commercial agility. “The rule changes strengthen disclosure standards while preserving flexibility for issuers,” he stated. “We encourage issuers to look beyond the minimum requirements, and to provide substantive and meaningful disclosures, such that they can attract global capital and improve valuations.”

Broader Impact, Market Implications, and Economic Analysis

The introduction of these stricter disclosure mandates arrives at a critical juncture for the Singapore Exchange. As global institutional investors increasingly prioritize Environmental, Social, and Governance (ESG) criteria alongside robust corporate governance, exchanges worldwide are locked in a fierce competition for liquidity. Markets that fail to enforce high standards of corporate transparency risk seeing capital flow toward more rigorous jurisdictions.

By forcing companies to articulate clear rationales for executive pay, capital retention, and dividend distributions, SGX RegCo is directly addressing the "valuation discount" that has historically plagued certain segments of Southeast Asian equity markets. When investors can clearly trace the line connecting board decisions, executive incentives, and shareholder value, perceived risk diminishes, frequently resulting in improved valuation multiples and enhanced stock liquidity.

Moreover, the codification of structured investor relations ensures that retail and institutional shareholders alike are no longer treated as passive bystanders. By mandating accessible digital touchpoints and regular communication channels, the regulations democratize information access, fostering a healthier, more participatory corporate ecosystem.

Looking ahead, listed companies have been afforded a generous runway. With an implementation date set for January 1, 2027, corporate boards, remuneration committees, and investor relations teams have ample time to audit existing policies, upgrade digital infrastructure, and align internal metrics with the upcoming expectations. As corporate Singapore prepares for this new era of accountability, the ultimate measure of success will be found in 2028, when the first wave of annual reports hits the market, showcasing whether heightened transparency successfully translates into sustained global capital inflows and enhanced long-term value creation.

September 26, 2026 0 comment
0 FacebookTwitterPinterestEmail
NFT & Digital Assets

NFT Project Passport: Galactic Geckos

by admin September 26, 2026
written by admin

The evolution of decentralized digital assets on the Solana blockchain has witnessed numerous trends rise and fall over the years, yet few collections have demonstrated the enduring resilience of Galactic Geckos. Launched on September 22, 2021, during the nascent stages of the Solana non-fungible token (NFT) boom, Galactic Geckos—often referred to as Galactic Gecko Space Garage or GGSG—has transcended its initial categorization as a mere profile picture (PFP) project. Over a four-and-a-half-year period encompassing shifting market cycles, leadership restructuring, and infrastructural developments, GGSG has evolved into a lore-driven intellectual property (IP) brand, social adventure club, and multifaceted ecosystem.

As digital asset markets mature, understanding the trajectory of foundational projects like Galactic Geckos offers critical insights into community governance, deflationary tokenomics, and long-term value accrual in Web3. This comprehensive profile examines the origins, developmental milestones, structural innovations, and broader market implications of the Galactic Geckos ecosystem.

Main Facts and Project Snapshot

Galactic Geckos entered the Solana ecosystem during a period when the network was rapidly establishing itself as an alternative to Ethereum for high-throughput, low-cost digital collectibles. Conceived as a collection of 10,000 hand-drawn, warrior-turned-space-racing geckos, the project introduced a distinct sci-fi narrative that separated it from the primate-heavy PFP landscape of late 2021.

The initial mint price was established at 2 SOL. Over the subsequent years, the project’s supply distribution has shifted dramatically due to staking mechanics and deflationary mechanisms. Out of the total 10,000 supply, 902 assets have been permanently immortalized or soulbound, while 7,111 tokens remain long-term staked, predominantly locked for periods of 12 months or longer. Consequently, the actively circulating liquid supply represents a thin float of approximately 2,000 assets. As of late June 2026, the collection maintains a floor price of approximately 6.26 SOL (roughly $455 USD), backed by a holder base of nearly 3,000 unique addresses, according to network analytics from HowRare.

NFT Project Passport: Galactic Geckos

Market accessibility for Galactic Geckos spans multiple prominent Solana marketplaces, including Magic Eden, Tensor, Artifacte, and Orbis. The project operates without an external corporate treasury funded by venture capital or public token sales, relying instead on organic community alignment and a lean executive model.

Chronology and Historical Evolution

The timeline of Galactic Geckos is defined by distinct phases of conceptual inception, crisis management, and structural reinvention.

Phase One: Launch and Early Expansion (2021)

On September 22, 2021, the collection debuted on Solana. The artistic vision was executed by acclaimed illustrator Gossip Goblin, whose professional portfolio includes work on prominent collectible card games like Magic: The Gathering and various digital media projects. Gossip Goblin individually hand-drew 162 unique traits, embedding specific narrative backstories into each attribute.

Narratively, the collection established a universe where intergalactic conflicts were resolved through high-stakes spaceship racing rather than traditional warfare. Holders were divided among four distinct factions—Alura, Targari, Martu, and Barada—providing an early layer of social organization and identity within the community.

Phase Two: Leadership Restructuring and Community Buyout (2022)

Despite an enthusiastic initial launch, the project encountered significant headwinds stemming from misaligned incentives between the original founding team and the holder base. These friction points led to intensive negotiations that culminated in February 2022, when Genuine Articles and a collective of community members executed a complete buyout of the original founders.

NFT Project Passport: Galactic Geckos

This transition marked a critical turning point. Governance shifted toward a hybrid Decentralized Autonomous Organization (DAO) model. This structure combined a streamlined, agile executive team with broad community input, ensuring that subsequent strategic initiatives directly benefited the holders of the core NFT collection rather than extracting value for external entities.

Phase Three: Diversification and Ecosystem Building (2023–2026)

Following the restructuring, the project focused on compounding utility without relying on recurring fundraising rounds. In 2022 and 2023, the community launched GreenListed, an investment affiliate network designed to support Web3 and Solana ecosystem builders. GreenListed notably led the seed funding round for Matrica with a seven-figure investment and a board seat, helping establish a cross-chain token-gating infrastructure that is now widely utilized across multiple blockchains.

Concurrently, the project developed internal expertise groups focusing on decentralized finance (DeFi) optimization, liquidity management (DLMM), wellness, and social media monetization. The Gecko Growth Group, for instance, has assisted dozens of community members in scaling and monetizing their digital presences.

In early 2026, Galactic Geckos expanded its cross-chain footprint through participation in a collaborative activation with Lucid, tied to Yuga Labs’ Otherside metaverse. This initiative granted holders allocations for upcoming token generation events (TGE), such as LucidAI. Furthermore, Space Squid Studios—an affiliated development team—advanced the alpha release of Galactic Overdrive, a trading card game (TCG) four years in the development pipeline, designed to prioritize gameplay mechanics over speculative financial layers.

Structural Innovations and Tokenomics

A defining characteristic of the Galactic Geckos ecosystem is its approach to supply management and holder alignment. Unlike many generative NFT projects that suffer from inflation or fragmented utility tokens, GGSG engineered a closed-loop economic model anchored directly to the base collection.

NFT Project Passport: Galactic Geckos

The Hero’s Journey and Immortalization

The project pioneered advanced staking frameworks within the Solana ecosystem, notably introducing long-term lockup mechanisms known as the "Hero’s Journey" and "immortalization." Holders who commit their Geckos to soulbound, permanent staking remove those assets from circulation entirely. With over 900 assets permanently immortalized and more than 7,000 staked long-term, the project has systematically constricted its circulating float. This deflationary pressure operates as an intrinsic value-compounding mechanism as demand interacts with a diminishing pool of liquid assets.

The GeckoDAO and Investment Arm

Through GeckoDAO and GreenListed, holders gain indirect exposure to early-stage venture investments and technological developments within the broader blockchain landscape. Value generated from these investments and associated ecosystem airdrops—such as anticipated distributions from CUBE ($ISO) and LucidAI—is funneled back to active participants and staked asset holders. Historical tracking indicates that cumulative rewards distributed to staked Gecko holders have exceeded $23,000 per asset when measured against peak market valuations.

Broader Market Implications and Analysis

The trajectory of Galactic Geckos offers a compelling case study regarding the sustainability of NFT-centric IP brands through multiple crypto market cycles. Industry analysts note that while newer projects frequently rely on aggressive public marketing and high-frequency hype cycles, GGSG has maintained its relevance through a strategy of quiet, continuous building and organic community retention.

By avoiding external venture capital funding and recurring token dilutions, the project has preserved its structural integrity, preventing the conflicts of interest that often plague heavily funded Web3 startups. However, this understated communication strategy—favoring internal development milestones and "surprise-and-delight" reveals over public roadmaps—presents certain visibility challenges in a fast-paced market environment where attention spans are frequently captured by newer speculative assets.

Nevertheless, the longevity of Galactic Geckos demonstrates that distinct artistic identity, robust lore, and deeply aligned holder incentives can serve as a viable foundation for multi-year survival. As the project prepares for the broader public beta release of Galactic Overdrive and expands its physical merchandise and tokenized real-world asset (RWA) initiatives through late 2026, it continues to test the boundaries of how decentralized communities can autonomously sustain and grow valuable intellectual property.

September 26, 2026 0 comment
0 FacebookTwitterPinterestEmail
Tech & Startup News

FDA Nominee Overton Faces Scrutiny Over Political Influence and Public Health Policy During Confirmation Hearing

by admin September 26, 2026
written by admin

The confirmation hearing for the next head of the Food and Drug Administration (FDA) has descended into a contentious examination of the agency’s independence, as nominee Dr. Overton faced a barrage of questions regarding her willingness to challenge the administration on scientific matters. Senators from both sides of the aisle pressed for clarity on whether the FDA would serve as a bastion of evidence-based policymaking or as an extension of the president’s political agenda. The hearing highlighted profound anxieties concerning the integrity of public health guidance, particularly regarding vaccine safety, the regulation of tobacco products, and the influence of campaign contributions on regulatory outcomes.

A Pattern of Evasion on Scientific Consensus

The tension in the chamber reached a boiling point during an exchange with Senator Maggie Hassan (D-N.H.), who sought a definitive statement regarding President Trump’s previous claims linking Tylenol use during pregnancy to autism in children. Despite the overwhelming consensus among pediatricians and medical researchers that no such causal link exists, Dr. Overton declined to state that the president was incorrect.

When pressed to answer with a simple "yes or no," Overton opted for a technical qualification, noting only that there is "no current evidence of a causal link between Tylenol and autism." Her refusal to directly address the president’s rhetoric—which public health experts fear could discourage necessary pain management during pregnancy—drew sharp criticism from Hassan. The senator expressed deep concern that the nominee’s reluctance to acknowledge scientific falsehoods suggests a willingness to prioritize political loyalty over objective truth. This dynamic mirrors broader concerns within the scientific community that the FDA’s role as an arbiter of health data is being compromised by a mandate to align with the president’s personal assertions.

The Debate Over Vaccine Protocols

The scrutiny intensified when Senator Lisa Blunt-Rochester (D-Del.) turned the discussion toward the administration’s public commentary on vaccine delivery. Reports have surfaced suggesting that Overton herself may have advised the president on the possibility of splitting combination vaccines, such as the MMR (Measles, Mumps, and Rubella) shot, into individual components.

From a clinical perspective, the transition to individual vaccine doses would represent a monumental shift in public health infrastructure. Such a change would require years of rigorous clinical trials, massive federal investment in manufacturing, and a total restructuring of current immunization schedules. When Blunt-Rochester asked if Overton believed the suggestion to split vaccines constituted a "good option," the nominee remained steadfast in her refusal to critique the policy, stating that her role was to provide the president with a range of options rather than to adjudicate their merit.

Blunt-Rochester pushed back, arguing that the nominee’s inability to distinguish between viable health strategies and potentially harmful or inefficient ones undermines the credibility of her candidacy. The senator further questioned the depth of Overton’s review process, asking specifically if she had examined the logistical data regarding vaccine dosage sizes and the potential impact of disrupting a proven, long-standing immunization framework. The lack of clarity provided by the nominee left many committee members questioning whether the FDA would retain the authority to reject scientifically unsound suggestions originating from the White House.

The Flavored Vape Controversy and Corporate Influence

Perhaps the most damaging portion of the hearing concerned the FDA’s recent reversal on flavored vape products. The agency has been without a confirmed commissioner since the resignation of Dr. Marty Makary, who stepped down after clashing with the administration over the deregulation of flavored electronic nicotine delivery systems. The move, which occurred in early May, defied significant bipartisan pushback and ignored warnings from public health advocates who argue that such products are specifically designed to entice youth consumers.

Senator Chris Murphy (D-Conn.) laid out a timeline that painted a stark picture of the intersection between high-dollar political donations and regulatory policy. According to Murphy, on April 30, a major tobacco firm, Reynolds, contributed $8 million to the president’s political coffers. Within 48 hours, company representatives were reportedly granted a meeting with the president at the White House to advocate for a relaxation of FDA rules regarding flavored vapes. Just three days later, the administration issued new guidance that effectively paved the way for the products to remain on the market.

When asked by Murphy whether she perceived a link between the tobacco company’s donation and the subsequent policy shift, Overton explicitly rejected the premise of the question. "I reject the framing of that question," she stated, reiterating her belief that the president is "committed to the best possible outcomes for Americans." This response failed to satisfy the committee, as Murphy argued that the sequence of events created a clear appearance of a quid pro quo that undermines the FDA’s mandate to protect public health over corporate interests.

Broader Implications for FDA Independence

The FDA’s mandate is to protect public health by ensuring the safety, efficacy, and security of human and veterinary drugs, biological products, and medical devices. However, the events surrounding this confirmation hearing suggest a potential shift toward a model where the agency is increasingly responsive to executive directives rather than independent scientific review.

The resignation of Dr. Makary and the subsequent vacancy at the top of the agency have already caused significant turbulence. If the agency is perceived as being susceptible to political pressure—whether through the influence of campaign donors or the president’s personal medical theories—it risks losing the public’s trust. In the realm of public health, trust is the primary currency; once that is eroded, compliance with vaccine programs, drug safety warnings, and nutritional guidelines typically plummets.

Furthermore, the "options-based" approach described by Overton has raised alarms among ethics experts in government. While it is standard for an agency head to provide the executive branch with options, those options are historically vetted for scientific viability. The concern among the Senate committee is that the current administration expects options that are politically palatable, regardless of their scientific or medical foundation. If a nominee is unwilling to say "no" to a proposal that lacks empirical support, the system of checks and balances designed to protect the American public effectively ceases to function.

Future Challenges and Oversight

As the confirmation process moves forward, the committee faces a difficult choice. On one hand, the FDA requires stable, confirmed leadership to address pressing issues like the opioid crisis, the oversight of artificial intelligence in healthcare, and the ongoing stabilization of the drug supply chain. On the other hand, the senators’ concerns suggest that they view the nominee’s lack of independence as a disqualifying factor for a role that requires a high degree of scientific autonomy.

The next stages of the confirmation process will likely involve further requests for documentation regarding the internal communications between the FDA, the Department of Health and Human Services, and the White House. Should the nominee continue to maintain that her primary responsibility is to serve as an advisor to the president’s agenda rather than a guardian of scientific integrity, the vote in the Senate is expected to be closely contested.

Ultimately, the hearing has served as a litmus test for the future of federal science agencies. The debate is no longer just about the specific merits of vape regulations or vaccine schedules; it is about the fundamental definition of the FDA’s mission. As Senator Murphy and others have indicated, the American public deserves an agency that operates on data and objective reality, not on the shifting tides of political donation timelines and executive whims. Whether Dr. Overton can provide that level of assurance in the coming weeks remains to be seen, but the skepticism currently present in the Senate suggests that the path to confirmation will be fraught with further challenges. The outcome of this nomination will likely set a precedent for how federal agencies navigate the tension between presidential authority and scientific independence for years to come.

September 26, 2026 0 comment
0 FacebookTwitterPinterestEmail
Artificial Intelligence & Tech

Google Beam expands with new regions, partners, and customers

by admin September 26, 2026
written by admin

The Evolution of the Beam Ecosystem

The journey of Google Beam began as an internal effort to bridge the gap between distributed teams during the shift toward hybrid work. After successful internal deployments, Google identified a clear market demand for technology that could replicate the experience of being in the same room. Today’s announcement marks a transition from a controlled, internal experiment to a scalable global product.

The expansion strategy is multi-faceted, focusing on both hardware distribution and physical access. Google is now shipping Beam units to six key countries: the United States, Canada, the United Kingdom, France, Germany, and Japan. This rollout is supported by an international network of 18 strategic channel partners. These partners are specialized audiovisual integrators and distributors tasked with the logistical complexity of installing and maintaining the high-performance hardware, ensuring that enterprises can deploy the system without significant technical overhead.

Data-Driven Impact: Beyond Video Conferencing

To validate the efficacy of the system, Google conducted an extensive eight-week internal study, comparing traditional video conferencing methods against sessions facilitated by Google Beam. The metrics collected provide a compelling case for the technology’s utility in high-stakes environments.

According to the study, teams utilizing the Beam hardware reported a 50% increase in the sense of connection to their colleagues. More significantly, participants found it 33% easier to ensure their feedback was accurately interpreted, a metric that highlights the importance of spatial audio and life-sized visuals in preventing communication drift. Perhaps most impactful for operational efficiency, the company observed a 21% reduction in the necessity for follow-up meetings. By improving the clarity and efficacy of the initial interaction, the technology effectively reduces the "meeting fatigue" often caused by the need for repeated clarifications or fragmented communication.

Strategic Industry Partnerships

A significant milestone in this expansion is the collaboration with Bain & Company, which serves as a prime example of how the technology is being utilized in high-touch, human-centric sectors. The recruiting process, traditionally reliant on physical presence to gauge a candidate’s fit, has been modernized through the use of HP Dimension with Google Beam.

Keith Bevans, EVP and Partner at Bain & Company, noted the critical role of non-verbal communication in their assessment process. "One of the most challenging things for us to assess with candidates is how they’ll be with clients," Bevans stated. "There are so many nuances in body language and eye contact, and Google Beam allows us to virtually understand how people will engage in person, which is critically important for their success at Bain and the success of our mission with our clients."

This partnership underscores a shift in how firms view remote interviewing. By eliminating the necessity for cross-continental travel while maintaining the "human" element of the interview, firms can widen their talent search pool without compromising on the quality of their candidate assessment.

Google Beam expands with new regions, partners, and customers

Democratizing Access: The Industrious Network

Perhaps the most ambitious component of this expansion is the partnership with Industrious, a leading provider of premium flexible workspaces. Recognizing that not all companies—particularly startups and mid-market firms—can afford or justify the installation of dedicated telepresence suites in every office, Google is creating the "Beam Extended Network."

Starting this October, organizations will be able to book and utilize HP Dimension with Google Beam units at select Industrious locations in major business hubs, including Atlanta, Chicago, New York City, and Palo Alto. This "on-demand" model effectively lowers the barrier to entry for enterprise-grade communication technology. It allows remote-first startups to host client consultations or board meetings in a professional environment that conveys the presence and gravity of an in-person interaction, regardless of where their distributed team members are based.

Implications for the Future of Work

The broader implications of this expansion are significant for the enterprise software and hardware sectors. By integrating support for both Google Meet and Zoom, Google has positioned Beam as a neutral, high-end infrastructure layer rather than a walled-garden solution. This interoperability is key to its adoption in complex corporate environments where different departments may utilize disparate collaboration tools.

From a macroeconomic perspective, the adoption of such technology represents a shift in how companies approach their real estate footprints and talent acquisition. If high-fidelity telepresence can successfully mimic the social and collaborative benefits of physical offices, firms may continue to downsize their central headquarters in favor of decentralized, flexible hubs equipped with advanced communication tools.

Furthermore, the technology addresses the psychological toll of prolonged remote work. By facilitating more "natural" conversations, the system addresses the "Zoom fatigue" that has plagued global workforces since 2020. The ability to see colleagues at a human scale, with natural eye contact and spatial audio, helps restore the social fabric that is often frayed by the grid-view format of standard webcams.

Technical and Operational Outlook

As Google continues to roll out these units, the focus will likely shift toward latency reduction and the integration of AI-driven features. Future iterations could potentially include real-time translation or advanced gesture analysis, further enhancing the "copresence" experience. However, the current priority remains infrastructure stability and partner enablement. The 18-partner ecosystem is designed to ensure that the hardware functions with the reliability of a standard office appliance—a necessity for any technology that aims to be a cornerstone of business operations.

For enterprises considering the shift, the ROI is becoming increasingly clear: reduced travel costs, increased speed in decision-making, and an enhanced ability to retain global talent. As companies like Netflix, Capital Group, and others begin to incorporate these systems into their workflows, the standard for what constitutes a "productive remote meeting" is likely to rise.

The expansion of Google Beam is not merely a hardware rollout; it is a strategic maneuver to define the next era of professional interaction. By combining the accessibility of flexible workspaces with the high-fidelity capabilities of dedicated telepresence, Google is attempting to ensure that geography is no longer a limiting factor in human performance. As the pilot programs transition into permanent fixtures at locations like Industrious, the business world will be watching to see if this technology becomes the new standard for the modern, distributed global enterprise. The era of the "virtual office" is evolving into the era of the "connected workspace," and Google is positioning itself at the very center of that transformation.

September 26, 2026 0 comment
0 FacebookTwitterPinterestEmail
Newer Posts
Older Posts

Recent Posts

  • The Ethereum Foundation Launches New Resource Hub to Promote Blockchain as Neutral Digital Public Infrastructure for Global Institutions
  • Kraken Expands European Capabilities with the Listing of Societe Generale-FORGE’s MiCA-Compliant EURCV Stablecoin
  • Hyperliquid Shifts From Decentralized Exchange to Institutional Financial Backbone as Wall Street Giants Move In
  • A New Phase of the Internet: From Execution to Intention
  • Anthropic Unveils Breakthrough Cryptanalytic Capabilities Using Unreleased Claude Mythos Model

Recent Comments

No comments to show.
  • Facebook
  • Twitter

@2021 - All Right Reserved. Designed and Developed by PenciDesign


Back To Top
Dr Crypton
  • Home
  • About Us
  • Contact Us
  • Cookies Policy
  • Disclaimer
  • DMCA
  • Privacy Policy
  • Terms and Conditions

We are using cookies to give you the best experience on our website.

You can find out more about which cookies we are using or switch them off in .

Dr Crypton
Powered by  GDPR Cookie Compliance
Privacy Overview

This website uses cookies so that we can provide you with the best user experience possible. Cookie information is stored in your browser and performs functions such as recognising you when you return to our website and helping our team to understand which sections of the website you find most interesting and useful.

Strictly Necessary Cookies

Strictly Necessary Cookie should be enabled at all times so that we can save your preferences for cookie settings.