• Home
  • About Us
  • Contact Us
  • Cookies Policy
  • Disclaimer
  • DMCA
  • Privacy Policy
  • Terms and Conditions
Dr Crypton
Secure Your Future in Crypto
FinTech Innovations

TechCrunch Disrupt 2026 Launches BOGO Ticket Promotion as Countdown to San Francisco Event Begins

by admin September 24, 2026
written by admin

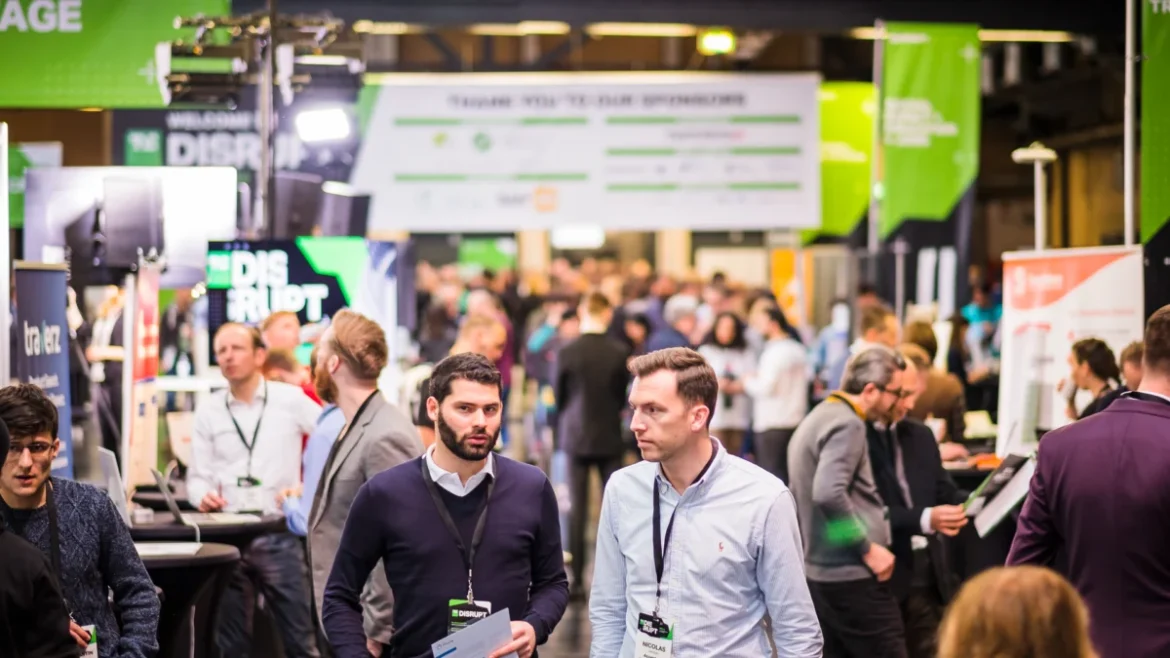
The technology industry’s premier innovation showcase, TechCrunch Disrupt 2026, is entering its final operational phase, with organizers announcing a strategic "Buy One, Get One" (BOGO) ticket initiative designed to bolster collaborative attendance. As the event approaches its October 13 opening at the Moscone West convention center in San Francisco, the organizers are offering a 50% discount on the second pass for any ticket type purchased. This promotional window remains active until the doors open at 8:00 a.m. PT on October 13, at which point standard pricing will resume.

The Strategic Value of Collaborative Attendance

The philosophy behind the BOGO promotion is rooted in the logistical reality of large-scale industry conferences. TechCrunch Disrupt, which runs from October 13 through October 15, serves as a hub for more than 10,000 founders, investors, engineers, and tech executives. Because the event features over 200 tactical sessions and spans six distinct industry stages, the organizers argue that the complexity of the agenda makes it difficult for a single individual to extract maximum value from the experience.

By incentivizing the attendance of co-founders, business partners, or colleagues, the event aims to facilitate a "divide and conquer" approach to networking and knowledge acquisition. When two members of an organization attend, they can simultaneously monitor different tracks—such as Artificial Intelligence, SaaS, Fintech, or hardware innovation—and synthesize their findings to create a more comprehensive strategic roadmap. This collaborative attendance model is intended to turn passive observation into actionable business intelligence, potentially accelerating product development cycles or fundraising efforts.

Event Overview and Industry Impact

Since its inception, TechCrunch Disrupt has positioned itself as a barometer for the broader technology ecosystem. The 2026 iteration is expected to host more than 300 early-stage and growth-stage startups, providing a centralized venue for deal-making and talent acquisition. The event’s structure is built on a foundation of "AI-powered matchmaking," a technology utilized to connect founders with investors based on specific industry verticals, funding stages, and technical requirements.

Bring your co-founder, partner, or colleague and get 50% off a second TechCrunch Disrupt 2026 pass

The significance of such gatherings has grown in the current economic climate, where capital efficiency and rapid iteration are prioritized. By gathering 250+ speakers—ranging from venture capitalists managing multibillion-dollar portfolios to technical leads from hyperscale enterprises—the event offers a unique cross-section of the industry’s current priorities. Historically, these sessions cover a spectrum of topics including the ethical implications of autonomous systems, the evolution of cloud infrastructure, and the changing landscape of global cybersecurity regulations.

Chronology and Operational Deadlines

The lead-up to Disrupt 2026 follows a structured timeline designed to manage attendee volume and logistical capacity.

  • Early September 2026: Initial registration phases for exhibitors and VIP attendees reach capacity, marking the shift toward general admission focus.
  • September 24, 2026: Launch of the BOGO 50% promotional offer for all ticket tiers, including Investor, Founder, Attendee, Non-profit, Student, and Expo+ passes.
  • September 25, 2026: A critical pricing deadline for individual ticket holders, with rates set to increase at 11:59 p.m. PT.
  • October 13, 2026 (8:00 a.m. PT): Official event kickoff at Moscone West. This serves as the absolute deadline for the BOGO offer; post-opening, standard pricing for remaining inventory applies.

Analysis of Ticket Tiers and Economic Implications

The promotional structure differentiates between the specific needs of various attendee cohorts, reflecting the diverse economic goals of participants:

Investors: This cohort is incentivized to bring associates or partners to help verify due diligence. By having two representatives on the floor, firms can increase their capacity for vetting startups, comparing signals in real-time, and identifying investment opportunities before they reach wider market awareness. The BOGO deal offers a potential savings of up to $450 per pair.

Founders: For early-stage companies, the cost of attendance is often weighed against potential funding outcomes. By reducing the cost for a co-founder or a key operational lead, the event allows startups to maintain a presence at booth exhibitions while simultaneously attending high-level investor panels. The potential $425 savings provides a meaningful reduction in the overhead required to participate in the event’s high-visibility startup showcase.

Bring your co-founder, partner, or colleague and get 50% off a second TechCrunch Disrupt 2026 pass

Operators and General Attendees: This category includes product managers, software engineers, and growth specialists. For these professionals, the value proposition lies in benchmarking their own company’s performance against industry peers. Accessing six industry stages allows teams to optimize their go-to-market strategies by learning from the successes and failures of others. Savings here reach up to $412 per pair.

Students and Non-profits: In a deliberate effort to lower the barrier to entry for the next generation of builders and mission-driven organizations, the BOGO initiative offers significant reductions for students ($175 savings) and non-profit representatives ($237 savings). These groups are encouraged to utilize the networking opportunities to secure mentorship or potential partnerships that might otherwise be inaccessible.

The Role of Networking and Infrastructure

The success of TechCrunch Disrupt is largely attributed to its role as a "force multiplier" for professional networks. Data from previous years suggests that the vast majority of participants identify "connection building" as their primary objective. The introduction of AI-driven matchmaking in recent years has shifted the event away from random encounters toward highly curated, intent-based meetings.

For attendees, the decision to bring a partner is not merely a financial calculation; it is a tactical choice to increase the "surface area" of the event. In a three-day window, a solitary attendee can typically participate in a limited number of high-stakes conversations. Two attendees, however, can effectively double the number of interactions, ranging from spontaneous networking at the coffee stations to formal, scheduled "Braindate" sessions that are a hallmark of the conference’s structure.

Navigating the Future of the Tech Landscape

As the industry prepares for the 2026 gathering, the prevailing sentiment among analysts is that the event will focus heavily on the maturation of generative AI applications and the transition from "hyped" technology to "utility" technology. The sessions are curated to address the "how" of business—how to scale under economic pressure, how to manage talent in a decentralized world, and how to maintain competitive advantages when technology commoditization occurs at an unprecedented rate.

Bring your co-founder, partner, or colleague and get 50% off a second TechCrunch Disrupt 2026 pass

The organizers emphasize that the event’s structure—from the "Builders Stage" to the "Investor Lounge"—is intended to mimic the actual lifecycle of a company. Whether an attendee is in the ideation phase, seeking Series A funding, or preparing for an IPO, the content is segmented to provide immediate, actionable relevance.

Final Call for Participation

As the October 13 deadline approaches, prospective attendees are encouraged to review the full agenda to ensure that the ticket type selected aligns with their specific professional objectives. The BOGO promotion is, by design, a limited-time opportunity to minimize the capital required to access a high-density network of peers and decision-makers.

For those who have not yet secured their place at Moscone West, the upcoming days represent the final opportunity to participate under the current promotional terms. Following the commencement of the event, the focus will shift entirely from acquisition to execution, as the global technology community converges in San Francisco to define the trajectory of the coming year.

(Disclosure: This article contains information regarding ticket sales and potential affiliate monetization through TechCrunch’s promotional links. Such arrangements do not influence the editorial content or the objective reporting of event details.)
September 24, 2026 0 comment
0 FacebookTwitterPinterestEmail
FinTech Innovations

Crowdcube Positions Secondary Share Trading as a Core Growth Driver with £750 Million Pipeline Backed by PISCES

by admin September 24, 2026
written by admin

Crowdcube, one of Europe’s leading equity crowdfunding and online investment platforms, has announced that secondary share transactions have rapidly evolved into a cornerstone of its commercial strategy. According to recent disclosures from the firm, an impressive £543 million in transactions facilitated through the United Kingdom’s Private Intermittent Securities and Capital Exchange System (PISCES) is currently winding its way through the platform’s pipeline. When calculated alongside other secondary listings, Crowdcube projects the potential for up to 29 distinct listings carrying a cumulative estimated value of £750 million over the course of the next two quarters.

This major strategic pivot highlights a broader maturation within the alternative finance sector. Traditionally, retail-focused equity crowdfunding platforms built their business models around primary issuances—connecting early-stage startups and high-growth ventures with retail and institutional risk capital. The fundamental objective was to democratize access to private asset classes that were historically reserved for venture capitalists and institutional heavyweights. Over the past decade, however, leading platforms have increasingly diversified their operations, moving beyond primary fundraising rounds to address a critical friction point in the private market lifecycle: liquidity.

The Evolution of Private Markets and the Rise of Secondaries

For years, the private market ecosystem faced a distinct structural bottleneck. As private companies chose to remain private for significantly longer periods—often delaying initial public offerings (IPOs) due to regulatory burdens, ample private liquidity, and shifting market conditions—early investors, founders, and long-serving employees found themselves locked into illiquid positions. While these firms achieved multi-billion-dollar valuations, stakeholders had few viable avenues to realize financial returns on their equity prior to a formal trade sale or public market debut.

Recognizing this market inefficiency, innovative platforms began laying the groundwork for secondary marketplaces. These secondary offerings enable the buying and selling of shares in privately held companies that have already secured substantial venture backing but have not yet gone public. By facilitating these transactions, platforms can bridge the gap between eager buyers seeking exposure to mature private firms and existing shareholders looking to monetize their stakes.

Crowdcube’s proactive stance in this arena began years before the introduction of formal governmental frameworks dedicated to private secondary trading. This early-mover advantage allowed the company to construct the underlying technological infrastructure, compliance protocols, and investor networks necessary to handle complex secondary transactions seamlessly. Consequently, when regulatory shifts created new pathways for private market liquidity, Crowdcube was uniquely positioned to capture significant market share.

The Role of PISCES and Regulatory Innovation in the United Kingdom

At the heart of the current surge in secondary trading is PISCES, an acronym for the Private Intermittent Securities and Capital Exchange System. PISCES represents a visionary legislative and regulatory initiative spearheaded by the UK government and financial authorities, designed to enhance the competitiveness and flexibility of both public and private capital markets across the country.

The primary objective of PISCES is to allow private companies to periodically trade their shares on a regulated platform without undergoing the rigorous, expensive, and time-consuming process of a full IPO. Under the PISCES framework, a private firm can remain private while still offering its shareholders and institutional investors structured windows of liquidity. These periodic trading events are hosted on authorized, regulated platforms, ensuring transparency, investor protection, and robust market integrity.

In a move that solidified its standing as a market leader, Crowdcube established a strategic partnership with the London Stock Exchange (LSE) to support this innovative service. Furthermore, Crowdcube operates as a Registered Auction Agent (RAA) on the London Stock Exchange Private Securities Market (PSM). The operational success of this ecosystem is already evident: the nascent PISCES and PSM framework has successfully facilitated four major transactions to date, with Crowdcube directly involved in three of those landmark deals executed on the LSE Private Securities Market.

Strategic Insights and Leadership Perspectives

The sheer velocity at which secondaries have integrated into Crowdcube’s overarching business model has surprised even industry veterans. The company notes that its current pipeline of secondary offerings features some of the most dynamic, fastest-growing technology and consumer brands across the United Kingdom and the broader European Union.

Matt Cooper, Co-Chief Executive Officer of Crowdcube, emphasized that the visibility and near-term nature of this pipeline distinguish it from traditional, highly unpredictable primary fundraising rounds.

"What is different about this pipeline is that it is near-term, and we have good visibility on it," Cooper stated in a recent company blog post. "We built the infrastructure for this before PISCES existed, and that is why these transactions are coming to us."

Cooper’s remarks underscore the importance of operational readiness in the fintech sector. By anticipating the regulatory shift toward private market liquidity and investing heavily in proprietary trading infrastructure years in advance, Crowdcube avoided the lag time that typically plagues legacy financial institutions when new asset classes emerge.

Global Parallels and Market Transformation

Crowdcube’s strategic pivot mirrors a broader macroeconomic trend observed globally, most notably in the United States. Over the past several years, multiple prominent US-based private market platforms have expanded their operational scopes well beyond primary issuances. By establishing robust secondary marketplaces, these platforms have transformed from niche startup funding portals into comprehensive private equity ecosystems.

For Crowdcube, this transition is fundamentally reshaping the company’s financial profile and commercial trajectory. Executive leadership notes that secondary transactions are not merely an auxiliary revenue stream; rather, they are actively driving overall corporate growth and geographic expansion. Industry analysts suggest that if current projections hold, secondary offerings could soon eclipse primary fundraising to become the single largest segment of Crowdcube’s business, fostering a more resilient, diversified, and sustainable corporate model.

While the vast majority of transactions executed under the PISCES framework thus far have involved domestic UK enterprises, Crowdcube reports a notable uptick in inbound interest from continental European companies. These firms are increasingly looking toward the UK’s regulatory framework and Crowdcube’s digital infrastructure to orchestrate their own upcoming liquidity events, signaling the cross-border appeal and scalability of the model.

Broader Economic Implications and Future Outlook

The rapid scaling of private secondary markets has profound implications for the wider financial ecosystem. For institutional investors, family offices, and high-net-worth individuals, platforms like Crowdcube offer unprecedented access to late-stage private companies that were previously walled off behind institutional syndicates. This democratization of private equity helps distribute wealth-generation opportunities more broadly across the investor base.

Simultaneously, for late-stage private companies, the availability of structured liquidity events via PISCES relieves the immense pressure to pursue premature public listings. Companies can focus on long-term operational execution and strategic growth without alienating early employees and angel investors who require periodic cash realization. By offering a controlled, periodic trading environment, PISCES bridges the historical chasm between private agility and public market liquidity.

As Crowdcube works to convert its £750 million pipeline over the upcoming quarters, the platform’s performance will likely serve as a bellwether for the broader viability of intermittent private trading systems. With strong institutional backing, regulatory support through the London Stock Exchange partnership, and a rapidly expanding European footprint, Crowdcube is well-positioned to lead the next evolution of private market finance.

September 24, 2026 0 comment
0 FacebookTwitterPinterestEmail
NFT & Digital Assets

NFT Project Passport: Galactic Geckos

by admin September 24, 2026
written by admin

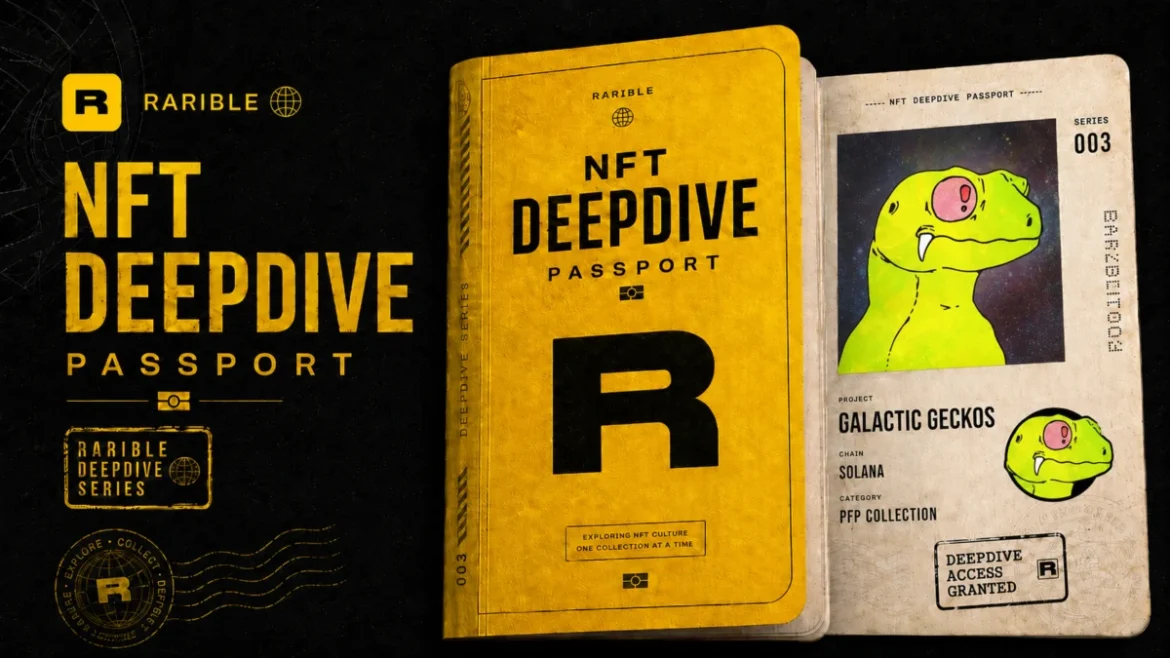
The digital asset landscape is littered with the remnants of short-lived hype cycles, failed roadmaps, and abandoned community initiatives. Yet, within the fast-moving and volatile Solana ecosystem, a select few foundational projects have managed to weather multiple market corrections, redefining what it means to be a long-term decentralized brand. Among these enduring pioneers is Galactic Geckos, officially recognized as Galactic Gecko Space Garage (GGSG). Launched in September 2021 during the nascent stages of Solana’s NFT boom, the project has evolved from a standard profile picture (PFP) collection into a comprehensive social adventure club, a lore-driven intellectual property (IP) brand, and a resilient decentralized autonomous organization (DAO) ecosystem.

This comprehensive project profile examines the historical trajectory, structural shifts, and recent developments surrounding Galactic Geckos. By evaluating its deflationary mechanics, community-led evolution, and expansion into gaming and cross-chain activations, this report provides a fact-based analysis of how GGSG has sustained its relevance and value proposition over nearly half a decade of Web3 evolution.

Project Snapshot and Market Fundamentals

At its core, Galactic Geckos is structured around a total fixed supply of 10,000 hand-drawn digital assets depicting warrior-class, space-racing reptiles. Minted originally on September 22, 2021, at an initial price of 2 SOL, the collection has witnessed significant market fluctuations, mirroring the broader macroeconomic cycles of the cryptocurrency industry.

As of June 2026, the collection maintains a floor price of approximately 6.26 SOL (roughly $455), backed by a holder base of approximately 2,983 unique wallets as tracked by analytics platforms such as HowRare. The historical performance of the asset highlights substantial value retention, reaching an all-time high floor of 65 SOL in April 2023, with CoinGecko data recording peak valuations of approximately $4,400 per unit in December 2023.

NFT Project Passport: Galactic Geckos

Crucially, the circulating supply of liquid Galactic Geckos is heavily constrained by structural design choices. Out of the 10,000 total supply, 902 assets have been permanently immortalized through soulbound staking mechanisms, while 7,111 tokens remain locked in long-term staking contracts—the majority of which have been committed for periods of 12 months or longer. This leaves an effectively thin float of approximately 2,000 actively tradeable assets on secondary marketplaces including Magic Eden, Tensor, Artifacte, and Orbis, creating an underlying supply-and-demand dynamic that protects the collection from sudden liquidity shocks.

Origins, Artistic Vision, and the 2022 Leadership Transition

The conceptual foundation of Galactic Geckos was established during a period when the Solana network was rapidly gaining traction as a high-speed, low-cost alternative to Ethereum for generative art and collectibles. While the early Solana landscape was heavily dominated by primate-themed PFP projects, GGSG introduced a distinct sci-fi narrative centered on intergalactic conflict resolved through high-stakes spaceship racing rather than traditional warfare.

The artistic integrity of the collection was spearheaded by acclaimed artist Gossip Goblin, whose professional portfolio includes contributions to major fantasy card games such as Magic: The Gathering. Gossip Goblin manually drew every individual trait within the collection, resulting in 162 unique visual components, each accompanied by detailed narrative lore. Furthermore, the collection was divided into four distinct factions—Alura, Targari, Martu, and Barada—which provided holders with an immediate sense of tribal identity and fueled community engagement beyond simple speculative trading.

Despite its strong conceptual launch, the project encountered severe operational friction during its first few months. A misalignment of financial and operational incentives between the original founding team and the broader holder community led to mounting dissatisfaction and protracted negotiations. Recognizing the existential threat posed by this friction, a decisive restructuring occurred in February 2022. GenuineArticles, alongside a dedicated collective of community members, successfully bought out the original founders, transitioning the project into a community-governed and led entity.

This leadership overhaul fundamentally altered the trajectory of GGSG. The newly established management team discarded top-down corporate directives in favor of a hybrid DAO executive model. This framework combined a lean, agile operational core with a flat organizational structure, enabling rapid execution while maintaining deep alignment with community stakeholders. Through this transition, the overarching mandate of the DAO became strictly focused on routing all ecosystem value back to the original Gecko holders, avoiding the recurring external fundraising rounds that often burden Web3 projects.

NFT Project Passport: Galactic Geckos

Ecosystem Expansion: From Staking Innovations to the Galactic Overdrive TCG

In the years following the 2022 buyout, Galactic Geckos systematically expanded its utility footprint without resorting to inflationary token models or aggressive public-facing marketing campaigns. Instead, the project adopted a "build quietly and compound capability" philosophy, resulting in a diverse suite of proprietary tools and ecosystem extensions.

Among its most notable structural innovations was the pioneering of the "Hero’s Journey" and "immortalization" staking mechanics. By committing assets to long-term lockups or soulbound permanent staking, holders effectively removed significant portions of the supply from circulation while unlocking tiered reward streams. According to project analytics and historical CoinGecko charts, cumulative rewards distributed to staked Gecko holders have historically exceeded $23,000 at peak valuations, augmented by anticipated token generation events (TGEs) from ecosystem partners such as LucidAI and CUBE ($ISO).

Simultaneously, the project established GreenListed, a community-led investment and incubation affiliate. GreenListed has functioned as an early-stage venture vehicle for Solana and broader Web3 builders, famously leading the seed funding round for Matrica with a seven-figure investment and a secured board seat. Matrica has since matured into a leading cross-chain token-gating protocol utilized across multiple blockchain ecosystems, validating the strategic foresight of the GGSG investment arm.

In January 2026, the ecosystem achieved a significant milestone with the alpha release of Galactic Overdrive, a trading-card game developed by Space Squid Studios in close partnership with GGSG. Designed after four years of deliberate development, the game prioritized user experience and engaging gameplay mechanics over immediate financialization. Initial alpha testing metrics on iOS, Android, and web demonstrated high user retention, with over 90 percent of participants returning for multiple sessions and more than 20 percent engaging on a daily basis without financial incentives. A broader public beta rollout is scheduled for the third quarter of 2026.

Concurrently, the project has enhanced its digital infrastructure by launching Collector Profiles and comprehensive holder tools. These applications provide advanced rarity research, airdrop tracking, and gamified badges that surface and reward active participation within the ecosystem. Furthermore, specialized internal community groups—focusing on domains ranging from artificial intelligence expertise and DeFi optimization to X (formerly Twitter) growth and personal wellness—have successfully equipped members with professional skills, with the Gecko Growth Group alone assisting over 80 members in monetizing their social media presence.

NFT Project Passport: Galactic Geckos

Broader Industry Impact and Strategic Implications

The longevity and trajectory of Galactic Geckos offer several important insights into the economic sustainability of NFT-based intellectual property brands. In an industry sector where public momentum is frequently manufactured through high-frequency marketing campaigns and expansive, often unfulfilled roadmaps, GGSG has maintained a deliberately understated public profile.

By prioritizing organic community alignment, deflationary supply mechanisms, and tangible utility over speculative hype, the project has demonstrated that legacy NFT collections can successfully transition into diversified decentralized enterprises. Cross-community initiatives, such as the January 2026 activation connecting Galactic Geckos to Yuga Labs’ Otherside metaverse via LucidAI allocations, further underscore the brand’s ability to transcend its native blockchain environment and integrate into broader digital culture.

Looking toward the remainder of 2026 and beyond, the project’s strategic roadmap remains deliberately flexible, eschewing rigid timelines in favor of adaptive execution. Confirmed initiatives include the forthcoming expansion of physical merchandise, tokenized physical goods, and real-world asset (RWA) partnerships, alongside the anticipated scale-up of the Galactic Overdrive TCG.

As the digital asset market matures, projects like Galactic Geckos serve as empirical testaments to the power of resilient community ownership. By weathering governance crises, shifting market narratives, and severe macroeconomic contractions without relying on external venture capital extraction, GGSG has established a durable blueprint for community-driven intellectual property development in the Web3 era.

September 24, 2026 0 comment
0 FacebookTwitterPinterestEmail
NFT & Digital Assets

The Rise of Argonauts and the Return to Artist-Centric NFT Collecting

by admin September 24, 2026
written by admin

Today, the digital art landscape witnessed a significant shift in market behavior as Argonauts, the latest 10,000-piece collection by the crypto-native artist a.c.k. (@lphaCentauriKid), minted out in a matter of minutes. Priced at approximately 0.12 ETH—roughly $300 at the time of the sale—the collection’s rapid depletion of supply was not driven by the typical speculative frenzy that characterized the 2021 bull market, but rather by a concentrated effort from a community of artists, long-term collectors, and patrons of crypto-native aesthetics. While the secondary market for NFTs has faced extreme volatility over the past twenty-four months, the success of Argonauts serves as a data point indicating a potential transition toward a more sustainable, art-first ecosystem.

The Mechanics of the Mint and Market Context

The minting process for Argonauts began with a clear, artist-led value proposition. Unlike the "roadmap-heavy" project models that dominated the NFT space in recent years—where utility, tokenomics, and metaverse integration were used to justify price floors—a.c.k. opted for a minimalist approach. By positioning the collection as a direct extension of his established body of work, the artist bypassed the need to manufacture artificial demand.

The chronology of the release was swift. Within minutes of the contract opening, the 10,000 pieces were fully distributed. This velocity of sale, particularly in a market environment currently wary of high-supply collections, suggests that the collector base for crypto-art has become highly sophisticated. Data from the mint suggests that the primary purchasers were not anonymous "flippers" seeking immediate arbitrage opportunities, but rather wallets with histories of holding blue-chip digital art and supporting mid-career digital creators.

Historical Context: From Speculation to Provenance

To understand the significance of the Argonauts mint, one must examine the evolution of the NFT sector. During the height of the 2021 market boom, the narrative surrounding NFTs became increasingly commoditized. Projects were frequently launched as startup entities, promising future perks, "staking" rewards, and elaborate, often undeliverable, utility. This shift alienated many traditional art collectors, who viewed these projects as financial instruments rather than creative assets.

The foundational promise of NFTs—the ability to establish digital provenance, enforce scarcity, and facilitate a direct, transparent relationship between the artist and the buyer—was often obscured by the noise of speculative trading. The Argonauts launch acts as a correction to this trend. By focusing on the visual language that a.c.k. has cultivated over several years of production, the collection returns to the fundamental utility of the medium: the act of owning and supporting the work of a specific artist.

The Role of Accessibility in Digital Art

A persistent challenge in the digital art market has been the issue of accessibility. As artists gain prestige, their primary works often reach price points that exclude all but the most affluent collectors. Historically, this has created a "whale-dominated" market, where only a small percentage of participants can afford to engage with an artist’s ecosystem.

The 10,000-piece format utilized by Argonauts provides a strategic solution to this barrier. By offering a larger supply at an accessible entry price, a.c.k. has effectively democratized participation in his body of work. This strategy allows a wider demographic—including fellow artists, curators, and emerging collectors—to secure a stake in the artist’s output. This shift is vital for the long-term health of the crypto-art market; it builds a broad, inclusive foundation that is more resilient to the departures of high-net-worth speculators.

Demographic Analysis: Artists Collecting Artists

One of the most notable aspects of the Argonauts collection is the demographic profile of the holders. Industry analysts have noted a trend where established digital artists are increasingly becoming the primary collectors of their peers’ work. This phenomenon creates a "virtuous circle" of value, where the credibility of the ecosystem is bolstered by the participation of those who understand the technical and aesthetic nuances of the medium.

When an artist with a significant following releases a collection that is immediately absorbed by other practitioners in the field, it signals a consensus on the work’s artistic merit. This form of "social proof" is far more durable than the marketing-led hype cycles that plagued the NFT space in the past. It suggests that the value of Argonauts is anchored in cultural capital rather than speculative volatility.

Implications for Future Market Cycles

The successful sellout of Argonauts provides a blueprint for the next phase of the digital asset market. If the primary driver of future success is, once again, the quality of the art and the strength of the artist’s reputation, then the industry is likely entering a period of "professionalization."

In this emerging era, we can expect a decline in the dominance of collections that rely on "roadmap" promises. Instead, collectors are likely to prioritize:

  1. Provenance: The verifiable history of the artist’s career and their previous output.
  2. Aesthetic Cohesion: A clear, identifiable visual language that exists independently of the blockchain.
  3. Community Composition: The presence of genuine peers and long-term supporters within the holder base.

This evolution mirrors traditional fine art markets, where reputation and provenance are the primary determinants of value. By aligning itself with these historical precedents, the digital art space may finally be moving toward a model of permanence.

The Sustainability of the Artist-Collector Relationship

The relationship between the artist and the collector is the bedrock of any successful creative economy. For years, the NFT space treated this relationship as a transactional, short-term arrangement. The Argonauts launch, however, highlights the importance of fostering long-term engagement. When collectors believe in the trajectory of an artist’s career, they are more likely to hold their assets through market fluctuations, providing the stability that digital creators need to produce their best work.

Furthermore, the lack of reliance on secondary-market volatility suggests that both a.c.k. and his collectors are focused on the long-term appreciation of the art. This is a critical departure from the "mint-and-dump" culture that characterized the early 2020s, where projects often collapsed as soon as the initial hype dissipated.

Broader Impact on Digital Infrastructure

The broader implications of this shift extend beyond the art market. It reinforces the utility of blockchain technology as a tool for artistic distribution rather than just financial speculation. As the industry moves toward more stable, interest-based communities, the technological infrastructure supporting these assets—such as marketplaces, smart contract standards, and display platforms—will likely evolve to cater to the needs of collectors who prioritize quality over quick returns.

The success of the Argonauts mint proves that the demand for crypto-native art has not evaporated; it has simply matured. Collectors are no longer satisfied with empty promises of utility. They are looking for substantive, artist-led projects that offer a clear connection to the creator’s vision.

Conclusion: A Return to Fundamentals

The Argonauts collection by a.c.k. stands as a testament to the endurance of artistic value in the digital age. By ignoring the pressures of the speculative market and focusing on the core relationship between artist and collector, the project has successfully navigated a challenging economic environment.

This development is a signal to the entire NFT ecosystem: the era of the speculative "road-mapped" project is waning, and the era of the artist-centric collection is emerging. If the market continues to prioritize genuine appreciation, provenance, and the sustained support of creators, the digital art world will emerge from its current period of volatility not only intact but more robust than it has ever been. The success of this mint is not just a triumph for a.c.k.; it is a proof-of-concept for a healthier, more sustainable future for digital ownership.

As the dust settles on the Argonauts mint, the focus remains on the art itself—a simple, revolutionary concept that, after years of complexity and confusion, finally feels like it is coming home. Through this collection, the community has shown that it is ready to move beyond the experimental phase of NFTs and into a more mature, refined chapter of digital art history.

September 24, 2026 0 comment
0 FacebookTwitterPinterestEmail
Tech & Startup News

Massive 75% Discount on One-Year BJ’s Wholesale Club Memberships Arrives Just in Time for the Holiday Shopping Rush

by admin September 24, 2026
written by admin

As autumn settles in and households begin shifting their focus toward seasonal festivities, cooler-weather cooking, and early holiday preparations, major warehouse clubs are rolling out aggressive membership promotions to capture budget-conscious consumers. Among the most competitive offers currently on the market is a newly launched deal that slashes the price of a standard one-year BJ’s Wholesale Club Membership down to just $15. Marking a substantial 75% markdown from the standard annual rate of $60, this limited-time promotion provides new members with full access to the retailer’s extensive network of wholesale goods, digital shopping conveniences, and specialized member perks.

The timing of the discount is strategically aligned with the calendar. Industry analysts frequently note that the final quarter of the year drives the highest volume of warehouse club acquisitions, as consumers prepare for large family gatherings, Thanksgiving dinners, winter holidays, and the stocking of pantry essentials. By reducing the barrier to entry to a mere $15, BJ’s Wholesale Club is positioning itself to attract shoppers who might otherwise hesitate to pay full price for an annual subscription they have yet to test.

Main Facts of the Promotion and Membership Structure

The $15 promotional rate applies strictly to new members who enroll using the designated digital redemption process. Purchasing the deal yields a unique redemption code that must be activated directly on BJs.com. As a condition of this heavily discounted rate, the membership automatically enrolls the user in BJ’s Easy Renewal program, a standard industry practice for introductory warehouse offers that ensures future renewals are billed at the standard annual rate unless canceled by the subscriber.

Once activated, the membership grants the cardholder full access to all physical club locations, online shopping platforms, and secondary services. According to corporate data published by BJ’s Wholesale Club, members can save up to 25% off traditional grocery store prices across a wide array of departments. This includes fresh produce, USDA Choice meats, deli platters, bakery goods, household paper products, cleaning supplies, consumer electronics, and rotating seasonal merchandise.

Furthermore, the membership extends beyond simple in-store shopping. Members are permitted to utilize a robust suite of digital and logistical conveniences, including Curbside Pickup and Same-Day Delivery options for those who prefer not to navigate crowded aisles. For in-store shoppers, the proprietary ExpressPay® feature within the BJ’s mobile app allows customers to scan item barcodes as they place them in their carts and pay digitally, bypassing traditional checkout lines entirely. Additionally, BJ’s maintains a unique pricing policy regarding coupons: the warehouse club accepts manufacturer coupons and permits shoppers to stack them alongside hundreds of in-house BJ’s digital coupons, maximizing potential savings on brand-name goods.

Background Context: The Evolution of Warehouse Clubs in the Retail Landscape

To fully understand the significance of steep membership promotions, one must examine the broader evolution of the warehouse club industry over the past several decades. Pioneered in the late 20th century, the warehouse club model relies on a membership-fee revenue structure that allows operators to sell merchandise at razor-thin profit margins. By limiting product variety—typically stocking only high-volume items and popular national brands rather than thousands of niche SKUs—clubs achieve immense purchasing power with manufacturers.

In recent years, macroeconomic pressures, including persistent inflation and fluctuating grocery costs, have driven a massive resurgence in consumer interest toward wholesale shopping. Households facing elevated grocery bills are increasingly looking for ways to stretch their disposable income. Buying in bulk has transitioned from a niche preference for large families to a strategic financial tool for households of all sizes aiming to lower their cost-per-unit spending on daily necessities.

Competitors such as Costco, Sam’s Club, and BJ’s Wholesale Club have all leveraged introductory discounts, gift card incentives, and digital app integrations to capture market share. BJ’s, with a strong historical footprint along the East Coast of the United States, has continuously expanded its digital infrastructure, refined its private-label offerings (such as Wellsley Farms and Berkley Jensen), and introduced fuel savings to remain competitive against its larger national rivals.

Chronology of Membership Incentives and Seasonal Retail Trends

The rollout of autumn membership promotions follows a predictable annual retail calendar that retailers have perfected over decades. Understanding this timeline highlights why discounts like the $15 BJ’s membership appear precisely when they do.

During the late winter and early spring months (January through April), warehouse clubs typically focus on health, fitness, organization, and early spring cleaning promotions. Membership drives during this quarter often target consumers seeking lifestyle resets or tax-season financial management.

As summer transitions into early fall (August and September), retail strategies pivot sharply. This period marks the back-to-school shopping rush, followed immediately by the arrival of autumn decorations, early Halloween inventory, and preparations for the final quarter’s major holidays. Retailers recognize that consumer spending velocity increases exponentially between October and December. By introducing a $15 promotional price point in September, BJ’s Wholesale Club captures consumers precisely at the psychological inflection point when shopping lists begin to expand.

Historically, warehouse club introductory rates fluctuate between free memberships, gift card bundles, and steep cash discounts. A flat $15 rate represents one of the most aggressive cash reductions offered by the brand, bypassing the need to wait for a promotional gift card to clear or meeting complex spending thresholds.

Detailed Analysis of Member Perks and Ancillary Services

Beyond the traditional savings found in grocery and household goods aisles, warehouse club memberships increasingly derive their value from ancillary services. For members who commute or travel frequently, these secondary perks often offset the cost of the membership entirely within the first few months of use.

Fuel Savings and Transportation Services
One of the most heavily utilized ancillary benefits of a BJ’s membership is access to BJ’s Gas stations. The company reports that members save an average of 20 cents per gallon compared to local average market fuel prices. For a standard commuter vehicle, these fuel savings accumulate rapidly over the course of a 12-month membership period.

In addition to fueling stations, BJ’s operates dedicated Tire Centers. Members can purchase major tire brands, receive complimentary tire rotation and balancing services for the life of tires purchased at the club, and utilize flat repair services.

Specialized In-Club and Partner Services
BJ’s operational footprint extends well beyond retail goods through partnerships and specialized in-house departments:

  • BJ’s Optical: Offers comprehensive eye exams (where available), designer frames, contact lenses, and prescription lenses at discounted member rates.
  • BJ’s Home Improvement: Provides members with vetted contractor services for major residential upgrades, such as roofing, siding, and window replacements, often backed by member-exclusive financing terms or gift card rebates.
  • BJ’s Travel: Functions as a full-service travel agency, offering members exclusive discounts on vacation packages, cruises, rental cars, and hotel bookings.

Economic Implications and Consumer Strategy

The strategy of offering a $15 annual membership carries distinct economic implications for both the retailer and the consumer. For BJ’s Wholesale Club, lower upfront membership fees serve as a customer acquisition engine. The primary goal of the business model is member retention; once a consumer becomes accustomed to bulk purchasing, digital coupon stacking, and same-day delivery services, they are statistically likely to renew their membership at the standard $60 rate upon expiration.

For the consumer, analyzing the utility of such an offer requires a basic calculation of household consumption patterns. Financial analysts note that a $15 investment carries virtually negligible financial risk. Even for single-person households or couples who do not purchase massive quantities of food, savings realized on household paper goods, gasoline, and occasional electronics purchases can easily surpass the $15 threshold within a single shopping trip.

However, consumers must remain cognizant of the automatic renewal mechanism attached to introductory offers. Because the promotion requires enrollment in BJ’s Easy Renewal, subscribers who do not wish to be billed the standard $60 rate for the subsequent year must proactively manage their account settings prior to the end of the 12-month term.

Statements and Industry Reactions Regarding Wholesale Membership Trends

While specific executive commentary regarding this exact $15 flash promotion reflects standard corporate promotional disclosures, broader retail industry consensus highlights the shifting demographics of warehouse club shoppers. Financial earnings reports released throughout the retail sector indicate that warehouse clubs are experiencing steady membership growth, driven heavily by younger demographics, including Millennials and Gen Z consumers setting up independent households.

Retail analysts point out that younger consumers are increasingly pragmatic regarding inflation, viewing warehouse clubs not merely as bulk-buying warehouses for large families, but as essential tools for household budgeting. The ability to purchase high-quality private-label goods—which often match national brand quality at a fraction of the cost—has become a cornerstone of modern consumer shopping strategy.

Furthermore, supply chain experts note that warehouse clubs have successfully insulated themselves against various supply disruptions by maintaining robust supplier relationships and focusing on high-velocity core items. This operational stability allows clubs to offer consistent pricing stability that traditional supermarkets struggle to match during inflationary cycles.

Conclusion and Actionable Information for Prospective Members

The availability of a one-year BJ’s Wholesale Club Membership for $15 represents a rare cost-reduction opportunity in an otherwise high-cost retail environment. With standard annual memberships normally priced at $60, the 75% discount lowers the financial barrier for households looking to test the benefits of wholesale shopping ahead of the holiday season.

The offer is strictly designated for new members. Interested individuals must purchase the redemption code through authorized promotional platforms, such as StackSocial, and subsequently complete the activation process on BJs.com. Because the promotion mandates enrollment in BJ’s Easy Renewal, users should keep track of their renewal timelines to maintain control over future subscription costs.

As the retail calendar moves deeper into the peak autumn and winter shopping season, promotional offers of this magnitude are typically subject to strict inventory or time limits. For consumers aiming to trim their grocery budgets, reduce fuel expenditures, and streamline holiday preparations, the $15 membership option provides an economically sound entry point into the world of wholesale retail.

September 24, 2026 0 comment
0 FacebookTwitterPinterestEmail
Artificial Intelligence & Tech

Model Context Protocol Explained: A Five-Minute Guide to AI Integration Standards

by admin September 24, 2026
written by admin

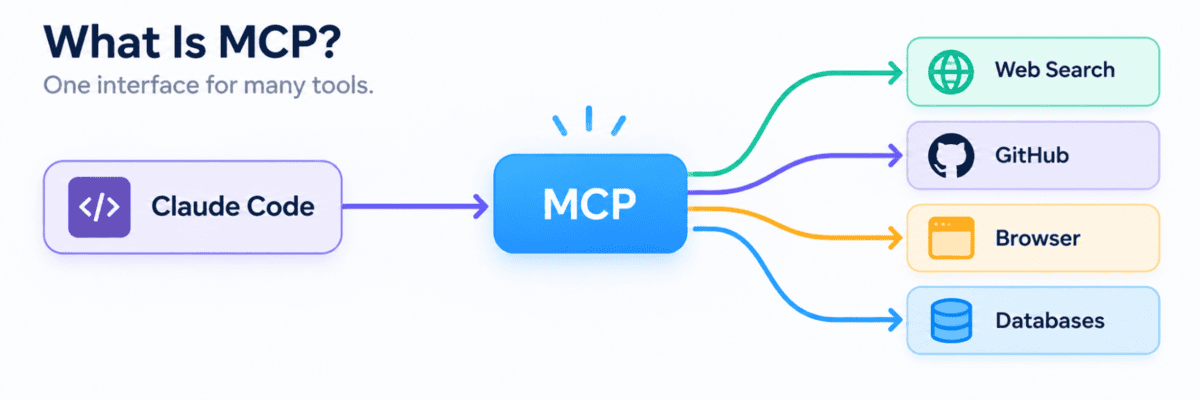
The rapid evolution of artificial intelligence has transitioned from simple text-based conversational interfaces to autonomous agents capable of performing complex, multi-step tasks. Central to this shift is the Model Context Protocol (MCP), an open-standard initiative that addresses one of the most significant bottlenecks in AI development: the fragmented ecosystem of data silos and incompatible tool integrations. By establishing a universal language for AI applications, MCP enables models like Claude to interact with external systems—such as databases, web browsers, and code repositories—without the need for bespoke, proprietary middleware for every connection.

The Problem of Fragmentation

Historically, integrating AI models with external tools has been an arduous, manual process. Each software vendor, database provider, or internal API required developers to write custom code, handle unique authentication flows, and manage specific data formatting. This "n-to-n" integration problem—where every AI application must build a unique bridge to every potential data source—has historically stifled the scalability of agentic workflows. If a developer wanted an AI to search the web, check a GitHub repository, and update a Jira ticket, they were forced to build three distinct integrations.

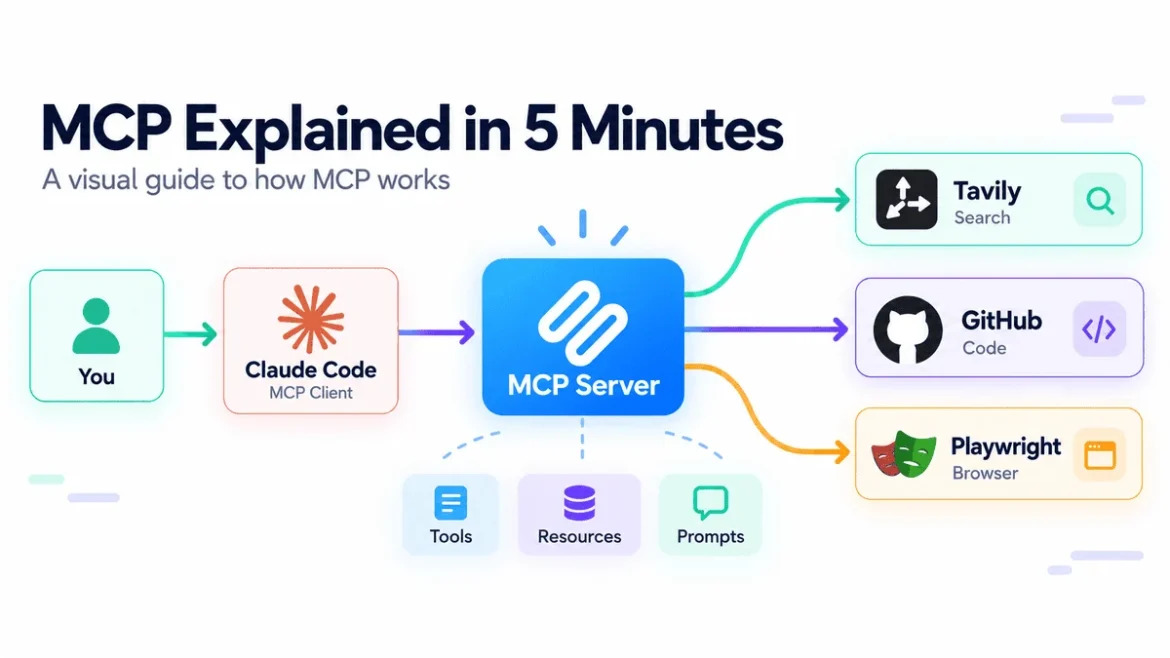
MCP Explained in 5 Minutes - KDnuggets

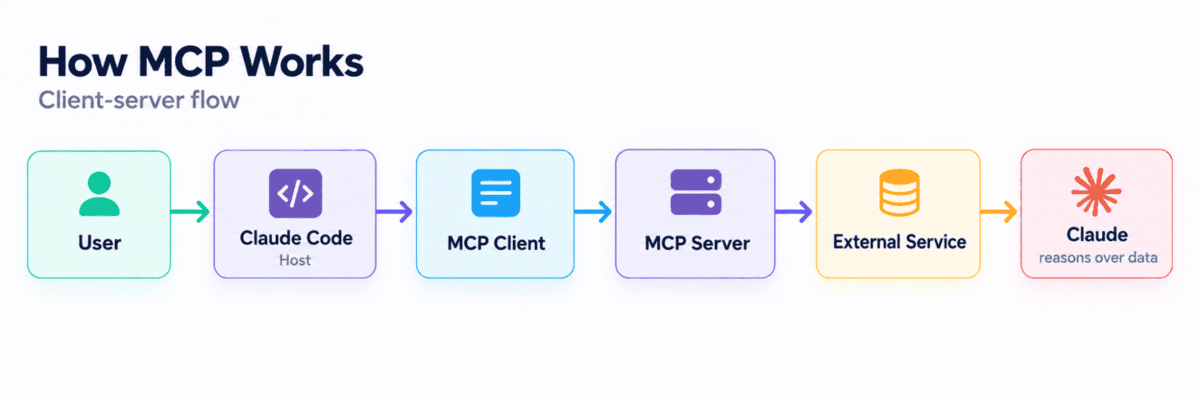
The Model Context Protocol solves this by introducing a standardized architecture that separates the AI application (the host) from the service providing the data or functionality (the server). In this framework, the host does not need to know the internal workings of the external tool; it only needs to know how to communicate via the MCP standard.

Chronology and Development

The concept of a standardized protocol for AI context gained significant momentum throughout 2024 as enterprises struggled to move AI agents beyond experimental, isolated environments. While early LLMs were largely "zero-shot" learners, the industry shift toward Retrieval-Augmented Generation (RAG) and agentic frameworks necessitated a more robust way to feed models high-fidelity, real-time data.

By late 2024 and early 2025, the industry saw the formalization of the MCP specification. Anthropic, which played a leading role in championing this standard, released documentation and support for MCP within its Claude Code environment. This was not merely a technical update but a strategic move to commoditize "tool-use," effectively turning the AI agent into an operating system for digital tasks. The release of the July 2026 specification marked a turning point, moving the protocol from a stateful, session-heavy architecture to a stateless, modular model capable of operating across distributed cloud infrastructure.

MCP Explained in 5 Minutes - KDnuggets

Architectural Components: How It Works

Understanding MCP requires dissecting its core architectural components. The protocol relies on three primary elements:

  1. The Host: This is the AI application or environment, such as Claude Code. The host initiates requests and manages the conversation with the user.
  2. The Client: Acting as the intermediary, the client resides within the host and facilitates communication with MCP servers.
  3. The Server: This is the lightweight wrapper around an external service. It exposes three specific capabilities:
    • Tools: Functions that the AI can execute (e.g., performing a web search or clicking a button).
    • Resources: Data that the AI can read (e.g., log files, database entries, or code documentation).
    • Prompts: Pre-defined templates that guide the AI’s behavior for specific tasks.

By utilizing a standard transport layer, usually JSON-RPC, the client and server can negotiate capabilities dynamically. When a user issues a prompt, the model evaluates its available tools and determines whether to invoke an MCP server to retrieve information or perform an action. This eliminates the need for the model to "guess" how to interact with an API; it simply queries the server for its capabilities and executes the command within the established parameters.

Practical Implementation: The Agentic Workflow

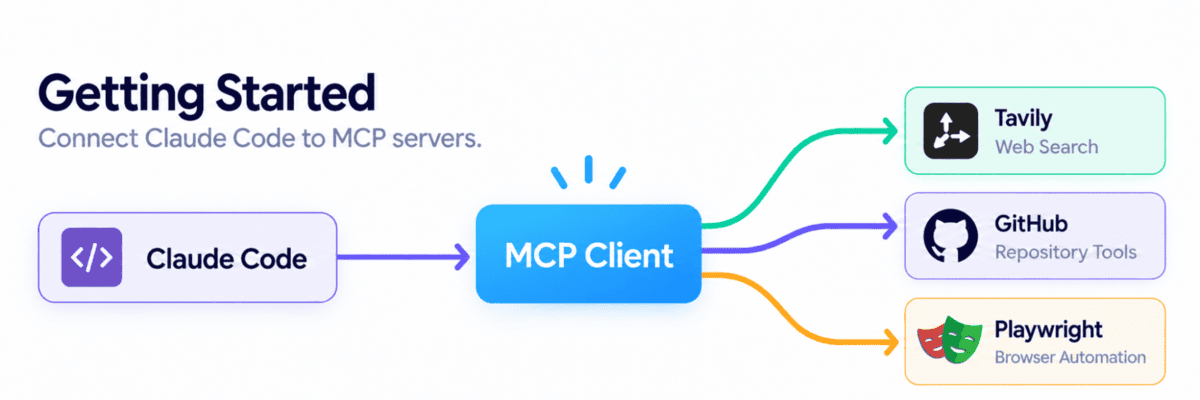
The efficacy of MCP is best illustrated through its practical application in professional developer workflows. By connecting Claude Code to specific MCP servers, developers can bridge the gap between intent and execution.

MCP Explained in 5 Minutes - KDnuggets

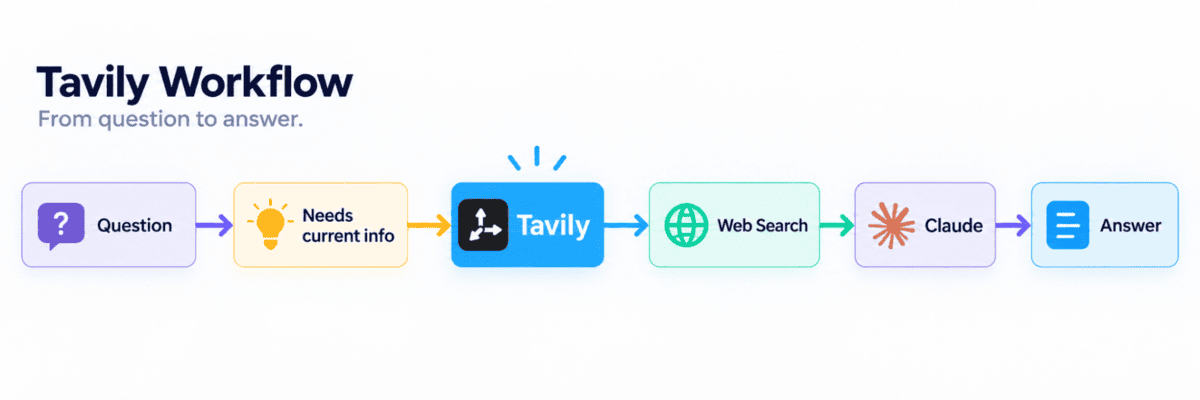
For instance, utilizing the Tavily MCP server allows an AI agent to bypass the "knowledge cutoff" limitations of LLMs. By providing a standardized interface for live web research, the agent can perform deep-web crawling and summarization, returning synthesized results to the user in seconds. Similarly, the GitHub MCP server enables an agent to authenticate via a Personal Access Token (PAT) to perform repository-wide audits, analyze pull requests, and identify bugs without the user ever leaving the command-line interface.

Furthermore, the integration of Playwright via MCP represents the frontier of browser-based automation. By transforming the browser into an API-accessible entity, the agent can interact with modern, dynamic websites, filling out forms or navigating UI-heavy applications that were previously inaccessible to pure-text models. These tools function not by overriding the underlying services but by acting as a universal translator that makes these systems "agent-ready."

Data and Implications

The transition to a stateless architecture in the 2026 specification has profound implications for enterprise adoption. Statelessness allows for horizontal scaling; as demand for agentic processing grows, organizations can deploy MCP servers across serverless architectures without worrying about session persistence or state synchronization. This shift lowers the barrier to entry for developers who are building high-concurrency AI systems.

MCP Explained in 5 Minutes - KDnuggets

Furthermore, industry analysis suggests that the widespread adoption of MCP could lead to a "standardization of tool-use," where the value of an AI platform is measured less by its base model performance and more by the breadth and depth of its MCP-compatible ecosystem. Just as the emergence of the HTTP protocol enabled the web to scale, MCP provides the foundation upon which an interoperable "AI Web" can be built.

Security and Governance

While MCP provides immense utility, it introduces new vectors for security and governance. Because an MCP server essentially gives an AI the ability to execute actions on behalf of a user, strict adherence to the "Principle of Least Privilege" is paramount. When configuring a GitHub MCP server, for example, developers are encouraged to use granular PATs that restrict the agent’s access to only the necessary repositories.

The protocol includes built-in mechanisms for security, such as standardized authentication headers and scoped access controls, ensuring that AI agents cannot inadvertently modify production databases or leak sensitive information unless explicitly granted permission. As the standard matures, the community is moving toward more robust identity and access management (IAM) integrations, which will allow enterprises to audit agent actions with the same level of scrutiny applied to human employees.

MCP Explained in 5 Minutes - KDnuggets

Future Outlook

The Model Context Protocol is not merely an incremental improvement; it is a foundational shift in how humans interact with machine intelligence. By decoupling the reasoning engine from the data source, MCP fosters a modular ecosystem where individual tools can be improved, replaced, or scaled independently of the AI model.

As we look toward the future, it is highly probable that major software platforms will begin shipping native MCP servers alongside their APIs. This would effectively turn every enterprise software tool into an "agent-native" application. For developers and businesses alike, the message is clear: the era of manual integration is coming to an end. The future of AI lies in the ability to connect disparate systems into a cohesive, intelligent whole, and MCP serves as the primary standard for achieving that connectivity.

September 24, 2026 0 comment
0 FacebookTwitterPinterestEmail
Cryptocurrency News

OpenZeppelin Brings Industry-Standard Smart Contract Security Suite to the TRON Network

by admin September 24, 2026
written by admin

LONDON, UK — September 24, 2026. In a landmark development for the decentralized finance and blockchain engineering sectors, OpenZeppelin has officially announced the integration of its premier smart contract libraries and secure development suite with the TRON network. This major technological convergence brings OpenZeppelin’s battle-tested security framework to one of the world’s most heavily utilized public blockchains, bridging the gap between institutional-grade development practices and TRON’s massive high-throughput ecosystem.

The integration addresses a critical scaling requirement for developers building sophisticated decentralized applications (dApps), stablecoin ecosystems, and enterprise-grade payment gateways on TRON. By introducing audited contract components, standardized upgrade workflows, and modern developer tooling, the collaboration aims to significantly reduce deployment friction while elevating the baseline of security across the network.

Bridging Institutional Security with High-Throughput Infrastructure

For years, OpenZeppelin has served as the gold standard for smart contract development across the broader blockchain industry. Since its inception in 2015, the organization’s flagship OpenZeppelin Contracts library has underpinned more than $37 trillion in total value transferred. Furthermore, its rigorous security team has conducted over 900 engagements, preemptively identifying and resolving more than 10,000 vulnerabilities prior to production deployment.

Until now, developers operating within the TRON ecosystem frequently had to navigate disparate security tooling or custom-built frameworks that lacked the universal standardization enjoyed by EVM-compatible networks. By bringing its comprehensive suite—including the widely popular Contracts Wizard, secure upgrade tools, and AI-assisted development support—to TRON, OpenZeppelin provides builders with a trusted, unified foundation.

The newly adapted suite is meticulously tailored to TRON’s specific network architecture. Beyond basic token creation and access control, the integrated tools support advanced, production-critical primitives such as passkey authentication, robust supply chain controls, decentralized permissions, and dynamic governance frameworks. These additions empower development teams to construct complex applications capable of safely evolving alongside user demand.

Strategic Perspectives from Industry Leaders

The integration has drawn enthusiastic responses from key stakeholders across both organizations, highlighting the mutual benefits of merging OpenZeppelin’s security pedigree with TRON’s unparalleled transaction volume.

Sam Elfarra, Community Spokesperson for the TRON DAO, emphasized the foundational role that robust security plays in the network’s ongoing evolution. "Security is fundamental to expanding what developers can build across the TRON ecosystem," Elfarra stated. "OpenZeppelin gives developers a trusted set of tools and standards that many already know from across the broader blockchain industry. Bringing that experience to TRON lowers friction for builders while giving teams stronger foundations for creating applications that can operate at scale."

Echoing this sentiment, Pepe Blasco, Engineering Manager at OpenZeppelin, underscored the importance of establishing reliability from the ground up. "Strong security starts at the foundation. Developers need primitives they can trust on the network they are deploying to," noted Blasco. "Bringing our contracts and tooling to TRON lets teams keep the assurances they know from other ecosystems, while accounting for the network-specific requirements that matter in production. The goal is a robust path from first line to production."

Context and Chronology: The Maturation of the TRON Network

To fully appreciate the significance of this integration, one must examine TRON’s trajectory since its inception. Founded in September 2017 by Justin Sun, the TRON blockchain achieved a major milestone with the launch of its MainNet in May 2018. Over the ensuing years, the network evolved from an ambitious content-sharing protocol into one of the dominant Layer-1 settlement layers for global decentralized transactions.

OpenZeppelin Integrates with TRON to Bring Its Security Standard to the Network

By late 2026, TRON had cemented its position as a primary global highway for digital dollars. The network currently hosts the largest circulating supply of USD Tether (USDT) of any blockchain, with figures exceeding $94 billion. Operational statistics compiled by TRONSCAN highlight the sheer scale of the network:

  • Total User Accounts: Surpassed 405 million globally.
  • Total Transactions: Exceeded 15 billion processed transfers.
  • Total Value Locked (TVL): Consistently maintains over $29 billion in ecosystem value.

Operating under the guiding ethos of "Moving Trillions, Empowering Billions," TRON has increasingly attracted traditional financial institutions, fintech enterprises, and sophisticated developers seeking high throughput and minimal transaction latency. However, as the network absorbs larger volumes of institutional capital and enterprise-grade financial instruments, the demand for uncompromising smart contract security has grown exponentially. The arrival of OpenZeppelin directly answers this call, providing the institutional assurance required to onboard the next wave of corporate and retail applications.

Implications for Decentralized Finance and Enterprise Adoption

The immediate implication of OpenZeppelin’s deployment on TRON is a marked reduction in development overhead and security vulnerabilities. Historically, smart contract bugs and faulty access controls have resulted in billions of dollars in exploits across the decentralized finance (DeFi) landscape. By standardizing the development lifecycle—from the initial writing of code to final deployment and ongoing upgrades—the integration mitigates human error and standardizes best practices.

Furthermore, the inclusion of AI-assisted development tools and automated security checks within the OpenZeppelin suite democratizes access to high-level engineering resources. Independent developers and small startup teams operating within the TRON ecosystem can now leverage the same structural guardrails previously reserved for heavily funded, enterprise-level protocols.

As TRON continues to expand its footprint across decentralized finance, cross-border payments, gaming, and tokenized real-world assets (RWAs), the presence of a trusted security framework will likely accelerate institutional participation. Financial institutions exploring blockchain integration frequently cite regulatory compliance, risk management, and smart contract auditability as non-negotiable prerequisites. By embedding OpenZeppelin’s proven architecture directly into its developer pipeline, TRON has substantially strengthened its value proposition for risk-averse corporate partners.

Looking Ahead

The partnership between OpenZeppelin and the TRON DAO marks a maturing milestone for the Web3 industry, demonstrating that platform interoperability and security standards can transcend individual blockchain architectures. As development teams begin leveraging the new suite to build the next generation of scalable dApps, the collective security posture of the TRON network is poised for a significant, measurable elevation.

With the tools now live and accessible to the global developer community, the focus shifts to execution—empowering builders to turn secure code into scalable, production-ready financial applications that serve hundreds of millions of users worldwide.


About OpenZeppelin

OpenZeppelin is recognized globally as the security standard for onchain finance. Since 2015, the organization has established the benchmark for blockchain and smart contract security through its industry-standard OpenZeppelin Contracts library, which has secured over $37 trillion in transferred value. Through more than 900 security engagements, OpenZeppelin has successfully identified and remediated over 10,000 vulnerabilities prior to production. The company routinely secures the world’s leading blockchain networks, decentralized finance protocols, and financial institutions.

  • Website: www.openzeppelin.com
  • Media Contact: Christian Santagata (Head of Marketing) | [email protected]

About TRON DAO

TRON DAO is a community-governed decentralized autonomous organization dedicated to accelerating the decentralization of the internet through blockchain technology and decentralized applications. Established in September 2017, the TRON network has grown into a premier global settlement layer characterized by massive user adoption, high transaction throughput, and deep liquidity, particularly in stablecoin markets.

  • Website: trondao.org / tron.network
  • Media Contact: Yeweon Park | [email protected]
September 24, 2026 0 comment
0 FacebookTwitterPinterestEmail
Blockchain Technology

MoonPay Expands Into Tokenized Assets With Acquisition of North Capital in All-Stock Deal Valued Over $60 Million

by admin September 24, 2026
written by admin

Crypto payments infrastructure giant MoonPay has officially entered the burgeoning market for tokenized real-world assets (RWAs) through a strategic all-stock acquisition of North Capital, a specialized financial services firm. According to industry reports, the transaction is valued at upwards of $60 million, contingent upon customary regulatory reviews and approvals. This major structural pivot marks a critical evolution for MoonPay, transitioning the company from a traditional fiat-to-crypto onboarding gateway into a fully integrated provider of regulated securities infrastructure.

By absorbing North Capital’s comprehensive suite of financial licenses and technological capabilities, MoonPay is positioning itself to capture institutional capital inflows looking to bridge traditional financial instruments with distributed ledger technology. The deal brings together MoonPay’s massive retail and institutional payment rails with North Capital’s robust compliance, brokerage, and alternative trading framework.

The Strategic Value of North Capital’s Infrastructure

Founded to streamline private capital formation and secondary market liquidity, North Capital has spent years establishing a formidable regulatory footprint in the United States. The firm is uniquely positioned in the fintech ecosystem due to its expansive compliance and operational licenses. North Capital operates the PPEX Alternative Trading System (ATS), a regulated platform that has successfully handled over $8.7 billion in total transaction volume. The PPEX ATS currently lists more than 1,250 eligible securities, providing a vital marketplace for private companies to issue and trade equity and debt instruments.

Beyond its alternative trading system, North Capital maintains critical regulatory registrations as a registered broker-dealer, transfer agent, and investment advisor. These components are notoriously difficult, time-consuming, and expensive to acquire independently, making North Capital an exceptionally attractive acquisition target for crypto-native enterprises seeking regulatory legitimacy.

For MoonPay, integrating these licenses means the company can legally bypass the traditional regulatory hurdles associated with handling securities. Rather than building a regulated securities stack from scratch—a process that can take years and encounter steep pushback from regulatory bodies like the Securities and Exchange Commission (SEC)—MoonPay can now leverage North Capital’s existing infrastructure. This allows MoonPay to offer tokenized equity, debt, and alternative assets directly to its extensive client base, opening new revenue streams well beyond conventional cryptocurrency purchasing.

MoonPay buys North Capital, including ATS for tokenized securities

Addressing Liquidity Fragmentation and the Agora Network Conundrum

One of the most consequential aspects of the acquisition involves North Capital’s recent strategic initiatives aimed at solving one of the tokenized asset sector’s most persistent challenges: liquidity fragmentation. Earlier, North Capital partnered with tZERO, another prominent tokenized securities venue, to launch Agora. Agora functions as a specialized network designed to connect disparate Alternative Trading Systems.

By linking these platforms, Agora allows qualified institutional participants to discover and route orders across multiple venues seamlessly, rather than being trapped in isolated liquidity silos. The network achieved a major milestone in July when it successfully executed its first routed order. However, the integration of North Capital into MoonPay introduces complex governance questions regarding Agora’s future.

With North Capital now absorbed into a vertically integrated financial group that concurrently owns its own transaction router and proprietary payment rails, industry observers are closely monitoring how Agora’s neutrality will be maintained. The success of multi-venue liquidity networks relies heavily on the perception of unbiased cooperation among founding members. Stakeholders in the tZERO-North Capital partnership will likely need to establish clear governance boundaries to ensure that MoonPay’s controlling stake in North Capital does not compromise the cooperative spirit of the Agora network.

The Broader Context: The Rise of Real-World Asset Tokenization

The acquisition of North Capital by MoonPay occurs against the backdrop of a broader, industry-wide race to tokenize real-world assets. Financial institutions, asset managers, and fintech pioneers are increasingly recognizing that blockchain technology offers unprecedented efficiencies for issuing, settling, and managing traditional financial instruments. From U.S. Treasury bills and commercial real estate to private equity and corporate debt, trillions of dollars in traditional assets are slowly migrating onto public and private ledgers.

Major global financial institutions—including BlackRock, Franklin Templeton, and JPMorgan—have launched proprietary tokenization initiatives to capitalize on the demand for instantaneous settlement, lower administrative overhead, and fractionalized ownership. For crypto infrastructure providers like MoonPay, participating in this macro trend is essential for long-term survival and growth. While retail crypto trading volumes remain cyclical, the market for tokenized securities represents a massive, sticky institutional opportunity that promises predictable, fee-based revenues.

MoonPay buys North Capital, including ATS for tokenized securities

By acquiring a licensed broker-dealer and ATS operator, MoonPay is effectively bridging the gap between Web3 native liquidity and traditional capital markets. This positioning makes MoonPay an appealing partner for legacy financial institutions that want to experiment with blockchain-based asset issuance without stepping outside the bounds of established regulatory frameworks.

Regulatory Realities and Future Outlook

As the transaction awaits final regulatory clearance, regulatory scrutiny remains a defining factor for both companies. The U.S. regulatory environment for digital assets and tokenized securities has historically been characterized by strict enforcement and a lack of bespoke legislative clarity. By acquiring an entity that already possesses SEC registration and FINRA membership, MoonPay is embedding compliance directly into its corporate DNA.

Market analysts view this move as a bellwether for future mergers and acquisitions within the fintech space. As crypto companies mature, many are discovering that raw technological innovation is insufficient without the regulatory permissions required to service institutional capital. Acquiring licensed legacy entities represents a fast-track solution to this dilemma.

Looking ahead, the integration of North Capital’s operations into MoonPay is expected to unfold over the coming months, pending the green light from relevant regulatory bodies. If successful, the combined entity will possess a rare combination of global consumer reach, frictionless fiat payment rails, and a fully compliant securities infrastructure. This positions MoonPay not merely as a gateway for buying digital currencies, but as a comprehensive financial utility capable of supporting the entire lifecycle of traditional and tokenized assets in the digital age.

September 24, 2026 0 comment
0 FacebookTwitterPinterestEmail
Cybersecurity & Hacking

OnePlus Security Vulnerability Allows Malicious Apps to Gain Full Root Access Without User Permissions

by admin September 24, 2026
written by admin

A critical security vulnerability affecting the latest iterations of OxygenOS, the proprietary Android-based operating system utilized by OnePlus and its parent company OPPO, has been publicly disclosed by security researcher Rasmus Moorats. The flaw allows a malicious application, requiring zero specific permissions, to escalate privileges to root access—the highest level of administrative control on an Android device. This discovery exposes a significant lapse in the security architecture of modern flagship smartphones, as it permits an attacker to bypass standard operating system protections, access sensitive user data, and execute arbitrary code at the kernel level.

The vulnerability stems from a sophisticated "chaining" of two distinct software flaws found within pre-installed OnePlus system services. By exploiting these weaknesses in tandem, an attacker can move from a low-privilege environment to absolute device ownership.

Chronology of the Disclosure and Corporate Tensions

The discovery process began in early 2026, leading to a strained period of communication between the independent researcher and the device manufacturer. According to the documented timeline provided by Moorats, the flaws were formally confirmed by OnePlus engineering teams in May 2026.

However, the path to resolution was hampered by significant disagreements regarding the disclosure process. In correspondence shared by the researcher, OnePlus management asserted that the company holds the "exclusive final right of vulnerability disclosure." The company explicitly warned the researcher that publishing the technical details without express authorization could result in legal action, citing European cybersecurity regulations as a basis for restricting independent reporting.

Despite these warnings and the absence of a patched version of OxygenOS, Moorats proceeded with a full public disclosure on September 24, 2026. At the time of publication, no Common Vulnerabilities and Exposures (CVE) identifier had been assigned, nor had a security patch been pushed to the affected devices. This move highlights a growing trend of friction between security researchers advocating for "responsible disclosure" and OEMs (Original Equipment Manufacturers) attempting to control the narrative surrounding product vulnerabilities.

Unpatched OnePlus Flaws Let Installed Android Apps Gain Root Without Permissions

Technical Breakdown: How the Chain of Vulnerabilities Works

The attack vector relies on the interaction between two specific components of the OxygenOS environment.

The first point of failure lies within a system service identified as "AtlasService." This service is designed to collect diagnostic and debugging data. Crucially, it operates with root-level privileges but fails to implement proper authentication checks, meaning it accepts requests from any application currently installed on the device, regardless of whether that application has been granted permissions by the user. An attacker can submit a specially crafted request to this service, which then passes the input to a secondary debugging tool. This tool executes the input as a system command without sufficient sanitization. While this initial exploit does not grant full system control, it does provide the attacker with root access within a restricted, sandboxed zone known as "dumpstate."

The second component of the attack involves a hardware-level helper service labeled "olc2." This service is intended to facilitate low-level hardware interactions. Under normal circumstances, the command structure of olc2 is guarded by a check that verifies the caller’s privilege level. Because the attacker has already gained root access via the AtlasService exploit, they successfully bypass this guard. Once the olc2 service is engaged, it executes the shell instruction provided by the attacker, effectively "breaking out" of the dumpstate sandbox and granting the malicious application full, unrestricted Linux kernel privileges.

Broader Implications and the OEM Ecosystem

The threat is not limited to a single model. While the testing was performed on a OnePlus 15, investigations suggest that the underlying codebase for OxygenOS is shared extensively across the OnePlus and OPPO product lines. The manufacturer has acknowledged that these vulnerabilities affect a wide range of devices, though it has remained opaque regarding the specific list of impacted models.

This incident is emblematic of a wider security crisis within the Android ecosystem known as "OEM-added vulnerabilities." While the Android Open Source Project (AOSP) undergoes rigorous security auditing by Google, the proprietary layers added by manufacturers to differentiate their products often introduce bespoke code that lacks the same level of scrutiny.

In August 2026, security firm Calif highlighted this systemic issue through their "OEMpocalypse" research. That study demonstrated that proprietary code added by major manufacturers—including Samsung, Xiaomi, OPPO, and OnePlus—frequently introduces paths for privilege escalation that allow third-party apps to gain root access on locked devices. These findings suggest that the security of a modern smartphone is increasingly dependent on the quality of code written by the manufacturer, rather than the core Android operating system alone.

Unpatched OnePlus Flaws Let Installed Android Apps Gain Root Without Permissions

User Risks and Mitigation Strategies

The primary constraint of the current exploit is that it requires a malicious application to be locally installed on the target device. This means the attack cannot be executed remotely via a webpage or a simple phishing link; a user must be tricked into installing an APK or a malicious application from a third-party source.

However, once installed, the malicious app operates entirely silently. Because the exploit uses pre-existing system services to escalate privileges, the application does not trigger the standard Android permission prompts that would normally alert a user to suspicious activity. There is currently no evidence that these vulnerabilities have been utilized in the wild by threat actors, but the public availability of the exploit code significantly increases the risk that malicious actors may develop automated tools to leverage these flaws.

Until OnePlus releases a comprehensive firmware update to address these vulnerabilities, the most effective defense remains traditional digital hygiene:

  1. Strict App Sourcing: Users should refrain from installing applications from outside the official Google Play Store. Sideloading applications from unverified sources remains the primary gateway for this exploit.
  2. Permission Auditing: While this specific exploit bypasses permission prompts, users should regularly review the list of installed applications and uninstall any software that is no longer required or originates from an untrusted developer.
  3. Firmware Updates: Owners of OnePlus and OPPO devices are urged to check for system updates frequently. While no fix was available at the time of the initial report, security patches are often bundled into monthly releases.

The Conflict Between Disclosure and Regulation

The dispute between Moorats and OnePlus underscores a critical debate in the cybersecurity community regarding the "Right to Disclose." OnePlus’s stance—that it possesses the sole right to determine when and how a vulnerability is made public—clashes with the industry-standard practice of coordinated disclosure. Industry norms typically allow a researcher to publish their findings after a set period (usually 90 days) if the vendor has failed to provide a fix or demonstrate progress toward one.

By threatening legal action, OnePlus is utilizing a strategy that critics argue stifles independent security research and leaves consumers at risk by suppressing information. The company’s reference to European cybersecurity regulations as a justification for silence is particularly contentious, as many cybersecurity experts interpret these regulations as a mandate for transparency and prompt remediation, rather than a tool for corporate obfuscation.

As the industry moves forward, the pressure on manufacturers to adopt more transparent security practices will likely increase. With the rise of sophisticated, proprietary "value-add" features in smartphones, the ability for manufacturers to rapidly identify, patch, and disclose flaws has become as important as the hardware specifications themselves. For now, users of OnePlus and OPPO devices remain in a vulnerable position, waiting for an official patch that addresses the core architectural weaknesses of their devices’ software.

September 24, 2026 0 comment
0 FacebookTwitterPinterestEmail
Cybersecurity & Hacking

MacSync Malware Evolves to Weaponize Public iCloud Calendars and Deliver Advanced macOS Payloads

by admin September 24, 2026
written by admin

Cybersecurity researchers have uncovered a sophisticated new iteration of the MacSync information-stealing malware that introduces an unconventional vector for command and control: public iCloud calendars. Initially spotted in early 2025 as a Swift-based variant loosely tied to the AMOS stealer family, MacSync has rapidly evolved into a modular, multi-stage threat targeting macOS environments. According to telemetry and analysis from Kaspersky, recent campaigns utilize elaborate social engineering—including deceptive ClickFix schemes and fraudulent cryptocurrency applications—to slip past user defenses. By leveraging legitimate cloud infrastructure such as Apple’s iCloud services, the operators of MacSync have demonstrated an increasing capacity to evade traditional endpoint detection systems, posing a renewed challenge for enterprise security teams and individual Mac users alike.

The Evolution of MacSync: From AMOS Offshoot to Advanced Multi-Stage Threat

To understand the current threat landscape surrounding MacSync, security analysts must examine its trajectory since it first emerged in April 2025. Initially characterized as a relatively straightforward Swift-based info-stealer derived from the notorious AMOS (Atomic macOS Stealer) family, the malware quickly caught the attention of threat intelligence researchers due to its rapid iteration cycle. Unlike early versions that relied solely on conventional payload delivery methods, the recent campaign analyzed by Kaspersky reveals a significant architectural overhaul.

The malicious operators behind MacSync have steadily modularized the malware, decoupling the initial downloader from the core infostealer modules and the newly introduced backdoor components. This modular design not only complicates the task of reverse-engineering the malware but also allows threat actors to dynamically provision payloads based on the compromised system’s profile. By separating the initial reconnaissance and delivery phases from data harvesting and remote administration capabilities, the creators of MacSync have mirrored the sophisticated tactics typically observed in advanced persistent threat (APTs) groups, bringing enterprise-grade stealth techniques to the macOS consumer and enterprise threat landscape.

Anatomy of an Attack: Social Engineering and iCloud Calendar C2

MacSync malware uses public iCloud calendars to deliver new payloads

The primary distribution vector for MacSync relies heavily on social engineering, capitalizing on user trust and the growing prevalence of browser-based deception tactics. Recent campaigns have heavily leveraged so-called ClickFix attacks, where users are manipulated into copying and pasting malicious terminal commands under the guise of fixing minor software errors or updating legitimate utilities such as Homebrew and disk space analyzers. Furthermore, threat actors have deployed bespoke fraudulent infrastructure, including dedicated promotional websites and social media campaigns advertising a fake cryptocurrency wallet application named "Toria."

Once a victim is lured into interacting with these malicious assets, the infection chain bifurcates into standard and highly complex delivery mechanisms. In the more intricate variant identified by Kaspersky, a specialized downloader script fetches hidden commands embedded directly within the description field of a public iCloud calendar event.

The mechanics of this technique highlight a clever abuse of native macOS utilities and legitimate cloud services. The downloader feeds the retrieved calendar data directly into the system’s default interactive shell, the Z shell (zsh). Because the calendar description contains a mixture of unstructured text and hidden executable code, standard lines generate benign parsing errors. However, specific instructions placed immediately following the designated description delimiter (DESCRIPTION:) are executed by the shell. These commands orchestrate the fetching of a subsequent archive containing multi-stage malware components from iCloud. Ultimately, this leads to the deployment of an application bundle acting as a dropper, which unpacks and launches the core MacSync payloads.

Comprehensive Data Harvesting and the New Objective-C Backdoor

Once successfully established on a compromised macOS host, MacSync executes a comprehensive sweep of the system to extract sensitive information. The core infostealer module targets a vast repository of personal, professional, and financial data. This includes browser history, cookies, and saved authentication credentials from all major web browsers; data associated with cryptocurrency wallet browser extensions and desktop applications; local data stores from messaging platforms like Telegram; and the system’s native Keychain file.

In addition to user-level credentials, the malware performs aggressive reconnaissance of developer and administrative assets. It scans for Secure Shell (SSH) keys, AWS credentials, Kubernetes configuration files, Git repositories, and various shell initialization and configuration files. This makes MacSync particularly dangerous for software engineers, systems administrators, and corporate employees who handle elevated access tokens on their personal or work-managed Mac computers.

MacSync malware uses public iCloud calendars to deliver new payloads

Compounding the threat is a newly observed Objective-C backdoor module. Disguising itself as Finder—the fundamental file manager interface of macOS—this backdoor is designed to maintain persistent unauthorized access. Upon installation, the backdoor establishes persistence mechanisms by configuring a LaunchAgent, modifying local .zshrc profile files, and injecting global Git hooks. To ensure the user remains oblivious to the compromise during these automated operations, the backdoor actively terminates legitimate macOS notification processes, effectively silencing system alerts and preventing warning banners from appearing on the desktop.

Capabilities and Mystery Components of the Backdoor Module

While security researchers were unable to fully analyze the specific AppleScript payloads executed by the backdoor due to obfuscation and missing script components, they were able to infer the intended functions of various commands based on their internal naming conventions and status messages. The backdoor is equipped to execute remote management commands, manipulate file systems, and execute arbitrary scripts supplied by the command-and-control (C2) infrastructure.

Of particular note to analysts is a mysterious command identified in the backdoor’s codebase designated as live_browser. When invoked, this command downloads and executes an auxiliary component known as sn_relay. As of the latest Kaspersky reports, the precise functional objective of sn_relay remains undetermined, leaving researchers to monitor its behavior closely for signs of secondary payloads, lateral movement tools, or proxy capabilities. The inclusion of such obscure components underscores the fluid nature of the MacSync project and suggests that the threat actors are actively testing new functional modules in the wild.

Industry Implications and the Broader Threat to macOS

The weaponization of public iCloud calendars and the integration of sophisticated backdoors into MacSync highlight a broader, concerning trend within the threat landscape: the continuous expansion of malware targeting Apple’s macOS ecosystem. Historically, macOS users enjoyed a degree of immunity from widespread cybercrime due to the platform’s stringent security controls, sandboxing, and market share dynamics. However, as enterprise adoption of Macs grows and cryptocurrency wealth becomes increasingly centralized on desktop environments, cybercriminals have invested heavily in bypassing macOS-specific security barriers.

MacSync malware uses public iCloud calendars to deliver new payloads

Security analysts emphasize that techniques abusing cloud services—such as leveraging public calendar events for command and control—blur the lines between legitimate administrative traffic and malicious activity. Because connections to Apple’s iCloud domains are universally trusted by corporate firewalls and endpoint security solutions, they rarely trigger traditional network-level alerts. This makes cloud-abusing malware exceptionally difficult to detect using legacy signature-based defenses, placing a heavier burden on behavioral monitoring and proactive user awareness.

Defensive Recommendations and Best Practices for macOS Users

In light of the evolving capabilities demonstrated by the MacSync malware family, cybersecurity professionals and incident responders strongly urge users to adopt rigorous defensive habits. Chief among these recommendations is avoiding the execution of raw terminal commands found in online forums, social media posts, or unexpected pop-up windows—a primary vector exploited by ClickFix campaigns.

Furthermore, users should exercise extreme caution when downloading disk image (.DMG) files, installers, or software updates from untrusted third-party websites, peer-to-peer networks, or unsolicited social media advertisements. Whenever an application requests administrative password prompts or terminal execution rights, users should independently verify the authenticity of the software vendor. Organizations managing fleets of macOS endpoints are encouraged to deploy modern endpoint detection and response (EDR) solutions capable of monitoring shell behavior, unauthorized modifications to shell configuration files, and abnormal launch agent installations to catch multi-stage threats like MacSync before critical data can be exfiltrated.

September 24, 2026 0 comment
0 FacebookTwitterPinterestEmail
Newer Posts
Older Posts

Recent Posts

  • Better.codes: The Ethereum Foundation and Partners Launch an Open Autoresearch Challenge to Secure the Future of Cryptography
  • Three Days in Jackson Hole: Inside Kraken’s Exclusive VIP Retreat Bridging High Finance and the Wild West
  • Justin Sun Accumulates Massive PEPE Holdings Amid Market Volatility and Rising Social Sentiment
  • The Ghost in the Machine: How Decades-Old Cryptography in Microsoft Active Directory Fuels Modern Ransomware Attacks
  • LendAPI Transforms Financial Infrastructure with No-Code Orchestration to Accelerate Product Innovation

Recent Comments

No comments to show.
  • Facebook
  • Twitter

@2021 - All Right Reserved. Designed and Developed by PenciDesign


Back To Top
Dr Crypton
  • Home
  • About Us
  • Contact Us
  • Cookies Policy
  • Disclaimer
  • DMCA
  • Privacy Policy
  • Terms and Conditions

We are using cookies to give you the best experience on our website.

You can find out more about which cookies we are using or switch them off in .

Dr Crypton
Powered by  GDPR Cookie Compliance
Privacy Overview

This website uses cookies so that we can provide you with the best user experience possible. Cookie information is stored in your browser and performs functions such as recognising you when you return to our website and helping our team to understand which sections of the website you find most interesting and useful.

Strictly Necessary Cookies

Strictly Necessary Cookie should be enabled at all times so that we can save your preferences for cookie settings.