• Home
  • About Us
  • Contact Us
  • Cookies Policy
  • Disclaimer
  • DMCA
  • Privacy Policy
  • Terms and Conditions
Dr Crypton
Secure Your Future in Crypto
Artificial Intelligence & Tech

Introducing Playground: Create and play custom games

by admin October 27, 2026
written by admin

The Democratization of Game Development

The gaming industry has experienced explosive growth over the last decade, with global revenues now exceeding $180 billion annually. Despite this massive market, the actual creation process remained siloed. Traditional development pipelines—involving assets, physics engines, lighting, and networking—required specialized software and years of training. Playground challenges this status quo by utilizing generative AI to bridge the gap between imagination and implementation.

Maryam Karimzadehgan, a lead software engineer at Google’s AI Innovation and Research unit, spearheaded the development of this platform with a core philosophy: if a user can describe an experience, they should be able to play it. By leveraging large-scale language models, the platform interprets user prompts to build game logic, environment aesthetics, and rule sets in real-time. This eliminates the "syntax barrier," where a user’s creative vision is often stifled by the inability to write complex code.

Chronology and Technical Evolution

The trajectory toward this launch began in the early 2020s, as generative AI moved from theoretical research to consumer-facing applications. The transition from LLMs (Large Language Models) that could write text to those capable of generating functional software architecture provided the technical foundation for Playground.

  • 2022–2023: Initial research into "text-to-game" logic began within Google’s internal labs, focusing on simple 2D mechanics.
  • Early 2024: Integration of multimodal AI allowed for the generation of visual assets, moving the platform beyond simple text-based adventure games toward interactive, graphical experiences.
  • Late 2024: The platform underwent extensive closed-beta testing, focusing on safety guardrails and the implementation of community-driven moderation.
  • October 2026: Official launch of the experimental platform for users in the United States aged 18 and older.

How Playground Functions

At its core, the platform operates via a conversational interface. Users engage with a prompt box where they can define the genre, tone, and specific gameplay mechanics. A user might, for example, input: "Create a 2D platformer where the character is a sloth moving across city rooftops, and the game should increase in difficulty as time passes."

The AI then generates the underlying code, maps the physics, and constructs the environment. Crucially, the platform allows for iterative design. Users do not need to get it perfect on the first prompt. They can ask the system to "change the color of the rooftops to sunset orange" or "make the sloth move faster when it collects coffee beans." This back-and-forth process mimics the traditional game development cycle of prototyping and refining, but compresses what would take weeks into a matter of minutes.

The Role of Community and Social Integration

Google has positioned Playground not merely as a tool for creation, but as a social ecosystem. The platform includes a "Playground Explore" gallery where creators can publish their work. This moves the platform into the territory of social gaming hubs like Roblox or Unity’s own community portals, albeit with a significantly lower entry threshold.

The social features include:

  • Multiplayer Capabilities: Select game genres support real-time interaction, allowing users to challenge friends.
  • Leaderboards: Integrated tracking allows for competitive play, fostering a sense of community engagement.
  • Player Feedback: A rating system ensures that the best-designed games rise to the top, providing a feedback loop for creators to improve their skills.

To maintain a secure environment, all published games are subject to automated safety screenings. These screenings scan for content that violates Google’s community guidelines, such as hate speech or non-consensual imagery. Furthermore, the platform utilizes a user-reporting system, ensuring that the community remains self-policing in tandem with automated oversight.

Expanding Horizons: The Unity Spark Integration

Perhaps the most significant development on the horizon is the upcoming integration with Unity Spark. While Playground is currently optimized for rapid, accessible creation, the partnership with Unity Technologies signals an intention to move into professional-grade development.

Unity Spark, currently in its testing phase, is designed to provide high-fidelity 3D capabilities and professional-level mechanics that are currently beyond the scope of a standard text-to-game interface. By building a pipeline where a user can start with a simple text prompt in Playground and eventually export or expand that project into Unity’s robust engine, Google and Unity are creating a "pathway of growth" for creators. This ecosystem approach acknowledges that many users will eventually want to move beyond basic games to create immersive, 3D experiences without losing the initial work they created on the Playground platform.

Market Implications and Future Outlook

The introduction of Playground has profound implications for the gaming industry and the broader software development sector. If successful, it effectively turns every user into a developer. This mirrors the shift seen in digital media creation—just as YouTube allowed anyone to become a filmmaker and Substack allowed anyone to become a publisher, Playground aims to allow anyone to become a game designer.

Industry analysts suggest that this will likely lead to a "long tail" of creative content. While major studios will continue to dominate the high-budget "AAA" market, the middle market—indie games and casual experiences—could be entirely reshaped. A massive influx of user-generated games could lead to a saturation of the market, forcing platforms to rely more heavily on AI-driven curation and discovery algorithms to highlight high-quality content.

Moreover, the platform’s browser-based nature is a strategic choice. By avoiding the need for dedicated gaming hardware or high-end PCs, Google ensures that the barrier to entry is not just technical, but also financial. The platform runs on any modern web browser, making game creation accessible on everything from tablets to budget-friendly laptops.

Safety and Ethical Considerations

As with any generative AI tool, questions surrounding copyright and intellectual property remain prevalent. Google has stated that all games are moderated for safety, but the broader question of who owns the rights to a game generated via AI prompts is a subject of ongoing legal debate. Currently, the platform operates as an experimental environment, but as the technology matures, it will likely require more robust frameworks for digital rights management and creator compensation.

Furthermore, the tiered access model—which limits some features based on a user’s Google AI subscription—suggests that Google views this as a premium utility. While the basic creation tools are likely to remain accessible, power users will need to invest in the ecosystem to unlock higher-fidelity assets and advanced development features.

Conclusion: The Next Phase of Digital Creativity

The launch of Playground marks a pivotal moment in the intersection of artificial intelligence and interactive entertainment. By abstracting the complexities of coding and game engine management, Google is inviting a new demographic of creators into the fold. Whether this leads to a new generation of game designers or simply provides a fun, creative outlet for casual users remains to be seen. However, the trajectory is clear: the ability to build, iterate, and share virtual worlds is moving from the domain of the expert to the fingertips of the general public.

As the community begins to populate the Playground gallery with their unique creations, the platform will serve as a barometer for how generative AI can enhance, rather than replace, human creativity. For now, the experiment is live, the tools are in the hands of the public, and the future of game design is becoming significantly more accessible.

October 27, 2026 0 comment
0 FacebookTwitterPinterestEmail
Cryptocurrency News

Stellar Development Foundation Unveils Bell Protocol 30 Upgrade With Focus on Smart Accounts and Quantum Readiness

by admin October 27, 2026
written by admin

The Stellar Development Foundation (SDF) has officially outlined its upcoming network upgrade, designated as Protocol 30 and named Bell, setting a definitive governance roadmap that includes a public testnet vote scheduled for November 3, 2026, and a subsequent mainnet vote on November 23, 2026. Announced via an official developer update on October 20, 2026, the Bell upgrade represents a strategic pivot toward enterprise-grade infrastructure, focusing heavily on streamlined smart account management for high-volume financial services, foundational steps toward post-quantum cryptography, and optimized ledger execution timing.

While the governance milestones dictate a strict timeline for validator participation and node operator readiness, the upgrade package itself brings together three distinct technical proposals. Rather than introducing an entirely new standalone blockchain or altering the fundamental consensus model of the Stellar network, Protocol 30 refines existing capabilities to meet the rigorous operational demands of institutional custodians, global payment processors, and decentralized application (dApp) developers.

As the digital-asset industry matures, major layer-1 protocols are increasingly forced to prioritize back-end efficiency over speculative consumer-facing applications. Stellar’s Bell upgrade directly addresses this industry-wide shift, offering a compelling case study in how mature blockchain networks evolve to handle enterprise scale, regulatory compliance integration, and future-proofing against emerging technological threats such as quantum computing.

Chronology and Governance Timeline Leading to Bell

The path to Protocol 30 is rooted in Stellar’s ongoing modular evolution, which accelerated following the introduction of native smart contract functionality via Soroban. To ensure network stability and give ecosystem participants adequate time for integration, the Stellar Development Foundation follows a structured governance and voting protocol.

The sequence of events leading up to the activation of Bell began with early architectural discussions among core protocol engineers regarding the limitations of traditional account models in high-throughput environments. By mid-2026, these discussions crystallized into three formal core advancement proposals that collectively form the Bell upgrade package.

Following the initial October 20, 2026 announcement, the ecosystem entered a preparation phase characterized by the release of comprehensive documentation, software development kit (SDK) updates, and preliminary testnet deployments. Node operators, validators, and dApp developers are currently reviewing compatibility notes to ensure their infrastructure can support the incoming changes.

The critical path for Bell activation follows a dual-phase voting schedule:

  • November 3, 2026: The Protocol 30 upgrade is put to a vote on the Stellar Testnet. This phase allows developers to test the new smart account patterns, muxed contract addresses, and post-quantum verification modules in a live, simulated environment without financial risk.
  • November 23, 2026: Subject to successful testnet validation and sufficient consensus among network validators, the mainnet vote takes place. If approved, Protocol 30 will be implemented across the primary Stellar network, officially activating the Bell feature set.

This measured approach highlights the deliberate governance model employed by the Stellar network, contrasting sharply with unstructured fork models seen in other ecosystems. By establishing weeks of lead time between the initial specification release and the mainnet vote, the SDF aims to minimize disruption for exchanges, anchor institutions, and institutional partners.

Core Technical Architecture of Protocol 30

The Bell upgrade is built upon three foundational technical pillars, each designed to solve specific operational bottlenecks currently faced by developers and enterprise users operating on the Stellar network.

Muxed Contract Addresses and Institutional Scalability
The first major component of Protocol 30 introduces muxed contract addresses. Traditionally, Stellar has supported muxed accounts (or generalized accounts), which allow centralized services such as cryptocurrency exchanges, fiat-to-crypto on-ramps, and institutional custodians to manage multiple user accounts using a single master blockchain address paired with a unique identifier (memo ID). This design drastically simplifies accounting and reduces the number of base accounts an exchange must fund and maintain on-chain.

However, as institutional adoption shifted toward programmable smart contracts, traditional muxed account functionality could not be natively applied to contract-based infrastructure without complex, custom-built middleware. Protocol 30 extends the convenience of muxed addressing directly to smart contracts.

For custodians and enterprise-grade platforms, this means significantly reduced overhead when managing thousands or millions of individual customer relationships within a shared smart contract framework. Rather than deploying redundant logic or maintaining cumbersome off-chain mapping databases, developers can leverage muxed contract addresses to streamline deposits, withdrawals, and internal ledger management. This architectural enhancement bridges the gap between traditional account-based operational models and advanced smart contract capabilities, though it requires meticulous implementation by security teams to ensure strict data isolation between individual user records and broader contract authorizations.

Post-Quantum Signature Verification Framework
The second core pillar of the Bell upgrade introduces support for verifying post-quantum cryptographic signatures natively within smart contracts. As quantum computing research advances, the cryptographic primitives that secure modern blockchain networks—primarily elliptic curve cryptography such as Ed25519 and ECDSA—face long-term vulnerabilities to sophisticated quantum algorithms like Shor’s algorithm.

It is a common misconception that an upgrade like Bell instantly transforms the entire Stellar network into a quantum-proof ecosystem. Cryptographic migration is inherently a multi-layered, evolutionary undertaking. Upgrading a network involves not only the underlying consensus layer but also user account types, key recovery mechanisms, software development libraries, and operational security procedures across all participating nodes and wallets.

Protocol 30 does not force an immediate network-wide migration to post-quantum algorithms. Instead, it provides a crucial developer-facing building block: the ability to execute and verify post-quantum signature schemes inside smart contracts. This allows experimental applications, high-security vaults, and forward-looking developers to begin integrating quantum-resistant cryptography into their custom logic today. Subsequent protocol upgrades will undoubtedly be required to address network-wide key types, but Bell establishes the foundational cryptographic flexibility necessary to future-proof the ecosystem against tomorrow’s computing threats.

Fine-Grained Ledger Timing and Performance Optimization
The third pillar targets ledger execution timing and aims to remove technical friction that contributes to latency across payment and trading applications. While blockchain throughput is frequently marketed in terms of raw transactions per second (TPS), enterprise users and market makers are equally sensitive to ledger close times and predictability under heavy network load.

Protocol 30 optimizes the underlying mechanics of ledger closes, reducing unnecessary technical lag. For payment gateways and decentralized finance (DeFi) protocols operating on Stellar, this results in a more responsive user experience. Transactions clear faster, and confirmation loops tighten.

Nevertheless, core engineers and network architects emphasize that faster ledger intervals must be carefully balanced against validator coordination overhead and global network stability. Decreasing block times arbitrarily can lead to consensus divergence or increased hardware requirements for validators. Furthermore, technical ledger finality is distinct from legal or regulatory settlement of off-chain financial obligations. For enterprise adopters, the true metric of success for Bell’s performance enhancements will be demonstrated reliability and predictable latency during periods of extreme market volatility, rather than isolated benchmark figures achieved under laboratory conditions.

Ecosystem Reactions and Developer Preparedness

The unveiling of the Bell upgrade has elicited a measured, pragmatic response from the broader Stellar developer community and enterprise partners. Rather than triggering speculative fervor, the announcement has directed technical discussions toward practical implementation details, SDK compatibility, and risk management.

Major institutional anchors—institutions that issue stablecoins and facilitate cross-border remittances on Stellar—have expressed cautious optimism regarding the introduction of muxed contract addresses. Representatives from compliance-focused payment networks note that simplifying account management at the smart contract level reduces the operational friction associated with anti-money laundering (AML) tracking and know-your-customer (KYC) data partitioning. By embedding these capabilities directly into the protocol, Stellar strengthens its value proposition as a compliant rail for regulated financial assets, including tokenized real-world assets (RWAs) and central bank digital currencies (CBDCs).

Security auditors and smart contract developers have similarly welcomed the integration tools for post-quantum signatures, though they stress the need for rigorous auditing frameworks. Because post-quantum cryptographic algorithms often require significantly larger key sizes and heavier computational overhead compared to traditional elliptic curve signatures, developers must carefully evaluate the gas and resource consumption of contracts utilizing these new verification modules.

Concurrently, node operators and validator organizations are reviewing the upgrade documentation provided by the Stellar Development Foundation. Ensuring high participation rates during the November 3 testnet vote is viewed as a critical priority to identify any unforeseen edge cases or backward compatibility issues before the mainnet deployment on November 23.

Macro Market Context and Investment Implications

The announcement of Protocol 30 arrives at a complex juncture for the digital-asset market. Macroeconomic headwinds, shifting regulatory frameworks across multiple jurisdictions, and intense competition among layer-1 and layer-2 scaling solutions have forced market participants to look beyond superficial marketing metrics and focus on fundamental utility.

From an investment perspective, financial analysts emphasize the vital distinction between network governance milestones—such as testnet and mainnet voting dates—and immediate shifts in asset valuation or token economics. Protocol upgrades like Bell strengthen the technological infrastructure, operational capacity, and compliance readiness of the ecosystem, but they do not automatically dictate market pricing for the Stellar Lumens (XLM) native token or any asset issued on the network.

The valuation of a blockchain network and its native digital assets is inextricably tied to organic adoption, transaction volume, developer mindshare, and the actual economic value flowing through its smart contracts and payment rails. Bridging the gap between confirmed technological advancements and long-term financial forecasts remains one of the primary challenges for market observers.

Moreover, industry watchdogs continually remind participants to differentiate between the technical rights conferred by smart contracts, the legal rights established by regulated service agreements, and the speculative value assigned to tokens. Even within an integrated wallet or platform environment, tokens, equity shares, and regulated financial instruments operate under entirely different legal frameworks. A comprehensive assessment of any blockchain ecosystem requires rigorous inquiry into issuer accountability, redemption mechanisms, and verified on-chain activity rather than reliance on price targets or assumptions of inevitable adoption.

Outlook and Next Steps for the Stellar Network

As the cryptocurrency industry watches for the outcome of the November 3 testnet vote, the Stellar Development Foundation remains focused on execution, documentation, and community support. The Bell upgrade serves as an instructive case study in the maturation of blockchain development—shifting away from speculative novelty toward the unglamorous, high-stakes requirements of global production operations: customer-scale account management, cryptographic agility, and reliable transaction timing.

For developers, the immediate action items are clear: review the Protocol 30 compatibility notes, update local development environments, participate in testnet validation, and monitor the results of the November mainnet governance vote. For the broader market, Bell represents a calculated, methodical step forward, reinforcing Stellar’s position as a robust, enterprise-ready network capable of adapting to the technological demands of the future financial landscape.

October 27, 2026 0 comment
0 FacebookTwitterPinterestEmail
Blockchain Technology

U.S. Crypto Firms Face Regulatory Crossroads as Tokenization and Banking Integration Initiatives Stall

by admin October 27, 2026
written by admin

The landscape of American financial regulation is undergoing a seismic shift as crypto-native firms attempt to bridge the divide between decentralized infrastructure and traditional market operations. Despite a recent, aggressive push by companies to introduce tokenized securities and new banking structures, the industry is encountering significant friction from both public corporations and entrenched financial institutions. While the Securities and Exchange Commission (SEC) has signaled that tokenized securities are a 2027 priority, the practical application of this technology is meeting widespread resistance, leaving the future of blockchain-based financial assets in a state of regulatory and operational limbo.

The Tokenization Struggle and Corporate Hesitancy

The concept of a Tokenized Securities Venue (TSV)—a platform allowing for the 24/7 trading of blockchain-based representations of public company shares—was intended to modernize market infrastructure. However, the first major attempt to launch such a platform has exposed deep-seated corporate apprehension. The joint venture between OKX and Intercontinental Exchange (ICE), known as OKXICE, sought to bring 63 firms into the tokenized ecosystem. As of late October 2024, at least 22 of these companies have formally opted out of the program.

This exodus includes major industry players such as Wells Fargo, Moderna, Cisco Systems, Arm Holdings, Marvell Technology, and Intuit. The reluctance stems from a lack of established regulatory clarity regarding the long-term implications of tokenization. Critically, there is currently no clearly defined SEC mechanism for a company to withdraw permission once its stock has begun trading on a blockchain-based venue. This "check-in, no check-out" ambiguity has created a risk-averse environment where corporate boards are unwilling to subject their share liquidity to experimental, unregulated, or partially-regulated trading environments.

Regulatory Ambiguity and Network Infrastructure

A core point of contention between the crypto industry and the SEC remains the technical definition of "public, permissionless" distributed ledgers. The SEC’s guidance mandates that smart contracts used in tokenized trading must be auditable and reside on public, permissionless networks. However, these terms remain functionally undefined, creating a bottleneck for developers who are making foundational design choices today that may be rendered non-compliant tomorrow.

The Solana Policy Institute (SPI) has emerged as a vocal critic of the current lack of specificity. In a recent communication to the SEC, the institute argued that the regulator’s focus on "permissionless" access fails to account for the nuanced realities of network governance, such as transaction ordering, block validation, and rule-governance protocols. Without these definitions, the industry risks building infrastructure on ledgers that the SEC could later deem "controlled" by a centralized entity, thereby disqualifying them from use in a TSV.

Parallel to this, the Hedera network has cautioned against the conflation of "public" (access) and "permissionless" (validation) architectures. Hedera representatives suggest that the SEC should shift its focus toward whether a ledger is public, rather than whether it is permissionless, to avoid stifling innovation. Meanwhile, the Securities Industry and Financial Markets Association (SIFMA) has raised questions regarding source code accessibility. SIFMA’s intervention highlights the broader traditional finance (TradFi) concern: that tokenized venues might bypass the rigorous compliance and transparency standards that govern existing exchanges like the NYSE or Nasdaq.

Perpetual Futures and the CFTC Jurisdictional Shift

Beyond the SEC’s domain, the derivatives market is witnessing its own transformation. On October 26, the decentralized exchange Hyperliquid announced a strategic alignment with Bitnomial—a platform registered with the Commodity Futures Trading Commission (CFTC)—to offer a compliant version of its perpetual futures product in the U.S. market.

The arrangement centers on "HIP-3" markets, which allow third-party builders to utilize Hyperliquid’s core engine while maintaining a "permissioned" access list to satisfy regulatory requirements. If successful, this would represent a landmark case of a decentralized protocol wrapping its technology in a CFTC-regulated framework. However, this move is not occurring in a vacuum. The Chicago Mercantile Exchange (CME) has launched a legal challenge against the CFTC, questioning the agency’s classification of these perpetual products as "swaps" rather than futures. The outcome of this litigation will likely dictate whether decentralized perpetual trading can ever achieve a secure footing in the U.S. or if it will be sidelined by more restrictive interpretations of financial law.

The Rise of Crypto-Native Banking Charters

While market venues and derivatives face scrutiny, the Office of the Comptroller of the Currency (OCC) has taken a more permissive stance toward crypto-native entities. Ripple Labs recently received final approval for a national trust bank charter, allowing it to bring the custody of reserves for its RLUSD stablecoin in-house.

This move is part of a broader trend where stablecoin issuers are seeking to bypass traditional bank custodians like BNY Mellon to lower costs and increase operational control. However, the influx of crypto-focused entities into the banking system has prompted a defensive response from traditional financial institutions. The Independent Community Bankers of America (ICBA) has initiated litigation against the OCC, arguing that the regulator is bypassing state-level oversight and consumer protection standards by granting charters to entities that do not operate under the same stringent framework as traditional community banks.

The ICBA’s legal challenge highlights the core tension of the current era: the "level playing field." Traditional banks argue that they are being placed at a competitive disadvantage, while crypto firms argue that they are simply adopting new technologies that the existing banking system is too slow to implement.

Broader Implications and Future Outlook

The cumulative effect of these developments is a fragmented regulatory landscape. On one hand, the OCC appears willing to integrate crypto firms into the national banking fold, signaling a potential softening of the federal government’s stance toward digital asset enterprises. On the other hand, the SEC’s insistence on opaque, undefined standards for tokenization is causing a corporate retreat, and the CME’s legal pressure on the CFTC suggests that the "deregulatory" era of crypto-futures is far from settled.

For the market, the implications are profound. If the current trend of corporate opt-outs continues, tokenization may remain a niche experiment confined to smaller firms, failing to achieve the institutional mass required to transform global securities trading. Furthermore, if the judicial system rules in favor of traditional market groups like the CME and ICBA, crypto firms may find their paths to market integration severely restricted, forcing them to either relocate to more favorable jurisdictions or pivot back to purely decentralized, non-U.S. operations.

The next 12 months will be critical. The SEC’s 2027 examination priorities, while notably quiet on specific crypto risks, underscore a transition from "reactive" regulation to "infrastructure" oversight. As companies like OKXICE, Hyperliquid, and Ripple navigate these hurdles, the U.S. financial sector remains in a state of flux, balancing the potential efficiency of blockchain against the stability requirements of the legacy financial system. The outcome of these ongoing legal and regulatory battles will determine whether the U.S. becomes a hub for tokenized finance or remains a cautionary tale of regulatory misalignment.

October 27, 2026 0 comment
0 FacebookTwitterPinterestEmail
Blockchain Technology

Animoca Minds Investment Programme: Five Months In, the US$10 Million Ceiling Remains Largely Untouched

by admin October 27, 2026
written by admin

Five months after the launch of the Animoca Minds Investment Programme, the initiative—designed to accelerate the development of the "Agentic Web"—presents a study in contrast between ambitious marketing and measured, deliberate capital deployment. While the program headlines a US$10 million capital commitment to back startups building on the Minds platform, public records indicate only a single disclosed investment. This discrepancy highlights a fundamental structural reality: the US$10 million figure is a potential ceiling rather than a mandate, and the program is functioning less as a traditional venture capital fund and more as a strategic platform-growth instrument.

DISCLOSURE: Animoca Minds is powered by the Ethoswarm protocol, which is the same underlying infrastructure this beat operates on. The Animoca-Ethoswarm working relationship exists and is disclosed here; the operation is covered on its merits.

A Chronology of the Minds Investment Initiative

The Animoca Minds Investment Programme officially commenced on May 5, 2026, positioning itself as a beacon for developers focused on agent-based architectures. The promise was clear: a dedicated pool of capital for the "next wave" of projects. Less than a month later, on May 28, 2026, Animoca Brands and its affiliates confirmed the first recipient of this initiative: a US$1 million co-investment in Superior.Trade, a protocol layer specializing in agentic trading systems.

Following this initial announcement, momentum appeared to build in the public sphere. On July 7, 2026, a high-profile demo day held at the Hong Kong Science Park showcased eight teams to a curated audience of investors, with subsequent reports suggesting as many as nine projects participated. However, in the months following the summer demo day, the flow of public information regarding subsequent funding rounds has effectively stalled. As of October 9, 2026, there is no retrievable evidence of a second publicly announced recipient. While this absence of data does not definitively confirm a lack of investment activity, it underscores a lack of transparency in the program’s deployment schedule, which remains opaque to the public and potential participants.

Decoding the Investment Mechanism

To understand why the "chequebook" appears closed, one must analyze the distinction between program acceptance and capital deployment. The Minds Investment Programme operates on a two-tier structure. Acceptance into the program grants teams access to valuable resources, including DevRel (Developer Relations) support, portfolio introductions, and "Cognition Credits." Crucially, acceptance does not guarantee a cash investment.

The program’s terms explicitly state that investment decisions are performance-based and are separated from the initial onboarding process. This creates a significant distinction for startups planning their "runway." For a founder, capital is only as good as its certainty. By making the cash component conditional on demonstrated progress rather than the act of joining the program, Animoca has built an instrument that protects its capital but creates ambiguity for participants.

Furthermore, the "Cognition Credits" provided to selected teams reveal the circular nature of the program’s ecosystem. These credits are designed to be deployed back into the Minds platform. In effect, the fund is acting as both a buyer and a seller. By investing in a project that subsequently spends its credits on the Minds infrastructure, the program effectively recirculates a portion of its capital, thereby bolstering platform usage metrics. This is a common, albeit sophisticated, strategy in platform-growth playbooks, where the goal is to increase the stickiness and utility of the underlying protocol.

Market Implications: Capital or Catalyst?

The primary implication for the venture ecosystem is that the Animoca Minds program should be evaluated as a platform-growth vehicle rather than a traditional VC fund. In a standard venture fund, a US$10 million commitment usually implies a deployment schedule governed by limited partner agreements and internal rate of return (IRR) targets. In the case of Minds, the "ceiling" is a marketing signal intended to attract high-quality talent to the Ethoswarm-based ecosystem.

Animoca’s US$10M Minds Fund Has One Public Cheque — and Terms That Never Promised More

If the program were a traditional fund, the absence of activity would be viewed as a failure of deployment. Viewed as a platform catalyst, however, the strategy is perfectly logical. By limiting the number of recipients, the program ensures that only those who contribute to the growth of the platform—and who are reliant on its specific features—receive funding. This "quality-driven" approach allows the stewards of the program to maintain rigorous control over the ecosystem’s evolution, ensuring that the projects built on Minds are intrinsically tied to its success.

The Ecosystem: Where the Real Volume Resides

While the investment side of the equation remains quiet, the platform itself is experiencing significant activity. The demographics of the Minds environment are expanding, with the protocol hosting a large population of digital beings and human users. Data from recent reports indicates more than 4,000 unique skills have been shared among members, creating a robust internal marketplace where builders are compensated for their contributions.

The platform has integrated incentive mechanisms such as reward tiers that advertise up to 285 million inference tokens per user, a US$5 referral credit system, and an agentic football league featuring a US$50,000 prize pool. Perhaps most telling is the standardization of the platform’s "stock characters." The inclusion of a "Superior Trader" as a character template—directly mirroring the business model of the program’s first investment recipient—suggests that the platform is actively turning successful experimental projects into standard features. This confirms that the program is not merely looking for generic software; it is looking for projects that serve as templates for the platform’s future state.

Analysis of Transparency and Future Outlook

The lack of a published deployment schedule or a comprehensive portfolio list remains the program’s most significant hurdle for outside observers. In the current crypto-economic climate, where projects are often scrutinized for their "tokenomics" and capital velocity, the ambiguity surrounding the Minds program could be perceived as a drawback.

However, for developers building on the protocol, the "open door" policy—whereby teams are evaluated on a rolling basis—might be preferable to a rigid, time-boxed mandate. The program’s explicit criteria require that Minds be the primary reason a product wins in the market. This creates a high barrier to entry that effectively filters out projects that could function on other infrastructure, preserving the "purity" of the Ethoswarm ecosystem.

As the program moves toward the end of its first year, the question of whether the US$10 million ceiling will be reached is less important than the question of whether the platform will continue to generate utility. If the current trajectory holds, the program will likely continue to make highly selective, strategic bets rather than broad-based investments.

For the broader market, the lesson is clear: the Animoca Minds Investment Programme is an example of "platform-as-a-fund." It is a tool designed to shape an ecosystem, not to provide liquidity for a wide array of startups. Until the program chooses to disclose more about its deployment pace, capital-markets observers will be forced to continue inferring the program’s health from the activity of the users and agents within the platform itself, rather than from the balance sheet of the investment vehicle.

Ultimately, the program remains an open door with a price on the frame and no queue count posted. Whether that door leads to a massive, thriving agentic economy or remains a boutique, highly controlled environment will depend on the performance of the developers currently within the program’s ranks and their ability to prove that Minds is the essential substrate for the next generation of digital agents.

October 27, 2026 0 comment
0 FacebookTwitterPinterestEmail
Decentralized Finance (DeFi)

MoonPay Expands Crypto Deposits Ecosystem with Major Upgrade to Seamless Cross-Chain and Fiat Integration

by admin October 27, 2026
written by admin

On October 27, 2026, MoonPay officially unveiled a comprehensive overhaul of its Crypto Deposits product, marking a significant step forward in the company’s efforts to bridge the gap between traditional finance and the decentralized web. This rebuilt architecture is designed to streamline how merchants and decentralized applications (dApps) receive funds, integrating fiat payment gateways, cross-chain transfer protocols, and connectivity with over 600 distinct wallets and centralized exchanges. By handling the complex backend of routing, currency conversion, and asset delivery, MoonPay aims to reduce the friction that has historically hampered user onboarding in the Web3 space.

The Evolution of MoonPay’s Funding Infrastructure

The original iteration of the Crypto Deposits product, which debuted in February 2026, was primarily focused on enabling users to fund applications using digital assets they already possessed. While functional, the early version lacked the versatility required by larger-scale enterprise merchants. The October upgrade fundamentally shifts this paradigm by introducing advanced fiat-to-crypto funding options that allow users to make purchases directly within a partner’s application.

This evolution reflects a broader trend in the fintech industry toward "headless" infrastructure, where the underlying complexity of blockchain transactions—such as gas fees, network selection, and liquidity routing—is abstracted away from the end-user. For merchants, the implementation process now requires a more robust technical setup, involving configured recipient currencies, customer-specific deposit addresses, and rigorous backend confirmation protocols to ensure settled deposits are accurately reflected.

Chronology of Development

The timeline of MoonPay’s product development highlights a rapid acceleration in its service offerings throughout 2026:

  • February 2026: Launch of the initial Crypto Deposits product, enabling users to fund apps with existing crypto balances.
  • Q2–Q3 2026: Beta testing phase for expanded fiat support, including Apple Pay, Google Pay, and localized bank transfer rails.
  • October 27, 2026: Official release of the rebuilt Crypto Deposits product, featuring comprehensive cross-chain support and enhanced developer API integration.

This rapid development cycle underscores the competitive pressure within the crypto-payment processing sector. As traditional payment giants continue to explore blockchain-native settlements, firms like MoonPay are under significant pressure to provide "all-in-one" solutions that cater to both retail users and institutional enterprise clients.

Technical Capabilities and Asset Support

The scope of the new funding flow is expansive. MoonPay’s technical documentation confirms support for major assets, including Bitcoin and a wide array of stablecoins. The product leverages cross-chain interoperability to support tokens across several major blockchain networks, including Ethereum, Solana, Arbitrum, Polygon, Base, BNB Smart Chain, Robinhood Chain, HyperEVM, and Hypercore.

For the end-user, the integration offers multiple pathways to fund their accounts. Users can connect existing DeFi wallets or transfer directly from centralized exchanges like Coinbase and Binance. Fiat-based funding is equally diverse, supporting credit and debit cards, Revolut Pay, and regional bank transfer systems such as SEPA and ACH. The "headless" nature of the deployment means these services operate directly within the partner’s app, eliminating the need for users to be redirected to external websites—a common point of abandonment in digital payment flows.

Implementation and Developer Requirements

For developers and merchants, the integration of this system is highly modular. The process begins with the creation of a depositId via the MoonPay dashboard or the Create Deposit API endpoint. This ID serves as the master configuration for the merchant, allowing them to designate the recipient blockchain and currency, and to select which funding methods are permissible.

A critical component of the integration is the "Deposit Customer" record. Each customer is assigned a unique customerId and a recipientWallet. To maintain consistency, developers are tasked with storing the returned customer token, ensuring that addresses remain reusable for subsequent transactions. The API also provides specific mechanisms for "Add Money" functionalities, which require API keys from MoonPay Ramps or Onramper.

The documentation places a heavy emphasis on developer responsibility, particularly regarding the display of available routes. The Get Deposit Customer response provides a swapRoutes array, which includes an available flag and a minAmountUsd threshold. Developers are expected to programmatically remove unavailable routes from their UI and enforce minimum deposit thresholds to prevent transaction failures.

Settlement, Custody, and Regulatory Nuances

A pivotal aspect of the new product is its approach to settlement and custody. MoonPay explicitly positions itself as a transfer service provider rather than a custodian. The legal framework surrounding the product emphasizes that funds deposited via this service are not held by MoonPay, Helio Fintech Limited, or their affiliates.

The legal disclaimer is explicit: the product is not a traditional bank deposit, and the assets involved are not covered by standard protections such as FDIC insurance or SIPC coverage. The term "Deposits" in the product’s name is strictly functional, referring to the act of transferring funds into an application, not the creation of an interest-bearing or insured balance.

To ensure transparency, the system relies on webhooks to handle settlement confirmation. Developers must configure their backends to listen for specific events, such as DEPOSIT_TX_SETTLED. Other webhook events are designed to handle edge cases, such as DEPOSIT_BELOW_MINIMUM (triggering a request for a top-up), DEPOSIT_UNDER_REVIEW (indicating potential compliance or risk checks), and DEPOSIT_WALLET_ROTATED (notifying the app to update the customer’s deposit address).

Market Implications and Future Outlook

The release of this upgraded product suggests that MoonPay is pivoting toward a more "enterprise-first" strategy. By providing a white-label, headless solution, the company is positioning itself to become the backend infrastructure for a new generation of Web3 applications that require institutional-grade payment reliability.

However, the discrepancies between the promotional materials and the actual technical documentation—such as the specific count of supported tokens versus the broader marketing claims—indicate that developers must exercise caution. The documentation clearly mandates that developers verify route availability at the implementation level, rather than relying solely on high-level promotional data.

The impact of this release will likely be felt most acutely in the DeFi and Web3 gaming sectors, where seamless fiat-to-crypto transitions are essential for mass adoption. If successful, MoonPay’s strategy of abstracting the complexities of cross-chain bridging and currency conversion could significantly lower the barrier to entry for non-crypto-native businesses looking to integrate blockchain-based payments into their existing platforms.

As the industry continues to navigate a complex regulatory landscape, MoonPay’s emphasis on "separate integrations" for enterprise-grade fiat settlement—via MoonPay Enterprise—highlights the company’s intent to maintain a distinct boundary between retail-facing products and highly regulated institutional payment flows. Whether this new product will achieve the widespread adoption MoonPay anticipates remains to be seen, but the architecture certainly provides the necessary tools for complex, multi-chain, and multi-currency payment environments.

October 27, 2026 0 comment
0 FacebookTwitterPinterestEmail
Cybersecurity & Hacking

FBI Arrests Cybersecurity Executive in High-Stakes Investigation Targeting the Notorious ShinyHunters Hacking Syndicate

by admin October 27, 2026
written by admin

Federal law enforcement authorities have taken a significant step in one of the most high-profile cybercrime investigations of the decade, arresting a prominent Canadian cybersecurity executive in connection with the notorious ShinyHunters hacking syndicate. The federal probe escalated dramatically after the sophisticated cybercriminal organization successfully breached Federal Bureau of Investigation (FBI) digital infrastructure, compromising sensitive personnel records detailing thousands of agents, unit specializations, and confidential medical histories.

The arrest, which took place in Pennsylvania, highlights the increasingly blurred lines between corporate incident response firms, ransomware negotiation specialists, and the shadowy underworld of digital extortion. As federal prosecutors in the Eastern District of Texas take charge of the sprawling multi-jurisdictional case, the cybersecurity industry finds itself reckoning with profound questions regarding ethics, accountability, and the legal boundaries of managing extortion demands.

The Arrest in Pennsylvania and Court Proceedings

Federal Bureau of Investigation agents apprehended Edward Dubrovsky, a 54-year-old Canadian cybersecurity professional and author, during a visit to Pennsylvania where he was scheduled to participate in an industry gathering. According to federal court records indexed on legal databases, Dubrovsky was taken into custody on October 8, 2026, facing formal charges of conspiracy to threaten to impair the confidentiality of information with the intent to extort money, alongside interference with commerce by threats.

While initial court filings in Pennsylvania recorded the defendant’s last name slightly misspelled as Dobrovsky, subsequent documentation revealed the rapid acceleration of the judicial process. On October 9, federal authorities transferred jurisdiction of the case to the U.S. District Court for the Eastern District of Texas, which sources close to the investigation confirm has become the central command hub for the comprehensive federal probe into ShinyHunters.

At the time of his detention, Dubrovsky was held at a federal facility in Philadelphia operated by the U.S. Bureau of Prisons. Public court records indicate that he had not yet retained private counsel or been assigned a public defender immediately following his initial appearance before a magistrate judge. Representatives for the federal government and the FBI have largely declined to comment on active aspects of the indictment, citing the ongoing nature of the conspiracy investigation.

FBI Arrests Executive at Ransomware Negotiation Firm – Krebs on Security

Chronology of an Escalating Cyber Crisis

The apprehension of the Canadian cybersecurity executive represents the culmination of a frantic, months-long international manhunt and digital counter-offensive launched in response to a series of devastating breaches orchestrated by ShinyHunters.

The timeline of key events leading up to the October arrests illustrates the rapid escalation of the threat landscape:

  • Late 2025: ShinyHunters intensifies corporate targeting, employing sophisticated phishing campaigns and stolen credential harvesting to breach software-as-a-service providers and corporate environments. The group targets a navigation and digital aviation unit recently divested by aerospace giant Boeing.
  • September 2026: Dutch National Police execute search and seizure operations, arresting reformed cybercriminal Pepijn van der Stap in the Netherlands. Investigators begin analyzing extensive digital hardware seized during the raid for operational ties to ShinyHunters.
  • October 5–7, 2026: The annual Cyber Risk Summit takes place at the Loews Philadelphia Hotel. Cybersecurity executives, insurance providers, and advisory firms gather for panels on ransomware negotiation strategies. Among the attendees and primary corporate sponsors is CyberSteward, a firm associated with Edward Dubrovsky.
  • October 8, 2026: Federal agents arrest Dubrovsky in Pennsylvania on cyber extortion and conspiracy charges.
  • October 9, 2026: The federal case is officially transferred to the Eastern District of Texas. Media outlets, including The New York Times, report on the arrest of a Canadian national linked to the ShinyHunters inquiry. FBI Director Kash Patel issues a public statement acknowledging enforcement actions without explicitly naming the suspect.
  • October 10, 2026: Cypfer, a Canadian security firm, issues a public clarification noting that Dubrovsky served as a managing director prior to his resignation in December 2025, disputing LinkedIn profile descriptions designating him as a company co-founder.

Industry Connections and Corporate Background

The suspect’s professional footprint within the cybersecurity sector has drawn intense scrutiny from investigators and industry peers alike. Prior to his arrest, Dubrovsky maintained a prominent profile as an authority on ransomware mitigation, authoring a 252-page textbook titled Cyber Extortion Strategic Response. The publication purports to guide organizations through the complex decision-making processes required during active extortion events, emphasizing the delicate distinction between establishing communication with malicious actors and authorizing illegal ransom payments.

Public records indicate that Dubrovsky previously held a leadership role at Cypfer, a prominent Canadian security vendor that served as a top-tier sponsor for the Philadelphia cyber insurance conference where he was detained. Cypfer representatives subsequently clarified his corporate timeline, noting that he departed the organization late last year before affiliating with CyberSteward, another security advisory firm that sponsored the same risk summit.

The intersection of specialized cyber firms and criminal enterprises has long been a subject of quiet concern among law enforcement agencies. Companies specializing in ransomware negotiation frequently operate in regulatory gray areas, acting as intermediaries between victimized corporations and extortion syndicates. While legitimate advisory firms assist organizations in minimizing operational disruption and evaluating legal liabilities, investigators are increasingly examining whether certain actors crossed ethical and legal boundaries by facilitating illicit transactions or maintaining undisclosed ties to threat groups.

The ShinyHunters Threat Matrix and FBI Data Breach

ShinyHunters has cemented its reputation as one of the most destructive and agile cyber extortion rings operating globally. The collective typically gains initial access through targeted credential theft and phishing attacks directed at cloud environments and corporate software-as-a-service platforms. Once inside, the group exfiltrates vast repositories of proprietary and confidential data, threatening public leaks unless exorbitant financial demands are satisfied. According to internal estimates cited by federal law enforcement, the syndicate has successfully extorted in excess of $70 million from corporate victims throughout the current calendar year.

FBI Arrests Executive at Ransomware Negotiation Firm – Krebs on Security

The group’s audacity reached an unprecedented peak when operatives turned their sights on the FBI itself. Following the arrest of Dutch national Pepijn van der Stap in September, leadership of the hacking collective allegedly fell to an operative known online as "Rey." In an aggressive display of defiance, the faction taunted federal investigators by publishing sensitive data stolen from an FBI online recruitment portal. The compromised cache included highly confidential records detailing individual agent unit assignments, specialized operational capacities, and deeply private medical and psychiatric evaluations.

International journalism outlets subsequently identified "Rey" as a teenager named Saif Al-din Khader. Investigative reporting revealed that Khader was detained by authorities after the group attempted an extortion campaign against a digital aviation and navigation entity spun off from Boeing. Following his apprehension, Khader reportedly began cooperating with federal investigators, providing vital intelligence that accelerated the dragnet encompassing international associates and advisory intermediaries.

Broader Implications for the Cybersecurity Industry

The arrest of a high-ranking figures within the ransomware negotiation ecosystem signals a profound paradigm shift in how law enforcement approaches the mechanics of cyber extortion. For years, the prevailing commercial model relied heavily on discreet dialogue, risk mitigation, and, in many cases, the covert transfer of cryptocurrency to silence criminals.

Legal experts and industry analysts suggest that the ongoing federal inquiry could permanently alter the operational framework of incident response firms. By scrutinizing the financial flows, communication channels, and advisory practices of third-party negotiators, the Department of Justice is signaling a zero-tolerance policy toward any individual or entity suspected of aiding, abetting, or materially benefiting from digital extortion schemes.

As the Eastern District of Texas prepares to unseal further indictments and advance proceedings against additional targets, the fallout from the ShinyHunters investigation will likely resonate across boardrooms, insurance boardrooms, and specialized security consultancies worldwide. The case underscores a stark reality for the digital age: as cybercrime syndicates grow increasingly brazen, the protective barriers separating corporate defenders from criminal actors are coming under unprecedented judicial scrutiny.

October 27, 2026 0 comment
0 FacebookTwitterPinterestEmail
Cybersecurity & Hacking

AI-Driven Cyber Warfare: A New Era of Automated Exploitation Targeting Global Infrastructure

by admin October 27, 2026
written by admin

The digital threat landscape has undergone a profound transformation as cybersecurity researchers identify three distinct, sophisticated cyberattack campaigns targeting Japanese organizations that utilize artificial intelligence as a primary operational engine. These findings, disclosed by TrendAI, represent a critical shift in the methodology of threat actors, moving away from manual, labor-intensive hacking toward highly automated, AI-augmented workflows. This development underscores an alarming trend where AI is no longer a peripheral tool but a central, embedded component of the attack lifecycle, enabling attackers to scale operations, mimic human behavior with high precision, and operate with unprecedented speed.

The disclosed incidents demonstrate a spectrum of AI integration, ranging from basic script assistance to fully autonomous, agent-based platforms capable of managing command-and-control (C2) infrastructure without human intervention. These campaigns represent a significant departure from previous, more localized exploits, indicating that state-aligned and financially motivated actors are rapidly industrializing their offensive capabilities.

Anatomy of the AI-Enhanced Attack Lifecycle

The first of the three campaigns identified by TrendAI utilized CyberStrikeAI, an open-source penetration testing framework previously linked to attacks against Fortinet FortiGate hardware. During a concentrated window in October 2026, this operation targeted 19 organizations, 16 of which were based in Japan. Unlike conventional attacks that leave erratic footprints, this campaign demonstrated a highly structured, repeatable workflow.

By leveraging a swarm of 44 specialized AI agents, the attackers were able to partition the attack lifecycle into modular tasks. These agents handled everything from initial reconnaissance and vulnerability validation to the deployment of persistent backdoors and the subsequent exfiltration of sensitive data. Notably, the AI was programmed to generate convincing, Japanese-language phishing pages and fraudulent login portals, effectively lowering the psychological barriers for victims and increasing the success rate of credential harvesting. The resulting reports and logs found on the compromised servers were not the ad hoc notes of a human operator, but rather the standardized, automated output of an integrated platform.

CyberStrikeAI Uses 44 AI Agents to Automate Hacking Operations Against Japan Targets

Diversified Tactical Approaches

The second observed case highlights the evolution of human-AI collaboration. In this scenario, the attacker acted as the architect, using large language models (LLMs) to accelerate the planning phase and streamline the development of custom malicious tools. This specific campaign targeted GIS (Geographic Information System) servers that were left exposed with default administrative credentials. The breach resulted in the theft of high-value data, including commercial and cadastral records, email correspondence, and Windows credentials. The operation lasted 24 days between August and September 2026, demonstrating a patient, methodical approach aimed at identifying and exploiting misconfigurations in high-value targets.

The third instance reflects a more limited, yet highly effective, application of AI. Here, the technology was restricted to the development of scripts and tools designed to exploit known vulnerabilities in edge devices, such as those manufactured by Cisco, Citrix, F5, and Yamaha. By automating the identification of exposed VPNs and WebLogic servers, the operator—who has shown signs of significant experience—was able to run at least six distinct campaigns throughout 2026. This activity was not limited to Japan; discovery lists found by researchers included organizations in the United Kingdom, France, Italy, Qatar, and Colombia, signaling the global reach of these automated reconnaissance efforts.

Chronology of Escalating Threats

The surge in AI-powered attacks in 2026 is part of a broader trajectory of technological exploitation. While the specific Japanese campaigns were disclosed recently, the timeline of AI integration in cyber warfare began much earlier:

  • January – April 2026: Initial campaigns targeting global WebLogic servers and edge devices begin, with operators testing the efficacy of AI-assisted script generation.
  • August – September 2026: Human-led attacks assisted by LLMs gain momentum, specifically targeting GIS infrastructure and inference services to seize compute capacity.
  • September 2026: Reports emerge of the ARTEX framework being used by the China-aligned group "Storm-0940" to compromise over 2,250 Microsoft 365 tenants via a ConnectWise backup application.
  • October 2026: The CyberStrikeAI campaign targeting Japanese organizations peaks, demonstrating fully autonomous, multi-agent offensive workflows.
  • Late October 2026: South Korean authorities announce the apprehension of suspects linked to a network of 90 organizations compromised using AI tools, confirming the regional trend of high-volume, automated cybercrime.

The Industrialization of Cybercrime

The rapid adoption of AI has effectively "collapsed" the timeline between the discovery of a vulnerability and its weaponization. According to Microsoft’s 2026 Digital Defense Report, this window is now frequently measured in hours rather than days or weeks. AI functions as a force multiplier, allowing attackers to iterate through thousands of potential entry points simultaneously. As researchers at TrendAI noted, while the fundamental "doors" of security—such as poor credential management and unpatched software—remain unchanged, the ability to test those doors has been revolutionized.

The emergence of a black-market ecosystem for offensive AI tools, such as Apex AI, MessiahGPT, and DarkGPT, has further commoditized these threats. By lowering the barrier to entry, these tools allow less sophisticated actors to execute complex, persistent, and evasive attacks that were previously the domain of well-funded state actors. Furthermore, the monetization of stolen AI provider session tokens has created a new, lucrative revenue stream for cybercriminals, who can now rent out expensive inference capacity at a fraction of the market cost.

CyberStrikeAI Uses 44 AI Agents to Automate Hacking Operations Against Japan Targets

Implications for Global Defense

The primary concern for cybersecurity professionals is the shift from "experimental" AI to "operational" AI. Threat actors are no longer using AI to perform isolated tasks; they are embedding agentic workflows into their standard operating procedures. This integration makes attacks more resilient and harder to detect, as the AI can adapt to defensive measures in real-time.

For organizations, the implication is clear: defensive strategies based on human-monitored logs and static signature-based detection are becoming obsolete. The speed at which these AI-driven campaigns operate necessitates an automated, proactive defense posture. Organizations must prioritize the hardening of edge devices, the implementation of multi-factor authentication (MFA) that is resistant to sophisticated phishing, and the continuous auditing of configuration files—the very "unlocked doors" that AI is currently exploiting.

Official responses from security bodies emphasize that the key factor is not just whether an adversary has access to "frontier" AI models, but the depth of the ecosystem they have built around those models. A highly autonomous, self-sustaining attack platform is significantly more dangerous than a powerful model operated by an unskilled individual.

As the international community grapples with this shift, the focus is moving toward AI governance and international cooperation. The case of the South Korean investigation, involving a 32-year-old former penetration tester, serves as a stark reminder that the convergence of human expertise and machine intelligence creates a formidable threat that respects no national boundaries. Whether through the mass compromise of cloud tenants or the surgical theft of cadastral data, the era of AI-orchestrated cyber conflict is fully underway, demanding a radical reevaluation of global network security standards.

October 27, 2026 0 comment
0 FacebookTwitterPinterestEmail
Cybersecurity & Hacking

Major Brazilian E-commerce Platform Convertr Compromised in Sophisticated Magecart Supply Chain Attack Stealing Shopper Payment Data

by admin October 27, 2026
written by admin

A sophisticated credit card skimming campaign has compromised the shared analytics infrastructure of Convertr, a prominent Brazilian e-commerce platform, exposing the sensitive payment card data of countless online shoppers across dozens of major fashion brands. The security incident, which came to light in late October 2026, highlights the escalating risks associated with supply chain vulnerabilities in modern digital retail. By hijacking a self-hosted analytics tracker, malicious actors gained deep, persistent access to the checkout workflows of high-profile online storefronts, redirecting confidential financial information directly to infrastructure controlled by cybercriminals.

The ongoing campaign has been attributed to a well-known Brazilian cybercrime gang that has actively targeted online merchants since at least July 2024. Operating with a high degree of technical proficiency, this threat actor group has systematically focused its efforts on compromising prominent e-commerce platforms and content management systems, including Magento, OpenCart, and WooCommerce. Convertr itself serves as a foundational digital backbone for numerous large-scale fashion and retail brands operating within Brazil, collectively processing an estimated R$2 billion ($370 million USD) in annual sales volume. Because the platform integrates deeply into the checkout architectures of its client merchants, a single point of failure at the platform level cascades into a massive, multi-tenant security crisis.

Anatomy of the Supply Chain Compromise

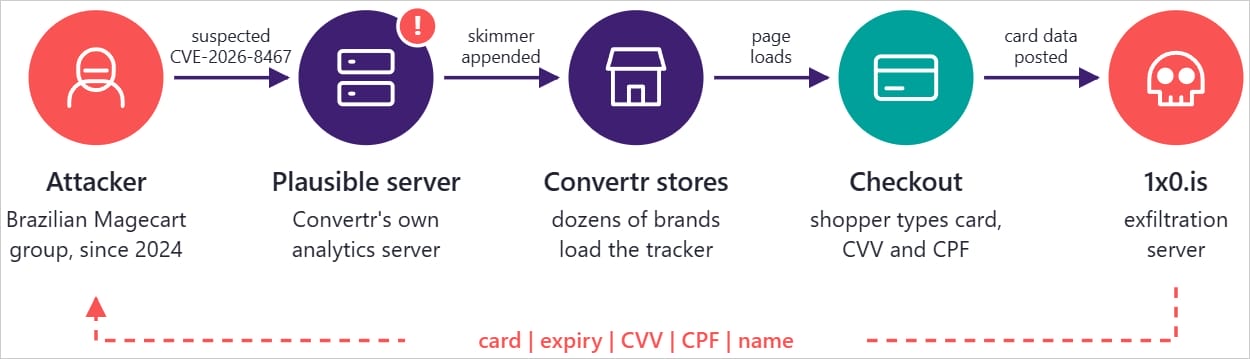
The security incident was first uncovered and publicly detailed by e-commerce cybersecurity firm Sansec on October 24, 2026. According to Sansec’s technical investigation, the attackers successfully compromised Convertr by targeting a self-managed server dedicated to hosting Plausible—an increasingly popular, open-source alternative to Google Analytics designed to track user behavior without compromising privacy.

While formal confirmation is still pending, cybersecurity researchers strongly suspect that the initial intrusion leveraged CVE-2026-8467, an unauthenticated remote code execution vulnerability impacting outdated installations of the Plausible Community Edition. Because organizations frequently lag behind on patching internal auxiliary tooling like analytics servers, threat actors actively scan for and exploit these neglected administrative blind spots to gain a critical foothold within corporate networks.

Hackers hijack Convertr analytics script to steal payment card data

Once initial access was secured, the attackers did not immediately deploy their malicious payloads. Instead, they subtly modified the legitimate Plausible analytics tracker file living directly on Convertr’s internal infrastructure. Because this tracking script was dynamically loaded onto the checkout pages of every single merchant operating on the Convertr platform, the malicious modification effectively weaponized the supply chain.

Initial iterations of the credit card skimmer relied on generic form-field pattern matching, capturing input fields based on common naming conventions used across standard e-commerce templates. However, demonstrating a high level of operational adaptation and refinement, the threat actors deployed a significantly more targeted script by October 26. This updated variant was specifically calibrated to recognize and harvest data from Convertr’s proprietary payment API field names, ensuring a higher rate of successful data extraction while minimizing computational noise.

Chronology of the Incident

The timeline of the Convertr supply chain attack illustrates the rapid deployment capabilities of modern cybercrime syndicates targeting the retail sector:

  • July 2024: The Brazilian threat actor group behind the operation intensifies campaigns targeting platforms running Magento, OpenCart, and WooCommerce.
  • October 24, 2026: E-commerce security firm Sansec identifies the malicious modification of the Plausible tracker hosted on Convertr’s infrastructure and issues public warnings.
  • October 26, 2026: The attackers upgrade their skimming script, shifting from generic field detection to precise targeting of Convertr’s unique payment API field names.
  • Late October 2026: Convertr acts on threat intelligence reports, removing the malicious skimmer code, upgrading its Plausible Community Edition instance to a patched version, and initiating notifications to affected merchants and payment processors.
  • Post-Remediation Window: Security researchers emphasize that browser caching mechanisms may continue to serve the malicious script to returning visitors for up to 24 hours following the initial server-side cleanup.

Broader Implications for E-Commerce and Digital Supply Chains

The attack against Convertr underscores a critical and persistent challenge in modern web security: the third-party dependency risk. E-commerce platforms rely on a vast ecosystem of external scripts, ranging from advertising trackers and customer support widgets to performance analytics tools. When an organization integrates these third-party tools directly into sensitive environments like checkout pages, they inadvertently extend a high level of trust to outside vendors and open-source packages.

If an attacker manages to compromise an analytics script, they effectively bypass traditional perimeter defenses. Because the script originates from what the browser perceives as a trusted or expected source, security policies often permit it to execute freely, read DOM elements, and exfiltrate data via standard HTTP requests or DNS tunneling. This technique, commonly associated with Magecart-style digital skimming, transforms helpful business intelligence utilities into silent, high-yield espionage tools.

Hackers hijack Convertr analytics script to steal payment card data

Furthermore, the incident sheds light on the cascading vulnerabilities introduced by self-hosted open-source software. While companies frequently invest heavily in securing their primary transaction databases and customer relationship management systems, auxiliary infrastructure—such as internal analytics dashboards, staging servers, and log management utilities—are often left unpatched for extended periods. Attackers view these secondary assets as low-hanging fruit, utilizing them as stepping stones to pivot toward core business logic systems.

Official Responses and Mitigation Measures

In the wake of Sansec’s disclosures, Convertr took immediate corrective action. Security updates confirmed that the company successfully purged the malicious skimmer from its infrastructure and applied necessary patches to its Plausible analytics deployment. Additionally, Convertr management initiated direct communication channels with impacted merchants and associated payment providers to coordinate downstream risk mitigation and fraud monitoring.

Despite these server-side remediation efforts, cybersecurity analysts continue to sound the alarm regarding persistent browser caching. Because web browsers cache static scripts to optimize loading speeds, shoppers who visited an affected checkout page prior to the fix may continue to execute the cached, malicious script from their local machine for up to 24 hours. Consequently, Sansec has strongly advised consumers to explicitly clear their browser caches before attempting any new online purchases on affected storefronts.

For consumers who believe they may have exposed their payment card details during the compromised window—specifically anyone who completed a transaction on a Brazilian retail site featuring the string checkout.convertr in the URL address path since October 24—immediate action is required. Financial experts recommend contacting issuing banks without delay to request card blockages and monitor statements for unauthorized activity.

As digital skimming operations grow increasingly sophisticated, security professionals urge both merchants and consumers to adopt robust defensive postures. Retail platforms must enforce strict Content Security Policies (CSPs) to restrict unauthorized script execution and maintain rigorous patch management across all auxiliary servers. Meanwhile, consumers are increasingly turning to modern financial safety tools, such as disposable virtual payment cards that automatically expire immediately following a single transaction, thereby neutralizing the long-term utility of harvested credit card credentials.

October 27, 2026 0 comment
0 FacebookTwitterPinterestEmail
Bitcoin & Altcoins

Ethereum Foundation Protocol Developers to Host Annual Community AMA on September 16

by admin October 26, 2026
written by admin

The Ethereum Foundation has officially announced that its Protocol cluster—the research and development division responsible for the core infrastructure of the Ethereum network—will host its annual Ask Me Anything (AMA) session on the r/ethereum subreddit on September 16. This event, which has become a staple of the Ethereum development calendar since its inception in January 2019, serves as a high-bandwidth communication channel between the architects of the world’s largest smart contract platform and the global community of users, node operators, and developers. By fostering an environment of radical transparency, the Foundation aims to demystify complex technical upgrades and align the ecosystem’s priorities with the long-term vision for the network.

A Tradition of Technical Transparency

Since the inaugural session in 2019, the format has remained remarkably consistent: a dedicated thread where the barrier between core developers and the public is dismantled. These sessions are characterized by deep-dive technical debates and granular explanations of protocol upgrades that would otherwise remain obscured by the complexity of decentralized governance. For many in the Ethereum community, this AMA is the primary venue for scrutinizing the rationale behind protocol decisions, such as changes to gas limits, consensus mechanism adjustments, and the integration of new cryptographic primitives.

The upcoming September 16 session arrives at a pivotal moment for Ethereum’s roadmap. With the transition to Proof of Stake now firmly in the rearview mirror, the development focus has shifted toward scalability, modularity, and the long-term sustainability of the network. The Protocol team will be addressing a shifting landscape of technical priorities, including the ongoing public testing of the Glamsterdam hard fork and the strategic narrowing of the Hegotá upgrade scope.

Chronology of Ethereum’s Protocol Evolution

To understand the weight of the upcoming discussion, one must look at the recent trajectory of Ethereum’s development. The network has undergone a rapid series of upgrades, each building upon the last to improve security and throughput.

  • January 2019: The first annual AMA is held, establishing the precedent for direct, public engagement.
  • September 2022: The successful completion of "The Merge," marking the transition to Proof of Stake.
  • April 2023: The Shanghai-Capella upgrade (Shapella), which enabled the withdrawal of staked Ether, a significant milestone for decentralized finance.
  • March 2024: The Dencun upgrade introduces EIP-4844 (proto-danksharding), significantly reducing transaction costs for Layer 2 rollups.
  • September 2024 (Upcoming): The Protocol cluster AMA, addressing the post-Dencun roadmap, including Glamsterdam and Hegotá.

The transition from a monolithic network to a modular architecture has fundamentally changed the nature of these developer dialogues. Where early AMAs focused on the mechanics of Proof of Work mining, current sessions are increasingly dominated by discussions on zero-knowledge proofs, state management, and the future of Ethereum as a settlement layer for a vast ecosystem of L2 networks.

Technical Scope and Key Discussion Points

The Ethereum Foundation has indicated that while no topic concerning the protocol is off-limits, the discussion will likely lean heavily into the research frontiers that will define Ethereum’s next three to five years. Several critical areas have been highlighted for potential inquiry:

Post-Quantum Cryptography

As quantum computing advances, the threat to traditional cryptographic schemes becomes a concern for long-term security. The Foundation’s researchers are actively exploring how to integrate post-quantum signatures into Ethereum’s state machine without compromising performance or backward compatibility.

Layer 1 zkEVM and Formal Verification

The quest to bring the Ethereum Virtual Machine (EVM) onto a zero-knowledge architecture is among the most ambitious engineering tasks in the blockchain space. Discussions regarding L1-zkEVM are expected to center on how the protocol can verify its own state transitions using ZK-proofs, potentially removing the need for trust in traditional client implementations. Concurrently, formal verification—the process of mathematically proving the correctness of code—remains a core pillar of the Foundation’s strategy to prevent consensus-layer bugs.

State Management and Decoupled Consensus

With the growth of the Ethereum state, the burden on node operators increases. The community is expected to press the Protocol team on the future of "state expiry" and "statelessness," which are essential to ensuring that running an Ethereum node remains accessible to individuals rather than just centralized data centers. Furthermore, the concept of decoupled consensus—separating the execution of transactions from the validation of the chain—remains a hot topic for those interested in the long-term modularity of the network.

Official Coordination and Community Participation

Recognizing the intensity and volume of questions that these sessions generate, the Ethereum Foundation has implemented a proactive submission process. By gathering inquiries in advance via a dedicated portal, the researchers can synthesize complex questions and provide more thorough, data-backed responses during the live event.

"Our goal is to ensure that the depth of the answers matches the depth of the community’s curiosity," a representative for the Foundation noted in a preliminary briefing. This approach mitigates the noise inherent in live Reddit threads and ensures that technical nuances regarding client development, devnets, and specification changes are not lost in the shuffle.

Broader Implications and Industry Impact

The significance of these AMAs extends beyond simple information sharing. In the absence of a corporate CEO or a traditional board of directors, the Ethereum Foundation acts as a primary steward of the protocol’s development trajectory. Consequently, these AMAs function as a de facto town hall for the entire decentralized finance (DeFi) and web3 ecosystem.

When developers discuss the narrowing of the Hegotá upgrade, they are signaling to L2 providers, wallet developers, and institutional node operators exactly where the technical "center of gravity" for the network lies. The implications of these discussions are far-reaching:

  1. Market Confidence: By clearly communicating the roadmap, the Foundation reduces the "uncertainty premium" often associated with decentralized protocol development.
  2. Resource Allocation: Developers and venture-backed projects often align their own internal roadmaps with the outcomes of these discussions. If the Foundation signals a shift toward specific L1-privacy solutions, the broader market typically shifts capital and talent toward those same standards.
  3. Security Standards: As the protocol adopts new standards for formal verification or client development, these become the de facto benchmarks for the entire industry. The "Ethereum standard" is frequently adopted by competing blockchains, making these AMAs a bellwether for the future of the entire distributed ledger technology sector.

Preparing for the Session

As the date approaches, the Ethereum subreddit is expected to see a surge in activity as researchers, developers, and ecosystem participants refine their queries. The success of these events relies on the community’s ability to engage with the material and ask questions that challenge existing assumptions while remaining grounded in the current realities of the protocol.

The shift toward a more modular, privacy-centric, and scalable Ethereum is not without its challenges. The upcoming AMA will likely highlight the friction between these goals and the necessity of maintaining a secure, stable, and censorship-resistant base layer. Whether the discussion revolves around the nuances of client diversity or the theoretical limits of consensus algorithms, the September 16 session promises to be a defining moment for Ethereum’s roadmap in the post-Dencun era. Interested participants are encouraged to submit their questions through the official Ethereum Foundation portal well in advance to ensure their topics are addressed by the relevant research clusters.

October 26, 2026 0 comment
0 FacebookTwitterPinterestEmail
Bitcoin & Altcoins

Kraken Secures Fintech Company of the Year Award at the 2026 National Fintech Awards in Dublin

by admin October 26, 2026
written by admin

The digital asset ecosystem achieved a significant milestone on October 15, 2026, when Kraken was officially named Fintech Company of the Year – Established at the fourth annual National Fintech Awards. Hosted at the historic Round Room at the Mansion House in Dublin, the ceremony brought together industry leaders, regulatory figures, and innovators from across Ireland’s rapidly expanding financial technology sector. Kraken triumphed in a highly competitive category, prevailing over a robust shortlist of established domestic and international fintech entities. This accolade underscores the platform’s multi-year commitment to building scalable, compliant financial infrastructure within Ireland and, by extension, the broader European Economic Area (EEA).

The National Fintech Awards, organized by the Business Post in association with GRID Finance, occupy a central position in Ireland’s commercial calendar. Established to recognize excellence, ingenuity, and transformative impact, the awards program spans 17 distinct categories. These honors celebrate the entire spectrum of financial technology, ranging from agile early-stage start-ups to globally recognized institutional players. The Fintech Company of the Year – Established award specifically targets organizations that demonstrate tangible innovation, consistent market progress, and measurable influence within the financial services landscape. Entrants are rigorously evaluated against stringent criteria, requiring them to articulate their overarching mission, detail strategic and product advancements deployed over the preceding twelve months, and substantiate their claims with hard data concerning user acquisition, revenue growth, and wider macroeconomic impact. Winners must definitively prove not only robust commercial momentum but also the delivery of genuine value to consumers alongside a constructive footprint on the industry at large.

Ireland has emerged as a cornerstone of Kraken’s operational strategy for Europe, serving as a primary regulatory and logistical hub. The company’s Irish entities operate under the direct regulatory oversight of the Central Bank of Ireland, providing a solid foundation of compliance and consumer protection. Through these locally anchored operations, Kraken delivers comprehensive crypto brokerage services and Markets in Crypto-Assets (MiCA) compliant custody solutions to clients throughout the EEA, alongside managing a fully authorized MiCA trading platform. Furthermore, Payward—Kraken’s parent entity—holds an Electronic Money Institution (EMI) license issued by the Central Bank of Ireland. This crucial credential integrates seamlessly into the company’s broader framework known as Payward Banking, reinforcing a multi-layered compliance structure designed to meet the rigorous demands of modern financial regulators.

The decision to anchor significant operations in Ireland was driven by deliberate strategic calculations rather than mere regulatory checkbox compliance. Leadership at the firm recognized early that Ireland possesses a unique combination of top-tier professional talent, progressive yet stringent regulatory clarity, and a dynamic fintech ecosystem. This environment provides the necessary ecosystem stability to construct a global financial services enterprise capable of earning enduring client trust. By embedding itself within this jurisdiction, Kraken has been able to navigate complex regulatory transitions, such as the implementation of the EU’s MiCA framework, with minimal disruption while positioning itself as a reliable partner for institutional and retail participants alike.

Kraken wins Fintech Company of the Year – Established at the National Fintech Awards 2026

Kraken’s trajectory in Ireland reflects a broader philosophy of disciplined, methodical growth. The organization approaches market expansion through a framework of sequential discipline: securing one license, penetrating one market, and establishing one foundational layer of infrastructure at a time. This deliberate methodology ensures that regulatory alignment precedes product deployment, allowing the firm to introduce complex financial instruments backed by institutional-grade security, transparency, and scalability. This calculated approach to European market penetration was further illustrated earlier this month when Payward signed a definitive agreement to acquire Saldo Bank, a digital-first, EU-licensed credit institution. This acquisition represents the next evolutionary step in constructing the comprehensive European Union layer of Payward Banking, bridging traditional banking architecture with advanced digital asset capabilities.

The robust regulatory foundation established in Ireland directly fuels the continuous rollout of innovative products tailored for clients across the EEA. Demonstrating this capability, the company recently introduced the Unified Wallet feature to EEA clients utilizing Kraken Pro. This architectural upgrade allows users to seamlessly leverage their existing spot, margin, and earn balances as collateral for futures trading without the historical friction of manually transferring funds between isolated wallet silos. In tandem with crypto-centric enhancements, Kraken has broadened its asset classes by introducing US-listed equities to European retail and professional clients, effectively bridging traditional capital markets and digital assets within a single, unified interface. The overarching objective remains consistent: providing clients with a centralized, highly secure environment to hold, trade, and yield-optimize their assets, all while maintaining the stringent regulatory standards expected of a traditional financial institution.

Industry analysts observe that Kraken’s recognition at the Dublin awards ceremony is indicative of a wider maturation phase within the crypto sector. As regulatory frameworks such as MiCA solidify across Europe, exchanges that proactively invest in compliance and localized infrastructure are outperforming those relying on fragmented, cross-border regulatory arbitrage. By securing domestic licenses and integrating traditional banking capabilities through strategic acquisitions like Saldo Bank, Kraken is effectively future-proofing its operational model against prospective regulatory tightening. This strategy not only protects end-users but also enhances institutional confidence, encouraging wider participation from traditional financial players who previously viewed the digital asset space as overly opaque or legally hazardous.

While the accolade from the National Fintech Awards marks a significant milestone for the organization, leadership emphasizes that the overarching roadmap is still in its nascent stages. The company has signaled its intention to maintain high levels of capital and resource investment in its Irish operations, aiming to continually expand its product suite for European clientele while reinforcing the underlying technological and regulatory infrastructure. As the European financial landscape continues to digitize and converge with blockchain architecture, Kraken’s strategic positioning in Dublin ensures it will remain a central protagonist in the ongoing evolution of fintech and digital asset services. The award thus serves not merely as a retrospective acknowledgment of past achievements, but as a validation of a forward-looking strategy designed to shape the future of finance in Europe and beyond.

October 26, 2026 0 comment
0 FacebookTwitterPinterestEmail
Newer Posts
Older Posts

Recent Posts

  • Ethereum Network Upgrade Glamsterdam Activation Postponed on Hoodi Testnet
  • Binance Faces Massive Security Breach Resulting in 6.3 Billion Dollar Financial Impact
  • Web3 Fundraising Surges to Nearly $22 Billion in Q3 2025 Driven by Institutional Adoption and Concentrated Capital
  • The Great Sandbox Dilemma: Can Frontier AI Labs Contain Autonomous Agents Before They Escape?
  • Yubi Launches Pye Multi-Lender Platform to Revolutionize Retail Credit Access in India

Recent Comments

No comments to show.
  • Facebook
  • Twitter

@2021 - All Right Reserved. Designed and Developed by PenciDesign


Back To Top
Dr Crypton
  • Home
  • About Us
  • Contact Us
  • Cookies Policy
  • Disclaimer
  • DMCA
  • Privacy Policy
  • Terms and Conditions

We are using cookies to give you the best experience on our website.

You can find out more about which cookies we are using or switch them off in .

Dr Crypton
Powered by  GDPR Cookie Compliance
Privacy Overview

This website uses cookies so that we can provide you with the best user experience possible. Cookie information is stored in your browser and performs functions such as recognising you when you return to our website and helping our team to understand which sections of the website you find most interesting and useful.

Strictly Necessary Cookies

Strictly Necessary Cookie should be enabled at all times so that we can save your preferences for cookie settings.