• Home
  • About Us
  • Contact Us
  • Cookies Policy
  • Disclaimer
  • DMCA
  • Privacy Policy
  • Terms and Conditions
Dr Crypton
Secure Your Future in Crypto
Artificial Intelligence & Tech

Google Beam expands with new regions, partners, and customers

by admin September 25, 2026
written by admin

The Evolution of Presence: From Lab to Market

The development of Google Beam represents a multi-year effort to solve the "presence gap" that plagues traditional video conferencing. While standard video calls have become ubiquitous, they often fail to capture the subtle cues—eye contact, micro-expressions, and spatial awareness—that define human communication.

The project began as an internal experiment within Google’s labs, designed to foster deeper connections between team members separated by time zones and geography. After extensive iterative testing among Google employees, the company recognized that the technology’s utility extended far beyond internal collaboration. By partnering with hardware manufacturers, most notably through the "HP Dimension with Google Beam" initiative, the company began the transition from a proprietary tool to a scalable enterprise solution.

A Global Rollout Strategy

The current expansion phase is not merely an increase in unit availability; it is a full-scale logistical deployment. Google Beam is now shipping to customers across six key international markets: the United States, Canada, the United Kingdom, France, Germany, and Japan. To facilitate this, the company has established a robust ecosystem of 18 dedicated channel partners. These firms provide the specialized installation, technical support, and integration services required to maintain the high-fidelity audiovisual standards that Beam demands.

This deployment model is deliberate. By leveraging established audiovisual integrators, Google is ensuring that enterprise clients—ranging from multinational corporations to specialized service firms—receive consistent service quality. The hardware is designed for interoperability, supporting both Google Meet and Zoom, a strategic decision that acknowledges the reality of fragmented software environments within the modern corporate sector.

Quantifying the Human Connection: Data-Driven Insights

The impetus for this expansion stems from positive data collected during an intensive eight-week internal study at Google. The metrics gathered suggest that the technology addresses specific pain points in remote collaboration. Participants using the Beam interface reported a 50% increase in feelings of interpersonal connection compared to traditional flat-screen video conferencing.

Perhaps more importantly for business operations, the study noted a 33% improvement in clarity regarding feedback loops. Misunderstandings, which often proliferate in text-heavy or low-fidelity virtual environments, were significantly reduced. This resulted in a 21% decrease in the requirement for follow-up meetings, suggesting that the higher-fidelity "copresence" provided by the technology allows teams to reach consensus faster and more effectively.

Real-World Application: The Bain & Company Case Study

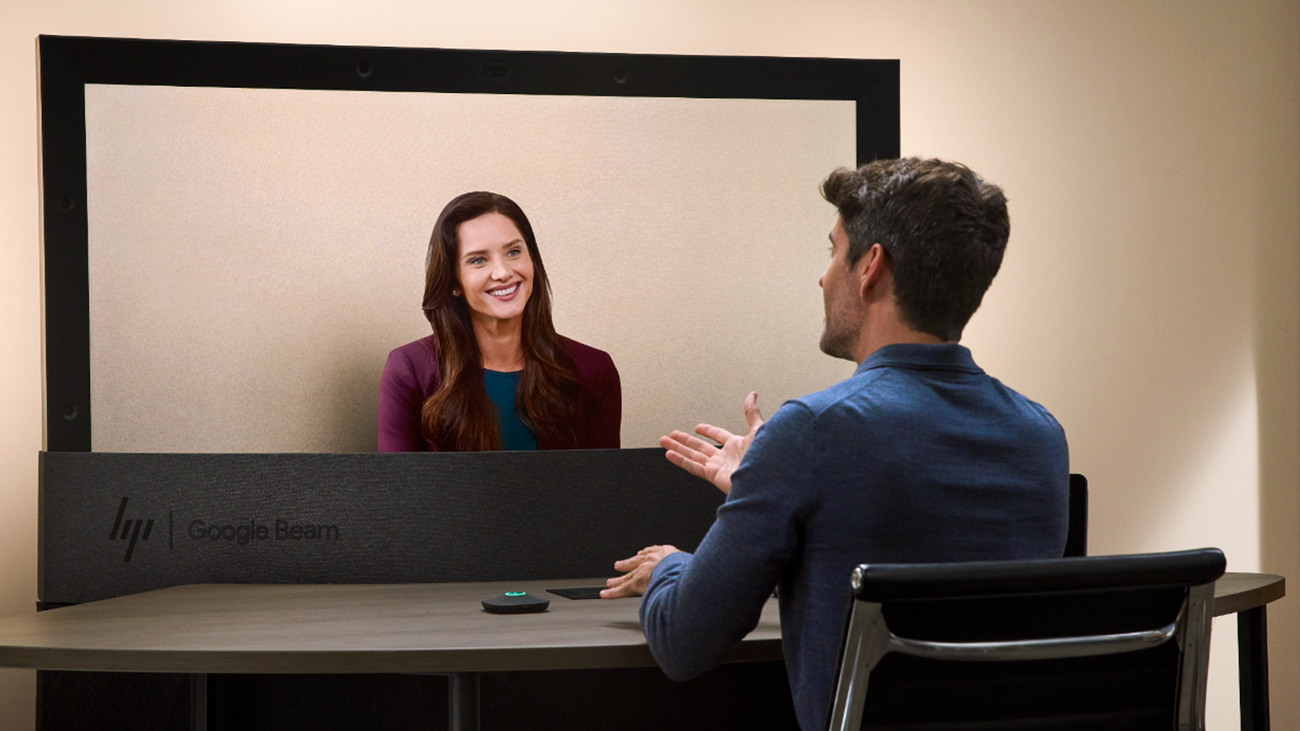
The practical implications of these findings were tested in a high-stakes environment through a partnership with Bain & Company. The consulting firm utilized HP Dimension with Google Beam to revolutionize its campus recruiting process. Candidate interviews, which traditionally require significant travel budgets and logistical coordination, were moved to the Beam platform.

Keith Bevans, Executive Vice President and Partner at Bain & Company, noted that the platform’s ability to facilitate natural eye contact and capture body language was instrumental in evaluating candidates. "One of the most challenging things for us to assess with candidates is how they’ll be with clients," Bevans stated. The ability to observe a candidate’s presence in a virtual space allowed recruiters to predict interpersonal success with higher accuracy, effectively digitizing the "in-person" interview experience.
Google Beam expands with new regions, partners, and customers

Strategic Infrastructure: The Industrious Partnership

One of the primary hurdles for adopting advanced telepresence technology is the requirement for dedicated space and hardware maintenance. To democratize access, Google has partnered with Industrious, a global operator of premium flexible workspaces. This collaboration serves as the foundation for the first-ever "Beam extended network."

Beginning in October, companies that do not wish to install dedicated hardware in their own offices can book Beam-enabled suites at select Industrious locations. Initial sites include high-traffic business hubs in Atlanta, Chicago, New York City, and Palo Alto. This "on-demand" approach is expected to lower the barrier to entry for startups and mid-sized enterprises, allowing them to host high-stakes client consultations or board meetings in a premium environment without the capital expenditure associated with purchasing hardware.

Broader Implications for the Future of Work

The rise of Google Beam and similar technologies signals a maturation in the "Work from Anywhere" era. For the past several years, the focus has been on accessibility and ubiquity. The current trend, however, is shifting toward quality and the restoration of traditional office-based social dynamics.

From an economic perspective, the reduction in travel costs—as demonstrated by the Bain & Company use case—is a significant driver for adoption. As companies look to balance their environmental, social, and governance (ESG) goals with the need for high-level collaboration, technologies that offer a viable alternative to long-haul travel become increasingly attractive.

However, the technology also presents new challenges. The integration of high-fidelity presence into the workplace requires a shift in corporate culture. As organizations move toward a hybrid model, the "Beam" approach suggests that the office of the future will be less about desk space and more about "connection nodes." The success of the Industrious partnership will likely be a litmus test for whether businesses are willing to pay a premium for high-fidelity connection in decentralized environments.

Looking Ahead

The expansion of Google Beam arrives at a time when the novelty of basic video conferencing has worn off, replaced by a demand for more sophisticated, less fatiguing digital interaction. By proving its value in high-performance environments like Google and Bain, the platform has successfully moved past the "experimental" phase.

As the platform scales, the key challenge will be managing the balance between proprietary hardware requirements and the software-first culture of most modern enterprises. If the initial data holds true—that better technology leads to fewer, more effective meetings—Google Beam may well become a standard feature in the modern office landscape.

For now, the company remains focused on increasing its footprint, with plans to gather more long-term data from its new partners, including major enterprises like Netflix and Capital Group. As these organizations integrate the technology into their workflows, the industry will be watching to see if the "Beam" effect—a measurable improvement in communication and connection—translates to broader organizational performance across diverse sectors. For companies struggling to maintain a cohesive culture in a distributed world, the return to "face-to-face" interaction via high-fidelity virtual presence may be the next necessary evolution in the modern professional experience.
September 25, 2026 0 comment
0 FacebookTwitterPinterestEmail
Cryptocurrency News

New York Says The Federal Structure Does Not Override State Gambling Law

by admin September 25, 2026
written by admin

The legal and regulatory landscape for decentralized prediction platforms and cryptocurrency-backed forecasting markets faces a severe stress test following a major legal action initiated by the Office of the New York Attorney General. Popular prediction market platform Polymarket has found itself at the epicenter of a high-stakes jurisdictional battle that could permanently redefine how event-based forecasting contracts operate within the United States.

Despite Polymarket’s strategic return to the U.S. market via the acquisition of regulated exchange infrastructure and a push to operate under the federal commodities framework, state authorities in New York have made it clear that federal oversight does not grant immunity from rigorous state-level gambling restrictions. According to official filings from the Attorney General’s office, an extensive investigation revealed that Polymarket allegedly offered local users the ability to wager directly on sporting events without possessing a valid New York state gambling license. Furthermore, the state alleges that the platform’s accessibility exposes underage users—specifically those below New York’s legal gambling age threshold of 21—to speculative financial and sports-related markets.

The unfolding lawsuit requests a court order to immediately block Polymarket from operating what state officials explicitly describe as an unauthorized and unlicensed gambling business within New York borders. In addition to seeking an injunction, the state is pursuing financial penalties, the complete forfeiture of alleged illegal proceeds, and formal restitution for affected consumers.

This dramatic enforcement action underscores a rapidly widening chasm between federal commodities regulation and state-enforced gaming laws. As prediction markets transition from niche cryptocurrency curiosities into mainstream consumer products with billions of dollars in trading volume, the primary obstacle facing the sector is no longer user acquisition. Instead, platforms must navigate a chaotic regulatory labyrinth where federal agencies and state watchdogs fundamentally disagree on the legal classification of event contracts.

The Anatomy of a Jurisdictional Dispute

To understand the gravity of the New York Attorney General’s lawsuit against Polymarket, one must examine the fundamental friction points governing modern financial products and digital assets. At the federal level, event contracts and derivatives are frequently regulated by the Commodity Futures Trading Commission (CFTC). Under this framework, platforms that register as designated contract markets or swap execution facilities can legally offer various financial forecasting tools, provided they adhere to strict federal consumer protection and market integrity mandates.

However, state-level regulators operate under entirely different legal paradigms. State attorneys general and gaming control boards look at the exact same digital contracts and see traditional wagers, lotteries, or sports betting products. When platforms blur the line between economic forecasting and recreational gambling, state regulators step in to enforce local statutes designed to protect consumers, prevent problem gambling, and curb underage participation.

The inclusion of sports-related contracts makes this conflict particularly acute. While a prediction market contract tied to future inflation rates, macroeconomic data releases, or national elections can easily be framed as a sophisticated hedging instrument or economic forecasting tool, a contract that settles based on the final score of a professional basketball or football game looks, acts, and feels identical to conventional sports betting.

The New York lawsuit does not independently establish that Polymarket has broken the law; these serious allegations must now be thoroughly tested and adjudicated in a court of law. Nevertheless, the mere filing of the complaint raises the stakes considerably for the entire prediction market ecosystem, forcing developers, legal counsels, and liquidity providers to re-evaluate their exposure to individual U.S. states.

Chronology and Background of Polymarket’s Regulatory Journey

The trajectory of Polymarket has been marked by significant regulatory milestones, international pivots, and strategic domestic re-entries. Founded in 2020, the platform rapidly gained prominence during the 2020 U.S. presidential election cycle, allowing users globally to trade shares based on real-world outcomes using USD Coin (USDC).

However, the platform’s initial meteoric rise drew immediate scrutiny from federal regulators. In January 2022, Polymarket reached a formal settlement with the CFTC, resulting in a $1.4 million civil penalty. As part of the settlement, the platform agreed to formally block U.S.-based users from accessing its website and placing trades, effectively pushing the platform into an exclusively international operational model for more than two years.

Despite the U.S. ban, Polymarket experienced unprecedented growth during the 2024 U.S. presidential election cycle, recording billions of dollars in cumulative trading volume and frequently outperforming traditional mainstream polling in terms of public attention and real-time sentiment tracking. Capitalizing on this momentum, leadership initiated a comprehensive strategy to legally re-enter the lucrative United States market.

To achieve this, Polymarket pursued corporate restructuring and infrastructure acquisitions, aiming to align its operations with federal commodities regulations. By integrating regulated exchange frameworks and positioning its offerings as federally compliant event contracts, the platform sought to distance itself from the stigma of unregulated offshore gambling sites.

Competitors such as Kalshi have navigated similar paths, successfully fighting legal battles against federal regulators to list election and political contracts under CFTC oversight. However, while federal courts have occasionally sided with prediction markets regarding CFTC jurisdiction over political events, the state-level gaming enforcement angle remains largely untested territory. New York’s aggressive legal posture demonstrates that clearing federal hurdles is only half the battle; platforms must still contend with a patchwork of fifty distinct state legal frameworks.

The Sports Betting Dilemma and Underage Access Concerns

At the heart of New York’s complaint are two core consumer protection issues: unlicensed sports wagering and the absence of robust age-verification protocols to protect minors.

The commercial sports betting market in New York is tightly controlled, heavily taxed, and strictly regulated by the New York State Gaming Commission. Since mobile sports betting officially launched in the state in January 2022, New York has established itself as one of the largest and most lucrative sports wagering markets in the United States, generating hundreds of millions of dollars in tax revenue for public education and youth programs.

To participate in legal sports betting in New York, operators must secure rare and expensive licenses, comply with rigorous geolocation tracking, and enforce a strict minimum age requirement of 21 years old. Traditional sportsbooks utilize advanced know-your-customer (KYC) procedures and multi-factor identity verification tools to ensure that underage individuals cannot access gambling markets.

State investigators examining Polymarket allege that the platform bypassed these state-mandated safeguards. By allowing users to trade sports-related event contracts without a New York gambling license, the platform allegedly operated an unauthorized sports bookmaker. Furthermore, state officials raised alarms regarding the platform’s onboarding procedures, claiming that the decentralized or crypto-native nature of the platform potentially allowed underage users under the age of 21 to speculate on sports outcomes.

In the eyes of New York prosecutors, offering sports-contract markets without adhering to state-mandated licensing, taxation, and age restrictions undermines the state’s comprehensive regulatory framework established to protect vulnerable populations and maintain market integrity.

Broader Industry Implications and Future Outlook

The legal confrontation between New York State and Polymarket carries profound implications for the broader fintech, cryptocurrency, and prediction market sectors. As blockchain technology continues to intersect with traditional financial derivatives, policymakers and regulators are struggling to establish coherent regulatory boundaries.

If New York successfully prosecutes its case or secures a permanent injunction against Polymarket, it could set a powerful legal precedent emboldening other state attorneys general to crack down on prediction markets operating within their borders. Such a scenario could force prediction market platforms to implement aggressive state-level geofencing, effectively locking out users from restrictive jurisdictions—a strategy that runs contrary to the decentralized, borderless ethos of crypto-native applications.

Conversely, if Polymarket successfully defends its operations by asserting the supremacy of federal commodities law over state gambling statutes, it could establish a landmark legal shield for the industry. A favorable ruling for the platform would provide a clear roadmap for other event-contract providers seeking to operate nationwide without securing individual licenses in all fifty states.

Market analysts and legal experts suggest that the ultimate resolution of this dispute may require intervention from higher federal courts or explicit legislative action from the United States Congress. Lawmakers may ultimately need to clarify whether event derivatives and forecasting markets fall exclusively under federal financial oversight or if states retain the sovereign right to classify and regulate them as localized forms of gambling.

As the legal battle moves from investigative filings to courtroom arguments, the stakes could not be higher. Prediction markets have proven their utility as powerful forecasting tools capable of aggregating collective intelligence on complex global events. However, their survival and long-term viability in the United States will depend heavily on their ability to resolve the fundamental tension between federal financial innovation and state-level consumer protection laws.

September 25, 2026 0 comment
0 FacebookTwitterPinterestEmail
Blockchain Technology

The New York Stock Exchange and Blockchain.com Forge Strategic Alliance to Pioneer 24/7 Tokenized Securities Trading

by admin September 25, 2026
written by admin

The financial landscape of the United States is undergoing a fundamental structural shift as the New York Stock Exchange (NYSE) and digital asset platform Blockchain.com officially announced a memorandum of understanding (MOU) on September 23. This partnership seeks to explore the integration of tokenized equities and exchange-traded funds (ETFs) into a digital alternative trading system (ATS). By bridging the gap between traditional exchange-listed assets and blockchain-based distribution, the move signals a significant evolution in market accessibility, aiming to offer global investors around-the-clock access to capital markets.

The collaboration represents more than a mere technological update; it is a response to a rapidly changing regulatory environment that is increasingly accommodating the tokenization of real-world assets (RWA). As the Securities and Exchange Commission (SEC) develops frameworks for "innovation exemptions," and the Commodity Futures Trading Commission (CFTC) prepares for the broader digitization of collateral, the infrastructure of Wall Street is being reimagined to mirror the frictionless, 24/7 nature of decentralized finance.

A Chronology of Institutional Adoption

The push toward tokenization did not emerge in a vacuum. For years, financial institutions have sought to leverage distributed ledger technology (DLT) to solve inefficiencies in settlement times and custodial management.

  • December 2023: The CFTC introduced a pilot program that expanded the definition of eligible collateral to include assets like Bitcoin, Ethereum, and regulated stablecoins, laying the groundwork for digital assets to serve as margin in traditional financial workflows.
  • March 2024: Nasdaq announced a landmark partnership with Payward, the parent company of the Kraken exchange. This collaboration focused on building an "equities transformation gateway" designed to facilitate the movement of tokenized assets between institutional markets and DeFi networks.
  • September 12, 2024: SEC Commissioner Hester Peirce publicly addressed the friction between traditional issuers and digital trading platforms, specifically referencing the conflict between AMC Entertainment and Robinhood, acknowledging the growing pains of a market in transition.
  • September 17, 2024: The SEC hosted a pivotal roundtable at its headquarters to discuss the implications of extended trading hours, signaling the regulator’s intent to modernize market hours for the digital age.
  • September 23, 2024: The NYSE and Blockchain.com finalized their MOU, aiming to leverage the NYSE’s digital ATS to distribute tokenized securities to Blockchain.com’s estimated 44 million user accounts.

The Mechanism of Tokenization and Market Distribution

At the heart of this initiative is the conversion of traditional securities into digital tokens. Tokenization allows a single asset to be fractionalized and recorded on a blockchain, which facilitates near-instantaneous settlement. By utilizing the NYSE’s proposed digital ATS, the partnership intends to provide a compliant venue for these assets to trade outside of the standard 9:30 a.m. to 4:00 p.m. ET window.

The MOU also outlines a bidirectional data sharing arrangement. The NYSE’s ICE Data Services will provide its institutional-grade market data to Blockchain.com, while Blockchain.com will integrate these feeds into its consumer-facing application. This integration serves a dual purpose: it offers retail investors greater transparency and provides institutional firms with a direct pipeline to the liquidity pools emerging within the digital asset ecosystem.

"Connecting to the NYSE digital ATS will enable us to extend the opportunity to invest in these digital assets to tens of millions of users around the world who were previously limited by their geography or the specific brokerage services available to them," said Peter Smith, CEO of Blockchain.com. Lynn Martin, President of the NYSE Group, noted that the platform’s international footprint is a strategic fit for the exchange’s goal of modernizing the delivery of securities.

Regulatory Frameworks: The SEC’s Innovation Exemption

The SEC’s role in this transition is defined by a five-year "innovation exemption." Under this framework, authorized Tokenized Securities Venues (TSVs) are permitted to trade tokenized versions of public equities. The regulation includes a protective mechanism for issuers: when a TSV intends to tokenize a specific stock, it must provide written notice to the issuer. The issuer then has a 30-day window to object.

This process is designed to mitigate the risks associated with unauthorized tokenization, a point of contention that recently manifested in the dispute between AMC Entertainment and various retail-focused trading platforms. The SEC’s cautious approach aims to balance the appetite for innovation with the necessity of maintaining corporate control over how equity is represented and traded.

The CFTC and the Future of Collateral

While the SEC governs the security itself, the CFTC is addressing the operational plumbing required to support these markets. On September 19, the CFTC released updated FAQs detailing how registrants can utilize blockchain for recordkeeping and how customer funds can be invested in tokenized assets.

CFTC Chair Michael Selig has been vocal about the necessity of this shift. In his address to the U.S. Treasury Market Conference, Selig emphasized that regulators cannot merely "modernize yesterday’s markets." Instead, the agency is actively preparing for "mass tokenization" by tailoring legacy frameworks to accommodate DLT and artificial intelligence. Selig argued that tokenized RWAs could lead to more dynamic liquidity and resilient market structures, particularly through the use of stablecoins for near-instantaneous settlement.

Implications: Is the Market Ready for 24/7 Trading?

The move toward round-the-clock trading is not without significant detractors and technical challenges. During the September 17 SEC roundtable, participants expressed "ambivalence" regarding the shift. Market makers and institutional participants raised concerns about:

  1. Thinner Liquidity: Overnight trading sessions may suffer from reduced participation, leading to thinner order books and more frequent price slippage.
  2. Increased Volatility: The absence of human oversight during late-night hours could exacerbate volatility, requiring a heavier reliance on automated trading algorithms and AI-driven risk management.
  3. Back-Office Compression: Current financial systems rely on end-of-day reconciliation. Moving to a 24/7 model necessitates an entirely new architecture for clearing and settlement that does not require "down-time" for balance sheet updates.

Despite these concerns, regulators point to the foreign exchange (FX) markets and the global crypto ecosystem as proof of concept. Foreign exchange markets have functioned on a 24/5 or 24/7 basis for decades, and the persistent nature of crypto markets demonstrates a clear consumer demand for non-stop trading access.

The CFTC, however, remains measured. Chair Selig noted that while digital assets and precious metals are well-suited for 24/7 environments, agricultural and energy derivatives may not be, due to the nature of their underlying physical supply chains. The regulator’s stance is one of "tailored implementation" rather than a blanket mandate.

The Role of Artificial Intelligence

As markets transition to extended hours, the role of AI is expected to transition from an auxiliary tool to a primary driver of market stability. With fewer human traders monitoring overnight sessions, algorithmic systems will be tasked with identifying anomalies and maintaining order flow. The integration of AI into payment rails and settlement systems—as suggested by recent industry standards like BRC-166—will likely be a prerequisite for the success of 24/7 stock trading.

Conclusion: A Decade of Transformation

The partnership between the NYSE and Blockchain.com, supported by the evolving regulatory posture of the SEC and CFTC, represents the vanguard of a new era for financial markets. The consensus among policymakers is that the next decade will witness a more profound transformation in market structure than the previous several decades combined.

As the U.S. financial system prepares to integrate tokenized securities, the focus will remain on whether these new, automated, and hyper-connected systems can provide the same level of security and investor protection that characterized the traditional, regulated markets of the 20th century. While the transition will undoubtedly involve technical friction and regulatory debates, the commitment from the world’s largest exchange suggests that the shift toward a digital, always-on financial infrastructure is no longer a matter of "if," but "how."

September 25, 2026 0 comment
0 FacebookTwitterPinterestEmail
Blockchain Technology

MoonPay Acquires North Capital in $60 Million All-Stock Deal to Expand Into Tokenized Securities and Real-World Assets

by admin September 25, 2026
written by admin

Crypto payments infrastructure provider MoonPay has reached a definitive agreement to acquire North Capital, a prominent regulated digital securities and private capital marketplace infrastructure firm, in an all-stock transaction valued at upwards of $60 million, according to industry reports and regulatory disclosures. Subject to customary regulatory reviews and approvals, the strategic buyout marks a pivotal milestone for MoonPay as the company aggressively transitions from its core crypto-fiat on-ramp services into the burgeoning institutional ecosystem of tokenized assets and real-world asset (RWA) digitization.

By absorbing North Capital’s sophisticated compliance, brokerage, and alternative trading infrastructure, MoonPay aims to bridge the gap between traditional web3 payment rails and highly regulated financial securities markets. The deal highlights a broader, industry-wide race among fintech heavyweights to capture market share in the rapidly expanding tokenization sector, where traditional financial instruments—ranging from corporate debt and private equity to real estate and commercial paper—are increasingly represented as digital tokens on distributed ledger networks.

Overview of the Transaction and Strategic Rationales

Under the terms of the agreement, MoonPay will acquire 100% of North Capital in a transaction structured entirely through stock. While initial reports peg the valuation at over $60 million, the final economic value will fluctuate depending on market conditions, the valuation of MoonPay’s equity, and the successful completion of regulatory milestones across multiple jurisdictions.

For MoonPay, which built its reputation as a leading consumer-facing gateway allowing users to purchase cryptocurrencies via credit cards, Apple Pay, and bank transfers, the acquisition represents a calculated pivot toward institutional-grade infrastructure. Over the past several years, consumer crypto volumes have faced cyclical volatility, prompting firms to diversify their business models. By integrating North Capital, MoonPay instantly equips itself with a fully compliant, SEC-registered suite of institutional tools.

North Capital brings a comprehensive regulatory and technological stack to the partnership. The firm operates the PPEX Alternative Trading System (ATS), a federally regulated venue that facilitates the secondary trading of private and exempt securities. To date, PPEX boasts a roster of more than 1,250 eligible securities and has cumulatively supported over $8.7 billion in transaction volume. Furthermore, North Capital holds vital regulatory registrations, including broker-dealer licenses with the Financial Industry Regulatory Authority (FINRA), transfer agent credentials, and registered investment advisory (RIA) capabilities.

Integrating these entities into MoonPay’s overarching platform allows the combined enterprise to offer end-to-end tokenized asset lifecycle management. Issuers can now leverage MoonPay’s global payment infrastructure to collect capital, utilize North Capital’s legal and technical exemptions to issue digital securities, and subsequently list those assets on a compliant secondary marketplace.

Background and Evolution of North Capital in Private Markets

MoonPay buys North Capital, including ATS for tokenized securities

Founded with the mission to democratize and streamline private capital formation, North Capital established itself as a pioneer in utilizing regulatory exemptions—such as Regulation D, Regulation A+, and Regulation CF—to help emerging companies raise capital efficiently from both accredited and retail investors.

The firm’s technological evolution centered heavily on the integration of blockchain solutions into traditional financial workflows. Recognizing that private securities have historically suffered from structural illiquidity, prolonged settlement times, and fragmented order books, North Capital invested heavily in developing programmatic compliance layers and automated issuance protocols.

A crown jewel in North Capital’s technological arsenal is the PPEX ATS. Unlike public stock exchanges like the New York Stock Exchange or NASDAQ, private markets are notoriously decentralized, with buyers and sellers often siloed within disparate private networks, broker-dealers, and online funding portals. PPEX was engineered to solve this friction by providing a centralized framework where multiple broker-dealers and issuers could plug in, share liquidity, and execute secondary trades of private company shares, real estate funds, and tokenized alternative assets within a rigorously regulated environment.

The Genesis of Agora and Cross-Venue Liquidity Networks

One of the most profound operational developments involving North Capital prior to the acquisition was its collaboration with tZERO, another heavyweight in the digital securities landscape. Together, North Capital and tZERO launched Agora, an innovative inter-ATS routing network designed to link disparate alternative trading systems.

Historically, liquidity fragmentation has stood as the single greatest impediment to the growth of tokenized and private securities. When an investor purchases a tokenized real estate equity share on Platform A, that asset typically cannot be easily discovered, bid upon, or settled by an investor participating exclusively on Platform B. Agora was built to break down these institutional walls.

The network connects multiple ATS venues, enabling qualified institutional participants to discover liquidity and route orders seamlessly across disparate platforms without necessitating redundant onboarding or fragmented custody arrangements. The system achieved a major operational milestone in July, successfully executing its first live routed order among institutional participants.

However, the acquisition of North Capital by MoonPay introduces complex governance and competitive dynamics regarding Agora’s future. Agora was originally founded as a collaborative, neutral utility jointly spearheaded by independent market operators. With North Capital now falling under the umbrella of MoonPay—a vertically integrated fintech giant that also controls proprietary payment rails and transaction routing technology—questions naturally arise among industry observers regarding how neutrality will be maintained. Competitors and market participants will be watching closely to see whether Agora remains an open, multi-party utility or if its governance structures evolve to reflect the strategic commercial interests of its new parent company.

Regulatory Compliance and the Regulatory Landscape for Tokenized Assets

MoonPay buys North Capital, including ATS for tokenized securities

The convergence of decentralized finance (DeFi) and traditional securities regulation has long been fraught with legal uncertainty. Regulators globally, and most notably the U.S. Securities and Exchange Commission (SEC), have maintained a strict stance that digital tokens representing ownership interests in underlying assets or corporate entities constitute securities, regardless of whether they are issued on a public blockchain or a private ledger.

By acquiring a licensed broker-dealer and ATS operator, MoonPay is effectively insulating its operations within a compliant, regulated perimeter. Rather than operating in the regulatory grey areas that historically characterized early crypto ventures, MoonPay is signaling to institutional investors, venture capital funds, and traditional financial institutions that its upcoming tokenization products will adhere strictly to existing securities laws.

This approach aligns with a broader industry trend where fintech unicorns seek out regulated entities to acquire compliance charters rather than attempting to build them from scratch. Obtaining broker-dealer status and transfer agent registrations can take years and require millions of dollars in legal overhead. For MoonPay, spending upward of $60 million in stock to instantly acquire a turnkey regulatory apparatus represents an efficient allocation of capital in a fiercely competitive market.

Industry Implications and Future Outlook

The acquisition of North Capital by MoonPay carries far-reaching implications for the fintech, cryptocurrency, and capital markets sectors.

First, it accelerates the mainstream adoption of real-world asset tokenization. Financial institutions ranging from BlackRock to JPMorgan have repeatedly emphasized that the tokenization of traditional assets represents the next structural evolution of global finance. By combining MoonPay’s frictionless global payment and fiat-to-crypto onboarding infrastructure with North Capital’s institutional issuance and trading capabilities, the merged entity is uniquely positioned to capture massive inflows as corporations, funds, and governments tokenize debt instruments, commodities, and equity.

Second, the deal underscores the ongoing consolidation within the digital asset infrastructure space. As regulatory scrutiny tightens globally, smaller compliance-heavy startups find themselves needing deep-pocketed partners to scale operations, while larger consumer-facing crypto firms urgently require B2B revenue streams and institutional-grade compliance frameworks to survive market cycles.

Finally, the transaction sets the stage for a new wave of competition among vertically integrated digital asset giants. As MoonPay expands its footprint from simple crypto transactions into investment advisory, transfer agency, and alternative trading systems, it will increasingly compete directly with both traditional prime brokers and native digital asset custodians.

As regulatory approvals are processed and the integration of North Capital’s team and technology stack gets underway, the market will monitor how successfully MoonPay can harmonize its consumer-centric brand identity with the solemn, highly regulated world of institutional securities trading. If executed effectively, the $60 million acquisition could well be remembered as the strategic catalyst that propelled MoonPay from a crypto payments utility into a cornerstone of the future global financial market infrastructure.

September 25, 2026 0 comment
0 FacebookTwitterPinterestEmail
Blockchain Technology

TechCrunch Disrupt 2026 Countdown: Final 24 Hours to Secure Early Registration Discounts and Up to $200 in Savings

by admin September 25, 2026
written by admin

The technology industry is preparing for its premier annual gathering as the final 24 hours of early-bird pricing for TechCrunch Disrupt 2026 draw to a close. Founders, investors, enterprise operators, and startup executives have until midnight to secure registration discounts of up to $200 for the upcoming conference, scheduled to take place from October 13 to October 15, 2026, at Moscone West in San Francisco.

Beyond individual ticket savings, event organizers have introduced promotional incentives designed to encourage team attendance, including a 50% discount on a second pass of the same category and group discounts of up to 30% for teams of four or more. As the tech ecosystem navigates an evolving macroeconomic climate characterized by cautious venture capital deployment and rapid artificial intelligence integration, industry participants are increasingly looking to large-scale summits to accelerate product development cycles, secure capital, and forge strategic partnerships.

Background Context and Event Evolution

TechCrunch Disrupt has long served as a bellwether for the global startup ecosystem. Established more than a decade ago, the conference has evolved from a nascent forum for digital entrepreneurs into a massive international convention. Historically, the event has acted as a launchpad for some of the world’s most recognizable technology companies, offering early-stage startups a global stage through its signature Startup Battlefield pitch competition.

Last 24 hours to save up to $200 on TechCrunch Disrupt 2026. Reason 5 of 5 to attend: Momentum

The 2026 installment at Moscone West arrives at a critical juncture for the technology sector. Following years of post-pandemic market corrections, inflated valuations adjustments, and workforce rationalization, founders are operating under heightened pressure to demonstrate sustainable unit economics, clear paths to profitability, and tangible technological utility. Concurrently, venture capitalists have adjusted their deployment strategies, prioritizing rigorous due diligence over rapid capital allocation.

Against this backdrop, Disrupt 2026 aims to bridge the gap between innovators and financiers. The venue will host more than 10,000 attendees, creating a high-density networking environment where months of independent research, digital correspondence, and preliminary negotiations can be condensed into three days of face-to-face engagement.

Structuring the Three-Day Experience: Momentum and Efficiency

The organizing framework of TechCrunch Disrupt 2026 is intentionally built around the concept of momentum—the idea that business breakthroughs rarely occur in isolation, but rather through the accumulation of targeted conversations, market intelligence, and collaborative decision-making.

Modern enterprise development requires founders and executives to simultaneously track shifting competitor landscapes, evaluate emerging technology stacks, identify prospective clients, and navigate fundraising landscapes. Accomplishing these tasks through traditional channels often stretches across months of fragmented video calls and isolated market research. Disrupt attempts to compress this timeline by placing key industry stakeholders under a single roof.

Last 24 hours to save up to $200 on TechCrunch Disrupt 2026. Reason 5 of 5 to attend: Momentum

The conference agenda features more than 250 interactive sessions, keynote addresses, and workshops distributed across six specialized industry stages. These stages are curated to dissect specific verticals—ranging from generative artificial intelligence and enterprise SaaS to climate tech, fintech, biotechnology, and hardware innovation. By embedding attendees directly within these sector-specific discussions, the event enables participants to transition seamlessly from theoretical market analysis on stage to direct, bilateral conversations with industry operators and investors on the exhibition floor.

Economic Implications and Strategic Value for Startups

For early-stage entrepreneurs, the financial investment required to attend major technology conferences must be weighed against tangible return on investment. The urgency surrounding the final 24 hours of ticket sales highlights the economic sensitivity of startup budgeting. Securing a registration discount of up to $200, paired with the 50% second-pass promotion, provides meaningful relief for bootstrapped teams and early-stage companies operating on lean operational runways.

Industry analysts emphasize that the true value of attending events like Disrupt extends far beyond passive listening. For founders preparing for a seed or Series A funding round, the conference offers unparalleled access to institutional venture capitalists, angel investors, and corporate venture arms who attend specifically to source proprietary deal flow. By engaging with these financial stakeholders in person, founders can test investor appetite for their underlying business models, refine their pitch narratives based on real-time feedback, and compress a fundraising timeline that might otherwise require months of cold outreach.

Furthermore, enterprise operators and corporate innovators utilize the conference to conduct competitive intelligence and vendor evaluation. As artificial intelligence fundamentally alters software architecture and enterprise workflows, decision-makers face mounting pressure to separate sustainable technological breakthroughs from market hype. The exhibition floor at Moscone West will showcase hundreds of early-stage startups demonstrating applied technologies, offering corporate buyers a comprehensive view of emerging software and hardware solutions.

Last 24 hours to save up to $200 on TechCrunch Disrupt 2026. Reason 5 of 5 to attend: Momentum

Chronology of the Final Countdown and Registration Details

The current registration window closes precisely at midnight, at which point standard ticket pricing structures will take effect. Event organizers have structured the final promotional push around a tiered discount model:

  • Individual Savings: Registrants purchasing passes before the midnight deadline save up to $200 off standard rates.
  • Companion Discount: Attendees who purchase one pass are eligible to acquire a second pass of the identical tier at a 50% discount.
  • Team Packages: Organizations registering groups of four or more individuals receive cumulative savings of up to 30%.

Prospective attendees can access ticketing portals and review detailed agenda breakdowns directly through the official TechCrunch Disrupt platform.

Broader Impact on the San Francisco Tech Economy

The return of TechCrunch Disrupt to Moscone West also underscores the ongoing economic revitalization of downtown San Francisco. As corporate events and tech conferences return to the city at pre-pandemic volumes, gatherings of this scale inject millions of dollars into the local hospitality, tourism, and service sectors. City officials and business leaders view anchor events like Disrupt as critical drivers of local economic activity, signaling San Francisco’s enduring status as the global epicenter of technology innovation and venture capital.

As the final hours of early registration tick away, the technology community faces a clear operational decision: commit to a concentrated period of high-impact networking, or navigate the remainder of the fiscal year through traditional, decentralized channels. For those seeking to accelerate product development, close funding rounds, and establish critical industry alliances before the close of 2026, the deadline represents the final opportunity to secure admission at subsidized rates.

September 25, 2026 0 comment
0 FacebookTwitterPinterestEmail
Decentralized Finance (DeFi)

Crypto Card Volume in 2026: $1.1 Billion a Month, and What Is Inside It

by admin September 25, 2026
written by admin

At 16:49:48 UTC on Friday, August 28, 2026, a Solana-based wallet—funded just three hours prior with 1.79 SOL via a bridge from Ethereum—executed the first of over 21,000 transactions that would systematically drain thousands of user accounts belonging to Avici, a prominent Solana-focused neobank. By the time the incident concluded, 1,685 users had seen their balances liquidated, totaling $500,859.22 in losses. This breach was not a result of compromised private keys or standard phishing; rather, it exploited a critical vulnerability in a shared smart contract architecture used by Avici and several other programs within the burgeoning self-custodial crypto card market.

The incident highlights a growing tension in the financial technology sector: the gap between the marketing promise of "non-custodial" finance and the technical reality of how these assets are governed. While Avici’s terms of service explicitly stated that the company would not hold custody of user collateral, the underlying smart contract infrastructure—managed by the card-issuing company Rain—contained an authorization flaw that allowed an attacker to bypass security checks. This event has forced a broader audit of the $1.1 billion monthly crypto card industry, raising questions about transparency, issuer reliance, and the legal status of digital assets in the event of platform failure.

The Anatomy of the August 28 Breach

The attack vector was surgically precise. The perpetrator’s wallet, identified on-chain as FVNFzqAny8spWdPmYw6RQ9TkYa29ueFFiqCFD1gQnCEj, targeted a vulnerability in the signature-verification instruction of a Rain-controlled Solana program. By manipulating signature and message offsets, the attacker effectively tricked the program into accepting a single signature as the required dual-authorization for administrative actions. Once the attacker granted themselves "Collateral Admin" status, they were able to initiate asset withdrawals from individual user accounts.

The chronology of the event reveals the speed at which modern on-chain exploits unfold. The initial exploit began at 16:49:48 UTC, and the final malicious transaction was recorded at 19:18:52 UTC. In the interim, the attacker managed to successfully process approximately 17,500 transactions. By 19:03:18 UTC, while the drain was still in progress, the attacker initiated a series of deBridge orders to move approximately 1.1 million USDC from the Solana network to Ethereum. These funds were subsequently funneled into Tornado Cash in a standard "laddered" withdrawal pattern, effectively obscuring the trail of the stolen capital.

Rain’s response was rapid but highlighted the centralized nature of what is often marketed as decentralized infrastructure. The company patched the affected Solana programs between 19:18 and 19:43 UTC, mere minutes after the drain concluded. Following the patch, Rain and the affected programs, including Avici and Tria, committed to full refunds. While this prevented a public relations catastrophe, it underscored a reality that the industry rarely discusses: the "non-custodial" cardholder was ultimately saved by the corporate balance sheet of a venture-backed firm, not by the inherent security of the blockchain itself.

The State of the Crypto Card Market: $1.1 Billion and Counting

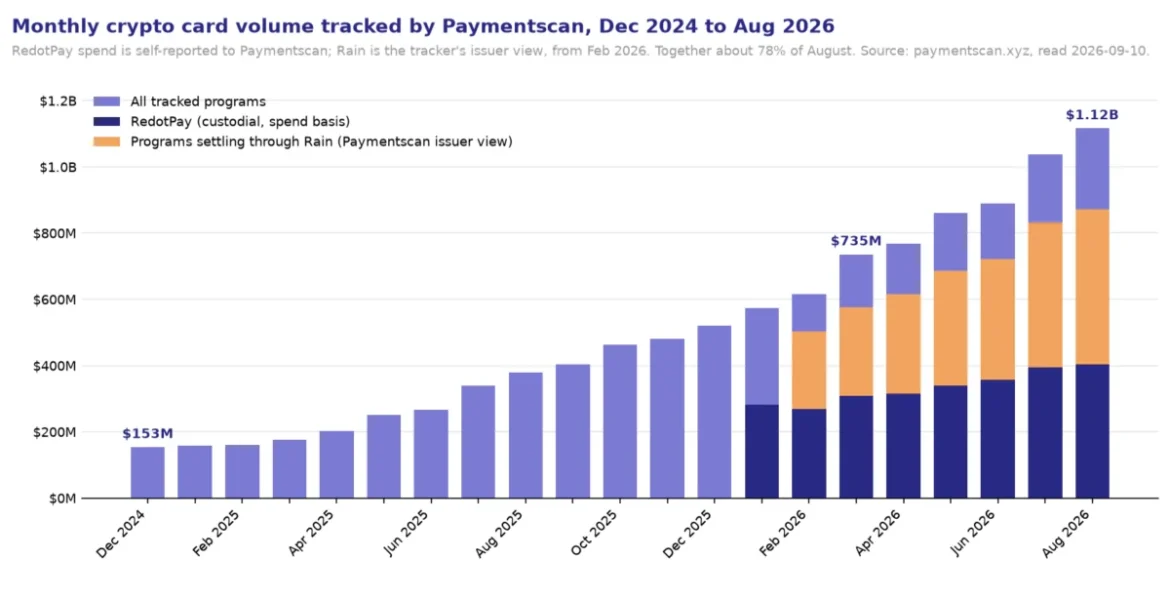
According to data from Paymentscan, the crypto card industry has seen explosive growth. As of August 2026, monthly transaction volume hit $1.116 billion across 11 million individual transactions and nearly 290,000 active addresses. This marks the second consecutive month that the sector has exceeded the billion-dollar milestone, following a steady climb from $153 million in December 2024.

However, these figures carry significant caveats. A substantial portion of this volume—nearly 42%—is routed through Rain, which acts as the infrastructure provider for numerous smaller programs. Furthermore, the reliance on self-reported data from major players like RedotPay makes it difficult to ascertain the true level of risk within the ecosystem. When adjusting for on-chain verifiable spend, the actual figures are closer to $545 million, representing a 55% increase since March 2026. This discrepancy highlights the lack of standardized reporting in the crypto payments space, where market share is often conflated with user activity.

Crypto Cards 2026: Who Holds the Money Before the Swipe

The Custody Spectrum: Five Models of Risk

To understand why some cards were vulnerable while others remained secure, one must look at the legal and technical "custody models" currently in operation. The industry generally falls into five distinct categories, ranging from total loss of ownership to true self-custody.

  1. Sold to the Operator: In this model, such as that employed by KAST, the user’s deposit is legally considered a sale of assets. The user no longer owns the cryptocurrency but instead holds a debt claim against the platform. In the event of a bankruptcy, these users are merely unsecured creditors.
  2. Held in Custody: Platforms like RedotPay and Revolut act as custodians. While they claim to hold assets for the user, these assets are often subject to general liens and may be reachable by the platform’s creditors during insolvency proceedings.
  3. Fiat Conversion: Exchange-based cards, such as those from Crypto.com or Kraken, often do not hold crypto on the card at all. Assets are converted to fiat at the moment of the transaction, and the fiat is held in regulated bank accounts. While this offers the most protection, it is dependent on the regulatory status of the bank, not the security of the blockchain.
  4. Program-Managed Smart Contracts: This was the model utilized by Avici and Tria. The collateral sits in a smart contract. While the user technically owns the assets, the "upgrade authority"—the power to change the rules of the contract—is often held by the program manager (in this case, Rain). The August breach occurred because this authority was centralized, not distributed.
  5. Direct Authorization Vaults: Gnosis Pay and Ether.fi Cash represent the most secure tier. Here, the user retains control over a smart contract (a "Safe") where funds remain until an authorization is explicitly signed. Even if the program manager fails, the user’s assets remain in their own vault, inaccessible to the provider.

The "Third National" Concentration Risk

A significant systemic risk identified in the 2026 data is the concentration of issuers. Seven major programs—KAST, Avici, Ether.fi, Plasma One, Solayer, Payy, and Tria—all name "Third National" as their card issuer. Investigations reveal that Third National is not a bank in the traditional sense, but a Puerto Rico-based money transmitter and a subsidiary of Signify Holdings (Rain).

This creates a "single point of failure" scenario. When an infrastructure provider like Rain faces a technical exploit, the impact is not isolated to one brand but ripples across the entire portfolio of programs that rely on their shared codebase. The August incident demonstrated that while the brands appear distinct to the consumer, they are fundamentally tethered to the same administrative keys and contract logic.

Regulatory Horizons and Future Implications

The industry is currently facing a dual challenge: increasing regulatory scrutiny and the natural consolidation of infrastructure. With the European Union’s Anti-Money Laundering Regulation (EU 2024/1624) set to take full effect in July 2027, the era of anonymous, no-KYC crypto cards is nearing an end. The new rules effectively ban anonymous prepaid cards loaded with crypto, forcing providers to either implement rigorous identity verification or face exclusion from EU merchant terminals.

For the self-custodial sector, the lessons of August 2026 are clear. "Non-custodial" is a marketing term that fails to describe the reality of governance. The security of a card program is not merely about whether the user holds their private keys, but about who holds the upgrade keys to the smart contracts, whether those contracts have been audited for the specific version currently in production, and how the program is financed.

As the industry matures, the survivors will likely be those who can provide the highest degree of technical transparency. Ether.fi and Gnosis Pay have set a new standard by publishing contract addresses and governance modules, allowing users to verify for themselves where their money sits. In contrast, programs that hide behind opaque "licensed partners" and "proprietary infrastructure" remain inherently vulnerable.

Ultimately, the August exploit serves as a stark reminder that while the blockchain provides a ledger of truth, the surrounding financial infrastructure—the bridges, the issuers, and the administrative authorities—is only as robust as its weakest line of code. For the 1,685 users who were made whole, the experience was a fortunate reprieve. For the industry, it is a definitive call to move away from centralized "non-custodial" templates toward architectures that truly prioritize user sovereignty over administrative convenience.

September 25, 2026 0 comment
0 FacebookTwitterPinterestEmail
Cybersecurity & Hacking

U.S. Army Soldier Sentenced to Nearly Six Years in Prison for Massive AT&T and Snowflake Extortion Scheme

by admin September 25, 2026
written by admin

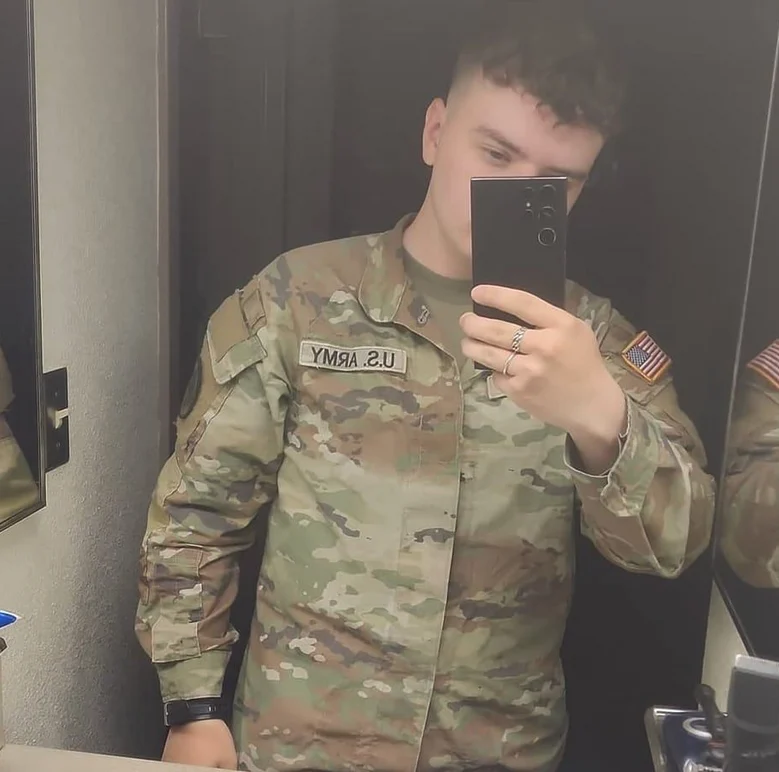
A federal court in Seattle has sentenced a 22-year-old active-duty U.S. Army soldier to 70 months in federal prison for orchestrating a sweeping international cybercrime and extortion campaign. Operating under the pseudonym “Kiberphant0m,” Cameron John Wagenius exploited unsecure cloud infrastructure to steal sensitive call and text metadata belonging to more than 100 million AT&T customers. In addition to his nearly six-year prison sentence, Wagenius was ordered to pay $294,978 in restitution to his victims, concluding a high-profile prosecution that exposed critical vulnerabilities in corporate data storage and highlighted the growing threat of insider actors within military ranks.

Wagenius, who was stationed at a U.S. Army base in South Korea at the time of the offenses, utilized his secret security clearance and technical acumen to coordinate cyberattacks against major telecommunications and data storage entities worldwide. Federal prosecutors detailed that Wagenius, alongside a network of international co-conspirators, weaponized compromised credentials from cloud data storage provider Snowflake to siphon proprietary corporate data. Despite the massive scale of the data breaches—which impacted dozens of global telecom providers, including Verizon’s Push-to-Talk division—investigators revealed that Wagenius profited remarkably little from his illicit operations, netting approximately $1,500 in direct sales of stolen information before federal law enforcement intervened.

The Chronology of an International Cyber Investigation

The unraveling of the Kiberphant0m persona represents a collaborative triumph for multi-agency federal law enforcement. The investigative timeline illustrates the rapid escalation of a complex digital threat that transitioned from an anonymous forum boast to an active national security investigation.

In October 2024, the cybercriminal operating as Kiberphant0m took to public dark-web and surface-web hacker forums to openly brag about infiltrating cloud environments and extracting call and text metadata—including source numbers, destination numbers, timestamps, and call durations—for tens of millions of AT&T subscribers. During this period, the extortion group engaged in aggressive public shaming and corporate extortion, threatening to leak sensitive internal archives unless corporate targets met substantial cryptocurrency ransom demands.

By late November 2024, cybersecurity journalism outlet KrebsOnSecurity published intelligence suggesting that the actor behind the Kiberphant0m moniker was likely an American military service member stationed in South Korea. This public revelation accelerated pressure on defense and federal investigators.

Less than a month after the initial public reporting, in December 2024, federal authorities arrested Wagenius. He was formally charged in dual federal indictments, moving swiftly through the judicial process to plead guilty to all counts. Throughout the proceedings, prosecutors noted that Wagenius cooperated extensively with investigators, though subsequent behavior while incarcerated would complicate his pre-sentencing assessment.

By August 2026, international co-conspirators faced similar judicial reckoning. Conor Riley Moucka, a Canadian national known online as “Judische,” pleaded guilty to his role in the Snowflake extortion scheme. Meanwhile, co-conspirator Kenneth Schuchman—a 28-year-old Washington resident with a prior federal conviction for operating the Satori Internet-of-Things botnet in 2019—faced separate federal charges for assisting in the extortion campaigns. Another co-conspirator, American national John Erin Binns, remained wanted internationally, linked to historical major data breaches including a 2021 T-Mobile network intrusion that exposed the records of 76 million customers.

The Mechanics of the Snowflake Breaches and Telecom Extortion

The backbone of the Kiberphant0m enterprise relied on exploiting third-party cloud data repositories rather than breaching corporate perimeters directly. Companies utilizing Snowflake’s cloud storage services frequently fell victim to credential-stuffing attacks and account takeovers due to a widespread failure among corporate clients to mandate multi-factor authentication (MFA) across all administrative and user accounts.

Once inside these vulnerable cloud environments, Wagenius and his associates harvested massive repositories of structured telecommunications data. AT&T bore the brunt of the exposure, with the metadata of over 100 million customers compromised. In an escalation of pressure tactics after AT&T reportedly paid a $370,000 Bitcoin ransom to the broader extortion collective, Kiberphant0m engaged in re-extortion efforts.

Seeking to maximize leverage, the hacker posted datasets online that allegedly included call logs belonging to prominent political figures, including then-President-elect Donald Trump and then-Vice President Kamala Harris. Furthermore, Kiberphant0m threatened to release classified or sensitive schematics allegedly sourced from the U.S. National Security Agency (NSA), crossing the threshold from corporate cybercrime into potential national security espionage.

The Insider Threat Dimension and Multi-Agency Response

The involvement of an active-duty U.S. Army soldier with a secret security clearance alarmed federal defense and intelligence agencies. Paul Russell, the resident agent in charge at the Defense Criminal Investigative Service (DCIS)—the criminal investigative arm of the Department of Defense Office of Inspector General—emphasized the atypical nature of the case.

“We don’t often get leads where there’s an active-duty soldier with a secret clearance who’s creating hacking tools and trafficking in data,” Russell stated. “That doesn’t happen every day, and so when that hits it really spins all of our partner organizations up. It was very serious from jump street, just because it was unique, it was an insider threat, and we weren’t sure what we were dealing with.”

The investigation required a coordinated, cross-jurisdictional task force comprising DCIS, the Federal Bureau of Investigation (FBI), the Army Criminal Investigation Division (CID), and the U.S. Secret Service. The convergence of military counterintelligence and civilian federal cybercrime divisions underscored the federal government’s zero-tolerance stance on service members leveraging classified access or military infrastructure to engage in transnational cybercrime.

Post-Arrest Misconduct and Bureau of Prisons Security Concerns

While Wagenius earned some leniency in prosecutorial sentencing memos for his immediate guilty plea and subsequent cooperation, his conduct while detained awaiting sentencing introduced fresh legal complications. Court documents filed in September by federal prosecutors in Seattle revealed that Wagenius attempted to probe the computer network security of the Bureau of Prisons (BOP) from inside a federal detention facility.

According to BOP records cited in the government’s sentencing memorandum, Wagenius utilized unauthorized access to other inmates’ email accounts in September 2025. Through these proxies, he prompted commercial artificial intelligence tools to bypass standard safety guardrails via prompt injection techniques. Wagenius explicitly requested specific Common Vulnerabilities and Exposures (CVEs) related to Windows 10 Enterprise privilege escalation, step-by-step instructions for exploiting CVE-2023-45208 (a command injection vulnerability in D-Link networking hardware), and methods for constructing makeshift antennas using commissary items to extend radio reception within a correctional facility. He also researched instructions pertaining to prison escape methodologies.

When confronted by authorities regarding these queries, Wagenius claimed he was merely researching system vulnerabilities to provide defensive intelligence back to the BOP. Prosecutors maintained there was no evidence that Wagenius successfully deployed or executed any exploits against BOP digital infrastructure, but the attempts demonstrated a persistent compulsion toward technical exploitation even while incarcerated.

Broader Implications for Corporate Cybersecurity and Cloud Hygiene

The sentencing of Cameron Wagenius closes a significant chapter in one of the most disruptive cyber extortion sprees in recent corporate history, yet the broader implications for cybersecurity architecture remain profound. The Snowflake-related extortions served as a watershed moment for cloud security, prompting enterprise vendors to universally enforce multi-factor authentication and re-evaluate third-party access controls.

Security analysts point out that the case underscores the severe vulnerabilities introduced by supply-chain dependencies. Major telecommunications providers often outsource data analytics and storage to third-party cloud ecosystems, creating centralized honeypots that, if left inadequately protected, expose millions of consumer records through a single point of failure.

Furthermore, the integration of generative AI tools by incarcerated hackers highlights an emerging frontier in digital security. The ease with which technical exploits and vulnerability bypass instructions can be extracted from commercial AI models through prompt engineering presents ongoing challenges for correctional authorities and software developers alike.

As Wagenius begins his 70-month federal prison term, federal agencies continue to pursue remaining co-conspirators across international borders. The case stands as a stark reminder of the convergence between modern cloud vulnerabilities, transnational extortion syndicates, and the complex challenges of managing insider threats within the United States military.

September 25, 2026 0 comment
0 FacebookTwitterPinterestEmail
Cybersecurity & Hacking

GitHub Actions Security Breach Resurfaces as Compromised Repositories Briefly Return to Public Access

by admin September 25, 2026
written by admin

The cybersecurity community is once again scrutinizing the resilience of software supply chain security after two GitHub Actions—previously flagged as malicious—briefly reappeared in the public domain this month. This incident, which occurred on September 16, 2026, highlights a critical vulnerability in how automated CI/CD pipelines handle versioning and repository integrity. Despite being initially neutralized following the widespread May 2026 Mini Shai-Hulud campaign, the sudden reactivation of these repositories allowed the dormant malicious payloads to once again become accessible to any automated workflow relying on them.

Chronology of the Incident

The origins of this security failure trace back to May 18, 2026, when threat actors successfully compromised several GitHub Actions. These tools, designed for routine repository housekeeping—such as closing stale issues, managing comment threads, and updating automated bot responses—were weaponized to exfiltrate sensitive credentials from CI/CD environments.

The malicious code remained embedded within the repositories, waiting for execution. By linking the exfiltration infrastructure to the domain "t.m-kosche[.]com," researchers identified the attackers as part of the "Mini Shai-Hulud" cluster. This same cluster was concurrently linked to malicious activity involving the @antv ecosystem in the npm package repository, signaling a coordinated effort to penetrate developer workflows through multiple vectors.

Compromised GitHub Actions Came Back Online and Resumed Executing Mini Shai-Hulud Malware

Following the discovery of the malicious payload, GitHub moved to disable the affected repositories, effectively halting the immediate threat. However, the situation took a concerning turn on September 16, 2026. Between 11:09 a.m. and 6:16 p.m. GMT+2, the repositories were mysteriously re-enabled and became accessible to the public once more.

Because the release tags within these repositories had not been scrubbed or updated to remove the malicious content, the repositories essentially "resumed" their compromised state the moment they were made public. Any CI/CD pipeline configured to reference these actions via version tags—such as "v1" or "latest"—automatically pulled the malicious code upon the next execution cycle, effectively re-infecting the downstream projects without any new action required from the original threat actors.

The Mechanism of the Supply Chain Attack

The vulnerability hinges on the common practice of using mutable tags in GitHub Actions workflows. When a developer references an action using a tag like "v1.0," the system fetches the current state of that tag at the time of execution. If the owner of that repository has updated the tag—or, in this case, if the repository is restored to a state containing a malicious payload—the user’s pipeline pulls that code without validation.

Socket researcher Karlo Zanki, who documented the reappearance, noted that the malicious payload was never removed from the codebases during the period they were disabled. Consequently, the threat remained dormant but ready to fire. "No new code was published and no configuration was changed," Zanki observed. "This incident shows that a mutable tag can be compromised, contained, and then reactivated without any change to your own workflow file."

Compromised GitHub Actions Came Back Online and Resumed Executing Mini Shai-Hulud Malware

This creates a "time-bomb" scenario. Organizations that believed they were protected because the malicious repositories had been taken offline were inadvertently exposed to the same threat the moment the platform’s access control settings were toggled. This underscores the fragility of relying on external, third-party infrastructure for mission-critical automation.

Broader Implications for CI/CD Security

The Mini Shai-Hulud incident is emblematic of a broader shift in threat actor strategy. Rather than attempting to break into well-defended production servers, adversaries are increasingly focusing on the "soft underbelly" of the software development lifecycle: the CI/CD pipeline. By compromising tools that developers trust and execute automatically, attackers can achieve high-impact breaches with minimal effort.

The incident carries significant implications for DevSecOps practices:

  1. The Failure of Implicit Trust: Developers often trust GitHub Actions published by well-known or popular sources. This incident proves that even previously reputable actions can be hijacked and that containment measures taken by platform providers may not be permanent or sufficient if the underlying malicious artifacts are not purged.
  2. The Necessity of Pinning: The only robust defense against this type of supply chain vulnerability is SHA pinning. By referencing a specific, immutable commit SHA rather than a mutable version tag, developers ensure that their workflows execute the exact code they have audited. If an attacker pushes a new version or restores a compromised one, a SHA-pinned workflow will continue to use the known-good version, protecting the pipeline from unauthorized changes.
  3. Governance of Automated Workflows: Organizations must maintain an inventory of all third-party actions used in their pipelines. Automated tools should be used to scan for updates, check for changes in repository ownership, and enforce policies that forbid the use of mutable tags in production environments.

Official Responses and Mitigation Strategies

While GitHub has since re-disabled the repositories, displaying the standard notice regarding violations of the platform’s Terms of Service, the incident serves as a stark reminder of the limitations of reactive platform-level security.

Compromised GitHub Actions Came Back Online and Resumed Executing Mini Shai-Hulud Malware

Security experts suggest that developers should perform an immediate audit of their GitHub Action workflows. Specifically, they recommend:

  • Switching to SHA Pinning: Immediately replace all version tags (e.g., actions/checkout@v4) with the corresponding commit hash (e.g., actions/checkout@1d96c77...).
  • Dependency Auditing: Use tools that track the provenance of third-party actions and alert developers to changes in the underlying repository source.
  • Pipeline Isolation: Ensure that CI/CD environments operate with the principle of least privilege. Sensitive credentials should not be exposed to every action in a workflow, particularly those that do not strictly require them.

The fact that these actions were compromised for months, disabled, and then briefly restored without any remediation of the malicious payload indicates a gap in the cleanup process following such incidents. Philipp Burckhardt, head of threat intelligence at Socket, previously emphasized that the Mini Shai-Hulud activity represents a sophisticated, persistent threat cluster. The ability of these actors to leverage the platform’s own mechanics to keep their payload active—even after platform intervention—is a development that should alarm security teams across the industry.

Conclusion

The September 2026 resurgence of the Mini Shai-Hulud GitHub Actions serves as a definitive case study in the dangers of mutable dependencies. In a modern software ecosystem where code is increasingly assembled from third-party building blocks, the security of the pipeline is just as important as the security of the product itself.

As organizations continue to embrace automation to increase development velocity, they must also embrace the inherent risks that come with it. The "set it and forget it" mentality regarding CI/CD configuration is no longer sustainable. By adopting stricter dependency management practices—most notably the universal adoption of SHA pinning—the developer community can insulate itself against the next iteration of supply chain attacks. The incident serves as a sobering reminder that in the world of software security, trust is not a strategy; verification is the only viable path forward. The brief window of exposure in September may not have led to widespread catastrophe, but it has provided a clear warning: the threat actors are waiting for the next accidental reactivation, and the only way to stay secure is to assume that any external dependency can, and eventually will, be compromised.

September 25, 2026 0 comment
0 FacebookTwitterPinterestEmail
Cybersecurity & Hacking

Kiteworks Urges Global Customers to Temporarily Shut Down Servers Amid Imminent Cyberthreat Warning

by admin September 25, 2026
written by admin

Secure file-sharing and managed file transfer (MFT) software provider Kiteworks has issued an urgent, worldwide advisory instructing its enterprise and government customers to temporarily take their servers offline for a six-hour window. The directive follows what the company describes as highly credible threat intelligence received directly from law enforcement and federal security agencies, warning of a potentially imminent, large-scale cyberattack targeting the platform.

The precautionary measure, which spans multiple global time zones, highlights the acute vulnerabilities facing modern enterprise file-transfer ecosystems. Because these platforms routinely process, store, and transmit massive volumes of highly confidential intellectual property, financial records, and classified government documents, they remain prime real estate for sophisticated, financially motivated cybercriminal syndicates.

The Emergency Advisory and Global Shutdown Windows

According to communications sent to clients by Kiteworks Chief Information Security Officer Frank Balonis—first brought to public attention by German technology publication Heise—the directive is sweeping and non-negotiable in its urgency. The company has strongly advised administrators to initiate server shutdowns ahead of the official regional windows, urging precautions even for deployments that are not directly exposed or accessible via the public internet.

The coordinated global shutdown required staggered operational pauses tailored to regional time zones to minimize disruption while maximizing defense efficacy:

  • Central Europe: Systems were directed to go offline between 4:00 a.m. and 10:00 a.m. local time on Saturday, September 26.
  • North America (Eastern Time): The operational window spanned from 10:00 p.m. Friday to 4:00 a.m. Saturday.
  • Australia and Asia-Pacific: Timelines were structured correspondingly to cover the same rotational weekend block, extending through Australian Eastern Standard Time (AEST).

In statements provided to cybersecurity publication BleepingComputer, Kiteworks confirmed that the warnings originated from authoritative federal channels. "Kiteworks received credible threat intelligence from federal intelligence authorities indicating that a threat actor may attempt to target some Kiteworks systems for customers," a company spokesperson stated. "Out of an abundance of caution, we notified customers directly and recommended a precautionary shutdown window while we and our law enforcement partners work through the matter."

Crucially, Kiteworks emphasized that the advisory is entirely preventative. The firm confirmed that it has received no reports of successful breaches, active data exfiltration, or unauthorized access linked to this specific warning. Furthermore, the company noted that all previously cataloged and disclosed vulnerabilities have already been patched in software release 9.5.1, urging all clients to ensure they are operating on this latest version.

Zero-Day Speculation and the Threat Landscape

While official company statements frame the shutdown as a preventative posture based on external intelligence, customer support inquiries reviewed by Heise indicate that the emergency steps are designed to mitigate potential zero-day exploits—vulnerabilities previously unknown to the vendor and therefore lacking a pre-existing software patch.

When contacted by journalists for clarification, Kiteworks support representatives reportedly acknowledged that the core motivation behind the offline mandate was protection against unpatched or zero-day attack vectors. This distinction is vital in the modern cybersecurity paradigm. Zero-day attacks represent the holy grail for advanced persistent threat (APT) groups and financially driven extortion gangs, as they bypass standard defense-in-depth measures and signature-based detection systems entirely.

Kiteworks urges 6-hour server shutdown over potential zero-day attacks

The deployment of MFT and secure collaboration platforms as vectors for enterprise compromise is a well-documented playbook. Over the past several years, the cybersecurity community has watched in real-time as corporate file-sharing gateways transformed into critical infrastructure choke points.

A Historical Precedent: The Rise of Extortion via Managed File Transfer

The current apprehension surrounding Kiteworks is heavily informed by past high-profile campaigns that disrupted global commerce through software supply chain and third-party file-transfer vulnerabilities. The architecture of platforms like Kiteworks makes them uniquely lucrative targets. By centralizing large-scale data transfers into a single application environment, a successful breach allows malicious actors to harvest terabytes of sensitive corporate data in a single sweep, bypassing the need to navigate complex internal enterprise networks.

Prominent extortion syndicates—most notably the Clop ransomware and data-theft gang (also tracked as TA505)—have repeatedly weaponized enterprise file-transfer gateways. The historical record of similar zero-day mass-exploitation campaigns reads like a timeline of modern enterprise security crises:

  • Accellion FTA (2020–2021): Aging legacy file-transfer appliances maintained by Accellion were exploited using zero-day vulnerabilities, leading to massive data thefts across hundreds of high-profile global corporations, universities, and government entities.
  • GoAnywhere MFT (Early 2023): Fortra’s GoAnywhere managed file transfer platform suffered a zero-day remote code execution flaw that was aggressively exploited by the Clop gang to steal data from dozens of enterprise organizations before patches could be deployed.
  • MOVEit Transfer (Mid-2023): Perhaps the most disruptive campaign of its kind, the exploitation of a zero-day SQL injection vulnerability in Progress Software’s MOVEit Transfer platform impacted over 2,500 organizations and tens of millions of individuals worldwide, triggering widespread regulatory scrutiny and class-action litigation.
  • SolarWinds Serv-U and Cleo Incidents: Similar vulnerabilities in Serv-U FTP and Cleo file-movement tools have underscored the systemic risk inherent in software designed to move data securely across organizational perimeters.

The sheer scale of financial damage and reputational fallout from the MOVEit and GoAnywhere crises prompted extraordinary measures from Western governments. Notably, the U.S. Department of State established a reward program offering up to $10 million for actionable information linking the leadership or infrastructure of the Clop ransomware syndicate to a foreign government or state-sponsored protection.

Industry Implications and the Paradigm of Proactive Defense

Kiteworks’ decision to unilaterally advise a global shutdown based on law enforcement intelligence rather than an active incident marks an evolving maturity in vendor-customer communication during high-threat scenarios. Historically, software vendors have sometimes delayed disclosures or downplayed potential risks to protect brand reputation, occasionally resulting in threat actors beating defenders to the punch.

By acting preemptively—even at the cost of short-term operational downtime for its global client base—Kiteworks and its federal partners have signaled a shift toward hyper-vigilance. In an era where automated scanning tools allow threat actors to weaponize newly discovered code flaws within hours of publication, the traditional timeline of vulnerability disclosure, patch development, and deployment is often too slow to prevent initial compromise.

For enterprise security leaders, the incident serves as a stark reminder of the fragile nature of perimeter defenses. Security teams are increasingly required to practice "assume breach" methodologies and maintain rapid incident response playbooks capable of physically or logically isolating critical infrastructure components on a moment’s notice.

As the six-hour shutdown windows close across various international jurisdictions, attention shifts back to Kiteworks and federal law enforcement agencies to determine whether the intelligence-indicated attack vector materializes, or if the preemptive blackout successfully neutralized a potentially catastrophic cyber operation. Organizations utilizing managed file transfer solutions are advised to maintain heightened monitoring, verify adherence to the latest firmware and software patches (such as Kiteworks version 9.5.1), and review their emergency offline-isolation procedures to prepare for future threat intelligence alerts.

September 25, 2026 0 comment
0 FacebookTwitterPinterestEmail
Bitcoin & Altcoins

Ethereum Foundation to Host Annual Protocol Development AMA on September 16

by admin September 25, 2026
written by admin

Since January 2019, the Ethereum Foundation has maintained a transparent and consistent dialogue with the global developer community through its recurring Ask Me Anything (AMA) sessions on the r/ethereum subreddit. These forums serve as a critical bridge between the foundational research teams and the broader ecosystem, providing a platform for technical scrutiny, strategic roadmap discussions, and direct engagement. On September 16, the Foundation will continue this tradition, featuring researchers and developers from the Protocol cluster to address inquiries regarding the current and future state of the Ethereum network.

The upcoming session arrives at a pivotal juncture for Ethereum’s technical evolution. With the industry shifting focus toward long-term scalability and security enhancements, the AMA is expected to cover a wide array of sophisticated topics, including the implementation of the Glamsterdam hard fork, the narrowing scope of the Hegotá upgrade, and the ongoing structural debates concerning Ethereum’s long-term consensus and execution architecture.

A Legacy of Transparency and Technical Discourse

The tradition of these AMAs was established to demystify the complex, often opaque, world of core protocol development. By dedicating an afternoon to answering community questions, the Ethereum Foundation ensures that the decision-making processes—which often involve months of rigorous peer review and simulation—are accessible to those building on or participating in the network.

Historically, these sessions have acted as a barometer for community sentiment. From the early days of the transition to Proof-of-Stake to the complexities of sharding and data availability, the Reddit format has allowed for nuanced, long-form technical debates. The persistence of this format is notable in an industry often characterized by rapid, ephemeral communication channels; it reflects a commitment to the "open research" philosophy that has defined Ethereum since its inception.

Chronology of Protocol Development

To understand the weight of the upcoming session, one must look at the recent timeline of Ethereum’s technical upgrades. Following the successful implementation of previous milestones, the current focus has shifted toward refining the network’s efficiency and security:

  • January 2019: The inception of the Ethereum Foundation’s Reddit AMA series, establishing a precedent for annual or semi-annual engagement.
  • The Transition Era: Major upgrades, including the London hard fork (EIP-1559) and the subsequent Merge, dominated the discourse in 2021 and 2022, focusing on fee markets and the shift to Proof-of-Stake.
  • Current Phase: The network is currently navigating the post-Merge roadmap. The Glamsterdam hard fork is presently in the public testing phase, acting as a stress test for new protocol improvements.
  • Future Outlook: The Hegotá upgrade is currently undergoing scope adjustments. Researchers are now evaluating how these changes align with the broader goals of state growth management and long-term protocol sustainability.

Technical Topics for Discussion

The scope for the September 16 session is intentionally broad, inviting inquiries on some of the most complex challenges facing blockchain technology today. Key areas expected to dominate the discussion include:

Post-Quantum Ethereum

As quantum computing matures, the threat to existing cryptographic standards becomes a primary concern. Researchers are exploring how Ethereum might transition to quantum-resistant signatures (such as STARKs or lattice-based cryptography) without compromising user experience or network throughput.

L1-zkEVM and Formal Verification

The integration of Zero-Knowledge Ethereum Virtual Machines (zkEVM) directly into Layer 1 (L1) is a hot topic of research. The objective is to enhance the network’s ability to verify transactions efficiently. Formal verification remains a cornerstone of this effort, ensuring that the code governing the protocol is mathematically proven to be free of critical bugs.

State Growth and Decoupled Consensus

One of the persistent challenges for Ethereum is the "state explosion" problem, where the size of the blockchain state grows beyond the capacity of standard consumer hardware. Discussions regarding the future of state, including state expiry and history expiration, are vital for maintaining decentralization. Furthermore, decoupled consensus—the idea of separating the validation of blocks from the execution of transactions—is being analyzed as a potential solution to improve modularity.

Supporting Data and Ecosystem Metrics

Ethereum’s development is supported by a robust ecosystem of developers and nodes. As of late 2024, the network maintains a high level of validator participation, with millions of ETH staked. The cost of running a node remains a key metric for the Foundation; keeping these costs low is essential for preserving the censorship resistance of the protocol.

The AMA provides a unique opportunity for independent node operators and infrastructure providers to voice their concerns regarding hardware requirements and software overhead, which are direct results of the technical decisions made by the Protocol cluster. The data collected from public testnets during the Glamsterdam phase will likely be presented as evidence of the protocol’s readiness for mainnet deployment.

Official Responses and Community Engagement

The Ethereum Foundation has emphasized that the AMA is not merely a Q&A session, but a mechanism for gathering feedback. By soliciting questions in advance, the researchers can provide more structured and data-backed responses. This proactive approach aims to minimize the "noise" often associated with social media platforms and maximize the signal regarding technical development.

While specific quotes from individual researchers are typically reserved for the day of the event, the general stance of the Foundation remains one of collaborative caution. The core development philosophy prioritizes "safety over speed," a sentiment that will likely be reiterated throughout the session as the community asks about the timelines for various upgrades.

Broader Impact and Implications

The implications of the September 16 AMA extend far beyond the technical details of the protocol. Ethereum’s governance model, often described as "rough consensus," relies heavily on the alignment between core developers and the broader community. These AMAs serve as the formal mechanism for that alignment.

If the community expresses significant concerns regarding the scope of the Hegotá upgrade or the trajectory of L1 privacy, the development team is expected to incorporate these insights into their research agenda. In this sense, the AMA is a vital component of Ethereum’s decentralized governance, ensuring that the protocol remains a neutral, public utility.

Furthermore, the discussion on L1 privacy is particularly timely. As regulatory scrutiny of blockchain transactions increases globally, finding a balance between privacy-preserving technology and compliance requirements is a delicate task. The upcoming session will likely reveal how the Foundation plans to navigate this tension while staying true to the principle of financial sovereignty.

How to Participate

The Ethereum Foundation has launched a dedicated submission form to ensure that questions are organized by topic. This method of collection serves two purposes: it allows researchers to group similar questions for comprehensive answers, and it prevents the session from being overwhelmed by repetitive inquiries.

Interested parties are encouraged to visit the official Ethereum Foundation submission portal. The Foundation has noted that while all questions are welcome, those that are specific, technically grounded, and relevant to the current roadmap are more likely to receive detailed attention.

As Ethereum enters its next phase of maturity, the importance of this open dialogue cannot be overstated. By maintaining this channel of communication, the Ethereum Foundation reinforces the idea that the network is not just a piece of software, but a living, evolving ecosystem built by a global community. The September 16 AMA stands as a testament to this commitment, offering a rare glimpse into the minds of the individuals building the future of decentralized finance and global compute.

September 25, 2026 0 comment
0 FacebookTwitterPinterestEmail
Newer Posts
Older Posts

Recent Posts

  • The Evolution of the Web3 Wallet: From Private-Key Vault to the Command Center of the Agentic Web
  • Ethereum Foundation Announces Annual Protocol AMA Session Scheduled for September 16
  • Kraken Expands Its Digital Asset Offerings with the Official Listing of Doppler Finance (Xdp)
  • CSD BR and Ripple Collaborate to Integrate XRP Ledger into Brazilian Financial Market Infrastructure
  • Web3 Venture Funding Surges to Record $22 Billion in Third Quarter 2025 Driven by Institutional Adoption

Recent Comments

No comments to show.
  • Facebook
  • Twitter

@2021 - All Right Reserved. Designed and Developed by PenciDesign


Back To Top
Dr Crypton
  • Home
  • About Us
  • Contact Us
  • Cookies Policy
  • Disclaimer
  • DMCA
  • Privacy Policy
  • Terms and Conditions

We are using cookies to give you the best experience on our website.

You can find out more about which cookies we are using or switch them off in .

Dr Crypton
Powered by  GDPR Cookie Compliance
Privacy Overview

This website uses cookies so that we can provide you with the best user experience possible. Cookie information is stored in your browser and performs functions such as recognising you when you return to our website and helping our team to understand which sections of the website you find most interesting and useful.

Strictly Necessary Cookies

Strictly Necessary Cookie should be enabled at all times so that we can save your preferences for cookie settings.