• Home
  • About Us
  • Contact Us
  • Cookies Policy
  • Disclaimer
  • DMCA
  • Privacy Policy
  • Terms and Conditions
Dr Crypton
Secure Your Future in Crypto
Cybersecurity & Hacking

CISA’s Critical Data Leak: An In-Depth Examination of Contractor Negligence, Remediation Delays, and Essential Cybersecurity Lessons

by admin July 18, 2026
written by admin

The Cybersecurity and Infrastructure Security Agency (CISA), America’s lead agency for safeguarding critical infrastructure from cyber threats, has released a comprehensive postmortem report detailing a significant data leak. The incident involved a contractor inadvertently publishing dozens of CISA’s internal credentials, including highly sensitive AWS GovCloud keys, to a public GitHub repository. This critical exposure persisted for nearly six months before being brought to CISA’s attention by independent security researchers via KrebsOnSecurity. The agency’s subsequent analysis and the identified gaps in its initial response have prompted cybersecurity experts nationwide to highlight crucial lessons for all organizations, emphasizing the perennial challenges of third-party risk, robust secret management, and effective incident response protocols.

The Genesis of the Exposure: A Contractor’s Critical Error

The root of the incident can be traced back to a contractor’s misstep, which led to 844 megabytes of CISA-related data being made publicly accessible on GitHub. Among the trove of exposed information were files containing administrative credentials to three Amazon AWS GovCloud servers, a highly secure cloud environment specifically designed for U.S. government agencies and contractors handling sensitive workloads. One particularly damning file, aptly named "importantAWStokens," contained these critical administrative keys. Further compounding the severity, another file, "AWS-Workspace-Firefox-Passwords.csv," explicitly listed plaintext usernames and passwords for numerous internal CISA systems. The presence of such unencrypted, high-privilege credentials in a public domain represents a profound security lapse, creating an immediate and severe risk of unauthorized access to CISA’s core infrastructure. This kind of exposure is a goldmine for malicious actors, offering direct pathways into an organization’s most protected digital assets.

A Chronology of Detection and Delayed Response

The timeline of the incident underscores significant challenges in both proactive threat detection and responsive incident management:

  • Pre-May 15, 2026 (Approximately six months prior): A CISA contractor uploads sensitive CISA credentials and data, including AWS GovCloud keys and plaintext passwords, to a public GitHub repository, initiating the exposure.
  • Ongoing Detection by GitGuardian: Security firm GitGuardian, which specializes in continuously scanning public code repositories for exposed secrets, identifies the CISA credentials in the "Private CISA" GitHub repository.
  • Repeated Automated Alerts Ignored: GitGuardian’s automated systems generate and send nine separate notification emails to CISA regarding the exposed credentials. All nine alerts reportedly go unanswered, allowing the exposure to persist.
  • May 15, 2026: External Notification Initiated: Frustrated by the lack of response from CISA, GitGuardian researcher Guillaume Valadon contacts cybersecurity journalist Brian Krebs of KrebsOnSecurity, providing details of the discovered leak.
  • May 15, 2026: KrebsOnSecurity Alerts CISA: KrebsOnSecurity promptly notifies CISA about the existence and contents of the public GitHub repository.
  • Initial Acknowledgment, Subsequent Delays: CISA quickly acknowledges the initial alert from KrebsOnSecurity. However, it takes more than 48 hours for the agency to invalidate the compromised AWS keys and other critical secrets found in the GitHub repository.
  • Post-Incident: CISA’s Internal Review and Public Report: Following the successful remediation, CISA conducts an internal review and subsequently publishes its official postmortem report, "Lessons from CISA’s Cyber Incident," detailing the incident, its causes, and the agency’s response.

The Gravity of the Compromise: AWS GovCloud and Plaintext Passwords

The nature of the leaked data amplifies the seriousness of this incident. AWS GovCloud (US) is Amazon Web Services’ dedicated cloud region designed to host sensitive data and regulated workloads for U.S. government agencies, contractors, and educational institutions. It adheres to stringent compliance standards, including FedRAMP High, DoD SRG IL2/IL4/IL5, and ITAR, making it a cornerstone for secure government operations. The exposure of administrative credentials for such an environment is akin to handing over the master keys to critical national infrastructure. It could have granted unauthorized parties extensive control over CISA’s cloud resources, potentially leading to data exfiltration, service disruption, or the establishment of persistent backdoors.

Moreover, the presence of plaintext usernames and passwords for dozens of internal CISA systems represents a fundamental breakdown in security hygiene. Storing credentials in plaintext is universally condemned as a critical security vulnerability. It eliminates any protective layers that hashing or encryption would provide, making the leaked information immediately usable by an attacker. This not only jeopardizes the systems directly associated with these credentials but also poses a significant lateral movement risk, as attackers often leverage compromised credentials to access other interconnected systems within an organization.

CISA’s Self-Assessment: Admissions and Lessons Learned

In its official report, authored by Preston Werntz, acting Chief Information Officer, and Brad Libbey, acting Chief Information Security Officer, CISA openly acknowledges several critical shortcomings. The agency attributed the protracted key rotation process – taking over 48 hours – to the "complexities of the agency’s systems and interconnections with federal and industry partners." This highlights the inherent challenges faced by large, interconnected governmental entities in swiftly responding to security incidents involving deeply embedded credentials. The report explicitly encourages other organizations to "maintain mature and well-tested key management capabilities," a direct reflection of CISA’s own struggle in this area.

Beyond the technical remediation, CISA also confessed to deficiencies in its incident reporting mechanisms. The postmortem stressed the necessity of "clear and distinct reporting channels" to differentiate between incidents affecting the organization itself and those involving its products or customers. The report candidly noted that CISA’s channels "were not well defined, leading the security researcher to try multiple avenues — including emailing the contractor, submitting through CISA’s vulnerability disclosure platform (intended for broader cybersecurity community vulnerabilities), and ultimately involving a reporter." This fragmented approach not only delayed the crucial initial notification but also underscores a broader systemic issue within many large organizations: the lack of a streamlined, universally recognized process for external parties to report vulnerabilities or exposures directly affecting the organization’s own infrastructure.

External Criticism and the Call for Continuous Vigilance

Guillaume Valadon, the GitGuardian researcher who initiated the process leading to CISA’s notification, provided a pointed critique of the agency’s initial response, particularly the nine ignored automated alerts. Valadon emphasized that "Letting nine notification emails go unanswered is how a one-day incident becomes a six-month exposure." His analysis, published on the GitGuardian blog, called for organizations to "Make it trivial to report a leak about you, not just about your products." He advocated for publishing clear reporting instructions in multiple prominent locations, beyond just a security.txt file, and ensuring that reports concerning internal infrastructure are not shunted into product-bug queues.

Valadon’s criticism resonates deeply within the cybersecurity community, which often faces similar frustrations when attempting to responsibly disclose vulnerabilities to organizations. The incident serves as a stark reminder that even agencies at the forefront of cybersecurity can falter in basic operational security practices and researcher engagement.

Broader Implications and Lessons for All Security Teams

This incident offers invaluable lessons that extend far beyond CISA, impacting government agencies, private enterprises, and the entire cybersecurity ecosystem:

  1. Third-Party Risk Management is Paramount: The leak originated from a contractor, highlighting the critical importance of rigorous vendor security assessments, strict access controls, and continuous monitoring of third-party activities. Organizations must extend their security perimeters to encompass all entities with access to their systems and data.
  2. Robust Secrets Management is Non-Negotiable: The exposure of AWS GovCloud keys and plaintext passwords underscores the need for advanced secrets management solutions. This includes secure storage (e.g., dedicated secrets managers), automated rotation, granular access controls, and robust monitoring for secret usage. Manual key management, especially for high-privilege credentials, is inherently risky.
  3. Continuous Scanning of Public Repositories: The fact that GitGuardian detected the leak through automated scanning, while CISA did not internally for six months, validates the necessity of continuously monitoring public code repositories (like GitHub) for inadvertent secret exposures. This proactive approach can significantly reduce the dwell time of such incidents.
  4. Clear and Accessible Incident Reporting Channels: Organizations must establish clear, well-publicized, and dedicated channels for security researchers and the public to report vulnerabilities or data exposures directly affecting the organization’s own infrastructure. These channels should be distinct from customer support or product-related bug reporting systems and must guarantee a prompt and effective response.
  5. Mature Incident Response Playbooks: While CISA had a cybersecurity incident playbook, it reportedly lacked specific guidance for incidents involving GitHub or other cloud services. This highlights the need for playbooks to be comprehensive, regularly updated, and thoroughly tested to cover all potential incident vectors and technologies in use.
  6. Transparency in Post-Incident Analysis: CISA’s decision to publish a transparent postmortem, detailing its failures and lessons learned, is highly commendable. As Valadon noted, "To my knowledge, it is also the first time a national cybersecurity agency has publicly advocated for secrets scanning and for simplifying relations with security researchers. That is exactly the incident communication we should expect from every organization." This level of transparency fosters trust, enables collective learning, and sets a positive precedent for the industry.

CISA’s Path Forward: Mitigation and Improvement

In response to the incident, CISA has outlined a clear action plan. The agency confirmed that all exposed secrets have been rotated, mitigating immediate risks. Furthermore, CISA has committed to improving its management of developer secrets and enhancing its monitoring capabilities to prevent similar incidents in the future. The agency also announced that the contractor responsible for the exposure had their system access revoked.

Despite the significant shortcomings, CISA’s report also highlighted areas where its security posture proved beneficial. The agency credited its enhanced logging capabilities and the adoption of zero-trust principles in both production and development systems with helping to gauge the scope and impact of the exposed secrets. These detailed logs reportedly allowed CISA to confirm that no customer or mission-critical data was exposed and that the leaked credentials were not utilized outside of CISA’s environments. This aspect underscores the importance of foundational security practices, even when other areas might be lacking. Zero-trust, by minimizing implicit trust and requiring continuous verification, likely limited the potential blast radius of the compromised credentials.

Conclusion: A Call for Collective Responsibility and Continuous Improvement

The CISA data leak serves as a sobering reminder that no organization, regardless of its cybersecurity mandate, is immune to human error and the complexities of modern IT environments. It powerfully illustrates the interconnectedness of security, from the actions of individual contractors to the efficacy of automated detection systems and the responsiveness of incident management teams. The agency’s transparency in admitting its missteps and articulating its lessons learned is a commendable step towards fostering a culture of continuous improvement across the cybersecurity landscape. Ultimately, the incident underscores the imperative for every organization to treat secrets management with the highest priority, cultivate robust relationships with security researchers, and maintain an adaptable, well-tested incident response framework capable of addressing the ever-evolving threat landscape. The collective security of critical infrastructure, governmental operations, and private data depends on it.
July 18, 2026 0 comment
0 FacebookTwitterPinterestEmail
Cybersecurity & Hacking

OpenSSL Servers Vulnerable to "HollowByte" DoS Attack as Okta Discloses Quietly Patched Memory Leak Flaw.

by admin July 18, 2026
written by admin

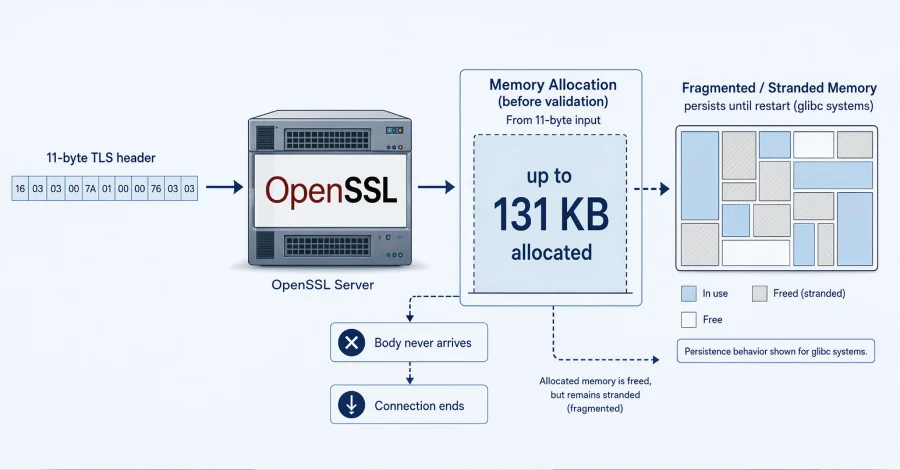
A subtle yet potent denial-of-service (DoS) vulnerability, dubbed "HollowByte" by Okta’s Red Team, has been revealed, affecting unpatched OpenSSL servers where a mere eleven bytes of attacker-controlled data can compel a server to reserve up to 131 KB of memory for a message that never fully materializes. This allocated memory, particularly on systems leveraging glibc (GNU C Library) for memory management, remains inaccessible until the affected process is restarted, leading to a persistent memory leak and potential system instability. The revelation by Okta on Thursday, July 18, 2024, has cast a spotlight on OpenSSL’s decision to integrate the fix for this critical issue without a Common Vulnerabilities and Exposures (CVE) identifier, a public advisory, or even a specific changelog entry, making it exceptionally challenging for system administrators and downstream distributors to identify and address the threat.

The HollowByte Vulnerability: A Deeper Dive into its Mechanics

At its core, the HollowByte vulnerability exploits a fundamental trust mechanism in older versions of OpenSSL’s TLS (Transport Layer Security) handshake process. Every TLS handshake message initiates with a 4-byte header. Crucially, three of these bytes are dedicated to declaring the anticipated length of the message body. Prior to the patch, vulnerable OpenSSL versions would immediately expand their receive buffer to accommodate this declared size upon receiving the header, even before a single byte of the actual message body had arrived and critically, before the handshake’s own internal validation checks could run.

For an inbound ClientHello message, a standard part of initiating a TLS connection, the maximum size ceiling is approximately 131 KB. An attacker can leverage this by sending only the initial 4-byte header, declaring a large body size up to this 131 KB limit, and then abruptly terminating the connection without ever sending the proclaimed message body. This forces the server’s worker thread to block indefinitely, awaiting data that will never arrive, tying up resources. The critical distinction of HollowByte from traditional connection-exhaustion attacks, such as Slowloris, lies in how the memory is handled post-disconnection.

The Crucial Role of Glibc and Persistent Memory Fragmentation

While typical connection-exhaustion attacks aim to overwhelm a server by exhausting its available connection slots, HollowByte introduces a more insidious problem: memory fragmentation and persistent consumption. When the attacker severs the connection, OpenSSL does attempt to free the allocated buffer. However, the interaction with glibc, the ubiquitous C standard library found on most Linux systems, prevents this memory from being truly returned to the operating system for immediate reuse.

Glibc employs sophisticated memory management strategies, often holding onto small and medium-sized memory chunks in various arenas for future reuse rather than immediately releasing them back to the kernel. This optimization is designed to improve performance by reducing the overhead of repeated system calls for memory allocation. In the context of HollowByte, the attack’s efficacy stems from varying the claimed message size across multiple, successive connections. Okta’s testing demonstrated that this variation in requested buffer sizes was sufficient to confuse glibc’s allocator, preventing it from effectively reusing the "freed" chunks.

The result is a phenomenon known as heap fragmentation. The server’s memory becomes littered with numerous small, unusable blocks of memory, effectively reducing the contiguous memory available to the application and the system. The resident set size (RSS) – the portion of memory held in RAM by a process – climbs steadily and remains elevated long after the attacker has ceased their activity. This "frozen" memory is not released until the entire OpenSSL process (or the service using it, like NGINX) is restarted, necessitating manual intervention and leading to prolonged degradation of service.

Impact and Scale of the Attack

Okta’s testing provided concrete figures illustrating the severity of the HollowByte attack. In one scenario involving an NGINX server with 1 GB of RAM, the system was subjected to an Out-Of-Memory (OOM) kill, with 547 MB of its memory permanently consumed by fragments. On a more robust 16 GB server, the attack managed to lock up 25% of the total system memory without ever hitting the server’s configured connection limit. This critical observation led Okta’s Red Team to conclude that "standard connection-limiting defenses won’t stop it," as the attack doesn’t rely on exhausting the number of concurrent connections but rather on depleting available memory through repeated, subtle fragmentation.

The absence of public exploit code or proof-of-concept repositories on platforms like GitHub as of July 18, 2024, suggests that the immediate risk of widespread, automated exploitation might be mitigated. However, the simplicity of the attack vector (11 bytes) means that a motivated attacker could quickly develop and deploy such tools, making the lack of official identification even more concerning.

OpenSSL HollowByte Flaw Could Freeze Server Memory with 11-Byte TLS Requests

OpenSSL’s Controversial Handling and Lack of Transparency

The most contentious aspect of the HollowByte saga is OpenSSL’s decision regarding its disclosure and classification. The fix, integrated into OpenSSL releases 4.0.1, 3.6.3, 3.5.7, 3.4.6, and 3.0.21, all dated June 9, was implemented by Matt Caswell, a prominent OpenSSL developer. His pull request, specifically for this patch, explicitly states the security team’s choice to "handle this as a ‘bug or hardening’ only fix."

OpenSSL’s official security policy delineates four severity tiers for vulnerabilities: Critical, High, Moderate, and Low. Notably, "bug or hardening" is not one of these categories. Even issues classified as "Low" typically warrant a CVE identifier, an entry in the project’s changelog, and a listing on the dedicated vulnerabilities page. HollowByte received none of these standard recognitions. The Hacker News confirmed the absence of any mention of this fix in the release notes or the 23 entries of OpenSSL’s 4.0.1 changelog.

This lack of transparency poses significant challenges. Without a CVE, security scanners cannot automatically detect the vulnerability. Without an advisory or changelog entry, system administrators have no official notification that a security-relevant update has been applied, or even that such a vulnerability existed.

OpenSSL has not publicly provided a detailed explanation for this specific classification. Potential arguments for their decision might include the bounded nature of the allocation (131 KB per connection is finite, unlike unbounded growth), and the general understanding that TLS servers inherently allocate memory per connection. From this perspective, a bounded allocation might not be seen as a true "vulnerability" in the traditional sense. However, Okta’s counter-argument, emphasizing that the memory never returns, fundamentally alters this calculus, transforming a bounded allocation into a persistent resource exhaustion mechanism.

Comparing to Other OpenSSL Vulnerabilities

The decision to triage HollowByte below the "Low" severity tier appears inconsistent when compared to OpenSSL’s past vulnerability classifications. For example, in January, OpenSSL assigned CVE-2025-66199 (rated Low) to a TLS 1.3 certificate-compression bug. This flaw involved a peer-supplied length growing a heap buffer before validation, potentially consuming around 22 MiB per connection. While requiring specific conditions (certificate compression compiled in, available algorithm, extension negotiated, client certificates requested on servers), it was still deemed worthy of a CVE. HollowByte, in contrast, requires none of these specific conditions, making it arguably simpler to exploit.

Furthermore, the same June 9 release that contained the HollowByte fix also assigned CVE-2026-34183 (rated Moderate) to an unbounded memory growth vulnerability within the QUIC PATH_CHALLENGE handler. Both this and HollowByte are memory-exhaustion DoS attacks, yet one received a CVE and a moderate rating, while the other was quietly integrated as a "bug fix." This disparity raises questions about the consistency and transparency of OpenSSL’s vulnerability management process. The June 9 release also notably closed 18 other CVEs, including a High-severity use-after-free bug in PKCS7_verify(), ensuring that users upgrading to these versions received these critical fixes, albeit without specific notice for HollowByte.

Challenges for Patching and Downstream Distributors

The implications of OpenSSL’s non-disclosure extend significantly to downstream distributors and system administrators. Major Linux distributions like Red Hat often employ a "backporting" strategy, where security fixes are applied to older, stable versions of software packages rather than forcing a full version upgrade. This means a patched OpenSSL package on a Red Hat system might still report its original, older version number.

Normally, the presence of a CVE identifier and corresponding security advisories (often linked to OVAL feeds) would enable distributors to clearly communicate the specific vulnerabilities addressed and allow automated tools to verify patch status. In the absence of a CVE for HollowByte, this standard process breaks down entirely. System administrators cannot rely on typical patch pipelines, vulnerability scanners, or official advisories to identify if their systems are vulnerable or have been patched.

Instead, they are forced into a manual, labor-intensive process: either consulting the package changelog (which may not explicitly mention the "bug or hardening" fix) or directly contacting maintainers to inquire whether their builds rebased on the June 9 releases or specifically incorporated the relevant pull requests. These pull request identifiers are 30792 for master and 4.0, 30793 for 3.6, 3.5, and 3.4, and 30794 for 3.0. Organizations that compile OpenSSL from source must proactively upgrade to the specified patched releases and ensure all services linking against the old library are restarted.

OpenSSL HollowByte Flaw Could Freeze Server Memory with 11-Byte TLS Requests

The Unaddressed DTLS Flaw

Adding another layer of concern, the fix for HollowByte explicitly covers only TLS. Matt Caswell noted in the pull request that addressing the same vulnerability in DTLS (Datagram Transport Layer Security) would have been "far more invasive," leading the project to defer a fix for it. Analysis by The Hacker News revealed that the DTLS handshake file remained byte-identical between OpenSSL 3.6.2 and 3.6.3 (the patched version), confirming that the vulnerability persists in DTLS. Even in OpenSSL 4.0.1, the newest release, the DTLS path continues to size its buffer based on the length declared by the peer, leaving it vulnerable to the same memory exhaustion attack.

OpenSSL has not classified this lingering DTLS vulnerability, nor has it committed to a timeline for its remediation. As with the TLS fix, no mention of this unaddressed DTLS path appears in release notes, changelogs, or the vulnerabilities page, with the only public acknowledgement residing within the pull request comments. This omission means that DTLS-based applications, which are often used in latency-sensitive or unreliable network environments, remain exposed to a known, unfixed memory exhaustion attack.

OpenSSL’s Role in Internet Security and Disclosure Standards

OpenSSL is a cornerstone of internet security, providing the cryptographic functions that underpin countless websites, applications, and services. Its ubiquity means that vulnerabilities, even seemingly minor ones, can have widespread repercussions. The project operates as an open-source endeavor, relying on community contributions and a dedicated core team. The transparency of its security advisories and patching processes is crucial for maintaining trust and enabling rapid, effective responses to threats across the global digital infrastructure.

The handling of HollowByte raises important questions about OpenSSL’s vulnerability disclosure policy and its commitment to transparency. While the project has a history of addressing critical flaws and providing detailed CVEs, the decision to quietly patch a DoS vulnerability that bypasses standard defenses and causes persistent memory leaks could erode confidence among its user base and security researchers.

Responsible disclosure typically involves public advisories, clear identification (like CVEs), and detailed changelogs to ensure that all stakeholders are aware of risks and can take appropriate action. Deviating from these established norms, especially for a widely used library like OpenSSL, introduces unnecessary risk and burden onto the very community it serves.

Recommendations and Mitigation

For system administrators and organizations utilizing OpenSSL, immediate action is paramount:

  1. Upgrade OpenSSL: The most direct mitigation is to upgrade to the latest patched versions: OpenSSL 4.0.1, 3.6.3, 3.5.7, 3.4.6, or 3.0.21. Ensure that any services or applications linking against OpenSSL are restarted after the upgrade to load the new library.
  2. Verify Patch Application: Due to the lack of a CVE, verify that the specific patches corresponding to pull requests 30792, 30793, or 30794 have been applied, especially if relying on distribution-specific packages. Consult package changelogs or contact maintainers directly.
  3. Monitor Memory Usage: Implement robust monitoring for memory consumption on TLS-serving processes. Anomalous, persistent increases in resident set size (RSS) that do not correlate with increased connection counts could indicate an ongoing HollowByte attack.
  4. Consider DTLS Implications: If using DTLS-based applications with OpenSSL, be aware that the HollowByte vulnerability remains unaddressed in this protocol. Implement additional application-level protections or explore alternative solutions if DTLS is critical to your infrastructure.

Ongoing Questions and Future Implications

As of the latest information, "The Hacker News" has reached out to OpenSSL for clarification on why HollowByte was triaged below "Low" and whether the fix will extend to the extended-support 1.1.1 and 1.0.2 branches. Inquiries have also been directed to Okta regarding whether the memory fragmentation effect survives with allocators other than glibc, which could broaden or narrow the scope of affected systems. The answers to these questions will be crucial in fully understanding the vulnerability’s impact and OpenSSL’s long-term strategy for addressing such subtle yet impactful flaws.

The HollowByte incident serves as a critical reminder of the complexities of securing fundamental internet infrastructure and the ongoing challenges faced by open-source projects in balancing rapid development with transparent and consistent security disclosure practices. The implications extend beyond just this single vulnerability, potentially influencing how future "bug or hardening" fixes are communicated and managed within the broader cybersecurity ecosystem.

July 18, 2026 0 comment
0 FacebookTwitterPinterestEmail
Cybersecurity & Hacking

HollowByte DDoS flaw bloats OpenSSL server memory with 11-byte payload

by admin July 18, 2026
written by admin

The Unseen Backbone: Understanding OpenSSL’s Critical Role

OpenSSL stands as an indispensable open-source cryptography library, serving as the bedrock for secure communication across the internet. It provides the implementation for the Transport Layer Security (TLS) and Secure Sockets Layer (SSL) protocols, which encrypt data transmitted between web browsers and servers, email clients and servers, and countless other applications. From securing e-commerce transactions to protecting sensitive personal data, OpenSSL’s functions are pervasive, underpinning a vast array of digital services. Its widespread adoption spans popular web servers like NGINX and Apache, various programming language runtimes such as Node.js, Python, Ruby, and PHP, and critical databases including MySQL and PostgreSQL. Furthermore, it is a standard component pre-installed on most Linux distributions, responsible for managing TLS encryption, digital certificates, and cryptographic operations.

Given its ubiquitous presence, any vulnerability within OpenSSL carries profound implications for global cybersecurity. Historically, major flaws like the "Heartbleed" bug in 2014 demonstrated the catastrophic potential of OpenSSL vulnerabilities, exposing sensitive data from millions of servers worldwide. While HollowByte does not involve data theft or remote code execution, its ability to induce a denial-of-service condition through resource exhaustion is a severe operational threat, capable of disrupting critical services, causing significant financial losses, and eroding user trust.

Dissecting HollowByte: An 11-Byte Path to Server Paralysis

The mechanics of the HollowByte vulnerability were brought to light by Okta’s Red Team in a detailed advisory published earlier this week. Their research meticulously describes how a seemingly innocuous design flaw in the TLS handshake process could be weaponized for a potent DoS attack. The vulnerability exploits a specific interaction during the initial phase of establishing a secure connection.

In a standard TLS handshake, each message exchanged between a client and a server begins with a 4-byte header. Within this header, a crucial three-byte field is designated to declare the expected size of the subsequent handshake data. This mechanism is designed to inform the receiving party about the incoming data’s length, allowing for appropriate buffer allocation. However, researchers discovered that vulnerable versions of OpenSSL prematurely allocate memory based on this declared length before validating the actual size of the incoming payload.

This pre-allocation without validation creates the perfect window for exploitation. An unauthenticated attacker can initiate a TLS connection and transmit an extremely small, malicious input—just 11 bytes—containing a header that falsely declares a significantly larger message body will follow. The server, trusting the header’s claim, allocates a substantial chunk of memory to accommodate the purported large message. Crucially, the worker thread responsible for this connection then enters a blocking state, indefinitely awaiting the arrival of the promised data that, by design, will never materialize.

The attacker can repeat this process across numerous concurrent connections. Each malicious connection triggers the server to allocate considerable amounts of memory based on exaggerated claims, while transmitting only a minimal volume of data. This efficient yet insidious method allows an attacker to rapidly deplete a server’s available memory resources.

The Memory Fragmentation Trap: Why Bloat Persists

A key aspect that exacerbates the impact of HollowByte is its interaction with the underlying memory management system, specifically the GNU C Library (glibc), which is widely used in Linux environments. While OpenSSL eventually frees the buffers associated with a dropped connection, glibc’s approach to memory handling introduces a critical caveat.

Okta researchers explain that glibc does not immediately return small-to-medium memory allocations to the operating system. Instead, it retains these freed chunks for potential reuse by the application. This optimization aims to reduce the overhead of constantly requesting and releasing memory from the kernel. However, in the context of a HollowByte attack, this mechanism becomes a liability.

HollowByte DDoS flaw bloats OpenSSL server memory with 11-byte payload

By launching waves of connections with randomized claimed sizes, an attacker prevents the memory allocator from efficiently reusing these freed chunks. This leads to severe "heap fragmentation," where the server’s memory becomes littered with numerous small, unusable blocks, even though the total "freed" memory might appear substantial. Consequently, the server’s Resident Set Size (RSS), which represents the portion of memory held in RAM, climbs continuously and remains permanently bloated. Even after the attacker disconnects and the malicious connections are terminated, the server does not fully recover its memory footprint. The only effective way to reclaim the wasted space and restore the server to its optimal memory state is through a full restart of the affected process. This requirement for manual intervention adds a significant operational burden and prolongs service disruption.

Timeline of Discovery and OpenSSL’s Response

The timeline surrounding the HollowByte vulnerability, while not explicitly detailed in public advisories, can be inferred from the available information. Okta’s Red Team likely discovered the flaw during routine security research or penetration testing activities. Following responsible disclosure protocols, they would have privately reported their findings to the OpenSSL project maintainers.

OpenSSL’s response was swift, albeit discreet. Instead of assigning a public Common Vulnerabilities and Exposures (CVE) identifier, the OpenSSL team opted for a "silent fix." This approach, while sometimes employed to expedite patching and minimize immediate exploitation risks before a full public disclosure, can also lead to challenges in tracking and prioritizing patches for system administrators. The fix was incorporated into the latest development branch and subsequently backported to several older, still-supported releases.

The patched versions include OpenSSL 4.0.1, with backports to 3.6.3, 3.5.7, 3.4.6, and 3.0.21. The core of the fix lies in modifying how OpenSSL handles buffer allocation. Instead of relying solely on the header’s declared length, the patched versions now grow the buffer incrementally only as the actual data arrives, effectively ignoring any potentially malicious oversized claims in the header. This "grow-as-you-go" approach prevents premature, excessive memory allocation, thereby mitigating the DoS vector.

Okta’s public advisory, issued "earlier this week" (referring to the week of June 24, 2026, based on the original article’s context), served as the formal public disclosure, urging organizations to apply the patches immediately. The decision by OpenSSL to categorize this as a "hardening fix" rather than a critical security vulnerability, despite its significant impact, has led security experts like Okta to emphasize the practical severity of the issue, strongly recommending an immediate upgrade.

Far-Reaching Impact and Operational Disruptions

The ubiquitous nature of OpenSSL means the HollowByte vulnerability has a vast potential blast radius. Any system or application that relies on a vulnerable version of the library for TLS communication is susceptible. This includes, but is not limited to:

  • Web Servers: NGINX and Apache, which power a significant portion of the internet, are directly impacted.
  • Application Servers and Runtimes: Node.js, Python, Ruby, and PHP environments often link against OpenSSL, making applications built on these platforms vulnerable.
  • Databases: MySQL and PostgreSQL, when configured for encrypted connections, utilize OpenSSL.
  • Operating Systems: Most Linux distributions come with OpenSSL pre-installed, affecting various system services.
  • Network Appliances and IoT Devices: Many embedded systems and network devices also rely on OpenSSL for secure communication, potentially exposing a wide array of infrastructure.

Okta’s testing demonstrated the practical impact of HollowByte across different server capacities. For low-capacity environments, the attack could easily lead to complete memory depletion, causing service crashes and prolonged downtime. Even on higher-specification servers, which typically have more robust resources, the attack proved effective, causing memory loss of up to 25% while remaining below typical security alerting thresholds for bandwidth usage. This stealthy characteristic makes HollowByte particularly dangerous, as attacks might go unnoticed by conventional network monitoring tools focused on traffic volume.

The consequences of a successful HollowByte DoS attack extend beyond mere technical disruption:

  • Operational Disruption: Unavailability of critical services, leading to loss of productivity and inability to conduct business.
  • Financial Loss: Direct revenue loss from inaccessible services, costs associated with incident response, system restarts, and potential hardware upgrades.
  • Reputational Damage: Erosion of customer trust, negative public perception, and potential legal or compliance repercussions.
  • Resource Strain: IT and security teams are diverted to handle the incident, troubleshoot memory issues, and implement emergency patching.
  • Cascading Failures: In complex, interconnected systems, the failure of one OpenSSL-dependent service could trigger failures in others.

While DoS vulnerabilities are sometimes perceived as less severe than those enabling data theft or code execution, their capacity for widespread operational paralysis makes them a significant threat in today’s interconnected digital landscape.

HollowByte DDoS flaw bloats OpenSSL server memory with 11-byte payload

Broader Implications and Mitigation Strategies

The HollowByte vulnerability serves as a stark reminder of several critical aspects of modern cybersecurity:

Supply Chain Security: As a foundational component, OpenSSL is deeply embedded in the software supply chain. A flaw in such a widely used library can ripple through countless applications and systems, making it challenging for organizations to identify all affected assets and apply patches uniformly. This highlights the importance of robust software bill of materials (SBOM) practices and continuous vulnerability management for third-party components.

Patch Management Challenges: The lack of a CVE identifier for HollowByte, while potentially speeding up initial fixes, creates hurdles for organizations relying on automated vulnerability scanning and patch management systems. System administrators must proactively monitor OpenSSL releases and security advisories from researchers like Okta, rather than waiting for CVEs to appear in their vulnerability databases. The need to backport fixes across multiple OpenSSL versions also complicates deployment, as organizations may be running older, but still supported, releases.

Detection and Response: The stealthy nature of HollowByte, characterized by a tiny attack payload and an impact that might initially fall below typical bandwidth-based alerting thresholds, demands more sophisticated detection mechanisms. Organizations need to implement robust memory usage monitoring (e.g., tracking RSS, heap usage) and anomaly detection systems that can flag unusual resource consumption patterns, even if network traffic remains low. Proactive threat hunting for suspicious TLS handshake patterns could also be beneficial.

The Role of Security Research: Okta’s Red Team’s discovery and detailed disclosure are crucial examples of how independent security research strengthens the overall cybersecurity ecosystem. By uncovering such subtle yet impactful flaws, researchers help improve the security posture of widely used open-source projects, benefiting countless users.

Recommendations for Organizations:
Security experts, including Okta, unequivocally recommend that organizations prioritize upgrading their distribution’s OpenSSL packages immediately. Even though OpenSSL categorized it as a "hardening fix," the practical implications of HollowByte warrant urgent attention.

  1. Immediate Patching: Identify all systems running vulnerable OpenSSL versions (specifically those older than 4.0.1, 3.6.3, 3.5.7, 3.4.6, and 3.0.21) and apply the available patches without delay.
  2. Inventory Management: Maintain an accurate inventory of all software and libraries, including their versions, to quickly identify affected assets during future vulnerability disclosures.
  3. Enhanced Monitoring: Implement advanced monitoring solutions that track system resource utilization, particularly memory (RSS, heap usage), and look for unusual spikes or persistent bloat, even in the absence of high network traffic.
  4. Incident Response Planning: Ensure incident response plans are updated to address DoS scenarios, including procedures for identifying compromised systems, mitigating attacks, and restoring services.
  5. Stay Informed: Regularly consult official OpenSSL project announcements, vendor security advisories, and reputable cybersecurity news sources for the latest vulnerability information.

The HollowByte vulnerability underscores the continuous arms race between attackers and defenders in the digital realm. As critical infrastructure increasingly relies on complex, interconnected software components, the security of foundational libraries like OpenSSL remains paramount, demanding vigilance, rapid response, and a collaborative effort from the entire cybersecurity community.

July 18, 2026 0 comment
0 FacebookTwitterPinterestEmail
Bitcoin & Altcoins

AI-Powered Agents Uncover Critical Vulnerabilities in Ethereum Protocol Code, Shifting the Security Landscape

by admin July 18, 2026
written by admin

The Ethereum Foundation’s Protocol Security team has achieved a significant milestone in its ongoing efforts to bolster the network’s security infrastructure. By deploying coordinated Artificial Intelligence (AI) agents against core components of the Ethereum protocol, the team has successfully identified and validated real-world bugs. This groundbreaking work, detailed in a recent announcement, not only underscores the growing efficacy of AI in cybersecurity but also highlights a crucial shift in the nature of security auditing. The most notable discovery, now publicly disclosed as CVE-2026-34219, is a remotely triggerable panic within libp2p’s gossipsub, a fundamental element of the peer-to-peer communication layer utilized by Ethereum consensus clients. This vulnerability, which has since been patched and disclosed, represents a tangible success for the AI-driven auditing approach.

While the discovery of bugs was an expected outcome, the Ethereum Foundation team expressed surprise at the efficiency of the AI agents in identifying genuine issues and, more importantly, the significant effort required to distinguish these from false positives. This realization is central to the team’s strategy, as they share their methodologies with client teams and security researchers aiming to replicate these advanced auditing techniques. The core of their approach involves directing sophisticated AI models toward codebases, allowing them to conduct automated searches and subsequently triage the findings. This mirrors strategies being adopted by other leading organizations in the field, including Anthropic’s Frontier Red Team, which has employed similar AI agents to uncover bugs across the Python ecosystem through property-based testing, and Cloudflare, which has integrated frontier models into its security research frameworks. The consensus across these efforts points to a recurring cycle: deploying AI for broad exploration, followed by rigorous validation. The primary challenge, therefore, lies not in the generation of potential issues, but in effectively filtering the signal from the considerable noise.

Orchestrating AI for Protocol Security: A Decentralized Approach

The operational framework established by the Ethereum Foundation’s Protocol Security team emphasizes a decentralized model for AI agent coordination. Multiple agents are deployed concurrently to analyze a single target system. Their collaboration is facilitated through the code repository itself, leveraging version control for shared state management and eliminating the need for a centralized coordination process. This architecture draws inspiration from Anthropic’s successful implementation of a fleet of AI agents for building a C compiler, where agents autonomously commit their findings and progress. This distributed methodology enhances robustness and reduces potential points of failure.

The roles within this system emerge organically from the nature of the discovered issues. The process follows a structured pipeline, refined through insights from organizations like Cloudflare, which emphasizes stages such as reconnaissance, parallel hunting, independent validation, deduplication, and reporting. For a candidate vulnerability to be recognized as a genuine finding, it must meet a stringent set of criteria. These criteria, codified in a schema, mandate specific, testable claims and a clear definition of completion. A candidate finding must detail:

  • Target: The specific component and entry point that an attacker can realistically access.
  • Invariant: The fundamental property that must remain unbroken within the system.
  • Mechanism: The precise method by which the invariant could be compromised.
  • Success: Observable proof of the exploit, such as a system panic, an unresponsiveness stall, or the acceptance of invalid input.
  • Reproducer: A self-contained artifact capable of consistently demonstrating the failure when executed against the actual codebase.
  • Dedup: A unique identifier to prevent redundant investigations of the same issue by different agents.

This rigorous schema compels agents to formulate concrete, verifiable assertions, preventing them from relying on subjective assessments of risk. The requirement for an observable proof ensures that findings are grounded in demonstrable system behavior rather than speculative concerns.

The Imperative of Reproducibility: "If It Cannot Be Reproduced, It Did Not Happen"

At the forefront of the Ethereum Foundation’s AI-driven security auditing is an unwavering commitment to reproducibility. A candidate vulnerability is only considered a validated finding once a self-contained artifact exists that can reliably reproduce the failure within the live codebase, and crucially, can be executed by individuals other than the original discoverer. This "reproducible or it didn’t happen" principle serves as the ultimate arbiter of truth, circumventing the eloquent, yet potentially misleading, narratives that AI agents can generate.

The reproducer acts as an objective arbiter, unswayed by the confidence of the AI’s write-up. Its efficacy lies in its binary outcome: it either works, or it does not. This process is particularly adept at identifying and mitigating common sources of false positives that have emerged from AI-driven security analysis. These recurring pitfalls include:

  • Call chains that appear reachable but are not: AI models can sometimes construct plausible execution paths that, upon closer inspection, are impossible to trigger in a typical operational environment.
  • Circumventing the success check: This occurs when an AI incorrectly identifies a system behavior as a vulnerability, but the "success" metric is achieved through a mechanism that is not indicative of a genuine security flaw. For instance, a temporary warning message might be misinterpreted as a critical failure.
  • Inflating severity claims: AI agents may overstate the impact of a discovered issue to align with the dramatic tone of their explanatory narratives, leading to misallocated resources and undue alarm.
  • Exploiting sequences of valid steps: The most insidious bugs are often those that manifest only when a series of seemingly innocuous actions are performed in a specific order. AI agents, particularly in their current iterations, can struggle to identify vulnerabilities that span multiple, sequential operations.

These issues are not unique to AI; they mirror analogous problems encountered in traditional testing methodologies. The novel challenge presented by AI is the sheer volume and speed at which these misleading candidates can be generated. The confidence with which AI presents these flawed findings necessitates an automated, rigorous verification process, as human oversight alone cannot keep pace with the output.

Navigating the Signal-to-Noise Ratio: The Triage as the True Bottleneck

The core challenge in AI-driven security auditing lies in effectively managing the signal-to-noise ratio. The vast majority of AI-generated candidates are ultimately incorrect, duplicates of already known issues, or fall outside the defined scope of the audit. This is not a flaw in the methodology itself, but rather an inherent characteristic of its operation. The objective is to rapidly discard invalid findings while backing legitimate ones with irrefutable proof.

Each candidate that passes initial screening undergoes two independent evaluations. First, an assessment is made to determine if a real-world attacker could realistically exploit the vulnerability in a standard network configuration. Second, the cost of exploitation for the attacker is weighed against the potential cost to the network if the vulnerability is realized. A bug exploitable by any single peer, for instance, carries a different implication than one requiring specialized access or substantial computational resources.

A critical component of this process is the continuous comparison of new findings against a constantly updated repository of known, resolved, or rejected vulnerabilities. Without this historical context, AI agents risk rediscovering and re-reporting issues that have already been addressed, leading to wasted effort and duplicated work.

The acceptance rate of AI-generated candidates varies significantly across different codebases. Auditing mature, heavily scrutinized code often results in a very low acceptance rate, a finding that is itself valuable. The declaration of "extensive investigation yielded no significant findings" is a valid and important security posture. Conversely, applying these methods to less explored code or to formally verified systems, where machine-checked proofs provide a model of correctness, can yield a higher proportion of validated issues.

Industry leaders echo this sentiment. Cloudflare’s experience suggests that a narrowly defined audit scope is more effective than broad, untargeted scanning. Anthropic’s property-based testing agent, for example, generated approximately a thousand candidate reports, but a subsequent ranking and expert review process distilled these down to a select few that held up under scrutiny, achieving an approximately 86% validation rate for the top tier. The generation phase, while impressive, was demonstrably less resource-intensive than the subsequent validation and triage.

AI’s Strengths and Weaknesses in Security Auditing

A balanced perspective on AI’s capabilities in security auditing reveals distinct areas of strength and notable limitations:

Strengths Weaknesses
Comprehending specifications and code Identifying call chains that appear plausible but are unreachable
Articulating and verifying invariants Exploiting validation checks for a misleading positive outcome
Generating reproducible exploit concepts Overstating vulnerability severity to match narrative impact
Proposing initial root cause hypotheses Detecting bugs that emerge from sequences of valid user actions

The performance of AI agents is not uniform across all tasks. Cybersecurity researcher Stanislav Fort describes this phenomenon as a "jagged frontier," where a model adept at reconstructing a complete exploit chain in one codebase might falter when performing basic data-flow tracing in another. This variability underscores the necessity of independently verifying each candidate finding.

Perhaps the most crucial limitation is the AI’s proficiency in one-shot reasoning versus its struggle with bugs that span a sequence of operations. In these cases, where each individual step is benign but the order of execution triggers a vulnerability, the AI’s role shifts from a primary search tool to a generator of potential sequences for a more traditional stateful test harness. When employed in this supportive capacity, AI proves highly effective. However, using it as a direct replacement for comprehensive stateful testing risks overlooking the most damaging vulnerabilities – those that only manifest under specific, multi-step conditions.

Maintaining Integrity: Foundational Practices for Trustworthy Audits

The trustworthiness of AI-generated security findings hinges on the consistent application of a few straightforward, yet essential, practices:

  • Reproducibility is Paramount: All findings must be accompanied by a self-contained, executable artifact that reliably reproduces the issue on the target system.
  • Independent Verification: Each candidate finding must undergo at least two independent checks to validate its authenticity and scope.
  • Maintain a Known Issues List: A comprehensive and up-to-date ledger of identified, resolved, and rejected vulnerabilities is crucial to prevent redundant investigations.
  • Consider Attacker Cost: The practical feasibility of exploiting a vulnerability should be assessed by comparing the resources required by an attacker against the potential impact on the network.
  • Define Scope Clearly: Audits should operate within clearly defined parameters to ensure that findings are relevant and actionable.

The Evolving Bottleneck: From Discovery to Judgment

The advent of AI in cybersecurity has not rendered human security researchers obsolete; instead, it has fundamentally reshaped their roles. The time previously dedicated to formulating and pursuing hypotheses is now redirected towards a more sophisticated form of judgment: evaluating AI-generated findings at scale. This involves the meticulous construction and maintenance of validation oracles, the rigorous execution of triage processes, the management of known issues databases, and the careful handling of vulnerability disclosures.

The bottleneck has not disappeared; it has merely relocated. It has moved from the act of bug discovery to the critical task of ensuring the veracity and trustworthiness of those discoveries. This shift represents a positive development, as it places human expertise at the nexus of judgment and validation, where nuanced understanding and critical thinking are most valuable. However, ignoring this enduring bottleneck can lead to the deployment of flawed security assurances.

The practices that underpin effective AI-driven security auditing are not novel. Reproducible failure analysis, the establishment of reliable validation mechanisms, and meticulous triage are the same foundational principles that have elevated fuzzing from a research curiosity to an industry standard over the past fifteen years. While the tools are new and rapidly advancing, the underlying methodologies remain constant.

The pace of change in AI tooling remains a subject of ongoing debate. Nicholas Carlini, a respected voice in AI security, posits that the exponential growth trajectory of AI capabilities warrants serious consideration, even while acknowledging the inherent uncertainties and broad error margins. Should the AI’s generation capacity continue to accelerate at this rate, the human capacity for judgment and verification must evolve in tandem. Failure to do so will result in an ever-widening chasm between the volume of AI-generated claims and the actual verified security posture of systems.

For the critical infrastructure upon which Ethereum relies, this emphasis on robust judgment is paramount. AI agents empower the security team to cover a significantly broader attack surface than manual methods alone would permit. In return, this capability demands a more rigorous and discerning approach to evaluating the vast array of confident-sounding claims that AI produces. This trade-off is undeniably beneficial, provided that the ultimate product – the verified security of the network – remains the central focus, underscored by the critical role of human expertise in the judgment process.

July 18, 2026 0 comment
0 FacebookTwitterPinterestEmail
Bitcoin & Altcoins

Kraken Welcomes Vanta Network (SN8) to Its Trading Platform

by admin July 18, 2026
written by admin

Kraken, a leading cryptocurrency exchange, has announced the highly anticipated listing of Vanta Network (SN8) on its platform, effective July 16, 2026. This strategic integration expands Kraken’s diverse portfolio of digital assets, offering its global user base access to a novel fintech infrastructure layer within the burgeoning decentralized intelligence ecosystem of Bittensor. The addition signifies a significant step for both Vanta Network, providing enhanced liquidity and accessibility, and for Kraken, reinforcing its commitment to pioneering digital asset offerings.

The Vanta Network: A Decentralized Intelligence Frontier

Vanta Network, operating as subnet 8 (SN8) within the broader Bittensor network, positions itself as a critical fintech infrastructure layer. Bittensor, a sophisticated protocol that incentivizes the creation and deployment of machine intelligence, aims to build a decentralized network of AI agents capable of learning and collaborating. Vanta Network specifically focuses on optimizing this ecosystem for financial applications, serving as a platform where quantitative traders, AI agents, and discretionary traders can converge.

The core innovation of Vanta Network lies in its unique approach to incentivizing and validating trading strategies. Participants, referred to as miners, run their strategies on the Vanta subnet. Their performance is meticulously scored on-chain using robust risk-adjusted metrics such as the Sortino and Omega ratios. This transparent and auditable scoring mechanism ensures that only the most effective and resilient strategies are recognized and rewarded. The network’s scoring rules are open-source, allowing for independent verification and fostering an environment of trust and accountability.

A Chronology of Integration and Opportunity

The journey to Vanta Network’s trading debut on Kraken is a testament to the growing maturity of decentralized finance and artificial intelligence integration. While the exact timeline of negotiations and technical integrations remains proprietary, the announcement on July 16, 2026, marks the culmination of extensive due diligence and partnership development.

Prior to this official listing, Vanta Network has been steadily building its presence within the Bittensor ecosystem. Its consistent ranking among the top subnets on Bittensor indicates a strong and active community of developers and participants. The protocol’s design, which allocates simulated capital to top-performing strategies based on verified on-chain performance, has been instrumental in attracting sophisticated algorithmic traders and researchers. This simulated-capital allocation mechanism provides a powerful incentive for continuous improvement and innovation, creating a virtuous cycle of performance enhancement.

The availability of SN8 on Kraken provides a crucial on-ramp for new participants seeking to engage with the Vanta Network. Historically, accessing and trading tokens within specialized subnets could involve complex technical processes. By integrating SN8, Kraken democratizes access, allowing a wider audience to participate in the Vanta Network’s innovative financial infrastructure.

SN8: The Native Token of Vanta Network

SN8 serves as the native utility and governance token of the Vanta subnet. Its integration into a major exchange like Kraken is expected to significantly bolster its liquidity and market presence. The token plays a vital role in the Vanta ecosystem, potentially facilitating:

  • Staking and Governance: SN8 holders may have the ability to stake their tokens to secure the network and participate in governance decisions, influencing the future development and direction of the Vanta subnet.
  • Incentivization: The token is likely used to reward miners for running successful trading strategies and contributing to the network’s overall performance.
  • Transaction Fees: SN8 could also be utilized to pay for transaction fees within the Vanta subnet, ensuring the smooth operation of the decentralized infrastructure.

The precise utility and governance mechanisms of SN8 are detailed within the Vanta Network’s whitepaper and associated documentation, which are publicly available. Kraken’s listing of SN8 means that investors and traders can now acquire and trade this token directly on a reputable and regulated platform, reducing friction and enhancing market efficiency.

SN8 is available for trading!

Strategic Implications for the Crypto Landscape

The listing of Vanta Network (SN8) on Kraken carries several significant implications for the broader cryptocurrency and decentralized finance (DeFi) landscape:

  • Validation of Decentralized Intelligence: The inclusion of a subnet token focused on AI and fintech infrastructure underscores the growing recognition of decentralized intelligence as a transformative technology. It signals that innovative applications beyond traditional DeFi protocols are gaining traction and investor confidence.
  • Enhanced Liquidity and Accessibility: For SN8, the immediate benefit is increased liquidity. Traders can now buy and sell SN8 on Kraken with greater ease, potentially leading to more stable pricing and reduced volatility. This accessibility is crucial for attracting more developers, traders, and capital to the Vanta Network.
  • Bridge Between AI and Finance: Vanta Network represents a compelling bridge between the rapidly evolving fields of artificial intelligence and financial markets. Its success on Kraken could inspire further integration of AI-driven strategies and infrastructure within the DeFi space, paving the way for more sophisticated and efficient financial tools.
  • Kraken’s Commitment to Innovation: This listing reinforces Kraken’s position as a forward-thinking exchange that actively seeks out and supports innovative projects. By providing a platform for novel assets like SN8, Kraken contributes to the diversification and maturation of the digital asset ecosystem.

Expert Perspectives and Industry Reactions (Inferred)

While direct quotes from Vanta Network developers or Kraken executives regarding this specific listing are not provided in the initial announcement, industry observers and analysts would likely view this as a positive development.

A representative from a prominent blockchain analytics firm might comment, "The listing of SN8 on Kraken is a significant endorsement for the Vanta Network and the broader Bittensor ecosystem. It validates the concept of decentralized intelligence applied to financial markets and provides a crucial gateway for wider adoption. We anticipate this will spur further development and participation in the subnet."

Similarly, a DeFi strategist could remark, "Kraken’s decision to list SN8 highlights the increasing institutional interest in specialized blockchain infrastructure. The focus on on-chain performance metrics like Sortino and Omega ratios is particularly noteworthy, showcasing a move towards more sophisticated and data-driven validation of decentralized applications."

The Taoshi Inc., the developer behind Vanta Network, is likely to express enthusiasm for the partnership, seeing it as a pivotal moment in their mission to build a robust and accessible decentralized intelligence platform. Their statement would likely emphasize the shared vision with Kraken in fostering innovation and providing secure, reliable access to cutting-edge digital assets.

Navigating the Risks: A Prudent Approach

It is crucial to acknowledge that participation in decentralized networks, including Vanta Network, inherently involves risks. These can encompass:

  • Smart Contract Risk: Vulnerabilities in the underlying smart contracts could lead to the loss of funds.
  • Market Risk: The value of SN8, like all cryptocurrencies, is subject to significant volatility and market fluctuations.
  • Regulatory Uncertainty: The regulatory landscape for digital assets is constantly evolving, which could impact the future usability and value of SN8.
  • Technical Complexity: While Kraken simplifies access, understanding the intricacies of the Vanta Network and Bittensor ecosystem requires ongoing learning and due diligence.

Kraken, in its announcement, explicitly advises users to deposit tokens only on networks supported by the exchange, warning that deposits made on unsupported networks will be irretrievably lost. This underscores the importance of user education and caution in the digital asset space. Past performance of any asset is not indicative of future results, and potential investors are strongly encouraged to conduct their own thorough research before engaging with SN8 or any other digital asset.

The Future of Asset Listings on Kraken

Kraken’s commitment to expanding its asset offerings is unwavering. The exchange maintains a policy of not disclosing potential future listings until shortly before their official announcement. This approach ensures that each listing meets rigorous standards and provides genuine value to the Kraken community. All currently available tokens can be found on Kraken’s comprehensive support pages, and future additions will be prominently featured on their Listings Roadmap and official social media channels. Kraken’s client engagement specialists are unable to provide information on unannounced assets, maintaining a consistent and transparent listing process.

The arrival of Vanta Network (SN8) on Kraken represents a significant milestone, not just for the Vanta Network itself, but for the broader narrative of decentralized intelligence and its integration into the financial world. As the digital asset landscape continues to evolve, such strategic partnerships promise to unlock new avenues of innovation and investment for a global audience.

July 18, 2026 0 comment
0 FacebookTwitterPinterestEmail
Bitcoin & Altcoins

FTX Announces Fifth Distribution of Approximately $900 Million to Creditors on July 31, 2026

by admin July 18, 2026
written by admin

The FTX Recovery Trust and FTX Trading Ltd. have unveiled plans for their fifth major distribution to creditors, a significant milestone in the ongoing bankruptcy proceedings of the once-dominant cryptocurrency exchange. Scheduled to commence on July 31, 2026, this payout is expected to distribute approximately $900 million to eligible holders of allowed claims, marking one of the most substantial bankruptcy recoveries in the history of the digital asset industry. This development signals continued progress in the complex process of unwinding the affairs of the failed exchange, which collapsed spectacularly in November 2022.

The record date for this distribution has been set for June 16, 2026. This means that only creditors who held allowed FTX claims and interests as of this date, and who have diligently completed all prerequisite requirements, will be eligible to receive funds. These essential pre-distribution steps include successful Know Your Customer (KYC) verification, submission of all necessary tax documentation, and onboarding with one of the FTX estate’s approved distribution service providers. Preferred equity holders will also be included in this distribution, receiving their payments on the same date and subject to the same record cutoff.

Significant Payout Signals Robust Recovery Efforts

The upcoming distribution of $900 million underscores the substantial assets that have been marshaled and recovered by the FTX estate under its new leadership. This amount represents a significant portion of the funds being returned to those who suffered losses following the exchange’s abrupt demise. The FTX estate has been actively engaged in a comprehensive asset recovery strategy, involving the liquidation of various investments, the pursuit of legal claims, and the diligent management of remaining assets.

According to the official press release, the distribution process will be managed by a consortium of FTX’s designated service providers. These include prominent entities such as BitGo, Kraken, and Payoneer, each playing a crucial role in facilitating the secure and efficient transfer of funds. The payouts will be made in U.S. Dollars (USD), offering recipients flexibility. Once the funds are received, eligible creditors will have the option to withdraw the cash directly or, where available, convert it into other digital assets or fiat currencies through their chosen service provider. Crucially, only claims that have been fully allowed and processed by the established record date, and for which any objection periods have concluded without challenge, will qualify for this payout.

Reducing Disputed Claims Reserve Frees Up Additional Capital

In a move designed to expedite the return of capital to creditors, FTX has also filed an amended notice with the court to reduce its disputed claims reserve. This reserve, initially set at approximately $2.4 billion, is slated to be lowered to $1.8 billion. If this reduction is approved by the bankruptcy court, it will effectively free up an additional $600 million in cash. This substantial sum will then be available to bolster the July distribution and contribute to future payouts, further accelerating the recovery process for creditors.

Beyond monetary distributions, the FTX estate is also addressing the recovery of non-fungible tokens (NFTs). Holders of Allowed NFT Customer Entitlement Claims will have the opportunity to initiate the NFT distribution process starting June 30, 2026. This phased approach to asset distribution acknowledges the diverse nature of claims and aims to provide equitable recovery across different asset classes.

The announcement of this fifth distribution round follows the successful completion of the fourth distribution, which took place in March 2026. This consistent schedule of payouts demonstrates the ongoing commitment of the FTX estate’s administrators to systematically returning assets to creditors.

A History of Substantial Recoveries

Prior to this fifth distribution, the cumulative payouts from the FTX estate had already approached or surpassed the remarkable figure of $10 billion. This impressive recovery rate has allowed many creditor classes to reach or even exceed 100% of their allowed claims. Notably, smaller "Convenience Class" claims, often designed for expedited resolution and smaller amounts, have frequently seen recoveries exceeding 100%, sometimes reaching up to 120% when factoring in interest adjustments accrued since the bankruptcy filing. This level of recovery is exceptional for a bankruptcy case of this magnitude.

A critical advisory issued by the FTX estate reiterates the nature of the distribution process. Creditors are reminded that by formally onboarding with a designated Distribution Service Provider, they are making an irrevocable election. This choice signifies their agreement to forego direct cash distributions from FTX and instead directs the estate to pay their entitled distributions to their selected provider. The press release explicitly states: "Customers should be aware that by onboarding with a Distribution Service Provider, they have irrevocably elected to forego their right to receive cash distributions from FTX and have instead directed FTX to pay, directly to such Distribution Service Provider, any distributions to which they otherwise would be entitled to under the Plan." For any inquiries regarding the availability of funds within their chosen provider’s account, creditors are advised to contact the customer support of their respective Distribution Service Provider directly.

The FTX Collapse: A Defining Moment in Crypto History

The impending distribution of nearly $1 billion occurs approximately four years after the seismic collapse of FTX in November 2022. At its peak, FTX was a titan in the cryptocurrency exchange landscape, once valued at an astonishing $32 billion. Its swift downfall was precipitated by a massive shortfall in customer funds, forcing the company to file for Chapter 11 bankruptcy protection. Investigations revealed that FTX had, without proper user consent, allegedly misused customer funds by extending loans to Alameda Research, its affiliated trading firm. At the time of its bankruptcy filing, the exchange held only a fraction of the crypto assets it claimed to possess on behalf of its users; for instance, it reportedly held merely 0.1% of the Bitcoin deposited by customers.

The FTX implosion sent shockwaves through the entire cryptocurrency market, contributing significantly to one of the most pronounced bear markets the sector had experienced. The widespread financial losses incurred by numerous creditors not only devastated individual investors but also intensified regulatory scrutiny on the broader crypto industry.

The fallout from the collapse led to legal repercussions for its founder, Sam Bankman-Fried. He was subsequently convicted on multiple charges of fraud and conspiracy and is currently serving a 25-year sentence in federal prison. The bankruptcy proceedings have been exceptionally complex, involving a global array of assets, extensive litigation, the strategic sale of various holdings, and recoveries from diverse ventures, including significant stakes in companies like Robinhood.

New Leadership and a Path to Substantial Recovery

Under the stewardship of John J. Ray III, a seasoned bankruptcy expert known for his role in the Enron liquidation, the FTX estate has made remarkable progress. Through meticulous asset management and navigating favorable market conditions, the estate has successfully recovered between $14.5 billion and $16 billion. The confirmed Chapter 11 plan has prioritized the recovery of customer assets, with a strong emphasis on achieving full repayment, including interest, for many creditor classes.

The estate’s ability to facilitate such substantial returns highlights the effectiveness of its recovery strategy. Many international customers are reportedly nearing full recovery of their funds, while U.S. customers and certain other creditor classes have already achieved 100% repayment. The estate’s capacity to deliver even more than 100% for smaller claims further illustrates the robust performance of the recovered assets, particularly in light of the market downturn that followed FTX’s collapse.

In March of this year, Sam Bankman-Fried himself made public statements challenging the narrative of fraud, asserting that his exchange always possessed the necessary funds to repay customers. These assertions stand in stark contrast to the legal findings that led to his conviction and imprisonment.

Looking Ahead: The Final Stages of Distribution

The forthcoming $900 million distribution represents a significant step towards the ultimate resolution of the FTX bankruptcy case. While the path has been arduous, marked by complex legal battles and market volatility, the consistent progress in asset recovery and creditor payouts offers a degree of vindication for those affected by the exchange’s collapse. The FTX estate’s administration continues to navigate the intricate process of asset liquidation and distribution, with the ultimate goal of maximizing returns for all legitimate creditors. The success of this operation is being closely watched as a benchmark for future large-scale cryptocurrency bankruptcies.

July 18, 2026 0 comment
0 FacebookTwitterPinterestEmail
Web3 & DApps

Token2049 Singapore 2025: Global Investors Rethink VC Allocation Amidst Post-Hype Cycle Recalibration

by admin July 18, 2026
written by admin

The recent Token2049 Singapore 2025, a premier gathering for the global cryptocurrency and Web3 industry, underscored a significant shift in venture capital allocation strategies. Insights gleaned from the event reveal that investors are actively reassessing their approach to venture capital in the wake of a discernible post-hype cycle. The conference, known for its energetic atmosphere and global attendance, adopted a notably pragmatic tone, with conversations steering away from speculative growth towards core principles of structure, liquidity, and institutional alignment. This recalibration signifies a maturing Web3 venture capital landscape.

Regional Shifts and Evolving Market Sentiment: A Tale of Two Hubs

A key observation from Token2049 Singapore 2025 was a discernible regional rebalancing of attention among venture capital participants. Anecdotal evidence suggested that a significant portion of attendees prioritized Korea Blockchain Week over the Singaporean event this year. This apparent shift can be attributed to a confluence of factors, including burgeoning enthusiasm within South Korea’s burgeoning crypto ecosystem and evolving regulatory landscapes in both regions.

South Korea has been actively formalizing its virtual asset framework, introducing clearer guidelines concerning custody, taxation, and investor protection. This proactive regulatory approach has fostered an environment of increasing confidence and formalization. Conversely, Singapore’s Monetary Authority (MAS) has expanded its licensing regime, imposing registration requirements on even offshore-facing crypto firms operating within its sphere of influence.

The consequence of these differing approaches is a bifurcated regulatory environment. South Korea is signaling a welcoming stance within defined parameters, fostering innovation under a structured framework. Singapore, on the other hand, is implementing stricter filters to ensure long-term market stability and investor protection. These contrasting dynamics provided a significant backdrop to the discussions and overall sentiment at Token2049 Singapore 2025, influencing the tenor of conversations and strategic considerations.

Market Discipline and VC Maturity: The Token2049 Singapore Revelation

Beyond these regional nuances, the venture capital insights shared at Token2049 Singapore 2025 pointed towards a pronounced evolution in market maturity. The effervescent speculative optimism that characterized earlier investment cycles has given way to a more grounded, pragmatic realism. This sentiment, initially hinted at during Token2049 Dubai earlier in the year, was definitively confirmed in Singapore. The Web3 ecosystem is demonstrably recalibrating around data-driven decision-making processes.

VC Insights from Token2049 Singapore 2025

For firms like Outlier Ventures, this evolution is viewed not as a contraction but as a natural progression towards a more robust and sustainable investment paradigm. This shift mirrors the evidence-based discipline that has guided their approach for over a decade. In the current climate, data is increasingly underpinning investment conviction, supplanting the reliance on hype with a more informed and selective allocation strategy.

Capital Concentration and the Dominance of Later-Stage Investments

Preceding Token2049 Singapore 2025, Outlier Ventures’ analysis of Web3 fundraising data for the first half of 2025 had already indicated a slowdown in allocations for pre-seed to Series A funding rounds. In contrast, later-stage rounds continued to command significant investor attention. Conversations with venture capitalists at the conference served to corroborate this trend, revealing a landscape characterized by fewer early-stage deals but a notable increase in the average size of Series B and beyond rounds.

Figure 1 illustrates the percentage of total capital deployed across different funding stages from Q1 2022 to Q3 2025. The data suggests a concentration of capital in later-stage funding rounds.

A primary driver behind this dynamic is the timing of fund deployment. Many venture capital vehicles that successfully raised substantial capital during the market boom of 2020-2021 are now fully allocated. General Partners (GPs) are consequently focusing on managing their existing successful investments and pursuing exit opportunities rather than making new, early-stage bets. The relative scarcity of new fund launches since that peak period has further reinforced this trend. Despite this, investor conviction remains; there is continued support for resilient founders who can demonstrate consistent usage, traction, and revenue growth across various market cycles. This observation is frequently reflected in the portfolios of venture firms, where founders are actively building and adapting rather than waiting for an upturn.

Data-Led Investment and the Imperative of Liquidity Management

Another significant VC insight emerging from Token2049 Singapore 2025 was the enhanced advantage that General Partners (GPs) now possess: data. Four years prior, this data advantage was considerably less pronounced. Today, GPs have access to far more comprehensive information regarding which portfolio sectors have demonstrated resilience, which founders have achieved genuine growth, and which asset classes have outperformed. The strategic redeployment of capital into existing successful investments is no longer viewed as a defensive maneuver but as a rational and data-informed decision.

In response to this evolving market, some GPs have proactively developed over-the-counter (OTC) trading capabilities or established internal liquidity teams. These initiatives enable them to capitalize on investment opportunities that might have been previously missed. This evolution signifies a broader industry shift towards precision investing. At Outlier Ventures, data continues to be the cornerstone of this strategy. Their extensive repository of benchmarks and traction metrics, meticulously gathered over more than a decade of accelerator operations, empowers venture partners to allocate capital with enhanced clarity and conviction.

VC Insights from Token2049 Singapore 2025

Figure 2 depicts trends in Web3 venture capital fund formation and the total capital raised by these funds from Q1 2020 to Q3 2025, highlighting shifts in fundraising activity.

From Momentum to Maturity: A Fundamental Shift in VC Strategy

The discussions at Token2049 Singapore 2025 also featured a candid reflection by many investors on the lessons learned from recent market cycles. The Web3 industry has demonstrably matured through successive phases, moving away from high-risk, speculative bets driven primarily by narrative momentum towards projects that can substantiate measurable traction, consistent revenue growth, and robust underlying fundamentals. The speculative reflex that once defined early Web3 investing has now been supplanted by a more disciplined, data-driven approach—a theme that resonated throughout the conference.

For many Web3 venture capital funds, this transition towards maturity has been a hard-earned process. An overreliance on thematic hype and subsequent disappointment with the performance of certain token launches have led to a reassessment of portfolio value, with greater emphasis now placed on equity holdings. Consequently, exit opportunities have become more elongated, reinforcing a more patient and evidence-based investment mindset among leading investors. This transition, a central topic at Token2049 Singapore, marks a fundamental departure from momentum trading towards conviction rooted in fundamental analysis.

Figure 3 shows Joy Sim, Ecosystem Manager at Outlier Ventures, participating in a discussion at Sonic Summit during Token2049 Singapore 2025, illustrating the active engagement of industry leaders.

The strategic imperative has therefore shifted towards more effective management of liquidity, particularly that recovered from prior market cycles. This renewed discipline has resulted in a reduced appetite for illiquid early-stage exposure. Instead, investors are increasingly seeking to balance their venture portfolios with liquid assets and yield-generating protocols. These strategies serve as crucial hedges against market volatility and ensure that capital remains productively deployed. Discussions at Token2049 Singapore 2025 highlighted this trend, underscoring how sophisticated liquidity management has become a core component of fiduciary responsibility within the Web3 venture ecosystem.

Digital Asset Treasuries (DATs): Liquidity as a Strategic Imperative

Liquidity management emerged as one of the most defining VC insights from Token2049 Singapore 2025, clearly signaling a fundamental shift in how funds approach capital efficiency. This trend is vividly illustrated by the prominent discussions surrounding Digital Asset Treasuries (DATs) both on stage and in informal conversations. The concept of a "DAT Revolution" was even articulated, reflecting the growing significance of these instruments. Initially conceived as an institutional bridge between traditional finance (TradFi) and the cryptocurrency markets, DATs have evolved into highly flexible instruments for short-term capital efficiency. Their increasing adoption is a direct manifestation of the broader market maturity, characterized by an emphasis on flexibility, transparency, and measured deployment over unchecked risk-taking.

VC Insights from Token2049 Singapore 2025

However, this evolution is not without its implications. The greater the allocation of capital towards DATs, the less capital becomes available for early-stage startups. In this context, the success of DATs could inadvertently exacerbate the existing funding squeeze for nascent ventures. Nevertheless, DATs should not be dismissed as a fleeting narrative. Their rise is indicative of a genuine and pressing need for enhanced liquidity, greater optionality, and more responsible treasury management, reflecting a growing financial sophistication rather than mere speculation.

LP Expectations and Headwinds in VC Fundraising

The landscape for raising new Web3 venture capital funds has become increasingly challenging. Limited Partners (LPs) are applying more stringent evaluation criteria, placing a significant emphasis on realized returns, transparency, and robust governance structures. A central VC insight from Token2049 Singapore 2025 was that this increased scrutiny signifies a maturing market rather than a decline in investor interest. While new funds will undoubtedly emerge, the process of closing them is expected to be longer and demand greater demonstrable proof of discipline and data-backed performance.

At Outlier Ventures, this market recalibration aligns seamlessly with their strategic positioning as a vital bridge between institutional capital and early-stage innovation. Leveraging over a decade of data and founder performance benchmarks from nearly 400 portfolio companies, they actively collaborate with VCs, LPs, and ecosystem partners to identify high-quality investment opportunities grounded in verifiable traction and long-term conviction.

Founder Perspective: Navigating Fundraising and Establishing Credibility

As consistently discussed throughout Token2049 Singapore 2025, founders are adapting to this evolving environment with heightened focus and a more pragmatic outlook. Bootstrapping and revenue-first business models have become the prevailing standard. Market participants now expect tangible, meaningful traction from projects before committing capital. Many founders interviewed at the event shared a common sentiment: while narrative may initially capture attention, it is consistent performance that sustains it.

Traditional fundraising mechanisms such as KOL (Key Opinion Leader) rounds or hype-driven launchpads have largely faded in significance. However, new avenues are emerging that prioritize transparency, liquidity, and community trust. Platforms like Virtuals and Hyperliquid, for instance, have gained traction through their fair launch models, offering projects a transparent, market-driven entry point. Concurrently, community-led token rounds facilitated through networks like Echo, Coinlist, and Legion continue to experience growth. These innovative models foster alignment among investors, early adopters, and users through shared long-term incentives, signaling a healthier and more sustainable pathway for capital formation within the Web3 ecosystem.

A Purposeful Recalibration for Venture Capital: Concluding Thoughts on Token2049 Singapore 2025

VC Insights from Token2049 Singapore 2025

Taken in aggregate, the VC insights gleaned from Token2049 Singapore 2025 illuminate a venture ecosystem entering a phase of deliberate and purposeful transformation. The industry is not contracting; it is maturing. Investors are assiduously balancing liquidity considerations with long-term investment conviction, LPs are demanding greater clarity on metrics and governance, and founders are adapting to a higher standard of validation before seeking capital.

While the rise of DATs and the concentration of capital in later-stage investments may pose challenges for early-stage activities, these trends also exemplify a market that is learning from past experiences and refining its inherent discipline. Token2049 Singapore 2025 effectively captured this profound shift in sentiment: a move from spectacle towards substance, and from momentum-driven speculation towards rigorous measurement.

The overarching message is unequivocally clear. Liquidity discipline, operational maturity, and demonstrated product-market fit have decisively replaced unchecked exuberance as the new definitive signals of strength. For seasoned investors, data-driven funds, and resilient founders who embrace this paradigm shift, this period represents not a downturn but a foundational stage for sustainable, long-term growth. The Web3 venture ecosystem is transitioning from a focus on narrative to one of necessity, and those entities prepared to meet this elevated standard will undoubtedly shape its future trajectory.

The Outlier Ventures team’s key VC insights from Token2049 Singapore 2025 underscore a venture capital landscape entering a phase of deliberate evolution, prioritizing substance, data, and sustainable growth over speculative hype.

Recruiting Now: Injective Ecosystem Builder Catalyst

Investors are increasingly backing sharper narratives, more robust infrastructure, and founders adept at aligning with powerful, established ecosystems. This precisely aligns with the objectives of the Injective Ecosystem Cohort. Whether building the next generation of DeFi protocols, facilitating cross-chain liquidity, or innovating at the cutting edge of trading, derivatives, and decentralized infrastructure, the program is designed to empower early-stage teams to translate conviction into tangible traction within one of Web3’s most dynamic ecosystems. Applications for this transformative initiative are currently open.

July 18, 2026 0 comment
0 FacebookTwitterPinterestEmail
Cryptography & Privacy

Unraveling the Mysteries of Encrypted Reasoning Blobs: A Deep Dive into LLM API Vulnerabilities

by admin July 18, 2026
written by admin

A recent deep dive into the intricate workings of Large Language Model (LLM) APIs, specifically focusing on the reasoning capabilities of models like OpenAI’s GPT and Anthropic’s Claude, has brought to light potential security implications previously overlooked by many developers and users. This exploration, initiated as a weekend hobby project, has revealed that the "thinking" or "reasoning" data generated by these advanced AI systems, when transmitted to the client application, is not merely an opaque black box but carries potential vulnerabilities related to replayability and side-channel leakage. While not exposing a critical system-breaking flaw, the findings offer a nuanced understanding of how LLM architecture might inadvertently expose sensitive information.

The Genesis of an Investigation: An Intriguing Error Message

The investigation began with an unexpected encounter during the setup of an OpenClaw agent, a sophisticated AI application. While the immediate utility of another AI in the author’s personal life was questionable, the configuration process exposed a peculiar error message. This message contained a digital signature within what was described as the LLM’s "thinking" block. This anomaly immediately piqued the interest of a cryptographer, raising fundamental questions: Why would an AI’s internal reasoning process be signed? What security implications arise if these reasoning blocks are indeed subject to tampering? This curiosity set the stage for an extensive weekend of analysis, involving approximately 5 million tokens processed by Codex.

Let’s talk about encrypted reasoning

Decoding the "Encrypted Reasoning" Mechanism

At the core of the discovery lies a feature of LLM APIs that is often not explicitly highlighted: the transmission of the model’s internal reasoning process, commonly referred to as "chain-of-thought" (CoT). While users interacting with models like ChatGPT see summarized outputs, the underlying API for developers often includes a hidden, encrypted copy of the raw CoT data. This data is sent to the client application as a JSON object, containing Base64-encoded strings. Documentation from providers like OpenAI and Anthropic indicates that this data is intended to be opaque, not for direct inspection, but rather to be sent back to the server in subsequent turns to maintain conversational context, especially in stateless or zero-retention environments.

However, upon closer examination, these encoded strings exhibit characteristics of authenticated ciphertexts. Their size fluctuates based on the complexity of the model’s reasoning, and any attempt to alter them results in a recognizable API error. This suggests a cryptographic layer designed to ensure the integrity and authenticity of the reasoning process as it’s passed between the server and the client.

  • OpenAI’s Reasoning Blocks: Analysis suggests that OpenAI’s reasoning blocks may be based on a standard like Fernet tokens, comprising various opaque fields that mutually authenticate each other. While modifications to individual fields are prevented, other aspects can be altered. The presence of 12-byte Initialization Vectors (IVs) hints at the use of encryption algorithms like GCM or ChaCha, although the IV length might be considered short.
  • Anthropic’s Reasoning Blocks: Anthropic’s implementation, while also involving authenticated ciphertexts, appears more complex. Notably, despite being labeled as a "signature," empirical testing indicated no actual cryptographic signature was present. The system primarily focuses on mutual authentication of opaque fields, preventing manipulation of individual components while allowing for modifications elsewhere. The IV lengths here also suggest similar encryption primitives.

The "Why" Behind the Encrypted Transmissions

The rationale for sending this encrypted reasoning data to the client, rather than keeping it entirely server-side, is rooted in the operational design of modern LLM APIs. In scenarios employing stateless, zero-retention, tool-loop, or client-managed conversation modes, the client application is responsible for maintaining the conversation history. Encrypted reasoning allows LLM providers to return hidden model states to the client in a format that is unreadable and unmodifiable by the client, yet verifiable and decryptable by the server upon replay. This ensures continuity in complex reasoning processes without compromising the integrity of the model’s internal state.

Let’s talk about encrypted reasoning

The "So What?": Potential Vulnerabilities

The implications of these encrypted reasoning blobs, though not immediately catastrophic, warrant careful consideration. The cryptographic protections generally prevent direct manipulation. However, two key areas of potential vulnerability have been identified:

1. Replayability of Reasoning Blobs

A significant finding is the ability to replay unmodified reasoning blocks. While direct tampering triggers API errors, unaltered blocks can be replayed without issue. This replayability extends beyond a single session, working across different accounts and even different models within OpenAI’s ecosystem (though Claude models proved more resistant).

From a cryptographic standpoint, this suggests the potential use of a single, global encryption key for all reasoning data transmitted to clients. This has implications for zero-data retention modes, as all users’ reasoning data could be escrowed under a single, infrequently changing key, rather than being protected on a per-account basis.

Let’s talk about encrypted reasoning

Furthermore, this replayability introduces a new threat vector for applications that expose chat interfaces to potentially malicious users. If an attacker can inject crafted JSON into the chat stream, they might be able to insert their own reasoning blobs, leading to unpredictable model behavior. This underscores the critical need for input sanitization in such applications.

While replayed blocks are accepted by the LLM, their "semantic activity"—whether the model truly processes and acts upon the decrypted data—can vary. Extensive experimentation with Codex revealed that while replayed blocks are often quietly absorbed, in some instances, models like GPT 5.5 demonstrably incorporate the replayed information. For example, one experiment showed a replayed reasoning block leading to the appearance of a specific number in a new session on a different account, raising questions about data persistence and inter-session influence. This confirmed that encrypted blocks can indeed be semantically active, although extracting actionable sensitive data remains challenging.

2. Side-Channel Leakage Through Reasoning

Beyond direct replay, the author explored whether metadata associated with reasoning blocks could be exploited as a side channel for data extraction. This includes observable signals such as the length of the reasoning blocks, token counts (like OpenAI’s reasoning_tokens field), and even wall-clock response times.

Let’s talk about encrypted reasoning

The hypothesis posits that if an LLM is instructed to keep a secret (e.g., a single bit or a string) from the user, but is allowed to reason about it internally, the computational complexity of that reasoning could leak information. For instance, a scenario where computing the bit as ‘1’ requires significantly more processing than computing it as ‘0’ would manifest as differences in reasoning block size, token counts, or response times.

An experiment was designed where a model was asked to compute a checksum when a secret bit was ‘1’. By analyzing the size of the reasoning blobs or the response times, it was possible to distinguish between the ‘0’ and ‘1’ states of the secret bit with a high degree of accuracy. This demonstrates that reasoning processes themselves can be inherently "leaky," even when the model is instructed not to reveal sensitive information directly. This signal is particularly concerning as it could potentially be extracted even from chat-only interfaces where direct access to encrypted blobs is not available.

The Pursuit of Platform Secrets

A more ambitious goal was to determine if this side-channel leakage could be leveraged to extract highly sensitive "platform secrets," such as the models’ top-secret system prompts—the underlying instructions that govern their behavior and safety protocols. This would involve a painstaking process of asking true/false questions about successive characters of the prompt.

Let’s talk about encrypted reasoning

However, this line of inquiry encountered significant resistance. Tools like Codex and Claude Code, after identity verification, actively refused to assist in extracting confidential information. Switching to OpenCode with Kimi 2.6, which exhibited fewer ethical qualms, yielded mixed results. While application-specific secrets that were deliberately embedded could be extracted, attempts to extract non-existent or non-embedded model prompts proved unsuccessful. The author concluded that while extracting embedded secrets is feasible, extracting system prompts that are not actively being reasoned about remains a "maybe," highlighting the need for providers to carefully consider the implications of their reasoning data.

Responses and Recommendations from LLM Providers

The findings were reported to OpenAI and Anthropic through their respective bug bounty programs. OpenAI initially deemed the report unreproducible, and while the author provided scripts, it was too late to rectify the situation. Anthropic acknowledged the findings but reasonably concluded that there were no significant security implications in the observed side channels or replayability. They indicated a potential update to their developer documentation to caution application developers about these aspects. Both providers granted permission to publish these findings.

Despite these responses, the author maintains that LLM providers should not dismiss these observations entirely.

Let’s talk about encrypted reasoning

Recommendations for Providers:

  • Enhanced Key Management: Providers should proactively improve their key management practices. If reasoning state is deemed valuable enough for encryption, it should be properly secured. Reasoning data should not be replayable across sessions or accounts. Patching potential vulnerabilities before they are exploited is crucial.
  • Addressing Side-Channel Leakage: The side-channel leakage is a more fundamental issue tied to the nature of model reasoning. If models can be induced to perform secret-dependent reasoning, leakage is almost inevitable. Future mitigation might involve implementing policy gates before models engage in reasoning about sensitive information. However, this itself presents a challenge, as policy enforcement often requires reasoning.

The author concludes by expressing a degree of relief that such complex issues fall outside the purview of a cryptographer, highlighting the intricate challenges faced by those responsible for the security and integrity of advanced AI systems. The exploration of encrypted reasoning blobs underscores the evolving landscape of AI security, where even seemingly opaque internal processes can harbor subtle vulnerabilities that require ongoing vigilance and innovative solutions.

July 18, 2026 0 comment
0 FacebookTwitterPinterestEmail
Web3 & DApps

Visa Unveils Stablecoin Platform, Empowering 15,000 Banks and 200 Million Merchants to Mint and Move Digital Assets

by admin July 18, 2026
written by admin

Visa’s strategic move into the stablecoin ecosystem has reached a new apex with the launch of its proprietary Visa Stablecoin Platform. This groundbreaking initiative empowers the company’s vast network of approximately 15,000 financial institutions and over 200 million merchants worldwide to mint and transfer stablecoins, integrating these digital assets seamlessly into their existing payment and treasury operations. The platform debuts with Open Standard’s OUSD, a dollar-pegged stablecoin that represents a significant step towards mainstream adoption of cryptocurrency within traditional finance. This development signals a pivotal shift for Visa, moving beyond simply processing stablecoin settlements to actively facilitating their creation and movement across its global network.

The Visa Stablecoin Platform is designed to demystify and streamline the integration of stablecoins for Visa’s extensive client base. By offering a dedicated infrastructure, Visa aims to accelerate the adoption of this nascent technology, making it accessible and practical for businesses of all sizes. Rubail Birwadker, Visa Global Head of Growth, emphasized the platform’s core objective: to connect stablecoins directly to clients’ treasury, settlement, and money-movement operations. This integration is crucial for unlocking the full potential of stablecoins, which offer the promise of faster, cheaper, and more efficient cross-border transactions compared to traditional fiat currencies. The platform’s architecture is built to encompass all of Visa’s current and future stablecoin services, ensuring a unified and robust offering.

This launch is not an isolated event but rather the culmination of years of strategic investment and exploration by Visa in the digital asset space. The payments giant was an early adopter, becoming the first major payments network to settle a transaction using USDC (USD Coin) in 2020. Since then, Visa has systematically expanded its stablecoin support across multiple blockchain networks, demonstrating a clear and consistent commitment to leveraging blockchain technology. This proactive approach has positioned Visa as a leader in bridging the gap between traditional finance and the burgeoning world of cryptocurrencies. The introduction of the Visa Stablecoin Platform represents the natural evolution of this strategy, transforming Visa from a facilitator of stablecoin transactions to a provider of comprehensive stablecoin infrastructure.

A New Era for Stablecoin Integration

The Visa Stablecoin Platform’s debut with Open Standard’s OUSD is a significant endorsement of the open-source stablecoin initiative. Open Standard, unveiled in late June, is a consortium backed by a formidable coalition of over 140 companies, including industry titans like Visa, Mastercard, and BlackRock. This broad support underscores a collective industry recognition of the need for standardized, interoperable stablecoin solutions. OUSD, as the initial offering on Visa’s platform, complements other stablecoins already supported by Visa, such as Circle’s USDC and Paxos’ USDG. This strategic inclusion of OUSD signals Visa’s commitment to an open and diverse stablecoin ecosystem, fostering competition and innovation.

The broader implications of this partnership are profound. Rivals Mastercard and American Express have also aligned themselves with Open Standard, indicating a unified push across major payment networks towards stablecoin integration. Mastercard, for instance, has already begun enabling banks to settle card transactions using six dollar-backed stablecoins. This coordinated effort by industry leaders suggests a concerted effort to establish stablecoins as a viable and integral part of the global financial infrastructure. The Visa Stablecoin Platform, by providing a ready-made infrastructure, significantly lowers the barrier to entry for financial institutions and merchants looking to engage with stablecoins.

The Strategic Imperative: Efficiency and Innovation

Visa’s foray into stablecoins is driven by a clear strategic imperative: to enhance the efficiency and reduce the cost of global payments. Traditional cross-border transactions often involve multiple intermediaries, complex reconciliation processes, and significant delays, leading to higher fees and reduced speed. Stablecoins, by leveraging blockchain technology, offer the potential to bypass many of these inefficiencies. They can be transferred directly between parties, often within minutes, and at a fraction of the cost of traditional wire transfers.

For Visa, this translates into an opportunity to solidify its position as a central player in the future of payments. By enabling its vast network to utilize stablecoins, Visa is not only offering a new product but also creating new revenue streams and strengthening its relationships with its existing client base. The ability for merchants to accept payments in stablecoins, and for banks to manage their liquidity and settlements using these digital assets, offers tangible benefits in terms of cost savings and operational agility.

Visa Launches Stablecoin Platform With OUSD Integration for Banks and Fintechs

Background: The Evolution of Stablecoins and Visa’s Role

The concept of stablecoins emerged as a response to the inherent volatility of many cryptocurrencies. Unlike Bitcoin or Ethereum, stablecoins are designed to maintain a stable value, typically pegged to a fiat currency like the US dollar. This stability makes them ideal for use in transactions and as a store of value, bridging the gap between the speculative nature of cryptocurrencies and the practical needs of commerce.

Visa’s engagement with this space began long before the formal launch of the Stablecoin Platform. Key milestones include:

  • 2020: Visa’s pioneering transaction settlement using USDC marked a significant moment, demonstrating the viability of stablecoins for large-scale financial operations.
  • Ongoing Expansion: Visa has consistently broadened its stablecoin support, integrating with various blockchain networks and exploring different stablecoin protocols. This continuous development has built the technical and operational expertise necessary for the current platform launch.
  • Strategic Partnerships: Collaborations with companies like Circle, which issues USDC, and now with the Open Standard consortium, highlight Visa’s approach of working with key players in the crypto ecosystem to drive innovation.

The establishment of Open Standard itself is a response to the evolving landscape of digital assets. By bringing together a diverse group of stakeholders, Open Standard aims to create a more unified and predictable environment for stablecoin development and usage. The involvement of major financial institutions like Visa, Mastercard, and BlackRock lends significant credibility to this endeavor, signaling a shift from niche adoption to mainstream integration.

Data and Supporting Evidence

The scale of Visa’s network underscores the potential impact of the Stablecoin Platform:

  • 15,000 Financial Institutions: This encompasses a vast array of banks, credit unions, and other financial service providers globally, each with their own treasury and payment needs.
  • 200 Million Merchants: This represents a colossal merchant base, from small businesses to large enterprises, all of whom could potentially benefit from faster, cheaper payment settlement options.
  • Billions in Stablecoin Settlements: Visa has already been processing substantial volumes of stablecoin settlements, indicating a proven demand and operational capability. The new platform aims to exponentially grow this figure.

The introduction of OUSD as the initial offering is noteworthy. As a stablecoin developed by a consortium of established players, it aims to address concerns around transparency and regulatory compliance that have sometimes plagued other stablecoins. The fact that Visa, Mastercard, and BlackRock are all partners in Open Standard suggests a shared vision for how stablecoins should be developed and deployed within the financial system.

Broader Impact and Future Implications

The Visa Stablecoin Platform is poised to have a transformative impact on several fronts:

  • Increased Efficiency for Businesses: Merchants can potentially receive payments faster and at a lower cost, improving cash flow and reducing operational expenses. This is particularly beneficial for cross-border transactions where traditional settlement times and fees can be prohibitive.
  • Enhanced Treasury Management: Banks and corporations can utilize stablecoins for more efficient liquidity management, interbank settlements, and programmatic payments. This could lead to significant cost savings and improved capital allocation.
  • Accelerated Mainstream Adoption: By integrating stablecoins directly into familiar payment workflows, Visa is making digital assets more accessible to a wider audience. This can demystify cryptocurrencies and encourage broader adoption beyond early adopters and crypto enthusiasts.
  • Innovation in Financial Services: The platform opens doors for new financial products and services built on stablecoins, such as tokenized assets, decentralized finance (DeFi) integrations, and programmable money solutions.
  • Competitive Landscape: The move by Visa will undoubtedly intensify competition among payment networks and financial technology companies in the stablecoin space. It may also spur further innovation from other established players and the broader crypto industry.

Official Responses and Industry Reactions

While the initial announcement came from Visa, the broader industry reaction is anticipated to be overwhelmingly positive, albeit with varying degrees of strategic response.

  • Visa’s Stance: As articulated by Rubail Birwadker, Visa sees this as a natural progression in its mission to modernize payments and provide innovative solutions to its clients. The company’s consistent investment in blockchain and digital assets reinforces this narrative.
  • Open Standard Partners: Companies like Mastercard and BlackRock, being partners in Open Standard, are likely to view this launch as a validation of their collaborative approach. Their own initiatives in the stablecoin space suggest a coordinated effort to shape the future of digital finance.
  • Fintechs and Developers: The platform offers a significant opportunity for fintech companies and developers to build new applications and services on top of Visa’s robust infrastructure. This could lead to a surge in innovation within the payments and digital asset sectors.
  • Regulatory Scrutiny: As stablecoins become more integrated into mainstream finance, regulatory bodies worldwide will likely increase their scrutiny. Visa’s emphasis on established stablecoins and its extensive compliance infrastructure may help navigate these regulatory waters, but ongoing dialogue and collaboration with regulators will be crucial.

Conclusion

The launch of the Visa Stablecoin Platform marks a pivotal moment in the integration of digital assets into the global financial system. By empowering its extensive network of banks and merchants to mint and move stablecoins, Visa is not just facilitating transactions but actively building the infrastructure for the future of payments. The strategic choice to debut with OUSD, backed by a broad industry consortium, underscores a commitment to open, standardized, and interoperable solutions. As Visa continues to build upon this foundation, the implications for financial efficiency, innovation, and the broader adoption of cryptocurrencies are immense, promising a more connected and dynamic financial landscape. This move solidifies Visa’s position as a key architect of the evolving digital economy, demonstrating its foresight and commitment to staying at the forefront of financial technological advancements.

July 18, 2026 0 comment
0 FacebookTwitterPinterestEmail
FinTech Innovations

FinovateFall 2025’s Best of Show Winners: A Year of Innovation and Market Impact

by admin July 18, 2026
written by admin

Last year’s FinovateFall conference, a premier event for the fintech and banking industries, brought together a global cohort of innovators, financial institutions, and industry experts. Held as a pivotal platform for showcasing cutting-edge solutions, the conference culminated in recognizing the most impactful technologies. On the second day of FinovateFall 2025, 63 companies presented their latest advancements to an engaged audience. From this impressive lineup, six fintech companies were awarded "Best of Show" honors for their groundbreaking presentations. As FinovateFall 2026 approaches, scheduled for September 9th through 11th, it is opportune to examine the trajectory of these distinguished winners and their subsequent influence on the financial technology landscape. This report delves into the developments and market contributions of Casap, Eko, Krida, LemonadeLXP, LendAPI, and Vertice AI since their recognition at the 2025 event.

The Finovate series of conferences has long served as a crucible for fintech innovation, providing a unique stage where emerging technologies are unveiled and vetted by a discerning audience of financial professionals. These events are characterized by rapid-fire demonstrations, where companies have a limited time to showcase the core value proposition of their solutions. The "Best of Show" award is not merely a mark of recognition; it often signifies a company’s readiness to address pressing industry challenges and its potential to drive significant change. FinovateFall, specifically, targets the North American market, focusing on solutions relevant to banks, credit unions, and other financial service providers. The 2025 edition was no exception, highlighting the evolving needs of the financial sector, from enhancing customer experience and operational efficiency to mitigating fraud and expanding access to financial products.

Casap: Revolutionizing Dispute Resolution with AI

Casap secured its "Best of Show" award at FinovateFall 2025 for its sophisticated AI-powered platform designed to transform the way financial institutions manage disputes. The company’s presentation demonstrated how its technology automates the complex and often labor-intensive process of dispute resolution, a critical area for both customer satisfaction and financial risk management. By leveraging artificial intelligence, Casap aims to reduce fraud losses, expedite resolution timelines, and ultimately strengthen the relationship between financial institutions and their customers.

Since its recognition, Casap has continued to refine and expand its dispute automation platform, delivering tangible results for its clients. The company reports impressive customer outcomes, including a remarkable 97% chargeback win rate, a 51% reduction in fraud losses, and a significant 40% decrease in call volumes. These metrics underscore the platform’s efficacy in streamlining operations and mitigating financial exposure. Further validating its innovative approach, Casap participated in Filene’s FiLab program earlier this year. This initiative involved credit unions evaluating Casap’s AI capabilities in reducing manual workloads and enhancing member experiences during fraud disputes. Such evaluations are crucial in the credit union space, where member service and operational efficiency are paramount. The success in these programs indicates a strong market fit and a growing acceptance of AI-driven solutions in traditionally conservative financial sectors. The implications of Casap’s technology are far-reaching, promising to alleviate a significant pain point for financial institutions and improve the security and trust for consumers.

Eko: Embedding Investing for Enhanced Digital Banking

Eko’s "Best of Show" win at FinovateFall 2025 was attributed to its innovative approach to embedded investing. The company’s demonstration highlighted how integrating investment capabilities directly into digital banking platforms can significantly boost engagement, foster deposit growth, and improve customer retention for financial institutions. This strategy addresses a growing consumer demand for seamless financial management, where users expect to handle all their financial needs within a single, convenient digital environment.

Following its success at the conference, Eko has experienced substantial growth in its embedded investing platform. The company has secured additional deployments with financial institutions, notably including Brooklyn Cooperative Federal Credit Union. Eko’s core mission remains focused on empowering banks and credit unions to offer integrated investing solutions. By embedding these services directly within their digital banking interfaces, these institutions can offer a more holistic customer experience, preventing customers from being redirected to external brokerage platforms. This approach not only enhances customer loyalty but also allows financial institutions to capture a larger share of their customers’ financial lives. The trend towards embedded finance is a significant one, and Eko is positioned at the forefront, enabling traditional financial players to compete more effectively in an increasingly digital-first world. The ability to offer investment services without the complexity of building entirely new infrastructure is a compelling proposition for many banks and credit unions.

Krida: Accelerating Loan Origination with Automation

Krida’s "Best of Show" recognition stemmed from its demonstration of technology designed to dramatically shorten lending cycle times, reduce manual intervention, and minimize borrower drop-off rates. Their solution empowers banks to originate loans more rapidly while simultaneously enhancing customer relationships. In the competitive landscape of lending, speed and efficiency are critical differentiators, and Krida’s platform addresses these needs directly.

While Krida has maintained a relatively low public profile since its award, the company has continued its dedicated development of its lending automation platform. The focus remains on streamlining the loan origination and underwriting processes, particularly for community financial institutions. These institutions often face resource constraints and are looking for effective ways to compete with larger banks and fintech lenders. Krida’s technology promises to deliver these efficiencies, allowing them to process more loans with greater accuracy and speed. The ongoing development suggests a commitment to refining its offerings and preparing for broader market adoption. The ability to reduce the time it takes from loan application to approval can have a profound impact on a financial institution’s revenue and its ability to serve its community effectively.

LemonadeLXP: Elevating Employee and Customer Knowledge with AI

LemonadeLXP earned its "Best of Show" award for InsightAI, a platform that leverages AI to enhance employee education, deepen customer understanding, and improve operational efficiency within financial institutions. The company’s presentation underscored the transformative power of AI in learning and development, enabling organizations to cultivate more knowledgeable employees and deliver superior customer interactions.

In the year since its win, LemonadeLXP has significantly invested in its AI-powered employee enablement solutions and has strategically expanded its leadership team. A key development was the launch of AI Conversations in November, an innovative AI-powered voice conversation training tool. This tool is designed to equip employees with the confidence and skills to handle customer interactions effectively, turning them into more trusted advisors. By simulating real-world scenarios, AI Conversations allows employees to practice and refine their communication skills in a safe, controlled environment. This focus on upskilling the workforce is crucial for financial institutions seeking to differentiate themselves through exceptional customer service. The ability to create more competent and confident employees translates directly into better customer experiences and stronger relationships, a vital component in today’s competitive market. The integration of AI into employee training represents a forward-thinking strategy to address the evolving demands of the financial services industry.

LendAPI: Building Collaborative Lending Infrastructure for the Future

LendAPI was recognized with a "Best of Show" award for its collaborative platform, which empowers technology, risk, and compliance teams to jointly develop lending products on a unified infrastructure. This approach fosters greater synergy and efficiency in product development, breaking down traditional silos within financial organizations.

LendAPI has continued to advance its embedded finance platform, strategically positioning itself for the anticipated rise of agentic AI in lending. The company achieved a significant milestone at the beginning of the year, surpassing 100 million credit applications processed globally on its platform. This impressive volume demonstrates the scalability and robustness of their technology. Further solidifying its market presence, LendAPI has strengthened its leadership team with key appointments and has launched innovative solutions, including instant commercial DDA (Demand Deposit Account) onboarding specifically for credit unions. Additionally, the company joined an accelerator program, indicating a commitment to fostering innovation and collaboration within the financial ecosystem. LendAPI’s focus on a shared infrastructure for lending product development aligns with the industry’s move towards more agile and integrated financial services. As the financial landscape evolves, platforms that facilitate seamless collaboration and rapid product iteration will become increasingly valuable. The processing of over 100 million applications signifies a proven track record and the trust placed in their platform by numerous institutions.

Vertice AI: Driving Customer Growth Through Personalized AI

Vertice AI’s "Best of Show" award acknowledged its AI-powered customer growth platform, which translates customer data into highly personalized product recommendations and targeted marketing campaigns for community financial institutions. This solution addresses the critical need for financial institutions to understand and engage their customers on an individual level in order to drive growth and loyalty.

Since its win, Vertice AI has built considerable momentum around its AI-driven personalization platform. Just one month after receiving the award, the company announced the availability of Vertice AGENT, its interactive copilot designed to empower credit unions in driving growth. This tool acts as an intelligent assistant, helping institutions leverage data to identify opportunities and execute targeted growth strategies. In February, Vertice AI further strengthened its capabilities by forming a strategic partnership with Ceto. This collaboration aims to enhance personalized growth initiatives for community financial institutions, combining Vertice AI’s data-driven personalization with Ceto’s expertise. The company’s proactive development and strategic alliances underscore its commitment to providing innovative solutions that help community financial institutions compete effectively by leveraging the power of data and AI. The ability to offer personalized recommendations and campaigns can significantly increase conversion rates and customer lifetime value, a crucial objective for any business.

Looking Ahead: FinovateFall 2026 and the Future of Fintech

As FinovateFall 2026 prepares to open its doors in New York from September 9th to 11th, the focus will once again be on the next wave of fintech innovators. The success stories of the 2025 "Best of Show" winners serve as a compelling testament to the transformative power of technology in the financial sector. These companies have not only showcased groundbreaking solutions but have also demonstrated their ability to execute and deliver tangible value to financial institutions and their customers. The continued evolution of AI, embedded finance, and data-driven personalization, as exemplified by these winners, suggests a future where financial services are more accessible, efficient, and customer-centric than ever before. Industry observers and participants are eagerly anticipating the innovations that will be unveiled at the upcoming conference, recognizing FinovateFall as a critical barometer of the fintech industry’s direction and potential. Attendees can still secure exclusive hotel discounts by booking their rooms before August 17th, underscoring the urgency and anticipation surrounding this key industry event. The ongoing dialogue and innovation fostered at FinovateFall are instrumental in shaping the future of finance, driving progress, and creating a more inclusive and effective financial ecosystem for all.

July 18, 2026 0 comment
0 FacebookTwitterPinterestEmail
Newer Posts
Older Posts

Recent Posts

  • How native transaction assertions could enforce a transaction’s final outcome
  • Kraken Officially Lists NEXO Token, Expanding Access to the Digital Asset Wealth Platform Ecosystem
  • Crypto.com and OG.com Revolutionize US Derivatives Market with Regulated Crypto Perpetual Contracts
  • Beyond the Seed Phrase: How Smart Wallets and AI Agents Are Redefining Digital Personhood in the Post Web
  • Why Artificial Intelligence Might Make Software Too Secure for Law Enforcement Surveillance

Recent Comments

No comments to show.
  • Facebook
  • Twitter

@2021 - All Right Reserved. Designed and Developed by PenciDesign


Back To Top
Dr Crypton
  • Home
  • About Us
  • Contact Us
  • Cookies Policy
  • Disclaimer
  • DMCA
  • Privacy Policy
  • Terms and Conditions

We are using cookies to give you the best experience on our website.

You can find out more about which cookies we are using or switch them off in .

Dr Crypton
Powered by  GDPR Cookie Compliance
Privacy Overview

This website uses cookies so that we can provide you with the best user experience possible. Cookie information is stored in your browser and performs functions such as recognising you when you return to our website and helping our team to understand which sections of the website you find most interesting and useful.

Strictly Necessary Cookies

Strictly Necessary Cookie should be enabled at all times so that we can save your preferences for cookie settings.