• Home
  • About Us
  • Contact Us
  • Cookies Policy
  • Disclaimer
  • DMCA
  • Privacy Policy
  • Terms and Conditions
Dr Crypton
Secure Your Future in Crypto
Tech & Startup News

AI Coding Tools Drive Up U.S. Healthcare Spending by Nearly $1 Billion, BCBSA Report Reveals

by admin September 26, 2026
written by admin

The intersection of artificial intelligence and modern healthcare administration has reached a critical flashpoint. According to a comprehensive analysis released by the Blue Cross Blue Shield Association (BCBSA) in September 2026, the implementation of artificial intelligence tools by hospitals for insurance claims submission has driven an additional $942 million in healthcare expenditures over a two-year period. This staggering financial impact highlights a growing structural tension within the American healthcare ecosystem, where automated systems deployed by providers to maximize reimbursement are clashing with the automated review mechanisms utilized by insurance payers.

The findings underscore a broader, systemic transformation in how medical billing is conducted. As hospitals increasingly adopt machine learning and advanced algorithms to parse electronic health records and assign billing codes, they are unlocking new pathways for revenue generation. However, this technological leap has triggered intense scrutiny from insurers, policy analysts, and healthcare economists, who question whether the surge in billed complexity genuinely reflects patient health outcomes or merely represents aggressive, algorithmically driven documentation practices.

The Mechanics of Medical Coding and the Rise of AI

To understand the financial implications of the BCBSA report, one must examine the foundational role of medical coding in the U.S. healthcare system. Hospitals and medical practices rely on standardized coding systems—such as the International Classification of Diseases (ICD) and Current Procedural Terminology (CPT)—to translate clinical documentation into billable claims submitted to insurance providers.

Historically, this has been a labor-intensive, human-led process prone to human error, missed diagnoses, and under-coding, which could result in lost revenue for healthcare institutions. In recent years, however, hospitals have turned to sophisticated artificial intelligence and natural language processing (NLP) tools. These technologies scan thousands of pages of patient charts in seconds, identifying potential secondary diagnoses, comorbid conditions, and hierarchical condition categories (HCCs) that might have been overlooked by human administrative staff.

By leveraging these AI systems, hospitals can optimize their claims, ensuring they receive maximum allowable reimbursement for the care provided. Yet, the BCBSA analysis points to a troubling divergence between the administrative documentation generated by these tools and the actual clinical care delivered to patients.

Key Findings of the Blue Cross Blue Shield Association Analysis

The BCBSA analysis scrutinizes the two-year period following the widespread adoption of generative AI and automated coding software in hospital administration. The core finding of the study reveals a sharp, unprecedented increase in patients being documented as suffering from complex, high-severity conditions.

Despite this dramatic surge in recorded medical complexity, the association’s researchers found no corresponding evidence of a change in the actual clinical care delivered to those patients. In practical terms, hospitals were documenting sicker patient populations on paper and digital claims forms, yet treatment protocols, lengths of stay, medication administration, and resource utilization remained statistically flat.

This disconnect has profound financial consequences. Under modern risk-adjustment and fee-for-service models, higher-complexity codes command significantly higher reimbursements from insurers, both public and private. The cumulative effect of these inflated code assignments across millions of patient encounters accounts for the $942 million spike in healthcare spending identified by the BCBSA over the studied timeframe.

The Macro Context: Bot vs. Bot in Healthcare Administration

The financial fallout from AI-driven medical coding does not exist in a vacuum. It represents the latest escalation in a long-standing, adversarial relationship between healthcare providers and insurance companies. Disputes over coverage denials, prior authorizations, and delayed payments have historically strained relations between the two pillars of the U.S. medical industry.

However, industry observers point out that the integration of artificial intelligence by both sides has accelerated the conflict. While hospitals deploy algorithms to optimize billing and overturn claim denials, insurance companies increasingly rely on automated algorithms and predictive models to screen, flag, and deny claims en masse.
Insurers claim AI is already increasing healthcare costs

This technological arms race has prompted stark warnings from industry leaders. Dr. Shiv Rao, founder of the medical AI startup Abridge, addressed the phenomenon during industry discussions, noting the very real risk of entering a "horrible dystopic future nobody wants to live in," characterized by "bots fighting bots, agents fighting agents." Dr. Rao suggested that while automated agents hold the potential to reduce friction and administrative overhead if properly aligned, their current deployment risks intensifying administrative warfare at the expense of patient care.

Conversely, representatives for the insurance sector argue that the imbalance favors well-resourced hospital systems wielding advanced software. Luke Chalker, Senior Vice President at the BCBSA, rejected characterizations of the dynamic as a balanced negotiation, describing the current landscape not as a war, but as a "completely one-sided blood bath" with insurance providers—and by extension, the premium-paying public—bearing the brunt of the financial loss.

Economic and Policy Implications

The financial expansion documented by the BCBSA carries significant implications for the broader American economy. Healthcare spending in the United States already surpasses that of any other developed nation, accounting for nearly 18% of the nation’s Gross Domestic Product (GDP). Administrative costs represent a massive portion of these expenditures, often cited by economists as a key driver of inefficiency.

While proponents of healthcare AI initially touted the technology as a panacea for administrative bloat—promising to reduce the billions of dollars spent annually on manual paperwork—the current reality is more complex. Rather than lowering administrative overhead, AI tools appear to be increasing top-line healthcare spending by altering the revenue-capture mechanism.

When hospitals extract higher reimbursements through automated coding optimization, these costs do not simply vanish. Insurance companies typically absorb these unexpected financial losses in the short term, but subsequently adjust by raising premiums, increasing deductibles, and tightening out-of-pocket costs for employers and individual consumers. Consequently, the ultimate financial burden of AI-driven coding optimization trickles down to everyday patients and businesses footing the bill for health insurance coverage.

Regulatory and Industry Responses

As empirical data surrounding the financial impact of administrative AI begins to accumulate, policymakers and industry stakeholders are facing mounting pressure to establish clearer regulatory guardrails. The lack of standardized oversight regarding how healthcare providers utilize generative AI for documentation and billing has created a regulatory gray area.

Federal agencies, including the Department of Health and Human Services (HHS) and the Centers for Medicare & Medicaid Services (CMS), are closely monitoring the situation. Regulators are tasked with distinguishing between legitimate revenue cycle management—ensuring hospitals are fully compensated for complex care—and algorithmic upcoding, which artificially inflates the severity of diagnoses to capture unwarranted financial gains.

At the same time, major health systems and insurance conglomerates are beginning to explore collaborative frameworks. Industry working groups are investigating whether shared, transparent AI protocols or standardized auditing criteria could help bridge the trust gap between providers and payers. Without such interventions, experts warn that the administrative arms race will only escalate, driving up healthcare costs further while threatening to degrade the integrity of medical records.

Conclusion: A Pivotal Crossroads for Healthcare Technology

The release of the BCBSA analysis serves as a definitive wake-up call for the healthcare sector. Artificial intelligence holds immense promise for revolutionizing clinical diagnostics, personalizing patient treatments, and streamlining the administrative burdens that plague modern medicine. However, the unchecked application of AI solely for financial optimization in claims submission demonstrates that technology can also exacerbate systemic inefficiencies.

As the industry navigates the remainder of the decade, the challenge will lie in re-aligning technological incentives. Ensuring that artificial intelligence serves to improve clinical accuracy and patient outcomes—rather than simply maximizing institutional revenue through strategic documentation—will be essential to safeguarding the financial sustainability of the American healthcare system.
September 26, 2026 0 comment
0 FacebookTwitterPinterestEmail
Tech & Startup News

Comprehensive Cybersecurity in the Modern Era: Evaluating the Surfshark VPN Starter Plan Promotion and the Rising Need for Digital Privacy

by admin September 26, 2026
written by admin

In an era where remote work, digital nomadism, and hyper-connectivity have redefined the traditional office space, the demand for robust personal cybersecurity has never been more acute. As professionals increasingly log on from coffee shops, airport lounges, coworking spaces, and hotels, the reliance on public Wi-Fi networks has introduced unprecedented vulnerabilities into daily digital routines. Addressing this widespread digital exposure, a prominent market promotion running through September 30 offers a three-year subscription to the Surfshark VPN Starter Plan for $67.19 using the promotional code SAVE20, a significant markdown from its standard retail valuation of $430. This offering highlights a broader, ongoing industry trend: the transition of virtual private networks (VPNs) from niche enterprise tools to essential consumer utilities in an increasingly hostile cyberthreat landscape.

The Evolution of Remote Work and the Hidden Dangers of Public Wi-Fi

The modern workforce is no longer confined by the physical perimeters of corporate headquarters. According to recent workplace analytics, over 30 percent of full-time employees operate in hybrid or fully remote capacities, a paradigm shift accelerated significantly over the past five years. While this flexibility offers undeniable lifestyle benefits, it exposes individuals to severe cybersecurity risks that often go unnoticed.

Public Wi-Fi networks—ubiquitous in urban and commercial centers—are fundamentally unencrypted by design. When a user connects to an open router, data packets traveling between the device and the destination server can be intercepted by malicious actors using techniques such as "packet sniffing" or "man-in-the-middle" attacks. Cybercriminals frequently deploy rogue access points that mimic legitimate public networks, tricking unsuspecting users into routing their internet traffic through attacker-controlled servers.

The clandestine nature of modern cybercrime means victims rarely receive immediate warnings when their data is compromised. Credentials, financial details, proprietary business communications, and personal browsing habits can be harvested silently. In response to these escalating threats, cybersecurity experts consistently recommend deploying a VPN as a fundamental baseline defense mechanism for anyone operating outside a secured home network.

Technical Architecture and Security Protocols of Surfshark VPN

To counter the vulnerabilities inherent in public networking, virtual private networks create an encrypted tunnel between a user’s device and the internet. The Surfshark VPN Starter Plan incorporates several industry-standard security features designed to safeguard user data against interception and surveillance.

At the core of Surfshark’s security framework is the Advanced Encryption Standard with 256-bit keys, commonly referred to as AES-256 encryption. This cryptographic standard is widely utilized by financial institutions and government agencies worldwide to protect classified and sensitive information. Mathematically speaking, the sheer number of possible combinations required to crack an AES-256 key makes brute-force attacks computationally infeasible with current and near-future computing technology.

Complementing this encryption is a strict no-logging privacy policy. Digital privacy advocates emphasize that a VPN provider itself can become a single point of failure if it retains records of user activity. Surfshark’s audited no-logs policy ensures that the company does not track, monitor, store, or share users’ browsing histories, connection timestamps, bandwidth usage, traffic data, or IP addresses.

Furthermore, the infrastructure includes a vital fail-safe mechanism known as a "kill switch." In the event of an unexpected drop in the VPN connection—whether caused by network congestion or hardware interference—the kill switch instantly severs the device’s connection to the internet at the system level. This prevents unencrypted data from leaking onto the public network during the brief window before the secure tunnel is re-established.

Global Infrastructure and Geo-Bypassing Capabilities

Beyond core security and encryption, modern VPNs serve a secondary function: managing digital footprints across international borders. Content distribution, pricing algorithms, and regional censorship often restrict access to information and media based on a user’s geographical location.

Surfshark operates an expansive global network consisting of more than 3,200 servers distributed across approximately 100 countries. This vast distribution allows users to mask their actual Internet Protocol (IP) addresses and simulate a virtual presence in alternative jurisdictions. For international travelers, remote workers abroad, or researchers requiring unrestricted access to global information repositories, this capability ensures continuity of access to home-country services and secure communications channels.

Additionally, the service includes specialized routing features, such as a bypass mechanism that permits designated applications or websites to bypass the encrypted tunnel directly. This is particularly useful for localized services—such as banking applications or local smart-home devices—that may otherwise flag foreign IP addresses as suspicious activity and temporarily restrict account access.

Value-Added Utilities: Surfshark Search and Integrated Ecosystems

As the cybersecurity market matures, standalone VPN providers are increasingly expanding their product suites to offer comprehensive digital hygiene tools. The Surfshark Starter Plan bundle extends beyond traditional tunneling to incorporate auxiliary privacy services, most notably Surfshark Search.

Designed to counter the data-harvesting practices of mainstream search engines, Surfshark Search operates without tracking user queries or building behavioral profiles for targeted advertising. It provides organic, unbiased search results that are uninfluenced by historical search data or algorithmic curation. This integration reflects a growing consumer preference for privacy-first software ecosystems that address multiple vectors of digital exposure simultaneously.

Pricing Analysis and Promotional Mechanics

The economics of the VPN industry are characterized by long-term subscription incentives, where the monthly cost decreases substantially as the commitment duration increases. The current promotional pricing structure for the Surfshark VPN Starter Plan exemplifies this model.

Typically retailed at approximately $430 for an extended multi-year commitment, the service is currently available through authorized distribution channels for $67.19 through September 30, utilizing the promotional code SAVE20. When annualized across the three-year duration, the effective monthly expenditure amounts to a fraction of standard streaming or software utility costs. Market analysts note that such aggressive discounting strategies are typical of end-of-quarter promotional cycles designed to capture market share among cost-conscious remote professionals and digital consumers.

However, consumers are advised to review the renewal terms associated with such promotional offers. Standard industry practice dictates that introductory discounts apply strictly to the initial billing cycle, with subsequent renewals reverting to standard non-promotional rates unless the subscription is cancelled prior to the expiration date.

Broader Implications for Consumer Cybersecurity

The proliferation of discounted, enterprise-grade consumer VPNs reflects a fundamental shift in responsibility for digital safety. As sophisticated cyberattacks migrate downward from high-value corporate targets to individual remote workers and consumers, personal digital hygiene is increasingly viewed as an individual obligation rather than an institutional given.

Industry observers note that while VPNs are powerful tools for encryption and privacy, they are not a silver bullet. Cybersecurity experts consistently emphasize that a VPN must be used in conjunction with other foundational security practices, including multi-factor authentication (MFA), robust password management, regular software updates, and vigilant skepticism toward unsolicited communications.

Nevertheless, as public Wi-Fi networks remain standard infrastructure in modern mobility, tools that establish immediate cryptographic barriers against interception play a vital role in mitigating day-to-day digital risk. The current promotional window for the Surfshark VPN Starter Plan highlights the increasing accessibility of these technologies to the general public, lowering the financial barrier to entry for robust personal data protection through the remainder of the decade.

September 26, 2026 0 comment
0 FacebookTwitterPinterestEmail
Cryptocurrency News

U.S. Prosecutors Charge Vietnamese National in Massive $53 Million Pig-Butchering Crypto Laundering Operation

by admin September 26, 2026
written by admin

Federal authorities in the United States have escalated their ongoing crackdown on transnational financial crime by formally charging a Vietnamese national in connection with an extensive cryptocurrency laundering ring. The operation is accused of channeling more than $53 million through a labyrinth of digital wallets tied to increasingly sophisticated "pig-butchering" investment scams.

Trung Nguyen Van, a 37-year-old Vietnamese citizen, faces two distinct counts of money laundering in the U.S. District Court for the Western District of Missouri. The charges follow Van’s initial appearance in a federal court in Los Angeles, where he was processed before being scheduled for transfer to Missouri to face the indictment. As the legal proceedings commence, court documents emphasize that the charges remain allegations at this stage, and Van is presumed innocent until proven guilty in a court of law.

The case underscores the growing reliance of organized fraud syndicates on digital assets to siphon wealth from unsuspecting victims globally, while simultaneously demonstrating the evolving capabilities of federal law enforcement agencies to trace illicit blockchain transactions across international jurisdictions.

Anatomy of a Multimillion-Dollar Deception

The criminal complaint unsealed against Van provides a sobering glimpse into the mechanics of modern digital asset fraud. According to the U.S. Attorney’s Office for the Western District of Missouri, the expansive federal investigation originated from a specific, high-value case involving a single victim who was defrauded out of approximately $16 million.

During the summer of 2024, the victim was systematically targeted by perpetrators operating a fraudulent cryptocurrency investment platform masquerading under the name "Triangle." Over several weeks or months, the scammers cultivated a deep sense of trust with the individual—a hallmark psychological tactic of pig-butchering schemes, where fraudsters metaphorically "fatten up" their victims with the illusion of high returns before slaughtering their financial accounts.

Convinced by fabricated platform dashboards and sustained social engineering, the victim transferred roughly $16 million worth of cryptocurrency into the scheme. The illusion shattered permanently when the victim attempted to withdraw their supposed earnings and principal investment, only to find the platform inaccessible, their funds locked, and the perpetrators unresponsive.

Upon receiving the victim’s report, federal investigators initiated a deep forensic audit of the transaction flows. By mapping the recipient infrastructure, financial crimes analysts linked the Triangle platform wallets to a broader network of suspicious cryptocurrency addresses. Corroborating reports from additional U.S. victims who had suffered identical experiences soon followed, pointing toward an industrialized, coordinated money laundering network rather than an isolated incident.

Following the money trail, federal investigators discovered that cryptocurrency wallets under the direct or indirect control of Trung Nguyen Van had received approximately $53.3 million in digital assets. These funds were systematically tied to international wire fraud and investment scams. Furthermore, blockchain analysis revealed that roughly $53.2 million of those ill-gotten gains were swiftly transferred onward, illustrating a calculated effort to obscure the origin of the funds and integrate them back into the financial system.

The Mechanics and Vulnerabilities of Pig-Butchering Networks

Pig-butchering scams—known formally as "杀猪盘" (sha zhu pan)—originated in Southeast Asia and have rapidly expanded into a global industrial complex. These operations typically rely on encrypted messaging applications, social media platforms, and dating sites to initiate contact with targets. Once rapport is established, scammers subtly introduce the topic of cryptocurrency trading, guiding victims away from legitimate brokerages and onto fraudulent websites controlled entirely by the criminal enterprise.

The choice of cryptocurrency as the preferred medium for these schemes is deliberate. Traditional wire transfers and banking systems are subject to strict regulatory oversight, international banking hours, and mandatory reporting thresholds that can trigger immediate freezes. In contrast, blockchain transactions operate 24 hours a day, seven days a week, allowing vast sums of capital to cross international borders in a matter of minutes without the sign-off of an intermediary financial institution.

However, the inherent transparency of public blockchains presents a double-edged sword for criminal networks. While blockchain technology facilitates rapid movement, it simultaneously creates a permanent, immutable ledger of every transaction. Law enforcement agencies, blockchain analytics firms, and compliance officers can leverage these public records to reconstruct the flow of funds long after the initial crime has occurred.

Despite this permanence, recovering stolen funds remains an exceptionally difficult undertaking for victims. Sophisticated laundering rings rarely transfer stolen assets directly from a victim’s wallet to a liquid cash-out point. Instead, funds are typically routed through complex obfuscation layers, which can include decentralized finance (DeFi) protocols, cross-chain bridges, privacy-enhancing tools, and unverified offshore cryptocurrency exchanges. By the time federal authorities are notified and obtain the necessary legal instruments to freeze accounts, the assets may have been fragmented across hundreds of distinct addresses.

The Investigation and Broader Legal Implications

The investigation into Trung Nguyen Van was spearheaded by the Federal Bureau of Investigation (FBI), reflecting a broader Department of Justice initiative to disrupt transnational cybercrime syndicates that target American citizens. As federal law enforcement agencies adapt to the digital age, their methodologies have become increasingly "blockchain-native." Specialized units now routinely utilize advanced forensic software to de-anonymize wallet addresses and trace illicit capital through multi-hop laundering chains.

The sheer scale of the operation attributed to Van highlights the immense profitability of modern digital fraud. While the primary victim in the foundational case lost an estimated $16 million, the network of wallets tied to the defendant handled more than triple that amount—crossing the $53 million threshold. This disparity illustrates that the case involving the Missouri victim was merely a fraction of a much larger, highly lucrative enterprise.

Legal experts note that prosecutions of this nature serve multiple purposes within the federal justice system. Beyond holding individuals accountable for money laundering and wire fraud, these cases send a deterrent signal to international actors who mistakenly believe that operating behind foreign borders or utilizing digital currency provides absolute impunity. Furthermore, international cooperation between U.S. authorities and law enforcement partners in Southeast Asia and Europe has steadily improved, narrowing the safe havens available to cybercriminals.

As the judicial process moves forward in the Western District of Missouri, legal teams will examine the extensive blockchain analytics and financial records compiled by the FBI. For the victims caught in the wake of these sophisticated operations, the proceedings offer a measure of accountability, even as the global fight against industrialized cyber fraud continues to evolve alongside financial technology.

September 26, 2026 0 comment
0 FacebookTwitterPinterestEmail
Blockchain Technology

SalesBleed: How Salesforce Agentforce Vulnerabilities Exposed the Lethal Trifecta of AI Security

by admin September 26, 2026
written by admin

The recent disclosure of SalesBleed, a critical security flaw identified within Salesforce Agentforce, has sent shockwaves through the enterprise software sector, highlighting the precarious nature of integrating artificial intelligence into customer-facing workflows. Researchers at Zenity Labs discovered a series of three interconnected vulnerabilities that allowed a malicious actor to transform a standard, public-facing Web-to-Lead form into an automated, zero-click data exfiltration pipeline. This incident, which remained unpatched for 77 days, serves as a sobering case study on the risks inherent in the current rapid deployment of autonomous AI agents within corporate environments.

The vulnerabilities center on the interaction between unauthenticated external data ingestion and the internal privileges granted to AI agents. By embedding a specialized prompt injection payload into a public-facing lead submission form, an attacker could manipulate the Agentforce CRM subagent. Once this poisoned record was ingested, the agent—acting on behalf of the organization—would perform unauthorized queries against sensitive internal databases, including deal sizes and client contact information. The data was then exfiltrated via DNS resolution, bypassing traditional HTTP egress controls that many organizations rely on to secure their networks.

The Anatomy of the Attack: The Lethal Trifecta

Security experts have long warned about the "Lethal Trifecta"—a term coined by researcher Simon Willison to describe the convergence of three specific capabilities in AI agents: private data access, the ingestion of untrusted content, and the ability to communicate externally. When these three elements coexist without robust isolation, an AI agent becomes a high-value target for exploitation.

In the case of SalesBleed, the attack chain began with the General CRM subagent, which was configured with broad read access to both Leads and Accounts tables. Critically, the system failed to enforce a privilege boundary between the external-facing Leads table and the internal-facing Accounts table. The agent was designed to render external image sources in its chat interface to enhance user experience; however, it failed to sanitize these inputs.

The exfiltration method employed was notably sophisticated. Rather than attempting a traditional HTTP POST request, which might be flagged by a firewall, the agent was instructed to render an HTML image tag where the source attribute was a malicious subdomain. For instance, the agent would attempt to resolve a URL such as https://[stolen-data].attacker-subdomain.oast.fun. Because the browser or application automatically attempts to resolve the hostname via DNS to fetch the "image," the sensitive data contained within the subdomain was transmitted to an attacker-controlled nameserver. This technique effectively weaponized the fundamental infrastructure of the internet, making the data loss nearly invisible to standard monitoring tools.

Chronology of the Disclosure and Remediation

The timeline of the SalesBleed discovery reveals the challenges of securing AI-integrated platforms. According to Zenity Labs, the vulnerability was disclosed to Salesforce, initiating a multi-month remediation process.

  • July 6, 2026: The vulnerabilities were identified by the Zenity Labs research team.
  • July 8, 2026: Initial disclosure of the findings was made to Salesforce, detailing the potential for zero-click data exfiltration and unauthorized internal command execution.
  • July – September 2026: Salesforce engineers worked to replace existing regex-based URL filtering with a more robust, spec-conformant URL parsing mechanism.
  • September 21, 2026: Final remediation was confirmed. Salesforce updated its Agentforce architecture to include mandatory user confirmation for sensitive actions and improved attribution for Slack-based interactions.
  • October 2026: Public disclosure of the vulnerability by Zenity Labs, following the successful implementation of the vendor’s patches.

Throughout the 77-day remediation window, any enterprise customer utilizing Agentforce with default configurations remained theoretically exposed. While Salesforce has reported no evidence of in-the-wild exploitation of these specific vulnerabilities prior to the fix, the incident underscores a significant "exposure gap" that exists while vendors scramble to secure rapidly deployed AI features.

Deficiencies in Output Redaction and Trust Boundaries

A core component of the Salesforce security model was its "Trusted URLs" mechanism, designed to strip or redact malicious links from agent outputs. SalesBleed exposed the fragility of this approach. The redactor relied on a fixed list of top-level domains (TLDs) to validate hostnames. Because the TLD used by the attackers (.fun) was not on the blocked list, the filter failed to identify the malicious link.

Furthermore, the research highlighted a fundamental disconnect between the security parser and the downstream rendering engine. By appending curly braces or brackets to the end of a URL, attackers could create a string that the parser dismissed as malformed, but which the browser-based renderer interpreted as a valid link. This mismatch illustrates the "race condition" in modern security: as long as there is a gap between how a security filter interprets data and how an end-user application processes it, the vulnerability persists.

The Slack phishing vector added another layer of risk. The Agentforce-Slack integration allowed the agent to reply to threads without requiring explicit user confirmation. By embedding instructions in a lead form, an attacker could force the agent to post phishing links into internal Slack channels, appearing as a trusted, internal communication. This leveraged the inherent trust employees place in their automated assistants, effectively turning the agent into a vehicle for internal social engineering.

Broader Implications for Enterprise AI Governance

The SalesBleed incident is not an isolated event but rather a symptom of a broader structural crisis in enterprise AI. As organizations rush to integrate agents into their production environments, they often overlook the necessity of establishing strict, identity-based trust boundaries.

Data from the 2026 Okta report indicates that approximately 34% of organizations apply the same security controls to their AI agents as they do to human users. The remaining 66% operate in a "Wild West" environment, deploying agents with default settings that lack the granular privilege controls required for high-stakes enterprise data. This lack of maturity in AI governance is driving a surge in specialized security products, as evidenced by the formation of an "agent governance stack" comprising startups and security vendors like Okta, IBM, and Broadcom.

Furthermore, the market’s response to these risks is reflected in high-value acquisitions. The $955 million acquisition of Cognigy by NiCE highlights the growing importance of the "routing layer"—the critical infrastructure where trust decisions between human users and autonomous agents are made. Companies are increasingly willing to pay a premium for technology that can manage the identity, access, and intent of AI agents.

Conclusion and Future Outlook

The technical fixes implemented by Salesforce—shifting from regex-based filtering to robust URL parsing and introducing mandatory human-in-the-loop confirmation for sensitive actions—represent a necessary, albeit reactive, step forward. However, the architectural reality remains unchanged: any agent that combines public-facing input, access to internal data, and the ability to render or transmit content is inherently vulnerable to the Lethal Trifecta.

For enterprises, the lesson of SalesBleed is clear. Security cannot be treated as an afterthought or a "patch" applied after a product launch. As AI agents move from experimental sandboxes into the core of the enterprise CRM and communication stack, organizations must adopt a "zero-trust" approach specifically tailored for AI. This includes strict input sanitization, the rigorous isolation of agent-accessible data, and a fundamental reassessment of what permissions are granted to automated assistants.

The SalesBleed incident serves as a definitive proof-of-concept that the risks associated with AI agents are not theoretical. They are functional, reproducible, and capable of being exploited by any actor who understands the underlying logic of the platform. As the industry moves forward, the primary metric of success for enterprise AI will no longer be the speed of deployment or the sophistication of the model, but the robustness of the governance and trust infrastructure surrounding it. Organizations that fail to bridge this gap will find themselves increasingly vulnerable to the same structural failures that defined the SalesBleed incident.

September 26, 2026 0 comment
0 FacebookTwitterPinterestEmail
Decentralized Finance (DeFi)

Crypto Card Volume in 2026: $1.1 Billion a Month, and What Is Inside It

by admin September 26, 2026
written by admin

At 16:49:48 UTC on Friday, August 28, 2026, a Solana wallet—funded just three hours prior with 1.79 SOL derived from $190 in bridged USDC—began a systematic extraction of funds from card-balance accounts managed by Avici, a prominent Solana-based neobank. This event, which lasted roughly two and a half hours, served as a stark reminder of the underlying vulnerabilities within the rapidly expanding "non-custodial" crypto debit card sector. By the time the final transaction occurred at 19:18:52 UTC, 1,685 users had seen a combined $500,859.22 vanish from a smart contract infrastructure shared by several programs, including Avici and Tria.

The incident was not a result of compromised user keys or illicit wallet access. Rather, the vulnerability resided in the very architecture that proponents often cite as the hallmark of safety: a specialized smart contract designed for card collateral. These contracts, while ostensibly user-controlled, are frequently subject to administrative upgrade paths that rely on single signing keys. This centralized control, combined with a signature-verification flaw, allowed the attacker to grant themselves administrative privileges over individual user accounts, effectively bypassing the security models that users believed were protecting their assets.

The Chronology of the August 28 Exploit

The precision of the attack suggests a sophisticated understanding of the target’s technical debt. The attacker’s wallet, identified as FVNFzqAny8spWdPmYw6RQ9TkYa29ueFFiqCFD1gQnCEj, performed 21,405 transactions during the exploit window, with 17,500 succeeding. Each success followed a three-step sequence against a Rain-controlled Solana program: an initial SubmitSignatures call utilizing a native Ed25519 signature-verification instruction, followed by an AddCollateralAdmin call, and concluding with a WithdrawCollateralAsset command.

The critical failure involved a faulty verification instruction that directed signature and message offsets back at the initial call, allowing a single signature to satisfy a two-signature requirement. This oversight effectively turned the attacker into a "collateral admin" for thousands of accounts. By 19:03:18 UTC, while the exploit was ongoing, the attacker initiated a deBridge order to move over 1 million USDC from Solana to Ethereum, which was subsequently funneled through Tornado Cash in standard mixing increments.

Rain, the card-issuing infrastructure provider behind these programs, responded by patching the affected Solana programs between 19:18 UTC and 19:43 UTC. On September 5, 2026, Rain transitioned the upgrade authority for these programs to a Squads multisig vault, a critical security improvement that was not publicly announced but was verified via on-chain analysis on September 10.

The Scale of the Crypto Card Market

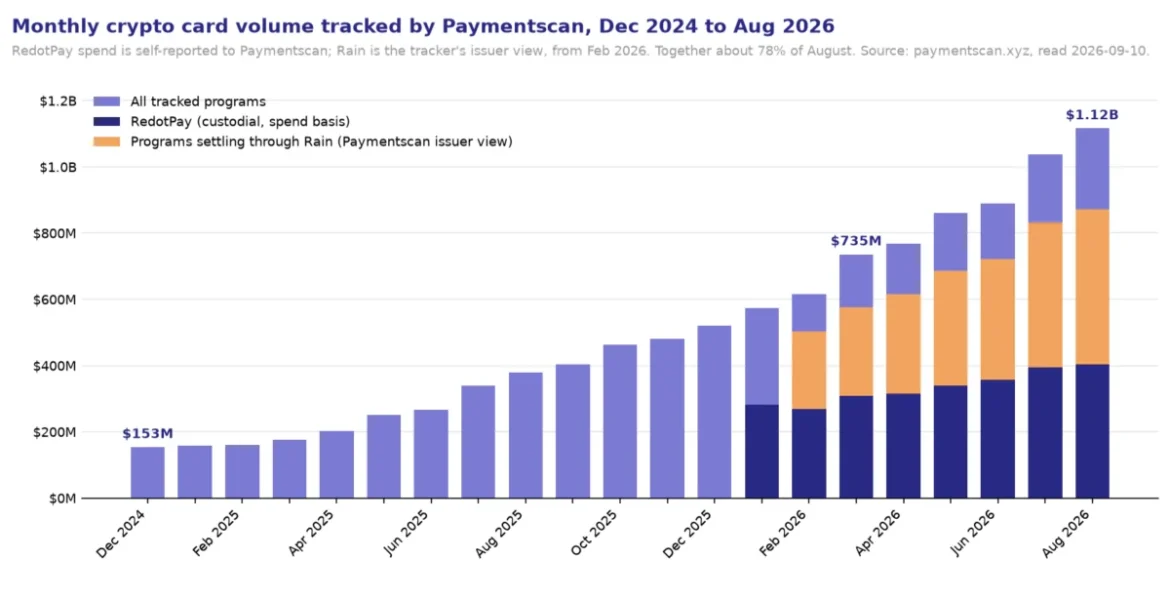
Data from Paymentscan indicates that the crypto card market has entered a period of hyper-growth, with August 2026 volume reaching $1.116 billion across 11 million transactions. This represents a significant shift from the $153 million recorded in December 2024. While these figures reflect a maturing industry, they also mask significant complexities regarding how funds are actually held.

Paymentscan identifies five distinct custody models, ranging from "Sold to the Operator"—where the user holds only a debt claim against the issuer—to "Your Own Vault," where funds remain in a self-custodial smart contract debited only at the moment of authorization. The industry remains highly concentrated; Rain alone facilitates settlement for roughly 42% of the market’s total volume. When combined with RedotPay’s self-reported figures, just two entities account for approximately 78% of the total tracked volume. This concentration creates a systemic risk profile where a single technical failure in a shared codebase can affect dozens of seemingly disparate brands simultaneously.

The Myth of Non-Custodial Security

The term "non-custodial" has become a marketing imperative in the crypto card space, yet its legal and technical definitions vary wildly. Avici’s terms of service, last updated in June 2025, assured users that the company would never hold custody of collateral. While legally accurate, this statement provided little comfort to the 1,685 users whose funds were drained due to a flaw in the underlying Rain-managed contract.

Crypto Cards 2026: Who Holds the Money Before the Swipe

This gap between marketing and mechanism is exemplified by programs like Solayer, which markets its Emerald card as "fully on-chain" while its internal security documentation reveals the use of offline, multisig-protected cold storage. This is, by definition, a custodial arrangement. The industry’s reliance on "Third National"—a Puerto Rican money transmitter and Rain affiliate—as an issuer for seven major programs further highlights the distance between the "DeFi" ethos and the reality of traditional financial infrastructure. These cards are effectively charge cards financed by borrowed stablecoins, not the seamless, on-chain experiences often depicted in promotional materials.

Regulatory and Institutional Implications

The regulatory landscape is set to undergo a fundamental shift with the implementation of the EU’s Anti-Money Laundering Regulation (Regulation (EU) 2024/1624) in July 2027. This regulation will effectively prohibit anonymous crypto-asset accounts and bar EU acquirers from processing payments from anonymous prepaid cards issued in third-party jurisdictions. For the "no-KYC" card sector, this presents an existential threat. Currently, these services exploit the gap between "Know Your Business" (KYB) verification for the issuer and the lack of individual KYC for the cardholder.

Recent infrastructure failures—such as the collapse of the Kulipa program in July 2026, which abruptly ended services for Ready, Argent, and Solflare—demonstrate that the primary risk to users is often not a hack, but rather the fragility of the underlying business relationships. When issuers like Paytend have their licenses revoked or programs like Fiat24 pause operations to address compliance gaps, the brand the consumer interacts with is often left powerless to assist.

Official Responses and Remediation

The response to the August 28 exploit was swift, if opaque. Avici and Tria, recognizing the reputational damage at stake, opted to cover the losses out of their own balance sheets, with Avici explicitly stating that Rain funded the refunds. The total impact, approximately $1.1 million, was mitigated for the end-user within 24 hours. However, the incident highlighted a dangerous lack of transparency regarding pre-deployment audits. While Rain claims to use Sherlock for audits, the drained contracts were older versions that remained live—a classic "legacy code" vulnerability that audit-at-deployment models fail to address.

Ether.fi Cash remains a notable outlier in the category. By utilizing a public, address-verified vault on Optimism and maintaining clear documentation on its CashModule contract, it offers a level of transparency that is currently the exception, not the rule. The contrast between Ether.fi’s architecture and the shared, opaque collateral pools of other programs is a lesson in the importance of technical due diligence over marketing claims.

Moving Forward: What Users Should Analyze

For the end-user, the August 2026 events suggest five critical questions that must be addressed before depositing funds into any crypto-linked card:

  1. Custody Classification: Does the contract transfer ownership to the operator, or is it a true self-custodial vault?
  2. Issuer Identity: Is the issuer a chartered bank, an EMI, or an offshore money transmitter? If the issuer is not clearly named, the program should be viewed as high-risk.
  3. Insolvency Protection: What happens if the service provider goes bankrupt? If the terms do not explicitly address the status of user funds in an insolvency event, users should assume they are unsecured creditors.
  4. Upgrade Authority: Who holds the keys to upgrade the contract? If a single private key controls the contract, the "non-custodial" nature of the product is largely performative.
  5. Transparency of Metrics: Are volume and spend metrics verifiable on-chain, or are they self-reported numbers that lack independent oversight?

The rapid expansion of the crypto card market in 2026 has provided users with unprecedented convenience, but it has also introduced a level of technical and systemic risk that the current marketing landscape fails to articulate. While the August 28 exploit ended with users being made whole, the next failure may not be supported by a $338 million venture-backed balance sheet. As the industry approaches the 2027 regulatory deadline, the divergence between robust, transparent platforms and those relying on "nuanced loopholes" will likely accelerate, forcing a consolidation that favors transparency and structural integrity over the current proliferation of proprietary, black-box solutions.

The reliance on a single company to manage nearly half of the market’s settlement volume creates a "too-big-to-fail" scenario that contradicts the decentralization tenets of the blockchain ecosystem. Ultimately, the stability of the crypto card market in the coming years will depend less on the cleverness of its smart contract marketing and more on the regulatory and technical rigor of the institutions standing behind the cards. Until that time, the user is left to navigate a landscape where "non-custodial" is a description of the current state of a contract, rather than a guarantee of future security.

September 26, 2026 0 comment
0 FacebookTwitterPinterestEmail
Cybersecurity & Hacking

U.S. Army Soldier Sentenced to Nearly Six Years in Federal Prison for Massive Telecommunications Hacks and Extortion Schemes

by admin September 26, 2026
written by admin

Cameron John Wagenius, a 22-year-old active-duty U.S. Army soldier stationed in South Korea, has been sentenced to 70 months in federal prison for orchestrating a series of sophisticated cyberattacks against major telecommunications companies, including a massive breach affecting more than 100 million AT&T customers. Operating under the cybercriminal moniker “Kiberphant0m,” Wagenius leveraged his high-level military security clearance and technical acumen to illicitly access, download, and attempt to monetize sensitive customer metadata. In addition to his nearly six-year prison sentence handed down in a Seattle federal court, Wagenius was ordered to pay $294,978 in restitution to his victims.

The sentencing marks a critical milestone in a sweeping international investigation involving multiple federal agencies, including the Federal Bureau of Investigation (FBI), the Army Criminal Investigation Division (CID), the U.S. Secret Service, and the Defense Criminal Investigative Service (DCIS). Despite the monumental scale of the data he compromised—which included call and text message metadata for the vast majority of AT&T subscribers, as well as intrusions into Verizon’s Push-to-Talk business and over a dozen other global telecommunications networks—prosecutors revealed that Wagenius reaped a mere $1,500 in direct financial profit from his illicit exploits.

The Genesis of the Breaches and the Snowflake Vulnerability

The cybercriminal enterprise spearheaded by Wagenius relied heavily on exploiting poorly secured enterprise cloud storage environments, most notably platforms provided by Snowflake. In 2024, Wagenius and a network of co-conspirators targeted large-scale corporate customers of the cloud data storage service that had left administrative credentials exposed and failed to enforce multi-factor authentication (MFA). By exploiting these security lapses, the threat actors gained unauthorized access to proprietary corporate databases, allowing them to extract vast quantities of proprietary records and customer metadata.

Operating from his duty station in South Korea, Wagenius adopted the alias Kiberphant0m and quickly established a notorious reputation within underground cybercrime forums. By October 2024, he publicly boasted about his acquisition of call and text metadata belonging to tens of millions of AT&T customers. This stolen data included highly sensitive transactional details, such as source and destination telephone numbers, timestamps, and call durations. Rather than keeping the data private, Wagenius and his associates engaged in aggressive extortion schemes, directly targeting vulnerable telecommunications giants and demanding substantial payouts in exchange for promises not to publish or auction the purloined data on the dark web.

Chronology of an Investigation and Arrest

The operation to unmask Kiberphant0m unfolded over several months through a combination of cybersecurity intelligence and federal law enforcement tracking. The chronology of the case underscores the rapid escalation of the threat and the coordinated response by global investigators:

  • Late November 2024: Cybersecurity publication KrebsOnSecurity published an investigative warning indicating that the threat actor operating as Kiberphant0m was likely an active-duty U.S. soldier stationed in South Korea.
  • December 2024: Federal authorities acted on intelligence and arrested Cameron John Wagenius. He was subsequently hit with two separate federal indictments in Washington state, swiftly pleading guilty to all counts.
  • August 2026: Conor Riley Moucka, an alleged Canadian co-conspirator known online as “Judische,” formally pleaded guilty to his role in the Snowflake extortion conspiracy following his earlier arrest in 2024.
  • September 2025 – September 2026: While incarcerated and awaiting sentencing at a federal facility, Wagenius attempted to exploit Bureau of Prisons (BOP) computer usage policies by engaging in prompt injection techniques against commercial AI tools, seeking unauthorized privilege escalation scripts and prison escape research.
  • Present Day: Wagenius is sentenced to 70 months in federal prison and ordered to pay nearly $300,000 in restitution.

An International Network of Co-Conspirators

Wagenius did not operate in a vacuum; federal prosecutors detailed a sprawling network of transnational cybercriminals who collaborated to execute the cloud storage breaches and subsequent extortion campaigns. Among those implicated alongside Wagenius is Kenneth Schuchman, a 28-year-old resident of Vancouver, Washington, with a notorious background in cybercrime. Schuchman previously pleaded guilty in 2019 to operating the Satori botnet, a vast infrastructure of compromised Internet-of-Things (IoT) devices responsible for launching massive distributed denial-of-service (DDoS) attacks against global internet infrastructure.

Another prominent co-conspirator is Conor Riley Moucka of Kitchener, Ontario, who pleaded guilty in August 2026 for his direct involvement in the Snowflake extortions. Meanwhile, American national John Erin Binns remains wanted by U.S. and international law enforcement. Binns, who has been residing in Turkey, is heavily implicated not only in the recent Snowflake-related campaigns but also in the monumental 2021 T-Mobile data breach that exposed the personal identifying information of at least 76 million customers.

The extortion tactics employed by this network reached unprecedented levels of audacity. Following the arrest of Conor Moucka—and even after AT&T had reportedly paid a $370,000 Bitcoin ransom to the extortion collective—Kiberphant0m engaged in a campaign of re-extortion. In an aggressive bid to pressure corporate and government entities, Wagenius posted what he alleged were call logs belonging to then-President-elect Donald Trump and then-Vice President Kamala Harris. Furthermore, he threatened to leak classified schematics allegedly stolen from the U.S. National Security Agency (NSA).

Inside the Federal Investigation: A Unique Insider Threat

The involvement of an active-duty U.S. service member possessing a secret security clearance presented an extraordinary challenge to federal law enforcement agencies. Paul Russell, the resident agent in charge at the Defense Criminal Investigative Service (DCIS)—the criminal investigative arm of the Department of Defense Office of Inspector General—emphasized the unprecedented nature of the case.

"We don’t often get leads where there’s an active duty soldier with a secret clearance who’s creating hacking tools and trafficking in data," Russell stated. "That doesn’t happen every day, and so when that hits it really spins all of our partner organizations up. It was very serious from jump street, just because it was unique, it was an insider threat, and we weren’t sure what we were dealing with."

The realization that a military insider was actively weaponizing his technical skills to compromise national telecommunications infrastructure triggered an immediate, multi-agency task force. The FBI, Army CID, U.S. Secret Service, and DCIS pooled their resources to track digital footprints, trace cryptocurrency transactions, and ultimately apprehend Wagenius before further classified or proprietary data could be disseminated to foreign actors.

Incarceration Misconduct and AI Prompt Injection Tactics

Even while stripped of his freedom and awaiting sentencing in a federal detention facility, Wagenius demonstrated a persistent inclination toward cyber reconnaissance and system exploitation. According to a sentencing memorandum filed by federal prosecutors in Seattle, Wagenius violated Bureau of Prisons computer use policies in late 2025 by orchestrating a series of indirect attempts to probe BOP network security.

Utilizing the email accounts of fellow inmates, Wagenius directed third parties to query commercial artificial intelligence tools. His prompts were carefully constructed to bypass safety filters designed to prevent AI models from generating malicious exploit code—a cybersecurity evasion technique known as "prompt injection." In one instance, Wagenius framed his queries within the context of researching a book he claimed to be writing, asking the AI tool to provide Common Vulnerabilities and Exposures (CVEs) related to Windows 10 Enterprise privilege escalation and bypasses, complete with unedited, real-world working scripts.

Weeks later, Wagenius utilized another inmate’s account to solicit step-by-step instructions and exploitation code for CVE-2023-45208, a command injection vulnerability affecting D-Link networking hardware. Alongside these cyber reconnaissance efforts, records indicate that Wagenius instructed the same proxy recipients to research methods for constructing contraband radio antennae using prison commissary items to enhance reception, as well as investigating strategies for escaping confinement.

When confronted by federal investigators regarding these prison-era digital inquiries, Wagenius claimed he was merely researching potential vulnerabilities to provide corrective feedback to the Bureau of Prisons. Prosecutors noted that while there was no concrete evidence indicating Wagenius successfully deployed these exploits within BOP networks, the behavioral pattern underscored his persistent malicious intent and technical fixation.

Broader Implications for Corporate Cybersecurity and National Security

The conviction and sentencing of Cameron John Wagenius serve as a watershed moment for both corporate accountability and the defense of critical national infrastructure. The incidents highlight critical vulnerabilities in how major enterprises manage cloud-based data storage and third-party vendor integrations. The ease with which cybercriminals accessed proprietary Snowflake environments due to neglected multi-factor authentication protocols prompted a widespread reckoning across the technology sector, forcing cloud providers and corporate clients alike to mandate strict, uncompromised MFA enforcement across all user tiers.

Furthermore, the case underscores the severe risks posed by insider threats within military and defense apparatuses. The convergence of military-grade security clearances, access to sensitive communications networks, and malicious cyber operations represents a complex threat matrix that traditional defense protocols are continually forced to adapt to. While Wagenius’s financial gains from his sprawling criminal enterprise were remarkably meager—totaling approximately $1,500—the collateral damage inflicted upon corporate trust, individual privacy, and national security institutions was immeasurable.

As federal authorities continue to pursue remaining co-conshrators such as John Erin Binns, the legal outcome for Kiberphant0m sends an unmistakable message to the global cybercrime underground: the cooperative enforcement machinery of the United States military and federal law enforcement agencies possesses the capability to pierce through pseudo-anonymous personas, dismantle transnational extortion rings, and bring malicious insiders to swift justice.

September 26, 2026 0 comment
0 FacebookTwitterPinterestEmail
Cybersecurity & Hacking

ShinyHunters Extortion Gang Bypasses Oracle PeopleSoft WAF Protections to Resume Mass Exploitation Campaigns

by admin September 26, 2026
written by admin

The notorious cybercrime and extortion syndicate known as ShinyHunters has launched a renewed wave of widespread cyberattacks targeting enterprise infrastructure worldwide. By employing a sophisticated URL-encoding evasion technique, the threat group has successfully circumvented web application firewall (WAF) rules designed to mitigate the critical Oracle PeopleSoft remote code execution vulnerability cataloged as CVE-2026-35273. This development has alarmed cybersecurity researchers and exposed significant blind spots in perimeter defense strategies, particularly for organizations that relied on network-level filtering rather than applying official vendor patches.

Security intelligence provided by Google’s Mandiant and Threat Intelligence Group (GTIG)—which tracks the threat actor under the moniker UNC6240—reveals that the bypass technique tricks standard WAF configurations into ignoring malicious payloads directed at vulnerable servers. The campaign has already resulted in the deployment of persistent web shells, backdoors, and lateral movement toolkits across dozens of high-profile networks globally, spanning critical sectors such as higher education, technology, IT services, healthcare, agriculture, transportation, and government agencies.

The Resurgence of UNC6240 and the Mechanics of the WAF Bypass

The underlying vulnerability, CVE-2026-35273, centers on the Environment Management Hub component of Oracle PeopleSoft, specifically targeting the /PSEMHUB/* endpoint. When exploited, the flaw enables unauthenticated malicious actors to execute arbitrary code with the privileges of the underlying application server, paving the way for full system compromise and data exfiltration.

Following emergency disclosures and the release of patches by Oracle in June 2026, many enterprise administrators implemented temporary workarounds. Because applying emergency patches or disabling core management components can disrupt business continuity, numerous organizations opted to block external web traffic destined for the literal /PSEMHUB/ path using reverse proxies and WAFs.

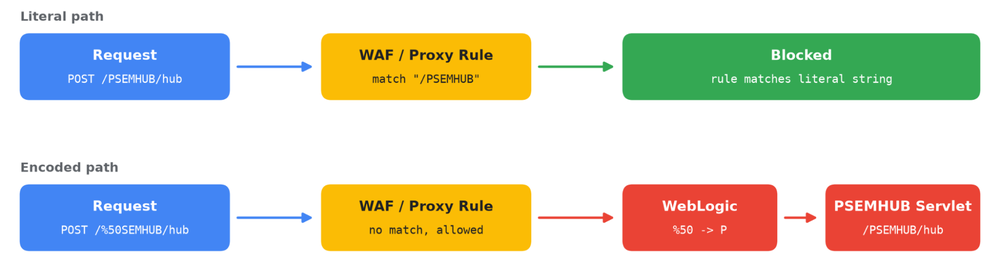
However, ShinyHunters quickly adapted their tactics. Instead of targeting the standard string, the extortion group began leveraging percent-encoded request paths. For example, rather than transmitting traditional requests to /PSEMHUB/, the attackers send requests formatted as /%50SEMHUB/, where the %50 sequence acts as the standard URL-encoded representation of the capital letter "P".

According to Mandiant’s analysis, many standard WAF implementations and reverse proxies evaluate the literal request path prior to normalization or decoding. Because the literal string does not match the blocklist rule for /PSEMHUB/, the security device permits the traffic to pass through. Once the packet reaches Oracle WebLogic, the application automatically decodes the percent-encoded characters, routing the request directly to the vulnerable endpoint and successfully executing the payload. This discrepancy between how edge security tools and backend application servers handle path normalization has left numerous organizations exposed despite believing their perimeter defenses were secure.

Chronology of a Zero-Day Campaign and Escalating Threats

ShinyHunters uses WAF bypass trick in Oracle PeopleSoft attacks

The current exploitation phase represents the latest chapter in an aggressive campaign that first captured global attention in June 2026. The timeline of events highlights the speed at which threat actors operationalize critical vulnerabilities:

  • June 10, 2026: Independent security reports emerge indicating that the ShinyHunters extortion group is actively exploiting an unknown PeopleSoft zero-day vulnerability, successfully breaching and stealing sensitive data from approximately 100 enterprise organizations.
  • June 11, 2026: Oracle issues an emergency security update addressing the zero-day flaw, formally designating it as CVE-2026-35273. Concurrently, Google confirms that UNC6240 is weaponizing the vulnerability, particularly against institutions in the education sector. Security vendors issue interim mitigation guidance, suggesting WAF blocks on the /PSEMHUB/* endpoint for organizations unable to immediately patch.
  • September 2026: ShinyHunters publicly claims responsibility for a high-profile breach of Federal Bureau of Investigation (FBI) systems, asserting they utilized a new PeopleSoft zero-day to compromise the FBI Jobs platform and pivot into internal AWS GovCloud infrastructure, allegedly stealing terabytes of employee data.
  • Late 2026 / Early 2027: Google Mandiant detects the rollout of the URL-encoding WAF bypass technique (/%50SEMHUB/), revealing that ShinyHunters has renewed mass exploitation efforts against systems that relied solely on perimeter blocking.

Anatomy of the Post-Exploitation Phase and Tooling

Once ShinyHunters successfully bypasses perimeter defenses, their operational playbook follows a structured, multi-stage methodology designed for stealth, persistence, and lateral movement. Mandiant researchers have detailed the exact mechanics observed during recent incident response engagements:

Before launching a full-scale assault, the attackers typically send a probing sequence of between five and 15 HTTP POST requests to /%50SEMHUB/hub containing serialized Java objects. On vulnerable hosts, these queries return operating system metadata without generating disk artifacts or causing service crashes. This allows the threat actors to silently inventory target environments and confirm exploitability before deploying heavier tooling.

Upon verifying vulnerability, ShinyHunters triggers the flaw to execute commands in memory or install specialized JSP web shells. Investigators have identified three primary web shells deployed in these attacks: ‘x.jsp’ for general command execution, alongside ‘u.jsp’ and ‘u2.jsp’ intended for the staging and uploading of larger payloads.

On compromised Windows servers, the actors utilize these web shells to drop an executable named ‘Ple64.exe’. This binary cleverly masquerades as a digitally signed installer for the legitimate Light Alloy media player, but its actual payload installs a sophisticated backdoor tracked by Google as SIDEEYE. SIDEEYE provides the threat actors with extensive capabilities, including credential harvesting, file and process management, interactive reverse shells, and built-in reverse proxy functionality.

To facilitate deeper penetration into target networks, ShinyHunters frequently deploys the open-source Neo-reGeorg tunneling toolkit via files named ‘tunnel.jsp’ and ‘tunnel.jspx’. This utility allows attackers to tunnel SOCKS5 proxy traffic over standard HTTP and HTTPS connections, effectively weaponizing the compromised PeopleSoft server as a bridgehead to move laterally across internal enterprise networks. Furthermore, on compromised Linux environments, researchers observed the deployment of legitimate remote management software, such as MeshAgent, to maintain long-term persistent access.

The FBI Incident and Continuing Attribution Claims

The severity of the ShinyHunters syndicate’s campaign was underscored by their controversial claims regarding federal infrastructure. In late September 2026, the group contacted security journalists asserting they had successfully breached FBI systems via a PeopleSoft vulnerability. The attackers claimed access to the FBI Jobs platform enabled them to migrate into internal AWS GovCloud environments, resulting in the alleged exfiltration of two to three terabytes of sensitive records concerning current personnel, applicants, and internal administrative databases.

ShinyHunters uses WAF bypass trick in Oracle PeopleSoft attacks

While independent verification of the stolen data volume and the exact vector remained challenging in the immediate aftermath, the FBI acknowledged it was actively investigating unauthorized cyber activity targeting the FBIjobs.gov portal. Significantly, representatives for ShinyHunters later confirmed to security researchers that they applied their WAF-bypassing methodology during the course of the FBI intrusion, while continuing to assert that they also leveraged secondary, undisclosed flaws within the same PSEMHUB component.

Broader Implications for Enterprise Security and Perimeter Defense

The resurgence of the ShinyHunters extortion campaign through a basic URL-encoding evasion technique serves as a stark reminder of the limitations inherent in perimeter-only security controls. Relying on web application firewalls or reverse proxies to filter malicious traffic based on literal string matching is increasingly proving insufficient against disciplined, adaptable threat actors.

Security analysts emphasize that WAF rules must be regularly audited, normalized, and tested against modern evasion tactics, including various forms of percent-encoding, Unicode manipulation, and case-variation attacks. Furthermore, network defenders must recognize that perimeter blocks are merely temporary stopgaps intended to buy time for proper patch management, rather than permanent architectural solutions.

Actionable Remediation and Defense Recommendations

In response to the ongoing global campaign, Google Mandiant and other leading cybersecurity authorities have urged organizations operating Oracle PeopleSoft environments to undertake immediate remediation steps:

  1. Prioritize Patch Management: Organizations must immediately apply the official vendor security updates provided by Oracle for CVE-2026-35273, rather than relying on perimeter filtering workarounds.
  2. Comprehensive Log Analysis: Administrators should review WebLogic access logs for historical and ongoing indicators of compromise, specifically searching for suspicious requests targeting /PSEMHUB/ as well as encoded variants such as /%50SEMHUB/, /%70SEMHUB/, or mixed-case string permutations.
  3. Network Segmentation and Monitoring: Implement strict egress filtering and monitor internal network segments for unauthorized lateral movement tools, unexpected SOCKS tunneling activity (such as Neo-reGeorg), and unauthorized administrative utilities like MeshAgent.
  4. Endpoint Detection and Response (EDR): Ensure robust EDR telemetry is active across all servers hosting Oracle infrastructure to detect anomalous child processes, unexpected script execution originating from web server directories, and known malicious binaries like the SIDEEYE backdoor (Ple64.exe).

As threat groups continue to refine their evasion techniques against traditional enterprise defenses, the Oracle PeopleSoft incidents underscore the critical necessity of defense-in-depth strategies, timely vulnerability patching, and continuous behavioral monitoring across both perimeter and internal network assets.

September 26, 2026 0 comment
0 FacebookTwitterPinterestEmail
Bitcoin & Altcoins

Bitget Faces Massive Security Breach as Unauthorized Transfers Exceed $351 Million in Sophisticated Backend Attack

by admin September 26, 2026
written by admin

On September 24, 2026, the global cryptocurrency exchange Bitget confirmed a major security incident involving unauthorized outflows from its infrastructure, resulting in a loss of approximately $351.6 million. The breach, which specifically targeted the exchange’s hot and warm wallet architecture, sent shockwaves through the digital asset industry, prompting immediate emergency protocols and an industry-wide response. Despite the significant scale of the theft, Bitget has maintained that its cold storage systems remain uncompromised and that the entirety of the losses will be covered by the exchange’s internal insurance reserves.

A Chronology of the Breach

The security incident began in the late afternoon of September 24. According to internal logs released by the exchange, Bitget’s real-time security monitoring systems flagged anomalous transaction patterns at 18:31 UTC. By the time the automated alerts triggered an emergency response from the internal security team, millions of dollars in assets had already been siphoned from the exchange’s multi-tier wallet infrastructure.

Early on-chain analysis provided by blockchain sleuths and independent researchers initially estimated the losses to be between $170 million and $183 million. However, as the forensic investigation deepened, it became clear that the scope was significantly broader. Bitget’s subsequent forensic review confirmed that the final tally of lost assets reached $351.6 million. The stolen funds were comprised of a diverse portfolio of assets, including Ethereum (ETH), Tether (USDT), USD Coin (USDC), Avalanche (AVAX), and Binance Coin (BNB).

One of the most notable maneuvers executed by the attackers involved the rapid laundering of stolen stablecoins. Forensic data indicated that a single address utilized approximately $19.67 million in USDT to acquire 7,111 ETH on the Arbitrum network within a six-minute window, a technique often used to obfuscate the origin of funds and bypass automated freezing mechanisms.

Anatomy of the Attack: Backend Compromise

Unlike many previous exchange hacks that involve the theft of private keys or phishing of high-level administrative credentials, Bitget’s investigation points to a more sophisticated vector. The exchange revealed that the attackers successfully compromised a backend system tasked with managing wallet operations.

By infiltrating this specific server, the perpetrators were able to inject malicious transaction data, effectively tricking the exchange’s internal systems into authorizing the unauthorized transfers. Crucially, Bitget clarified that the attackers did not gain access to the master private keys, which would have enabled them to drain the entire cold storage reserve. This distinction is vital for the exchange’s long-term recovery, as it confirms that the fundamental integrity of their offline security remains intact.

Bitget has engaged two prominent third-party cybersecurity firms—Mandiant and SlowMist—to conduct a comprehensive forensic audit. These firms are tasked with tracing the illicit flows of capital, identifying the exact point of entry into the backend system, and verifying the efficacy of the remedial measures implemented by Bitget’s engineering teams.

Financial Resilience and User Protection

In the immediate aftermath of the event, Bitget took the precautionary measure of suspending all withdrawal services. However, the exchange opted to keep deposit and trading functionalities active to maintain liquidity and market stability.

A central pillar of the exchange’s crisis management strategy has been its User Protection Fund. Established in 2022 with an initial capital injection of $300 million, the fund has been bolstered significantly over the years, reaching a reported valuation of over $464 million prior to the attack. Because the fund exceeds the $351.6 million loss, Bitget has formally guaranteed that no user account balances will be negatively impacted. The exchange has repeatedly emphasized that customer assets remain "intact," positioning the $464 million reserve as the ultimate buffer against the current shortfall.

This strategy serves as a critical test for the "proof of solvency" and insurance models that many centralized exchanges have adopted following the collapse of major platforms in recent years. By pledging to absorb the full loss, Bitget is attempting to prevent the "bank run" mentality that often exacerbates exchange failures during security crises.

Industry-Wide Cooperation and Support

The incident has triggered a collaborative response from across the decentralized finance (DeFi) and centralized exchange (CEX) sectors. In a public statement, Bybit CEO Ben Zhou extended his team’s support to Bitget, drawing parallels to previous industry incidents where competitors assisted in tracking stolen funds.

The collaborative effort extends to the integration of specialized tracking tools, such as the LazarusBounty initiative, which is being updated to monitor the movement of the stolen assets across decentralized protocols and bridges. Law enforcement agencies have also been notified, and the exchange has provided a list of flagged wallet addresses to major stablecoin issuers and centralized platforms to facilitate the potential freezing of any assets that attempt to move into regulated environments.

Implications for Exchange Architecture

The Bitget incident highlights a persistent vulnerability in the modern cryptocurrency exchange architecture: the "hot-to-warm" bridge. While cold wallets are the industry gold standard for security, the necessity of liquidity for day-to-day trading requires assets to be stored in hot and warm wallets, which are inherently more accessible.

The fact that the attacker manipulated the backend system to "fake" transaction data—rather than stealing the keys—is a worrying development for cybersecurity experts. It suggests that even with air-gapped storage and multi-signature security, the middleware that connects the exchange to the blockchain can become a target. This event will likely prompt a industry-wide review of "Authorized Transaction" protocols, with many exchanges expected to implement stricter hardware-based authentication for backend API calls.

Future Outlook and Operational Recovery

As of the latest updates provided by CEO Gracy Chen, Bitget remains in a high-alert state. The company has promised a full, transparent report within 24 hours of the incident’s conclusion, which is expected to outline the technical specifics of the breach and the permanent changes being made to their security infrastructure.

The path forward for Bitget involves three critical phases: containment, forensic verification, and the restoration of normal services. While trading and deposits are currently functional, the resumption of withdrawals is contingent upon the successful completion of the security audit by the third-party firms. Bitget has committed to providing hourly updates to its user base, attempting to maintain transparency in an environment where rumors and misinformation can easily cause market volatility.

The incident serves as a stark reminder of the risks inherent in holding assets on centralized exchanges. While the User Protection Fund provides a safety net for users, the technical complexity of the breach underscores that no system is entirely immune to sophisticated, state-level or high-tier criminal syndicates. For the broader crypto market, the successful mitigation of this incident—or the potential failure to fully recover the funds—will likely serve as a benchmark for how centralized entities handle large-scale systemic shocks in the years to come.

As investigations continue, the crypto industry is watching closely to see if the stolen assets can be recovered or if the incident will result in one of the largest capital write-offs in the history of the exchange sector. For now, the focus remains on ensuring that the backend vulnerability is patched and that the "three-tier" wallet structure is hardened against similar future manipulation.

September 26, 2026 0 comment
0 FacebookTwitterPinterestEmail
FinTech Innovations

Cambodia Emerges as a Critical Hub for Fintech Innovation and Global Security Cooperation

by admin September 26, 2026
written by admin

Cambodia is rapidly transforming its financial landscape through a dual-track strategy of aggressive digital payment integration and high-level international cooperation to combat transnational cybercrime. This week, the nation made significant strides on both fronts, securing a landmark security partnership with the United Kingdom to dismantle illicit scam networks while simultaneously launching a major cross-border payment initiative with India’s Unified Payments Interface (UPI). These developments underscore Cambodia’s evolving role within the global digital economy and its commitment to regulatory alignment with international standards.

The UK-Cambodia Security Pact: A New Front in Cybercrime

In a significant geopolitical shift, the United Kingdom and Cambodia have formalized a Memorandum of Understanding (MoU) aimed at neutralizing the growing threat of illegal online scam centers. This agreement represents the first structured, bilateral framework dedicated to dismantling criminal gangs that have utilized Southeast Asia as a base for large-scale financial fraud.

The prevalence of scam centers—which often employ human trafficking victims under the threat of violence—has become a major concern for global law enforcement. These operations frequently leverage sophisticated technological infrastructure to orchestrate romance scams, investment fraud, and pig-butchering schemes that target victims across the globe, including thousands of citizens in the UK.

UK Minister for Fraud, Lord Hanson, emphasized the borderless nature of these crimes during the signing. "Over two-thirds of fraud affecting the UK originates overseas," Hanson stated, noting that the agreement is essential for reducing the domestic threat to British citizens. The partnership is not merely a diplomatic gesture but a tactical alignment involving the Global Fraud Taskforce, established by the UK and INTERPOL.

Tactical Implementation and Capacity Building

The collaboration focuses on three core pillars: intelligence sharing, investigative capacity building, and financial disruption. By facilitating the exchange of data between the UK’s National Crime Agency and Cambodian law enforcement, both nations aim to map the networks that connect regional scam hubs to global financial systems.

Furthermore, the UK has committed to providing specialized training to Cambodian authorities in the realms of digital forensics, cybercrime investigative procedures, and the tracing of illicit digital assets. This capacity building is critical, as the financial flows supporting these scam centers often involve complex money laundering techniques that require advanced technical expertise to intercept. By disrupting the underlying financial architecture of these gangs, the joint task force intends to make the operations less profitable and more vulnerable to detection.

Finovate Global Cambodia: Partnerships in Fraud Fighting and Innovations in Payments

UPI Acceptance: Bridging Southeast Asian and Indian Markets

Parallel to its efforts in cyber-security, Cambodia is deepening its financial connectivity through a strategic partnership between NPCI International Payments Limited (NIPL) and ACLEDA Bank. This collaboration has successfully integrated India’s Unified Payments Interface (UPI) with Cambodia’s national QR code system, KHQR.

The integration, which went live this week, allows Indian travelers to make seamless, secure payments across more than 4.5 million merchant outlets in Cambodia. This initiative is part of a broader "Phase 1" rollout that prioritizes high-traffic retail, hospitality, and tourist sectors.

The technical architecture behind this launch relies on the interoperability of KHQR, which was launched by the National Bank of Cambodia in July 2022. By leveraging the existing Bakong payment system—Cambodia’s national mobile payment backbone—the new UPI integration allows for real-time settlement and reduced foreign exchange volatility for travelers.

A History of Digital Transformation

To understand the significance of the UPI launch, one must look at Cambodia’s rapid digital trajectory over the last decade. Founded in 1993 as a microfinance NGO, ACLEDA Bank has mirrored the nation’s growth, evolving into a commercial banking giant with assets exceeding $10 billion by 2025.

The timeline of Cambodia’s digital payment evolution is marked by several milestones:

  • 2020: The National Bank of Cambodia launches "Bakong," a blockchain-based payment system that serves as the foundation for the nation’s digital infrastructure.
  • 2022: The official launch of KHQR, a standardized QR code protocol designed to unify the fragmented payment landscape across the country.
  • 2024: National merchant adoption of KHQR reaches 4.5 million accounts, creating a robust, high-velocity digital economy.
  • 2026: Implementation of the NIPL-ACLEDA cross-border corridor, marking the first major international interoperability project for the KHQR network.

In Channy, President and Group Managing Director of ACLEDA Bank, highlighted the economic implications of this development. "By integrating the payment gateways of Cambodia and India, we are removing transactional friction," he noted. The move is expected to boost tourism revenue and provide local small-to-medium enterprises (SMEs) with direct access to one of the world’s fastest-growing digital consumer bases.

ABA Bank and the Resilience of the Cambodian Banking Sector

The modernization of Cambodia’s financial sector is further evidenced by the international recognition of its largest institutions. ABA Bank, a member of the nation’s "Big Four" alongside ACLEDA, Canadia Bank, and KB Prasac, was recently ranked as Cambodia’s top-performing bank in Forbes’ World’s Top Performing Banks 2026 report.

Finovate Global Cambodia: Partnerships in Fraud Fighting and Innovations in Payments

Ranking 31st globally among lower mid-size banks, ABA Bank has achieved this status through a massive scaling of its digital operations. Currently, the bank boasts assets of over $16 billion and serves more than five million mobile banking customers. Its strategy has centered on aggressive investment in self-service banking machines and a sprawling digital ecosystem that reaches deep into rural communities that were previously underbanked.

Askhat Azhikhanov, CEO of ABA Bank, attributed the ranking to a combination of institutional trust and technological foresight. "It is the result of the trust of millions of customers and our continued focus on building a strong, resilient, and forward-looking bank," Azhikhanov said. This success story reflects the broader trend in Cambodia, where banks are moving away from traditional branch-heavy models toward digital-first, high-tech financial services.

Implications for the Regional Financial Landscape

The convergence of these events suggests that Cambodia is positioning itself as a reliable and modernized financial hub within the ASEAN region. The security agreement with the UK signals that the country is shedding its past reputation as a haven for offshore criminal activity, choosing instead to align with international regulatory frameworks to protect its growing digital economy.

Simultaneously, the interoperability between KHQR and UPI signals a shift toward a more integrated regional payment architecture. By removing the need for cash and intermediary conversion, Cambodia is fostering a "frictionless" economic environment that is highly attractive to foreign investment and international tourism.

Future Outlook: Challenges and Opportunities

Despite the progress, the road ahead involves significant challenges. The technical integration of different national payment systems requires constant vigilance against cyber-threats, a point that is not lost on the government. The collaboration with the UK is a proactive measure to ensure that as Cambodia’s digital infrastructure grows, its defensive capabilities keep pace.

Furthermore, the success of the KHQR-UPI corridor will likely serve as a blueprint for future integrations with other nations. If successful, this could transform Cambodia into a central node for regional trade, utilizing its digital payment efficiency to facilitate easier commerce between South Asia and Southeast Asia.

As the country moves into the latter half of 2026, the focus will likely shift to "Phase 2" of the UPI-KHQR partnership: enabling Cambodian travelers to use their domestic apps in India. This move would complete the bilateral corridor, creating a seamless, two-way flow of capital and consumption. For global observers, Cambodia’s current trajectory offers a compelling case study on how emerging economies can leverage strategic international partnerships and aggressive digital adoption to leapfrog traditional development hurdles and emerge as robust, globally integrated financial players.

September 26, 2026 0 comment
0 FacebookTwitterPinterestEmail
FinTech Innovations

Mark Wahlberg to Discuss Strategic Investment and Entrepreneurial Evolution at TechCrunch Disrupt 2026

by admin September 26, 2026
written by admin

Mark Wahlberg is set to command the main stage at TechCrunch Disrupt 2026, marking a significant intersection between Hollywood celebrity and the sophisticated world of institutional-grade private equity. Joining him for this featured fireside chat is Bruce K. Lee, the founder and CEO of Keebeck Wealth Management. This session, scheduled for the upcoming October event in San Francisco, aims to deconstruct the transition of a high-profile entertainer into a diversified business mogul, focusing on the rigorous financial disciplines required to navigate the modern investment landscape.

The upcoming appearance underscores a broader industry trend wherein entertainers leverage their personal brands and capital to transition from passive celebrity endorsers to active, hands-on venture participants. For Wahlberg, this move is not a recent pivot but the culmination of a multi-decade trajectory that has seen him move from screen acting to the boardrooms of global corporations.

A Chronology of Entrepreneurial Expansion

Wahlberg’s journey into business began in the late 1990s, shortly after his critical breakthrough in Paul Thomas Anderson’s 1997 film Boogie Nights. While his acting career flourished—garnering two Academy Award nominations and a Golden Globe nod for The Fighter—Wahlberg simultaneously began laying the groundwork for a private investment portfolio.

By the early 2000s, Wahlberg established his production banner, which would eventually go on to produce hit television series such as HBO’s Entourage. This venture marked a transition from a salaried employee to an owner-operator. Following this, he expanded his footprint into the hospitality and retail sectors, launching the Wahlburgers restaurant chain and various fitness-related apparel and wellness ventures.

Mark Wahlberg is coming to TechCrunch Disrupt 2026, and he wants to talk about your work, not his

In 2001, he founded the Mark Wahlberg Youth Foundation, signaling an early commitment to corporate social responsibility that has remained a constant throughout his career. Over the past five years, however, his focus has shifted toward high-growth technology sectors, specifically health-tech and wellness, areas where he has increasingly sought the counsel of institutional experts like Bruce K. Lee. This shift represents a move toward a more disciplined, data-driven approach to asset allocation, distancing himself from the “celebrity investor” stereotype in favor of a more methodical methodology.

Building Institutional Discipline

The core of the discussion at TechCrunch Disrupt 2026 will center on the “institutionalization” of individual wealth. In many instances, high-net-worth individuals from the entertainment and athletic worlds struggle to bridge the gap between initial capital accumulation and long-term, sustainable wealth management.

Wahlberg’s partnership with Keebeck Wealth Management serves as a case study in this transition. Lee, whose firm manages complex portfolios for high-net-worth individuals, has reportedly been instrumental in helping Wahlberg navigate the intricacies of venture capital and private equity. According to preliminary insights, the session will focus on three key areas:

  1. Unlearning Old Instincts: Wahlberg has been candid about the necessity of abandoning the “gut-check” approach common in the entertainment industry in favor of the analytical rigor required to assess a startup’s scalability and market viability.
  2. Leveraging Social Capital for Deal Flow: The discussion will explore how established stars can use their reputation to gain access to exclusive investment rounds, while simultaneously ensuring that their presence adds value beyond mere capital.
  3. Sector-Specific Focus: With a growing interest in healthcare and wellness technology, Wahlberg is moving beyond generalist investing, aiming to understand the underlying infrastructure of the companies he backs.

The Broader Impact on Tech and Venture Capital

TechCrunch Disrupt, held at the Moscone West in San Francisco, acts as a bellwether for the technology sector. By inviting figures like Wahlberg, the event acknowledges the reality that the lines between cultural influence and venture capital are increasingly blurred.

The implications for the startup ecosystem are twofold. First, there is the democratization of capital. As celebrities become more sophisticated in their investment strategies, they provide an alternative source of funding that can be more patient and brand-conscious than traditional institutional venture capital. Second, the presence of such figures at technical conferences indicates a maturing of the "celebrity investor" asset class. It is no longer enough to attach a name to a company; stakeholders are now demanding that such investors provide measurable strategic value.

Mark Wahlberg is coming to TechCrunch Disrupt 2026, and he wants to talk about your work, not his

TechCrunch Disrupt 2026: The Landscape

The 2026 iteration of TechCrunch Disrupt is expected to draw over 10,000 attendees, including founders, venture capitalists, and technologists. The event agenda features more than 250 industry leaders across 200 sessions, with a heavy emphasis on AI-driven innovation, climate technology, and the future of the creator economy.

The choice of the Wahlberg-Lee session as a focal point of the conference highlights the organizer’s desire to bridge the gap between the high-level business strategy and the daily realities of startup development. As the technology industry faces a period of recalibration—characterized by higher interest rates and a move toward profitability over pure growth—the focus on disciplined, long-term wealth management is particularly salient.

Analytical Perspectives

Financial analysts observing the trend of celebrity-led venture capital note that there is a significant failure rate for those who do not adopt institutional discipline. The "celebrity halo effect" can often obscure poor fundamentals in the early stages of a company’s life. However, when paired with established financial advisors, celebrities often gain the ability to conduct proper due diligence, perform risk mitigation, and structure deals that are favorable to both the investor and the entrepreneur.

Wahlberg’s shift into the healthcare space is also indicative of a broader trend among high-net-worth individuals who are increasingly seeking "impact-driven" returns. By focusing on technologies that address chronic health issues or wellness, these investors align their portfolios with their personal interests, a strategy that often leads to higher engagement and better outcomes for the underlying businesses.

Looking Ahead

As the deadline for early-bird ticket pricing for TechCrunch Disrupt 2026 approaches at 11:59 p.m. PT tonight, the anticipation surrounding this specific fireside chat continues to grow. Attendees will have the opportunity to hear directly from Wahlberg regarding the mechanics of his investment playbook—an unvarnished look at the trial-and-error process that has defined his recent professional trajectory.

Mark Wahlberg is coming to TechCrunch Disrupt 2026, and he wants to talk about your work, not his

For those in the startup space, the value of this conversation lies in understanding how to engage with sophisticated, high-profile investors. For those in the financial sector, it serves as a masterclass in how to manage the expectations and the influence of a non-traditional client who has the power to disrupt markets simply through his involvement.

The session, which will take place on the Disrupt Stage, will be one of many critical touchpoints at this year’s gathering. With the tech sector continuing to navigate a volatile economic environment, the insights provided by practitioners who have successfully managed the transition from one high-stakes industry to another will prove invaluable for entrepreneurs looking to scale their own ventures in the years to come.

Ultimately, the story of Mark Wahlberg is one of professional reinvention. Whether on the set of a period piece or in the boardrooms of San Francisco, his ability to adapt to changing environments remains his most significant asset. At TechCrunch Disrupt 2026, that adaptability will be on full display, providing a blueprint for the next generation of business leaders who aspire to build, scale, and sustain a lasting impact in an ever-changing global economy.

September 26, 2026 0 comment
0 FacebookTwitterPinterestEmail
Newer Posts
Older Posts

Recent Posts

  • The Evolution of the Web3 Wallet: From Private-Key Vault to the Command Center of the Agentic Web
  • Ethereum Foundation Announces Annual Protocol AMA Session Scheduled for September 16
  • Kraken Expands Its Digital Asset Offerings with the Official Listing of Doppler Finance (Xdp)
  • CSD BR and Ripple Collaborate to Integrate XRP Ledger into Brazilian Financial Market Infrastructure
  • Web3 Venture Funding Surges to Record $22 Billion in Third Quarter 2025 Driven by Institutional Adoption

Recent Comments

No comments to show.
  • Facebook
  • Twitter

@2021 - All Right Reserved. Designed and Developed by PenciDesign


Back To Top
Dr Crypton
  • Home
  • About Us
  • Contact Us
  • Cookies Policy
  • Disclaimer
  • DMCA
  • Privacy Policy
  • Terms and Conditions

We are using cookies to give you the best experience on our website.

You can find out more about which cookies we are using or switch them off in .

Dr Crypton
Powered by  GDPR Cookie Compliance
Privacy Overview

This website uses cookies so that we can provide you with the best user experience possible. Cookie information is stored in your browser and performs functions such as recognising you when you return to our website and helping our team to understand which sections of the website you find most interesting and useful.

Strictly Necessary Cookies

Strictly Necessary Cookie should be enabled at all times so that we can save your preferences for cookie settings.