
Intelligence and cybersecurity agencies across the United States, the United Kingdom, and the Netherlands have issued a joint high-priority advisory warning the public of an escalating global espionage campaign orchestrated by Iranian state-sponsored threat actors. The campaign relies on a sophisticated Windows malware strain identified as CHOSEN BRICK, which is specifically engineered to target, surveil, and harass dissidents, human rights activists, journalists, and perceived political opponents operating outside of Iran.
The coordinated alert, published following a joint investigation by the FBI and international counterparts, highlights a worrying escalation in transnational repression. Rather than targeting critical infrastructure or corporate intellectual property—the typical hallmarks of state-backed economic espionage—this campaign zeroes in on individuals. The attackers seek to compromise personal communications, harvest sensitive documents, monitor daily activities, and amplify psychological pressure on exiles and critics of the Iranian government.
Anatomy of a CHOSEN BRICK Infection
The CHOSEN BRICK malware is a feature-rich espionage tool designed for stealth, persistence, and comprehensive data collection. Once successfully deployed on a victim’s machine, the malware grants operators extensive surveillance capabilities. These include the automated harvesting of communications from encrypted messaging platforms such as Telegram and WhatsApp, the extraction of email archives, the capture of live screenshots, and the covert recording of surrounding audio via device microphones.
To evade detection by modern security software, CHOSEN BRICK employs several sophisticated defense-evasion techniques. Upon installation, the malware automatically appends exclusions to Microsoft Defender, preventing the built-in antivirus utility from scanning or flagging its malicious components. For persistence, it writes malicious entries into the Windows Registry Run keys, ensuring that the spyware re-launches automatically every time the operating system boots up.
Rather than relying on traditional, easily blockable command-and-control (C2) infrastructure, CHOSEN BRICK cleverly abuses legitimate platforms for its operations. Stolen data and telemetry are exfiltrated using Telegram’s API or decentralized cloud storage providers such as VultrObjects, Backblaze B2, and StorjShare. Furthermore, newer iterations of the malware incorporate SOCKS5 proxy routing via providers like IPRoyal and LightningProxies, effectively masking the true origin of the network traffic and complicating attribution and network forensic analysis.

Social Engineering and Tailored Lures
The intrusion vector for CHOSEN BRICK heavily relies on targeted social engineering. Threat actors initiate contact with their victims via popular messaging applications, particularly WhatsApp and Telegram, posing as trusted acquaintances, colleagues, or technical support representatives. Over time, the hackers build a rapport or exploit existing professional networks before delivering the malicious payload.
Victims are tricked into downloading and executing malicious files disguised as legitimate, highly useful software applications. Common software facades utilized in this campaign include productivity and creative tools such as Pictory and RunwayML, utilities like KeePass and Adobe Flash Player, and widely recognized security software including Norton Antivirus.
To bypass corporate endpoint detection and response (EDR) systems—which frequently monitor and block suspicious software execution on enterprise networks—the hackers routinely instruct targets to launch the purported applications on their personal, unmonitored devices.
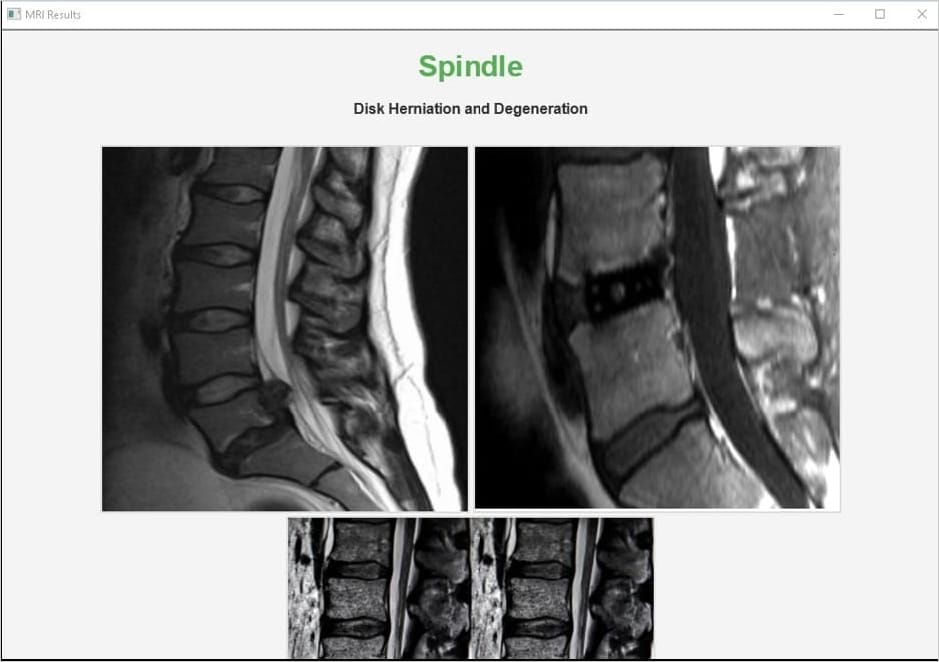
In particularly calculated operations, the threat actors tailor their pretexts to the specific profile of the individual. Cybersecurity analysts discovered that the campaign has occasionally leveraged highly sensitive medical lures, such as fraudulent MRI scan documents and medical reports. By exploiting personal health concerns or professional research interests, the hackers significantly increase the likelihood that the victim will open the file without hesitation, lower their guard, and execute the embedded payload. Upon opening, the application displays a convincing user interface mirroring the legitimate software it impersonates, completely masking the silent background installation of the CHOSEN BRICK malware.
The Broader Threat Landscape of Transnational Repression
The deployment of CHOSEN BRICK is not an isolated incident, but rather a prominent manifestation of a broader strategy employed by Iranian intelligence and security services. According to government assessments, Tehran increasingly utilizes cyber operations to augment physical surveillance, harassment, and intimidation campaigns against individuals living abroad who are perceived as threats to the regime.
Historically, state-backed cyber espionage focused heavily on government networks, defense contractors, and financial institutions. However, the maturation of targeted spyware has allowed nation-states to extend their reach directly into the private lives of critics, journalists, and diaspora communities. The advisory emphasizes that data stolen during these cyber operations is frequently weaponized. In several recorded instances, exfiltrated personal data, private photographs, and confidential communications have been leaked on pro-Iranian harassment and smear websites. This public exposure is designed to humiliate targets, disrupt their professional lives, and intimidate broader diaspora communities into silence.
More alarmingly, the joint advisory underscores that cyber espionage is frequently a precursor to more severe kinetic actions. Intelligence assessments indicate that Iranian security services have previously plotted physical kidnappings, assaults, and targeted lethal operations against individuals residing internationally whom the regime views as enemies of the state. Consequently, a digital compromise via CHOSEN BRICK introduces immediate physical risks to the affected individuals and their families.
Indicators of Compromise and Defensive Recommendations
In response to the widespread deployment of CHOSEN BRICK, the FBI, NCSC, and partner agencies have released comprehensive technical guidance and Indicators of Compromise (IoCs) to help at-risk individuals, civil society organizations, and IT administrators identify and remediate potential infections.
Defenders and potential targets are strongly advised to audit their Windows environments for unauthorized or anomalous persistence mechanisms. Specifically, system administrators should inspect Windows Registry Run and RunOnce keys for suspicious application paths or unrecognized executables. Regular reviews of local system logs can reveal unauthorized alterations to Microsoft Defender exclusions, which serve as a primary fingerprint of a CHOSEN BRICK compromise.
Network traffic analysis remains one of the most effective methods for detecting active infections. Security teams should monitor egress traffic for unexpected or unauthorized connections to the Telegram API, as well as traffic directed toward cloud storage and proxy networks such as Backblaze B2, VultrObjects, StorjShare, IPRoyal, and LightningProxies.
Civil society organizations, independent media outlets, and human rights groups working with high-risk individuals are encouraged to adopt robust operational security (OpSec) measures. This includes enforcing hardware-based multi-factor authentication (MFA), conducting regular security hygiene training focused on identifying sophisticated social engineering ploys, and separating personal communications from sensitive operational assets. As Iranian threat actors continue to refine their tooling and social engineering tactics, international cybersecurity agencies stress that heightened vigilance and proactive threat hunting remain vital components in safeguarding global civil society from state-sponsored digital intrusion.

