The Ethereum Foundation’s ongoing commitment to robust ecosystem security, formally organized under the Trillion Dollar Security initiative, has identified a systemic vulnerability in the way transactions are authorized and executed. The core issue lies in the current architecture of the Ethereum Virtual Machine (EVM), which executes user-signed instructions without verifying that the ultimate state change aligns with the user’s intent. As the ecosystem matures and moves toward mass adoption, the Foundation is now prioritizing "native transaction assertions" as a critical safeguard to be implemented alongside Clear Signing protocols.
The Anatomy of Transaction Uncertainty
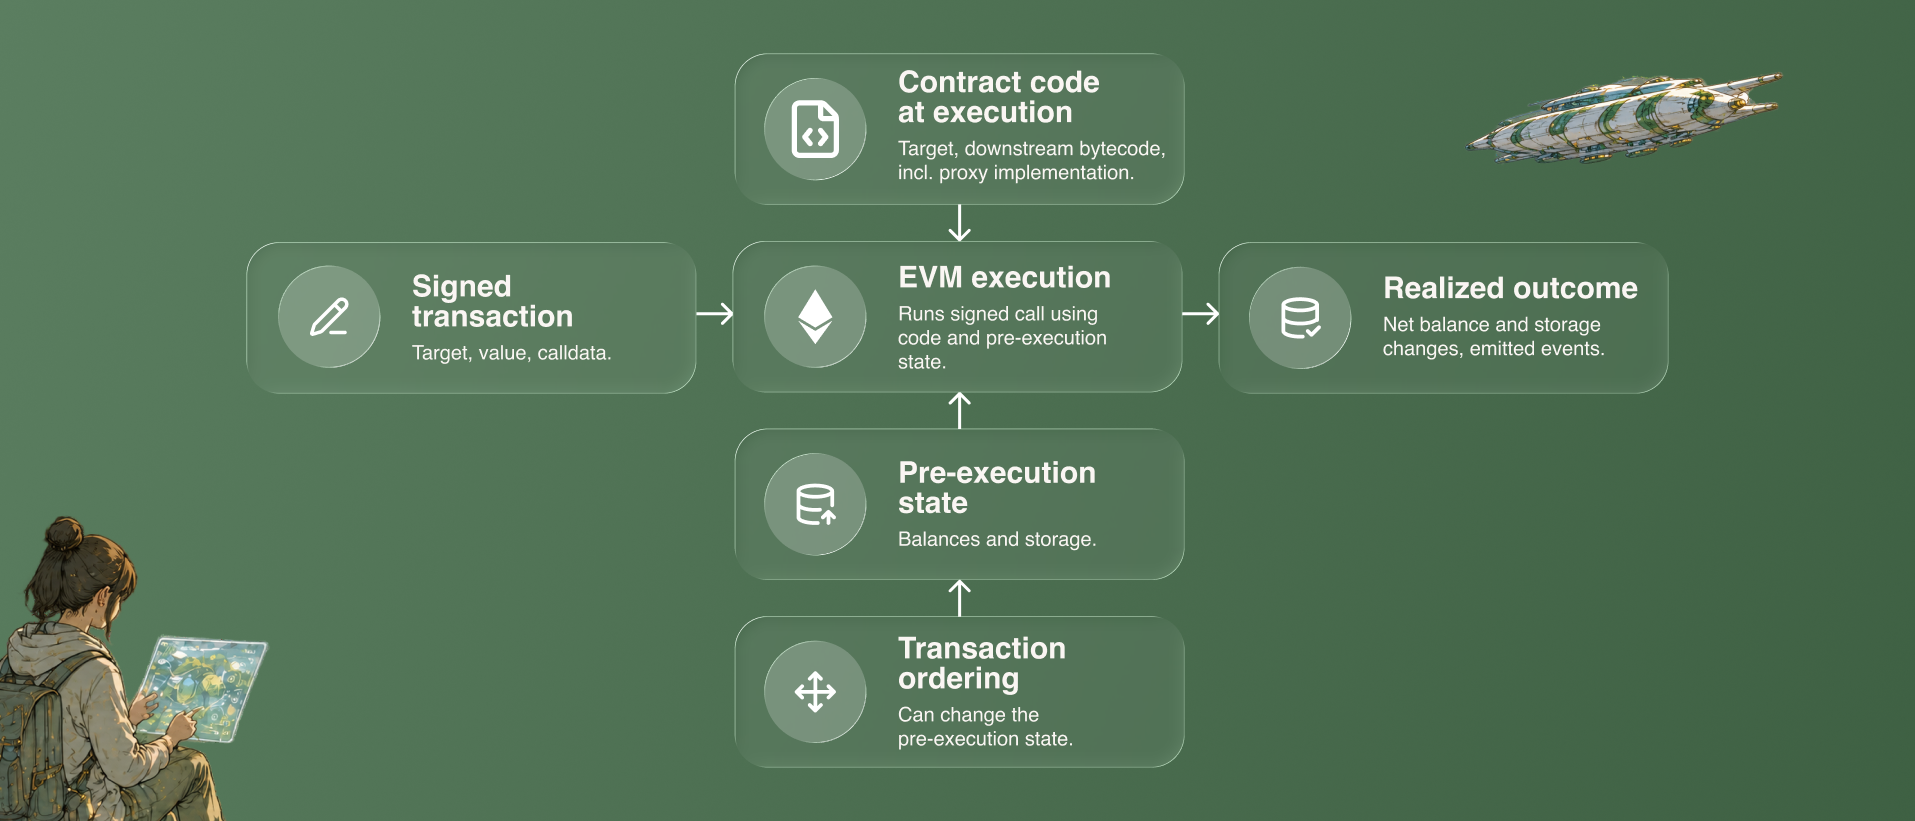
In the current paradigm, an Ethereum signature acts as a digital seal of approval for a specific set of parameters—the target contract, the value being transferred, and the accompanying calldata. However, this signature does not provide a guarantee regarding the state of the network at the moment of execution. Because Ethereum is a dynamic, asynchronous environment, the conditions existing at the time of signing may change by the time the transaction is included in a block.
This discrepancy has led to two distinct categories of failure: intent mismatch and outcome mismatch. Intent mismatch occurs when the transaction request itself is manipulated, often through compromised frontends or malicious interface injections. High-profile incidents, such as the Bybit Safe wallet incident and the BadgerDAO attack, serve as sobering reminders of this vulnerability. In these cases, users believed they were authorizing a benign action, while the underlying code was engineered to execute unauthorized changes, such as replacing implementation contracts or granting unlimited token spending permissions.
Outcome mismatch, conversely, represents a scenario where the transaction is technically valid and authorized, but the economic result is catastrophic due to external market factors. A prominent example occurred with a CoW Swap user who attempted to swap $50.4 million of aEthUSDT for aEthAAVE. Due to thin liquidity and the specific limitations of the gas-sensitive verification protocol, the user received a vastly inferior execution. Despite receiving a warning, the user’s inability to enforce an independent "minimum outcome" rule—separate from the interface’s display—resulted in a loss of over $50 million in potential value. These events highlight a glaring gap: Ethereum currently lacks a general mechanism for onchain code to verify the net state changes of a transaction before it is finalized.
A Chronology of Vulnerability
The history of Ethereum security is punctuated by these "blind spots." Early efforts to mitigate these risks relied on off-chain simulation, where a wallet provider predicts the outcome of a transaction using a snapshot of the current chain state. However, as demonstrated by the Radiant Capital post-mortem, simulation is insufficient if the signer’s local environment is compromised. If a user’s device is infected with malware, the malicious actor can swap the intended transaction for a fraudulent one at the moment of signing, effectively bypassing simulation safeguards.
The evolution of security defenses has been slow but steady. Clear Signing emerged as a pivotal development, providing users with a human-readable interpretation of complex calldata. While this significantly reduces the risk of phishing, it does not address the risk of execution-time state changes. Contract-level guards, such as those implemented by the Gnosis Safe (now Safe) or Uniswap, provide a degree of protection, but they are often fragmented. They require specific implementation and often struggle to read state across different types of contracts, particularly those that use proxies or opaque storage patterns.
Technical Implications of EIP-7906
The proposed solution, EIP-7906, seeks to integrate transaction assertions directly into the protocol layer. By leveraging the framework established by EIP-8141—which introduces "frame transactions"—EIP-7906 proposes a POST_TX frame. This frame would act as a read-only validation step, executing after the primary transaction actions have been processed but before the state is committed.
This mechanism utilizes three specific opcodes to provide granular control:
- TXTRACE: Enumerates the net state changes, including ETH balances, storage modifications, and emitted events.
- TXDIFF: Retrieves the precise "before" and "after" values for specified addresses and storage slots.
- EVENTDATACOPY: Facilitates the extraction of event data into memory for validation.
Crucially, this check happens at the protocol level. If the POST_TX frame detects a deviation from the user’s established rule—such as a price impact exceeding a threshold or a change in an implementation contract address—it forces the entire transaction to revert. This ensures that users are protected from both malicious actors and unfavorable market conditions that arise between the moment of signing and the moment of inclusion.
Official Responses and Industry Sentiment
The Ethereum Foundation, through its Trillion Dollar Security initiative, has solicited feedback from a broad range of stakeholders, including wallet developers, DeFi protocol architects, and security researchers. While the industry largely agrees on the necessity of this functionality, the implementation challenges are significant.
Market participants, particularly those in the MEV (Maximal Extractable Value) space, have raised questions regarding the impact of these assertions on block building and gas efficiency. Because the POST_TX frame consumes gas, the Foundation has clarified that even if a transaction reverts due to an assertion failure, the gas payer remains liable for the fees consumed. This is a deliberate design choice intended to prevent "denial of service" attacks, where malicious actors might otherwise flood the network with transactions that deliberately trigger reverts to congest the mempool.
Broader Implications for the DeFi Ecosystem
The introduction of native transaction assertions could mark a paradigm shift in how users interact with decentralized finance. Beyond simple security, these assertions enable a more sophisticated form of "delegated agency." Users could theoretically grant an agent (a smart contract or a third-party service) the authority to perform trades on their behalf, subject to strict, onchain, immutable rules.
For instance, a user could set a policy that any transaction initiated by their agent must result in a minimum token output of $X, or that no transaction may result in a new token approval exceeding $Y. This removes the need for the user to manually verify every minor step of a complex, multi-step transaction. Furthermore, it allows protocols to define "safety envelopes" for their users. A liquidity protocol could mandate that any interaction with its pools must include an assertion verifying the price impact, effectively shifting the burden of safety from the user to the protocol’s own internal logic.
Future Outlook and Research Direction
As the research surrounding EIP-7906 advances, the focus remains on balancing user safety with network performance. The "Considered for Inclusion" status of the proposal indicates that the core development community recognizes its importance, though it has not yet been solidified for a specific hard fork.
The next phase of the Trillion Dollar Security initiative will involve rigorous testing of these opcodes in testnet environments. The Foundation is currently encouraging teams to experiment with the POST_TX frame to understand how it might integrate with existing account abstraction (ERC-4337) wallets. As the ecosystem looks toward a future of increased complexity—spanning Layer 2 rollups, cross-chain messaging, and sophisticated agent-based automation—the ability to cryptographically enforce intent will be the bedrock of user confidence.
Industry observers suggest that while adoption will take time, the shift toward "intent-based" security is inevitable. By moving the definition of a successful transaction from an off-chain expectation to an on-chain requirement, Ethereum is taking a definitive step toward fulfilling its promise of a secure, trustless, and reliable financial layer for the internet. Interested parties are encouraged to engage with the EIP-7906 discussion threads and coordinate with the Ethereum Foundation to ensure that these tools are built with the needs of the end-user at the forefront.

