
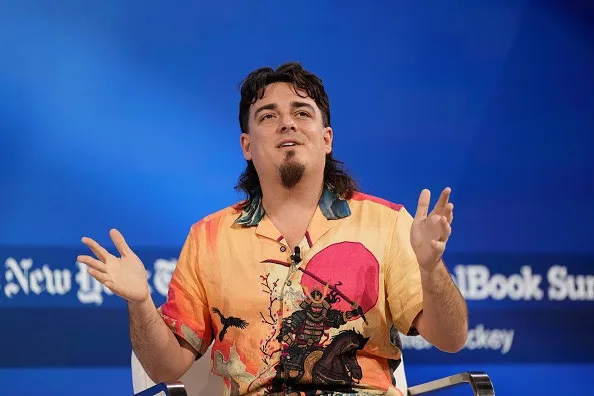
The rapid evolution of artificial intelligence has introduced unprecedented security vulnerabilities across the global digital landscape, fundamentally altering the nature of modern cyber warfare. Speaking at The New York Times DealBook Summit on Tuesday, tech entrepreneur and defense innovator Palmer Luckey delivered a stark warning regarding the widening gap between advanced AI-driven cyber threats and the defensive capabilities of legacy infrastructure. According to the Oculus founder and Anduril Industries co-founder, malicious actors are leveraging cutting-edge machine learning and automated exploit generation at speeds that outpace the operational capabilities of outdated corporate and governmental technology systems.
The high-profile discussion, moderated by journalist Andrew Ross Sorkin, brought to the forefront growing anxieties surrounding recent, widespread technical outages and critical infrastructure disruptions. As government agencies and private enterprises scramble to patch critical software vulnerabilities, cybersecurity experts increasingly point to systemic technological debt as a primary driver of modern digital vulnerability. Luckey’s remarks underscore a critical inflection point in cybersecurity, wherein the defensive posture of major institutions is being severely tested by adversaries employing sophisticated automated tools for both espionage and financial gain.
The Escalation of AI-Powered Cyber Threats
The intersection of artificial intelligence and cybersecurity has shifted from theoretical modeling to active, large-scale deployment. In recent years, threat actors—ranging from sophisticated nation-state syndicates to decentralized criminal cartels—have integrated automated systems capable of scanning networks, discovering zero-day vulnerabilities, and deploying bespoke exploits with minimal human intervention. This shift drastically reduces the time required to compromise a network, moving the timeline from weeks or months down to mere minutes or seconds.
Luckey highlighted that the current wave of security incidents represents the natural realization of advanced generative and analytical AI tools being weaponized. Traditional defense paradigms, which rely heavily on manual patch management, perimeter-based security architectures, and periodic vulnerability assessments, are fundamentally unequipped to handle threats moving at machine speed. Consequently, organizations operating on legacy infrastructure find themselves in a perpetual game of catch-up, attempting to fix vulnerabilities discovered and exploited by automated systems after the fact.
Furthermore, state-sponsored entities have accelerated their offensive operations. Luckey specifically pointed to North Korea as a prominent actor utilizing advanced cyber capabilities to execute financially motivated attacks, such as cryptocurrency theft and corporate extortion, alongside traditional strategic espionage. These state actors effectively exploit the friction inherent in bureaucratic technology upgrades, targeting older systems that lack modern telemetry, automated threat response, and robust segmentation.
The Broader Context of Recent Tech Outages and Government Response
The urgency of Luckey’s warning was underscored by real-world disruptions that directly impacted high-level political and economic programming. The severity of recent technical outages forced U.S. Vice President J.D. Vance to cancel his scheduled appearance at the DealBook Summit. According to conference organizers, Vance was required to abruptly pivot to high-level emergency briefings and strategy meetings addressing the cascading system failures affecting critical sectors.
While federal officials have largely characterized the recent spate of digital disruptions as the byproduct of a frantic patching cycle—wherein organizations rush to secure systems against newly publicized AI-discovered flaws—industry analysts view these incidents as symptomatic of a deeper structural weakness. The rapid discovery of vulnerabilities by automated systems has created an unprecedented volume of critical patches, overwhelming the internal resources of IT and security departments across both the public and private sectors.
This operational bottleneck creates a dangerous window of exposure. Even when a patch is made available by software vendors, the time required for an enterprise to test, validate, and deploy the fix across complex legacy environments often spans weeks. In an era where AI-driven scanners can identify and weaponize unpatched systems within hours of a disclosure, this delay is frequently fatal to network integrity.
Strategic Implications and the Path Toward AI-Driven Defense
Despite the sobering near-term outlook, Luckey emphasized that artificial intelligence is not exclusively an instrument of offense. Over a longer time horizon, the structural advantages of AI will inevitably accrue to the side that implements defensive automation most effectively. However, realizing this advantage requires a fundamental paradigm shift in how organizations conceptualize and execute cybersecurity strategy.
The foundational thesis presented by Luckey centers on the necessity of moving from reactive security frameworks to proactive, autonomous defense mechanisms. Because human analysts alone cannot parse the sheer volume of telemetry, log data, and threat intelligence generated across modern enterprise networks, organizations must deploy AI-powered security orchestration, automated remediation, and resilient zero-trust architectures.
"In the long run, the advantages are going to accrue to the side that is most effectively using AI for defense," Luckey stated during the summit. Addressing the pervasive industry sentiment that absolute security is impossible, he acknowledged the validity of the claim that systems can theoretically be compromised, yet stressed that operational speed remains the decisive variable. "With the people who say that everything can be hacked — they are right, for now. That actually may be the case with certain new techniques that are coming along. But as of right now, there’s a mismatch between the attackers who are very fast-moving and using technology and old, outdated systems that are not able to adopt technology as quickly as it is developed."
Economic and National Security Analysis
The macroeconomic and national security implications of this technological asymmetry are profound. Critical infrastructure—including energy grids, financial institutions, healthcare networks, and transportation systems—frequently relies on industrial control systems (ICS) and operational technology (OT) designed decades ago. These systems were built with reliability and longevity in mind, often prioritizing continuous operation over dynamic security adaptability, and were never engineered to withstand targeted, AI-directed cyber warfare.
As hostile nation-states continue to embed persistent threats within critical infrastructure, the potential for catastrophic economic disruption escalates. The financial costs associated with data breaches, ransomware remediation, intellectual property theft, and system downtime already amount to trillions of dollars globally each year. When scaled by the efficiency gains of artificial intelligence, the economic damage threatens to overwhelm traditional cyber insurance markets and destabilize supply chains.
In response, defense contractors, venture capitalists, and federal agencies are dramatically increasing capital allocation toward dual-use technologies that merge artificial intelligence with defensive cybersecurity operations. Programs initiated by agencies such as the Defense Advanced Research Projects Agency (DARPA) and the Cybersecurity and Infrastructure Security Agency (CISA) are increasingly focused on automated vulnerability discovery and self-healing networks. Yet, the transition timeline for private enterprises remains painfully slow.
Preparing for the Next Phase of Cyber Warfare
As the global technological ecosystem confronts this accelerated threat landscape, industry leaders are echoing Luckey’s call for immediate, decisive action. The era of passive cybersecurity—characterized by compliance-driven checklists and periodic security audits—is drawing to a close. Organizations can no longer afford the institutional inertia that permits legacy hardware and unpatched software to persist in production environments.
When pressed by Andrew Ross Sorkin on the precise level of concern the public and corporate leaders should maintain regarding these vulnerabilities, Luckey offered a pragmatic and sobering assessment. "It depends on how well prepared you are," he noted, before concluding with a stark caution regarding impending disclosures: "You guys are going to find out what’s going on soon enough."
The imperative moving forward is clear. Enterprises, defense institutions, and government regulators must compress their upgrade cycles, abandon outdated technological architecture, and aggressively adopt AI-native defensive tools. As Luckey succinctly summarized for the assembled leaders at the DealBook Summit: "People are going to have to pick up the pace. It’s time to start running."

