At 16:49:48 UTC on Friday, August 28, 2026, a Solana wallet, which had been funded just three hours earlier with 1.79 SOL—purchased with roughly $190 in USDC bridged from Ethereum—initiated a systematic drainage of card-balance accounts associated with Avici, a prominent Solana-based neobank. This breach, which persisted for over two hours, exposed the inherent risks hidden within the rapidly expanding "non-custodial" crypto card sector. By the time the incident was contained, 1,685 users had seen their balances liquidated, resulting in a total loss of $500,859.22.
The event serves as a stark case study in the gap between legal marketing and technical reality. Avici’s terms of service, last updated in June 2025, explicitly stated that neither the platform nor its issuer held custody of collateral. While legally accurate, the statement masked a technical vulnerability: the funds resided in a contract that, while nominally belonging to the user, remained under the administrative control of the program manager—a party capable of upgrading the contract with a single, plain signing key.
A Chronology of the Breach
The exploit was precise. The attacker’s wallet, identified by the address starting in "FVNFz," remained idle for 189 minutes after its initial funding before launching the attack. Between 16:49:48 and 19:18:52 UTC, the attacker executed approximately 21,405 transactions against a Solana-based program managed by Rain, the infrastructure provider powering the card.
The mechanics of the exploit exploited a flaw in signature verification. Each successful transaction involved a call to the native Ed25519 verification instruction. The attacker pointed the signature, key, and message offsets back at the initial instruction, allowing one signature to satisfy a check that required two. This granted the attacker administrative rights over individual user accounts, enabling the withdrawal of assets.
Rain, the card-issuing company behind Avici and several other programs, intervened by patching the affected contracts. The first patch was pushed at 19:18:37 UTC, just fifteen seconds before the final exploit transaction occurred. While the damage was significant, the immediate financial impact was mitigated by a prompt, company-led refund initiative. Avici and Tria—a second program hit by the same vulnerability—confirmed that all impacted users were made whole, with the companies absorbing the losses and providing an additional 10% premium to affected customers.
The Ecosystem: $1.1 Billion in Monthly Volume
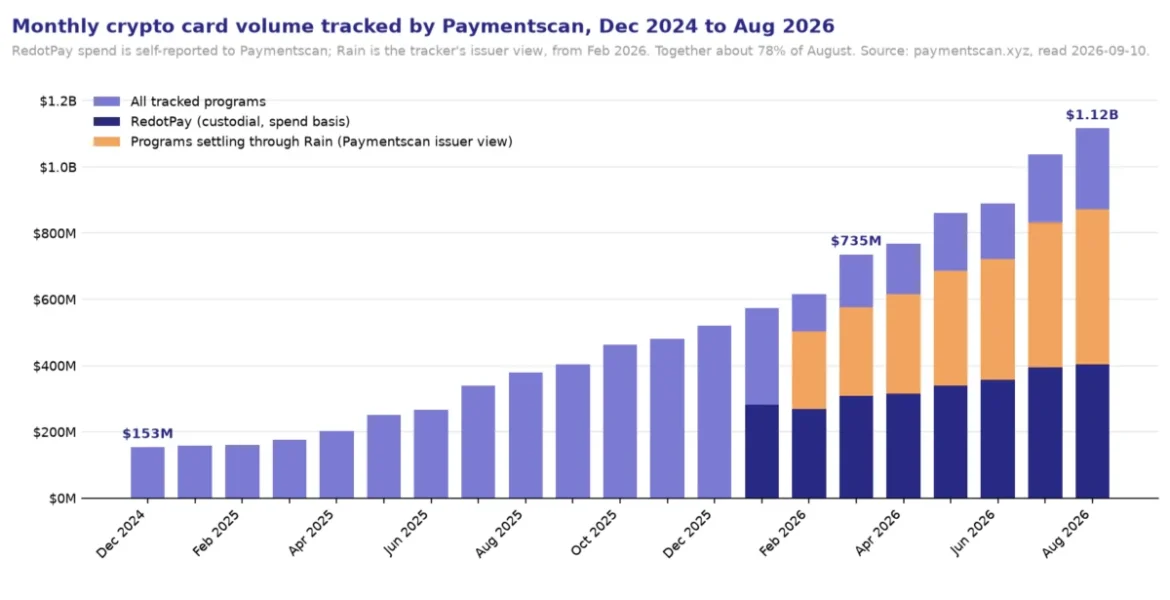
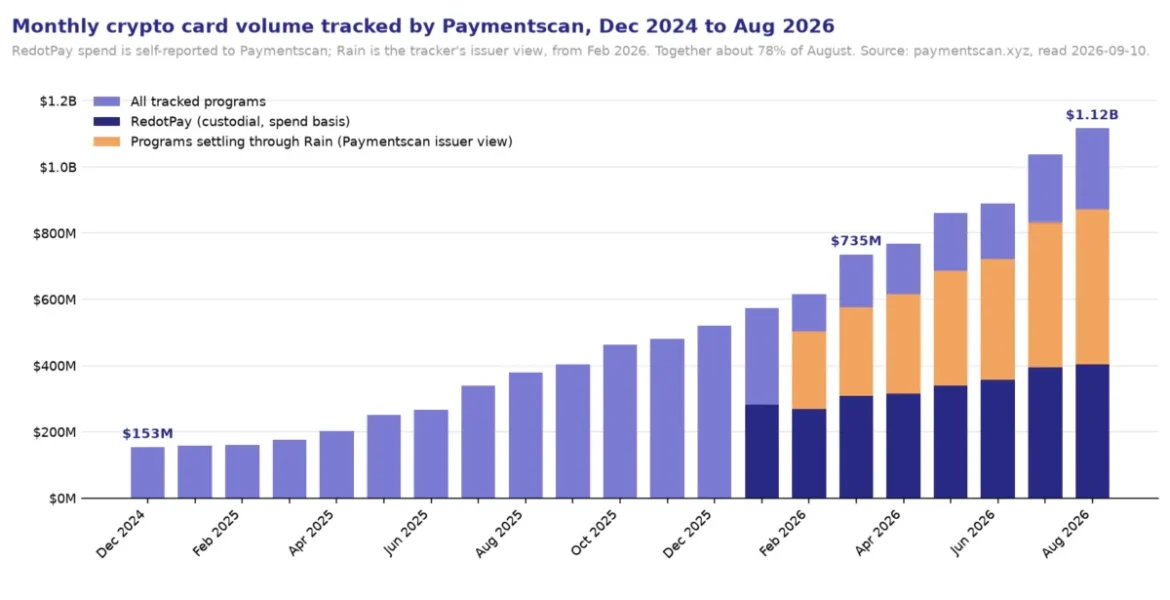
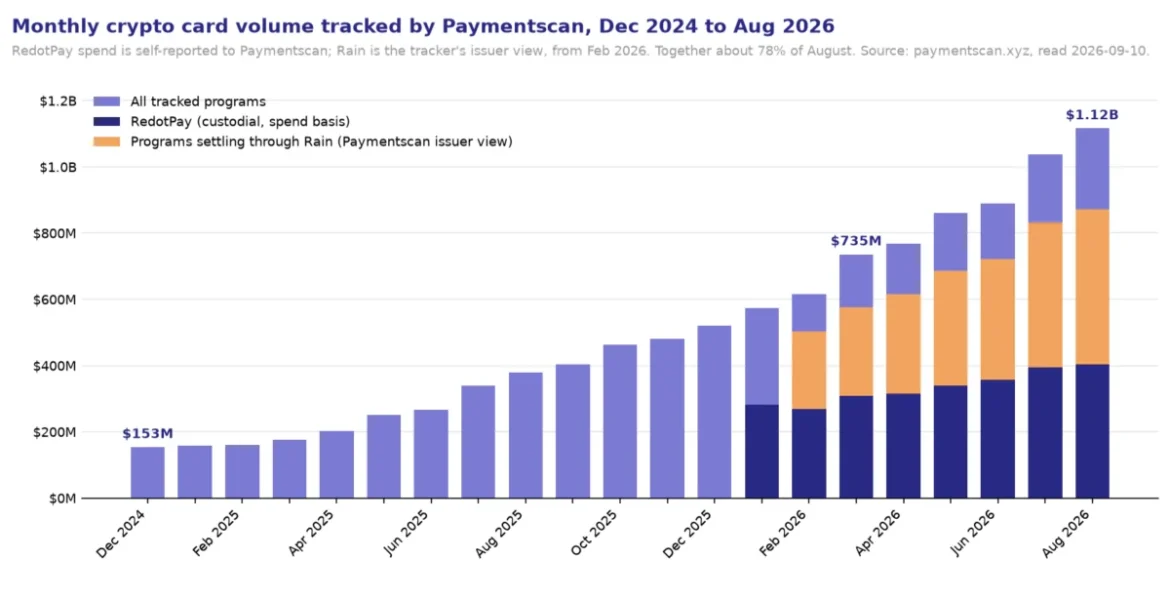
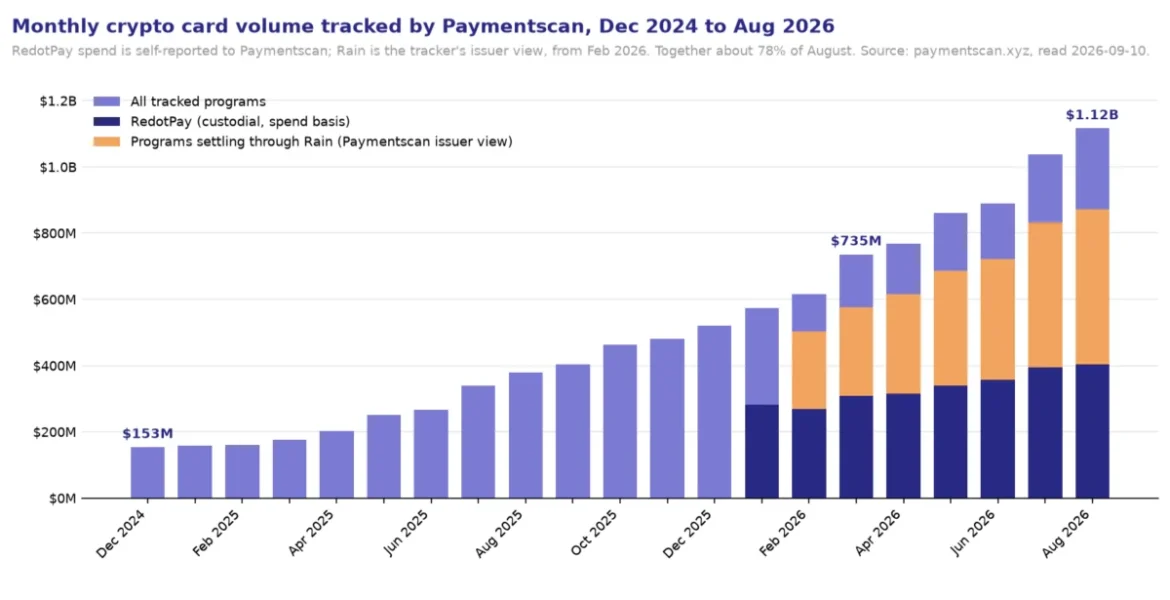
The incident occurred against a backdrop of explosive growth for the crypto card industry. According to data from Paymentscan, the total monthly volume for crypto-linked cards reached $1.116 billion in August 2026, spanning 11 million transactions and nearly 288,000 active addresses. This marks the second consecutive month exceeding the $1 billion threshold.
However, these figures require nuance. The Paymentscan series has been restated to include previously unattributed issuer flows and to shift from on-chain top-up tracking to self-reported spend figures for platforms like RedotPay, which alone accounts for approximately 36% of the headline volume. When filtering for purely on-chain observable spend, the volume is closer to $545 million, reflecting a 55% increase since March 2026.
Concentration remains a critical structural factor. Nearly 42% of the total monthly volume is settled through Rain-affiliated programs. When combined with other major providers, a small cohort of companies facilitates over three-quarters of the entire tracked market. This concentration suggests that while the industry is scaling, it is also becoming increasingly reliant on a handful of underlying infrastructure providers.

The Five Custody Models
To understand the risk, one must categorize how these cards manage assets. Research into 18 leading programs reveals five distinct custody models, ranked from the weakest to the strongest user protection:
- Sold to the Operator: In this model, as seen with KAST, assets transferred to the platform are legally considered sold to the company. The user essentially holds an unsecured debt claim against the operator.
- Held in Custody for the User: Platforms like RedotPay and Revolut act as custodians. While legal title often remains with the user, these assets are typically subject to general liens and creditor claims in the event of insolvency.
- Fiat Conversion at a Licensed Issuer: Programs like Crypto.com and Kraken convert crypto to fiat immediately upon sale. In the EU, these funds are subject to "safeguarding" regulations, which provide statutory protection against insolvency.
- Program-Pool Smart Contracts: This model, utilized by Avici and Rain, places user funds in smart contracts. While "non-custodial" in spirit, the program manager often retains upgrade authority, as demonstrated by the August 28 exploit.
- Self-Custodial Vaults: The strongest tier, exemplified by Gnosis Pay and Ether.fi, uses smart account modules that prevent the operator from accessing user funds, typically relying on time-locked modules or user-controlled multisig keys.
The "Third National" Connection
A significant portion of the self-custodial card market relies on an entity known as "Third National." While marketing materials often frame this as a bank, the entity is a Puerto Rico-based money transmitter and an affiliate of Signify Holdings (Rain).
The reliance on a non-bank issuer for credit-card-style settlement highlights the complexity of the "stablecoin-powered" payment model. When a user taps their card, Visa settles with the merchant, and Rain settles with Visa using borrowed stablecoin liquidity, later clawing back the funds from the user’s smart contract. This creates a reliance on institutional liquidity that, while efficient, introduces systemic risk if the underlying program manager faces operational or regulatory hurdles.
Regulatory and Structural Implications
The regulatory environment is shifting rapidly. With the European Union’s Anti-Money Laundering Regulation (Regulation 2024/1624) set to take effect in July 2027, the "no-KYC" (Know Your Customer) model faces a potential existential threat. The new rules effectively bar anonymous crypto-asset accounts and prohibit EU acquirers from processing transactions from anonymous prepaid cards issued in third-party jurisdictions.
The failure of the Gnosis Pay consumer interface in September 2026, alongside the winding down of other infrastructure providers like Kulipa and the loss of Paytend’s license, underscores the fragility of these programs. In many instances, the shutdown of a service is not decided by the consumer-facing brand, but by the underlying bank or payment network.
Lessons from the August Breach
The August 28 incident was not a failure of "self-custody" as a concept, but a failure of operational transparency. The users who lost funds held their own keys, but they relinquished control to a smart contract architecture where the upgrade authority was held by a single, centralized key—a detail that was not explicitly disclosed in user-facing documentation.
The fact that users were reimbursed is a testament to the venture-backed capital reserves of the platforms involved. However, relying on the benevolence of a private company to cover losses is a far cry from the technical, trustless guarantees promised by decentralized finance. As the sector matures, the focus must shift from marketing "non-custodial" status to providing verifiable audits of contract upgrade authorities, clear legal definitions of asset ownership during insolvency, and transparent reporting on the identity and regulatory standing of the card issuer.
The industry is clearly at an inflection point. As volume crosses the billion-dollar mark, the "black box" nature of card infrastructure—where users cannot see who holds the upgrade keys or how the settlement is financed—represents the most significant tail risk for the average consumer. For the 11 million transactions occurring monthly, the question remains: is the user a participant in a decentralized network, or simply a creditor to a new type of digital bank? The answer, as of late 2026, is that for most, it is the latter.