• Home
  • About Us
  • Contact Us
  • Cookies Policy
  • Disclaimer
  • DMCA
  • Privacy Policy
  • Terms and Conditions
Dr Crypton
Secure Your Future in Crypto
Cryptocurrency News

Jumper Spins Out as an Independent Onchain Super-App and Announces Debut JUMP Token Sale via Legion

by admin September 28, 2026
written by admin

BRITISH VIRGIN ISLANDS — In a significant structural evolution for the decentralized finance (DeFi) sector, Jumper, a leading consumer application for moving and trading assets across blockchain networks, has officially announced its transition into an independent entity. Previously incubated within LI.FI, the platform is carving out a distinct operational identity backed by robust usage metrics, including more than $40 billion in lifetime trading volume and a loyal base exceeding 100,000 monthly active users. Concurrently, Jumper has revealed plans for its inaugural JUMP token sale through the Legion platform, marking a pivotal milestone in the protocol’s lifecycle as it sets its sights on broader market dominance.

The strategic spin-out signifies a major maturity phase not only for Jumper but also for its parent incubator, LI.FI. Moving forward, the two organizations will operate as distinct entities positioned at complementary layers of the Web3 technology stack. While LI.FI continues to focus on orchestration infrastructure and cross-chain routing architecture, Jumper will concentrate its efforts on being the premier consumer-facing application. This structural division allows each team to optimize its operational roadmap, dedicating specialized capital, distinct leadership, and focused engineering resources to their respective core competencies.

Evolution from Bridging Leader to Comprehensive Onchain Super-App

Since its inception, Jumper has established itself as a cornerstone of cross-chain liquidity management. By simplifying the often fragmented process of transferring value between disparate blockchain networks, the platform captured a dominant market share, establishing itself as the premier aggregator by bridging volume with over 15% of the total market. However, leadership’s vision has consistently extended beyond simple asset transfer. The platform is actively expanding its suite of financial products to transform into a unified "super-app" for onchain finance—a single portal where users can seamlessly execute swaps, bridge tokens, access high-yield opportunities, trade perpetual futures, and interact with tokenized real-world assets (RWAs) such as traditional equities.

The core philosophy driving this expansion is user-centric consolidation. In the current fragmented blockchain ecosystem, retail and institutional traders frequently find themselves navigating dozens of separate interfaces, liquidity pools, and network-specific bridges to execute basic multi-step investment strategies. Jumper aims to abstract away this underlying technical complexity. By unifying diverse protocols, liquidity venues, and blockchain networks behind a singular, intuitive interface, the application bridges the gap between traditional financial expectations and decentralized execution.

According to Marko Jurina, CEO of Jumper, the platform’s foundational success in bridging was merely the entry point to a much larger market opportunity. As an increasing volume of traditional financial instruments, commodities, and corporate securities migrate onto public ledgers, the demand for unified access points will scale exponentially. Jurina notes that the company’s strategic objective is to position Jumper as the default application that users open whenever they need to deploy, trade, or move value across the decentralized economy.

Chronology and Strategic Milestones
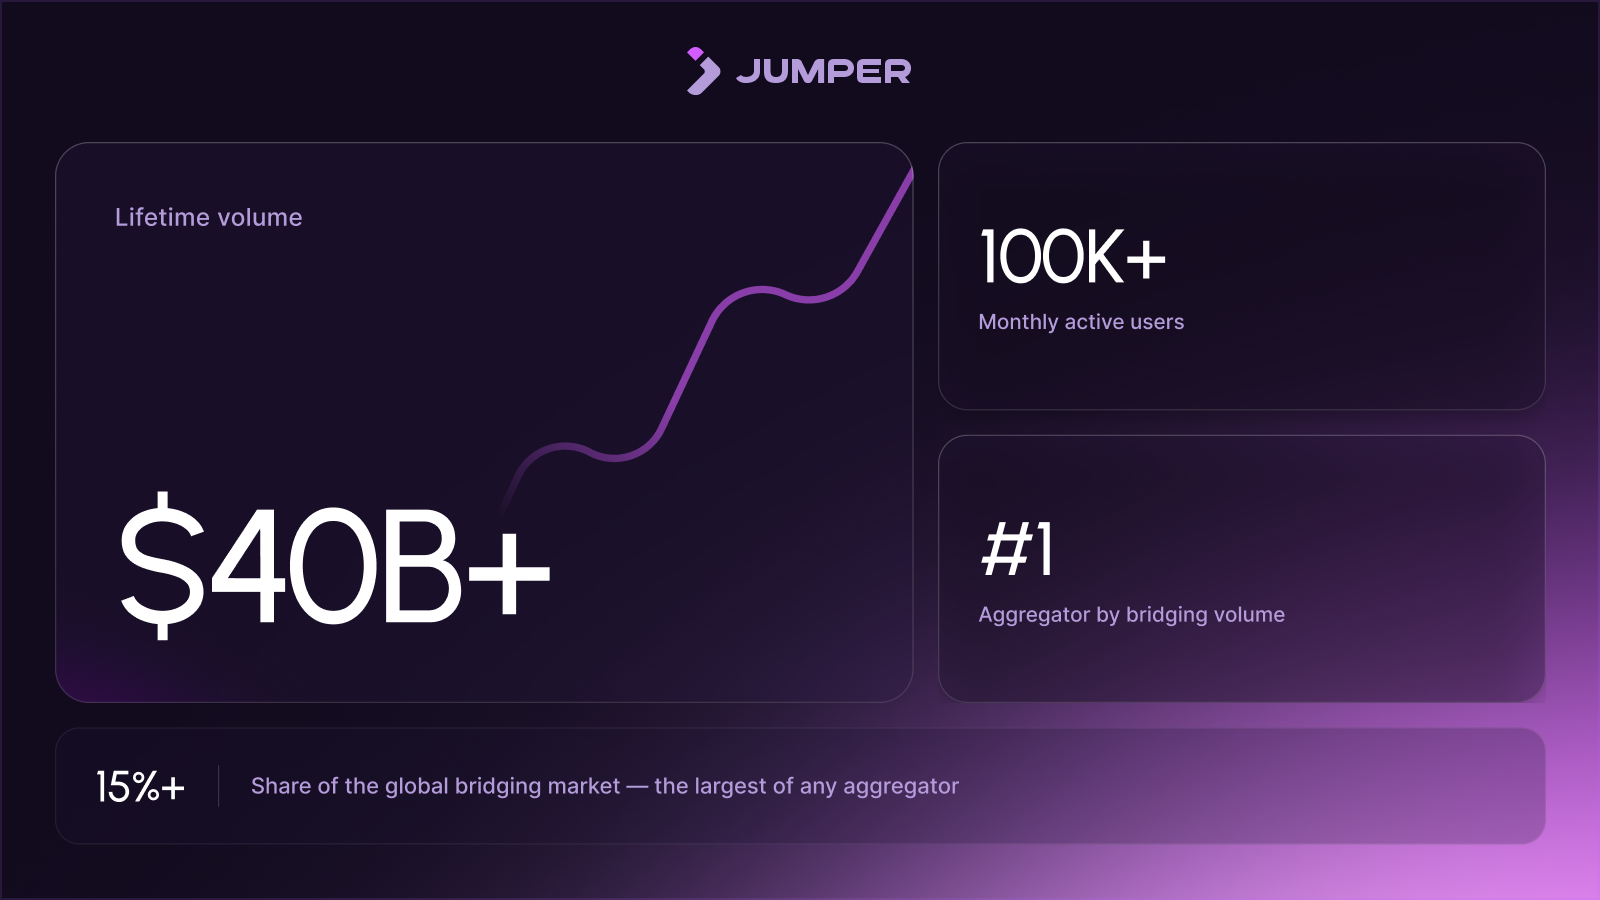
Jumper to Launch JUMP Token Sale on Legion as it Spins Out to Build the Super-App for Onchain Finance

The journey toward full independence and tokenization has been characterized by deliberate architectural and product milestones. Understanding the trajectory of Jumper requires examining the sequence of developments that have shaped its current market standing:

  • Incubation and Foundation (LI.FI Era): Jumper was originally conceived and developed under the umbrella of LI.FI, leveraging the latter’s advanced cross-chain bridging infrastructure to build an intuitive, user-friendly frontend.
  • Volume and User Milestones: Through continuous feature rollouts and strategic liquidity integrations, the application crossed the $40 billion threshold in cumulative lifetime volume while sustaining a monthly active user base exceeding 100,000 participants.
  • Diversification into RWAs and Advanced Trading: The platform expanded its offering beyond native cryptocurrencies and meme assets, integrating yield-generating mechanisms and paving the way for advanced trading verticals.
  • Independence and Spin-Out Announcement: Leadership formally initiated the corporate and structural carve-out, establishing Jumper as a standalone entity with dedicated capital, management structures, and a localized roadmap.
  • Upcoming Launch of Jumper Perps: Slated for release in the coming weeks, the integration of perpetual futures aggregators represents the next major product milestone, designed to capture high-value derivatives trading volume.
  • Debut JUMP Token Sale via Legion: Scheduled as the platform’s first-ever capital-raising event, the Legion token sale will fuel the next phase of expansion, ecosystem development, and user acquisition.

Expanding Product Ecosystem: The Arrival of Jumper Perps

A critical driver behind Jumper’s growth strategy is the continuous introduction of high-margin, high-demand trading verticals. The platform’s upcoming product release, Jumper Perps, is designed to aggregate leading perpetual futures venues into a single, cohesive trading environment. Derivatives trading represents a massive share of total crypto market volume, yet executing perpetual trades often requires specialized platforms that lack integration with broader spot and bridging infrastructure.

By embedding perpetual futures directly into the Jumper ecosystem, the platform creates a powerful synergy. Users can manage their spot portfolios, bridge assets across networks, and open leveraged positions within the same interface. Each newly introduced product vertical functions as an organic catalyst for protocol revenue and volume growth, providing existing users with compelling incentives to centralize their entire onchain financial activity within a single application environment. Furthermore, this multi-product approach shields the protocol from cyclical downturns in any single market sector, balancing spot trading fees with derivatives revenue and yield-aggregation streams.

A Token-First Ownership Model and the Legion Capital Raise

Perhaps the most disruptive aspect of Jumper’s current transition is its approach to capital formation and governance alignment. Unlike traditional web3 and fintech ventures that frequently conduct separate private equity financing rounds alongside public token generation events, Jumper has made a definitive structural choice: it is bypassing traditional equity fundraising in favor of a unified, token-first model.

The upcoming token sale, hosted on the Legion platform, represents the first time Jumper has raised external capital. Crucially, the proceeds generated from the JUMP token sale will be deployed directly to accelerate product development, drive user acquisition, and expand distribution networks. Because there is no parallel equity tier, the JUMP token serves as the exclusive instrument for value capture, governance participation, and economic exposure.

In this framework, everyday users, early contributors, and strategic investors all hold the exact same asset class. This deliberate alignment aims to eliminate the historical friction often observed in crypto projects, where early venture capital equity holders and retail tokenholders possess divergent financial incentives and exit timelines.
Jumper to Launch JUMP Token Sale on Legion as it Spins Out to Build the Super-App for Onchain Finance

Addressing the Industry Paradigm Shift

In commentary surrounding the spin-out and token launch, CEO Marko Jurina emphasized that the decision to implement a token-first ownership structure reflects a broader philosophical critique of prevailing industry norms. For years, many blockchain-based projects have treated utility tokens as marketing add-ons or secondary mechanisms detached from the core underlying business operations. Jurina argues that this legacy model is fundamentally flawed and undermines the original promise of decentralization.

According to leadership, if the blockchain industry is genuinely committed to pioneering new economic models of ownership, the individuals who actively utilize, support, and build these platforms must have direct participation in the financial value they generate. By establishing JUMP as the sole vehicle for enterprise exposure, Jumper seeks to set a new benchmark for corporate governance and stakeholder alignment in the decentralized technology sector. The company hopes to catalyze a broader industry-wide standard where application ownership is democratized from day one.

Broader Market Implications and Future Outlook

The spin-out of Jumper and its upcoming JUMP token generation event occur against a backdrop of rapid maturation within the decentralized finance sector. As modular blockchain architectures proliferate and Layer-2 scaling networks multiply, user fragmentation has emerged as one of the primary hurdles to mass adoption. Consumers are increasingly fatigued by the cognitive load required to track gas tokens, manual bridging routes, and siloed application interfaces.

Super-apps like Jumper represent a structural solution to this fragmentation. By abstracting the backend mechanics of multi-chain routing and bundling diverse financial services—from spot trading and yield generation to perpetual contracts and real-world asset exposure—into a unified consumer touchpoint, the platform addresses the core usability barriers facing the industry.

The success of the Legion token sale and the subsequent rollout of Jumper Perps will serve as a crucial test case for token-first business models in Web3. If Jumper can successfully demonstrate that a standalone application powered exclusively by a unified token economy can scale efficiently and compete with traditional equity-backed fintech giants, it may well chart a new blueprint for entrepreneurial growth in the decentralized era. With $40 billion in proven volume already secured, Jumper enters this next chapter not as an untested concept, but as an established market leader ready to redefine the boundaries of onchain finance.
September 28, 2026 0 comment
0 FacebookTwitterPinterestEmail
Blockchain Technology

BSV Blockchain Ecosystem Evolution and the Emerging Infrastructure for Digital Asset Custody

by admin September 28, 2026
written by admin

The Bitcoin SV (BSV) ecosystem, historically defined by a philosophy of high-velocity utility and micropayment-focused development, is undergoing a significant shift in its infrastructure landscape as of September 2026. For years, the network’s development culture prioritized the "spend-and-build" ethos, encouraging users to leverage the blockchain for data storage, tokenization, and rapid transactions rather than long-term asset retention. However, a recent maturation in security tooling, coupled with evolving global regulatory discourse regarding digital identity, suggests that the network is entering a new phase of institutional readiness.

The current market valuation of BSV—trading at approximately 4% of its April 2021 all-time high of $489.75—reflects a period of prolonged downward pressure. Market analysts point to several contributing factors: a lack of user-friendly cold storage solutions, limited institutional on-ramps, and a broader, often hostile, media environment that frequently misaligned the project’s technical capabilities with its public perception. With the introduction of robust security hardware and the potential for regulatory alignment with self-sovereign identity frameworks, the ecosystem is now attempting to bridge the gap between its high-performance technical architecture and the practical requirements of long-term investors.

A Chronology of Infrastructure Development

The month of September 2026 marked a departure from the status quo for BSV, specifically concerning custodial security. On September 8, 2026, the community saw the introduction of the PiWallet, an open-source, air-gapped hardware wallet built on the Raspberry Pi architecture. The device addresses the long-standing critique that BSV lacked a verifiable, cold-storage mechanism. By utilizing an offline system that avoids Wi-Fi, Bluetooth, or Ethernet connectivity, the PiWallet allows users to sign transactions via animated QR codes. This design choice removes the reliance on third-party firmware update servers or proprietary hardware manufacturers, effectively democratizing the security layer for the network.

Following this development, on September 16, 2026, the team behind Yours Wallet released version 5.1.0, which introduced a mandatory USB Security Key feature. This update provides a middle-ground solution for users who require enhanced security without the complexity of a fully air-gapped device. By requiring a physical, external drive to unlock the wallet in conjunction with a user password, the update introduces a multi-factor authentication (MFA) layer to the browser-based extension. These two developments, while distinct in their approach, collectively represent the first meaningful step in years toward resolving the "custody deficit" that has hampered BSV’s adoption among risk-averse holders.

Regulatory Alignment and Digital Identity

The timing of these technological upgrades coincides with a broader shift in the regulatory environment, particularly in the United States. On September 23, 2026, SEC Commissioner Hester Peirce delivered a pivotal address at the SIFMA Digital Assets Conference. Her remarks highlighted the necessity for a regulatory framework that encourages the adoption of attribute-based credentials—a system where individuals are verified once by a trusted entity, with that verification then serving as a reusable credential across various financial and institutional platforms.

This vision of self-sovereign identity mirrors the technical implementation of projects like Sigma Auth, which leverages the BSV blockchain to store verified account facts in a user-controlled wallet. The implications of this are profound: if regulators move toward a framework that supports permissionless, blockchain-based identity, the BSV network—which already possesses the throughput to handle such identity rails—could find itself at the center of a new institutional standard.

Latest Blockchain News, BSV Insights, and AI Web3 Trends from CoinGeek

Furthermore, the SEC’s September 17 Innovation Exemption has paved the way for tokenized stocks to be managed via smart contracts on public, permissionless distributed ledgers. As institutions like Nasdaq prepare for 23-hour trading cycles, the requirement for "auditable and public" infrastructure becomes a critical differentiator. BSV’s architecture, characterized by its UTXO-based token standard and massive scalability, is technically optimized for these specific requirements, creating a potential point of divergence between it and layer-2 solutions that rely on centralized settlement queues.

Analyzing the Market Asymmetry

The disparity between the technical capabilities of the BSV blockchain and its current market position is frequently cited as a "value asymmetry." With a market capitalization of approximately $430 million as of late September 2026, the asset occupies a significantly different tier than larger, more liquid networks. The central argument for a re-evaluation of the asset’s position lies in the historical lack of infrastructure. For five years, the narrative was focused on immediate usage, which, while beneficial for network throughput, failed to build the "savings" culture required for sustained capital appreciation.

The absence of a yield-generation narrative, combined with a lack of institutional-grade custodial support, created a vacuum that effectively barred the entry of conservative capital. However, the introduction of the PiWallet and the USB security key feature in Yours Wallet changes the entry conditions. These tools provide the necessary, albeit basic, infrastructure for users to secure their holdings. As the network matures, the focus is shifting toward whether the market will recognize the utility of a chain that can support high-frequency, permissionless, and scalable financial transactions.

Broader Implications and Future Outlook

The trajectory of the BSV ecosystem is now heavily reliant on two factors: the continued hardening of its custodial infrastructure and the industry-wide transition toward tokenized real-world assets. The move toward 23-hour trading and the increasing demand for instant settlement in financial markets create a natural environment for a blockchain that can handle high transaction volumes at low costs.

While the "spend-and-build" culture remains a core tenet of the community, the shift toward providing options for "saving" marks a significant evolution in the network’s lifecycle. The upcoming months will likely test whether these new security features gain traction among users and whether the broader financial sector will acknowledge the alignment between current regulatory discourse and the technical realities of the BSV protocol.

If the goal of the BSV network is to function as a truly scalable, peer-to-peer electronic cash system, the last few weeks of September 2026 may be viewed in hindsight as the moment the ecosystem finally began to prioritize the foundational security requirements of a global, institutional-grade monetary network. As these tools become more accessible, the barrier to entry for prospective users—and the risk profile for existing ones—will continue to evolve, potentially reshaping the competitive landscape of the digital asset economy.

In summary, the confluence of new custodial hardware, improved MFA wallet features, and a clearer regulatory appetite for blockchain-based identity rails suggests that the BSV ecosystem is positioning itself for a different phase of growth. Whether this will result in a realignment of the asset’s market valuation remains a point of intense debate, but the technical infrastructure is undeniably moving toward a more mature, robust, and secure configuration. The ability to hold, secure, and verify assets on-chain is the bedrock of any financial system; for BSV, the establishment of this bedrock may be the most significant development of the current year.

September 28, 2026 0 comment
0 FacebookTwitterPinterestEmail
Blockchain Technology

MoonPay Expands Into Tokenized Assets With Acquisition of North Capital in All-Stock Deal Valued Over $60 Million

by admin September 28, 2026
written by admin

Crypto payments infrastructure giant MoonPay has officially reached an agreement to acquire North Capital, a prominent registered securities infrastructure provider, in an all-stock transaction valued at more than $60 million, pending standard regulatory approvals. This strategic maneuver marks a pivotal evolutionary step for MoonPay, broadening its operational horizons far beyond traditional cryptocurrency payments and into the rapidly expanding sector of tokenized real-world assets and private securities. By integrating North Capital’s comprehensive regulatory framework and technological stack, MoonPay aims to position itself as a dominant, fully compliant end-to-end infrastructure provider capable of bridging traditional financial systems with the decentralized digital asset economy.

The acquisition brings a robust suite of regulatory credentials and institutional capabilities under the MoonPay umbrella. North Capital is well-known within the financial technology sector for enabling companies to raise capital seamlessly through specialized regulatory exemptions. Crucially, the firm operates the PPEX Alternative Trading System (ATS), a digital marketplace boasting more than 1,250 eligible securities that has collectively supported over $8.7 billion in transaction volume. Furthermore, North Capital holds vital regulatory registrations as a broker-dealer, a transfer agent, and an investment advisor. MoonPay has confirmed that these comprehensive brokerage and advisory business lines will be directly integrated into its existing global infrastructure platform, allowing the firm to facilitate compliant issuance, trading, and settlement of digital securities on a global scale.

Understanding the Genesis and Chronology of the Deal

The path toward this acquisition reflects the broader, accelerating convergence between traditional capital markets and blockchain-based tokenization. Over the past several years, MoonPay established itself as a premier fiat-to-crypto on-ramp and off-ramp service, partnering with major global brands, wallets, and decentralized applications to simplify the user purchasing experience. However, as the digital asset landscape matured, executive leadership recognized that the next wave of financial innovation would not merely involve speculative cryptocurrencies, but the tokenization of traditional financial instruments, including private equity, real estate, debt instruments, and institutional funds.

Concurrently, North Capital spent years building out its compliance-first architecture. Recognizing the strict regulatory parameters governing securities in the United States and international jurisdictions, North Capital focused on acquiring the necessary licenses—such as FINRA broker-dealer status—to ensure that digital asset innovators could operate legally within established legal boundaries. The culmination of these efforts made North Capital an attractive acquisition target for infrastructure giants like MoonPay, which sought to bypass the lengthy and costly process of obtaining independent regulatory approvals from scratch.

Strategic Data and Market Footprint

MoonPay buys North Capital, including ATS for tokenized securities

To fully grasp the magnitude of this transaction, one must examine the operational scale of North Capital within the alternative trading ecosystem. Operating the PPEX ATS, the firm has successfully processed billions of dollars in transaction volume, providing a vital lifeline for private companies seeking liquidity outside of traditional public exchanges.

Private markets have historically suffered from severe structural inefficiencies, including illiquidity, lengthy settlement times, high intermediaries’ fees, and extreme market fragmentation. North Capital’s infrastructure was specifically engineered to alleviate these pain points by utilizing digital ledger technology and automated compliance protocols. By absorbing this infrastructure, MoonPay acquires not only the software and regulatory licenses but also an established client roster of issuers, investors, and broker-dealers who rely daily on the PPEX ATS for secondary market liquidity.

The Agora Network and Industry Governance Implications

One of the most complex and fascinating subplots of this acquisition involves North Capital’s strategic partnership with tZERO, another leading tokenized securities venue. Earlier in the industry’s recent development cycle, North Capital and tZERO joined forces to launch Agora, an innovative inter-ATS routing network designed to connect disparate alternative trading systems.

The primary objective behind Agora was to solve the persistent problem of liquidity fragmentation that has historically plagued private and tokenized securities markets. Rather than forcing qualified institutional participants to remain siloed within a single, isolated trading venue, Agora created a routing network enabling cross-venue discovery and order execution. The network achieved a major operational milestone in July when it successfully executed its first routed order among qualified institutional participants.

However, MoonPay’s acquisition of North Capital introduces intricate governance questions regarding the future of the Agora network. Because Agora was originally conceived as a collaborative, neutral initiative between independent ATS operators, the absorption of North Capital into a vertically integrated corporate entity—one that simultaneously owns transaction routing technology, digital payment rails, and now a primary ATS—changes the competitive dynamics. Industry analysts and market participants will be closely monitoring how governance, neutrality, and data-sharing protocols within Agora are managed moving forward to ensure that competing venues feel comfortable participating in a network partially owned by a direct competitor.

Broader Industry Impact and Market Implications

MoonPay buys North Capital, including ATS for tokenized securities

The $60 million all-stock transaction is emblematic of a broader macroeconomic and technological trend: the institutionalization and tokenization of real-world assets (RWA). Financial institutions, asset managers, and fintech giants are increasingly investing heavily in blockchain infrastructure to reduce administrative overhead, accelerate settlement cycles to near-instantaneous speeds, and unlock fractional ownership models for high-value assets.

By combining MoonPay’s frictionless user experience, global payment processing rails, and massive retail footprint with North Capital’s institutional-grade regulatory stack and ATS capabilities, the combined entity creates a formidable powerhouse. MoonPay is effectively building a comprehensive bridge that allows traditional financial institutions to issue, market, trade, and settle tokenized securities with the same regulatory rigor they expect from legacy financial systems, combined with the technological efficiencies of distributed ledger networks.

Furthermore, this move signals a maturation phase in the cryptocurrency and fintech merger-and-acquisition landscape. Early-stage crypto companies are no longer just acquiring smaller protocols for niche developer talent or decentralized finance (DeFi) primitives; they are aggressively acquiring regulated, licensed legacy financial institutions to achieve full regulatory compliance and institutional legitimacy. As global regulatory bodies—such as the U.S. Securities and Exchange Commission (SEC) and international counterparts—intensify their oversight of digital assets, possessing recognized legal registrations like broker-dealer and transfer agent licenses has transitioned from a competitive advantage into an absolute necessity for survival and growth.

Looking Ahead: Regulatory Approvals and Integration Roadmap

As the ink dries on the initial acquisition agreement, all eyes turn toward the regulatory review process. Because the transaction involves regulated entities holding broker-dealer registrations and operating an Alternative Trading System, formal approvals from regulatory bodies such as the Financial Industry Regulatory Authority (FINRA) and potentially other federal and state agencies will be required before the deal can reach final closing.

Once regulatory clearance is achieved, the integration phase will test MoonPay’s operational capabilities. Merging a technology-first consumer crypto payments firm with a compliance-heavy, highly regulated securities infrastructure provider requires meticulous cultural and technical alignment. If executed successfully, the acquisition could establish a new blueprint for how fintech and crypto enterprises scale into traditional financial markets, accelerating the mainstream adoption of tokenized assets and reshaping the future of global capital formation.

September 28, 2026 0 comment
0 FacebookTwitterPinterestEmail
Blockchain Technology

North Korean Hackers Suspected in Massive $351 Million Bitget Cryptocurrency Exchange Heist

by admin September 28, 2026
written by admin

Cryptocurrency exchange Bitget has suffered a devastating cyberattack resulting in the unauthorized transfer of more than $351 million in digital assets. The breach, which occurred on Thursday, has immediately been flagged by cybersecurity experts and exchange leadership as bearing the unmistakable hallmarks of state-sponsored cyber warfare originating from North Korea.

This multi-million-dollar heist officially stands as the largest digital currency theft recorded globally this year. It eclipses a major security breach from earlier in September, which involved a $340 million theft—though that incident concluded with the hacker unexpectedly returning the vast majority of the funds, leaving a net loss of $47 million. In contrast, the perpetrators behind the Bitget attack have shown no inclination toward returning the stolen capital, leaving the digital asset community on high alert as regulatory bodies and blockchain investigators race to trace the laundered funds.

Main Facts and the Anatomy of the Breach

The cyberattack struck Bitget’s infrastructure, specifically targeting its hot wallets. In the architecture of cryptocurrency exchanges, hot wallets are digital storage solutions connected directly to the internet to facilitate fast, active trading and liquidity for users. While essential for daily exchange operations, these internet-facing wallets represent a significantly higher risk profile compared to cold storage offline wallets, making them prime targets for sophisticated threat actors.

During the Thursday intrusion, unauthorized actors managed to bypass internal security protocols and drain vast quantities of cryptocurrency from these active liquidity pools. The exact vector of the attack—whether it involved compromised administrative credentials, zero-day vulnerabilities in the exchange’s application programming interfaces (APIs), or sophisticated social engineering campaigns targeting internal developers—remains under active investigation by third-party cybersecurity forensics teams and law enforcement agencies.

Immediately following the detection of abnormal outflow volumes, Bitget enacted emergency protocols. The platform took the decisive step of suspending all cryptocurrency deposits and withdrawals across its network to prevent further drainage of user assets. As of publication, exchange leadership has not provided a definitive timeline regarding when standard withdrawal functionalities will be restored, emphasizing that security audits must be completed comprehensively before normal operations can resume.

Chronology of Events

The unfolding crisis followed a rapid timeline over a 48-hour period:

  • Thursday Morning: Abnormal, unauthorized transactions are detected moving out of Bitget’s hot wallets. Automated security alerts trigger internal reviews, and executive leadership is notified.
  • Thursday Afternoon: Bitget officially halts all cryptocurrency withdrawals to contain the bleeding. Initial internal assessments reveal that losses have surpassed the $300 million threshold.
  • Thursday Evening: Bitget releases its first public statements across social media channels, confirming the security incident and assuring users that internal safety nets are available.
  • Friday: CEO Gracy Chen issues statements pointing the finger toward North Korean threat groups based on behavioral patterns. Blockchain intelligence agencies release telemetry supporting the state-sponsored hypothesis.
  • Friday Afternoon: Industry analysts begin contextualizing the heist against historical trends, confirming it as the largest single crypto theft of 2026.

Supporting Data and the Growing Threat of State-Sponsored Crypto Heists

The scale of the Bitget breach highlights a troubling macroeconomic trend within the digital asset economy: the increasing professionalization and frequency of state-backed cybercrime. According to data compiled by prominent blockchain intelligence firm TRM Labs, North Korea-linked threat actors are responsible for approximately 75 percent of all stolen cryptocurrency value throughout 2026.

What makes the North Korean cyber warfare apparatus particularly dangerous is its methodical evolution. Historically known for direct spear-phishing campaigns against exchange employees, groups such as the Lazarus Group and associated state-backed syndicates have increasingly expanded their attack vectors. Modern campaigns frequently involve complex supply-chain attacks, compromising open-source software libraries used by financial technology firms, and executing elaborate, multi-month social engineering schemes designed to infiltrate high-value cryptocurrency infrastructure.

North Korean hackers suspected in $351M crypto theft, the largest so far this year

For North Korea, these illicit operations serve as a vital financial lifeline. International economic sanctions have severely constrained the regime’s traditional avenues of revenue generation, forcing Pyongyang to pivot heavily toward cyber-enabled financial theft. The digital proceeds are widely documented by international intelligence agencies and United Nations panels as a primary funding mechanism for the regime’s prohibited ballistic missile and nuclear weapons development programs. Consequently, what begins as a cybersecurity incident at a commercial exchange ultimately transforms into a matter of global geopolitical security.

Official Responses and Mitigation Efforts

In the wake of the breach, Bitget executive leadership moved swiftly to reassure panicked account holders and stabilize market confidence. In a series of official updates published on the social media platform X, the exchange confirmed the freezing of operations and addressed user solvency concerns head-on.

Bitget Chief Executive Gracy Chen publicly addressed the nature of the attack, noting that the methodology, velocity, and execution of the heist were “highly consistent with known patterns of North Korean hacker organizations.” Chen’s assessment aligns closely with the consensus of independent cybersecurity researchers who track advanced persistent threat (APT) groups operating out of East Asia.

Crucially, Bitget sought to mitigate user panic by highlighting its financial safety reserves. The company formally announced that its dedicated user protection fund currently sits at $464 million. Because this reserve exceeds the estimated $351 million value of the stolen assets, Bitget leadership has expressed confidence that user balances will remain fully protected and that no individual customer will ultimately bear the financial burden of the compromise.

Despite these assurances, financial analysts note that maintaining user trust in the wake of a nine-figure breach remains an uphill battle. The indefinite suspension of withdrawals has created liquidity bottlenecks for active traders, many of whom are demanding greater transparency regarding how the unauthorized access was achieved in the first place.

Broader Impact and Implications for the Crypto Industry

The Bitget incident serves as a stark reminder of the persistent vulnerabilities plaguing centralized financial intermediaries within the Web3 ecosystem. While decentralized finance (DeFi) protocols have historically accounted for a large share of security exploits, major centralized exchanges remain lucrative honeypots for state-sponsored syndicates commanding advanced technical capabilities.

The heist is expected to trigger increased scrutiny from international financial regulators and compliance watchdogs. Regulators in major jurisdictions—including the United States, the European Union, and Asia-Pacific financial hubs—have increasingly pressured cryptocurrency exchanges to adopt rigorous institutional-grade security frameworks, mandatory proof-of-reserves audits, and advanced anti-money laundering (AML) controls to track stolen capital as soon as it hits the blockchain.

Furthermore, blockchain analytics firms and cross-chain bridging platforms are currently on high alert. When sophisticated hackers loot hundreds of millions of dollars in digital assets, their immediate challenge is laundering the capital without leaving a permanent, traceable footprint. Security researchers and decentralized finance protocols are actively blacklisting wallet addresses associated with the Bitget heist, creating friction for the attackers as they attempt to mix, bridge, and cash out the stolen funds through illicit over-the-counter (OTC) broker networks.

As the investigation continues, the focus remains on forensic blockchain tracking and the eventual reopening of Bitget’s platform. For the broader cryptocurrency industry, the $351 million heist underscores an uncomfortable reality: as long as digital assets remain lucrative, highly liquid, and easily transferrable across borders, exchanges will remain primary targets in an ongoing cyber arms race against nation-state adversaries.

September 28, 2026 0 comment
0 FacebookTwitterPinterestEmail
Cybersecurity & Hacking

Court-Ordered Seizure of Radaris.com Marks Milestone in Enforcement of Daniel’s Law

by admin September 28, 2026
written by admin

The consumer data broker Radaris.com, long notorious for ignoring removal requests and scrubbing personal data from its expansive people-search network, has faced a severe legal reckoning. In a landmark enforcement action, a New Jersey judge ordered the transfer of radaris.com and more than a dozen associated data broker domains to the plaintiffs following extensive stonewalling and evasive legal maneuvering by the company.

The forfeiture stems from a lawsuit filed in February 2024 by Atlas Data Privacy Corp. The legal challenge targets data brokers accused of violating a stringent New Jersey privacy statute known as Daniel’s Law. Enacted following a tragic family shooting involving the son of a federal judge, the legislation protects state law enforcement personnel, government officials, judges, and their families by compelling commercial data brokers to completely remove their personal information. The statute carries a penalty of $1,000 per violation for entities that ignore removal requests.

The fallout from the Radaris litigation exposes deep structural vulnerabilities in the global data brokerage ecosystem. By blending complex corporate shell games, fictitious executive identities, and aggressive litigation tactics, Radaris operated with impunity for over a decade. The intervention by Atlas Data Privacy Corp and the subsequent court-mandated domain seizures represent a major disruption to a business model that has historically relied on the exhaustion of its legal opponents.

Anatomy of a Corporate Shell Game

The operations behind Radaris trace back to Russian-born brothers Igor and Dmitry Lubarsky, who reside in Massachusetts and manage a vast portfolio of people-search engines, affiliate programs, and foreign-language dating platforms. Just weeks after Atlas initiated legal proceedings in early 2024, investigative reporting revealed the structural framework of the brothers’ network. Rather than directly confronting the allegations, attorneys representing the Lubarskys threatened defamation lawsuits and claimed the true owners were Ukrainian nationals living in Ukraine.

Subsequent investigations dismantled these assertions, uncovering that Radaris and its sister companies utilized a fictitious chief executive officer named "Gary Norden." Boston Law Group attorney Val Gurvits, representing Radaris, later admitted to the invention of the pseudonym. Court records and promotional materials revealed that the company had repeatedly deployed the fake executive in press releases to secure venture capital and attract investors.

Data Broker Radaris Loses Domains in Privacy Fight – Krebs on Security

As legal pressure intensified, the defendants engaged in what Atlas CEO Matt Adkisson described as an "island-hopping phase." Corporate registrations shifted dynamically across international tax havens, including the Marshall Islands, the British Virgin Islands, and Cyprus.

"Privacy policies changed constantly, and new entities kept appearing," Adkisson noted. "Behind the scenes, it felt like a shell game. Defense lawyers told the court that certain entities merely operated the domains and were the proper parties to sue. But by the time a judgment neared, those entities would be discarded and new entities would appear."

In one instance, after the defense updated its terms of service to designate a newly formed Marshall Islands enterprise as the managing party, investigators discovered the entity did not even exist legally. This strategy of procedural attrition had previously shielded the network from accountability, most notably in a 2017 class-action lawsuit where Radaris failed to contest claims, leading to a $7.5 million default judgment and an initial, though subsequently halted, domain transfer involving Verisign.

Inside the Interconnected Data Broker Ecosystem

Discovery materials obtained through the litigation—encompassing over 10,000 emails and corporate documents—shed unprecedented light on the financial scale and administrative centralization of the Radaris network.

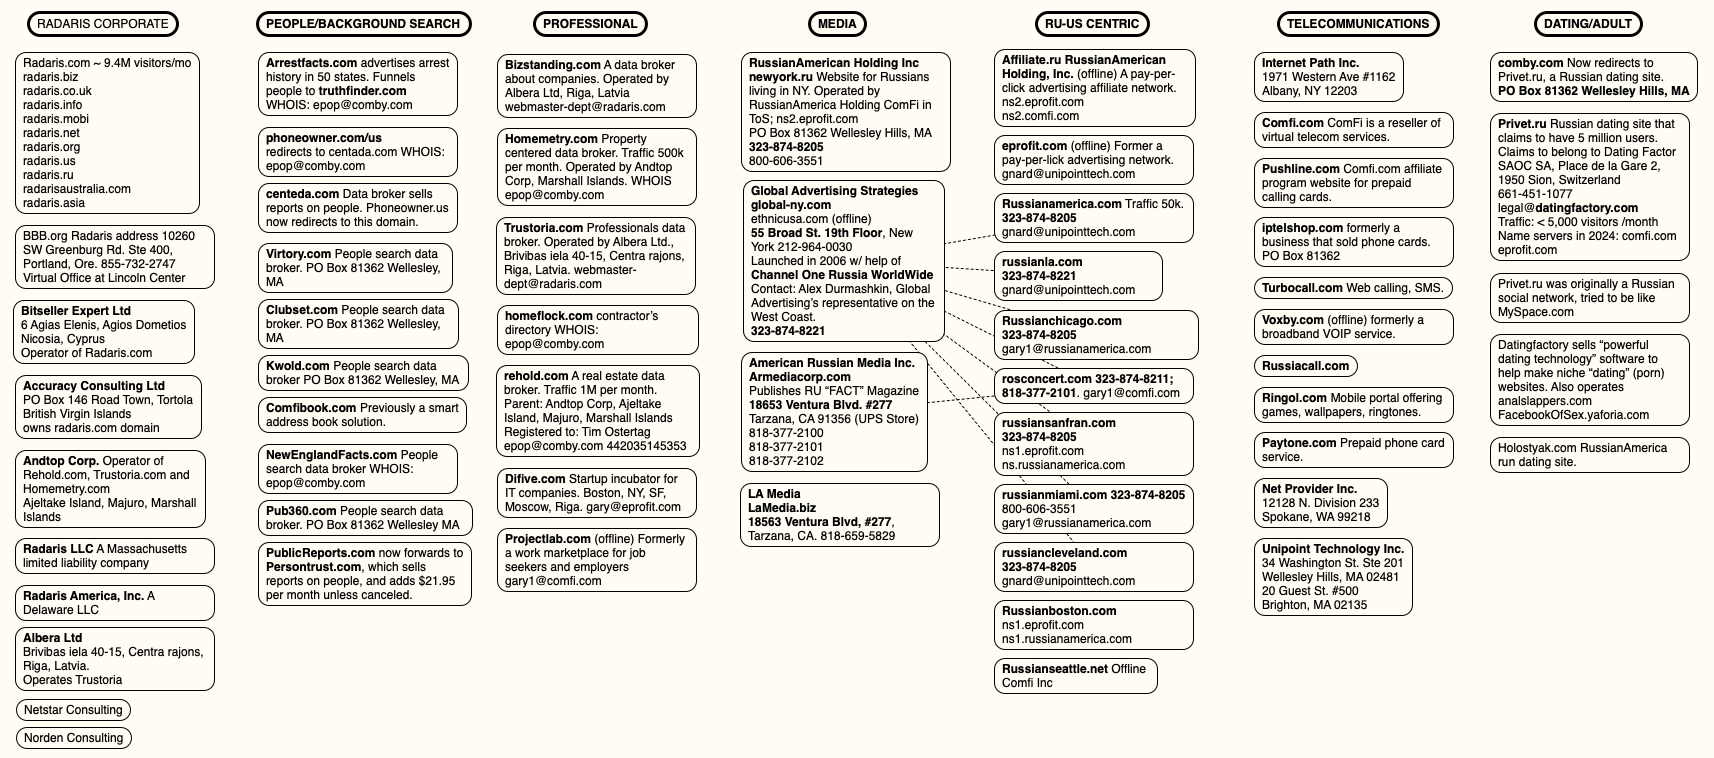
The documents demonstrate that nominal corporate shells—including Radaris America, Inc., Bitseller Expert Limited, Digital Orbit Corp, Core Solutions Group Inc, Lucky Solutions Inc, Virtura Corp, Veripages Inc., Nuform Solutions Inc., Growth Data Advisors Inc., and Property Experts, Inc.—were administered by a core group of three or four individuals. These entities shared financial accounts, payment card systems, virtual office addresses, and core technical infrastructure hosted under mail domains such as difive.com, centerex.com, scienteco.com, and pub360.com.

Financial records uncovered in the discovery process indicate substantial revenue generation across the network. Radaris.com generated approximately $42,000 monthly, while its sister site Veripages.com earned roughly $45,000 per month. These earnings were bolstered by strategic partnerships with major marketing and advertising networks, including the Lifetime Value Company—operator of brands like PeopleLooker, PeopleSmart, NumberGuru, and Bumper.

Data Broker Radaris Loses Domains in Privacy Fight – Krebs on Security

Furthermore, the document corpus revealed financial ties to Onerep, a privacy service that assists consumers in removing personal data from people-search sites. According to Atlas, the Radaris family of websites secured up to $25,000 monthly from partnerships with Onerep. Investigative findings previously tied Onerep’s founder to the creation and operation of competing people-search engines, illustrating a circular business model where companies profit simultaneously from publishing personal data and offering services to remove it.

Constitutional Challenges and the Future of State Privacy Laws

While the New Jersey court has successfully transferred 14 domain names to Atlas—with radaris.com now redirecting to an informational notice regarding the court order—the broader legal battle is far from over.

Radaris and approximately 150 other consumer data brokers targeted by Atlas have mounted a coordinated constitutional defense. Over 70 of these lawsuits have been removed to federal court, with defense attorneys arguing that Daniel’s Law violates the First Amendment by imposing unconstitutional restrictions on the publication of legally gathered public records. The U.S. Court of Appeals for the Third Circuit is currently weighing these constitutional arguments, with legal analysts predicting the dispute will ultimately reach the U.S. Supreme Court.

The legislative landscape surrounding data privacy remains deeply fragmented. Following New Jersey’s lead, at least 14 other states have enacted statutes modeled after Daniel’s Law, while several others have proposed similar measures. However, judicial resistance is emerging on multiple fronts; in August 2025, a federal district court ruled West Virginia’s version of Daniel’s Law facially unconstitutional under the First Amendment.

Broader Implications for 21st Century Data Privacy

Privacy experts point out that state-level statutes, while impactful for targeted groups like law enforcement and judicial officials, fail to address the systemic vulnerabilities affecting the general population. Justin Sherman, a privacy researcher and author examining the data broker industry, emphasizes that federal legislative paralysis continues to leave consumers exposed.

Data Broker Radaris Loses Domains in Privacy Fight – Krebs on Security

"These days at the federal level, add in the intense amount of lobbying against these laws from social media companies, big tech, cryptocurrency firms, and now AI proponents in the mix who claim that limiting their data scraping is somehow going to collapse the whole U.S. economy under Chinese rule," Sherman stated.

Sherman notes that people-search businesses operate legally within the grey areas of existing frameworks, as virtually all state privacy laws exempt records classified as public documents. Voting registries, property filings, marriage certificates, motor vehicle logs, criminal histories, and professional licenses remain freely accessible for commercial exploitation.

The absence of comprehensive federal data protection standards extends beyond traditional people-search engines. While numerous states mandate age-verification protocols for online services—requiring users to submit sensitive documentation such as state-issued driver’s licenses—federal law imposes minimal restrictions on how third-party intermediaries handle, retain, or secure that data. Industry analysts warn that without federal guardrails, high-profile security incidents, such as the recent breach at IDScan.net which exposed the driver’s license data of over 153 million Americans, will continue to threaten consumer security.

As the legal proceedings surrounding Radaris and Daniel’s Law proceed through appellate courts, the outcome is expected to redefine the legal boundaries between commercial speech protections for data brokers and the digital privacy rights of individuals in the United States.

September 28, 2026 0 comment
0 FacebookTwitterPinterestEmail
Cybersecurity & Hacking

Citrix NetScaler Zero-Day Vulnerabilities Under Active Exploitation Spark Urgent Patching Requirements

by admin September 28, 2026
written by admin

Citrix has confirmed that two critical remote code execution (RCE) vulnerabilities in its NetScaler Application Delivery Controller (ADC) and NetScaler Gateway products are currently being exploited in the wild. The disclosure, issued on September 27, 2026, has triggered a global security scramble, as these appliances represent the critical edge of enterprise network infrastructure, serving as primary gateways for VPN access, load balancing, and identity verification. The newly identified flaws, tracked as CVE-2026-88771 and CVE-2026-88772, allow unauthenticated attackers to execute arbitrary code, effectively granting them full control over compromised systems.

Chronology of the Discovery and Disclosure

The revelation follows a period of heightened concern within the cybersecurity community. On September 26, 2026, the security firm watchTowr publicly alerted the industry to rumors of multiple unpatched RCE vulnerabilities targeting NetScaler hardware. The firm noted that, while specific technical details remained scarce at the time, the intelligence regarding active exploitation was highly credible.

The situation escalated rapidly throughout the day. By the late hours of September 26, reports emerged on platforms such as Reddit, where IT administrators shared that their security vendors and upstream suppliers had advised them to pull their NetScaler appliances offline immediately. This precautionary measure was taken in the absence of an official patch, reflecting the severity of the threat. The official Citrix bulletin, released the following morning on September 27, confirmed that the flaws identified by researchers matched the accounts of the ongoing attacks.

Technical Scope and Affected Deployments

NetScaler ADC and Gateway are ubiquitous in corporate environments, acting as the "front door" for remote workforces and cloud-based application access. The current threat is particularly dangerous because one of the two exploited vulnerabilities affects every deployment on an affected version, even those configured with default settings. This means that hardening measures or "security by default" configurations are insufficient to repel an attacker who knows how to weaponize the exploit.

The vulnerability impacts a wide range of customer-managed appliances, including those deployed in Secure Private Access Hybrid configurations. Citrix noted that its own internal cloud services and proprietary Adaptive Authentication modules have already been mitigated. However, for the thousands of organizations relying on on-premises or hybrid hardware, the responsibility for patching rests entirely with the end-user.

Warning: Two Unpatched Citrix NetScaler RCE Zero-Days Under Active Exploitation

Critically, the update requirements extend to systems that were previously patched for earlier vulnerabilities. Appliances running on versions 14.1-73.32 and 13.1-63.21—which were specifically updated in August 2026 to address an authentication bypass flaw (CVE-2026-19490)—remain vulnerable to these new threats and must be upgraded again to the latest security releases.

Broader Implications for Network Security

The emergence of these zero-day exploits highlights a recurring challenge for organizations utilizing edge devices. Because these appliances are positioned at the perimeter, they are among the first points of contact for internet-facing traffic. When a vulnerability is discovered in such a device, the window for remediation is often measured in hours rather than days.

The lack of indicators of compromise (IoC) provided by the vendor presents a significant hurdle for incident responders. Because the exploits occurred before a patch was available, simply applying the software update is insufficient to determine if a breach has already taken place. If an attacker successfully gained a foothold prior to the update, they may retain persistence through backdoors, web shells, or compromised credentials, even after the original vulnerability is patched.

Lessons from Previous Compromises

The cybersecurity industry remains cautious, drawing lessons from the 2025 exploitation of NetScaler vulnerabilities, which targeted organizations in the Netherlands and other regions. During that event, the Netherlands’ National Cyber Security Centre (NCSC) issued stern warnings that patching was merely the first step. The agency emphasized that in many instances of high-level exploitation, attackers had already established long-term access that survived standard firmware updates.

For organizations currently managing these systems, the standard recovery playbook involves more than just clicking "update." Security professionals recommend:

  1. Full Forensic Review: Analyzing system logs, core dumps, and traffic flows for signs of lateral movement.
  2. Credential Rotation: Assuming that any credentials stored on or passing through the NetScaler during the period of vulnerability have been compromised.
  3. Segmentation: Ensuring that the management interface of the NetScaler is not exposed to the public internet, restricting access to internal, audited IP ranges only.
  4. Scripted Integrity Checks: Utilizing specialized forensic tools—such as those historically provided by the NCSC—to scan for malicious file modifications or unauthorized configuration changes.

Official Guidance and Remediation

Citrix has urged all customers to install the relevant patches immediately. In its official support bulletin, the company listed six additional, non-exploited flaws alongside the two critical RCEs, emphasizing that the update is comprehensive.

Warning: Two Unpatched Citrix NetScaler RCE Zero-Days Under Active Exploitation

The inclusion of a fix for the 13.1 branch is particularly notable. This version had reached its "End of Maintenance" milestone on September 15, 2026, under the standard product lifecycle. By providing a fix for an EOM (End of Maintenance) product, Citrix is signaling the severity of the threat, essentially offering a "hotfix" for legacy systems that would otherwise be left exposed.

Analyzing the Threat Landscape

The speed at which these vulnerabilities were weaponized underscores the increasing sophistication of threat actors targeting network appliances. Unlike generic malware, RCE exploits against ADC and gateway products provide attackers with a high-value entry point. From a single compromised NetScaler, an adversary can often perform reconnaissance on the internal network, intercept VPN traffic, or pivot into the data center to deploy ransomware.

The fact that these vulnerabilities were exploited as zero-days—meaning the vendor was unaware of them until active attacks were observed—suggests that the discovery was likely made by highly capable research groups or sophisticated threat actors. The "silent" nature of the initial exploitation, where attackers were able to move through networks undetected for days or weeks before the security community caught wind of the activity, represents a systemic risk to the digital supply chain.

Conclusion: The Path Forward

As of late September 2026, the situation remains fluid. While patches are available, the burden of proof rests on the administrators to verify the integrity of their networks. The reliance on edge-security devices has made companies more efficient, but it has also created a centralized point of failure that, when compromised, offers an outsized reward to malicious entities.

Organizations are advised to prioritize the following actions:

  • Immediate Patching: Validate the version numbers of all NetScaler ADC and Gateway instances and deploy the latest updates provided in the Citrix bulletin (CTX697096).
  • Incident Response Mobilization: Review logs from the period starting in early September to identify any anomalies in traffic patterns or administrative account access.
  • Vigilance: Maintain close contact with managed service providers and monitor official security channels for any secondary guidance or post-exploitation detection scripts that may be released in the coming weeks.

As the industry grapples with these revelations, the event serves as a stark reminder of the necessity for "defense-in-depth." Relying solely on a perimeter device for security is increasingly insufficient; as these vulnerabilities demonstrate, when the gatekeeper is compromised, the entire infrastructure must be treated as hostile until proven otherwise.

September 28, 2026 0 comment
0 FacebookTwitterPinterestEmail
Cybersecurity & Hacking

Bitget Resumes Bitcoin Withdrawals After North Korean Hackers Steal Nearly $400 Million in Massive Cyber Heist

by admin September 28, 2026
written by admin

Cryptocurrency exchange Bitget has officially resumed Bitcoin withdrawals following a temporary, platform-wide freeze enacted last week. The suspension was triggered by a sophisticated security breach that resulted in the theft of hundreds of millions of dollars in digital assets. According to internal investigations and on-chain analytics, the devastating cyber attack has been attributed to state-sponsored hackers operating out of North Korea.

The exchange confirmed that the specific security vulnerability exploited during the breach has been successfully patched and secured. While Bitcoin withdrawals are once again operational, Bitget management has laid out a phased restoration schedule for other supported assets, networks, and fiat channels to ensure systemic stability and safety.

Phased Withdrawal Restoration Schedule

To prevent network congestion and maintain rigorous security oversight, Bitget has instituted a staggered timeline for bringing its remaining withdrawal functions back online.

According to the exchange’s official roadmap, withdrawal services will return in distinct waves:

  • Bitcoin (BTC): Resumed immediately following the initial security patch.
  • Ethereum and Layer-2 Networks (ETH via Ethereum, BSC, Arbitrum, Base, and Optimism): Scheduled to resume on September 29 at 8:00 UTC.
  • Tether and Major Stablecoins (USDT via Ethereum, BSC, Solana, and Tron): Scheduled to resume on September 30 at 8:00 UTC.
  • Remaining Tokens, Fiat, and P2P Assets: Scheduled to open progressively starting October 2 at 8:00 UTC.

Throughout the disruption, Bitget has maintained that trading and deposit functionalities remained fully operational. Executives have repeatedly emphasized that the withdrawal pause was strictly a precautionary defense mechanism rather than a reflection of liquidity insolvency or asset depletion.

"The temporary withdrawal pause remains a security measure and is not related to the availability of user assets. User account balances remain unaffected, and Bitget’s Protection Fund covers the financial impact of this platform-wide incident," the company stated in a public announcement. Furthermore, leadership confirmed that the threat has been entirely contained, ensuring that no further unauthorized transfers can take place.

Chronology of the Breach

The unfolding crisis began late last week when automated security monitoring systems at Bitget detected anomalous transactional behavior. Security teams flagged multiple unauthorized transfers originating from a limited number of the exchange’s hot and warm wallets.

Upon deeper inspection, engineers discovered that malicious actors had successfully breached a critical backend system nested within Bitget’s proprietary wallet infrastructure. By infiltrating this subsystem, the attackers managed to spoof transaction data, effectively tricking the exchange’s automated authorization protocols into approving outbound transfers to external, attacker-controlled addresses.

By Thursday, the scale of the breach became evident, forcing Bitget executives to pull the emergency brake. All withdrawal operations were immediately suspended to stanch the flow of capital out of the ecosystem. Initial estimates placed the losses at roughly $350 million.

However, as blockchain forensics teams conducted more comprehensive tracing, the estimated financial damage was revised upward. On Friday, updated figures released by Bitget—backed by on-chain tracking and transaction classification data—revealed that the final sum stolen in the multi-chain assault totaled an astounding $387.5 million.

Bitget CEO Gracy Chen provided further technical color on the attack, noting that the multi-pronged exploit targeted multiple blockchains, including Ethereum, the XRP Ledger, Arbitrum, Avalanche, Optimism, Binance Smart Chain (BSC), and Base. A wide variety of digital assets were siphoned during the raid, prominently featuring ETH, XRP, BNB, AVAX, USDT, and USDC.

Bitget resumes Bitcoin withdrawals after $387.5 million crypto heist

Attribution to North Korean State-Sponsored Actors

Through intensive on-chain analysis, IP behavior profiling, and tactical tracking, Bitget leadership and independent cybersecurity researchers swiftly pointed the finger at North Korea. The sophisticated nature of the exploit—characterized by deep backend infrastructure compromise and precise transactional spoofing—bears the classic hallmarks of advanced persistent threat (APT) groups hailing from the hermetic nation.

Prominent state-backed cyber-espionage and financial theft units from North Korea, most notably the Lazarus Group and related syndicates, have built a formidable reputation over the past decade for targeting the global cryptocurrency industry. These operations are frequently utilized by the regime to launder money and bypass heavy international economic sanctions, funding state priorities through targeted cyber warfare.

The Bitget incident is merely the latest in a long, troubling lineage of massive cryptocurrency heists linked to Pyongyang. The scale of these operations has expanded dramatically over recent years. For instance, the cybersecurity community is still reeling from the historic Bybit exploit, which saw malicious actors walk away with an unprecedented $1.5 billion from an Ethereum cold wallet—securing its place as the largest crypto theft recorded in history.

Data compiled by blockchain analytics firm Elliptic in February 2025 underscores the staggering scope of these state-sponsored campaigns. According to Elliptic’s estimates, North Korean threat groups have successfully plundered more than $6 billion in cumulative cryptocurrency assets since 2017.

Mitigation, Recovery Efforts, and Bounty Programs

In the wake of the disaster, Bitget has moved aggressively to mitigate customer losses and track down the stolen funds. The exchange has repeatedly reassured its user base that individual account balances are completely safe and insulated from the corporate loss. Management has reiterated that Bitget’s heavily capitalized Protection Fund will absorb the financial impact of the platform-wide breach, preventing any direct socialization of losses onto everyday traders.

To incentivize the crypto community and decentralized finance (DeFi) investigators to aid in the recovery, Bitget launched an official Recovery Bounty Program. Under this initiative, the exchange is offering a generous 5% bounty reward to individuals, security researchers, or white-hat hackers who provide actionable intelligence that leads to the successful freezing or recovery of the stolen capital.

Additionally, Bitget has actively collaborated with centralized exchanges, decentralized finance protocols, and major blockchain analytics firms to blacklist addresses linked to the attackers. By blacklisting these wallets, the exchange aims to make it exceedingly difficult for the hackers to launder or cash out the stolen tokens through legitimate liquidity pools or fiat off-ramps.

Broader Implications for Centralized Crypto Exchanges

The Bitget breach serves as a stark reminder of the persistent and evolving cybersecurity threats facing centralized cryptocurrency exchanges (CEXs) worldwide. Despite substantial investments in multi-signature architecture, hardware security modules, and real-time anomaly detection, exchanges remain prime targets for state-sponsored threat actors wielding nation-state resources.

Industry analysts point out that as perimeter security surrounding cold storage solutions continues to harden, attackers are increasingly shifting their focus toward complex backend infrastructure, third-party vendor integrations, and internal authorization pipelines. By compromising these auxiliary systems, hackers can manipulate transactional validation frameworks from the inside, bypassing standard withdrawal limits and manual review triggers.

The incident is expected to prompt a sweeping audit across the centralized exchange sector. Security posture reviews will likely focus heavily on backend wallet management systems, API keys, administrative access controls, and multi-factor authorization workflows.

Furthermore, regulatory bodies and compliance watchdogs are likely to scrutinize how exchanges handle emergency liquidity crises, reserve proofs, and incident transparency. Bitget’s swift communication, albeit disruptive to users, has been viewed by some market observers as a necessary containment playbook, though the long-term reputational and financial fallout remains to be seen.

As Bitget works through its phased withdrawal schedule over the coming days, the cryptocurrency market will be watching closely to ensure that user funds are successfully returned without further technical hitches. Meanwhile, international law enforcement and blockchain intelligence agencies continue their pursuit of the stolen funds, though recovering assets from sophisticated state-sponsored syndicates remains an exceptionally difficult uphill battle.

September 28, 2026 0 comment
0 FacebookTwitterPinterestEmail
Bitcoin & Altcoins

Ethereum Foundation Announces Annual Protocol AMA Session Scheduled for September 16

by admin September 27, 2026
written by admin

Since January 2019, the Ethereum Foundation has maintained a transparent, open-door policy with the global blockchain community by hosting annual Ask Me Anything (AMA) sessions on the r/ethereum subreddit. These sessions serve as a critical bridge between the researchers, core developers, and the broader ecosystem, fostering a direct line of communication that demystifies complex protocol upgrades and long-term technical roadmaps. On September 16, the Foundation will continue this established tradition, focusing this year’s discussion on the Protocol cluster of researchers and engineers who are responsible for the foundational architecture of the network.

A Tradition of Technical Transparency

The AMA format remains consistent with previous years, designed to facilitate deep-dive technical debates and nuanced explanations of Ethereum’s development lifecycle. By consolidating community queries into a single, high-traffic thread, the Foundation ensures that technical discourse is archived, accessible, and subject to rigorous community peer review. Historically, these sessions have been instrumental in addressing community anxieties during major network shifts, including the transition from Proof-of-Work to Proof-of-Stake and the implementation of various EIPs (Ethereum Improvement Proposals).

This year’s session arrives at a pivotal juncture. With the network’s roadmap evolving toward increased scalability and long-term security, the participants are expected to tackle complex topics ranging from post-quantum cryptography to the integration of ZK-proof technology into the Layer 1 (L1) core.

The Current State of Ethereum Development

The technical landscape for this year’s session is defined by several active development workstreams. The most immediate items on the agenda are the ongoing public testing of the Glamsterdam hard fork and the narrowing scope of the Hegotá upgrade. These upgrades represent the incremental progress required to maintain Ethereum’s competitiveness and security in an increasingly crowded Layer 1 landscape.

  • Glamsterdam: Currently in public testing, this hard fork focuses on refining network efficiency and stability. Developers are currently monitoring client performance across various testnets to ensure that the transition remains seamless for node operators and infrastructure providers.
  • Hegotá: The scope of this upgrade is currently undergoing a process of refinement. The Protocol team is focusing on balancing the desire for feature-rich updates with the necessity of maintaining a stable, conservative core protocol.
  • Post-Upgrade Planning: Beyond these two upgrades, the Ethereum research community is engaged in a wide-ranging debate regarding the long-term shape of the network. This includes discussions on state growth management, the viability of decoupled consensus mechanisms, and the implementation of advanced privacy features at the base layer.

Chronology of Ethereum Governance and Development

The commitment to public discourse has been a hallmark of the Ethereum Foundation since its inception, but the formalization of the annual AMA began in early 2019.

  • 2019-2020: The early AMAs focused heavily on the transition from the Serenity phase to the eventual Beacon Chain launch. These sessions were vital for aligning node operators and staking pools on the technical requirements of the new consensus engine.
  • 2021-2022: The focus shifted toward the Merge, with extensive sessions covering client diversity, the impact of the transition on network security, and the decommissioning of energy-intensive mining hardware.
  • 2023: Discussions centered on the successful implementation of the Shanghai/Capella upgrades, which enabled staked ETH withdrawals, and the beginning of the "Surge" era, focused on rollups and data availability.
  • 2024: The current focus is on the long-term sustainability of the protocol, including L1-zkEVM integration and formal verification methods to ensure the codebase remains bug-free as it grows in complexity.

Technical Scope: What to Expect

The upcoming session is expected to cover a wide spectrum of technical architecture. The Foundation has encouraged the community to prepare questions on several high-priority domains:

  1. Post-Quantum Ethereum: With the maturation of quantum computing, the research team is actively exploring cryptographic primitives that can withstand future quantum attacks, ensuring the long-term safety of user assets.
  2. L1-zkEVM: Integrating zero-knowledge proofs directly into the Layer 1 protocol is one of the most ambitious goals in Ethereum’s history. This would allow the main chain to verify proofs of execution directly, significantly enhancing the security and trustlessness of scaling solutions.
  3. Formal Verification: As the Ethereum codebase becomes more sophisticated, formal verification—the mathematical proof of software correctness—is becoming essential to prevent vulnerabilities.
  4. The Future of State: The network’s state size continues to grow. Discussions will likely cover state expiry and history pruning, which are critical to keeping the network accessible to home stakers.
  5. Decoupled Consensus: Exploring how to separate block production from block validation to prevent centralization at the validator level.
  6. L1 Privacy: Addressing the demand for greater user privacy without sacrificing the transparency required for regulatory compliance and auditability.

Data-Driven Development: The Metrics Behind the Protocol

The efficiency of Ethereum is measured through several key performance indicators (KPIs) that inform the developers’ work. As of the third quarter of 2024, the network maintains a high level of client diversity, with multiple independent implementations (such as Geth, Nethermind, and Besu) operating concurrently. This diversity is a primary defense against systemic failures.

Furthermore, the average block time remains consistently around 12 seconds, despite the increasing complexity of data handled by the network. The success of EIP-4844 (Proto-Danksharding), which significantly reduced fees on Layer 2 rollups, has served as a validation of the current roadmap’s focus on off-chain scaling. The Foundation’s researchers will likely present findings on how these metrics have influenced the scope of the upcoming hard forks.

Official Response and Community Engagement

In anticipation of the September 16 session, the Ethereum Foundation has moved to a proactive engagement model. By gathering questions via a centralized submission form, the team ensures that the most technical and pertinent queries are prioritized, reducing the signal-to-noise ratio often found in live social media threads.

A spokesperson for the Protocol cluster noted that the goal is not merely to provide answers, but to solicit feedback from the developers and users who build on top of the protocol. "We treat the AMA not as a press release, but as a collaborative design session," said an internal source familiar with the planning. "The feedback we receive often influences how we prioritize documentation and, in some cases, the technical specifications for future EIPs."

Broader Implications and Strategic Outlook

The implications of this AMA extend far beyond a single day of discussion. For institutional stakeholders, the session provides a glimpse into the risk mitigation strategies the Foundation is employing. For the developer community, it offers clarity on where the "building blocks" of the network are heading, allowing for better alignment between application-layer projects and core protocol upgrades.

The shift toward L1-zkEVM and quantum resistance indicates that the Ethereum Foundation is planning for a multi-decade horizon. This long-term focus distinguishes Ethereum from many of its contemporaries, which often prioritize short-term performance gains over long-term cryptographic stability.

Conclusion

The September 16 AMA serves as a vital touchpoint for the health of the Ethereum ecosystem. As the network navigates the challenges of scaling, privacy, and long-term security, the willingness of the Foundation to engage in direct, technical, and open dialogue remains one of its most significant assets. Community members interested in participating are encouraged to submit their questions via the official Ethereum pad form, ensuring that their technical inquiries are included in the preparatory documentation for the researchers and engineers. As the industry watches, the outcomes of this session will likely set the tone for the Ethereum development cycle heading into 2025.

September 27, 2026 0 comment
0 FacebookTwitterPinterestEmail
Bitcoin & Altcoins

Bitget Security Breach: Cryptocurrency Exchange Reports $351.6 Million Loss in Sophisticated Wallet Compromise

by admin September 27, 2026
written by admin

The cryptocurrency sector experienced a major shock on September 24, 2026, when prominent exchange Bitget confirmed a significant security incident involving the unauthorized transfer of approximately $351.6 million from its hot and warm wallet infrastructure. The breach, which was detected by the exchange’s internal security monitoring systems at 18:31 UTC, has prompted a swift emergency response, a temporary suspension of withdrawal services, and an extensive forensic investigation involving top-tier third-party security firms. Despite the magnitude of the unauthorized outflows, the exchange has moved quickly to reassure its global user base that the incident was contained within specific layers of its multi-tier wallet architecture, leaving cold storage assets untouched.

A Chronology of the Breach and Initial Detection

The incident unfolded with rapid velocity, beginning with anomalous blockchain activity that caught the attention of on-chain analysts. Early reports, based on real-time monitoring of decentralized ledger activity, initially estimated that between $170 million and $183 million had been siphoned from various Bitget-linked wallets. These initial calculations, however, proved to be conservative as the exchange’s internal audit teams conducted a more granular analysis. By the time the final tally was verified, Bitget confirmed a total loss of $351.6 million across a diverse portfolio of assets, including Ethereum (ETH), Tether (USDT), USD Coin (USDC), Avalanche (AVAX), and BNB.

The sophistication of the attack was highlighted by specific, high-velocity transactions. In one notable sequence, an illicit actor utilized approximately $19.67 million in USDT to acquire 7,111 ETH on the Arbitrum network in a span of just six minutes. This maneuver suggested a coordinated attempt to obfuscate the origin of the stolen funds and move them across cross-chain bridges to complicate recovery efforts.

Upon detecting the breach at 18:31 UTC, Bitget’s security operations center initiated emergency protocols. The exchange’s technical team acted within minutes to isolate the compromised segments of its wallet system, effectively severing the attacker’s access to further funds. While deposits and trading activities remained operational to maintain market liquidity, the exchange implemented a mandatory freeze on all withdrawal requests to prevent the further movement of assets and to facilitate a forensic audit.

Technical Analysis of the Compromised Infrastructure

Bitget employs a robust three-tier wallet architecture designed specifically to mitigate the impact of localized security failures. The system consists of hot wallets for immediate liquidity, warm wallets for secondary operational needs, and air-gapped, offline cold wallets for long-term storage. According to official disclosures, the attacker managed to breach a critical backend system responsible for managing the orchestration of the hot and warm wallet tiers.

Crucially, the exchange clarified that the attacker did not compromise the private keys themselves, which would have signified a catastrophic failure of the core security protocol. Instead, the perpetrator leveraged a vulnerability within the backend management system to falsify transaction data. By injecting fraudulent instructions into the system, the attacker successfully tricked the exchange’s automated authorization mechanism into signing off on unauthorized transfers.

The investigation into how the intruder initially gained access to the backend management system remains ongoing. Bitget has opted for transparency in its communication, stating that it will refrain from speculation regarding the "how" and "why" of the initial entry point until a comprehensive forensic report is completed. To ensure the integrity of this investigation, Bitget has onboarded two industry-leading security firms, Mandiant and SlowMist. These firms are tasked with conducting an exhaustive post-mortem, verifying the patches applied to the backend system, and providing actionable intelligence to law enforcement agencies globally.

Financial Resilience and User Protection

A primary concern for the digital asset industry during such incidents is the impact on retail customer balances. Bitget has maintained a consistent narrative that user accounts remain fully intact. The exchange’s ability to absorb a loss of $351.6 million without impacting user equity is attributed to its "User Protection Fund."

Established in 2022 with an initial capital injection of $300 million, the fund was designed specifically to act as an insurance layer against exchange-level hacks and systemic market failures. By 2023, the fund had expanded to include 5,500 BTC, and at the time of the September 2026 incident, the fund’s valuation was reported to be in excess of $464 million. This capital buffer is sufficient to cover the total identified loss, allowing the exchange to commit to a full restoration of assets without requiring a "haircut" or financial loss for its users.

The exchange has pledged to issue hourly updates throughout the recovery period, with a full, transparent report detailing the technical failure and the remedial steps taken expected within 24 hours of the discovery. This level of communication is intended to maintain market confidence and provide clarity to institutional and retail partners alike.

Industry-Wide Implications and Cooperation

The incident has triggered a broader conversation regarding the security of centralized exchange (CEX) infrastructures. In an era of increasing cross-chain complexity, the risk profile of backend management systems has grown, providing new attack vectors for sophisticated threat actors.

The crypto industry has demonstrated a notable degree of solidarity following the announcement. Bybit, a key industry peer, was among the first to publicly offer assistance. CEO Ben Zhou confirmed that his team is coordinating with Bitget to monitor potential movement of the stolen assets, noting that Bitget had previously provided similar assistance to Bybit during its own historical security challenges. Bybit has also taken the step of updating its LazarusBounty.com platform—an initiative aimed at tracking the proceeds of major crypto hacks—to include the addresses associated with the Bitget incident.

This collaborative approach is indicative of a maturing industry. The involvement of global law enforcement and the active tracking of stolen funds by centralized exchanges and blockchain analytics firms like Chainalysis or Elliptic (often engaged in such scenarios) significantly reduces the probability that the perpetrator will be able to "cash out" through regulated off-ramps.

Broader Market Impact and Future Outlook

While the breach is undoubtedly a negative development, the swift containment and the presence of a well-capitalized User Protection Fund have prevented a systemic market contagion. Unlike previous historical hacks where exchanges lacked the liquidity to cover losses, leading to insolvency, Bitget’s financial positioning suggests a high probability of recovery.

However, the event serves as a stark reminder of the persistent threats facing the centralized finance (CeFi) space. As the incident remains under investigation, the market will be watching closely to see how Bitget restores full functionality. The timeline for reopening withdrawals is currently contingent upon the successful completion of the security audit and the implementation of enhanced backend monitoring.

Furthermore, the breach will likely necessitate a industry-wide review of "three-tier" wallet security models. The ability of an attacker to manipulate backend transaction data suggests that the integration between management software and automated signing services requires more rigorous, perhaps multi-signature, verification processes that cannot be overridden by a single compromised system.

As Bitget continues to work with law enforcement and forensic experts, the priority remains the tracking of stolen funds and the stabilization of their operational environment. For the users, the immediate takeaway is the assurance that their assets are covered by the protection fund, though the incident serves as a salient reminder of the risks inherent in holding assets on centralized platforms. As the investigation progresses, the industry awaits the final forensic report, which will likely serve as a foundational case study in modern crypto-exchange security architecture and crisis management.

September 27, 2026 0 comment
0 FacebookTwitterPinterestEmail
Web3 & DApps

Outlier Ventures and Injective Unveil the Next Wave of Financial Innovation Through the Ecosystem Builder Catalyst Cohort

by admin September 27, 2026
written by admin

The landscape of decentralized finance (DeFi) is undergoing a profound structural evolution, shifting away from basic token exchanges toward high-performance, institutional-grade financial layers. Marking a pivotal step in this transition, Web3 accelerator Outlier Ventures and Layer-1 blockchain Injective have officially announced their latest cohort for the Injective Ecosystem Builder Catalyst. This intensive nine-week virtual accelerator program has been meticulously designed to discover, mentor, and back visionary founders who are constructing high-growth decentralized finance and core infrastructure projects natively within the Injective ecosystem.

As the decentralized economy matures, the convergence of sub-second transaction finality, gasless user experiences, and MultiVM interoperability has established a new standard for application development. The newly selected startups are not merely iterating on existing financial products; they are architecting novel financial primitives—ranging from autonomous agent-driven trading systems to sophisticated on-chain repurchase agreements—that capitalize on Injective’s specialized financial infrastructure and shared liquidity framework.

The Macroeconomic and Technical Backdrop of the Cohort

The launch of this accelerator cohort arrives at a critical juncture for the broader digital asset economy. Decentralized finance Total Value Locked (TVL) has steadily approached the $140 billion threshold, while Real-World Asset (RWA) tokenization has experienced explosive growth, scaling by more than 380% since 2022. This rapid expansion underscores an institutional demand for blockchain rails that can match or exceed the operational efficiency of traditional financial markets.

9 Startups Selected for the Injective Ecosystem Builder Catalyst: Scaling the DeFi-First Future

Injective has systematically positioned itself as a premier destination for developers seeking robust technical performance and deep, unified liquidity. By leveraging native financial modules rather than relying strictly on generic smart contract environments, developers within the ecosystem can achieve unprecedented capital efficiency. The nine-week accelerator curriculum is tailored to address the unique complexities of this environment, providing participating startups with comprehensive mentorship, strategic regulatory and legal guidance, and direct access to ecosystem growth incentives designed to fast-track their go-to-market strategies.

Meet the Startups: A Comprehensive Breakdown of the Cohort

The nine chosen projects represent a diverse cross-section of decentralized finance, institutional tooling, fintech, and artificial intelligence integration. Each team addresses specific friction points in current global financial and digital asset markets.

Institutional Infrastructure and Trading Systems

  • QuantCite: Operating as an institutional-grade Order and Execution Management System (OEMS) alongside a smart-routing platform, QuantCite bridges the gap between centralized exchanges and decentralized liquidity venues. It equips quantitative funds and professional traders with enterprise-grade infrastructure designed for high-frequency execution and deep liquidity access.
  • Choice: Serving as a specialized decentralized exchange and aggregation layer optimized specifically for Injective, Choice employs a proprietary routing algorithm. By tapping into fragmented liquidity across multiple venues simultaneously, the platform guarantees users optimal swap execution while minimizing slippage and maximizing trade efficiency.

Fintech, Consumer Access, and Payments

  • Joinn: Focused on emerging markets, Joinn delivers a fintech application that enables everyday users to protect and grow their capital through stable, yield-generating tokenized assets. Built on secure blockchain infrastructure, the application features gasless and signless transactions operating seamlessly across multiple chains. It integrates round-the-clock access, a physical Visa card experience, and an autonomous AI agent to automate compounding returns, all wrapped in a user experience mirroring traditional Web2 applications.
  • Stabled: Stabled addresses the inefficiencies of international trade by providing a cross-border payments platform built for businesses. The platform facilitates instant, compliant stablecoin transactions that bypass traditional correspondent banking networks, effectively mitigating foreign exchange (FX) losses and eliminating multi-day settlement delays.

Asset Tokenization and Structured Finance

  • Quantum Street: Comprising seasoned capital markets and financial engineering experts, Quantum Street specializes in bridging off-chain cash-flowing assets into the on-chain ecosystem. By structuring compliant transactions for cash-flowing commercial enterprises, the firm introduces genuine fundamental utility to stablecoins while driving meaningful growth in aggregate Total Value Locked.
  • Spout: Spout targets the equities sector by introducing a decentralized platform for borrowing and lending U.S. public equities. Through the tokenization of equities and the implementation of a Collateralized Debt Position (CDP) model, Spout facilitates 0% annual percentage rate (APR) margin loans while simultaneously offering competitive lending yields hovering around 10% APY.
  • Chain Capital: Seeking to overhaul the private debt market, Chain Capital transforms historically illiquid financial instruments into tradable, programmatic securities. By tokenizing invoices and corporate receivables and automating the underlying securitization workflows, the platform claims to reduce middle-office operational costs by up to 75% while granting institutional investors compliant access to high-yield risk profiles.

Web3 Social Media and Artificial Intelligence

  • Dapps.co: Positioned as a Web3-native social network, Dapps.co aims to restore financial and structural agency to digital creators through tokenized communities and embedded on-chain economies. The platform incorporates an advanced AI provenance layer designed to combat low-quality synthetic media while empowering creators to monetize directly via peer-to-peer tipping and paid direct messaging capabilities.
  • HodlHer: HodlHer introduces the world’s first AI-driven Web3 operating system built directly on Injective. Utilizing specialized intelligent personas, the platform assists everyday users, creators, and protocol teams in navigating the complete lifecycle of on-chain engagement—spanning initial market perception and data reasoning to automated transactional execution.

Industry Implications and the Path Forward

The overarching trajectory of decentralized finance indicates that the next wave of adoption will rely heavily on systemic composability and deep functional parity with traditional finance (TradFi). While early DeFi iterations focused primarily on replicating basic spot trading and lending primitives, the projects nurtured within the Injective Ecosystem Builder Catalyst demonstrate a shift toward complex financial engineering—such as automated institutional execution, synthetic equities, and private credit securitization.

Market analysts note that accelerators like the one managed by Outlier Ventures and Injective play a vital catalytic role in maturing the crypto-asset sector. By institutionalizing early-stage development, providing rigorous compliance frameworks, and connecting founders with deep liquidity networks, these initiatives bridge the gap between experimental code and production-ready enterprise applications.

9 Startups Selected for the Injective Ecosystem Builder Catalyst: Scaling the DeFi-First Future

Looking Ahead: Demo Day and Future Growth

As the nine-week intensive accelerator program progresses, the cohort teams are actively refining their products in preparation for their public unveiling. The milestone event for the cohort will take place at the upcoming Injective Ecosystem Builder Catalyst Demo Day, scheduled for February 25, 2026.

The Demo Day will serve as a primary platform for founders to present their finalized products to a global audience of venture capitalists, institutional investors, and ecosystem partners. Industry stakeholders and technology enthusiasts interested in attending the virtual showcase can register for the event via the official Luma platform. As these startups transition from development to active deployment, their infrastructure is expected to play a foundational role in shaping the operational standards of the next generation of global finance.

September 27, 2026 0 comment
0 FacebookTwitterPinterestEmail
Newer Posts
Older Posts

Recent Posts

  • The Evolution of the Web3 Wallet: From Private-Key Vault to the Command Center of the Agentic Web
  • Ethereum Foundation Announces Annual Protocol AMA Session Scheduled for September 16
  • Kraken Expands Its Digital Asset Offerings with the Official Listing of Doppler Finance (Xdp)
  • CSD BR and Ripple Collaborate to Integrate XRP Ledger into Brazilian Financial Market Infrastructure
  • Web3 Venture Funding Surges to Record $22 Billion in Third Quarter 2025 Driven by Institutional Adoption

Recent Comments

No comments to show.
  • Facebook
  • Twitter

@2021 - All Right Reserved. Designed and Developed by PenciDesign


Back To Top
Dr Crypton
  • Home
  • About Us
  • Contact Us
  • Cookies Policy
  • Disclaimer
  • DMCA
  • Privacy Policy
  • Terms and Conditions

We are using cookies to give you the best experience on our website.

You can find out more about which cookies we are using or switch them off in .

Dr Crypton
Powered by  GDPR Cookie Compliance
Privacy Overview

This website uses cookies so that we can provide you with the best user experience possible. Cookie information is stored in your browser and performs functions such as recognising you when you return to our website and helping our team to understand which sections of the website you find most interesting and useful.

Strictly Necessary Cookies

Strictly Necessary Cookie should be enabled at all times so that we can save your preferences for cookie settings.