• Home
  • About Us
  • Contact Us
  • Cookies Policy
  • Disclaimer
  • DMCA
  • Privacy Policy
  • Terms and Conditions
Dr Crypton
Secure Your Future in Crypto
Blockchain Technology

The Escalating Cyber Threat Landscape in the Middle East: A New Era of Digital Insecurity 2025-2026

by admin September 25, 2026
written by admin

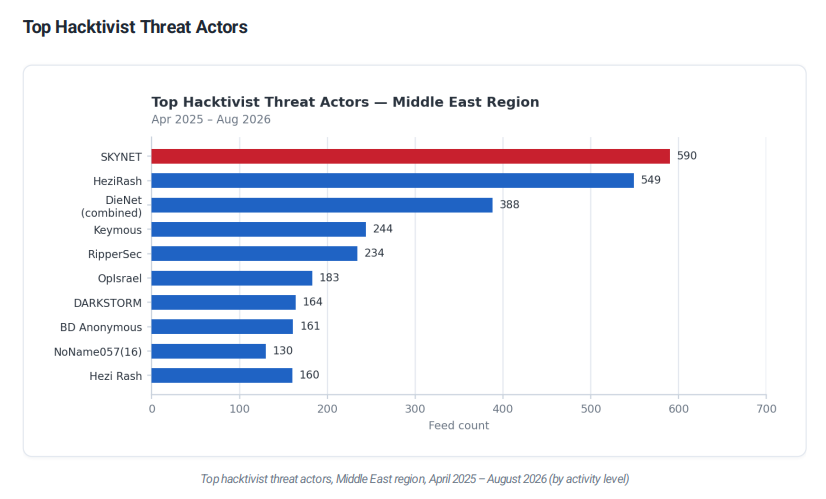
The Middle East is currently navigating an unprecedented transformation in its digital threat environment, as a convergence of geopolitical volatility, rapid digital transformation, and the weaponization of artificial intelligence creates a fertile ground for cyber-adversaries. According to the Middle East Cyber Threat Landscape 2025-2026 analysis published by the AI-powered monitoring firm CloudSEK, the region has transitioned from a landscape dominated by localized hacktivism to one defined by sophisticated, financially motivated ransomware campaigns and state-aligned digital espionage. This shift poses a severe challenge to the region’s critical infrastructure, including its vital oil and gas sectors, maritime chokepoints, and burgeoning digital economies.

The data, spanning from April 2025 to August 2026, illustrates a region under siege. While earlier periods were marked by ideological protest—driven largely by regional military tensions involving Israel, Iran, and the United States—the latter half of the reporting period saw a pivot toward more damaging, profit-driven intrusions. Ransomware, in particular, has emerged as the primary tool of choice for criminal syndicates, with attack frequency increasing by more than twenty-fold within a seventeen-month window.

A Chronology of Escalation: From Hacktivism to Ransomware

The timeline of cyber activity in the Middle East over the past year and a half reflects the broader geopolitical unrest of the period. In mid-2025, as military tensions reached a crescendo, the region saw a massive surge in hacktivist activity. Groups such as SKYNET, HeziRash, and DieNet orchestrated a sustained campaign of distributed denial-of-service (DDoS) attacks, website defacements, and SQL injection maneuvers. Israel bore the brunt of this activity, accounting for approximately 37.8% of all regional hacktivist events.
Latest Blockchain News, BSV Insights, and AI Web3 Trends from CoinGeek

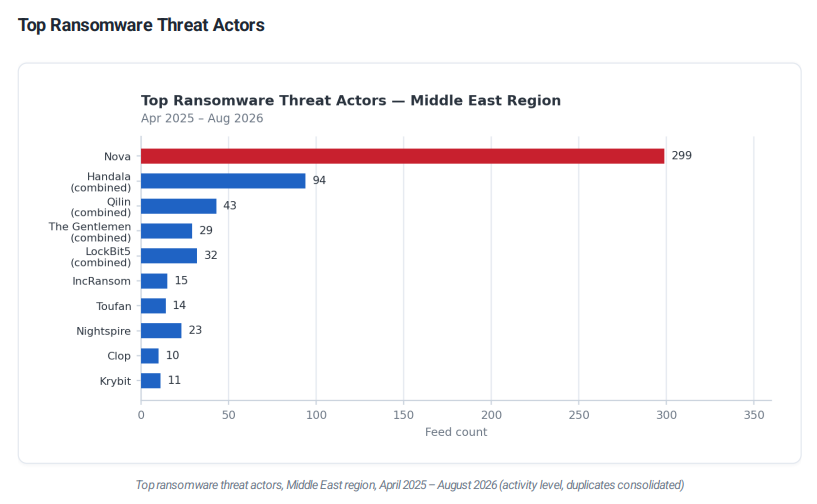
By April 2026, however, the landscape began to shift. While politically motivated disruption did not vanish, it plateaued, ceding the spotlight to professionalized ransomware operations. The most significant spike in ransomware activity occurred in June 2026, when 357 distinct activity signals were recorded—a stark contrast to the 17 signals logged in April 2025. This rapid escalation suggests that threat actors are no longer merely seeking to make a statement; they are seeking to monetize vulnerabilities in sectors that are critical to the region’s stability.

The facility management sector has emerged as the primary victim of these attacks, followed closely by infrastructure, manufacturing, and property management. This prioritization indicates a strategic focus on entities that cannot afford downtime, thereby increasing the leverage held by extortionists.

Geographical Distribution and Threat Sources

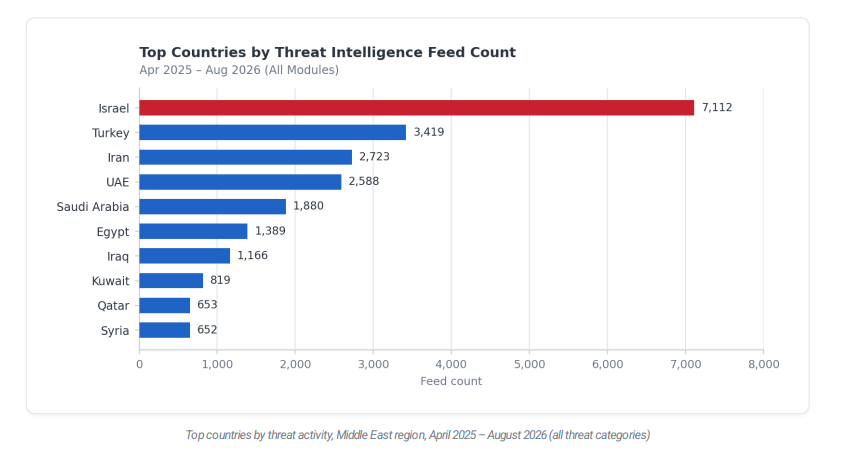
The geography of cyber risk in the Middle East is multifaceted. While Iran is often framed as a focal point of regional conflict, security analysts clarify that it serves primarily as a hub for threat actor development rather than the sole victim. Conversely, Türkiye has been identified as the most targeted nation for ransomware, followed by Israel, the United Arab Emirates, Egypt, and Saudi Arabia.

The dark web has become the backbone of this criminal ecosystem. In this hidden marketplace, stolen government credentials, financial data, and proprietary corporate intelligence are traded at a premium. Türkiye and the UAE exhibit the highest levels of darknet engagement, while Israel leads the region in total threat intelligence feed volume, with over 7,100 specific alerts documented in the study. The prominence of these nations reflects their high levels of digital adoption; as these economies modernize and integrate advanced e-commerce and banking systems, they inadvertently expand their attack surface.
Latest Blockchain News, BSV Insights, and AI Web3 Trends from CoinGeek

The Weaponization of Artificial Intelligence

Perhaps the most alarming development in the 2025-2026 threat landscape is the integration of artificial intelligence into the cybercrime toolkit. AI has significantly lowered the barrier to entry for novice hackers while drastically increasing the efficiency of established criminal groups.

Ram Narayanan, Middle East country manager at Check Point Software Technologies, has noted that AI is now influencing nearly every stage of the cyber-kill chain. The most critical shift is the acceleration of the vulnerability exploitation cycle. Previously, there was a window of several days between the disclosure of a software vulnerability and its active exploitation by bad actors. Today, that window has shrunk to mere hours. AI-driven automation allows attackers to scan networks, identify weaknesses, and deploy payloads at speeds that human-led security teams struggle to match.

The implications of this are profound. As AI tools become cheaper and more accessible, the "cost per attack" continues to plummet, encouraging a surge in smaller, highly targeted campaigns that are difficult to attribute and even harder to mitigate.

Official Responses and Strategic Resilience

In response to these mounting pressures, regional governments are prioritizing "cyber-resilience" over traditional, perimeter-based security models. The United Arab Emirates has led the charge with the introduction of its V7 cybersecurity model, a sophisticated framework designed to automate malware detection and support continuous penetration testing. This initiative is complemented by a national commitment to reskilling the workforce, acknowledging that human error remains the weakest link in any security architecture.
Latest Blockchain News, BSV Insights, and AI Web3 Trends from CoinGeek

However, the consensus among cybersecurity experts is that technological solutions alone are insufficient. The nature of modern threats—characterized by autonomy and rapid evolution—requires a fundamental change in corporate and government culture. Organizations are increasingly advised to adopt a "zero-trust" architecture, enforce rigorous identity and access controls, and maintain immutable, offline backups. The latter is considered essential in the face of ransomware attacks that specifically target cloud-based or networked backups to force a ransom payment.

Broader Economic and Geopolitical Implications

The persistence of cybercrime in the Middle East has tangible economic consequences. When critical infrastructure sectors like energy and manufacturing are targeted, the ripple effects can disrupt global supply chains, particularly given the region’s role as a major maritime corridor through the Straits of Hormuz and Bab el-Mandeb.

Moreover, the convergence of criminal and state-sponsored activity creates a complex attribution problem. When a ransomware group like Nova or Qilin attacks a government agency, it is often unclear whether the motive is purely financial or if the group is being utilized as a proxy for state-level interests. This ambiguity complicates international cooperation and legal response efforts, as traditional diplomatic channels are often ill-equipped to deal with decentralized, non-state actors operating from the dark web.

Looking Toward 2027: A Proactive Defense

As the region moves toward the end of 2026 and into 2027, the emphasis must remain on proactivity. The era of reactive security, where an organization waits for an alert before taking action, has passed. Proactive threat hunting, the use of AI to defend against AI, and the fostering of regional intelligence-sharing partnerships will be the defining factors of success.
Latest Blockchain News, BSV Insights, and AI Web3 Trends from CoinGeek

The message for enterprises and government agencies is clear: the threat environment is not a temporary anomaly, but a permanent feature of the modern digital economy. Organizations that fail to integrate security into their core operations risk not only financial loss but also the erosion of public trust and the compromise of national security. As the Middle East continues to innovate, its ability to secure its digital foundations will ultimately determine its capacity to thrive in a global market that is increasingly defined by the security of information.

Summary of Key Findings

  • Ransomware Surge: The most common form of attack, with a twenty-fold increase in activity signals recorded between early 2025 and mid-2026.
  • Targeted Sectors: Facility management, industrial systems, and infrastructure are the most frequently targeted, signaling a focus on critical, high-impact systems.
  • Leading Actors: Groups such as Nova, Handala, and Qilin continue to dominate the extortion landscape, often utilizing botnets and phishing as primary delivery mechanisms.
  • Technological Shift: The adoption of AI by criminal groups has drastically reduced the time-to-exploit, making rapid, automated defense mechanisms mandatory.
  • Strategic Imperative: Cyber-resilience is now an economic necessity, requiring a shift toward offline backups, constant threat monitoring, and robust identity management.

While the challenges are significant, the region’s commitment to building advanced, AI-driven defense models shows a recognition of the stakes. By fostering a culture of security and investing in both the technology and the talent required to manage it, the Middle East is positioning itself to withstand the next generation of digital conflict. The path forward is not to shun innovation, but to build it upon a foundation of absolute vigilance.
September 25, 2026 0 comment
0 FacebookTwitterPinterestEmail
Blockchain Technology

MoonPay to Acquire North Capital in Major Expansion into Tokenized Securities Infrastructure Valued at Over $60 Million

by admin September 25, 2026
written by admin

Crypto payments and infrastructure giant MoonPay has officially reached an agreement to acquire North Capital, a prominent player in private securities and alternative trading systems, in an all-stock transaction reportedly valued at upwards of $60 million, contingent upon customary regulatory approvals. This strategic acquisition marks a significant milestone for MoonPay as it aggressively broadens its operational scope beyond traditional cryptocurrency transactions and fiat-to-crypto on-ramps, diving deep into the rapidly growing market of tokenized real-world assets (RWAs) and regulated digital securities.

By absorbing North Capital, MoonPay acquires a comprehensive, fully compliant securities infrastructure stack. This integration provides the crypto native firm with critical regulatory licenses and operational frameworks, including broker-dealer capabilities, a registered transfer agent, and investment advisory registrations. These regulatory pillars are essential for navigating the complex legal landscape of digital asset securities in the United States and global jurisdictions. As the boundary lines between traditional finance (TradFi) and decentralized finance (DeFi) continue to blur, this transaction positions MoonPay to bridge the gap by offering institutional-grade compliance alongside its established consumer-facing payment rails.

Understanding the Target: North Capital’s Footprint in Alternative Markets

Founded with a vision to modernize private capital markets, North Capital has built a robust reputation for helping companies raise capital efficiently by leveraging regulatory exemptions. More importantly, the firm operates the Private Placement Exchange Alternative Trading System (PPEX ATS). The PPEX ATS is a powerhouse within the private securities ecosystem, boasting a catalog of more than 1,250 eligible securities and having successfully supported over $8.7 billion in cumulative transaction volume.

The platform provides a compliant venue for the issuance, trading, and settlement of private securities—an asset class historically plagued by illiquidity, manual paperwork, and fragmented market structures. By incorporating North Capital’s broker-dealer and advisory arms directly into its infrastructure platform, MoonPay is no longer merely a conduit for buying and selling cryptocurrencies like Bitcoin and Ethereum. Instead, it is transforming into a full-spectrum financial technology conglomerate capable of handling the entire lifecycle of tokenized equities, debt instruments, and alternative investment funds.

The Nexus of Liquidity: Agora and the tZERO Partnership

MoonPay buys North Capital, including ATS for tokenized securities

One of the most intriguing and complex dimensions of the North Capital acquisition involves its strategic partnerships within the tokenized securities landscape, most notably its collaboration with tZERO. Earlier, North Capital and tZERO joined forces to launch Agora, an innovative inter-market routing network designed specifically to connect alternative trading systems (ATSs).

Historically, tokenized and private securities markets have suffered from severe liquidity fragmentation. Different trading venues operate in isolated silos, meaning that buyers and participants on one platform cannot easily access liquidity or execute orders on another. Agora was built to solve this exact problem by establishing a unified routing network that allows qualified institutional participants to discover and route orders seamlessly across multiple venues.

The initiative achieved a major operational milestone in July when it successfully executed its very first routed order on the live network. However, the integration of North Capital into MoonPay’s corporate umbrella introduces new governance questions for Agora. With one of its two founding ATS platforms now absorbed by a vertically integrated corporate group that simultaneously owns transaction routing technology and consumer payment rails, industry observers are closely watching how Agora will manage neutrality, competitive dynamics, and institutional trust moving forward.

Strategic Implications for the Tokenized Asset Boom

The timing of MoonPay’s acquisition reflects a broader, industry-wide race toward the tokenization of real-world assets. Traditional financial institutions, asset managers, and fintech pioneers are increasingly recognizing that blockchain technology can drastically reduce settlement times, lower administrative overhead, and democratize access to asset classes that were once restricted to ultra-high-net-worth individuals and institutional giants.

Tokenization involves representing ownership of physical or traditional financial assets—such as commercial real estate, corporate bonds, private equity, and commodities—as cryptographic tokens on a distributed ledger. While the technological plumbing for tokenization has existed for years, widespread adoption has been severely bottlenecked by regulatory uncertainty and the lack of compliant, interconnected secondary markets.

By acquiring North Capital, MoonPay bypasses years of regulatory licensing hurdles. Rather than building a broker-dealer and an alternative trading system from scratch and waiting for approvals from regulatory bodies like the Financial Industry Regulatory Authority (FINRA) and the Securities and Exchange Commission (SEC), MoonPay instantly inherits a licensed, battle-tested compliance machine. This move allows the company to offer tokenization as a service to enterprise clients, enabling banks, fintechs, and issuers to tokenize assets and distribute them in full compliance with securities laws.

MoonPay buys North Capital, including ATS for tokenized securities

Navigating Regulatory Scrutiny and Future Outlook

While the all-stock deal valued at over $60 million represents a lucrative exit for North Capital’s stakeholders and a transformative growth catalyst for MoonPay, the transaction remains subject to rigorous regulatory review. Given the current regulatory climate surrounding digital assets and securities in the United States, regulators will likely scrutinize the transfer of broker-dealer registrations and alternative trading system ownership.

The convergence of crypto payment rails with regulated securities infrastructure also places MoonPay under a brighter regulatory spotlight. As the company expands its footprint from retail crypto onboarding into institutional-grade capital markets, compliance, anti-money laundering (AML) protocols, and know-your-customer (KYC) standards will become even more critical to its ongoing operations.

Market analysts view this acquisition as part of a larger consolidation wave within the digital asset sector. As standalone startups find it increasingly difficult to navigate high regulatory compliance costs and fragmented liquidity pools, well-capitalized infrastructure giants like MoonPay are stepping in to acquire regulated entities. This consolidation trend is expected to accelerate, ultimately shaping a more mature, institutionalized digital asset economy where compliance and innovation go hand in hand.

As the deal moves toward final approval, the industry will be monitoring how MoonPay integrates North Capital’s technology stack into its existing ecosystem. The success of this integration will not only determine MoonPay’s trajectory in the multi-trillion-dollar tokenized asset market but may also set a precedent for how crypto-native firms successfully transition into regulated traditional financial infrastructure.

September 25, 2026 0 comment
0 FacebookTwitterPinterestEmail
Blockchain Technology

SAP Is Taming the Wild West of AI Agents With Its New Enterprise Governance Hub

by admin September 25, 2026
written by admin

For the modern Chief Information Officer, the proliferation of autonomous AI agents has created a digital blind spot that threatens to eclipse the security challenges of the early cloud-computing era. While enterprises have spent the last two years rushing to integrate Large Language Models into their workflows, the result has been the emergence of "Shadow AI"—a landscape where thousands of independent agents operate across departments with little to no centralized oversight. SAP is now positioning itself to address this chaotic sprawl, leveraging its massive global footprint to introduce the first ERP-scale solution for agent discovery, inventory, and governance.

The SAP AI Agent Hub, built upon the foundation of SAP LeanIX, represents a significant shift in how organizations manage their technical debt. By providing a vendor-agnostic command center capable of cataloging not only SAP-native agents but also third-party LLMs and Model Context Protocol (MCP) servers, SAP is attempting to act as the primary cartographer for the uncharted territories of enterprise AI.

A Chronology of the Autonomous Enterprise Shift

The road to the AI Agent Hub’s Q3 2026 general availability has been marked by a deliberate, multi-phased rollout. The concept was first introduced to the public during the SAP Sapphire conference in May 2026, where the company outlined its vision for the "Autonomous Enterprise." At that stage, the hub was a conceptual framework designed to help enterprises move beyond experimental pilot programs into sustainable production environments.

Following the initial reveal, the summer of 2026 served as an incubation period for the technology. By September, the narrative shifted from theoretical potential to tangible market penetration. On September 22, 2026, SAP published a comprehensive roadmap detailing the practical integration of the hub into existing IT stacks. This was immediately followed by a series of technical demonstrations at the SAP Transformation Excellence Summit in Atlanta, where industry leaders began to engage with the tool’s capability to trace, monitor, and decommission agents that had drifted from their operational goals.

The Scale of the Shadow AI Problem

The urgency behind SAP’s release is backed by stark industry data regarding the failure rates of autonomous systems. According to research from IDC and Lenovo, a staggering 88% of custom agent builds fail to transition successfully from a controlled pilot environment to a production setting. This "pilot purgatory" often stems from a lack of visibility: if an IT department cannot see what is running, they cannot audit it, secure it, or scale it.

Further compounding the issue is the difficulty of tracking the economic impact of these agents. PYMNTS reported in September 2026 that only 23% of merchants currently possess the capability to accurately track agent-driven transactions. In an era where AI agents are increasingly tasked with executing procurement, supply chain logistics, and customer-facing interactions, this opacity represents a direct financial risk. Without a centralized "agent inventory," organizations are essentially running blind, vulnerable to security leaks, data hallucinations, and unintentional financial exposure.

The Competitive Landscape of Governance

SAP is not operating in a vacuum. The governance of AI agents has become the most contested frontier in enterprise software, with at least five major governance-focused products debuting in the two-week window surrounding the September summit. The market is witnessing a rapid consolidation of the "control layer," as vendors race to provide the guardrails necessary for enterprise adoption.

Dataiku has launched a standalone Agent Management product aimed at cross-platform monitoring, while NiCE’s $955 million acquisition of Cognigy underscores the high value placed on the routing and orchestration layer of AI agents. Meanwhile, Collibra has introduced "Guardian Agents" for runtime governance, and identity giant Okta has begun integrating agent-specific identity verification into its platform.

Despite this flurry of activity, SAP maintains a distinct competitive advantage: the sheer size of its installed base. With roughly 425,000 customers already utilizing its ERP infrastructure, SAP possesses a distribution channel that few, if any, of its competitors can match. While competitors may offer specialized features, SAP’s integration into the core transactional systems of the global economy provides a "home-field advantage" for compliance and governance tasks.

Technical Capabilities and the Promise of Interoperability

The AI Agent Hub is designed as a three-pillar architecture: discovery, observability, and behavior mining. The discovery phase uses the LeanIX backbone to identify agents across an entire IT landscape, regardless of whether they are hosted on AWS, Google Cloud, or Microsoft Azure. Once discovered, the observability component, integrated with SAP Cloud ALM, allows administrators to perform session tracing and monitor goal completion in real-time.

Perhaps most critically, the hub features the AI Agent Excellence framework, powered by SAP Signavio. This tool performs "behavior mining," a process that analyzes agent output against intended workflows to detect drift. If an agent begins to deviate from its operational parameters—potentially engaging in unauthorized tasks or inefficient processes—the hub alerts the administrator.

The platform is also bolstered by SAP Company Memory, a governed knowledge layer currently in beta. This layer is designed to ground agents in the specific, historical context of the enterprise, ensuring that AI responses are not just accurate to the LLM, but accurate to the business’s internal logic and regulations. Furthermore, SAP has solidified partnerships with major players including Microsoft, Google Cloud, AWS, Anthropic, and NVIDIA, ensuring that its Joule assistant can interoperate with external frameworks in a bidirectional manner.

The Reality Check: Heterogeneous Environments

While the preliminary numbers provided by SAP—150 organizations and 180,000 discovered agents—are impressive, industry analysts caution that the true test of the hub lies in its performance in "messy" environments. SAP’s internal metrics remain self-reported and have not been subject to independent audits. More importantly, the hub’s effectiveness in a "clean" SAP-centric environment is markedly different from its performance in a fragmented, multi-cloud architecture.

Most modern enterprises operate in a state of high technical heterogeneity. Different departments often employ different agent frameworks, data silos, and cloud providers, leading to a complex web of dependencies. The true value of the AI Agent Hub will only be realized if it can successfully bridge these divides. If the tool proves to be effective primarily within SAP-heavy environments, its impact will be limited to a portion of the enterprise market. If it truly acts as a universal governance layer, it could set the industry standard for the next decade of autonomous computing.

Implications for the Future of Enterprise AI

The rise of the AI Agent Hub signals that the "Wild West" phase of corporate AI adoption is drawing to a close. Organizations are moving away from a fascination with what agents can do, and toward a rigorous evaluation of how they should operate within the boundaries of enterprise compliance.

For the CIOs and CTOs currently struggling to manage a fleet of autonomous bots, the SAP AI Agent Hub offers a potential solution to a critical problem. However, it is essential to view this not as a plug-and-play panacea, but as a foundational attempt to bring discipline to a nascent field. Visibility is the first step toward governance, but true control will require a shift in organizational culture—one that prioritizes oversight and accountability alongside innovation.

Whether SAP succeeds in dominating this space depends on the transition from marketing rhetoric to widespread, cross-platform adoption. As the company moves past the September 2026 hype cycle and into the reality of long-term product support, the success of the hub will be measured by its ability to secure the diverse, messy, and rapidly evolving architectures that define the modern, autonomous enterprise. For now, the hub stands as a promising, distribution-backed attempt to turn the chaos of AI agent proliferation into a manageable, governed asset.

September 25, 2026 0 comment
0 FacebookTwitterPinterestEmail
Decentralized Finance (DeFi)

Crypto Card Volume in 2026: $1.1 Billion a Month, and What Is Inside It

by admin September 25, 2026
written by admin

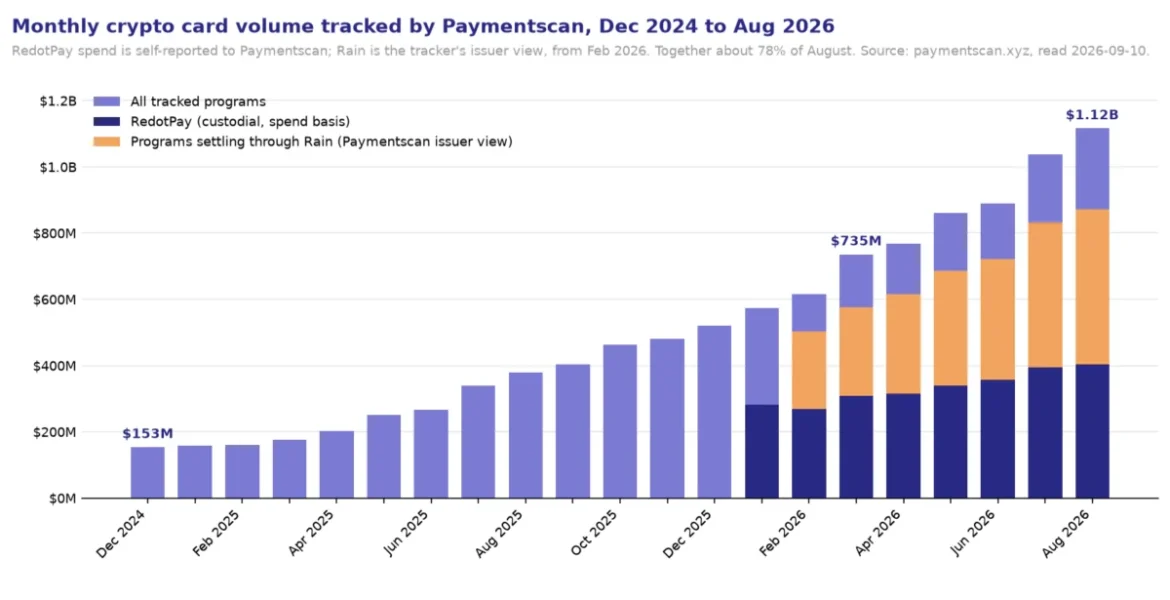
At 16:49:48 UTC on Friday, August 28, 2026, a Solana wallet—funded just three hours prior with 1.79 SOL derived from $190 in USDC bridged from Ethereum—initiated a series of commands that began systematically draining card-balance accounts held by users of Avici, a prominent Solana-based neobank. By the time the exploit was neutralized, 1,685 users had seen their balances liquidated, totaling a loss of $500,859.22. This incident, while rapidly contained, has cast a harsh spotlight on the "non-custodial" crypto card market, a sector that has seen its monthly transaction volume explode to over $1.1 billion as of August 2026.

The vulnerability did not stem from stolen private keys or compromised user devices. Instead, it lay within a specific Solana card contract shared by Avici and several other programs. The underlying infrastructure belongs to Rain, a card-issuing company that has become the backbone of much of the self-custodial card market. While Avici’s terms of service, last updated in June 2025, assured users that neither the company nor the issuer held custody of their collateral, the technical reality of the smart contract architecture allowed for a systemic failure. The incident serves as a stark reminder that in the world of crypto-native finance, the definition of "non-custodial" is often dictated by the nuance of smart contract permissions rather than the absolute security of user assets.

A Chronology of the August Drain

The exploit was surgical and efficient. The attacker’s wallet, identified on-chain as 0xFVNFzqAny8spWdPmYw6RQ9TkYa29ueFFiqCFD1gQnCEj, remained dormant for 189 minutes after its initial funding before launching its first attack at 16:49:48 UTC. Over the next two and a half hours, the wallet executed approximately 21,405 transactions, with roughly 17,500 successfully interacting with the Rain-controlled Solana program.

The mechanics of the exploit relied on an authorization bug within the SubmitSignatures call. By manipulating the signature-verification instruction—pointing the signature, key, and message offsets back at one another—the attacker managed to satisfy a two-signature check with only a single signature. This granted the attacker administrative status over individual user collateral accounts, allowing for the immediate withdrawal of funds.

The fallout was swift. Between 19:03 and 19:49 UTC, as the drain was concluding, the stolen funds were bridged from Solana to Ethereum and moved through Tornado Cash. By 19:18 UTC, Rain had begun patching the affected programs. By September 5, all upgrade authorities for the involved contracts were successfully migrated to a Squads multisig vault, providing a long-term fix to the security architecture.

Market Growth and Concentration Risks

According to data from Paymentscan, the crypto card market has witnessed extraordinary growth, rising from $153 million in monthly volume in December 2024 to $1.116 billion by August 2026. This trajectory highlights a significant shift in consumer behavior, as users increasingly seek to bridge the gap between volatile digital assets and daily retail spending.

However, this growth is heavily concentrated. Paymentscan’s issuer mapping attributes approximately 42% of August’s total volume—$468 million—to programs settling through Rain. When combined with the self-reported figures from RedotPay, these two entities facilitate roughly 78% of the entire tracked crypto card market. This concentration presents a systemic risk: while the August exploit was limited to specific Solana contracts, the reliance on a narrow set of infrastructure providers means that a single architectural flaw can ripple across multiple independent brands simultaneously.

Crypto Cards 2026: Who Holds the Money Before the Swipe

Decoding Custody Models

The industry’s terminology often obscures the legal reality of where money resides. An analysis of 18 major crypto card programs reveals five distinct custody models, ranging from direct debt claims to fully on-chain vaults:

  1. Sale-to-Operator: Programs like KAST have adopted language that characterizes user deposits as a "sale" of assets to the company. In this model, the user holds a USD-denominated debt claim against the operator, often with limited liability protections and no guarantee of asset segregation in the event of bankruptcy.
  2. Nominee Custody: Platforms like Revolut act as a "nominee" for the user. While the platform holds legal title, the user is defined as the beneficial owner. This model relies on the robustness of the platform’s balance sheet and the clarity of its insolvency procedures.
  3. Fiat-Only Issuers: Many exchange-based cards, such as those from Crypto.com or Kraken, do not hold crypto assets on the card account at all. Crypto is held in exchange custody and converted to fiat only at the moment of a transaction. In the EU, this is governed by strict e-money safeguarding regulations.
  4. Shared Program Pools: This is the category that suffered the August exploit. In this model, user collateral is held in a smart contract. While the user technically owns the collateral, the contract is managed by an operator with administrative upgrade keys. If the authorization logic is flawed, the "non-custodial" nature of the account provides no protection.
  5. Self-Custodial Vaults: Programs like Gnosis Pay and Ether.fi Cash utilize sophisticated smart account architectures (such as Safe) where the user maintains control over their assets, often utilizing modules for spend permissions or time-delayed transactions. These are currently the most robust designs, though they are not immune to logic errors.

The Issuer Landscape: Beyond Traditional Banking

A significant finding in the current market structure is the role of "Third National." Seven of the programs analyzed—including Avici, KAST, and Ether.fi Cash—list Third National as their card issuer. Investigations reveal that Third National is not a chartered bank, but rather a Puerto Rico-based money transmitter operating under the corporate umbrella of Signify Holdings, Inc. (Rain).

This underscores a broader trend: many crypto-native card programs are built on non-bank infrastructure, utilizing stablecoin lending networks to facilitate settlement. When a user taps their card, Rain settles with the merchant via Visa and is subsequently repaid from the user’s collateral contract. This "charge card" model, financed by institutional stablecoin liquidity, is highly scalable but introduces dependencies on the creditworthiness and operational security of the underlying infrastructure provider.

The Regulatory Horizon and Future Outlook

The regulatory landscape is poised to change dramatically with the implementation of the EU’s Anti-Money Laundering Regulation (Regulation (EU) 2024/1624), effective July 2027. This framework will effectively prohibit anonymous crypto-asset accounts and limit the usage of anonymous prepaid cards. These impending rules are expected to force a consolidation in the market, favoring programs that maintain transparent KYC (Know Your Customer) and KYB (Know Your Business) compliance.

The recent failures of programs like Kulipa and the closure of Bit.Store following the revocation of its issuer’s license serve as reminders that card programs are fragile. Often, the decision to terminate a service is made by a sponsor bank or a network, leaving the consumer brand with little recourse.

Lessons from the August Incident

Despite the loss of $500,000, the August 28 incident had a relatively positive outcome for users. Rain and the affected programs, such as Avici and Tria, stepped in to refund all impacted users within 24 hours. This response highlights that, for now, the industry is operating on a model of "socialized risk," where venture-backed entities prioritize reputation and customer retention by covering losses out of their own balance sheets.

However, the event serves as a warning for the next phase of market development. As transaction volumes continue to grow, the industry can no longer rely on the promise of venture-backed refunds to mitigate smart contract risks. The path forward requires a transition toward more transparent, immutable, and fully audited on-chain vault architectures. For the end user, the lesson is clear: "non-custodial" is not a synonym for "invulnerable." Before topping up a card, users should look past the marketing, verify the issuer’s regulatory standing, and understand whether the smart contract holding their collateral is truly isolated or subject to the administrative whims of a single, centralized key.

As of September 2026, the sector stands at a crossroads. The integration of stablecoin-powered payments into the Visa network is a major technological milestone, but the infrastructure supporting this growth remains a work in progress. For the millions of users participating in this ecosystem, the security of their assets depends as much on the quality of the legal documentation and the strength of the multisig upgrade keys as it does on the underlying blockchain technology.

September 25, 2026 0 comment
0 FacebookTwitterPinterestEmail
Cybersecurity & Hacking

Court-Ordered Seizure of Radaris.com Domain Marks a Watershed Moment in the Enforcement of Daniel’s Law and the War on Data Brokers

by admin September 25, 2026
written by admin

The landscape of online consumer privacy and the murky world of commercial data brokers underwent a dramatic shift when a New Jersey court ordered the seizure and transfer of the high-traffic people-search domain, Radaris.com. For over a decade, Radaris operated as a pervasive fixture in the digital ecosystem, systematically scraping, compiling, and monetizing the personal dossiers of millions of Americans while routinely ignoring deletion requests and consumer complaints. That era of impunity slammed into a judicial roadblock following a relentless legal campaign spearheaded by Atlas Data Privacy Corp under New Jersey’s stringent Daniel’s Law.

The punitive domain transfer—which swept up Radaris.com alongside more than a dozen sister domains—was not merely a routine civil penalty. It represented the culmination of years of calculated obfuscation, international shell games, and aggressive legal posturing by the platform’s operators. As privacy advocates hail the ruling as a monumental victory for public safety officials, legal experts warn that the battle over commercial data harvesting is rapidly escalating into a constitutional showdown with far-reaching implications for the entire information broker industry.

Anatomy of a Lawsuit: The Battle Over Daniel’s Law

Passed in response to a horrific tragedy involving the family of a federal judge, New Jersey’s Daniel’s Law is designed to shield law enforcement personnel, judicial officers, prosecutors, and their immediate family members from targeted harassment and violence. The statute grants these public servants the absolute right to have their personal information completely expunged from commercial people-search engines and data broker databases. Crucially, the law carries teeth, imposing statutory fines of $1,000 per violation against companies that willfully ignore valid removal requests.

In February 2024, Atlas Data Privacy Corp—a private entity dedicated to enforcing privacy mandates—initiated legal action against Radaris, alleging systematic and flagrant violations of Daniel’s Law. Rather than engaging constructively with the judicial process, Radaris and its legal representation allegedly engaged in a familiar pattern of delay, stonewalling, and jurisdictional maneuvering.

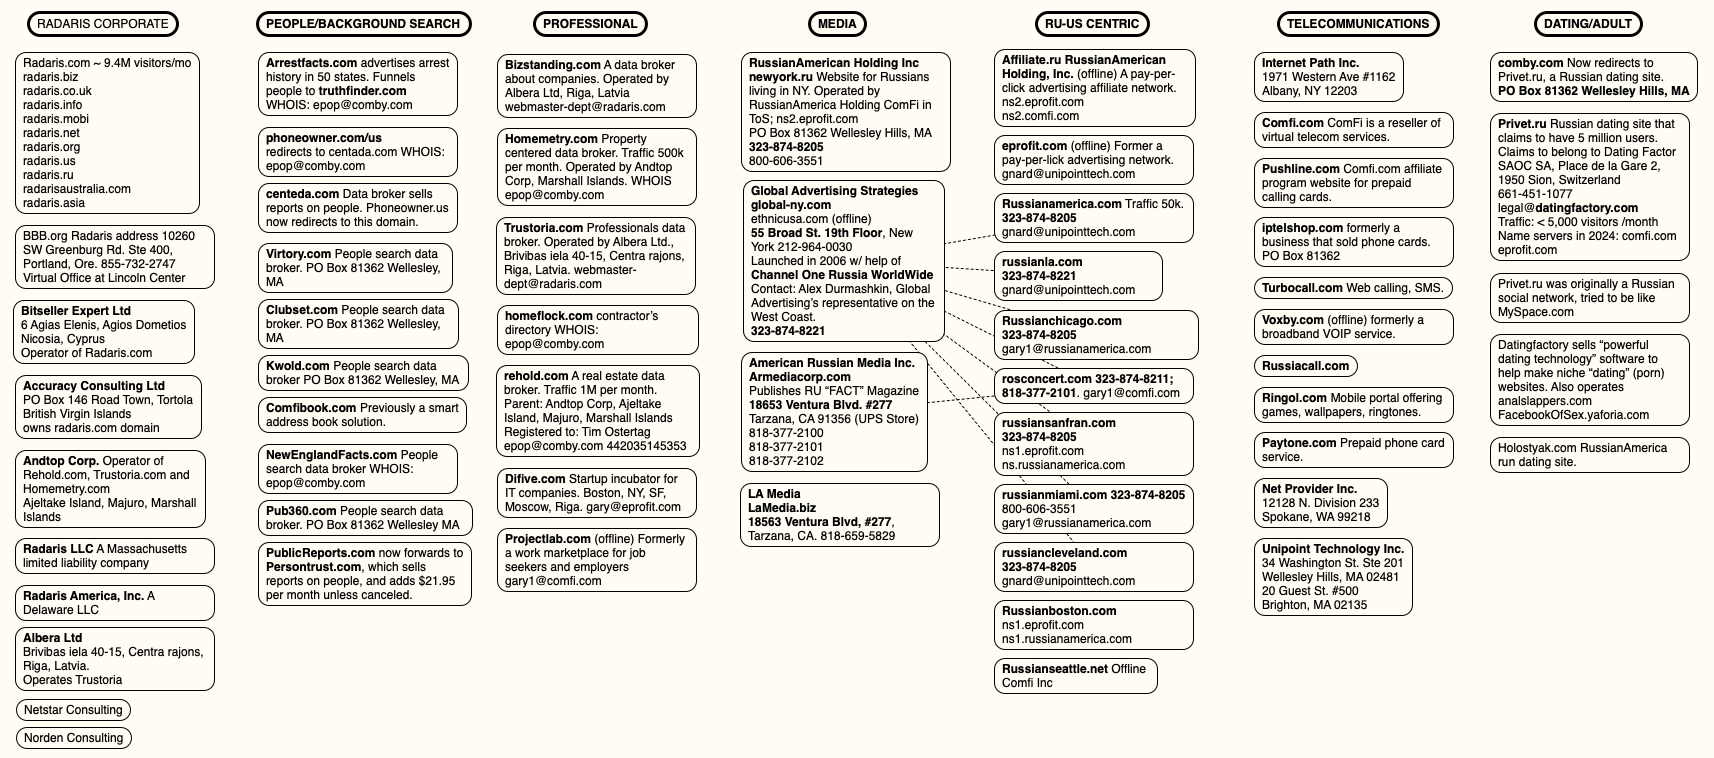
As the litigation progressed, investigative reporting by cybersecurity journalist Brian Krebs unmasked the true masterminds behind the sprawling enterprise: Igor and Dmitry (also known as Dan) Lubarsky, Russian-born brothers residing in Massachusetts. The investigation revealed that the brothers operated an intricate web of dozens of people-search subsidiaries, Russian-language dating portals, and affiliate marketing networks. Furthermore, court filings and investigative disclosures exposed that Radaris had historically utilized a fictitious chief executive officer named "Gary Norden" to front operations and court investors, an admission later confirmed by Boston-based attorney Val Gurvits during legal proceedings.

Data Broker Radaris Loses Domains in Privacy Fight – Krebs on Security

The Corporate Shell Game and International Evasion

The legal confrontation with Radaris exposed the sophisticated mechanics employed by modern data brokers to evade accountability. According to Matt Adkisson, president and CEO of Atlas, the defendants frequently engaged in what he characterized as an "island-hopping phase" designed to frustrate plaintiffs and exhaust judicial resources.

As legal pressure mounted across various jurisdictions, the corporate entities ostensibly owning and managing Radaris shifted continuously across offshore tax havens, including the Marshall Islands, the British Virgin Islands, Cyprus, and the Seychelles. Terms of service agreements were allegedly altered on the fly to reflect newly minted shell companies. In one notable instance, when Radaris updated its corporate documentation to claim management by a newly incorporated Marshall Islands entity, an Atlas-commissioned local investigator discovered that the alleged management firm did not even physically exist at the time of the claim.

This strategy of tactical attrition had served Radaris well for nearly ten years. Plaintiffs’ attorneys, worn down by complex jurisdictional challenges, opaque corporate structures, and the immense cost of pursuing foreign-shielded operators, typically abandoned their suits. However, recognizing the acute physical threat that exposed home addresses and personal records posed to New Jersey law enforcement officers, Atlas committed the requisite financial resources and investigative stamina to pierce the corporate veil.

Financial Interconnections and Industry Partnerships

Discovery materials obtained through the litigation—encompassing upwards of 10,000 internal emails, financial documents, and operational records—provided empirical proof of how the Radaris ecosystem functioned behind closed doors. The records reportedly validated that nominal legal entities such as Radaris America Inc., Bitseller Expert Limited, Digital Orbit Corp, Core Solutions Group, Lucky Solutions, and Veripages were centrally administered by a tight-knit cluster of individuals operating out of the Boston area.

These diverse corporate storefronts shared centralized banking channels, payment card processors, virtual office addresses, and core technical infrastructure routed through shared mail domains. The documentary evidence demonstrated that individual nodes within the network, such as Radaris.com and Veripages.com, generated substantial monthly revenues ranging between $42,000 and $45,000.

Data Broker Radaris Loses Domains in Privacy Fight – Krebs on Security

Moreover, the financial disclosures highlighted lucrative partnerships between the Radaris network and mainstream marketing conglomerates. Revenue streams were significantly augmented through data-sharing and affiliate arrangements with entities like the Lifetime Value Company—operator of consumer search brands such as PeopleLooker, PeopleSmart, and Bumper—as well as Onerep, a prominent privacy-management firm whose founder had similarly launched multiple people-search properties. The convergence of companies claiming to clean up personal data while simultaneously feeding the commercial data broker machine underscored the incestuous and contradictory nature of the modern surveillance economy.

Constitutional Challenges and the National Landscape

While the immediate fallout of the New Jersey court’s decision has crippled Radaris’s primary domain—which now redirects visitors to an informational notice managed by Atlas—the broader legal war is far from over. Victor Worms, legal counsel representing the defendants, moved to vacate the default judgment, arguing that Radaris.com is a non-entity lacking legal capacity to be sued, and asserting that the domain seizure constitutes an unconstitutional forfeiture.

Compounding the legal complexity, the broader data broker industry has launched a coordinated counter-offensive against Daniel’s Law. More than 70 parallel lawsuits initiated by Atlas have been removed to federal court by data broker defendants challenging the constitutionality of the New Jersey statute. Industry advocates argue that sweeping restrictions on publishing legally acquired public records infringe upon commercial free speech protections under the First Amendment of the U.S. Constitution.

The outcome of these challenges—which are widely anticipated to climb the judicial ladder to the Supreme Court of the United States—carries profound implications. While at least 14 other U.S. states have enacted legislation modeled after Daniel’s Law, parallel statutes face severe judicial scrutiny. Notably, a federal district court ruled West Virginia’s version of Daniel’s Law facially unconstitutional under the First Amendment, illustrating the friction between state-level privacy mandates and constitutional jurisprudence.

The Structural Deficit in American Data Privacy

Privacy experts point out that the protracted legal battles over Daniel’s Law highlight a glaring structural deficit in American governance: the enduring absence of a comprehensive federal consumer privacy framework.

Data Broker Radaris Loses Domains in Privacy Fight – Krebs on Security

According to privacy researcher and author Justin Sherman, state-level statutes—while well-intentioned—offer fragmented and incomplete protection because they almost universally exempt records categorized as "public" or "government" documents. Vital information including voting registries, property deeds, marriage licenses, motor vehicle registrations, criminal histories, and court documents remain legally accessible for commercial exploitation. Consequently, unless federal lawmakers enact robust baseline regulations governing data scraping and commercial surveillance, people-search enterprises will simply adapt their business models to harvest and repackage legally accessible public registries.

The systemic risks associated with unchecked data collection extend far beyond people-search directories. The ease with which sensitive personal information can be aggregated, monetized, and exposed was starkly demonstrated by high-profile breaches, such as the security failure at IDScan.net, which briefly exposed the driver’s license data of over 153 million Americans on the dark web. Despite repeated legislative wake-up calls and catastrophic corporate data leaks, comprehensive federal oversight remains paralyzed by intensive lobbying from big tech, social media platforms, cryptocurrency advocates, and artificial intelligence developers.

Conclusion: A Precedent With Limitations

The forced transfer of Radaris.com and its sister properties stands as a landmark tactical victory for privacy enforcement agencies and public safety officials. By systematically dismantling the corporate infrastructure of a notorious data broker through relentless litigation and exhaustive forensic accounting, Atlas Data Privacy Corp has demonstrated that even the most deeply entrenched commercial surveillance operations can be held accountable.

Yet, as the legal battleground shifts to federal appellate courts and the constitutional merits of Daniel’s Law are weighed, the case serves as a stark reminder of the limitations of piecemeal state regulation. Until the United States enacts comprehensive, 21st-century federal privacy legislation that restricts the commercial aggregation of public records, the multi-billion-dollar data broker industry will likely continue its high-stakes game of regulatory evasion.

September 25, 2026 0 comment
0 FacebookTwitterPinterestEmail
Cybersecurity & Hacking

Cloudflare Containers vulnerability exposed sensitive customer data due to thin provisioning flaw

by admin September 25, 2026
written by admin

A significant security vulnerability within Cloudflare’s containerization infrastructure has been identified, allowing a paying customer to inadvertently access residual data left behind by other tenants on shared servers. The flaw, which originated from the way Cloudflare managed disk space allocation, affected the company’s "Containers" and "Sandboxes" services, potentially exposing sensitive information ranging from database structures to environment variables and user credentials. While the vulnerability has since been fully mitigated, the incident highlights the complex security challenges inherent in multi-tenant cloud environments where resource isolation is paramount.

The Mechanism of the Flaw

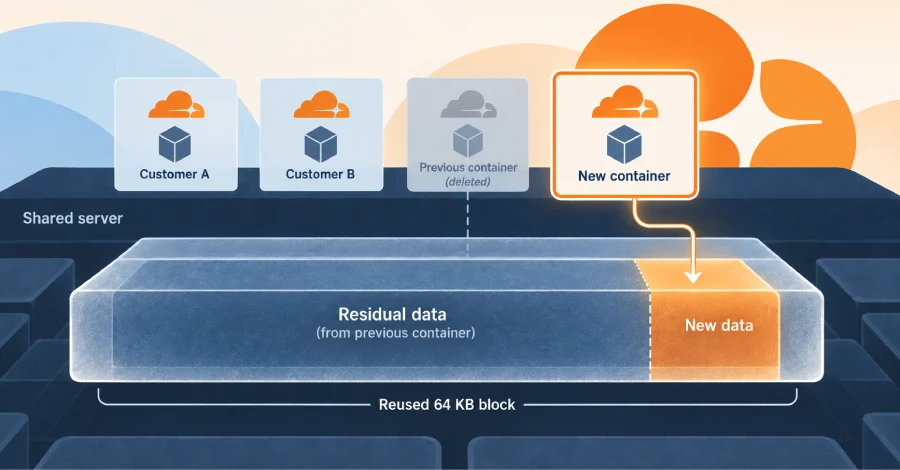
The vulnerability centered on the implementation of "thin provisioning," a storage optimization technique used by Cloudflare to manage disk space across its global fleet of servers. In this architecture, storage is allocated to containers in discrete, 64-kilobyte blocks. When a customer’s container is terminated, these blocks are returned to a global pool, theoretically to be reallocated to future workloads.

Under normal circumstances, the Linux kernel’s device-mapper thin provisioning module is configured to "zero out" or wipe these blocks before they are assigned to a new user. However, a misconfiguration in Cloudflare’s infrastructure caused the system to skip this critical security step. Consequently, when a new container was provisioned, it would occasionally inherit a block that still contained data fragments from a previous tenant.

Because the system did not perform a secure wipe, an attacker could write a small amount of data to a block and then read the remainder of that block at a raw disk level. By doing so, they could recover up to 60 kilobytes of residual information from the preceding user. This data included sensitive directory structures, SQLite database pages, and configuration files, such as .env files and browser profiles, which often house highly sensitive credentials.

Timeline of Discovery and Remediation

The flaw was discovered by Oren Yomtov of the cybersecurity firm Accomplish. On September 4, 2024, the researchers utilized Cloudflare’s bug bounty program to formally report the vulnerability. The discovery process involved systematic testing across various servers, revealing that the issue was not isolated to a single machine but was systemic across Cloudflare’s global infrastructure.

The chronology of the incident and the subsequent cleanup are as follows:

Cloudflare Fixes Flaw That Let One Container Read Another Customer's Leftover Disk Data
  • September 4, 2024: Accomplish researchers report the vulnerability through the official bug bounty channel, providing a proof-of-concept that demonstrated the ability to read residual data.
  • September 14, 2024: Cloudflare implements a fix by re-enabling the block-wiping mechanism. The researchers verify that their proof-of-concept is no longer functional.
  • September 19, 2024: Recognizing that the initial fix did not address data already cached in active memory or existing image layers, Cloudflare completes a comprehensive, multi-day purge of all running container disks and clears associated caches. This process required draining and restarting servers during low-traffic periods to ensure zero downtime for clients.
  • September 24, 2024: Cloudflare officially discloses the vulnerability, detailing the scope and the steps taken to resolve it.

Empirical Scope and Data Analysis

The researchers conducted extensive testing to determine the prevalence of the issue. Across 24 production-level tests on servers selected by Cloudflare, they successfully recovered data on 18 occasions. Furthermore, the issue was validated across 22 underlying machines spanning four continents, suggesting that the misconfiguration was deeply embedded in the company’s global server provisioning scripts.

The recovered data was not merely fragmented noise; the researchers reported successfully capturing structurally complete SQLite databases and directory listings. Despite the sensitivity of the information, the researchers emphasized that their analysis scripts were strictly designed to perform format checks and count data snippets. They explicitly confirmed that no third-party names, credentials, or proprietary content were stored or transmitted beyond the verification required by Cloudflare’s security team.

In its official response, Cloudflare confirmed that the researchers handled the findings with high ethical standards. The company stated that the recovered data was kept private during the testing phase and subsequently destroyed in a secure manner.

Cloudflare’s Investigation and Forensic Audit

Following the report, Cloudflare initiated an internal forensic audit to determine whether the vulnerability had been exploited by malicious actors prior to the report. The company leveraged the researchers’ proof-of-concept to develop detection signatures, which were then applied to historical disk-activity logs.

According to Cloudflare, the audit uncovered no evidence of unauthorized access. The only recorded instances of the exploit were those generated by the Accomplish research team and Cloudflare’s own engineers during the verification phase. However, the company has not provided a definitive window for how long the unsafe "skip-wipe" configuration was in place, making it impossible to fully quantify the duration of the potential exposure.

Broader Implications for Cloud Security

This incident serves as a stark reminder of the "noisy neighbor" and data leakage risks inherent in shared infrastructure. As cloud providers move toward increasingly granular isolation—such as sandboxes designed specifically for AI agents and untrusted code—the complexity of managing storage and memory at the kernel level grows exponentially.

For enterprises relying on containerized environments, the reliance on the cloud provider’s "thin provisioning" security measures is a critical point of trust. The fact that a single flag in a configuration file could compromise the confidentiality of thousands of customers underscores the necessity for robust defense-in-depth strategies.

Cloudflare Fixes Flaw That Let One Container Read Another Customer's Leftover Disk Data

Furthermore, the Accomplish team noted that this was their sixth successful "sandbox escape" since July 2024. Their track record includes similar findings in platforms such as Anthropic’s Claude, Cursor, Docker, and OpenAI’s Codex. This trend indicates that as AI-integrated development environments become more prevalent, the sandboxes protecting these environments are becoming prime targets for security researchers and potential attackers alike.

The Role of Bug Bounty Programs

The successful resolution of this issue highlights the efficacy of bug bounty programs in modern cybersecurity. By incentivizing independent researchers to report vulnerabilities, companies can identify systemic flaws before they are weaponized by threat actors. Cloudflare’s decision to quickly validate the report, implement a global fix, and perform an extensive audit of their infrastructure demonstrates the standard operating procedure for major cloud service providers when dealing with high-severity disclosures.

However, the incident also raises questions about internal auditing processes. While the bug bounty program caught the issue, the fact that the vulnerability existed in a production environment suggests a gap in automated security regression testing. As providers scale their services globally, ensuring that infrastructure-as-code deployments strictly adhere to security defaults remains a significant operational challenge.

Moving Forward

For Cloudflare customers, no action was required, as the company performed the necessary remediation on the backend. Nevertheless, the incident serves as a catalyst for organizations to review their data handling practices in the cloud. Experts suggest that for highly sensitive data, customers should continue to rely on encryption-at-rest and strict access controls, as these measures provide a second layer of defense even if the underlying container infrastructure is compromised.

As for the industry at large, this case will likely prompt a re-evaluation of disk-provisioning standards. The trade-off between the performance gains of thin provisioning and the security requirements of multi-tenancy is now at the forefront of cloud engineering discussions. Cloudflare’s transparency in disclosing the nature of the "skip-wipe" configuration provides a valuable case study for other providers to audit their own storage allocation mechanisms.

The incident is now officially closed, with Cloudflare maintaining that no customer data was compromised beyond the controlled tests performed by the researchers. The company has moved to strengthen its monitoring tools, ensuring that any future deviation from standard security configurations is identified and mitigated in real-time.

September 25, 2026 0 comment
0 FacebookTwitterPinterestEmail
Cybersecurity & Hacking

Cryptocurrency Exchange Bitget Suffers $351.6 Million Breach Linked to Suspected North Korean State-Sponsored Hackers

by admin September 25, 2026
written by admin

Major cryptocurrency exchange Bitget has confirmed a devastating security breach resulting in the theft of approximately $351.6 million from its hot and warm wallets. The incident, which unfolded on Thursday evening, has sent shockwaves through the digital asset ecosystem, once again casting a harsh spotlight on the vulnerabilities plaguing centralized crypto platforms and the persistent threat posed by state-sponsored cybercriminal syndicates.

According to official disclosures from the exchange and statements provided by Bitget CEO Gracy Chen, preliminary forensic assessments strongly link the sophisticated intrusion to North Korean advanced persistent threat (APT) groups. The attackers successfully compromised a critical backend wallet-service system, allowing them to manipulate transaction metadata and trigger unauthorized authorization-signing processes across multiple blockchain networks.

Despite the staggering financial loss, Bitget leadership has emphasized that the platform’s cold storage infrastructure—which houses the overwhelming majority of user assets—remains entirely secure and untouched. Furthermore, the exchange’s independent self-custodial product, the Bitget Wallet, was isolated from the attack vector and experienced zero disruption. To mitigate panic and reassure the user base, executives confirmed that the company’s robust User Protection Fund, which currently boasts a reserve of over $464 million in Bitcoin, will fully cover all stolen funds. Customer account balances remain accurate, and while withdrawals were temporarily halted as a precautionary containment measure, trading and deposits have continued to operate normally.

Chronology of the Breach and Immediate Response

The timeline of the incident highlights a rapid detection by automated security monitoring mechanisms, followed by an aggressive, multi-layered containment strategy executed in collaboration with global cybersecurity heavyweights.

Thursday evening marked the critical turning point when Bitget’s internal security operations center flagged anomalous outbound transactions originating from a restricted cohort of hot and warm wallets. Realizing that unauthorized transfers were actively draining funds, exchange engineers initiated emergency protocols.

By Friday morning, Bitget had temporarily suspended all platform withdrawals to halt the bleeding and prevent further asset exfiltration. Simultaneously, the exchange mobilized an elite incident response coalition, partnering with prominent on-chain security institutions, law enforcement agencies, and premier cybersecurity firms Mandiant and SlowMist.

By analyzing IP behavior patterns, transaction signatures, and routing methodologies, investigators quickly drew parallels to the tactics, techniques, and procedures (TTPs) historically employed by North Korean hacking organizations. Swift coordination with blockchain protocols and validator nodes across the affected networks resulted in the immediate freezing of several hacker-controlled wallet addresses, effectively locking a portion of the stolen capital before it could be laundered through privacy mixers or decentralized finance (DeFi) protocols.

Scope of the Attack and Affected Assets

The breach was not limited to a single blockchain ecosystem, highlighting the operational complexity and multi-chain capabilities of the threat actors. According to details shared by CEO Gracy Chen, the exploit spanned at least seven distinct major blockchain networks.

The targeted chains included:

  • Ethereum (ETH)
  • XRP Ledger (XRP)
  • Arbitrum
  • Avalanche (AVAX)
  • Optimism
  • Binance Smart Chain (BSC)
  • Base

A diverse basket of digital assets was compromised during the assault. While single-chain losses were most heavily concentrated in XRP on the XRP Ledger, the attackers also siphoned substantial quantities of Ether (ETH), Binance Coin (BNB), Avalanche (AVAX), Tether (USDT), USD Coin (USDC), and various other altcoin tokens.

In her public statements, CEO Gracy Chen elaborated on the mechanics of the intrusion. "The attacker compromised a critical backend system within our wallet infrastructure, used it to spoof transaction data, and triggered our authorization process to move funds out," Chen explained. "No further unauthorized transfers are possible. The specific method of system intrusion remains under active investigation."

Hackers steal $351.6 million in Bitget crypto exchange hack

Bitget has committed to maintaining transparent communication with its global user base. Executives have reiterated that normal operations—including the resumption of withdrawals—will be systematically restored as soon as external forensic investigators and internal security teams officially confirm that the environment is thoroughly sanitized and safe.

The Financial Safety Net: Bitget’s User Protection Fund

In the wake of major exchange hacks, user trust is frequently decimated by insolvency fears and prolonged withdrawal freezes. To counter this, modern crypto exchanges have increasingly relied on dedicated insurance reserves, often styled as user protection funds.

Bitget’s response to the $351.6 million heist serves as a stress test for its own financial safety net. The Bitget User Protection Fund, which currently holds 5,500 BTC valued at approximately $464 million, exceeds the total value of the stolen assets. Because this fund is held in reserve specifically for catastrophic scenarios, the exchange is uniquely positioned to absorb the blow without passing losses onto individual account holders.

Industry analysts have noted that while the presence of the User Protection Fund prevents immediate systemic insolvency for Bitget, the psychological toll on retail investors and the reputational damage to the platform’s security architecture will require sustained remediation efforts. Transparency regarding the exact vulnerability in the backend wallet-service system will be paramount for restoring absolute confidence among institutional and retail clients alike.

The Shadow of State-Sponsored Cybercrime: North Korea’s Crypto Arsenal

The attribution of the Bitget heist to North Korean state-sponsored hackers places the event within a well-documented, highly alarming macroeconomic trend. Over the past decade, Pyongyang-linked hacking collectives—most notably groups like the Lazarus Group and related sub-units—have evolved from traditional bank robberies into highly specialized, hyper-efficient cryptocurrency cyber-armies.

Intelligence agencies and blockchain analytics firms have repeatedly warned that state-backed cyber operations in North Korea are explicitly designed to bypass international economic sanctions and generate revenue for the regime’s heavily sanctioned weapons programs, including its ballistic missile development initiatives.

The scale of these operations is staggering. According to comprehensive data published by blockchain intelligence firm Chainalysis, state-backed North Korean hacking syndicates amassed an estimated $1.34 billion across 47 distinct cryptocurrency heists over the course of a single calendar year. Furthermore, digital asset intelligence firm Elliptic reported that North Korean threat actors have collectively stolen upwards of $6 billion in cryptocurrency assets since 2017.

The Bitget incident also follows closely on the heels of other historic cyber attacks targeting the centralized exchange ecosystem. Most notably, the digital asset community is still reeling from the unprecedented Bybit hack, in which North Korean operatives successfully penetrated an Ethereum cold wallet to steal a staggering $1.5 billion—marking the largest recorded crypto heist in financial history.

Broader Implications for Centralized Crypto Exchanges

The Bitget breach underscores enduring vulnerabilities within the centralized exchange (CEX) model. While platforms invest heavily in cold storage solutions—offline cryptographic vaults that are virtually immune to remote network intrusions—operational hot and warm wallets remain necessary to facilitate day-to-day liquidity, instant trading, and user withdrawals. These active operational systems inherently require network connectivity, presenting a persistent attack surface for sophisticated adversaries.

Security experts emphasize that as perimeter defenses around cold storage improve, advanced threat actors are increasingly shifting their focus toward backend infrastructure, third-party service providers, API gateways, and authorization-signing workflows. By compromising the administrative or backend systems that govern hot wallet transactions, attackers can trick internal authorization protocols into executing fraudulent transfers under the guise of legitimate administrative operations.

For the broader fintech and cryptocurrency sectors, the Bitget incident serves as an urgent reminder of the necessity for Zero Trust architecture, rigorous internal segmentation, multi-party computation (MPC) key management, and continuous behavioral anomaly detection. As long as centralized platforms hold billions of dollars in liquid digital assets, they will remain primary targets for sophisticated, well-funded nation-state actors.

As the global investigation into the Bitget breach continues, regulatory bodies, cybersecurity firms, and exchange operators will be watching closely to see how quickly the platform can safely resume normal withdrawal operations and whether international law enforcement can successfully track, freeze, and recover the remaining unrecovered funds from the sprawling multi-chain exploit.

September 25, 2026 0 comment
0 FacebookTwitterPinterestEmail
Web3 & DApps

9 Startups Selected for the Injective Ecosystem Builder Catalyst: Scaling the DeFi-First Future

by admin September 25, 2026
written by admin

The landscape of decentralized finance (DeFi) is undergoing a structural transformation, transitioning away from rudimentary token exchanges toward sophisticated, institutional-grade financial infrastructure. Amidst this rapid evolution, Web3 accelerator Outlier Ventures and Layer-1 blockchain network Injective have officially announced the launch of their latest cohort under the Injective Ecosystem Builder Catalyst. This intensive, nine-week virtual accelerator program has been meticulously designed to incubate and scale the next generation of high-growth decentralized applications and foundational infrastructure projects built natively on the Injective network.

The initiative arrives at a critical juncture for the broader digital asset economy. As the global financial sector increasingly intersects with distributed ledger technology, market metrics indicate robust expansion. Decentralized finance Total Value Locked (TVL) has hovered near $140 billion, while the tokenization and integration of Real-World Assets (RWAs) have experienced an exponential growth trajectory, surging by over 380% since 2022. By leveraging Injective’s high-performance architecture—which boasts sub-second block finality, gasless transaction mechanics, and robust MultiVM interoperability—the newly selected startups are positioned to construct financial primitives that bridge traditional finance (TradFi) and the decentralized web.

The Macroeconomic Context and the Shift Toward DeFi-First Infrastructure

For years, the initial waves of decentralized finance were characterized by iterative replication of legacy financial models, often constrained by high transaction fees, network congestion, and fragmented liquidity pools. However, the current maturation phase of the industry demands a "DeFi-first" approach, where protocols are architected from the ground up to capitalize on the unique composability and speed of modern blockchain networks.

Injective has steadily positioned itself as a premier destination for developers seeking a distinct technical edge. By offering native financial modules that streamline order books, derivatives trading, and automated collateral management, the network provides developers with capabilities that surpass the operational efficiencies of legacy financial systems. The current cohort of startups participating in the Injective Ecosystem Builder Catalyst is not merely porting traditional applications onto the blockchain; they are engineering advanced paradigms, ranging from agentic autonomous trading systems to on-chain repo and private debt markets.

According to industry analysts, the convergence of high-speed execution environments and institutional compliance frameworks is vital for driving the next wave of capital adoption. Traditional financial institutions, constrained by legacy ledger systems and high middle-office overhead, are increasingly looking toward high-throughput blockchains to optimize settlement times and minimize counterparty risk. The nine-week accelerator aims to bridge this gap by providing selected founders with comprehensive mentorship, regulatory guidance, and strategic access to ecosystem liquidity incentives.

A Comprehensive Overview of the Cohort Startups

The newly selected cohort features a diverse array of projects addressing various verticals within the digital asset and financial technology sectors, ranging from institutional execution platforms to AI-driven Web3 operating systems.

QuantCite spearheads the institutional tier of the cohort as an advanced Order and Execution Management System (OEMS) integrated with smart-routing technology. Designed specifically for quantitative hedge funds and professional traders, QuantCite unifies execution venues across both centralized exchanges and decentralized liquidity pools, delivering the low latency and deep liquidity access required for institutional-grade strategies.

9 Startups Selected for the Injective Ecosystem Builder Catalyst: Scaling the DeFi-First Future

In the consumer fintech sector, Joinn aims to bridge the gap between emerging markets and global capital yields. The application provides everyday users with seamless access to stable, yield-generating tokenized financial assets through an interface modeled after mainstream Web2 applications. Featuring gasless, signature-free cross-chain transactions, 24/7 account access, an integrated Visa card experience, and an autonomous AI agent, Joinn seeks to simplify the mechanics of wealth accumulation and compound growth for retail participants.

Choice addresses liquidity fragmentation by functioning as a specialized decentralized exchange and aggregation layer optimized explicitly for the Injective network. Utilizing a sophisticated routing algorithm that queries liquidity across multiple decentralized venues, Choice aims to optimize swap execution prices while minimizing slippage for end users.

Stabled tackles the complexities of international trade by offering an enterprise-grade cross-border payments platform. Designed to facilitate instant, compliant stablecoin transactions for businesses, Stabled bypasses traditional correspondent banking rails, thereby mitigating foreign exchange losses and significantly reducing settlement delays.

Focusing on the burgeoning RWA sector, Quantum Street comprises a team of capital markets and financial engineering specialists dedicated to onboarding off-chain assets onto the blockchain. By structuring cash-flowing business transactions into verifiable on-chain instruments, Quantum Street generates authentic utility for stablecoins while actively contributing to the expansion of decentralized finance TVL.

Spout introduces a novel model to the public equities market by facilitating the borrowing and lending of tokenized U.S. equities. Utilizing a Collateralized Debt Position (CDP) framework, Spout enables users to access 0% annual percentage rate (APR) margin loans while simultaneously offering competitive lending yields hovering around 10% APY.

Dapps.co focuses on the intersection of social networking and tokenized economies, offering a Web3-native social platform designed to restore economic agency to content creators. The platform incorporates an artificial intelligence provenance layer intended to combat low-quality synthetic content, while providing direct monetization channels through creator tipping and paid direct messaging features.

Chain Capital addresses liquidity constraints within private credit markets by transforming illiquid private debt instruments into tradable securities. Through the tokenization of corporate invoices and receivables, the platform automates the securitization workflow, reportedly reducing middle-office operational costs by up to 75% while providing institutional investors with compliant access to high-yield investment exposures.

Completing the cohort is HodlHer, positioned as the world’s first AI-driven Web3 operating system native to Injective. Utilizing specialized intelligent software personas, HodlHer assists individual users, creators, and enterprise projects in executing complex workflows, encompassing market perception, analytical reasoning, and automated on-chain execution.

9 Startups Selected for the Injective Ecosystem Builder Catalyst: Scaling the DeFi-First Future

Chronology and Program Roadmap

The Injective Ecosystem Builder Catalyst operates on a structured, nine-week virtual accelerator timeline tailored to accelerate product development, refine go-to-market strategies, and prepare participating founders for institutional fundraising.

The program officially kicked off with the selection and onboarding of the cohort, bringing together technical founders from diverse global jurisdictions. Throughout the nine-week duration, participants engage in rigorous workshops, technical deep-dives with core Injective developers, and one-on-one mentorship sessions led by venture capitalists, legal experts, and seasoned operators from Outlier Ventures and the broader Web3 ecosystem.

The culmination of the accelerator program is scheduled for the upcoming Injective Ecosystem Builder Catalyst Demo Day, set for February 25, 2026. During this flagship virtual event, cohort founders will present their refined protocols, technical achievements, and future roadmap milestones to a curated audience of leading venture capital investors, institutional allocators, and ecosystem partners.

Industry Implications and Broader Market Outlook

The launch of this accelerator cohort underscores a broader structural shift within the cryptocurrency industry toward functional utility, composability, and regulatory alignment. As regulatory frameworks across major global jurisdictions become increasingly defined, institutional investors and fintech innovators are placing heightened emphasis on infrastructure that can scale securely without sacrificing decentralization or performance.

Observers note that the integration of artificial intelligence agents with high-performance blockchain rails—as demonstrated by several projects within the current Injective cohort—represents a burgeoning frontier for financial technology. By automating complex multi-step financial transactions and risk management strategies, these systems have the potential to drastically reduce administrative overhead and democratize access to sophisticated financial instruments.

Furthermore, the emphasis on Real-World Asset tokenization and private debt securitization highlights the ongoing convergence between traditional capital markets and decentralized finance. As platforms like Chain Capital and Quantum Street successfully bridge off-chain cash flows with on-chain liquidity pools, the boundaries separating traditional banking from decentralized networks will continue to blur.

Leadership from both Outlier Ventures and Injective have emphasized that the success of the current cohort will serve as a bellwether for the next generation of financial applications. By equipping visionary founders with the necessary capital, mentorship, and technical foundation, the initiative aims to establish a sustainable baseline for the future architecture of global finance. Stakeholders across the digital asset ecosystem are closely monitoring the progress of these startups as they prepare to unveil their production-ready technologies at the upcoming Demo Day.

September 25, 2026 0 comment
0 FacebookTwitterPinterestEmail
Web3 & DApps

Outlier Ventures and Injective Unveil the Next Cohort of High-Growth Startups for the Ecosystem Builder Catalyst Accelerator

by admin September 25, 2026
written by admin

The modern architecture of global finance is undergoing a profound structural evolution, shifting away from experimental token swaps toward a mature, institutional-grade financial layer. Marking a significant milestone in this transition, Web3 accelerator Outlier Ventures and Layer-1 blockchain platform Injective have officially announced their latest cohort of startups selected for the Injective Ecosystem Builder Catalyst.

This intensive nine-week virtual accelerator program has been meticulously designed to identify, mentor, and back the next generation of pioneering founders. These entrepreneurs are building high-growth decentralized finance (DeFi) and core infrastructure projects natively on the Injective network. By capitalizing on Injective’s advanced technological framework—which boasts sub-second block finality, gasless transaction capabilities, and MultiVM interoperability—the newly selected startups aim to bridge the gap between traditional financial markets and decentralized ledgers.

The launch of this cohort arrives at a critical juncture for the digital asset industry. Decentralized finance Total Value Locked (TVL) has steadily climbed toward the $140 billion threshold, while Real-World Assets (RWAs) tokenization has scaled by more than 380% since 2022. This rapid maturation underscores a broader macro trend: institutional players and retail users alike are demanding high-performance, purpose-built infrastructure that can handle complex financial instruments without sacrificing speed or security.

Navigating the Injective Ecosystem Builder Catalyst Cohort

The selected participants in the current cohort are not merely porting legacy financial products onto a blockchain ledger. Instead, they are engineering novel financial primitives—ranging from agentic trading systems to advanced on-chain repo markets—that are uniquely enabled by Injective’s shared liquidity architecture.

9 Startups Selected for the Injective Ecosystem Builder Catalyst: Scaling the DeFi-First Future

During the nine-week program, these teams receive comprehensive, hands-on mentorship, targeted legal guidance, and direct access to vital ecosystem incentives designed to accelerate their path to market. The initiative seeks to ensure that these early-stage companies can scale efficiently while maintaining regulatory awareness and technical robustness.

The diverse array of startups chosen for this cohort spans institutional trading, fintech, decentralized exchanges, international payments, real-world asset tokenization, equity lending, Web3 social networks, private debt, and AI-driven operating systems:

  • QuantCite: Operating as an institutional-grade Order and Execution Management (OEM) and smart-routing platform, QuantCite unifies execution across both centralized exchanges and decentralized venues. It is engineered to provide quantitative funds and professional traders with high-performance infrastructure and deep liquidity access.
  • Joinn: A consumer-focused fintech application aimed at emerging markets. Joinn helps everyday users protect and grow their savings through access to stable, yield-generating tokenized financial assets. Designed with a seamless Web2-like user experience, it operates on secure blockchain rails featuring gasless and signless cross-chain transactions, 24/7 account access, a connected Visa card experience, and an integrated AI agent to automate compounding.
  • Choice: A decentralized exchange and aggregation layer specifically optimized for the Injective network. By employing a sophisticated routing algorithm that aggregates liquidity across all available venues, Choice guarantees users optimal swap execution while minimizing slippage.
  • Stabled: A cross-border international payments platform tailored for modern businesses. Stabled facilitates instant, compliant stablecoin transactions that bypass legacy correspondent banking networks, effectively minimizing foreign exchange losses and settlement delays.
  • Quantum Street: Comprising capital market experts and financial engineering specialists, Quantum Street bridges the gap between traditional finance and decentralized ledgers by bringing off-chain assets on-chain. By structuring transactions for cash-flowing businesses, they introduce tangible utility to stablecoins and contribute to broader Total Value Locked (TVL) expansion.
  • Spout: A platform transforming the multi-trillion-dollar equities market by facilitating the seamless borrowing and lending of U.S. public equities. Spout tokenizes traditional equities and implements a Collateralized Debt Position (CDP) model, enabling 0% APR margin loans alongside competitive lending yields of approximately 10% APY.
  • Dapps.co: A Web3-native social network designed to restore agency to digital creators through tokenized communities and robust on-chain economies. The platform incorporates an AI provenance layer to combat low-quality generated content, while empowering creators to monetize their work directly through transparent tipping mechanisms and paid direct messaging.
  • Chain Capital: A specialized platform that converts illiquid private debt into tradable, standardized securities. By tokenizing invoices and commercial receivables, Chain Capital automates complex securitization workflows, cutting middle-office operational costs by up to 75% and granting institutional investors compliant access to high-yield investment exposures.
  • HodlHer: Positioned as the world’s first AI-driven Web3 operating system built on Injective, HodlHer utilizes unique intelligent personas to assist users, creators, and projects in navigating the complete lifecycle of on-chain engagement—from market perception and analytical reasoning to automated execution.

Background Context and Strategic Alignment

The partnership between Outlier Ventures and Injective reflects a broader industry recognition that the next wave of blockchain adoption will be dictated by system interoperability and functional parity with traditional finance (TradFi). While early DeFi iterations focused heavily on speculative token generation and isolated liquidity pools, the current market cycle demands sophisticated collateral management, robust order books, and institutional-grade compliance frameworks.

Injective has deliberately positioned itself as a destination for developers demanding a definitive technical edge. By offering native financial modules at the base layer, the network enables capital efficiency metrics that far surpass those of general-purpose smart contract platforms. This specialized focus has made it an ideal breeding ground for founders looking to construct scalable financial infrastructure.

Industry analysts note that programs like the Ecosystem Builder Catalyst play a vital catalytic role in the lifecycle of early-stage Web3 startups. By providing structured institutional backing during a startup’s formative months, accelerators significantly mitigate the execution risks inherent in building complex financial applications within a rapidly shifting regulatory and technological landscape.

9 Startups Selected for the Injective Ecosystem Builder Catalyst: Scaling the DeFi-First Future

Broader Market Implications and Future Outlook

The convergence of decentralized infrastructure with traditional financial assets represents one of the most significant macro trends in contemporary fintech. As decentralized finance total value locked rebounds and traditional financial institutions increasingly explore tokenized instruments, the infrastructure being built by the Injective cohort is expected to lay the groundwork for the next decade of global financial operations.

By eliminating settlement lags, reducing intermediary overhead, and leveraging artificial intelligence to streamline user interactions, these startups are addressing long-standing inefficiencies in both emerging and developed markets. The ability to execute cross-border transactions instantly or tokenize private debt and public equities without friction signals a permanent shift in how capital is allocated, managed, and distributed globally.

As the current nine-week accelerator cohort progresses toward its culmination, stakeholders, investors, and community members are preparing for the upcoming Injective Ecosystem Builder Catalyst Demo Day, scheduled for February 25, 2026. The event, hosted via Luma, will provide founders with a direct platform to present their refined technologies, business models, and growth strategies to a curated audience of venture capitalists, institutional investors, and ecosystem partners.

With mentorship and technical integration now well underway, the solutions developed within this cohort are projected to transition from testnet environments into active commercial deployment, marking another step forward in the mainstream integration of decentralized financial architecture.

September 25, 2026 0 comment
0 FacebookTwitterPinterestEmail
Bitcoin & Altcoins

Ethereum Foundation Announces Upcoming Protocol AMA Session to Engage Community on Future Development Roadmap

by admin September 24, 2026
written by admin

Since January 2019, the Ethereum Foundation has maintained a transparent, albeit informal, channel of communication with the broader blockchain ecosystem through dedicated Ask Me Anything (AMA) sessions hosted on the r/ethereum subreddit. These periodic digital town halls have evolved from simple Q&A threads into a critical pillar of Ethereum’s decentralized governance model. By providing a platform for direct engagement between core protocol researchers, developers, and the community, the Foundation ensures that the complex technical trajectory of the network remains accessible to those who build upon and invest in it. This tradition of open discourse is set to continue on September 16, as the Foundation’s Protocol cluster prepares to field questions regarding the current state of Ethereum’s technical evolution and its long-term research objectives.

A Tradition of Transparency: The Evolution of Ethereum’s AMA Sessions

The origin of these AMA sessions lies in the need for clarity during Ethereum’s rapid developmental phases. In early 2019, as the community looked toward the horizon of the transition from Proof of Work to Proof of Stake, the gap between core research and user understanding was significant. The Ethereum Foundation leveraged the decentralized, community-driven nature of Reddit to bridge this divide. Over the past five years, these sessions have hosted prominent figures within the Ethereum ecosystem, facilitating deep dives into EIPs (Ethereum Improvement Proposals), client diversity, and the philosophical shifts underpinning the protocol’s architecture.

For the upcoming session on September 16, the focus shifts toward the post-Dencun era. As Ethereum matures, the complexity of its upgrades has increased, necessitating more granular communication. The format remains consistent: a curated thread where technical debates are encouraged, and developers provide nuanced explanations for the design choices that define the network’s future. This approach serves as a counterweight to the often-opaque nature of large-scale decentralized protocol development.

Current Developmental Milestones: Glamsterdam and Hegotá

The Ethereum roadmap is currently navigating a period of intensive testing and strategic realignment. Two major areas of interest for the community are the Glamsterdam hard fork and the Hegotá upgrade. Glamsterdam, currently in its public testing phase, represents a continued effort to optimize network performance and security. The deployment of such upgrades requires rigorous validation across multiple testnets, ensuring that client software from teams like Geth, Nethermind, and Besu can maintain consensus without disruption.

Simultaneously, the scope of Hegotá is undergoing a process of refinement. In the lifecycle of an Ethereum upgrade, "scoping" is a critical phase where researchers weigh the urgency of specific technical implementations against the risk of network instability. As the Ethereum Foundation moves to narrow the focus of Hegotá, community interest has peaked regarding which features will be prioritized for inclusion and which will be deferred to subsequent, yet-to-be-defined upgrades. This transition period highlights the tension between the desire for rapid innovation and the necessity of maintaining the "slow and steady" security profile that has become a hallmark of the Ethereum protocol.

Technical Scope: From Post-Quantum Cryptography to L1 Privacy

The September 16 session is expected to cover a wide spectrum of technical inquiries. Based on current research initiatives, participants are likely to focus on several high-impact domains:

Post-Quantum Ethereum

As quantum computing advances, the long-term security of cryptographic signatures becomes a point of concern. The Ethereum Foundation has been actively exploring the integration of post-quantum resilient signature schemes. The transition to such schemes represents a massive engineering undertaking that would require long-term planning and community consensus.

L1-zkEVM and Formal Verification

The quest to integrate Zero-Knowledge Ethereum Virtual Machine (zkEVM) functionality directly into the Layer 1 protocol is one of the most ambitious research goals currently under consideration. The goal is to provide native scalability that does not sacrifice the security guarantees of the base layer. Complementing this, formal verification—the mathematical proof of software correctness—has become a standard requirement for all new protocol changes, minimizing the surface area for critical bugs.

Decoupled Consensus and State Growth

The future of state management remains a pressing concern for the network. As the amount of historical data stored on the blockchain grows, the requirements for running a validator node increase. Researchers are examining methods to decouple consensus from execution and implement more efficient state-pruning techniques to ensure that Ethereum remains decentralized and accessible to hobbyist validators.

Analytical Context: The Role of Community Feedback in Protocol Governance

While the Ethereum Foundation does not hold absolute authority over the protocol—governance is fundamentally determined by node operators and the ecosystem at large—the insights provided during these AMAs act as a "temperature check" for the community. The information shared by developers during these sessions often informs the discourse on various Ethereum forums and developer calls.

Data from previous years suggests that these sessions successfully reduce market uncertainty. Following major AMA sessions, there is historically an uptick in developer activity surrounding the discussed EIPs. By allowing researchers to explain the "why" behind their "what," the Foundation fosters an environment where third-party developers can build applications with a clearer understanding of the protocol’s future technical constraints.

Official Procedure for Submission

To ensure that the upcoming session remains productive and addresses the most pressing concerns, the Ethereum Foundation has implemented a proactive submission process. Rather than relying solely on real-time questions, which can often be repetitive or lack depth, the team is gathering inquiries in advance. This allows researchers to prepare data-backed, comprehensive responses to complex technical queries.

Interested parties, including developers, researchers, and network participants, are encouraged to submit their questions through the designated Ethereum Foundation portal. By aggregating these questions early, the Foundation intends to categorize them by topic—ranging from client development and devnets to long-term L1 privacy strategies—ensuring that the session on September 16 provides the maximum possible value to the technical community.

Broader Implications for the Blockchain Industry

The approach taken by the Ethereum Foundation—prioritizing open communication and transparent technical roadmapping—stands as a case study for decentralized organizations. In an industry often marred by volatility and sudden pivots, the predictable cadence of these AMAs provides a stabilizing influence.

As Ethereum moves further into the "Age of Scarcity" and "Age of Scale" phases of its roadmap, the role of these public engagements will likely become even more significant. With the rise of L2 scaling solutions and the increasing institutionalization of the network, the ability to articulate complex technical changes to a diverse audience is a vital skill. By continuing this tradition, the Ethereum Foundation demonstrates that despite the protocol’s massive growth and complexity, the core development process remains deeply rooted in the community that first imagined its potential.

As the September 16 deadline approaches, the anticipation within the developer community is palpable. The questions raised will not only address the immediate technical hurdles of the Glamsterdam and Hegotá upgrades but will also help define the intellectual agenda for the next generation of Ethereum research. Whether regarding the integration of advanced cryptographic primitives or the long-term sustainability of the protocol’s consensus mechanisms, the upcoming AMA is poised to serve as a definitive resource for understanding where Ethereum is headed in the months and years to come.

September 24, 2026 0 comment
0 FacebookTwitterPinterestEmail
Newer Posts
Older Posts

Recent Posts

  • The Evolution of the Web3 Wallet: From Private-Key Vault to the Command Center of the Agentic Web
  • Ethereum Foundation Announces Annual Protocol AMA Session Scheduled for September 16
  • Kraken Expands Its Digital Asset Offerings with the Official Listing of Doppler Finance (Xdp)
  • CSD BR and Ripple Collaborate to Integrate XRP Ledger into Brazilian Financial Market Infrastructure
  • Web3 Venture Funding Surges to Record $22 Billion in Third Quarter 2025 Driven by Institutional Adoption

Recent Comments

No comments to show.
  • Facebook
  • Twitter

@2021 - All Right Reserved. Designed and Developed by PenciDesign


Back To Top
Dr Crypton
  • Home
  • About Us
  • Contact Us
  • Cookies Policy
  • Disclaimer
  • DMCA
  • Privacy Policy
  • Terms and Conditions

We are using cookies to give you the best experience on our website.

You can find out more about which cookies we are using or switch them off in .

Dr Crypton
Powered by  GDPR Cookie Compliance
Privacy Overview

This website uses cookies so that we can provide you with the best user experience possible. Cookie information is stored in your browser and performs functions such as recognising you when you return to our website and helping our team to understand which sections of the website you find most interesting and useful.

Strictly Necessary Cookies

Strictly Necessary Cookie should be enabled at all times so that we can save your preferences for cookie settings.