
Federal Bureau of Investigation agents have arrested a prominent Canadian cybersecurity executive in Pennsylvania in connection with a sweeping international investigation into the notorious ShinyHunters hacking collective. The high-profile arrest marks a critical turning point in a federal probe that recently suffered an embarrassing breach, during which the cybercrime syndicate allegedly exfiltrated sensitive data pertaining to thousands of federal law enforcement agents.
Multiple sources familiar with the ongoing federal inquiry confirmed the arrest to investigative journalist Brian Krebs, aligning with initial reports published by The New York Times. The suspect has been identified as 54-year-old Edward Dubrovsky, a veteran cybersecurity professional, author, and executive associated with Canadian security firms specializing in ransomware negotiation and cyber extortion advisory services. Dubrovsky’s apprehension during a professional cyber insurance conference in Philadelphia highlights a dramatic convergence between the formal incident response industry and the shadowy underworld of international cybercrime.
Main Facts and Circumstances of the Arrest
Federal court records indicate that Dubrovsky was taken into custody on October 8, 2026, in Pennsylvania, facing federal charges that include conspiracy to threaten to impair the confidentiality of information with the intent to extort money, alongside interference with commerce by threats. Although several core documents associated with the initial complaint remain sealed under judicial order, a docket summary indexed on CourtListener outlines the formal allegations against him.
At the time of his arrest, Dubrovsky was visiting Philadelphia to attend the Cyber Risk Summit, an annual cyber insurance and risk management conference held at the Loews Philadelphia Hotel between October 5 and October 7. Conference documentation lists CyberSteward, a Canadian security firm with which Dubrovsky is affiliated, as a participant, while his previous professional home, Cypfer, served as one of the summit’s premier sponsors.
Following his apprehension, Dubrovsky was initially held at a federal detention facility in Philadelphia according to the U.S. Bureau of Prisons inmate locator. However, court filings reveal that the case was swiftly transferred on October 9 to the U.S. District Court for the Eastern District of Texas. Legal and law enforcement sources indicate that the Eastern District of Texas has been designated as the centralized command hub for the multifaceted, multi-jurisdictional investigation into the ShinyHunters operation. At present, court records reflect that Dubrovsky has not yet retained private legal counsel, nor has a public defender been formally appointed by the court.

Professional Background and Industry Profile
The arrest of a senior figure within the incident response community has sent shockwaves through the cybersecurity sector. Dubrovsky has cultivated a long-standing public profile as an authority on ransomware mitigation, digital extortion dynamics, and corporate crisis management. His LinkedIn profile states that he previously served in leadership roles at Cypfer—though a corporate spokesperson clarified that he departed his position as managing director in December 2025 and was never a co-founder, contrary to social media claims—before moving to CyberSteward.
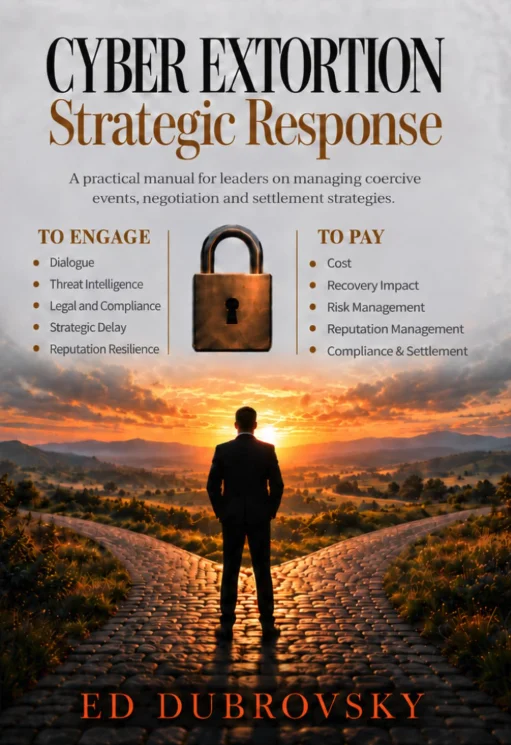
Furthermore, Dubrovsky is the author of Cyber Extortion Strategic Response, a 252-page textbook designed to guide corporate executives through the complexities of ransomware negotiations. The publication emphasizes the nuanced distinctions between communication, tactical negotiation, and capitulation to criminal demands. Ironically, the central thesis of his professional literature underscores the delicate balance of engaging with threat actors to buy time, test claims, and preserve organizational options—principles that federal prosecutors now allege crossed legal and criminal boundaries.
Chronology of the ShinyHunters Escalation
To contextualize Dubrovsky’s arrest, industry analysts point to an escalating series of international law enforcement actions and high-stakes digital confrontations that have defined the latter half of 2026.
- Late 2025: ShinyHunters intensifies its targeting of corporate accounts at software-as-a-service (SaaS) providers, deploying sophisticated phishing tactics and credential theft to extract proprietary data and execute corporate extortion schemes.
- September 2026: Dutch law enforcement authorities execute a series of targeted raids, arresting reformed hacker Pepijn van der Stap in connection with the broader ShinyHunters enterprise. Federal investigators immediately begin forensic analysis of electronic devices seized during the operation.
- Early October 2026: Following Van der Stap’s arrest, an individual operating under the alias "Rey" assumes operational control of ShinyHunters. In a brazen display of defiance, "Rey" begins taunting federal authorities online after stealing sensitive files from the FBI’s online recruitment portal, including personnel unit assignments, specializations, and confidential medical and psychiatric records.
- October 5–7, 2026: Edward Dubrovsky attends the Cyber Risk Summit in Philadelphia, where industry networking intersects with the quiet coordination of federal investigators tracking illicit ransomware facilitators.
- October 7, 2026: Reuters and investigative reporters reveal that "Rey"—identified as a teenager named Saif Al-din Khader—has been detained by authorities and is cooperating with the FBI. The arrest coincides with attempts by the syndicate to extort a navigation and digital aviation unit divested by Boeing in late 2025.
- October 8, 2026: Edward Dubrovsky is arrested by FBI agents in Pennsylvania on federal cyber extortion and conspiracy charges.
- October 9, 2026: Federal court documents formally transfer Dubrovsky’s prosecution to the Eastern District of Texas, aligning with the centralized federal task force managing the ShinyHunters dossier.
Supporting Data and Scale of Operations
The ShinyHunters organization has evolved into one of the most destructive and financially lucrative cyber extortion syndicates operating globally. According to official FBI assessments, the group has successfully extorted in excess of $70 million from corporate and institutional victims during the 2026 calendar year alone.
The methodology favored by the group typically relies on initial access brokers, credential harvesting, and sophisticated social engineering targeting cloud-hosted data environments. Once inside a corporate network, the collective exfiltrates proprietary intellectual property, customer databases, and internal communications, threatening public disclosure via dedicated leak sites unless exorbitant cryptocurrency demands are met. The group’s infiltration of federal recruitment infrastructure represents an unprecedented operational security failure, prompting intense congressional scrutiny and an aggressive, unyielding response from federal law enforcement leadership, including FBI Director Kash Patel.
Official Responses and Industry Implications
As of press time, the Federal Bureau of Investigation has declined to comment publicly on the specifics of Dubrovsky’s indictment, citing the active and ongoing nature of the judicial proceedings. Representatives for CyberSteward have not yet issued a formal statement regarding the arrest of their affiliate.

Legal and security analysts suggest that Dubrovsky’s arrest signals a paradigm shift in how federal authorities view the ecosystem surrounding ransomware and extortion negotiations. For years, the incident response and cyber insurance industries have operated in a gray area, facilitating communication and settlements between victimized enterprises and illicit threat actor groups.
The prosecution of a high-profile negotiation expert introduces profound legal ambiguity regarding the boundary between legitimate crisis management and criminal conspiracy, material support, or aiding and abetting extortion. Legal scholars note that prosecutors will bear the burden of proving that Dubrovsky’s actions went beyond standard advisory protocols and constituted active criminal conspiracy under U.S. federal statutes.
Broader Impact on the Cybersecurity Ecosystem
The unfolding legal battle is expected to have far-reaching ramifications for commercial cybersecurity firms, incident response providers, and cyber insurers worldwide. Cybersecurity firms that offer ransomware negotiation services may face heightened regulatory scrutiny, stricter compliance mandates, and increased legal exposure when handling client communications with sanctioned or criminal hacking groups.
Furthermore, sources close to the investigation indicate that federal authorities are continuing to examine forensic evidence recovered from previous arrests in Europe and North America. Additional indictments targeting principals, facilitators, and negotiators associated with other prominent ransomware advisory entities are widely anticipated in the coming weeks. As this complex, fast-moving national security story continues to develop, federal prosecutors in the Eastern District of Texas are expected to unveil further details regarding the nexus between corporate cyber defense and transnational criminal extortion syndicates.
