• Home
  • About Us
  • Contact Us
  • Cookies Policy
  • Disclaimer
  • DMCA
  • Privacy Policy
  • Terms and Conditions
Dr Crypton
Secure Your Future in Crypto
Artificial Intelligence & Tech

Top 5 MCP Servers for High-Performance Agentic Development

by admin July 21, 2026
written by admin

The landscape of artificial intelligence development underwent a fundamental transformation in late 2024 when Anthropic introduced the Model Context Protocol (MCP). Prior to this standardization, developers were forced to engineer bespoke "glue code" for every unique integration between an Large Language Model (LLM) and an external data source or tool. This fragmented approach created significant friction, limiting the scalability of autonomous agents. However, with the subsequent adoption of MCP by industry titans including OpenAI, Google, and Microsoft throughout 2025, the protocol has solidified its position as the universal standard for agentic interoperability. Often described as the "USB-C for AI," MCP allows any compliant tool to interface seamlessly with any compliant agent, effectively decoupling the intelligence of the model from the specific mechanics of the tools it employs.

As the ecosystem matured, the repository of available MCP servers expanded exponentially. By the end of 2025, following the protocol’s donation to a Linux Foundation-governed body, the community faced a new challenge: distinguishing high-performance, maintained tools from the "noise" of experimental or abandoned projects. Several early-stage servers, once touted in initial industry reports, have since been archived or superseded by more robust alternatives. For developers aiming to build production-grade agentic workflows, selecting the right server stack is now a matter of technical necessity rather than mere convenience.

The Genesis and Standardization of the Model Context Protocol

The transition from static LLM interactions to dynamic agentic workflows required a reliable method for models to access local and remote resources. Before MCP, an agent tasked with reviewing a GitHub repository and deploying a fix would require custom API integrations for GitHub, a local file system handler, and a separate logic layer for terminal execution. Each of these components had to be re-written or heavily modified whenever the underlying model or the external API changed.

The timeline of MCP’s ascent is marked by rapid industry consolidation:

  • Late 2024: Anthropic open-sources the Model Context Protocol, providing a JSON-RPC-based standard for tool use.
  • Early 2025: Major IDE providers and LLM developers (OpenAI, Microsoft, and Google) announce native support for MCP in their respective developer environments.
  • Mid-2025: The emergence of specialized "MCP Server Marketplaces" and automated discovery tools.
  • Late 2025: The protocol is officially donated to the Linux Foundation, ensuring neutral governance and long-term stability for the standard.

This standardization has shifted the focus from how to connect tools to which tools provide the highest fidelity of data and the most reliable execution.

1. GitHub MCP Server: The Core of Agentic Software Engineering

The official GitHub MCP server has emerged as the foundational tool for any agent involved in the software development lifecycle. Maintained directly by GitHub, this server provides a high-fidelity bridge between an LLM and the complex environment of a modern repository. Unlike generic API wrappers, the GitHub MCP server exposes a structured set of tools that allow an agent to perform complex operations through natural language commands.

The server’s capabilities extend beyond simple code reading. It allows agents to manage the entire "inner loop" of development, including:

  • Repository Management: Searching code, managing issues, and triaging pull requests.
  • CI/CD Integration: Monitoring GitHub Actions and interpreting failure logs to suggest or implement fixes.
  • Security Auditing: Accessing code security alerts and Dependabot findings.

With approximately 30,000 GitHub stars and a rigorous update schedule, this server is optimized for agents that need to "move" code rather than just "reason" about it. By providing a direct line to the version control system, it enables agents to act as autonomous junior developers capable of handling routine maintenance and initial bug triage.

2. Playwright MCP: Deterministic Web Interaction via Microsoft

Web automation has historically been a point of failure for AI agents. Traditional methods often relied on vision models interpreting screenshots—a process prone to errors in coordinate calculation and high latency. Microsoft’s Playwright MCP server addresses this by bypassing the visual layer entirely. Instead, it interacts with the browser through the accessibility tree.

This approach provides several critical advantages for high-performance development:

  • Structured Data: The agent receives deterministic, text-based representations of page elements rather than ambiguous pixels.
  • Speed: Eliminating the need for constant screenshot processing significantly reduces token consumption and latency.
  • Reliability: Interactions are based on the DOM (Document Object Model) and accessibility roles, making them resilient to minor CSS or layout changes.

Currently maintaining a count of roughly 31,000 stars, Playwright MCP offers over 40 distinct tools. It is the preferred choice for agents tasked with automated testing, web scraping of JavaScript-heavy sites, or navigating complex enterprise web portals where vision-only models frequently stumble.

3. Context7: Mitigating Hallucinations through Live Documentation

One of the primary obstacles in AI-assisted coding is the "knowledge cutoff" and the subsequent hallucination of APIs. Context7, developed by Upstash, serves as a specialized RAG (Retrieval-Augmented Generation) layer specifically for library documentation. It injects up-to-date, version-specific documentation directly into the agent’s context window.

The impact of Context7 on code quality is quantifiable. By ensuring the agent is working with the exact syntax of the current library version—rather than a version from eighteen months ago—it eliminates the "trial and error" loop often seen in agentic coding.

  • Popularity: With nearly 59,000 stars, it is one of the most widely adopted servers in the ecosystem.
  • Efficiency: It targets the highest-leverage point of failure: the discrepancy between the model’s training data and the current state of software libraries.
  • Use Case: Essential for agents working with fast-moving ecosystems like Next.js, Tailwind CSS, or evolving AI SDKs.

4. Serena: Semantic Code Understanding via LSP

While many agents interact with code as simple text, Serena (by Oraios) treats code as a structured tree of symbols. By leveraging the Language Server Protocol (LSP), Serena provides an agent with an IDE-like understanding of a codebase across more than 40 programming languages.

The distinction between Serena and standard text search is significant:

  • Symbol-Level Precision: An agent can ask to "find the definition of the calculateTax function" rather than searching for a string that might appear in comments, logs, or multiple files.
  • Token Efficiency: By identifying the exact lines and symbols needed for a change, Serena prevents the "context bloat" that occurs when an agent must read entire files to find a single variable definition.
  • Cross-Reference Capabilities: It allows agents to understand how a change in one part of a codebase will affect dependencies elsewhere, mirroring the workflow of an experienced human architect.

With 24,000 stars, Serena is increasingly viewed as the "brain" of the coding agent, providing the semantic clarity required for complex refactoring tasks.

5. The Official Reference Servers: The Essential Primitives

The Model Context Protocol’s own reference server collection acts as the "standard library" of the MCP world. This monorepo, which holds over 80,000 stars collectively, provides the fundamental building blocks necessary for any agentic system.

Key servers within this collection include:

  • Filesystem: Provides secure, scoped access to the local file system.
  • Sequential Thinking: Enables the agent to use a dedicated "scratchpad" for multi-step reasoning before executing a command, which has been shown to improve the success rate of complex tasks.
  • Memory: Allows agents to persist information across sessions, creating a "long-term memory" of user preferences or project context.

Industry analysts note that while these reference servers are excellent for development and prototyping, they are maintained as educational standards. Developers are encouraged to monitor the repository closely, as the project recently archived several standalone servers—such as the Postgres and Puppeteer implementations—to focus on core primitives. This transition underscores the importance of verifying server maintenance status before integration.

Market Implications and the Future of the Agentic Stack

The consolidation of these five servers represents a shift toward a more professionalized AI development environment. The move away from brittle, custom-coded integrations toward a standardized "Agentic Stack" has several broader implications for the tech industry:

Economic Efficiency: By reducing the "token tax" associated with inefficient search-and-replace methods and vision-model overhead, MCP-compliant servers like Serena and Playwright make autonomous agents more cost-effective to run at scale.

Security and Governance: The standardization provided by the Linux Foundation allows for better security auditing. When an agent uses a standardized Filesystem MCP server, security teams can implement universal permission sets rather than auditing dozens of different custom scripts.

Developer Productivity: The "USB-C" nature of these tools means developers can swap out underlying LLMs (e.g., moving from GPT-4o to Claude 3.5 Sonnet) without rewriting their tool integrations. This prevents vendor lock-in and fosters a more competitive model market.

Conclusion: Engineering a Coherent Set of "Hands"

Building a high-performance AI agent is no longer just about the "intelligence" of the model; it is about the quality of the "hands" that the model is given. By wiring together GitHub for version control, Playwright for web interaction, Context7 for accurate documentation, Serena for semantic code understanding, and the reference servers for local plumbing, developers can create agents that are both reliable and efficient.

As the Model Context Protocol continues to evolve under the guidance of the Linux Foundation, the focus will likely shift toward even deeper integrations with enterprise systems. For now, the servers highlighted here represent the gold standard for developers seeking to move beyond experimental chatbots and toward truly autonomous, high-performance agentic systems. The key to success in this rapidly changing field is not just choosing the most popular tools, but choosing those that offer deterministic, structured, and actively maintained pathways to the data an agent needs to succeed.
July 21, 2026 0 comment
0 FacebookTwitterPinterestEmail
Artificial Intelligence & Tech

Ask an AI expert: What exactly is the full stack?

by admin July 21, 2026
written by admin

As the global landscape of artificial intelligence shifts from experimental prototypes to enterprise-grade deployments, the term "full stack" has moved from the lexicon of web development into the core of the AI revolution. In a recent technical briefing, Richard Seroter, Google Cloud’s lead for developer experience, outlined the critical importance of a vertically integrated approach to AI. This strategy, which Google has cultivated for over a decade, is now being positioned as the primary differentiator in a crowded market where speed, cost-efficiency, and reliability determine the success of generative AI applications.

The Evolution of the Full-Stack Philosophy

To understand full-stack AI, one must first look at the history of software engineering. Approximately a decade ago, the tech industry popularized the "full-stack engineer"—a developer capable of handling the three primary tiers of an application: the user interface (frontend), the server logic (backend), and the data management (database). This shift was driven by the need for agility; having a single individual or a cohesive team manage every layer of an application reduced the friction of "handoffs" and accelerated product cycles.

In the context of artificial intelligence, this concept has expanded significantly. A modern AI stack is no longer just about code and data; it encompasses everything from the physical silicon in data centers to the final user interface in a consumer app. According to Seroter, who leads developer relations and technical writing at Google Cloud, the transition to full-stack AI represents an end-to-end principle. Instead of developers sourcing hardware from one vendor, models from another, and orchestration tools from a third, a full-stack approach provides a pre-integrated system where every component is optimized to work with the others.

The Four Layers of the Modern AI Infrastructure

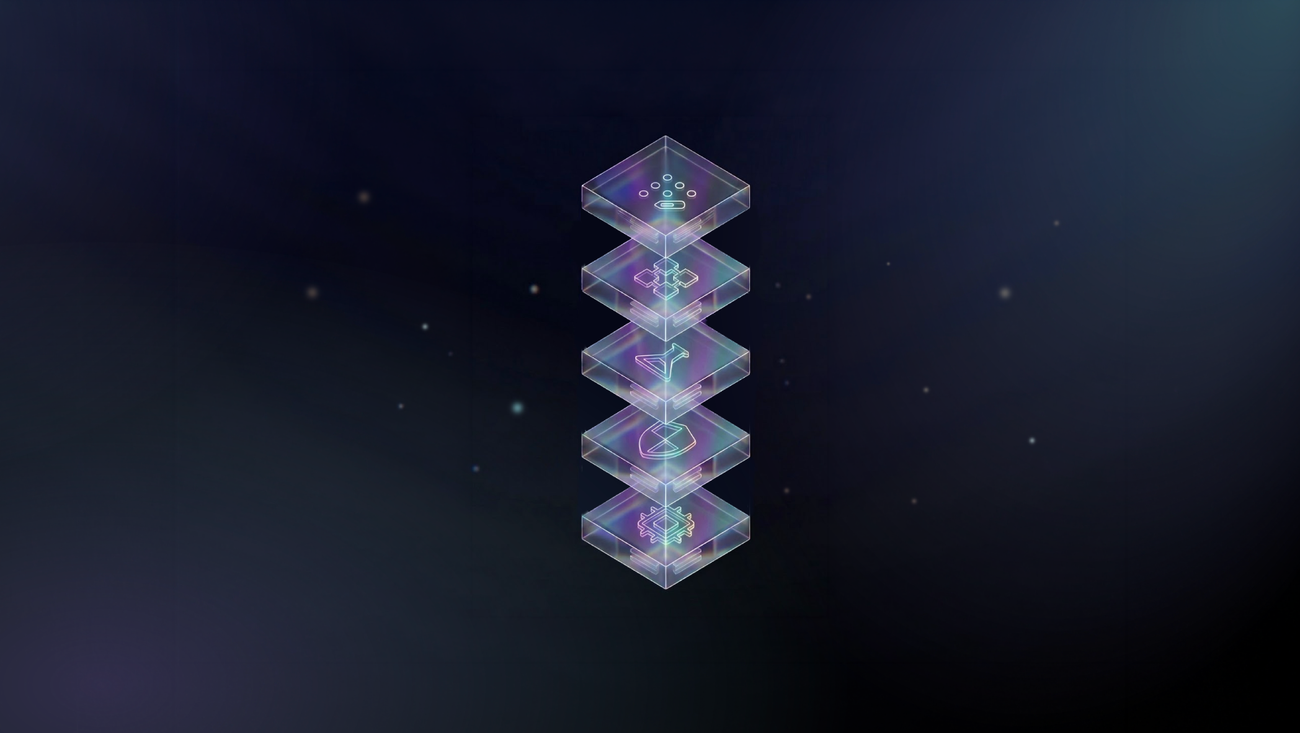
The industry generally recognizes four distinct layers that constitute a comprehensive AI stack. Google’s current strategy involves heavy investment and proprietary control over each of these segments:

Ask an AI expert: What exactly is the full stack?

1. Compute Infrastructure: The Silicon Foundation

At the base of the stack lies the hardware. While much of the industry relies on general-purpose Graphics Processing Units (GPUs), Google made a strategic pivot over ten years ago to develop custom silicon known as Tensor Processing Units (TPUs). These Application-Specific Integrated Circuits (ASICs) are designed specifically for the mathematical workloads required by neural networks. By owning the hardware design, a company can optimize power consumption and processing speed, bypassing the supply chain bottlenecks and high margins associated with third-party chip manufacturers.

2. The Model Layer: Frontier Intelligence

The second layer consists of the Large Language Models (LLMs) and multimodal models that serve as the "brain" of the system. This includes the Gemini family of models, developed by Google DeepMind. These models are trained on the underlying TPU infrastructure, creating a feedback loop where the hardware is tuned for the model’s architecture, and the model is optimized for the hardware’s specific capabilities.

3. The Orchestration Platform

Between the raw model and the user lies the orchestration layer. This includes platforms like the Gemini Enterprise Agent Platform and Vertex AI. These tools allow developers to manage "agents"—AI entities that can perform tasks, call APIs, and reason through complex workflows. Without a robust orchestration layer, a model remains a static entity; with it, the model becomes a functional tool capable of interacting with the real world.

4. The User Interface: Direct Integration

The final layer is where the AI meets the end-user. For Google, this manifests in ubiquitous services like Gmail, Maps, and Workspace. By integrating AI directly into these interfaces, the company ensures that the technological advancements made at the hardware and model layers result in immediate, tangible utility for billions of users.

A Decade in the Making: The Chronology of Integration

The move toward a full-stack AI model was not a reactive response to the recent generative AI boom but a calculated, multi-year progression. Industry analysts point to several key milestones in this timeline:

Ask an AI expert: What exactly is the full stack?
  • 2013: Google initiates the internal TPU project, recognizing that the computational demands of voice search and image recognition would eventually exceed the capacity of traditional CPUs and GPUs.
  • 2014: The acquisition of DeepMind provides the research horsepower necessary to develop frontier models.
  • 2016: The first generation of TPUs is publicly announced, powering systems like AlphaGo.
  • 2017: Google researchers publish "Attention is All You Need," introducing the Transformer architecture that serves as the foundation for almost all modern LLMs, including GPT-4 and Gemini.
  • 2023-2024: The launch of the Gemini era marks the full convergence of these efforts, where custom silicon, transformer-based models, and cloud-based orchestration platforms are offered as a single, unified service.

Economic and Technical Implications of Vertical Integration

The primary advantage of the full-stack approach is what engineers call "system reliability." Seroter notes that when a company manages the entire stack, it can diagnose and resolve failures more efficiently. If a latency issue arises at the application level, engineers can trace it down to the orchestration platform or even the hardware level, rather than waiting for an external vendor to issue a patch.

Furthermore, there is a significant economic incentive. Vertical integration allows a provider to eliminate the "stack tax"—the cumulative markups applied by multiple vendors at different layers of the infrastructure. By removing these third-party margins, companies can offer more competitive pricing to developers and enterprise clients. This is particularly crucial as the cost of "inferencing" (running a model after it has been trained) remains a significant barrier to the widespread adoption of AI.

The Open Source Counter-Argument: Opinionated vs. Extensible

A common criticism of the full-stack approach is the risk of "vendor lock-in," where a customer becomes so dependent on a single provider’s integrated system that switching becomes prohibitively expensive. Seroter addresses this by describing Google’s AI platform as "opinionated but extensible."

While the stack is designed to work best as a unit (the "batteries included" philosophy), it remains compatible with external components. For example, developers can use Google’s infrastructure to run open-source models like Gemma, or they can use the Gemini model through third-party orchestration tools. This hybrid approach aims to balance the efficiency of integration with the flexibility required by modern enterprise IT departments.

Tools for the Next Generation of Builders

To make this full-stack technology accessible, the industry is moving toward "low-code" and "no-code" interfaces. Seroter highlights three primary entry points for different skill levels:

Ask an AI expert: What exactly is the full stack?
  • Google AI Studio: Designed for rapid prototyping, this tool allows developers to build and deploy web applications to the cloud with minimal configuration.
  • Gemini Enterprise Platform: A low-code solution aimed at business users who wish to automate workflows, such as inbox management or data parsing, without writing code.
  • Antigravity: A sophisticated platform for building complex AI agents and orchestrated systems, providing a high degree of control for advanced developers.

Industry Impact and the Road Ahead

The shift toward full-stack AI is triggering a broader trend across the tech sector. Competitors like Microsoft and Amazon are also racing to develop their own custom AI chips (such as Microsoft’s Maia and AWS’s Trainium/Inferentia) to complete their respective stacks. The battle for AI supremacy is increasingly being fought not just in the realm of algorithms, but in the efficiency of the entire integrated system.

As AI models become more complex, the ability to fine-tune the hardware they run on will likely become the standard for the industry. For the end-user, this means AI tools that are faster, more reliable, and more deeply integrated into daily digital tasks. For the developer, it means a shift from managing fragmented infrastructure to focusing on the "vibe" and functionality of the application itself.

The full-stack approach represents a maturation of the AI industry. It is a move away from the "move fast and break things" era of disparate tools toward a more stable, industrialized model of technology delivery. As Richard Seroter suggests, the goal is to provide a "front door" for every level of creator, ensuring that whether one is a professional engineer or a casual hobbyist, the underlying complexity of the AI stack remains invisible, leaving only the power of the technology accessible to all.

July 21, 2026 0 comment
0 FacebookTwitterPinterestEmail
Cryptocurrency News

Aave Picks Chainlink CCIP As Default Standard For Cross-Chain sGHO

by admin July 20, 2026
written by admin

Aave governance has moved to make Chainlink CCIP the default standard for cross-chain sGHO transfers, reinforcing the critical role of security-focused infrastructure in the ongoing evolution and maturation of the decentralized finance (DeFi) sector. This strategic decision by one of DeFi’s leading lending protocols signals a broader industry shift towards prioritizing robust, secure, and reliable cross-chain communication, especially for core protocol assets and stablecoins. The move, enacted through a recent Aave governance proposal, specifically targets the launch of sGHO (staked GHO) across multiple blockchain networks, designating Chainlink’s Cross-Chain Interoperability Protocol (CCIP) as the primary and preferred pathway for these transfers.

Aave’s Strategic Imperative: Securing Cross-Chain Stablecoin Transfers

Aave stands as a cornerstone of the DeFi ecosystem, boasting a Total Value Locked (TVL) that frequently ranks among the highest in the industry, often fluctuating between $5 billion and $10 billion across various chains. Its primary function as a non-custodial liquidity protocol allows users to lend and borrow a wide array of digital assets. The introduction of GHO, Aave’s native decentralized, collateral-backed stablecoin, in 2023 marked a significant expansion of its ecosystem. GHO is designed to be overcollateralized, minted against a diverse basket of crypto assets supplied by users to the Aave Protocol, and aims to maintain a soft peg to the U.S. dollar. Staked GHO (sGHO) represents GHO tokens that have been staked within the Aave Safety Module, contributing to the protocol’s security and earning staking rewards.

For a stablecoin like GHO, particularly its staked variant sGHO, cross-chain availability is not merely a convenience but a strategic necessity for broader adoption and utility. As DeFi activity proliferates across an increasingly fragmented multi-chain landscape, stablecoins must be able to move seamlessly and securely between different Layer 1 and Layer 2 networks to serve their purpose effectively. This includes enabling liquidity provision, facilitating decentralized exchange trading, supporting lending and borrowing on various instances of Aave, and ensuring consistent accounting and risk controls across disparate environments. The decision to make sGHO cross-chain is thus integral to enhancing GHO’s reach and competitiveness in a market dominated by established players like USDC, USDT, and DAI.

The Perilous History of Cross-Chain Bridges and the Need for Enhanced Security

The DeFi industry has, unfortunately, accumulated a costly history lesson regarding the vulnerabilities inherent in cross-chain bridges. These bridges, designed to connect isolated blockchain networks, often serve as critical conduits for value and information transfer. However, their architectural complexity, diverse consensus mechanisms, and often centralized points of failure have made them prime targets for sophisticated exploits. Data from various blockchain security firms and industry reports consistently highlight bridges as one of the most susceptible components of the DeFi stack.

According to reports from companies like Chainalysis and Immunefi, billions of dollars have been lost in bridge exploits over the past few years. Notable incidents include the Ronin Bridge hack in March 2022, which saw over $600 million stolen; the Wormhole Bridge exploit in February 2022, resulting in a loss of over $320 million; and the Nomad Bridge hack in August 2022, which drained nearly $190 million. These incidents underscore a fundamental challenge: bridges often operate at the intersection of different security models and trust assumptions, creating complex attack surfaces. When an exploit occurs, the consequences are typically severe and rapid, leading to massive financial losses and eroding user trust in the affected protocols and the broader multi-chain vision.

For a protocol of Aave’s stature, with significant TVL and a reputation built on robust security and reliability, the choice of cross-chain infrastructure is far from a minor technical detail. It directly impacts user trust, the integrity of its stablecoin, the efficacy of its governance across chains, and its overall capacity for secure expansion. The Aave governance’s move to designate Chainlink CCIP as the default for sGHO reflects a deep understanding of these risks and a proactive stance to mitigate them.

Chainlink CCIP: A Security-First Approach to Interoperability

Chainlink’s Cross-Chain Interoperability Protocol (CCIP) has been explicitly engineered to address the critical security gaps that have plagued previous cross-chain solutions. It is positioned not just as another bridge, but as a comprehensive, security-first standard for secure cross-chain messaging and token transfers. At its core, CCIP leverages Chainlink’s decentralized oracle network (DON) infrastructure, which has a proven track record of securely delivering billions of dollars in value across various blockchains.

Key architectural features that underpin CCIP’s security claims include:

  1. Decentralized Oracle Networks (DONs): CCIP utilizes multiple independent and geographically diverse Chainlink DONs to monitor and validate cross-chain transactions. This decentralization minimizes single points of failure, making it significantly harder for an attacker to compromise the entire system.
  2. Active Risk Management (ARM) Network: This innovative feature acts as an additional layer of security. The ARM network is a separate, independent network of oracle nodes that continuously monitors CCIP transactions for suspicious activity. If the ARM network detects an anomaly, such as a transaction exceeding predefined rate limits or attempting to move an unusually large amount of funds, it can pause the flow of funds to prevent potential exploits. This circuit-breaker functionality provides a crucial safety net.
  3. Programmable Token Transfers: CCIP supports arbitrary message passing, allowing not just value but also complex data and instructions to be transferred securely between chains. This enables more sophisticated cross-chain applications and smart contract interactions.
  4. Rate Limiting: To mitigate the impact of potential exploits, CCIP incorporates configurable rate limits on token transfers, capping the amount of value that can be moved within a specific timeframe. This helps to contain losses in the event of a breach.

Chainlink has consistently articulated that major DeFi protocols require more than just basic connectivity; they need a robust, audited, and battle-tested solution capable of supporting large-scale cross-chain communication without relying on fragile, centralized routes. Aave’s governance proposal explicitly aligns with this philosophy, seeking a standard that can facilitate cross-chain expansion while substantially reducing operational risk.

The Governance Decision: ARFC and Multi-Bridge Redundancy

The Aave governance process, known for its decentralized and deliberative nature, involved a series of steps culminating in the decision to adopt CCIP. The process typically begins with an Aave Request for Comment (ARFC) on the governance forum, allowing the community to discuss and refine proposals. This particular ARFC, titled "ARFC: Launch sGHO Cross-Chain," detailed the rationale for moving sGHO across chains and specifically nominated Chainlink CCIP as the default mechanism. Following community discussion, a Snapshot vote often gauges sentiment before an on-chain vote is initiated. The successful passage of this proposal reflects broad community consensus on the importance of secure cross-chain infrastructure.

It is crucial to note the nuance in Aave’s decision. While CCIP is designated as the default standard for sGHO transfers, the broader Aave Delivery Infrastructure (a.DI) retains a multi-bridge architecture for redundancy. This means that CCIP is not the only infrastructure in Aave’s overall cross-chain strategy, and alternative bridges are not being simply deactivated. This approach highlights a sophisticated understanding of risk management in complex DeFi systems. A default route provides consistency, operational efficiency, and a high baseline of security, while the retention of a multi-bridge design ensures that Aave avoids single points of failure and maintains flexibility should issues arise with any single provider. This layered security approach is a hallmark of mature infrastructure planning.

Implications for GHO Distribution and Aave’s Ecosystem

The adoption of CCIP for sGHO carries significant implications for the GHO stablecoin and the wider Aave ecosystem. GHO’s success, like any stablecoin, hinges on its ability to achieve widespread distribution, deep liquidity, seamless integrations, and consistent demand across various use cases. Making sGHO easier and safer to move across networks is a direct pathway to expanding its utility and adoption.

By leveraging CCIP, Aave can enable users and other protocols to transfer sGHO more confidently and securely between different blockchain environments. This fosters broader GHO adoption without forcing activity to remain concentrated on a single chain, thereby improving liquidity, increasing trading opportunities, and potentially driving demand for GHO across the DeFi landscape. For instance, sGHO could be used more effectively on Layer 2 networks for faster, cheaper transactions, or integrated into new DeFi protocols deployed on emerging chains.

However, the stablecoin market remains intensely competitive. Established giants like Tether’s USDT and Circle’s USDC command hundreds of billions in market capitalization and enjoy pervasive liquidity and integration. Decentralized stablecoins like MakerDAO’s DAI also possess a significant first-mover advantage and robust ecosystems. GHO, despite its innovative design and backing by Aave, must continually build clear advantages to gain market share. While cross-chain accessibility via a secure solution like CCIP is a vital component of this strategy, Aave must also continue to foster demand for GHO itself through integrations, partnerships, and novel use cases. The CCIP integration provides a strong foundation, but it is one piece of a larger puzzle.

DeFi’s Maturation: An Infrastructure-Led Future

Aave’s decision is highly indicative of the broader trajectory of the DeFi industry. The early phases of DeFi growth were often characterized by rapid innovation, yield farming incentives, and a focus on speculative opportunities. While these elements remain, the industry is increasingly moving towards a more infrastructure-heavy and security-conscious phase. This maturation is driven by the realization that for DeFi to truly scale and support larger amounts of institutional and retail capital, it requires more formal risk controls, superior governance execution, deeper and more secure inter-network integrations, and robust, battle-tested infrastructure.

This "infrastructure-led" future may not generate the same speculative fervor as meme tokens or new yield strategies, but it represents the foundational work necessary for DeFi to become a truly resilient and reliable financial system. Protocols are becoming more selective about the underlying technologies they integrate, understanding that security failures can have catastrophic consequences. The trend points towards a more professionalized and institutional-grade ecosystem where reliability and trust are paramount.

For Chainlink, Aave’s endorsement strengthens CCIP’s position as a leading cross-chain interoperability solution and validates its security-first design philosophy. It adds a major blue-chip DeFi protocol to its growing list of adopters, reinforcing its role as a core infrastructure provider for the Web3 economy. For Aave, it provides sGHO with a clearer, more secure path for multi-chain expansion, enhancing its utility and competitive standing. For DeFi users, this shift ultimately promises a smoother, more secure experience when moving assets and interacting with protocols across different blockchain networks, minimizing the risks associated with cross-chain transfers.

While this decision does not instantly resolve every challenge associated with cross-chain communication, it signifies a crucial pivot. Leading protocols are no longer content with basic connectivity; they are actively investing in and adopting infrastructure that can withstand the rigors of a high-value, multi-chain environment. This increased selectivity in infrastructure choices is a testament to DeFi’s journey towards a more secure, sustainable, and mature future.

July 20, 2026 0 comment
0 FacebookTwitterPinterestEmail
Blockchain Technology

UK Grapples with "Fraud Epidemic" as Independent Review Urges Judicial Training for Digital Asset and AI Crimes

by admin July 20, 2026
written by admin

A major independent review of fraud in the United Kingdom has warned that it has “grown exponentially in the last 20 years” and recommended that judges and magistrates be trained to handle increasing cases involving digital assets and artificial intelligence (AI). The Independent Review of Disclosure and Fraud Offences, established in October 2023, recently published its second comprehensive report, "Fraud in the Digital Age," painting a stark picture of a nation besieged by a rapidly evolving criminal landscape. The report highlights how emerging technologies, particularly AI, deepfakes, and crypto-assets, are not merely contributing to a "fraud epidemic" but are actively "equipping criminals to deceive at scale and to launder proceeds with unprecedented ease, frequently from overseas." This alarming assessment underscores a critical challenge for the UK’s legal and enforcement systems, necessitating a profound shift in approach to combat sophisticated digital criminality.

The Independent Review, chaired by the eminent Jonathan Fisher KC, was specifically commissioned to confront the complexities of investigating and prosecuting fraud cases in an increasingly digitalized world. Its initial report, "Disclosure in the Digital Age," published in March, addressed the procedural hurdles in handling vast quantities of digital evidence. The subsequent report, "Fraud in the Digital Age," delves deeper into the substantive barriers impeding effective investigation and prosecution, particularly those perpetrated against businesses and individuals using novel technologies. It asserts that contemporary fraud cases have moved far beyond simple acts of deception, now routinely involving multiple layers of technical and evidential complexity, directly driven by the widespread adoption of AI, intricate cross-border fund transfers, and the burgeoning use of cryptocurrency. Among its 47 wide-ranging recommendations, the call for bespoke training for judges on emerging technology-related fraud stands out as a crucial step towards equipping the judiciary to dispense justice in this new era of crime.

The Alarming Scale and Economic Impact of Digital Fraud

The report lays bare the staggering economic and societal toll of fraud in the UK. Annual losses from fraud are conservatively estimated at a colossal £2.3 billion ($3.11 billion USD), making it the single largest category of criminal activity, accounting for a staggering 44% of all reported crimes. Within this disturbing figure, an overwhelming 80% is attributed to digital and internet-facilitated fraud, highlighting the pervasive nature of online deception. With an estimated 4.1 million offenses recorded in the year leading up to June 2025 alone, the report ominously predicts that fraud may soon constitute half of all crime in England and Wales. This exponential growth represents not just a financial drain but a significant erosion of public trust and security.

Jonathan Fisher KC, in his foreword to the report, did not mince words, declaring, "It is no exaggeration to describe fraud as the criminal scourge of our age." He emphasized that fraud is fundamentally "a crime against possession, which infringes autonomy by undermining the right to enjoy property." The systemic consequence of this widespread criminality, he argued, is the denial of "the expectation of trust and security between people which allows a market economy to flourish." This philosophical underpinning highlights that the fight against fraud is not merely about financial recovery but about preserving the very fabric of societal and economic interactions. The sheer volume and sophistication of these crimes are overwhelming traditional law enforcement and judicial mechanisms, making a comprehensive and innovative response imperative.

The Dual Challenge: AI and Cryptocurrencies

A primary driver for the alarming rise in fraud cases, according to the review, is the parallel ascent of AI and cryptocurrencies. These technologies, while offering immense potential for innovation and efficiency, have concurrently "further complicated the landscape, enabling new forms of deception and challenging traditional enforcement models." The report details how criminals are leveraging these advancements to amplify their illicit activities.

  • Artificial Intelligence (AI): AI’s role extends to creating highly convincing deepfakes—synthetic media that can manipulate images, audio, and video—which are increasingly used in sophisticated scams, identity theft, and corporate espionage. AI algorithms can also be employed to automate phishing campaigns, personalize scam messages to increase their effectiveness, and analyze vast datasets to identify potential victims or vulnerabilities. The ability of AI to generate realistic fraudulent content at scale makes detection significantly harder for both individuals and automated security systems.
  • Cryptocurrencies: The report specifically highlights the critical role of digital assets in facilitating fraud and money laundering. A Financial Ombudsman Service report from July 2025 indicated that over half of all investment scams in the UK now involve crypto-assets. Globally, blockchain analysis firm Chainalysis reported in January that a record $17 billion was estimated to have been stolen through digital asset scams and fraud in 2025.
    The appeal of cryptocurrencies for fraudsters lies in their inherent characteristics: "These decentralized assets bypass traditional banking systems and offer anonymity, making them attractive for fraud and money laundering." Assets like Bitcoin, Ethereum, and other digital tokens enable "fast, cross-border value transfer without traditional financial intermediaries," providing "pseudo-anonymity and agility" that are ideal for laundering illicit proceeds. This presents a formidable challenge for investigators. Tracing funds often requires complex blockchain analysis to identify suspicious wallets and follow transaction flows. The task is further complicated by obfuscation tools such as "tumblers" or "mixers," which pool and redistribute coins across numerous addresses, rendering forensic tracing exceptionally difficult, if not impossible, for many law enforcement agencies.

Judicial Preparedness: A Critical Gap and Proposed Solutions

A central tenet of the review’s recommendations is the urgent need to enhance the technological literacy and specialized training of the judiciary. The report candidly states that UK magistrates and non-specialist Crown Court centers will increasingly encounter cases of a "nature and scale" they have not previously dealt with, involving technologies with which they are "relatively unfamiliar and inexperienced." This gap in expertise poses a significant threat to the fair and effective administration of justice in digital fraud cases.

The review explicitly argues that "in light of the volume of fraud cases, it would be valuable for the wider judiciary to have a greater awareness of how to manage cases involving AI-enabled fraud and cryptocurrency-based money laundering." To address this critical shortcoming, it recommends that the Judicial College, the body responsible for training judges in the UK, undertake a thorough review. This review would ascertain whether current and future judges are "adequately equipped, or willing to develop expertise, in managing complex economic crime."

Specific measures proposed include:

  1. Expanding Existing Courses: The Judicial College should consider expanding the scope of its existing training programs to incorporate detailed modules on AI-enabled fraud and cryptocurrency-based money laundering.
  2. Dedicated Programs: Alternatively, the introduction of a dedicated, bespoke program specifically focused on fraud and related offenses in the digital age is recommended. This would ensure comprehensive coverage of the unique technical and legal challenges.
  3. Preparing All Judges: The review emphasizes the need to prepare all judges, including magistrates, for the likely increase in hearing cases related to AI-enabled fraud and crypto-asset laundering. This acknowledges that digital fraud is no longer a niche area but a pervasive challenge.
  4. Mandatory Training: Crucially, the report suggests that "consideration should also be given to mandating such training for judges likely to preside over complex fraud cases." Making this training a requirement would ensure a baseline level of competence and understanding across the judiciary, particularly for those handling the most intricate economic crimes.

Fisher KC reiterated the importance of this judicial empowerment, stating that "effective criminal prosecution lies at the heart of the response to those who commit fraud." Without a judiciary capable of understanding and navigating the intricacies of digital evidence, blockchain analysis, and AI forensics, even the most robust investigations and prosecutions risk faltering.

Broader Recommendations for a Comprehensive Digital Defense

The judicial training recommendation is but one of 47 measures put forth by the Independent Review, forming a holistic strategy to counter the digital fraud epidemic. These recommendations span legislative, enforcement, public awareness, and international cooperation domains:

  • Legislative and Enforcement Powers:
    • Civil Fines: Granting law enforcement the power to issue civil fines to individuals purchasing fraud-enabling products online, thereby targeting the supply chain of fraudulent tools.
    • Anti-Fraud Levy: Implementing an anti-fraud levy on digital and communications infrastructure providers, recognizing their role in facilitating digital interactions and potentially contributing to the ecosystem where fraud thrives. The revenue generated could fund anti-fraud initiatives.
    • Sanctioning Foreign Nationals: Strengthening powers to sanction foreign nationals orchestrating fraud, acknowledging the significant cross-border nature of much digital crime. This could involve asset freezes and travel bans.
  • Public Awareness and Education: Launching extensive public awareness campaigns to educate individuals and businesses about common fraud tactics, the risks associated with digital assets, and how to protect themselves online. This proactive approach aims to reduce victim vulnerability.
  • Intelligence Sharing and Coordination:
    • Public-Private Partnerships: Enhancing intelligence sharing mechanisms within public-private partnerships, allowing financial institutions, tech companies, and law enforcement to collaboratively identify and disrupt fraud networks.
    • Cross-Government Fraud Lead: Appointing a cross-Government fraud lead, or "Fraud Czar," to drive strategic coordination and accountability across various government departments and agencies involved in the UK’s response to fraud. This would ensure a unified and coherent national strategy.
  • International Cooperation: Strengthening international collaboration with law enforcement agencies and regulatory bodies in other jurisdictions to tackle cross-border digital asset fraud and money laundering effectively. This includes sharing intelligence, coordinating investigations, and harmonizing legal frameworks.

Strategic Implications and the Path Forward

The Independent Review’s "Fraud in the Digital Age" report represents a seminal moment in the UK’s fight against economic crime. Its comprehensive analysis and wide-ranging recommendations acknowledge that traditional methods are no longer sufficient to combat the scale and sophistication of modern fraud. The report implicitly calls for a multi-faceted, adaptive, and technologically informed response across all sectors.

Implementing these recommendations will present significant challenges, requiring substantial investment in training, technology, and inter-agency cooperation. The proposed "Fraud Czar" role highlights the need for strong central leadership to overcome bureaucratic hurdles and ensure coordinated action. Furthermore, the legal and ethical implications of some proposals, such as civil fines for purchasing fraud-enabling products, will require careful consideration and public debate.

However, the urgency of the situation cannot be overstated. As Fisher KC concluded, "The measures put forward in this Review should shift the dial, to ensure that the time when there has been little to deter fraudsters is over. This is not only a matter of maintaining law and order; it is a duty to secure justice for the more than four million adults who fall victim to fraud each year." The report serves as a clarion call for the UK to refresh its "anti-fraud armory" and introduce "new measures appropriate to fighting fraud in a digital age," ultimately aiming to restore trust, secure property rights, and protect its citizens from the relentless onslaught of digital deception.

Beyond the immediate policy recommendations, the report also implicitly points towards the need for advanced technological solutions to combat fraud. For artificial intelligence to operate effectively and ethically within legal frameworks, and to thrive amidst escalating challenges, it will necessitate the integration of robust enterprise blockchain systems. Such systems are crucial for ensuring the quality, immutability, and undisputed ownership of data inputs, thereby bolstering data security and integrity. This foundational technological layer can play a pivotal role in creating a trustworthy environment for AI development and deployment, which in turn could aid in fraud detection and prevention by providing verifiable data trails and secure digital identities. As AI continues to evolve, understanding why enterprise blockchain will be the backbone of its secure and compliant operation becomes increasingly vital in the collective effort to safeguard against sophisticated digital threats.

The video below, "Inside Philippine Blockchain Week 2026 | Driving the Future of Blockchain, AI & Web3," offers a glimpse into global efforts and discussions surrounding the integration of these cutting-edge technologies, illustrating the broader context of innovation and the ongoing challenges in harnessing their potential responsibly while mitigating risks.

July 20, 2026 0 comment
0 FacebookTwitterPinterestEmail
Blockchain Technology

CryptoPunks Defy Downturn Speculation with Million-Dollar Sales Streak Amidst Shifting NFT Market Dynamics

by admin July 20, 2026
written by admin

CryptoPunks, the pioneering non-fungible token (NFT) collection, demonstrated remarkable resilience this week, securing its third consecutive day atop CryptoSlam’s daily sales chart. On Wednesday, the iconic digital collectibles registered a robust US$1.29 million in sales, a performance that comes amidst intense community speculation regarding a potential decline in their intrinsic and market value. This streak underscores the enduring appeal of blue-chip NFTs, even as the broader digital asset market navigates a period of significant recalibration and volatility.

The recent flurry of activity surrounding CryptoPunks has been particularly scrutinized following high-profile transactions that fueled narratives of a market downturn. Central to this discussion was the recent sale announced by investor Deepak Thapliyal, involving Punk #5822. This particular NFT, a rare ‘Alien’ CryptoPunk, once commanded a staggering valuation of US$24 million, making it one of the most expensive digital assets ever sold at its peak. Thapliyal’s decision to offload Punk #5822 for an undisclosed sum quickly ignited a firestorm of speculation within the NFT community. While the exact figure remains confidential, market participants widely believe the sale concluded at a significant loss, with estimates circulating around 5,000 Ether (approximately US$12.8 million at the time of the transaction). This perceived markdown sent ripples through the ecosystem, prompting questions about the long-term sustainability and valuation methodologies of high-value NFTs.

A Closer Look at Wednesday’s Performance

Despite the surrounding skepticism, Wednesday’s data painted a picture of sustained demand for CryptoPunks. The US$1.29 million in sales was distributed across 15 distinct transactions, indicating active trading rather than a single large purchase artificially inflating the figures. These transactions involved a healthy mix of market participants, with 11 unique buyers acquiring Punks from 13 different sellers. This diversity suggests a dynamic marketplace with both new entrants and existing holders engaging in trade. The average sale price for a CryptoPunk on Wednesday stood at US$86,582, a figure that, while fluctuating, remains indicative of the collection’s premium status within the NFT hierarchy. This average price reflects a blend of sales across various rarity tiers, from common Punks to those possessing rarer attributes, demonstrating a broad market interest.

This latest performance contributed significantly to CryptoPunks’ already formidable legacy, pushing its all-time sales volume to an impressive US$2.87 billion. This monumental figure firmly establishes CryptoPunks as the third-highest-ranking NFT collection by sales volume across the entire market, a testament to its pioneering status and enduring cultural impact. Only a handful of collections have managed to breach the multi-billion-dollar mark, solidifying CryptoPunks’ position as a cornerstone of digital art and collectibles.

The Genesis and Evolution of CryptoPunks: A Chronology of Digital Scarcity

To fully appreciate the current market dynamics, it is crucial to understand the historical context of CryptoPunks. Launched in June 2017 by Larva Labs, a two-person development team comprising Matt Hall and John Watkinson, CryptoPunks predated the mainstream NFT boom by several years. The collection consists of 10,000 unique, algorithmically generated 24×24 pixel art images, each with distinct features and attributes. Initially, these digital avatars were offered for free to anyone with an Ethereum wallet, a move that, in retrospect, appears incredibly prescient.

  • June 2017: CryptoPunks are launched by Larva Labs. 9,000 Punks are claimed for free, while Larva Labs retains 1,000 for themselves.
  • 2018-2020: The collection slowly gains traction within early crypto circles, with a nascent secondary market forming. Prices remain relatively low, often in the hundreds or low thousands of dollars.
  • 2021: The NFT Bull Run: CryptoPunks explode into mainstream consciousness during the global NFT frenzy. Prices skyrocket, driven by celebrity endorsements, institutional interest, and a surge in cryptocurrency valuations. Rare Punks begin selling for millions of dollars.
  • March 2021: Punk #3100 and #7804 (both Alien Punks) sell for 4,200 ETH each, then equivalent to US$7.58 million.
  • June 2021: Sotheby’s auctions "Covid Alien" Punk #7523 for US$11.75 million, solidifying Punks’ status as fine art.
  • February 2022: Deepak Thapliyal acquires Punk #5822 (an Alien Punk) for 8,000 ETH, valued at US$23.7 million at the time, marking the highest-ever sale of a CryptoPunk to a single buyer.
  • March 2022: Yuga Labs, the creators of the Bored Ape Yacht Club (BAYC), acquire the intellectual property rights to CryptoPunks and Meebits from Larva Labs, a landmark deal that reshaped the NFT landscape. This acquisition was met with mixed reactions but promised further development and utility for the Punks ecosystem.
  • Late 2022-Present: The broader NFT market enters a significant cooling-off period, often referred to as an "NFT winter." Trading volumes and floor prices for many collections decline. Amidst this backdrop, speculation about the long-term value of blue-chip NFTs intensifies.
  • Recent Weeks: The sale of Punk #5822 by Deepak Thapliyal for an estimated US$12.8 million (5,000 ETH), a significant reduction from its peak valuation, fuels concerns about asset depreciation, even as CryptoPunks log impressive daily sales.

The acquisition by Yuga Labs was a pivotal moment. It brought the Punks under the umbrella of a company known for its aggressive ecosystem expansion and community-driven initiatives, promising potential new utility and integration into the broader Yugaverse. However, it also introduced questions about the original ethos of the Punks and the future direction of the collection.

The Broader NFT Market Landscape: A Comparative View

While CryptoPunks commanded the top spot on Wednesday, the rest of the NFT market also showed diverse activity, highlighting different segments and investor interests.

  • Bored Ape Yacht Club (BAYC): Securing the second position, the Bored Ape Yacht Club recorded US$861,724.21 across 26 transactions. BAYC, another cornerstone of the blue-chip NFT space and now a sister collection to CryptoPunks under Yuga Labs, continues to demonstrate strong demand. Its ecosystem, rich with intellectual property rights for holders, extensive partnerships, and ventures into gaming and entertainment, provides a different value proposition compared to the more ‘historical artifact’ status of CryptoPunks. The consistent performance of both Punks and Apes suggests a flight to quality within the NFT market, where established collections with strong brands and communities maintain investor confidence.

  • Mythos Chain’s DMarket: In third place, DMarket, operating on the Mythos Chain, showcased a distinct market segment. It generated US$738,879 in sales but achieved this through a massive 25,578 transactions. This stark contrast to Punks and Apes, which have higher average sale prices, indicates DMarket’s focus on in-game assets and digital collectibles with lower individual price points but significantly higher trading frequency. This segment caters to a different demographic, often gamers and collectors seeking utility-driven assets rather than pure speculative art.

  • Pudgy Penguins: Coming in fourth with US$587,545 in sales, Pudgy Penguins have seen a remarkable resurgence in recent times. After initial struggles and a change in leadership, the collection has revitalized its brand through strong community engagement, licensing deals, and a focus on tangible products, demonstrating how effective leadership and strategic vision can breathe new life into an NFT project.

  • Guild of Guardians Heroes and Mutant Ape Yacht Club (MAYC): These collections followed closely, generating US$464,522 and US$433,094 in sales, respectively. Guild of Guardians, a mobile RPG, highlights the growing integration of NFTs into the gaming sector, offering in-game assets and play-to-earn mechanics. Mutant Ape Yacht Club, an offshoot of BAYC, continues to leverage the brand equity of its parent collection, offering a more accessible entry point into the Apes ecosystem while retaining significant value.

The diversity in these top-performing collections underscores the multifaceted nature of the NFT market. While high-value "blue-chip" art NFTs like CryptoPunks and BAYC continue to attract significant capital, utility-driven gaming NFTs and community-focused projects like Pudgy Penguins also carve out substantial market shares, catering to varied investor motivations and use cases.

Ethereum’s Unyielding Dominance in the NFT Realm

Underpinning much of this activity is the Ethereum blockchain, which continues its reign as the undisputed leader for NFT transactions. On Wednesday, Ethereum alone accounted for a staggering US$6.46 million in sales, far surpassing other blockchain networks. This dominance is not new; Ethereum has been the preferred network for high-value NFTs since their inception, largely due to its robust security, established developer ecosystem, and widespread adoption among crypto users and platforms.

While alternative blockchains like Solana, Polygon, and Immutable X have emerged with promises of lower transaction fees and higher scalability, Ethereum’s network effect remains unparalleled for premium digital assets. The recent shift to Ethereum 2.0 (The Merge), transitioning from proof-of-work to proof-of-stake, has also enhanced its energy efficiency, addressing a common criticism leveled against early blockchain technologies. Despite occasional concerns about network congestion and gas fees, the perceived security and liquidity of the Ethereum ecosystem continue to draw the largest share of NFT capital.

Analysis of Implications: Resilience, Revaluation, and Market Maturity

The CryptoPunks’ recent sales streak, juxtaposed with the high-profile loss-taking sale of Punk #5822, offers several critical insights into the evolving NFT market:

  1. Resilience of Blue-Chip Assets: The consistent daily sales volume for CryptoPunks suggests that top-tier, historically significant NFT collections retain substantial market interest and liquidity, even during broader market corrections. This indicates a "flight to quality" where investors may be divesting from speculative, lower-tier projects and consolidating their holdings in established assets.

  2. Market Revaluation and Price Discovery: The sale of Punk #5822, while indicative of a significant individual loss, can also be viewed as part of a larger market revaluation process. The euphoric valuations of the 2021 bull run were, in many cases, unsustainable. Current market conditions are forcing a more sober assessment of asset values, moving away from pure hype towards more fundamental considerations like historical significance, brand equity, and potential utility (as facilitated by Yuga Labs’ acquisition). This revaluation is a natural, albeit painful, part of market maturation.

  3. Shifting Investor Psychology: The speculation surrounding the #5822 sale highlights the acute sensitivity of the NFT community to whale movements. Large sales, especially those perceived as being at a loss, can trigger FUD (fear, uncertainty, and doubt) and impact overall market sentiment. Conversely, a sustained sales streak like CryptoPunks’ can inject confidence, suggesting that there are still active buyers willing to pay significant sums for these digital artifacts.

  4. The Role of Scarcity and Heritage: CryptoPunks’ continued appeal is deeply rooted in its status as a historical artifact in the digital realm. As one of the first NFT collections, its scarcity (fixed supply of 10,000) and pioneering role in defining the PFP (profile picture) genre contribute to its enduring value proposition. This "digital heritage" factor provides a strong narrative moat against newer, less established collections.

  5. Future Outlook: Utility vs. Collectibility: While CryptoPunks are primarily valued for their collectibility and historical significance, the Yuga Labs acquisition has introduced the potential for future utility within the broader Yugaverse. The balance between maintaining their status as standalone collectibles and integrating them into a larger ecosystem will be crucial for their long-term trajectory. For the overall NFT market, the trend suggests a growing demand for projects that offer not just art, but also community, utility, and intellectual property rights.

In conclusion, CryptoPunks’ recent performance serves as a microcosm of the dynamic and often paradoxical NFT market. It demonstrates that while speculative bubbles may burst and individual investors may incur losses during market corrections, the underlying value of pioneering and culturally significant digital assets can prove remarkably resilient. The streak underscores a market in flux, undergoing a necessary revaluation, but one where the foundations laid by early innovators like CryptoPunks continue to command substantial attention and capital. The ongoing narrative of digital scarcity, community engagement, and evolving utility will undoubtedly continue to shape the future of this nascent but rapidly maturing asset class.

July 20, 2026 0 comment
0 FacebookTwitterPinterestEmail
Blockchain Technology

Sam Bankman-Fried Seeks Presidential Pardon from Donald Trump Amidst 25-Year Prison Sentence

by admin July 20, 2026
written by admin

Sam Bankman-Fried, the disgraced co-founder of the now-defunct cryptocurrency exchange FTX, has formally submitted an application for a presidential pardon to President Donald Trump. This significant development, confirmed by the Justice Department’s Pardon Attorney Office website, comes as Bankman-Fried serves a substantial 25-year prison sentence following his conviction on a myriad of fraud and money laundering charges in 2024. The initial report regarding this application was first published by Bloomberg News, bringing into sharp focus the convicted crypto mogul’s latest attempt to navigate his legal predicament.

The filing of a pardon application by Bankman-Fried, a figure who once commanded immense influence in the digital asset space, introduces a complex layer to the ongoing public and legal discourse surrounding his spectacular downfall. It also places his fate, however distant, within the purview of a former president known for his unconventional approach to executive clemency, particularly in cases involving financial crimes and political affiliations.

The Meteoric Rise and Catastrophic Collapse of FTX

To fully comprehend the gravity of Bankman-Fried’s current situation and his bid for clemency, it is essential to revisit the dramatic trajectory of FTX and its charismatic founder. Sam Bankman-Fried, often referred to by his initials SBF, emerged as a prominent figure in the cryptocurrency world in the late 2010s. A graduate of MIT, he founded Alameda Research, a quantitative trading firm, in 2017, quickly establishing a reputation for high-volume trading and arbitrage. Building on this success, he co-founded FTX in 2019, positioning it as a user-friendly and sophisticated cryptocurrency exchange.

FTX rapidly ascended to become one of the largest and most influential crypto platforms globally, attracting millions of users and billions in assets under management. Its valuation soared, reaching an astonishing $32 billion at its peak in early 2022. SBF became a ubiquitous presence in media, a major political donor, and an advocate for crypto regulation, often testifying before Congress. He cultivated an image as a benevolent leader, committed to "effective altruism" and ethical conduct within the volatile crypto industry.

However, this carefully constructed edifice began to crumble in November 2022. A report by CoinDesk revealed a concerning link between FTX and Alameda Research, specifically that Alameda’s balance sheet heavily relied on FTT, the native token of the FTX exchange. This exposure raised red flags about the interconnectedness and potential instability of SBF’s empire. The situation escalated rapidly when Changpeng Zhao, the CEO of rival exchange Binance, announced his intention to liquidate Binance’s holdings of FTT, triggering a massive sell-off and a crisis of confidence.

A deluge of customer withdrawal requests overwhelmed FTX, exposing a critical liquidity shortfall. Within days, FTX, once a titan of the crypto industry, found itself on the brink of collapse. On November 11, 2022, FTX, Alameda Research, and over 100 affiliated companies filed for Chapter 11 bankruptcy in the United States. The subsequent investigations uncovered a staggering misappropriation of customer funds, estimated to be in the billions of dollars, which were allegedly diverted to cover losses at Alameda Research, make risky investments, and fund lavish lifestyles and political donations.

The Legal Saga and Conviction of Sam Bankman-Fried

The implosion of FTX triggered immediate legal and regulatory scrutiny. On December 12, 2022, Sam Bankman-Fried was arrested in the Bahamas, where FTX was headquartered, at the request of the U.S. government. He was subsequently extradited to the United States to face a barrage of federal charges.

The prosecution, led by the U.S. Attorney for the Southern District of New York, painted a picture of calculated deception and large-scale fraud. Bankman-Fried was accused of orchestrating a multi-year scheme to defraud customers and investors of FTX, diverting billions of dollars in customer deposits to Alameda Research for its own use. The charges included wire fraud, conspiracy to commit wire fraud, conspiracy to commit money laundering, and conspiracy to commit securities fraud, among others. Crucially, the prosecution argued that SBF knew his actions were illegal and intentionally misled investors and customers.

During the high-profile trial in late 2023, prosecutors presented compelling evidence, including testimony from former FTX and Alameda executives, such as Caroline Ellison (Alameda CEO) and Gary Wang (FTX co-founder), who had pleaded guilty and cooperated with the government. These witnesses detailed how customer funds were commingled and used without consent, how a secret backdoor allowed Alameda to access FTX customer funds, and how Bankman-Fried directed these illicit activities.

Bankman-Fried’s defense team, while acknowledging poor risk management and oversight at FTX, argued that he never intended to defraud anyone and was merely overwhelmed by the rapid growth and complexity of his businesses. They attempted to portray him as a well-intentioned but ultimately naive entrepreneur who made mistakes. However, the jury was unconvinced. On November 2, 2023, after less than five hours of deliberation, Sam Bankman-Fried was found guilty on all seven counts of fraud and conspiracy brought against him.

The Sentencing: A Landmark Decision

Following his conviction, the focus shifted to sentencing. On March 28, 2024, U.S. District Judge Lewis Kaplan handed down a 25-year prison sentence to Sam Bankman-Fried. The sentence, while less than the 40-50 years sought by prosecutors, was significantly more than the 6.5 years proposed by his defense team. Judge Kaplan emphasized the immense scale of the fraud, the betrayal of trust, and the devastating impact on victims. He stated that Bankman-Fried’s actions constituted a deliberate and knowing scheme to defraud, rejecting the defense’s characterization of his conduct as merely negligent.

Judge Kaplan highlighted several factors contributing to the severe sentence:

  • Magnitude of Loss: Billions of dollars were stolen from customers, investors, and lenders.
  • Perjury: The judge noted Bankman-Fried’s evasive and untruthful testimony during the trial.
  • Lack of Remorse: Kaplan observed Bankman-Fried’s apparent lack of genuine remorse for the harm he caused.
  • Deterrence: The sentence was intended to send a strong message to others who might consider engaging in similar financial crimes.

The 25-year sentence cemented Bankman-Fried’s transformation from a crypto visionary to one of the most prominent white-collar criminals in recent memory, marking a definitive end to his reign in the digital asset world.

Presidential Pardons: A Historical Context with Donald Trump

The application for a pardon from President Trump is particularly noteworthy given the former president’s distinctive record on executive clemency. During his single term in office, Donald Trump granted pardons and commutations to hundreds of individuals, often drawing controversy and scrutiny.

An analysis by NBC News in January found that more than half of the individual pardons granted by Trump were for people who committed white-collar crimes, including money laundering, bank fraud, and wire fraud – precisely the types of offenses for which Bankman-Fried was convicted. This pattern included high-profile figures such as Steve Bannon, Roger Stone, and Michael Flynn, as well as a significant number of individuals who had made substantial political donations to his campaigns or had personal connections to his administration.

It is crucial to note that many of these pardons bypassed the traditional review process of the Justice Department’s Pardon Attorney Office, instead being granted directly by the President, often in the final days of his term. The fact that Bankman-Fried has filed an official application through the Justice Department suggests an attempt to follow established protocol, a path less frequently chosen by those who ultimately received Trump’s clemency. While Trump also issued numerous pardons to individuals involved in the January 6, 2021 Capitol riot, his affinity for pardoning financial criminals remains a defining characteristic of his clemency record.

The Mechanics of a Presidential Pardon Application

The process for a presidential pardon involves several stages, though the President ultimately retains sole discretionary power. When an application is filed with the Justice Department’s Pardon Attorney Office, it typically triggers a thorough investigation. This investigation includes reviewing the applicant’s criminal record, the circumstances of the conviction, their conduct since conviction, and often soliciting input from prosecutors, judges, and victims.

The Pardon Attorney then makes a recommendation to the Deputy Attorney General, who in turn advises the President. However, presidents are not bound by these recommendations and can grant pardons or commutations at their own discretion, often without explanation. Pardons are generally granted for federal offenses and restore certain civil rights, such as the right to vote or hold public office, and remove legal disabilities resulting from the conviction. They do not, however, expunge a criminal record or prevent civil lawsuits.

For Bankman-Fried, the timing of his application is significant. With Trump currently a leading contender for the Republican presidential nomination in 2024, the application anticipates a potential return to the White House. Presidential pardons are typically granted towards the end of a president’s term, if at all, making Bankman-Fried’s application a long-term strategic move rather than an immediate solution.

Potential Implications and Reactions

The news of Bankman-Fried’s pardon application is likely to provoke a wide range of reactions across various segments of society:

  • Victims of FTX: For the countless individuals and institutions that lost billions in the FTX collapse, the idea of Bankman-Fried receiving a pardon would undoubtedly be met with outrage and a profound sense of injustice. They have spent over a year seeking restitution and accountability, and a pardon could be seen as an undermining of the judicial process.
  • Legal Experts: Legal scholars and former prosecutors will likely analyze the merits of the application, the political considerations, and the precedent it could set. The sheer scale of Bankman-Fried’s fraud and the deliberate nature of his actions, as determined by the jury and judge, make him an unlikely candidate for a pardon based on traditional criteria of remorse, rehabilitation, and minor offense severity.
  • Political Landscape: Should Trump win the presidency and consider such a pardon, it would undoubtedly become a significant political flashpoint. Bankman-Fried, through FTX and Alameda, was a prolific political donor, contributing tens of millions to both Democratic and Republican campaigns, often through "dark money" channels. While his most public donations favored Democrats, his extensive network and strategic giving could be a point of contention. A pardon for such a high-profile financial criminal could invite criticism from across the political spectrum, particularly given Trump’s own history of financial dealings and legal challenges.
  • Crypto Community: Reactions within the cryptocurrency world would likely be divided. Some might view it as an attempt by a powerful figure to escape accountability, further eroding trust in the industry. Others might see it as a reflection of the arbitrary nature of justice or a sign of the deep political connections that continue to influence high-stakes cases.
  • Broader Economic Implications: A pardon for Bankman-Fried would not negate the fundamental issues of regulatory oversight and investor protection highlighted by the FTX collapse. However, it could send a mixed message about the seriousness with which white-collar crime is treated at the highest levels of government.

Broader Significance and Future Outlook

Sam Bankman-Fried’s pardon application represents more than just a desperate plea from a convicted felon; it symbolizes a confluence of high-stakes finance, political power, and the complex mechanics of justice. It underscores the enduring influence of political figures in the legal system and raises fundamental questions about the criteria for executive clemency, especially in cases of profound public harm.

The likelihood of such a pardon being granted remains highly speculative. While Donald Trump has demonstrated a willingness to pardon individuals convicted of financial crimes, Bankman-Fried’s case is unique in its scale, its public notoriety, and the recency of his conviction and sentencing. Furthermore, a pardon would likely be perceived as politically risky, potentially alienating voters concerned about financial accountability.

Regardless of the outcome, Bankman-Fried’s application ensures that his name will continue to be associated with significant legal and political discussions, even as he serves his lengthy sentence. For the victims of FTX, the pursuit of justice and recovery remains paramount, with or without a presidential intervention in his criminal conviction. The process itself will serve as a stark reminder of the long shadow cast by the FTX scandal and the ongoing debate surrounding accountability in the rapidly evolving world of digital finance.

July 20, 2026 0 comment
0 FacebookTwitterPinterestEmail
Cybersecurity & Hacking

The Gentlemen Ransomware Group’s Alleged Administrator Identified as Russian National Alexander Andreevich Yapaev

by admin July 20, 2026
written by admin

A sophisticated cybercrime syndicate, notoriously dubbed "The Gentlemen," has rapidly ascended to become the second most prolific ransomware group globally by victim count. This meteoric rise is attributed to an aggressive recruitment strategy that offers affiliates an unprecedented 90 percent share of ransoms paid by victims, a significantly more lucrative incentive compared to the industry-standard 80/20 split. This detailed investigation examines the intricate web of digital clues and intelligence findings that point to the real-life identity of the individual believed to be the primary administrator of The Gentlemen ransomware group.

The Rise of "The Gentlemen": A New Threat Landscape

Emerging in mid-2025, The Gentlemen quickly established itself as a formidable force in the burgeoning "ransomware-as-a-service" (RaaS) ecosystem. RaaS models operate similarly to legitimate software-as-a-service businesses, where developers (the core group) create and maintain the ransomware tools and infrastructure, while affiliates (independent hackers) deploy the malware against targets. The core group then takes a cut of the successful ransom payments. In the competitive landscape of cybercrime, the 90/10 revenue split offered by The Gentlemen has proven to be a powerful magnet, attracting experienced and highly skilled operators away from rival programs.

Security experts at Check Point Software, who have been diligently tracking the group’s exploits, highlighted this aggressive recruitment as a key driver of The Gentlemen’s rapid expansion. By April 2026, Check Point’s research indicated that the group had already claimed at least 332 published victims since its inception, with over 240 of these occurring in 2026 alone, making them the second most active ransomware group by victim count for the year. This aggressive operational tempo underscores the severe and escalating threat posed by such highly organized cybercriminal enterprises.

The modus operandi of The Gentlemen typically involves targeting internet-facing devices such as Virtual Private Networks (VPNs) and firewalls as their initial point of entry. Once inside a victim’s network, the group moves with alarming speed, often encrypting entire networks within a matter of hours. This rapid execution minimizes the window for detection and response, leaving organizations scrambling to contain the damage and often facing immense pressure to pay the ransom.

Unmasking the Administrator: A Trail of Digital Breadcrumbs

The investigation into The Gentlemen’s operations, particularly following a breach of the group’s backend infrastructure, revealed critical insights into its leadership. Check Point Software identified the administrator and primary operator of the ransomware group as an individual using the nickname "Zeta88" on Russian-language cybercrime forums. Further analysis revealed that "Zeta88" had previously operated under the moniker "Hastalamuerte." The leaked backend data unequivocally showed that Hastalamuerte/Zeta88 was responsible for assembling the ransomware locker, managing the RaaS panel, handling payment distributions, and essentially overseeing the entire program, from which they received their 10 percent share of all ransoms.

The journey to unmask Hastalamuerte began by meticulously piecing together digital footprints left across various cybercrime forums and open-source intelligence platforms. The cyber intelligence firm Intel 471 played a crucial role, revealing that the user "Hastalamuerte" was a Russian and English-speaking individual who had registered on nearly a dozen prominent cybercrime forums between 2019 and the present day. These platforms included notorious sites like Exploit, Breachforums, Ramp_V2, BHF, Raidforums, and Nulled. This extensive forum presence provided a rich tapestry of data points for analysis.

A significant breakthrough came from Intel 471’s finding that Hastalamuerte registered on Breachforums in January 2025 from an Internet Protocol (IP) address located in Izhevsk, the capital city of Russia’s Udmurt Republic. Intriguingly, the user "Zeta88" had also registered on the English-language cybercrime forum Breached in August 2022, from a different IP address, but also within Izhevsk. The consistent geographical link to Izhevsk across different monikers and timeframes provided a strong foundational clue.

Further digging by Intel 471 uncovered that Hastalamuerte had registered on Raidforums in 2020 using the email address "[email protected]." The inclusion of "1488" in the email address immediately raised a red flag. "1488" is a widely recognized numeric symbol associated with white supremacy, a combination of the "Fourteen Words" slogan (14 words) and the eighth letter of the alphabet repeated twice, standing for "Heil Hitler" (HH). This detail offered a glimpse into the individual’s ideological leanings, a common, albeit concerning, element found in some segments of the cybercriminal underworld.

A lookup of this Protonmail address using the open-source intelligence service Epieos revealed its connection to an Apple account and a phone number ending in "04." Epieos also linked the Protonmail address to a GitHub account operating under the username "SantaMuerte." While this GitHub account was marked private, a historical activity timeline of "SantaLaMuerte" (a slight variation, often used to evade detection) showed the user actively watching and developing various malware tools and exploits, indicating a deep engagement with offensive cybersecurity practices.

In April 2020, Hastalamuerte publicly shared their Telegram instant messenger handle, "@hastalamuerte18," on the crime forum Nulled. The threat intelligence company Flashpoint subsequently identified the unique Telegram ID number associated with this username as "30907522." This unique identifier proved to be a critical pivot point in the investigation.

The breach tracking service Constella Intelligence then reported that Hastalamuerte’s Telegram ID was connected to another username, "bu4vs," and more crucially, to a Russian phone number: "79127650004." This phone number became the linchpin for identifying the real-world individual.

From Hastalamuerte to Alexander Yapaev: A Detailed Profile

Pivoting on the Russian phone number "79127650004" within Constella’s databases yielded multiple records from hacked Russian government databases. These records unambiguously assigned the phone number to one Alexander Andreevich Yapaev, a 36-year-old individual residing in Izhevsk – precisely the geographical location consistently linked to Hastalamuerte’s and Zeta88’s digital activities.

Constella’s findings further revealed that this phone number was used to create an account on the Russian social media platform Pikabu under the name "4apai18." The numeral "4" is frequently used in Russian online communities as a shorthand for the "ch" sound, suggesting "Chapaev18." Mr. Yapaev was also found to have used common surnames like "Ivanov" or "Chapaev" when signing up for various websites, indicating an attempt, albeit often insufficient, to obfuscate his identity.

A subsequent search by Intel 471 for cybercrime forum members using the nickname "SantaMuerte" unearthed an account created in 2020 on the Russian hacking forum Codeby. This user had originally registered on Codeby with the less-than-subtle nickname "Alexandr 4apaev," providing yet another direct link to Alexander Yapaev.

Constella further established that Mr. Yapaev regularly used the email address "[email protected]." Epieos corroborated this by linking the "[email protected]" address to a LinkedIn account belonging to Alexander Yapaev. On his LinkedIn profile, Yapaev lists himself as the head of B2B marketing at Uralenergo Udmurtia, one of Russia’s largest suppliers of electrotechnical and lighting products. This professional background, particularly in a marketing role, suggests an individual with organizational skills and a potential understanding of business operations, which could be leveraged in the administration of a complex RaaS operation. Multiple attempts to contact Mr. Yapaev for comment went unanswered.

The Russian Cybercrime Ecosystem: A Haven for Operators

The unmasking of Alexander Yapaev, much like previous "Breadcrumbs stories" that expose Russian cybercriminals, often prompts questions about why these individuals seemingly do so little to hide their real-life identities. The reality is multifaceted. Many individuals, Russian or otherwise, do not initially set out to become "arch-criminals." Instead, they are often drawn into the cybercrime scene gradually, their skills broadening and sharpening over several years through engagement in online communities.

A critical dynamic specific to Russia is the government’s stance on cybercriminal activity. The Russian government generally either co-opts or tacitly ignores cybercriminal operations within its borders, provided the hackers do not target or steal from Russian businesses and citizens. This implicit "safe haven" status means that successful cybercriminals in Russia are largely insulated from prosecution and arrest by foreign law enforcement agencies, as long as they adhere to these unwritten rules, occasionally pay off the right people, and refrain from traveling abroad where they might be subject to international extradition. For those who intend to strictly abide by these parameters, the initial concern for rigorous online anonymity might be significantly reduced.

However, the simplest explanation for many operational security (OpSec) mistakes lies in the early stages of a cybercriminal’s career. Individuals of all nationalities tend to make fundamental errors when they are less savvy and have less to lose from their carelessness. A review of Hastalamuerte’s early posts on crime forums (circa 2019-2020) indeed paints a picture of a relatively unsophisticated and low-skilled hacker, actively trying to learn the ropes and build a reputation within these communities. For instance, in June 2020, Hastalamuerte’s Telegram account joined a multi-month training program (@pntst) focused on teaching popular penetration testing tools. Candid posts from this hacker training camp revealed Hastalamuerte struggling to use these tools effectively, demonstrating a learning curve that eventually led to more advanced capabilities.

Evolving Tactics: AI and the Future of Ransomware

A recent and significant development in understanding The Gentlemen’s operations comes from the threat research group PRODAFT. In a detailed writeup released on June 11, PRODAFT corroborated the persona identified, matching it with "high confidence." Their investigation provided further insights into the group’s technical execution, revealing that the administrator (Zeta88/Hastalamuerte) directly supplies affiliates with initial access, primarily through Fortinet SSL-VPN credentials. These credentials are obtained either through brute-force attacks or sourced from the group’s own leak database. This direct provision of initial access streamlines the attack process for affiliates and ensures a consistent flow of targets.

Perhaps most concerning is PRODAFT’s discovery that the administrator is leveraging artificial intelligence (AI) to develop and maintain the ransomware and its associated tooling. AI is also reportedly used to assist with post-exploitation activities, indicating a sophisticated and forward-thinking approach to cybercrime. The integration of AI in ransomware development could lead to more evasive, adaptive, and rapidly evolving malware strains, posing an even greater challenge to cybersecurity defenses.

Implications and Broader Impact

The unmasking of Alexander Yapaev as the alleged administrator of The Gentlemen ransomware group carries significant implications for global cybersecurity and law enforcement. For businesses and critical infrastructure, it reinforces the persistent and evolving threat posed by highly organized cybercriminal syndicates. The Gentlemen’s aggressive recruitment and sophisticated tactics, now including AI, mean that organizations must redouble their efforts in network security, patch management, multi-factor authentication, and robust incident response planning. The focus on internet-facing devices highlights the critical need for strong perimeter defenses and continuous vulnerability assessments.

For law enforcement agencies, such detailed investigations provide actionable intelligence, even if direct arrests remain challenging due to geopolitical complexities. The exposure of an individual’s identity, professional background, and digital footprint can disrupt operations, deter potential affiliates, and create leverage for future interdictions should the individual travel outside the relative safety of Russia. It also underscores the importance of international cooperation in cyber intelligence sharing to combat cross-border cybercrime effectively.

The competitive RaaS model, driven by lucrative revenue splits, indicates a highly commoditized and professionalized cybercrime market. The rapid growth of groups like The Gentlemen, fueled by skilled affiliates, suggests a continuous need for innovative defense strategies that outpace the adversaries. The advent of AI in ransomware development marks a new frontier in cyber warfare, potentially accelerating the creation of novel attack vectors and making detection even more complex.

In conclusion, the meticulous investigation into "The Gentlemen" ransomware group has culminated in the alleged identification of its administrator, Alexander Andreevich Yapaev. This exposure not only shines a light on the individual behind one of the most active ransomware operations but also provides crucial insights into the evolving tactics, recruitment strategies, and the geopolitical context that enables such pervasive cybercrime. As the digital landscape continues to evolve, the ongoing fight against ransomware demands unwavering vigilance, collaborative intelligence, and adaptive defense mechanisms to protect global digital infrastructure.

July 20, 2026 0 comment
0 FacebookTwitterPinterestEmail
Cybersecurity & Hacking

Sophisticated FakeGit Campaign Exploits GitHub and AI Agents to Deliver SmartLoader and StealC Malware

by admin July 20, 2026
written by admin

Cybersecurity researchers have uncovered a vast and evolving malicious campaign, dubbed FakeGit, which has leveraged nearly 7,600 illicit GitHub repositories to distribute the SmartLoader malware family. A particularly alarming development within this campaign, known as AgentBaiting, sees threat actors weaponizing artificial intelligence (AI) agents to inadvertently discover and propagate these malicious payloads, bypassing direct human intervention. This sophisticated operation marks a significant escalation in software supply chain attacks, demonstrating a novel method for delivering malware and establishing persistent access to compromised systems.

The FakeGit Campaign: A Deep Dive into Digital Deception

The FakeGit operation, meticulously documented by Oleg Zaytsev, lead security researcher at Island, has established a sprawling infrastructure designed to ensnare unsuspecting developers and, more recently, autonomous AI agents. At its core, FakeGit employs deceptive tactics including the creation of copied projects, meticulously crafted lookalike developer profiles, convincing README files, and the distribution of malicious ZIP archives. These elements collectively serve to deliver SmartLoader malware, a versatile initial access broker. Out of the thousands of identified malicious repositories, more than 800 specifically masquerade as legitimate AI skills or Model Context Protocol (MCP) servers, capitalizing on the burgeoning interest and reliance on AI-driven tools and integrations.

GitHub, as the world’s largest platform for software development and version control, serves as a critical hub for open-source projects and collaborative coding. Its immense repository of code, tools, and developer resources makes it an attractive target for threat actors seeking to inject malicious code into the software supply chain. The sheer volume of repositories and user activity on GitHub provides a fertile ground for blending in malicious projects with legitimate ones, making detection challenging for both automated systems and human users. The FakeGit campaign exploits this environment by mirroring popular projects and services, creating a convincing façade of legitimacy that developers often rely on when seeking new tools or integrations.

Understanding the Malware Payload: SmartLoader and StealC

The primary objective behind the FakeGit campaign is to establish a foothold on compromised systems using SmartLoader. This initial payload acts as a highly adaptable loader, designed to execute further malicious code and ensure persistence. Once SmartLoader has successfully infiltrated a system, it is leveraged to deploy secondary payloads, most notably StealC.

StealC is a potent information stealer, a class of malware specifically designed to exfiltrate a wide array of sensitive data from compromised machines. Its capabilities typically include harvesting credentials (usernames, passwords, tokens), browser history, cookies, cryptocurrency wallet information, system configuration details, and various other files. The data collected by StealC can then be used for a multitude of nefarious purposes, ranging from financial fraud and identity theft to corporate espionage and further network intrusion. The modular nature of SmartLoader allows the attackers significant flexibility, enabling them to adapt their post-compromise activities based on the target and their evolving objectives, making it a formidable threat in the cybercriminal toolkit.

FakeGit Campaign Uses 7,600 GitHub Repositories to Spread SmartLoader Malware

The Emergence of AgentBaiting: AI-Driven Compromises

A concerning evolution within the FakeGit campaign is what researchers have termed AgentBaiting. This novel technique represents a significant leap in attack sophistication, where AI agents themselves become vectors for malware delivery. Traditionally, social engineering attacks rely on deceiving human users into clicking malicious links or downloading compromised files. AgentBaiting, however, manipulates the autonomous search and discovery functions of AI agents.

In an AgentBaiting scenario, an AI agent, tasked with searching for a specific "skill" or an MCP server to augment its capabilities, inadvertently discovers one of these bogus GitHub repositories. These repositories are meticulously designed to appear relevant to AI agents’ search queries. Upon discovery, the AI agent, processing the convincing (but malicious) README files as legitimate documentation, proceeds to execute the attacker’s instructions. This means the AI agent, without any direct intervention or suspicious action from a human user, effectively "does the attacker’s bidding" by leading itself or its user down the malicious attack chain.

Island’s tests confirmed the susceptibility of leading AI models, including Anthropic Claude Code, Google Gemini, and OpenAI ChatGPT, to this trickery. These models were observed to surface malicious campaign repositories in response to general prompts, even without being explicitly provided a malicious link. This groundbreaking method demonstrates how a social engineering technique originally crafted to deceive humans has been refined to equally deceive advanced AI agents operating on their behalf, introducing an entirely new dimension to cyber threats.

Historical Context and Previous Warnings

The use of trojanized MCP servers for distributing SmartLoader and StealC is not entirely new. Earlier this year, cybersecurity firms Straiker AI and Derp.ca independently flagged similar activities. Straiker AI initially highlighted the deployment of SmartLoader via trojanized Oura AI components, while Derp.ca’s research further detailed a campaign involving FakeGit and LuaJIT on GitHub. These earlier observations served as precursors to the more expansive and AI-aware FakeGit operation now being detailed.

The current campaign, however, distinguishes itself through its sheer scale and the integration of AgentBaiting. The progression from human-targeted social engineering to AI-targeted deception underscores a rapid adaptation by threat actors to the evolving technological landscape. The July 2026 data indicating over 14 million downloads across GitHub Release assets in approximately 200 campaign repositories points to the significant success and reach of this persistent threat. This chronology illustrates a clear and escalating pattern of cybercriminal innovation, moving from opportunistic attacks to more targeted and automated methodologies.

Scale and Reach of the Operation

The FakeGit operation exhibits an alarming scale, with researchers identifying approximately 7,600 malicious GitHub repositories originating from around 6,600 distinct profiles. A significant portion of these, specifically 800 repositories, were designed to mimic legitimate AI Skills or MCP servers. These counterfeit offerings spanned a wide range of integrations, targeting both individual and enterprise users. Examples included bogus integrations for popular consumer applications like Gmail and WhatsApp, as well as critical enterprise tools such as Databricks, Jenkins, and Docker. This broad targeting strategy aims to maximize the potential victim pool, exploiting the demand for tools that enhance productivity and automation across various platforms.

FakeGit Campaign Uses 7,600 GitHub Repositories to Spread SmartLoader Malware

The high volume of downloads—over 14 million by July 2026—underscores the efficacy of the attackers’ deception. These downloads indicate that a substantial number of users, and potentially AI agents, have interacted with and likely executed the malicious payloads. Furthermore, the discovery of over 600 campaign listings across various public MCP and Skill registries, including LobeHub, Glama, MCP.so, and MCP Market, grants these malicious projects a false sense of legitimacy. The presence on these reputable platforms makes them more discoverable and trustworthy in the eyes of both human users and AI agents performing automated searches, significantly amplifying the threat.

Mechanism of Deception: A Credible Lure

The success of FakeGit hinges on its sophisticated mechanism of deception. Attackers meticulously craft counterfeit repositories, which are either entirely fabricated or cleverly copied from existing legitimate projects. This replication includes not just the code structure but also the branding, documentation, and even developer identities, creating a highly convincing facade. The core of the attack chain is initiated when a user or an AI agent downloads a seemingly innocuous ZIP archive from one of these repositories.

Upon execution, this ZIP archive triggers a LuaJIT loader chain. LuaJIT is a Just-In-Time compiler for the Lua programming language, often used for performance-critical applications. In this context, it is exploited to execute an obfuscated Lua script. This script is responsible for dropping the SmartLoader malware onto the compromised system. Following the successful deployment of SmartLoader, the loader proceeds to deploy StealC, ensuring that the attackers gain persistent access and the ability to exfiltrate sensitive data. Oleg Zaytsev elaborates, "The repositories were designed to meet demand already forming around AI capabilities, borrowing the names and workflows of familiar consumer and enterprise tools. That familiarity gave the malicious ZIP files a credible reason to be downloaded, while the README guided users or agents from what appeared to be routine setup into the SmartLoader attack chain." This strategy highlights the psychological engineering employed, exploiting users’ trust in familiar names and the perceived utility of AI enhancements.

Implications for Software Supply Chain and AI Trust

The FakeGit campaign, particularly with its AgentBaiting component, carries profound implications for software supply chain security and the burgeoning trust placed in AI systems. The ability of attackers to inject malicious code into widely used platforms like GitHub and then propagate it through both human interaction and autonomous AI agent discovery represents a significant escalation in cyber threats. It fundamentally challenges the integrity of open-source ecosystems and the security assumptions underlying AI-driven workflows.

For the software supply chain, this campaign underscores the vulnerability inherent in relying on external dependencies and public repositories. Developers often integrate third-party libraries, tools, and components into their projects, inadvertently inheriting any security risks associated with those external elements. When malicious actors can so effectively mimic legitimate projects, the entire chain of trust is compromised, potentially leading to widespread infections across numerous applications and systems that consume these "skills" or "servers."

The advent of AgentBaiting also erodes trust in AI agents. If AI models designed to assist users can be tricked into facilitating malware delivery, it raises serious questions about their security posture and the prudence of granting them extensive autonomy. As AI agents become more prevalent in daily tasks, from code generation to data analysis and system management, ensuring their resilience against such sophisticated deception becomes paramount. The incident highlights a critical new attack surface where AI models, without direct human input, can inadvertently become instruments for malicious actors, transforming routine AI-assisted discovery operations into pathways for executing harmful code.

FakeGit Campaign Uses 7,600 GitHub Repositories to Spread SmartLoader Malware

Official Responses and Industry Vigilance

While specific official statements from GitHub or the developers of the directly impacted AI models (Anthropic, Google, OpenAI) were not immediately available in the context of this specific report, such widespread malicious activity typically prompts swift and decisive action from platform providers. GitHub, for instance, maintains robust policies against malware distribution and copyright infringement, and it is highly probable that they are actively working to identify and remove the offending repositories and developer profiles associated with FakeGit. Their ongoing efforts often include automated scanning for suspicious code and user-reported takedowns.

Similarly, AI model developers are likely to be closely monitoring these developments. The susceptibility of their models to AgentBaiting necessitates a re-evaluation of their security frameworks, particularly concerning how their AI agents interact with external data sources and interpret documentation. Enhancements to prompt engineering defenses, improved content validation mechanisms, and stricter vetting of external "skills" or "plugins" are crucial steps for these companies to mitigate future risks. The cybersecurity industry as a whole is likely to increase its focus on AI security, developing new tools and methodologies to detect and counteract AI-driven deception tactics.

Mitigating the Threat: Recommendations for Users and Enterprises

Given the sophistication and evolving nature of the FakeGit campaign, robust mitigation strategies are essential for both individual developers and large enterprises. Island researchers provide several key recommendations to counter this emerging threat:

  1. Build a Catalog of Reviewed Skills, MCP Servers, and Agent Plugins: Organizations should establish and maintain an internal, curated catalog of approved AI skills, MCP servers, and agent plugins. This involves thorough vetting and verification of each component before it is integrated into operational workflows. Relying solely on public registries or ad-hoc discovery carries inherent risks.
  2. Evaluate New Agent Capabilities in a Sandboxed Environment: Before rolling out new AI agent capabilities or integrating new external skills across an enterprise, it is critical to test them within an isolated, sandboxed environment. This allows for observation of their behavior, network interactions, and potential vulnerabilities without risking production systems.
  3. Verify Both the Publisher and the Project to Ensure Credibility: A fundamental security practice is to rigorously verify the legitimacy of both the publisher (developer profile) and the project itself. This goes beyond a cursory glance at the README. Developers should check for signs of authenticity, such as a long-standing reputation, official affiliations, consistent coding practices, and a community of trusted contributors. Be wary of newly created profiles or projects with minimal history.
  4. Monitor Agentic Pathways: Enterprises utilizing AI agents should implement continuous monitoring of the pathways these agents use for discovery and interaction with external resources. This includes logging agent queries, responses, discovered resources, and any subsequent actions taken. Anomalous behavior or interactions with suspicious repositories should trigger immediate alerts and investigations.
  5. Educate Users on Supply Chain Risks: Continuous education for developers and end-users about the risks associated with software supply chain attacks and the importance of verifying open-source components is vital. Awareness campaigns can help foster a culture of security vigilance.

"FakeGit did not need to breach anything. It published convincing repositories, borrowed real developers’ identities, spread its listings across public registries, and let discovery do the rest," Island emphasized in its report. "With AgentBaiting, that discovery no longer requires a person at all: an agent searching for a Skill or MCP server can find the lure, read the attacker’s README, and carry its instructions forward. The defenses that matter are the ones that interrupt this chain before execution." This highlights the shift from active breaching to passive luring, making detection and prevention even more challenging.

The Evolving Cyber Threat Landscape

The FakeGit and AgentBaiting campaigns serve as a stark reminder of the rapidly evolving cyber threat landscape. As AI technologies become increasingly integrated into everyday computing and development processes, threat actors will inevitably seek to exploit their capabilities and vulnerabilities. The transition from human-centric social engineering to AI-centric deception marks a significant turning point, demanding innovative and proactive cybersecurity strategies. The battle against malware is no longer just about protecting endpoints and networks from direct attacks but also about securing the intelligent agents that interact with and interpret our digital world. The future of cybersecurity will increasingly involve understanding and defending against threats that leverage AI’s own mechanisms for nefarious purposes, making vigilance, robust verification, and continuous adaptation more critical than ever before.

July 20, 2026 0 comment
0 FacebookTwitterPinterestEmail
Cybersecurity & Hacking

Zero-Day Exploitation of SonicWall SMA1000 Vulnerabilities Led to Custom Malware Deployment for Weeks

by admin July 20, 2026
written by admin

Two recently disclosed critical vulnerabilities within SonicWall’s SMA1000 Secure Mobile Access appliances were exploited in sophisticated zero-day attacks for a period spanning several weeks, enabling threat actors to install bespoke malware on compromised VPN devices. This alarming discovery highlights the persistent and evolving threat landscape facing critical network infrastructure, underscoring the urgency for robust patching and proactive security measures. The vulnerabilities, identified as a critical server-side request forgery (SSRF) and a high-severity command injection flaw, provided attackers with unauthenticated access and root privileges, leading to deep infiltration of targeted systems.

Unveiling a Covert Campaign: The Initial Disclosure

The initial warning came from SonicWall itself last week, alerting customers to active exploitation of previously undisclosed flaws affecting its SMA1000 Series VPN appliances. At that time, SonicWall urged immediate action, releasing patches for affected versions 12.4.3-03453 and 12.5.0-02835. However, the initial advisory was notably sparse on the specifics of the exploit chain or the nature of the compromise, leaving many organizations in the dark about the full extent of the threat. The affected models specifically included SMA1000 6210, 7210, and 8200v appliances, which are widely deployed by enterprises for secure remote access.

The two vulnerabilities at the heart of this campaign are tracked as CVE-2026-15409, a critical server-side request forgery (SSRF) vulnerability, and CVE-2026-15410, a high-severity command injection flaw. An SSRF vulnerability allows an attacker to induce the server-side application to make HTTP requests to an arbitrary domain of the attacker’s choosing. This seemingly innocuous capability can be leveraged for internal network reconnaissance, accessing sensitive data, or even triggering further attacks by interacting with internal services that are not directly exposed to the internet. Command injection, on the other hand, is a much more direct and immediately dangerous flaw, enabling an attacker to execute arbitrary commands on the host operating system, often with elevated privileges, by injecting malicious code into input fields that are not properly sanitized. The combination of these two vulnerabilities proved to be devastating, providing a clear path from initial unauthenticated access to full system compromise.

Volexity’s Deep Dive: Exposing the Full Attack Chain

SonicWall SMA1000 flaws exploited as zero-days to push custom malware

The full gravity and technical intricacies of the attacks were brought to light through a comprehensive report issued by incident response firm Volexity. Volexity, which collaborated with SonicWall in the investigation, meticulously detailed the exploitation chain, revealing how threat actors managed to install custom malware on compromised SMA1000 appliances. This report painted a stark picture of a sophisticated and persistent threat actor operating with a high degree of technical prowess.

According to Volexity, the threat actor, which they track as UTA0533, initiated exploitation of these vulnerabilities as early as June 22, 2026. This critical detail means that organizations using vulnerable SonicWall SMA1000 devices were exposed to active compromise for weeks before SonicWall publicly disclosed the flaws and released patches. This timeline underscores the inherent danger of zero-day exploits, where defenders are often caught unaware with no readily available defenses. Volexity’s analysis was based on an exhaustive examination of logs, disk images, and memory from compromised appliances, providing undeniable evidence of the attacker’s presence and methods.

The Sophisticated Exploitation Process

The attack chain, as meticulously reconstructed by Volexity, began with the exploitation of CVE-2026-15409, the critical SSRF vulnerability. UTA0533 leveraged this flaw to abuse the SMA1000’s /wsproxy endpoint. This endpoint, intended for legitimate internal proxying, was weaponized to establish unauthenticated WebSocket tunnels. Crucially, these tunnels allowed the attackers to gain access to services that should have been strictly confined to the appliance’s internal network, effectively bypassing perimeter defenses. This exposure included sensitive internal applications such as CouchDB, a NoSQL database often used by web applications, and the VPN device’s own management service.

With this newfound internal access, the attackers proceeded to query CouchDB. Their objective was to extract the appliance’s product_uuid, a unique identifier critical for the subsequent stages of their attack. While the precise method used to exploit CouchDB for this data exfiltration remains undisclosed by Volexity, its successful retrieval demonstrated the attackers’ ability to navigate and interact with internal system components.

The product_uuid served as the key to unlock the next phase of the assault: the exploitation of CVE-2026-15410, the high-severity command injection vulnerability. This flaw was exploited through the Appliance Management Console’s sysCtrl.execRemoveHotfix RPC method. By injecting malicious commands into this method, UTA0533 gained the ability to execute arbitrary commands with root privileges, effectively taking full control of the compromised appliance. Root access is the ultimate prize for attackers, granting them unrestricted control over the operating system, allowing for the installation of persistent backdoors, data manipulation, and further network penetration.

SonicWall SMA1000 flaws exploited as zero-days to push custom malware

Deployment of Custom Malware: KNUCKLEBALL, Sou5, and ORANGETAIL

Once root access was established, UTA0533 wasted no time in installing a custom malware dropper, which Volexity aptly named KNUCKLEBALL. This dropper was observed under the filename deploy_new.py, indicating a Python-based script. KNUCKLEBALL’s primary function was to deploy two distinct Java-based malware families specifically designed for SonicWall SMA1000 appliances: Sou5 (identified as agent_wp8.jar) and ORANGETAIL (identified as agent_wp9.jar). The development of custom malware tailored to a specific target system underscores the advanced capabilities and focused intent of UTA0533.

  • Sou5: This malware family functioned as a sophisticated reverse proxy. By establishing covert tunnels, Sou5 allowed the attackers to funnel traffic through the compromised SMA1000 appliance, thereby maintaining persistent and clandestine access to internal network resources. A reverse proxy can be incredibly effective for attackers, as it masks their true origin, blends malicious traffic with legitimate network activity, and allows them to bypass egress filtering rules that might otherwise block direct outbound connections.
  • ORANGETAIL: Complementing Sou5, ORANGETAIL was a custom Java webshell. Webshells are persistent backdoors that provide remote administrative access to a compromised web server. In this case, ORANGETAIL enabled attackers to send encrypted Java payloads to the compromised appliance and dynamically execute them within an active HTTP session. This functionality granted UTA0533 real-time command and control, allowing for flexible and adaptable post-exploitation activities without needing to continually re-exploit the initial vulnerabilities.

Beyond these core malware components, Volexity also discovered that the attackers had modified the appliance’s nginx configuration. This modification was crucial for remotely exposing the ORANGETAIL webshell, ensuring that the attackers could access their backdoor from outside the network. Furthermore, the threat actors installed ROOTRUN, a privilege-escalation tool. While root access had already been achieved, ROOTRUN likely served as a persistent mechanism to regain or maintain root privileges, ensuring that even if certain processes were restarted or security measures attempted to demote their access, they could quickly re-escalate.

Broader Implications and the Threat Landscape

The campaign, while technically sophisticated in its exploitation and malware development, showed a mixed level of success in terms of lateral movement within victim networks. Volexity noted that UTA0533 was "less successful at spreading into victims’ internal networks" beyond the initial compromise of the SMA1000 appliances. This observation, while somewhat reassuring, does not diminish the severity of the initial breach or the potential for significant damage had the attackers been more aggressive or successful in their post-exploitation activities.

This incident highlights several critical aspects of the contemporary cybersecurity landscape:

SonicWall SMA1000 flaws exploited as zero-days to push custom malware
  1. VPN Appliances as High-Value Targets: VPNs are gateways to an organization’s internal network, making them prime targets for sophisticated threat actors. A compromise of a VPN appliance can bypass layers of perimeter security, providing direct access to sensitive internal systems and data. The widespread reliance on VPNs for remote work and distributed operations further elevates their criticality.
  2. The Peril of Zero-Day Exploits: The fact that these vulnerabilities were exploited for weeks before public disclosure and patching underscores the immense challenge posed by zero-day threats. Organizations have no defense against such attacks until a patch is released and applied, emphasizing the need for robust threat hunting, anomaly detection, and advanced endpoint protection that can identify post-exploitation activities even if the initial breach was unknown.
  3. Sophistication of Threat Actors: The development of custom, tailored malware (KNUCKLEBALL, Sou5, ORANGETAIL) and the intricate multi-stage exploit chain demonstrate the high level of technical skill and resources possessed by groups like UTA0533. This signifies a move beyond off-the-shelf tools to highly specialized attack methodologies, making detection and attribution more challenging.
  4. Supply Chain Security: This event also touches upon the broader issue of supply chain security. As organizations increasingly rely on third-party hardware and software, vulnerabilities in these components become critical points of failure. Vendors like SonicWall bear a significant responsibility to rigorously test their products and respond swiftly and transparently to discovered flaws.
  5. Urgency of Patching and Proactive Defense: SonicWall’s urgent recommendation to patch immediately was well-founded. However, the period of active exploitation before patches were available serves as a potent reminder that patching, while crucial, is only one component of a comprehensive security strategy. Organizations must also invest in robust incident response capabilities, continuous monitoring, network segmentation, and user behavior analytics to detect and mitigate threats that bypass traditional defenses.

Official Responses and Industry Recommendations

Following Volexity’s detailed report, SonicWall reiterated its strong recommendation for all customers utilizing SMA1000 appliances to apply the latest patches (versions 12.4.3-03453 and 12.5.0-02835) without delay. While SonicWall had initially confirmed the zero-day nature of the attacks, Volexity’s findings provided the crucial operational intelligence needed for organizations to understand the full scope of compromise and potential indicators of compromise (IOCs) to search for within their environments.

Cybersecurity experts across the industry echoed these calls for immediate patching, alongside a broader set of recommendations. These include:

  • Thorough Log Review: Organizations should review logs from their SMA1000 appliances and surrounding network infrastructure for any indicators of compromise (IOCs) provided by Volexity or other threat intelligence sources, dating back to at least June 2026.
  • Network Segmentation: Isolating critical systems and data through network segmentation can limit the lateral movement of attackers, even if an initial compromise occurs.
  • Multi-Factor Authentication (MFA): While the exploit bypassed authentication, strong MFA for all VPN and administrative access points remains a fundamental security control to prevent unauthorized access through other means.
  • Endpoint Detection and Response (EDR): Implementing EDR solutions on internal endpoints can help detect unusual activity or the deployment of malicious payloads if attackers manage to move beyond the VPN appliance.
  • Regular Security Audits and Penetration Testing: Proactive testing can help identify weaknesses before threat actors exploit them.

The SonicWall SMA1000 zero-day attacks serve as a potent reminder that the battle against cyber threats is continuous and ever-evolving. The sophistication demonstrated by UTA0533, coupled with the critical nature of the compromised infrastructure, underscores the imperative for organizations to maintain unwavering vigilance, prioritize rapid patching, and adopt a multi-layered, proactive approach to cybersecurity defense. The collaborative effort between vendors like SonicWall and incident response firms like Volexity is crucial in dissecting these complex attacks and providing the necessary intelligence to protect the global digital infrastructure.

July 20, 2026 0 comment
0 FacebookTwitterPinterestEmail
Bitcoin & Altcoins

Ethereum Core Developers Convene in the Arctic Circle to Forge the Future of Scalability

by admin July 20, 2026
written by admin

Just over one hundred core contributors to the Ethereum network recently gathered in Longyearbyen, Svalbard, nestled above the Arctic Circle, for an intensive week of collaborative development known as Soldægn Interop. The primary objective of this gathering was to advance the critical "Glamsterdam" network upgrade, a pivotal step in enhancing Ethereum’s scalability and efficiency. This event follows in the tradition of previous interop sessions, including Berlinterop, Amphora, Edelweiss, and Nyota, each focused on specific network enhancements. The Soldægn Interop, however, returned to a single-track format, emphasizing deep, multi-client collaboration toward a singular, ambitious goal: hardening the Glamsterdam upgrade.

The intense week of development, held under the perpetual daylight of the Arctic summer, culminated in the achievement of three principal objectives by Friday. These included establishing alignment on a post-Glamsterdam gas limit floor of 200 million, ensuring the stability of execution-payloads-by-builders (ePBS) implementations operating with external builders, and finalizing the repricing numbers for EIP-8037. Significant headway was also made on future features, such as those planned for the Hegedas upgrade, including FOCIL (Formal Consensus Layer) and native account abstraction, alongside progress on numerous other technical fronts.

The Strategic Choice of Svalbard: A Nexus of Innovation and Preservation

The selection of Longyearbyen, Svalbard, as the venue for Soldægn Interop was deliberate and multifaceted. Beyond its unique geographical location, Svalbard offers an environment where individuals from any nation can live and work without visa restrictions, fostering an inclusive atmosphere for global collaboration. More profoundly, the archipelago is home to the Svalbard Global Seed Vault and the Arctic World Archive. These remarkable facilities, carved into the permafrost, serve as repositories for humanity’s most vital data and genetic heritage, safeguarding everything from crop diversity to cultural artifacts and source code for future generations. Notably, Ethereum’s own source code is part of this digital ark, symbolizing the project’s commitment to long-term data preservation.

Soldøgn Interop Recap ☀️

Furthermore, the extended daylight hours in Svalbard from late April through August provided a unique operational advantage. This period of 24/7 sunlight mirrored the continuous uptime characteristic of the Ethereum network itself, allowing core developers to maximize their working hours and foster an environment of constant progress, much like the network they are dedicated to building. This unique setting, combined with the shared objective of advancing Ethereum’s scalability, created an unparalleled atmosphere for focused development.

Hardening Glamsterdam: Paving the Way for Enhanced Scalability

The central mission of the Soldægn Interop was to solidify the technical foundations for the Glamsterdam upgrade, with a particular focus on establishing a robust and sustainable gas limit. Safely increasing Ethereum’s gas limit is a complex, multi-dimensional challenge that Glamsterdam is designed to address. The upgrade tackles several key areas: optimizing how blocks are constructed and proposed, ensuring that client implementations have sufficient operational headroom under increased load, and refining how state-creation costs scale in tandem with transaction throughput.

The practical outcome of the week’s efforts was the establishment of a stable, multi-client Glamsterdam development network. This network was configured to run the latest ePBS implementations, alongside finalized specifications for gas repricing and block access lists. Crucially, the week generated extensive benchmarking data, which now serves as a solid empirical basis for proposing a credible increase to the gas limit. The majority of the developers’ time was spent in deep coding sessions, often extending into the early hours of the morning. These periods of intense individual work were interspersed with focused breakout sessions dedicated to aligning on critical design decisions and discussing the long-term roadmap for Ethereum’s evolution.

The logistical and technical support for the event was provided by three dedicated teams from the Ethereum Foundation. EthPandaOps delivered their advanced tool, ethIQ, and a panda MCP server to facilitate agentic workflows, enhancing the development process. The Protocol Support team established soldogn.xyz as the centralized repository for interop goals, schedules, and meeting notes, ensuring clear communication and documentation. Additionally, the EF Digital Studio team meticulously documented the entire week, promising a forthcoming documentary that will capture the essence of this significant collaborative effort.

Soldøgn Interop Recap ☀️

ePBS: Reimagining Block Construction for Increased Throughput

Execution-payloads-by-builders (ePBS) represents a fundamental shift in how Ethereum blocks are constructed. This system restructures block production by introducing specific deadlines for block construction, payload revelation, and attestation finalization. By explicitly allocating time for execution within the block production cycle, ePBS significantly increases the available headroom for raising the network’s gas limit.

The week began with an ambitious goal: a fully functional 4-Execution Layer (EL) by 4-Consensus Layer (CL) Glamsterdam development network by Monday evening. The initial attempts revealed a number of critical issues, necessitating a revised target for Tuesday. By Tuesday, a 4×3 configuration was running stably enough to commence rigorous stress testing. The remainder of the week was dedicated to an intensive ePBS hardening cycle: stress testing, identifying edge cases, implementing fixes, and repeating the process.

A significant development occurred on Tuesday morning with a breakout session focused on the Builder API. This session substantially simplified the specification concerning validator registration, the flow of bids, headers, and commitments, the trust model for builder payments, and the implementation of circuit-breaker mechanisms. Mid-week debugging efforts zeroed in on cross-client edge cases, particularly concerning the invalidation of beacon requests by execution-layer requests. A newly developed test suite highlighted a critical gap across all client implementations in this area. By Thursday morning, CL teams reported stable ePBS operations, while EL-side bid pathways were still undergoing debugging. These were resolved through Thursday and into Friday. Two contentious issues remain under active discussion within the All-Core Developers (ACD) community: whether a request signature should explicitly commit to the receiving builder, and how to ensure the resilience of a 1 ETH-staked-builder design against Sybil-based liveness attacks on the peer-to-peer network. By Friday, nearly all participating clients were operating in concert on the glamsterdam-devnet-2 network, with the external builder pipeline successfully tested end-to-end.

BAL Optimizations and Gas Repricings: The Execution Layer’s Scaling Strategy

While ePBS addresses the consensus layer’s role in scaling, the execution layer’s contribution is driven by two primary components: gas repricings and Block-Level Access Lists (BALs). BALs provide clients with advance information about a block’s read and write sets, enabling critical optimizations such as parallel execution, batched I/O operations, and parallel state-root computation. These advancements directly influence the maximum block size that clients can comfortably process.

Soldøgn Interop Recap ☀️

The BAL optimization track at Soldægn Interop operated on separate development networks, distinct from the Glamsterdam ePBS chains. This separation ensured that optimization benchmarks were not conflated with the complexities of stabilizing consensus-layer components. Each optimization was implemented behind a feature flag, allowing for isolated performance comparisons rather than evaluating them as a monolithic bundle. The BAL benchmark dashboard and leaderboard were instrumental in identifying the worst-case scenarios for each client across the test suite. By prioritizing and addressing the slowest execution paths, developers aimed to elevate the gas limit floor across the entire network, rather than solely benefiting the most optimized implementations.

EIP-8037, a key element of the gas repricing strategy, focuses on increasing the gas cost associated with creating new state. This adjustment is crucial to prevent an unbounded increase in state growth, even with a higher gas limit. The initial specification for EIP-8037, as it stood before Soldægn, featured dynamic per-state-byte pricing that was directly tied to the block gas limit. This dynamic approach presented significant challenges for testing, creating a combinatorial explosion of fuzz matrices for each gas limit band, and making benchmarking an arduous task. Early in the week, the development teams reached a consensus to abandon dynamic pricing in favor of a fixed cost_per_state_byte. Future repricing adjustments will be managed at future fork boundaries, rather than being dynamically determined within a single fork.

The accounting model itself underwent a more iterative refinement process. A breakout session on Monday shifted state-gas accounting from the mid-execution phase to the end of the call frame. A follow-up session on Tuesday addressed account creation costs, code deposit costs, and CREATE-transaction reverts. By Wednesday, edge cases related to reservoir refunds and refills necessitated a re-evaluation of the model. A breakout session on Thursday reverted the accounting back to the opcode level, recognizing that the primary complexity lay within the reservoir model itself, rather than the computational aspects of accounting. By Friday, the specification had stabilized on the bal-devnet-6 network, and the BAL track successfully delivered the final repricing numbers. This iterative process underscores the power of interop events, where complex specification, implementation, testing, and debugging challenges can be resolved in hours rather than weeks, compressing asynchronous progress into days.

The convergence of these three critical threads—ePBS, BAL optimizations, and gas repricings—culminated in the week’s headline achievement: the establishment of a credible target for a 200 million gas limit floor post-Glamsterdam. This substantial increase is made possible by the synergistic effect of ePBS structuring the slot to allocate more time for execution, BAL optimizations providing clients with the necessary throughput headroom within that structure, and EIP-8037 ensuring that the higher gas limit does not lead to unsustainable state growth.

Soldøgn Interop Recap ☀️

Other Glamsterdam Initiatives and Future Outlook

Beyond the core components of ePBS, BALs, and gas repricings, the Soldægn Interop also addressed numerous other aspects of the Glamsterdam upgrade. Consensus Layer (CL) teams finalized decisions on several smaller EIPs slated for Glamsterdam. EIP-8061, which aims to increase exit and consolidation churn, was successfully integrated into glamsterdam-devnet-1. Conversely, EIP-8080, proposing exits via the consolidation queue, was declined for inclusion in this upgrade. EIP-8045, concerning the removal of slashed validator duties, was scoped down to apply only to proposer duties within the look-ahead window. EIP-7688, focusing on SSZ stable containers, remains within Glamsterdam’s scope but was intentionally held out of glamsterdam-devnet-1 to allow for further work on bounded gossip-message sizes for attestations under progressive lists.

A significant architectural breakout session on Wednesday morning, involving both EL and CL teams, led to the decision to defer EIP-8237 from Glamsterdam. This move preserves optionality for a more comprehensive "top-up sync" architecture in a future fork. In its place, the participants agreed to draft a new EIP that will standardize the sequencing of forkchoiceUpdated, newPayload, and getPayload calls, specify an initiation handshake for snap sync, and enhance consistency between the engine API surfaces for valid and invalid states.

Hardening and testing were pervasive themes throughout the week. A dedicated session on Thursday focused on the development of fork-choice compliance testing frameworks. The Diamond repository, a collection of reproducible CL edge-case scenarios, and buildoor, PandaOps’s external builder testing tool, were showcased. Attendees actively suggested attack scenarios in real-time, demonstrating the collaborative and responsive nature of the interop process.

Looking beyond Glamsterdam, several breakout sessions were dedicated to the Hegedas upgrade and subsequent forks. A proposal-agnostic session on native Account Abstraction explored the fundamental requirements and constraints for any future design. Key feature goals such as alternative signature schemes, aggregation, batching, recovery, gas sponsorship, flexible nonces, and keystore wallets were discussed alongside critical hard constraints like public mempool compatibility, statelessness, and L2 Denial-of-Service (DoS) resistance.

Soldøgn Interop Recap ☀️

A FOCIL breakout on Thursday focused on implementation updates, with early prototypes already demonstrating functionality. The immediate next steps involve multi-client interoperation and the establishment of a dedicated FOCIL development network. Two significant design decisions were made: FOCIL will be disabled during periods of 2-epoch non-finality, mirroring the behavior of the proposer-boost circuit breaker, and an index-based bookmark approach will be adopted to ensure compatibility with frame transactions and EIP-7702.

Further into the future, an extended ETH P2P track explored the potential for a QUIC-based replacement for libp2p, emphasizing privacy-by-default and slot-aware integration. A prototype for erasure-coded broadcast demonstrated a simulated propagation speed approximately six times faster than GossipSub for 2.4 MB payloads. The CL track also indicated a strong sentiment towards eventually deprecating consolidations entirely. The proposed approach involves declaring a final fork that supports consolidations, followed by a mandatory exit-and-redeposit mechanism, presenting a cleaner long-term solution for managing validator set state growth.

Refining the All-Core-Developers Process

A pivotal session on Wednesday afternoon, led by ACDE co-leads Nixo and Ansgar, gathered input from core contributors regarding the All-Core-Developers (ACD) process. This session revisited the "headliner" construct, a mechanism for selecting major upgrade themes. The pros and cons of maintaining a "strawmap," a flexible, community-driven roadmap, were debated, and criteria for EIP Selection Framework Initiative (SFI) were formalized. The consensus favored retaining headliners but with increased flexibility regarding the rigidity of EIP-versus-theme alignment, accepting a "theme plus candidate EIP" approach as a viable pattern. The strawmap’s per-fork year assignments beyond 2026 were identified as potentially over-canonicalized and likely to be softened. A new four-point SFI definition was proposed, with ACDT (All-Core-Developers-Technical) signaling readiness and ACDE (All-Core-Developers-Execution) and ACDC (All-Core-Developers-Consensus) retaining final decision-making authority. A new prioritization and ordering process, to be determined after CFI (Core Feature Inclusion) decisions and reflected in a meta-EIP, will supersede SFI’s previous role in driving devnet inclusion, commencing with the Hegedas upgrade.

On the call coordination front, Alex Stokes announced a three-month sabbatical commencing the following week. Pari will assume ACDC moderation duties in the interim, and Barnabas will fill the role for ACDT. The current leadership structure for core developer coordination is as follows: Nixo and Ansgar chair ACDE, Pari serves as interim ACDC moderator, and Mario, Barnabas, and Danceratopz rotate ACDT moderation responsibilities.

Soldøgn Interop Recap ☀️

Broader Progress and Future Endeavors

In addition to the major initiatives, the in-person gathering facilitated progress on a wide array of other crucial areas. Teams worked on enhancing test harnesses, significantly compressing Hive feedback loops from hours to minutes. Improvements were made to engine API plumbing, including gossip deduplication, batched calls, and light-client-driven head discovery. Difficult trade-offs regarding client diversity were addressed, alongside numerous other technical topics. A comprehensive list of session notes is publicly available at soldogn.xyz.

Next Steps for Ethereum Development

Following the productive Soldægn Interop, development teams will now focus on transforming the week’s prototypes into production-ready code. The coming weeks will be characterized by intensive efforts to harden client implementations against the new specifications, finalize test coverage, and integrate the draft Pull Requests from Soldægn into the main codebase.

As is customary, final decisions on key values, such as the 200 million gas limit target and specific repricing numbers, will be formally announced and shared publicly during All-Core-Developers calls. These discussions are expected to be the central focus of upcoming developer meetings.

The success of Soldægn Interop is a testament to the dedication and collaborative spirit of the Ethereum core development community. The contributions made under the Arctic sun have significantly advanced the network’s scalability roadmap, ensuring a more robust and efficient future for the Ethereum ecosystem. The forthcoming documentary promises to offer a compelling visual narrative of this critical phase in Ethereum’s ongoing evolution.

July 20, 2026 0 comment
0 FacebookTwitterPinterestEmail
Newer Posts
Older Posts

Recent Posts

  • Ethereum Foundation’s Trillion Dollar Security initiative explores native transaction assertions to combat blind signing and outcome uncertainty.
  • Outlier Ventures and Injective Unveil the Injective Ecosystem Builder Catalyst Cohort to Accelerate Institutional-Grade Decentralized Finance
  • Outlier Ventures and Injective Unveil the Injective Ecosystem Builder Catalyst Cohort to Accelerate Institutional-Grade Decentralized Finance
  • Dutch Authorities Arrest Convicted Cybercriminal Linked to ShinyHunters as International Hackers Launch Unprecedented Retaliation
  • Web3 Venture Capital Surges to $7.2 Billion in September 2025 as Late-Stage Deals and Token Megarounds Dominate the Landscape

Recent Comments

No comments to show.
  • Facebook
  • Twitter

@2021 - All Right Reserved. Designed and Developed by PenciDesign


Back To Top
Dr Crypton
  • Home
  • About Us
  • Contact Us
  • Cookies Policy
  • Disclaimer
  • DMCA
  • Privacy Policy
  • Terms and Conditions

We are using cookies to give you the best experience on our website.

You can find out more about which cookies we are using or switch them off in .

Dr Crypton
Powered by  GDPR Cookie Compliance
Privacy Overview

This website uses cookies so that we can provide you with the best user experience possible. Cookie information is stored in your browser and performs functions such as recognising you when you return to our website and helping our team to understand which sections of the website you find most interesting and useful.

Strictly Necessary Cookies

Strictly Necessary Cookie should be enabled at all times so that we can save your preferences for cookie settings.