• Home
  • About Us
  • Contact Us
  • Cookies Policy
  • Disclaimer
  • DMCA
  • Privacy Policy
  • Terms and Conditions
Dr Crypton
Secure Your Future in Crypto
Cybersecurity & Hacking

Dangerous LastPass Authenticator Impersonation Campaign Deploys Kernel-Level Malware to Bypass Security Defenses

by admin September 21, 2026
written by admin

A sophisticated malware campaign masquerading as a legitimate LastPass Authenticator installer has been identified by researchers from LastPass and Delphos Labs, revealing a critical security vulnerability that exploits the trust Windows places in signed hardware drivers. The malicious campaign, which surfaced in late summer 2024, utilizes a deceptive GitHub repository to lure unsuspecting users into downloading a file that, once executed, installs a kernel-level driver capable of systematically disabling antivirus and endpoint detection and response (EDR) software. This high-level compromise allows an information-stealing payload—dubbed "Rapuncel"—to harvest sensitive data, including browser-stored credentials, cryptocurrency wallets, and session tokens for platforms such as Discord, Steam, and Telegram.

The Anatomy of the Deception

The attackers behind this operation demonstrated a high degree of technical proficiency in both search engine optimization (SEO) and malware delivery. By creating a fraudulent GitHub repository titled "LastPass-Authenticator," the threat actors effectively manipulated search engine rankings. When users searched for "LastPass Authenticator download," the malicious site often appeared as a top result, mimicking the professional aesthetic of an official product page.

The delivery mechanism is a classic example of social engineering combined with advanced evasion techniques. Upon clicking the download button on the fake GitHub page, users are redirected through a series of intermediary pages before being served a large ZIP archive. These archives, typically ranging between 127 MB and 148 MB, are intentionally padded with "junk" files to ensure they bypass the file-size scanning limits imposed by many automated security gateways and email filters.

Once the archive is extracted, the victim is presented with a folder containing two critical files: a renamed copy of the legitimate Microsoft debugging tool vsdbg.exe and a malicious file named vsdbg.dll. The infection relies on a technique known as "DLL side-loading." When the user runs the executable, the Windows operating system inadvertently loads the malicious DLL from the same directory, granting the attacker the ability to escalate privileges to the SYSTEM level—the highest possible authority on a Windows machine.

The Role of the Kernel Driver

The most alarming aspect of this campaign is the deployment of a kernel driver, identified by researchers as Alinubx.sys. Because a kernel driver operates at a level deeper than traditional security software, it is uniquely positioned to neutralize defensive measures. Upon execution, the driver references a pre-configured list of 145 known security processes and antivirus programs, forcibly terminating any that are found running on the host system.

Fake LastPass Authenticator Installer Abuses Microsoft-Signed Driver to Kill Antivirus and EDR

The driver itself is a rebadged version of CcProtect.sys, a component of the Chinese disk-encryption software CnCrypt. While the original driver was already documented in the LOLDrivers catalog—a database tracking legitimate drivers that can be abused for malicious purposes—the threat actors successfully evaded detection by renaming the file and altering its metadata. By submitting this altered driver through the Microsoft Windows Hardware Compatibility Publisher chain, the attackers obtained a legitimate signature. This signature provides a false sense of security, as Microsoft’s attestation process confirms that a driver passed through a validation pipeline, but it does not perform a functional analysis to determine if the driver’s behavior is inherently malicious.

Chronology of the Threat

The emergence of this threat highlights a persistent issue in software supply chain security. According to investigations by Delphos Labs, the driver was signed in March 2023, suggesting that the campaign may have been in development or preparation for a significant duration before being deployed in the wild.

  • August 19, 2024: Researchers at Delphos Labs identified the malicious driver and officially reported it to Microsoft, identifying its potential for abuse and its capability to disable security products.
  • August 20, 2024: Internal assessments by Delphos confirmed that the driver was not present on Microsoft’s official vulnerable driver blocklist, nor were there any detection flags on platforms like VirusTotal at the time of the investigation.
  • September 17, 2024: LastPass and Delphos Labs jointly disclosed the findings to the public, confirming that while the attackers leveraged the LastPass brand, no internal LastPass systems, services, or customer vaults were compromised during the incident.

The "Bring Your Own Vulnerable Driver" (BYOVD) Paradigm

This incident underscores the growing prevalence of "Bring Your Own Vulnerable Driver" (BYOVD) attacks. By leveraging legitimate, signed drivers, attackers can bypass modern security features like Kernel Mode Code Signing (KMCS), which typically prevents unsigned code from executing in the Windows kernel. Because the driver is signed by a trusted publisher, the operating system permits its installation and execution, essentially granting the malware the "keys to the kingdom."

The fact that the driver is not currently on Microsoft’s blocklist is a significant point of concern for security professionals. Microsoft’s blocklist, which is active by default in Windows 11, relies on known file hashes. Because attackers can easily recompile or modify these drivers to generate new hashes, the blocklist often lags behind the threat landscape. Microsoft has maintained that the driver does not strictly meet its definition of a security vulnerability, as the component itself is third-party software, placing the onus on third-party security vendors and system administrators to manage driver-level policies.

Implications for Data Security

Once the defensive wall of the EDR and antivirus software is dismantled, the Rapuncel stealer acts with relative impunity. It systematically scans the infected machine for sensitive information. A primary target is the browser-stored credential database. Modern browsers like Google Chrome and Microsoft Edge utilize app-bound encryption to protect saved passwords; however, the Rapuncel stealer circumvents this by injecting code directly into the browser process, requesting that the browser’s own authenticated services perform the decryption.

In addition to browser credentials, the malware targets:

Fake LastPass Authenticator Installer Abuses Microsoft-Signed Driver to Kill Antivirus and EDR
  • Cryptocurrency Wallets: Locating and exfiltrating wallet files that grant access to digital assets.
  • Session Tokens: Hijacking login sessions for applications such as Discord, Telegram, and Steam, allowing attackers to bypass multi-factor authentication (MFA) and assume the identity of the user.
  • Credential Manager: Scraping sensitive data stored within the Windows Credential Manager.
  • Targeted File Search: Searching specifically for files with keywords like "password," "seed," or "recovery" to capture private keys and recovery phrases.

Remediation and Best Practices

The severity of this compromise cannot be overstated. Because the malware operates at the kernel level and re-infects the system upon every reboot, standard removal tools are often ineffective. Researchers strongly advise that any machine confirmed to have run the fake installer be treated as fully compromised.

For victims, the remediation steps are stringent:

  1. Isolate the Device: Immediately disconnect the affected machine from the internet to prevent further exfiltration of data.
  2. Assume Total Compromise: Treat all credentials stored on the machine as exposed.
  3. Perform Remediation from a Clean Device: Use a separate, uncompromised computer to change all passwords, particularly for primary accounts (email, banking, and cloud storage) and to reset 2FA seeds where applicable.
  4. Forensic Rebuild: Due to the kernel-level persistence of the driver, the most secure course of action is to perform a full wipe and reinstallation of the operating system.

Broader Landscape and Industry Response

This campaign is not an isolated event. It is part of a larger, ongoing trend of attackers using GitHub as a distribution platform for malware. Reports from organizations like Trend Micro and Arctic Wolf have previously identified hundreds of repositories disguised as legitimate software, ranging from game cheats to productivity tools, all designed to deliver similar information-stealing payloads.

The use of the Cruciferra crypter—a modular tool often sold on underground forums—further suggests that the attackers are using professional-grade "Malware-as-a-Service" (MaaS) infrastructure. As threat actors continue to innovate in their use of signed drivers and SEO manipulation, the responsibility falls on both software providers and end-users to remain vigilant. Defenders are encouraged to monitor for unusual kernel-mode activity and to employ strict application control policies that limit the installation of drivers to those explicitly approved by organizational IT departments.

As the industry grapples with the limitations of driver-signing trust models, this incident serves as a stark reminder that digital trust is not synonymous with digital safety. Users are urged to download software exclusively from official, verified domains and to exercise extreme caution when navigating search results that promote "download" links for popular software, particularly when hosted on public code repositories.
September 21, 2026 0 comment
0 FacebookTwitterPinterestEmail
Bitcoin & Altcoins

Pcaversaccio Joins the Ethereum Foundation Board as the Organization Strengthens Its Commitment to Cypherpunk Values

by admin September 21, 2026
written by admin

The Ethereum Foundation (EF), the non-profit organization dedicated to supporting the Ethereum protocol and ecosystem, has officially appointed pcaversaccio—a prominent security researcher and long-time contributor—to its Board of Directors. This strategic appointment marks a significant shift in the Foundation’s governance structure, signaling a reinforced focus on the core tenets of decentralization, privacy, and proactive security. By integrating a figure deeply rooted in the "cypherpunk" movement, the EF aims to align its long-term stewardship more closely with the foundational ethos of the Ethereum network.

The current composition of the Board now features Aya Miyaguchi as President, co-founder Vitalik Buterin, Swiss counsel Patrick Storchenegger, and the newly appointed pcaversaccio. This leadership cohort is tasked with overseeing the Foundation’s strategic trajectory, ensuring that high-level operational decisions remain consistent with the EF’s core values and legal requirements as a Swiss-based entity.

A Legacy of Security and Advocacy

The appointment of pcaversaccio is not a departure from his previous work but rather a formalization of his long-standing influence within the Ethereum ecosystem. Known widely in the community by his handle "pc," he has been a pivotal force in the realm of protocol security and privacy preservation.

Most notably, pcaversaccio serves as a co-founder and lead of SEAL 911 (Security Alliance), an emergency response network designed to assist protocols and users during active security threats. His work with the Security Alliance has been instrumental in mitigating the impact of exploits and providing a coordinated defense mechanism for the decentralized finance (DeFi) sector. Furthermore, his membership in the EF’s Silviculture Society—a collective providing informal, expert counsel to the Foundation—has allowed him to exert influence on the preservation of Ethereum’s "heart and soul," specifically regarding censorship resistance and open-source integrity.

His intellectual contributions have been equally influential. In 2024, pcaversaccio authored The Ethereum Cypherpunk Manifesto, a modern adaptation of Eric Hughes’ foundational text. The document serves as a bridge between the early internet-era privacy movement and the contemporary challenges facing decentralized ledgers. This was followed in 2025 by Ethereum Privacy: The Road to Self-Sovereignty, a publication that outlines the technical and philosophical hurdles to achieving truly private transactions in a transparent blockchain environment.

Governance and the EF Mandate

The role of the Ethereum Foundation Board has evolved significantly since the organization’s inception. Following the publication of the "EF Mandate" earlier this year, the Board’s responsibilities have been clearly delineated to provide a framework for accountability. The Board acts as a high-level oversight body, ensuring that management’s strategies—which include resource allocation, grant distribution, and research initiatives—align with the Foundation’s mission.

As a Swiss foundation, the EF is bound by specific legal obligations that require a robust governance structure. The Board serves not only as a strategic vision-setting body but also as a compliance anchor. By bringing on pcaversaccio for an initial one-year voluntary term, the Foundation is effectively institutionalizing the role of "guardian of values." This move is seen by industry observers as a defensive measure to ensure that, as Ethereum scales and interacts with global financial institutions, the underlying principles of the network are not compromised by regulatory or commercial pressures.

The Cypherpunk Renaissance

To understand the implications of this appointment, one must look at the broader context of the Ethereum ecosystem’s evolution. Since the transition to Proof-of-Stake (PoS) in 2022, Ethereum has faced increasing scrutiny regarding its decentralization metrics and its susceptibility to censorship. Regulatory bodies worldwide have scrutinized the role of validators, MEV-boost (Maximal Extractable Value) relays, and the centralized nature of some infrastructure providers.

The inclusion of an outspoken advocate for privacy and cypherpunk ideals suggests that the EF is prioritizing a "back to basics" approach. Analysts note that while Ethereum has become a massive economic engine, the technical challenges regarding privacy—such as the integration of Zero-Knowledge proofs and the protection of user data—remain unfinished business. By appointing a researcher whose primary focus is the technical advancement of privacy-preserving tools, the Board is signaling that "Self-Sovereignty" is a top-tier objective for the coming years.

Supporting Data and Ecosystem Growth

The scale of the Ethereum ecosystem today dwarfs that of its early years, making the Board’s oversight function more critical than ever. As of Q1 2025, the Ethereum network supports thousands of decentralized applications (dApps), a total value locked (TVL) in the tens of billions of dollars, and a validator set exceeding one million active participants.

Managing this growth while maintaining the network’s original security model requires a delicate balance. The EF’s recent focus on the "Silviculture Society" and similar advisory groups highlights a realization that decentralized networks require more than just code; they require a "culture of resistance."

Data from the Security Alliance indicates that the frequency and sophistication of smart contract exploits have increased in tandem with the network’s value. The integration of a security-first leader like pcaversaccio into the Board is a direct response to this threat landscape. It provides a feedback loop between the front lines of incident response (SEAL 911) and the highest level of governance (the EF Board).

Strategic Implications for the Future

The appointment is largely viewed as a stabilizing force. Within the crypto-industry, there is often a tension between the need for institutional adoption and the desire to maintain the permissionless nature of blockchain technology. The EF Board, by balancing the experience of long-time leaders like Buterin and Miyaguchi with the ideological rigor of pcaversaccio, creates a multi-generational governance model.

  1. Focus on Privacy: The focus on "The Road to Self-Sovereignty" implies that the Foundation may increase funding and structural support for privacy-preserving research, such as Stealth Addresses, ZK-rollups, and decentralized identity solutions.
  2. Security Resilience: The connection to SEAL 911 suggests a more formal integration of emergency response protocols into the EF’s broader strategy, potentially leading to faster deployment of security patches and better coordination between the Foundation and infrastructure providers.
  3. Values-Based Stewardship: The "Silviculture Society" model suggests that the EF is moving toward a more decentralized form of governance where experts from the community are given a seat at the table, potentially serving as a blueprint for other decentralized organizations looking to maintain their ethos while scaling.

Industry Reception and Expectations

While the Foundation has not released specific internal transcripts regarding the deliberation process, the community reaction to the appointment has been overwhelmingly positive. Developers and researchers within the Ethereum ecosystem have praised the choice as a validation of the "builder-first" culture that has historically defined the Foundation.

"pc represents the bridge between the old guard of cypherpunks and the new generation of Ethereum developers," noted one anonymous researcher familiar with the Foundation’s inner workings. "He doesn’t just talk about decentralization; he writes the code, manages the incident response teams, and publishes the manifestos that keep us focused on why we are doing this in the first place."

As pcaversaccio begins his one-year term, the industry will be watching to see how his influence manifests in the Foundation’s upcoming grant cycles and strategic roadmap. The mandate is clear: the Ethereum Foundation must ensure that the technical complexity of the protocol does not outpace its philosophical commitment to the principles of open-source software and personal autonomy.

In the coming months, the Foundation is expected to provide further updates on how this board appointment will influence its specific research initiatives. For now, the move serves as a clear signal that the Ethereum Foundation is doubling down on its commitment to its foundational values, even as it navigates an increasingly complex global regulatory environment. The inclusion of pcaversaccio is not merely an administrative update; it is a declaration of intent to preserve the cypherpunk legacy in a post-commercialization era of blockchain technology.

September 21, 2026 0 comment
0 FacebookTwitterPinterestEmail
Cryptography & Privacy

Apple iMessage Security Gaps Leave Users Exposed Despite Advanced Encryption Protocols

by admin September 21, 2026
written by admin

In an era where digital privacy is increasingly intertwined with personal security and professional survival, prominent cryptographers and cybersecurity experts are raising urgent concerns about a glaring omission in Apple’s flagship messaging platform, iMessage. While Apple has long championed its end-to-end encryption and recently integrated cutting-edge post-quantum cryptography into its communication architecture, the platform lacks a fundamental privacy tool that has become an industry standard across almost every other major messaging application: disappearing messages.

This security gap has profound implications for everyday users, particularly public servants, political workers, and private citizens navigating a volatile sociopolitical landscape where digital communications can be weaponized against them. As modern surveillance practices, data harvesting, and device searches become more pervasive, the inability to automatically purge sensitive conversations poses a critical risk to user safety.

Dear Apple: add “Disappearing Messages” to iMessage right now

The Core Vulnerability: Transit Security Versus Endpoint Retention

To understand the current debate, industry analysts emphasize the distinction between data security in transit and data retention at the endpoint. Apple’s iMessage has utilized end-to-end encryption (E2EE) since 2011. This cryptographic framework ensures that messages and attachments are scrambled using keys inaccessible to Apple, protecting data as it travels across networks. Furthermore, Apple bolstered this architecture by introducing PQ3, a post-quantum cryptographic protocol designed to safeguard communications against theoretical future quantum computing threats.

However, cryptographers point out that uncompromising transit encryption is only half the equation. Once an encrypted message is successfully delivered and decrypted on a recipient’s device, it is stored locally. By default, iMessage retains chat histories indefinitely. Combined with standard device backups and cloud-syncing features, this turns an iPhone into a permanent archive of a user’s personal life, professional discussions, and political thoughts.

Dear Apple: add “Disappearing Messages” to iMessage right now

An individual searching their iMessage history can frequently retrieve transcripts dating back a decade. While historical record-keeping is convenient for casual chats, it transforms messaging archives into high-liability databases. In environments where private text messages are routinely scrutinized, subpoenaed, or exposed via physical device access, indefinite retention strips users of practical confidentiality.

Industry Standards and the Disappearing Message Deficit

The absence of native, per-conversation disappearing messages in iMessage is an anomaly within the modern consumer software ecosystem. Competitors across the spectrum—including Signal, WhatsApp, Meta Messenger, Snapchat, and even Telegram—have implemented ephemeral messaging controls for years.

Dear Apple: add “Disappearing Messages” to iMessage right now

Typically, these features allow users to establish an expiration timer for chats, ranging from five minutes to 90 days. Once the predetermined window closes, the messages are automatically erased from both the sender’s and the recipient’s devices. Moreover, robust implementations of disappearing messages ensure that expired content is excluded from automated cloud backups, reinforcing the core premise that the conversation was never intended to be archived.

Despite repeated calls from cybersecurity researchers and privacy advocates, Apple has declined to introduce a comparable, thread-specific disappearing message feature. While iOS does include a global setting under device preferences labeled Keep Messages—allowing users to limit message retention to one year instead of indefinitely—the option has significant limitations. It operates universally rather than per chat, it does not purge messages from communication partners’ devices, and opting for a shorter retention window forces users to sacrifice older, non-sensitive conversation histories they may wish to preserve.

The Illusion of Security: iCloud Backups and Advanced Data Protection

Dear Apple: add “Disappearing Messages” to iMessage right now

Compounding the issue of message retention are complexities surrounding Apple’s cloud backup infrastructure. Apple offers a feature known as Messages in iCloud, designed to sync and back up chat databases across multiple Apple devices associated with a single user account. While Apple promotes this feature as end-to-end encrypted, technical audits reveal critical nuances that can mislead consumers.

By default, standard iCloud backups store the encryption keys required to access Messages in iCloud databases on Apple’s servers in a format accessible to the company. Consequently, law enforcement agencies armed with a valid subpoena—or unauthorized actors who compromise an Apple ID password—can potentially reconstruct a user’s entire message history from cloud servers.

Apple does provide a remedy through its Advanced Data Protection (ADP) feature, which extends end-to-end encryption to iCloud backups, preventing even Apple from accessing stored keys. While activating ADP significantly hardens cloud security, it remains an opt-in setting that the vast majority of mainstream consumers leave disabled due to user friction and the risk of permanent data lockout if account recovery keys are lost. Even when ADP is enabled, however, it merely protects backups; it does not solve the underlying problem of messages persisting indefinitely on local hardware.

Dear Apple: add “Disappearing Messages” to iMessage right now

Chronology of Apple Security Developments

To contextualize Apple’s current cryptographic posture, industry observers look back at a steady evolution of platform security enhancements over the past decade and a half:

  • 2011: Apple introduces end-to-end encryption for iMessage, ensuring third parties and network intermediaries cannot intercept messages in transit.
  • 2016: Security researchers uncover and publicly disclose cryptographic implementation flaws in the iMessage protocol, which Apple patches rapidly.
  • 2022: Apple rolls out Advanced Data Protection for iCloud, enabling optional end-to-end encryption for device backups, photos, and messages.
  • 2024: Apple introduces the PQ3 protocol, upgrading iMessage to post-quantum cryptographic standards to future-proof against quantum decryption attacks.
  • 2025: Privacy advocates and cryptography engineers renew public appeals for native disappearing message controls, highlighting the disconnect between futuristic transit security and static endpoint retention.

Implications for Users and Industry Pressures

Dear Apple: add “Disappearing Messages” to iMessage right now

The persistence of legacy message retention models places Apple at odds with evolving privacy expectations. For government employees, whistleblowers, journalists, and everyday citizens operating in polarized political climates, the threat landscape has shifted. Digital security is no longer merely about thwarting sophisticated nation-state hackers or bulk data collection agencies; it is increasingly about mitigating the fallout from local device seizures, compromised accounts, and social retaliation based on archived personal communications.

When technology platforms fail to provide ephemeral communication options, they inadvertently shift the burden of risk onto the user. Critics argue that a company that prides itself on marketing privacy as a "fundamental human right" should provide the tools necessary to ensure that private conversations remain genuinely private.

Internal hesitation within Apple regarding privacy features often stems from balancing user data loss anxiety against security upgrades. When pressed on why robust security features like end-to-end encrypted backups are not enabled by default, Apple engineers frequently cite user fear of permanent data loss and the operational challenges of managing zero-knowledge account recovery. However, when questioned about the absence of disappearing messages—an optional feature that users explicitly choose to activate—industry insiders offer few technical justifications. Observers speculate that corporate caution, regulatory pressure from law enforcement agencies, or entrenched legacy codebase limitations may be contributing factors, though none have been officially confirmed.

Dear Apple: add “Disappearing Messages” to iMessage right now

Broader Impact and Future Outlook

As the debate over digital civil liberties continues to shape the technology sector, consumer expectations are shifting toward default-private architectures. Ephemeral messaging is no longer viewed as a niche tool for clandestine operations; it is recognized as a vital hygiene practice for digital communication in an era of ubiquitous data storage and aggressive surveillance.

For Apple, the path forward involves reconciling its advanced cryptographic achievements—such as PQ3 and Advanced Data Protection—with practical, user-centric privacy controls. Until native, flexible disappearing message functionality is integrated into iMessage, millions of users will remain vulnerable to the unintended permanence of their own digital footprints, leaving a noticeable void in an otherwise robust security ecosystem.

September 21, 2026 0 comment
0 FacebookTwitterPinterestEmail
FinTech Innovations

FintechOS Secures $28 Million in Combined Debt and Equity to Accelerate Global Expansion and US Market Penetration

by admin September 21, 2026
written by admin

Fintech enablement platform FintechOS has successfully closed a $28 million financing round, consisting of a strategic mix of equity and debt, to propel its aggressive expansion plans into the United States market and deepen its footprint across Europe. This latest infusion of capital brings the company’s total funding raised since its inception in 2017 to $178.9 million, marking a significant milestone in its transition from a high-growth startup to a profitable, enterprise-scale provider of financial technology solutions.

The equity portion of the funding was provided by a consortium of existing investors, including Bek Ventures, the International Finance Corporation (IFC), Cipio Partners, and Molten Ventures. Complementing this, Santander CIB provided a debt facility, a financial instrument that reflects the company’s newfound fiscal maturity and stable balance sheet.

A Strategic Pivot Toward Sustainable Growth

The recent funding round represents a pivotal shift for the London-headquartered firm. Having spent the preceding years meticulously refining its operational efficiency, cost structure, and margins, FintechOS has successfully reached profitability. This trajectory stands in contrast to many firms in the fintech sector that prioritize "growth at all costs." By achieving profitability first, the company has positioned itself to scale without the existential risks often associated with rapid expansion.

Teo Blidarus, Founder and CEO of FintechOS, emphasized that the decision to pursue this specific funding mix was calculated. "Santander CIB’s support, alongside other investors that trust us, is a strong vote of confidence in the path we’re on," Blidarus stated. "It gives us the capital to go after the extraordinary potential we see ahead, particularly in the US, without compromising the discipline that got us to profitability in the first place."

Cyril Desouza, CFO of FintechOS, echoed these sentiments, noting that the company’s current financial health is the result of a deliberate, multi-year strategy. "Reaching profitability was not an accident; it was the outcome of a deliberate, multi-year effort to get our cost base, our margins, and our delivery practice right before we pushed harder on growth again," Desouza explained. "Now that discipline is paying off twice over: the business has reached profitability, and we’ve already made the shift back into high growth, which is exactly the combination that lets us take on a round like this one."

The Evolution of FintechOS: A Timeline of Growth

Since its founding in 2017, FintechOS has navigated the complex landscape of financial services by focusing on the "plumbing" of the banking industry. The company provides a low-code enablement platform that allows financial institutions to deploy new products and services rapidly, bypassing the need for cumbersome, legacy-system overhauls.

  • 2017: FintechOS is founded with the mission to accelerate digital transformation for retail and commercial banks.
  • 2019-2021: The company focuses on scaling its core technology, the "Unified Origination" tool, and expanding its presence across European markets.
  • 2022-2024: A period of internal restructuring begins, with a focus on unit economics, sustainable margins, and achieving EBITDA-positive status.
  • 2026 (Year-to-Date): FintechOS reports a 40% increase in recurring revenue and a 102% year-over-year growth in operational EBITDA. The company also marks a 130% expansion in its US operations, with plans to add over 20 new banking clients by the end of the year.

Technological Impact: Modernizing Legacy Infrastructure

At the heart of the FintechOS value proposition is its ability to integrate with existing banking stacks. Rather than forcing financial institutions to "rip and replace"—a process that is notoriously expensive, risky, and time-consuming—FintechOS offers a modular, low-code architecture.

The company’s flagship product, Unified Origination, is an AI-first, cross-product origination solution designed specifically to help retail and commercial banks shorten the time-to-market for new credit and account offerings. By abstracting the complexity of back-end legacy systems, the platform enables banks to launch customer-facing products in weeks rather than months or years. Additionally, the company serves the insurance sector with a composable core product, further diversifying its revenue streams and proving the versatility of its underlying technology.

Market Implications and Competitive Landscape

The decision to incorporate debt capital alongside equity is a signal to the market that FintechOS has moved beyond the "venture-dependent" phase of its lifecycle. Debt financing is typically more accessible to companies with predictable, recurring revenue streams and a clear path to profitability. By choosing this route, FintechOS avoids the excessive dilution of its equity holders while maintaining the financial agility required for international expansion.

In the US market, FintechOS is entering a crowded but high-demand space. Financial institutions across North America are under intense pressure to modernize their digital interfaces and back-end processes to compete with agile neobanks and digital-first incumbents. The demand for "composable banking"—the ability to swap out or add specific banking functions without retooling an entire system—is rising, and FintechOS is positioning itself as a primary enabler of this trend.

Analysis: The Future of Fintech Enablement

Industry observers note that the success of FintechOS highlights a broader trend in the financial technology sector: the shift from "disruption" to "enablement." In the early 2010s, the goal of many fintechs was to displace traditional banks. Today, the focus has shifted toward providing the tools that allow traditional institutions to survive and thrive in a digital-first economy.

The firm’s ability to secure a debt facility from a major global player like Santander CIB underscores the institutional credibility it has built. It also serves as a benchmark for other growth-stage fintechs that are looking to move toward IPO-readiness or long-term sustainability. By focusing on the "middle layer" of banking infrastructure, FintechOS has insulated itself from the volatility of consumer-facing fintech products, building instead on the long-term, sticky relationships inherent in enterprise software.

Looking Ahead: The 2026 Milestone

The projections for 2026 are ambitious. With a client acquisition goal of over 20 new banks for its FintechOS 8 platform, the company is aiming to solidify its status as a standard-bearer for low-code banking solutions. The expansion into the US is not merely a geographic growth strategy; it is a strategic move to capture market share in a region where banks are increasingly willing to spend on modernization to combat declining customer loyalty and high operational costs.

As the company prepares to deploy the $28 million in capital, the focus will likely remain on enhancing its AI capabilities and scaling its sales and customer success teams in North America. For banks, the entry of a well-capitalized, proven, and profitable provider like FintechOS into the US market offers a viable alternative to traditional consultancy-heavy digital transformations.

The successful closing of this funding round at this specific time is indicative of a maturing market. Investors are increasingly favoring companies that demonstrate not only technological innovation but also the operational rigor to sustain that innovation through varying economic cycles. As FintechOS continues its expansion, the industry will be watching to see if this "discipline-first" approach to scaling can effectively translate into market dominance in the world’s most competitive financial hub.

September 21, 2026 0 comment
0 FacebookTwitterPinterestEmail
FinTech Innovations

Former xAI and Google Engineer Tina Oberoi Targets $50 Million Seed Funding for Anti-Deepfake Startup Moir at a $250 Million Valuation

by admin September 21, 2026
written by admin

The artificial intelligence boom has ushered in an era of unprecedented productivity and innovation, but it has simultaneously unlocked a Pandora’s box of digital deception. As generative tools evolve from clunky novelties into sophisticated, hyper-realistic engines capable of cloning human faces, voices, and behaviors in real-time, the boundary between authentic human interaction and synthetic fabrication has dissolved. Addressing this existential crisis of digital trust, Tina Oberoi, a veteran machine learning engineer with high-profile tenures at both xAI and Google, is positioning herself at the forefront of the counter-offensive.

According to industry reports emerging in late September 2026, Oberoi is actively engaged in early-stage capital-raising talks to secure $50 million in seed funding for her nascent venture, Moir. The proposed funding round values the stealth-mode startup at an eye-watering $250 million—a testament to the immense investor appetite for robust infrastructure capable of authenticating human identity in a world saturated by synthetic media. Moir’s core mission centers on developing cryptographic and verification frameworks that empower everyday individuals to unequivocally prove their identity online, thereby neutering the threat vector posed by malicious deepfakes.

Despite the significant market chatter surrounding the nascent company, representatives for Moir have maintained a strict posture of silence, declining to comment on the fundraising negotiations or the technical architecture powering the platform. Nevertheless, the mere whisper of Oberoi’s involvement has sent ripples through both the venture capital ecosystem and the broader cybersecurity landscape.

The Rise of Moir: Founder Background and Professional Pedigree

The credibility driving Moir’s astronomical seed valuation stems largely from Tina Oberoi’s impressive technical lineage. Her professional footprint bridges major tech titans and positions her at the bleeding edge of modern artificial intelligence development.

Prior to setting her sights on entrepreneurial endeavors—signaling her pivot on social platform X with the succinct biography line "building something new"—Oberoi spent eight intensive months at Elon Musk’s xAI. During her tenure at the cutting-edge AI laboratory, her work focused heavily on post-training protocols and human data optimization for multimodal models, specifically contributing to the refinement of the Grok 3 and Grok 4 architectures. This insider perspective on how frontier large multimodal models are trained, tuned, and coaxed into mimicking human outputs provides her with a rare tactical advantage in building detection and verification tools designed to outsmart those very same models.

Before her time at xAI, Oberoi spent five formative years at Google. Her career trajectory within the search giant saw her transition from a traditional software engineer into a customer engineer specializing in data and artificial intelligence infrastructure. This dual background—combining deep foundational training in distributed software systems with hands-on experience in generative AI post-training—provides a formidable foundation for tackling one of the digital age’s most complex security challenges.

The Deepfake Epidemic: A Crisis of Digital Forensics

Moir enters a market in the throes of a full-scale security emergency. For years, digital forensics experts relied on subtle visual anomalies—such as unnatural blinking patterns, lighting inconsistencies, or audio artifacts—to unmask synthetic media. However, the relentless velocity of generative AI research has rendered traditional forensic methodologies nearly obsolete.

Research published earlier in 2026 revealed a grim reality: the vast majority of ordinary citizens can no longer reliably distinguish between authentic photographs, video footage, or voice recordings and their AI-generated counterparts. More alarmingly, the technology has advanced to a point where seasoned digital forensics experts openly harbor doubts regarding their own analytical capabilities. When the professionals whose life work is authentication can no longer trust their senses, the foundational pillar of digital verification collapses.

This technological leap has translated into an unprecedented wave of corporate and consumer cybercrime. In April 2026, cybersecurity firm CybelAngel published alarming data compiled by Keepnet Labs, documenting a staggering 1,600% surge in deepfake-enabled vishing (voice phishing) attacks across the United States during the first quarter of 2025 compared to the final quarter of 2024. Fraudsters are no longer relying solely on phishing emails or static text messages; they are cloning the voices of corporate executives, family members, and trusted advisors in real-time, executing high-stakes financial fraud with chilling precision.

The Macroeconomic Toll: FBI Data and Corporate Vulnerabilities

The financial fallout of this synthetic crime wave is meticulously documented in official law enforcement metrics. The Federal Bureau of Investigation’s (FBI) 2025 Internet Crime Report cataloged over 22,000 distinct AI-related fraud complaints, with cumulative financial losses exceeding an astonishing $893 million. These figures reflect only reported crimes, suggesting the true economic drain on individuals and enterprises is significantly higher.

Enterprise organizations are finding themselves directly in the crosshairs of this evolutionary threat. Insights from PYMNTS Intelligence, highlighted in the April report titled "Scale Amplification: How Revenue Amplifies Agent-Driven Identity," underscore the gravity of the situation. According to the research, 47% of firms generating between $50 million and $250 million in annual revenue—alongside a staggering 58% of enterprises boasting over $1 billion in annual revenue—successfully detected AI-generated identity documents and deepfakes within their systems over the preceding twelve months.

The report notes a critical structural shift in how cybercriminals operate: "At scale, the attack surface shifts from synthetic identity fraud toward deepfakes and automated scraping, revealing how the composition of agent attacks changes with scale." As organizations scale their digital operations, automated, AI-driven impersonation becomes the weapon of choice for sophisticated threat actors.

A Paradigm Shift for Financial Institutions and Digital Issuers

For financial institutions, payment processors, and identity issuers, the proliferation of deepfakes introduces an agonizing strategic dilemma. Historically, fraud detection systems focused on flagging anomalous transaction patterns, unusual geographic logins, or irregular spending velocity. However, because modern generative AI can seamlessly mimic normal human behavioral patterns, transactional monitoring alone is no longer sufficient.

A September PYMNTS Intelligence report, titled "When Fraud Becomes the Customer: The Next Battlefront for Issuers," emphasized that issuers must fundamentally rethink how trust is established in a digital-first economy. The primary challenge has evolved from simply identifying suspicious transactions to distinguishing genuine customers from convincing imposters—all while avoiding the introduction of friction that drives legitimate users away.

When an adversary can present a live, interactive video feed of a verified human face and a synchronized voice stream generated entirely by algorithms, standard know-your-customer (KYC) protocols crumble. This exact vulnerability forms the market opening that Tina Oberoi and Moir intend to exploit.

Analyzing Moir’s Market Position and Strategic Value

Securing a $250 million valuation at the seed stage is an extraordinary feat, even within the hyper-inflated venture capital environment of the generative AI boom. It signals that institutional investors do not view Moir as a minor software plug-in, but rather as foundational infrastructure for the next generation of the internet.

To justify such a lofty valuation, Moir will likely need to pioneer a decentralized or interoperable identity framework that moves beyond traditional document verification. Rather than asking systems to check if a passport or selfie is real—a game of cat-and-mouse that AI is winning—next-generation identity platforms aim to cryptographically bind human identity to actions from the ground up, ensuring that verified individuals can interact online with mathematical certainty.

However, the path forward is fraught with systemic hurdles. Any identity verification system attempting widespread adoption faces the eternal trade-off between security, privacy, and user accessibility. If Moir’s solution introduces excessive privacy intrusions or heavy operational friction, consumer and enterprise adoption could stall. Furthermore, tech giants like Apple, Google, and Microsoft are aggressively baking native identity credentials and biometric verification safeguards directly into their operating systems and hardware, meaning Moir will need to carve out a distinct, enterprise-grade niche or offer superior cross-platform interoperability to survive.

Conclusion

As Tina Oberoi navigates the final stages of her $50 million seed raise, the launch of Moir underscores a sobering reality of the modern digital landscape: the tools used to verify who we are must evolve just as rapidly as the algorithms designed to impersonate us. With the backing of top-tier investors and informed by her technical mastery gained inside the walls of Google and xAI, Oberoi’s venture represents a formidable, highly anticipated attempt to reclaim the integrity of human identity in an increasingly synthetic world.

September 21, 2026 0 comment
0 FacebookTwitterPinterestEmail
FinTech Innovations

Coordinated Attack on AI Crypto Ecosystem Exposes Vulnerabilities as Fetch.ai and NuNet Suffer $2 Million Loss

by admin September 21, 2026
written by admin

The decentralized artificial intelligence sector experienced a severe security shock on September 19, 2026, when a single malicious on-chain actor executed a sophisticated, multi-pronged exploit targeting two closely related blockchain projects within minutes of each other. The coordinated breach compromised the token conversion infrastructure of Fetch.ai and severely inflated the circulating supply of NuNet, resulting in a combined estimated loss and market damage valued at approximately $2.01 million at the time of the attacks.

Security intelligence firms and blockchain analytics providers tracking the attacker’s wallets reported that the incident highlights systemic vulnerabilities within interconnected Web3 ecosystems. By leveraging compromised administrative privileges or exploiting logical flaws in token management contracts, the perpetrator managed to drain millions of tokens, convert them into highly liquid assets, and trigger cascading market collapses that wiped out substantial portions of the tokens’ market capitalization.

Chronology of the Attack: A Minute-by-Minute Breakdown

The sequence of events unfolded rapidly on the afternoon of September 19, leaving little time for automated security sentinels or protocol developers to intervene. On-chain forensic investigations conducted by prominent security firms such as PeckShield and Blockaid established a precise timeline of the breach.

The first phase of the attack targeted Fetch.ai, a prominent decentralized machine-learning network. At approximately the same time, the malicious cluster initiated a withdrawal from Fetch.ai’s TokenConversionManagerV3 contract deployed on the Ethereum blockchain. The attacker successfully extracted approximately 8.72 million FET tokens without encountering resistance from the smart contract’s validation logic. Depending on the precise price snapshot used at the moment of the extraction, the value of the drained FET tokens was estimated to be between $1.53 million and $1.56 million.

Mere minutes after emptying the Fetch.ai conversion contract, the exact same on-chain actor pivoted to target NuNet, a decentralized computing framework that shares ideological and structural ties within the broader Artificial Superintelligence alliance ecosystem. Using or interacting with NuNet’s primary deployer account, the attacker generated and received a freshly minted batch of roughly 408.5 million NTX tokens. This unauthorized minting event instantly introduced hundreds of thousands of dollars worth of newly created coins into the blockchain ecosystem, effectively bypassing the protocol’s intended tokenomics and governance safeguards.

Following the successful acquisition of both the drained FET tokens and the newly minted NTX tokens, the attacker consolidated the digital assets into a single destination wallet. To obscure the trail and secure the stolen value, the perpetrator rapidly executed a series of decentralized exchange swaps, converting a large share of the ill-gotten tokens into hundreds of Ether. According to telemetry provided by Blockaid and PeckShield, the attacker successfully swapped the assets into roughly 546 ETH, valued at approximately $1.44 million, successfully transitioning the stolen capital into a highly liquid and censorship-resistant asset.

Technical Analysis: Flawed Conversion Logic and Compromised Deployer Rights

Blockchain security auditors examining the mechanics of the exploit have pointed to two distinct vulnerabilities that facilitated the breach. While both events were orchestrated by the same malicious actor, the execution vectors exploited different layers of smart contract architecture.

On the Fetch.ai side of the incident, the vulnerability appeared to reside within the TokenConversionManagerV3 contract. Preliminary forensic findings suggest that the contract accepted a conversion authorization request without appropriately verifying whether matching tokens had been genuinely locked, burned, or verified elsewhere in a cross-chain or multi-token bridge environment. In essence, the smart contract executed a legitimate-looking command issued by the caller, functioning precisely as programmed, but lacking the necessary cryptographic or state-validation checks to prevent unauthorized drains.

Conversely, the NuNet incident was characterized not by a logical error in a conversion contract, but rather by compromised administrative or minting rights on the project’s deployer account. The unauthorized creation of 408.5 million NTX tokens indicates that the attacker either gained access to private signing keys, compromised a multi-sig administrative quorum, or exploited a privilege escalation flaw within the deployer architecture. Because the contract deferred to the commands of a privileged caller, it executed the minting command without secondary validation from the decentralized community or time-locked safety mechanisms.

Market Impact: Divergent Fates for FET and NTX

The financial repercussions of the September 19 breach impacted the two tokens in vastly different ways, reflecting the contrasting nature of a treasury drain versus an existential supply shock.

Fetch.ai’s native asset, FET, experienced an immediate downward price correction as traders and automated market makers priced in the converter failure and a broader loss of confidence surrounding the security of the Artificial Superintelligence alliance infrastructure. Although the loss of 8.72 million FET tokens represented a significant financial blow to the protocol’s reserves, the liquid market for FET was deep enough to absorb the initial shock without collapsing entirely.

In stark contrast, the impact on NuNet’s NTX token was catastrophic. The sudden issuance of 408.5 million new tokens represented an astonishing 42 percent expansion of NuNet’s total circulating supply in a single transaction. This dramatic inflation fundamentally broke the token’s economic model overnight.

As the newly minted tokens hit open markets, trading volume spiked violently, driven not by organic buying interest, but by forced selling, panic liquidations, and desperate attempts by holders to salvage remaining value. Market trackers recorded a devastating collapse in the price of NTX, with valuations plummeting anywhere from 65 percent to more than 90 percent in the hours following the mint. According to select decentralized exchange analytics, the token’s price crashed from approximately $0.0013 down to fractions of a cent as liquidity pools were drained and sell pressure overwhelmed order books.

Broader Industry Implications: The Risks of Interconnected AI Crypto Stacks

The dual exploit has triggered urgent discussions across the decentralized finance and AI crypto sectors regarding the hidden risks of shared infrastructure and allied ecosystems. Projects operating under common alliances or umbrella organizations frequently utilize shared development frameworks, overlapping security practices, or similar administrative key management structures.

Security analysts have emphasized that when administrative privileges—such as those residing in token converters or deployer accounts—are compromised, the blast radius rarely remains contained to a single project. The ability of a single actor to transition seamlessly from a Fetch.ai contract to a NuNet deployer account underscores the dangers of centralized signing authority and highlights the urgent necessity for robust, decentralized key management.

Furthermore, the incident serves as a sobering reminder of the complexities inherent in token conversion managers and cross-chain or multi-asset frameworks. As artificial intelligence protocols increasingly integrate blockchain technology to facilitate decentralized compute, data sharing, and autonomous agent economies, securing the underlying smart contract infrastructure becomes paramount.

Response from Project Teams and Ongoing Investigations

In the wake of the breach, core developers and security teams from both Fetch.ai and NuNet initiated emergency incident response protocols. On-chain monitoring services, centralized exchanges, and decentralized liquidity providers were immediately alerted to blacklist wallets associated with the attacker and freeze suspicious transactions where possible. However, due to the rapid conversion of stolen assets into Ether and the utilization of privacy-enhancing routing mechanisms, recovering the entirety of the funds remains a formidable challenge.

As of publication, affected stakeholders and independent security auditors are conducting comprehensive forensic reviews of the compromised smart contracts and signing infrastructure. Market participants and token holders await formal, detailed post-mortem reports from both project teams outlining the root causes of the key compromises and detailing the security upgrades planned to prevent similar incidents in the future.

Until comprehensive transparency is achieved and security audits verify the integrity of patched deployment pipelines, the market consensus remains cautious. The September 19 incident stands as a defining case study in the vulnerability of modern AI-crypto integration—demonstrating how a single sophisticated operator can exploit structural vulnerabilities across multiple doors, instantly reshaping token economics and inflicting millions of dollars in damages.

September 21, 2026 0 comment
0 FacebookTwitterPinterestEmail
NFT & Digital Assets

The Shifting Tides of Web3: Magic Eden Retreats from EVM and Bitcoin Markets as Rarible Positions Itself for Multichain Consolidation

by admin September 21, 2026
written by admin

The digital asset ecosystem is experiencing a profound structural realignment following a major announcement from Magic Eden, one of the most prominent names in the non-fungible token (NFT) industry. The marketplace has officially confirmed the winding down of its operations across all Ethereum Virtual Machine (EVM) compatible networks and Bitcoin. This strategic retreat marks a definitive turning point for creators, collectors, and high-volume traders who have historically relied on the platform to navigate multi-chain digital economies. Assets and trading activities anchored to Ethereum, Base, Polygon, and several other prominent blockchain networks are now forced to find alternative infrastructure. Amid this sudden displacement, legacy multichain pioneer Rarible has stepped forward, positioning its robust, five-year-old ecosystem as the primary landing zone for displaced market participants.

The decision by Magic Eden to curtail its EVM and Bitcoin marketplace support arrives during a volatile chapter for the broader digital collectibles sector. Once hailed as a hyper-growth frontier of cryptocurrency, the NFT landscape has matured past its speculative genesis, forcing platforms to reckon with hyper-competitive fee structures, shifting liquidity pools, and the high operational costs of maintaining cross-chain infrastructure. Magic Eden, which originally scaled to prominence as a dominant force within the Solana ecosystem before aggressively expanding into Bitcoin ordinals and EVM-compatible chains, appears to be pivoting its focus or consolidating resources in response to these macroeconomic headwinds.

Industry analysts tracking the chronology of the multichain marketplace boom note that the rapid proliferation of Layer 2 networks and alternative base layers between 2021 and 2024 severely fractured liquidity. Platforms attempting to support every emerging network often found themselves stretched thin across fragmented user bases. Magic Eden’s withdrawal underscores the immense difficulty of sustaining universal chain coverage without capturing a definitive, long-term share of daily trading volume. While the marketplace initially gained immense traction by offering user-friendly interfaces for Bitcoin ordinals and Ethereum-based digital art, the sheer overhead of supporting disparate technological stacks—ranging from Bitcoin’s UTXO model to account-based EVM architectures—has evidently compelled a strategic retrenchment.

This sudden market exit immediately impacts thousands of active participants who utilized Magic Eden for listing, bidding, and executing peer-to-peer trades across chains like Ethereum, Base, and Polygon. However, rather than stalling transactional activity, the vacuum left in Magic Eden’s wake has triggered an immediate consolidation phase. Platforms boasting deep historical roots, battle-tested smart contracts, and comprehensive cross-chain aggregation tools are absorbing the displaced capital and user base.

Leading this charge is Rarible, which has operated continuously as a multichain marketplace since 2020. Having weathered multiple distinct crypto market cycles—from the euphoric bull runs of 2021 to the prolonged consolidation periods of subsequent years—Rarible has engineered an infrastructure designed precisely for moments of industry transition. By maintaining a unified interface that supports major EVM networks simultaneously, Rarible eliminates the operational friction of juggling multiple application windows or fragmented wallet configurations.

A structural analysis of the current market reveals several reasons why institutional-grade collectors and independent creators are migrating toward platforms with proven staying power. First, the liquidity aggregation model deployed by established platforms ensures that buyers and sellers have transparent access to cross-platform pricing. Instead of forcing users to check isolated order books on single-chain applications, modern aggregators pull listings from across the ecosystem, guaranteeing optimal price discovery. Second, creator-centric mechanics, such as customizable royalty enforcement and dedicated launchpad suites, have re-emerged as a critical battleground for platform loyalty. During the height of the marketplace fee wars in 2023, many platforms raced to the bottom by making creator royalties optional. Rarible, conversely, has consistently championed a creator-first philosophy, building dedicated architectures—such as the RARI Chain—to ensure that artists retain sustainable revenue models from secondary sales.

The scope of network integration currently available across the surviving multichain infrastructure is vast. For traders migrating away from Magic Eden, continuity of operations depends heavily on the breadth of chain support. Ethereum remains the foundational layer for high-value cultural artifacts and blue-chip digital art collections, commanding the deepest historical liquidity in the industry. Meanwhile, Ethereum Layer 2 networks like Base, incubated by Coinbase, have experienced exponential transaction growth due to lightning-fast settlement times and negligible gas fees, making them the preferred environment for social tokens and high-frequency community drops.

Similarly, Polygon continues to anchor high-volume gaming, brand loyalty programs, and enterprise-grade utility tokens owing to its high throughput and cost-efficiency. Specialized environments, such as RARI Chain—an EVM-equivalent network custom-built for creators with native royalty enforcement—and high-performance execution layers like MegaETH, represent the cutting edge of what next-generation decentralized applications demand. By maintaining deep integration across all these specialized execution environments, platforms like Rarible ensure that users do not have to compromise on speed, cost, or security when migrating their digital assets.

The mechanics of transitioning marketplace activity to a new provider have been intentionally streamlined to prevent market friction. For most users, the migration process requires little more than navigating to the platform interface, connecting an existing Web3 wallet—such as MetaMask, Coinbase Wallet, or other major injected providers—and reviewing pre-existing portfolio holdings. Because blockchain data is decentralized and permissionless, NFTs do not need to be manually bridged or transferred out of personal wallets simply because a frontend marketplace is shutting down; the underlying smart contracts remain secure on-chain. Creators and traders simply need to re-list their assets on a functioning marketplace interface to resume trading activity. Furthermore, incentive structures such as native token rewards ($RARI) have been integrated into daily trading operations, providing active participants with governance rights and platform utility that offset the disruption caused by platform closures.

The broader implications of Magic Eden’s departure from EVM and Bitcoin markets point toward a more mature, consolidated digital asset economy. In the early phases of the Web3 expansion, venture-backed marketplaces frequently engaged in protracted capital burn strategies, subsidizing zero-fee trading to capture market share regardless of profitability. As macroeconomic conditions tightened across both traditional and cryptocurrency sectors, the imperative shifted from speculative expansion to sustainable unit economics. Platforms that relied heavily on speculative trading volume without establishing deep, sticky utility for creators and core collectors are finding it increasingly difficult to justify the engineering and maintenance costs of supporting dozens of disparate blockchains.

Industry stakeholders and market observers note that consolidation is a natural hallmark of technological maturation. Just as early internet browser wars eventually stabilized into a handful of dominant, highly optimized engines, the multichain NFT landscape is rapidly coalescing around platforms that offer robust security audits, reliable uptime, cross-chain flexibility, and unbreakable alignment with content creators. When major players exit a vertical, the remaining infrastructure must absorb not only the transactional volume but also the cultural trust of displaced communities.

For the creators and collectors affected by Magic Eden’s operational pivot, the transition period represents both a logistical hurdle and an opportunity to engage with platforms structurally designed for long-term resilience. As digital ownership expands deeper into gaming, real-world asset tokenization, and cross-chain interoperability, the demand for reliable, multichain infrastructure will only intensify. The ability of legacy marketplaces to seamlessly onboard waves of displaced users will serve as a definitive test of their operational readiness in an increasingly competitive decentralized economy.

September 21, 2026 0 comment
0 FacebookTwitterPinterestEmail
Tech & Startup News

The new iPhone A20 Pro chip benchmark results: Yeah, it’s very, very fast

by admin September 21, 2026
written by admin

Apple’s annual hardware refresh cycle has once again pushed the boundaries of mobile computing performance. Following the commercial launch of the iPhone 18 Pro and iPhone 18 Pro Max, preliminary laboratory tests evaluating the newly integrated A20 Pro processor reveal performance metrics that significantly outpace preceding hardware generations and rival architectures currently available on the consumer market. Built upon an advanced 2-nanometer fabrication node, the silicon powering Apple’s latest flagship lineup demonstrates unprecedented capabilities in both synthetic and computational processing workloads, cementing the company’s long-standing dominance in mobile chip design.

The new iPhone A20 Pro chip destroys the competition in benchmarks

Technical Architecture of the A20 Pro

To understand the scale of the performance leap demonstrated in recent benchmarks, one must examine the physical architecture of the A20 Pro. Fabricated using cutting-edge 2-nanometer process technology—a milestone that shrinks transistors to molecular scales to maximize energy efficiency while boosting raw compute power—the processor layout is carefully engineered for hybrid workloads.

The system-on-a-chip (SoC) features a redesigned 6-core central processing unit (CPU) configuration, comprising two high-performance "super cores" designed for intensive tasks and four efficiency cores optimized for background operations and battery preservation. Alongside the CPU is a 7-core graphics processing unit (GPU) equipped with dedicated Neural Accelerators, designed to handle advanced rendering, ray tracing, and high-fidelity mobile gaming. Furthermore, the architecture incorporates a dual 16-core Neural Engine specifically purposed for accelerated on-device artificial intelligence operations, machine learning inference, and ambient intelligence tasks integrated deeply into the operating system.

The new iPhone A20 Pro chip destroys the competition in benchmarks

Comprehensive Benchmark Analysis and Methodology

To maintain scientific integrity and eliminate variables that could artificially suppress or inflate scores, standardized testing protocols were applied. Evaluation units of the iPhone 18 Pro were subjected to assessment immediately following initial activation. The devices operated on a clean system installation devoid of third-party applications, background synchronization routines, or active cellular data connections during the testing window.

Testing utilized industry-standard benchmark suites, specifically Geekbench 6 and Geekbench 7, which measure single-core and multi-core CPU capabilities as well as GPU computation throughput.

The new iPhone A20 Pro chip destroys the competition in benchmarks

In the rigorous Geekbench 7 CPU evaluation—the premier benchmark framework utilized for contemporary mobile and desktop architecture assessments—the iPhone 18 Pro recorded a single-core score of 3,959 and a multi-core score of 10,854. In the corresponding Geekbench 7 GPU test, the hardware achieved an unprecedented score of 61,194.

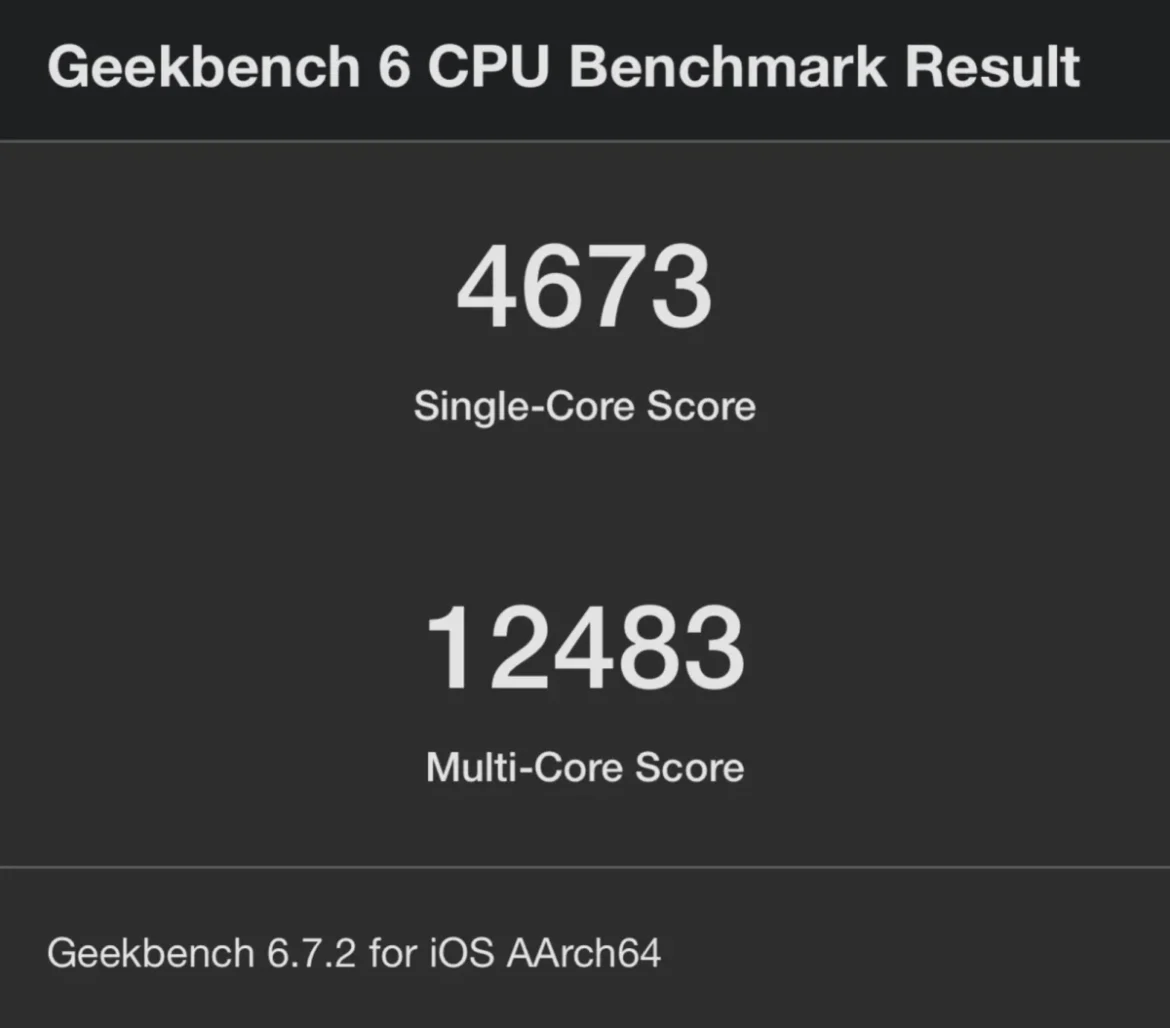
When evaluated using the legacy Geekbench 6 framework to allow direct cross-generational comparisons with previous iterations, the performance margins widened further. The device registered a single-core CPU score of 4,673 and a multi-core result of 12,483. When juxtaposed with competing flagship smartphones powered by alternative silicon—such as Qualcomm’s Snapdragon 8 Elite Gen 5 architecture featured in rival ultra-tier Android devices—the A20 Pro maintains a substantial performance lead, particularly in single-threaded operations and sustained thermal efficiency. Compared directly against its immediate predecessor, the A19 Pro found in the previous generation, the A20 Pro delivers a uniform performance uplift of approximately 25 percent across all primary testing vectors.

The new iPhone A20 Pro chip destroys the competition in benchmarks

Historical Context and the Evolution of Apple Silicon

The ascent of Apple’s proprietary silicon program represents one of the most successful strategic transitions in the consumer electronics industry. Initiated earnestly over a decade ago under the leadership of executive teams that included former hardware engineering chiefs and current corporate leadership, the shift away from third-party merchant silicon providers allowed Apple to co-design software and hardware in tandem.

This vertical integration has consistently yielded processors that outpace industry roadmaps, forcing competitors in both the mobile and personal computer spaces to accelerate their own research and development efforts in advanced node fabrication and heterogeneous computing architecture. The A20 Pro represents the pinnacle of this multi-year evolutionary arc, serving not only as the engine for the traditional candy-bar smartphone form factor but also as the processing foundation for experimental hardware categories, such as the upcoming foldable iPhone Duo.

The new iPhone A20 Pro chip destroys the competition in benchmarks

Real-World Implications and User Experience

While synthetic benchmarks provide an objective framework for comparing processing ceilings, industry analysts and reviewers emphasize the nuance regarding real-world application. For the average consumer executing routine tasks—such as web browsing, messaging, high-resolution media streaming, and casual photography—the computational headroom provided by the A20 Pro may remain largely underutilized.

Because Apple’s previous generations of mobile processors have consistently delivered responsive performance, the marginal velocity gains of the A20 Pro are most pronounced during specialized, resource-intensive workflows. These include complex 4K video rendering directly on a timeline, high-end mobile gaming with ray tracing enabled, and extensive on-device generative artificial intelligence tasks. For power users and developers leveraging advanced machine learning models locally on the device, the dual 16-core Neural Engine provides the necessary throughput to execute complex prompts without relying on cloud-based server infrastructure.

The new iPhone A20 Pro chip destroys the competition in benchmarks

Industry Response and Market Reception

The arrival of the A20 Pro has prompted immediate re-evaluations from semiconductor analysts and competitors regarding the state of 2-nanometer mass production yields. Industry observers note that Apple’s ability to secure substantial allocation of cutting-edge fabrication lines has once again given the corporation a distinct competitive moat.

Concurrently, telecommunications providers and retail partners have initiated aggressive promotional campaigns surrounding the iPhone 18 Pro launch. Major carriers, including T-Mobile, have rolled out trade-in incentives offering up to $1,200 in bill credits for qualifying devices, signaling robust initial market demand despite broader economic headwinds affecting consumer discretionary spending on consumer electronics.

The new iPhone A20 Pro chip destroys the competition in benchmarks

Future Outlook: Expanding the A20 Ecosystem

As the hardware lifecycle for the 2026 release cycle progresses, technical evaluation will inevitably expand beyond the standard Pro and Pro Max configurations. Industry researchers are particularly focused on the forthcoming performance metrics of the foldable iPhone Duo, which utilizes the exact same A20 Pro silicon package. Because the Duo incorporates an expansive, foldable primary display and a structurally distinct thermal dissipation profile compared to traditional monolithic handsets, engineers and consumers alike await independent verification of how thermal management impacts sustained performance under prolonged workloads.

Ultimately, the benchmark results of the A20 Pro reaffirm Apple’s technical leadership in mobile semiconductor engineering. Whether this computational dominance translates into long-term shifts in mobile software development—particularly regarding localized artificial intelligence capabilities—will depend heavily on how software developers harness the expanded hardware capabilities in the application ecosystem over the coming years.

September 21, 2026 0 comment
0 FacebookTwitterPinterestEmail
Artificial Intelligence & Tech

What Everyone Is Getting Wrong About TypeSafe AI’s Jev

by admin September 21, 2026
written by admin

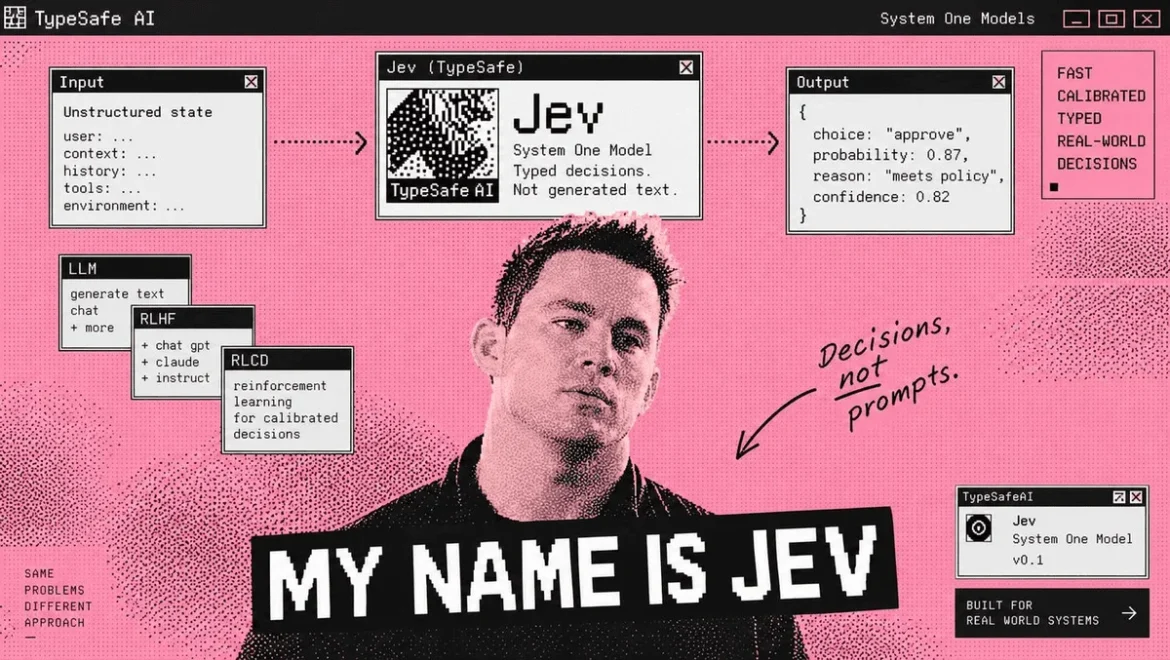
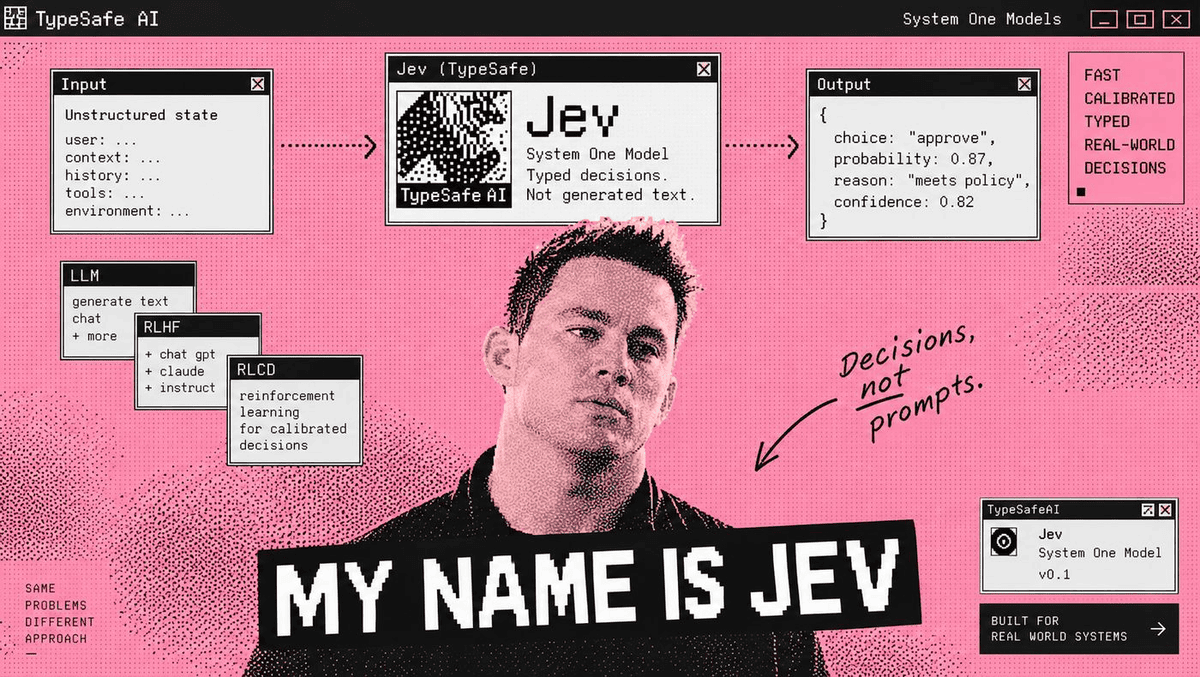
The rapid ascent of generative artificial intelligence has fundamentally altered the landscape of software engineering, leading to a surge in specialized models designed to handle tasks previously reserved for general-purpose Large Language Models (LLMs). Among the most discussed entries in this new category is Jev, developed by TypeSafe AI. As social media discourse and influencer commentary continue to frame Jev as a groundbreaking shift in artificial intelligence, a closer technical inspection reveals a more nuanced reality: Jev is not an invention of an entirely new category of intelligence, but rather a specialized, highly optimized architecture designed to address the long-standing challenges of probabilistic, structured decision-making in machine learning.

The Core Architecture of System One Models

To understand Jev, one must first distinguish between the prevailing paradigms of AI processing. TypeSafe AI classifies Jev as a "System One Model," a term derived from the dual-process theory of cognition popularized by psychologist Daniel Kahneman. In this framework, System 1 thinking is fast, intuitive, and automatic, whereas System 2 thinking is slow, deliberate, and logical.

Most frontier LLMs, such as OpenAI’s GPT-4 or Anthropic’s Claude, operate in a manner analogous to System 2. They engage in intensive reasoning, multi-step planning, and token-by-token generation to construct complex outputs. While effective, this process is inherently computationally expensive and latent. In contrast, Jev is architected for the speed of System 1. Rather than generating prose, it processes input text and immediately outputs structured data—typically a probability distribution across a set of predefined labels.

What Everyone Is Getting Wrong About TypeSafe AI's Jev - KDnuggets

This architectural shift moves away from the generative paradigm. By bypassing the need to generate coherent text, Jev avoids the overhead of autoregressive token prediction. Instead, it utilizes parallel inference to compute the likelihood of various outcomes simultaneously. This allows developers to integrate the model directly into high-throughput production pipelines, such as automated ticket routing, intent classification, and real-time content moderation.

Historical Context and Evolution of NLP

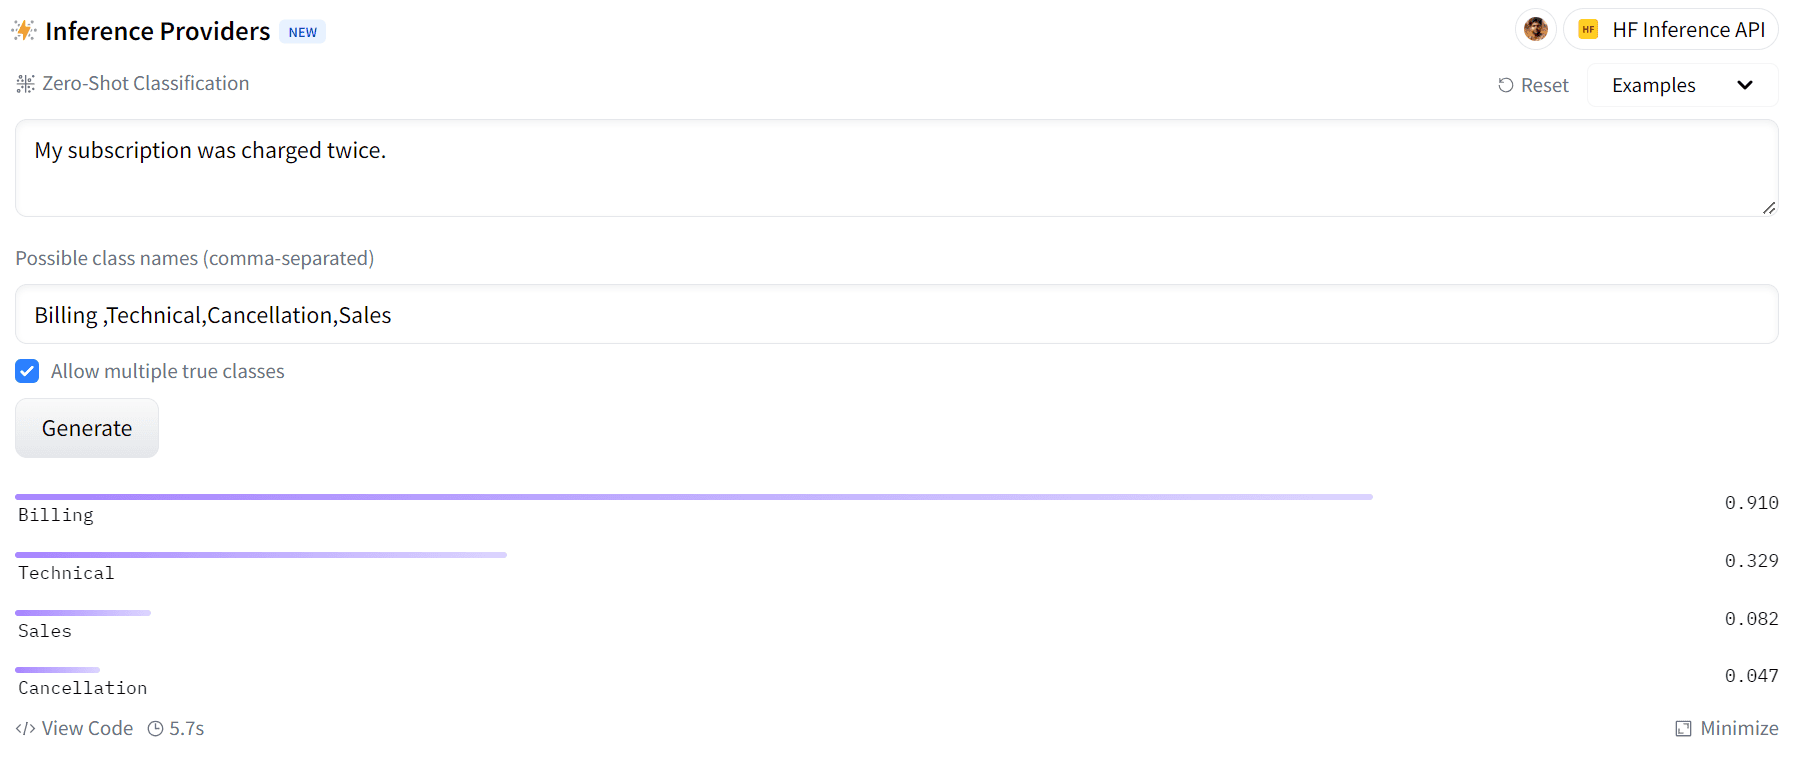
The problems Jev aims to solve—classification, intent detection, and routing—are foundational to natural language processing. For decades, engineers have utilized various techniques to categorize data. In the mid-2010s, deep learning models like BERT (Bidirectional Encoder Representations from Transformers) revolutionized these tasks by providing context-aware embeddings. By 2019 and 2020, zero-shot classification via Natural Language Inference (NLI) became the industry standard for models like Facebook’s BART (Bidirectional and Auto-Regressive Transformers).

NLI-based zero-shot classifiers allowed developers to pass arbitrary labels to a model without retraining it for specific categories. Jev represents the next logical step in this evolutionary timeline. While it shares the "spirit" of zero-shot classification, TypeSafe AI has introduced a proprietary training regimen known as Reinforcement Learning for Calibrated Decisions (RLCD). This method ensures that the model’s probability outputs are not just accurate, but calibrated, meaning the numerical confidence score provided by the model accurately reflects its actual performance reliability.

The Myth of Hallucination-Free AI

One of the most common marketing claims surrounding Jev is its resistance to hallucinations. In the context of large language models, a hallucination typically refers to the generation of false or fabricated information. However, in the context of structured classification models, "hallucination" is a misnomer.

What Everyone Is Getting Wrong About TypeSafe AI's Jev - KDnuggets

Jev operates within a rigid schema. If a user defines a set of categories—for example, "Billing," "Technical," and "Sales"—the model is mathematically constrained to return a probability distribution across only those variables. It cannot output a category outside of this predefined set. While this effectively eliminates "out-of-schema" hallucinations, it does not guarantee accuracy. The model remains susceptible to misclassification; it may, for instance, label a "Technical" support request as "Billing." Therefore, while Jev provides structural stability, it remains subject to the inherent limitations of statistical inference.

Technical Performance and Independent Evaluation

As of the current reporting cycle, empirical data regarding Jev’s performance remains limited to TypeSafe AI’s internal benchmarks and preliminary, third-party experiments. TypeSafe AI cites a 68% accuracy rate on its internal workflow evaluations. However, industry analysts caution that these metrics are derived from comparisons against frontier LLMs rather than absolute, ground-truth data sets.

Early independent tests provide a mixed picture. A small-scale fact-checking evaluation reported an accuracy of 96.3%, while a separate assessment of 275 documents showed significant alignment with human labeling. Despite these promising indicators, the lack of a standardized, peer-reviewed benchmark makes it difficult to definitively rank Jev against established alternatives. The current consensus among machine learning practitioners is to view Jev as a high-potential tool for specific, narrow-scope applications rather than a universal replacement for existing classification frameworks.

The Economic Case for Specialized Models

The primary value proposition of Jev lies in its economic efficiency. General-purpose LLMs are notoriously expensive to run due to their massive parameter counts and the computational cost of generating long-form text. In a production environment, routing a support ticket through an LLM is often overkill, consuming unnecessary compute cycles for a task that requires only a single output label.

What Everyone Is Getting Wrong About TypeSafe AI's Jev - KDnuggets

Jev addresses this through "narrow-task optimization." Because the model is trained specifically for decision-making rather than generation, it is inherently leaner. By reducing the complexity of the inference process, TypeSafe AI has lowered the barrier to entry for companies looking to implement AI-driven automation at scale. This suggests that the future of enterprise AI may not lie in larger, more complex models, but in a tiered ecosystem where specialized, low-latency models handle the "System 1" tasks, while larger, more expensive models are reserved for complex "System 2" reasoning.

Broader Implications for AI Development

The development of Jev underscores a growing trend in the AI industry: the maturation of specialized architectures. As organizations move from the initial "experimentation" phase of AI adoption to the "integration" phase, the demand for precision, reliability, and cost-effectiveness is eclipsing the demand for general-purpose versatility.

If TypeSafe AI can successfully prove that RLCD produces models with superior calibration, it could set a new standard for how AI systems communicate uncertainty. In many mission-critical applications—such as medical diagnostics, financial fraud detection, or legal document review—knowing how confident a model is in its decision is often as important as the decision itself. A system that can automatically route "high-confidence" cases for execution and "low-confidence" cases for human intervention represents a significant advancement in operational efficiency.

Ultimately, Jev is not a revolutionary break from the past, but a sophisticated refinement of the foundational principles of machine learning. By packaging these principles into a user-friendly, specialized product, TypeSafe AI is signaling that the next wave of AI innovation will likely be defined by efficiency and reliability rather than sheer scale. As more organizations subject Jev to rigorous, independent testing, the industry will gain a clearer picture of whether this "System One" approach can become the new backbone of intelligent, automated decision-making.

September 21, 2026 0 comment
0 FacebookTwitterPinterestEmail
Artificial Intelligence & Tech

Watch astronaut Christina Koch and Google’s James Manyika discuss space, technology, and discovery.

by admin September 21, 2026
written by admin

The conversation between Christina Koch, a veteran of the International Space Station (ISS) and a designated crew member for the upcoming Artemis II lunar mission, and James Manyika, who leads Google’s research initiatives into the societal impact of technology, serves as a high-level assessment of how artificial intelligence and human ingenuity converge in the final frontier. This dialogue, released as part of Google’s ongoing effort to examine the ethical and technical challenges of modern innovation, highlights the shift from purely mechanical space exploration to an era defined by symbiotic partnerships between human pilots and autonomous systems.

A Career Defined by Extremes

Christina Koch’s professional trajectory has placed her at the vanguard of modern space exploration. An electrical engineer by training, Koch gained international recognition for her tenure on the ISS, where she logged 328 consecutive days in space—a record-breaking duration for a female astronaut. During this mission, which spanned 2019 and 2020, she participated in the historic first all-female spacewalk alongside NASA colleague Jessica Meir. This milestone was more than a symbolic achievement; it represented the evolution of mission logistics and the increasing diversity of the astronaut corps, which is essential for long-duration missions to the Moon and eventually Mars.

Her selection for the Artemis II mission marks the next chapter in this narrative. As a member of the four-person crew that will orbit the Moon, Koch is tasked with testing the Orion spacecraft’s life support and navigation systems in deep space. This mission is the first crewed flight of the Artemis program, designed to establish a sustainable human presence on the lunar surface and provide the foundation for future interplanetary travel.

The Evolution of the Artemis Program: A Chronology

The context of the discussion between Koch and Manyika is deeply rooted in the rapid acceleration of NASA’s lunar ambitions. The following timeline outlines the milestones leading to the current technological intersection of human and machine:

  • 2017: The Artemis program is officially formalized under Space Policy Directive 1, aiming to return humans to the lunar surface.
  • 2020: Christina Koch completes her 328-day mission aboard the ISS, providing critical data on the physiological effects of long-duration spaceflight.
  • 2022: The uncrewed Artemis I mission successfully orbits the Moon, testing the Space Launch System (SLS) and the Orion capsule.
  • 2023: NASA announces the crew for Artemis II, featuring Christina Koch as a mission specialist.
  • 2024–2025: Current development phase focused on integration of AI-driven navigation and robotics to assist in lunar orbit rendezvous and ground operations.

Symbiosis: Robotics, AI, and the Astronaut

One of the central themes addressed by Manyika and Koch is the shifting reliance on automation. In the early days of the Mercury and Apollo programs, spaceflight was characterized by manual control and ground-based trajectory calculations. Today, the complexity of mission parameters has necessitated the integration of sophisticated AI and robotics.

Koch notes that for an astronaut, the spacecraft is no longer just a vessel; it is an extension of the crew. Robotics, such as the Canadarm2 or the sophisticated diagnostic systems on the ISS, act as force multipliers. When Manyika queries the role of artificial intelligence in space, the focus shifts to predictive maintenance and data synthesis. As astronauts venture further from Earth, the communication delay—which reaches approximately 1.3 seconds for lunar missions and up to 20 minutes for Mars—makes real-time ground control impossible. Consequently, the spacecraft must possess an onboard intelligence capable of diagnosing anomalies and optimizing energy consumption without human intervention from Earth.

Earth as a Lifeboat: The Perspective Effect

The "Overview Effect"—a cognitive shift reported by astronauts when viewing Earth from space—forms a significant portion of the dialogue. Koch describes the planet as an "electric blue lifeboat," a fragile, self-contained system suspended in the vacuum of space. This perspective serves as a powerful motivator for the integration of technology that promotes sustainability.

Manyika, in his capacity at Google, connects this sentiment to the broader application of technology. He argues that the tools developed for space—such as high-efficiency energy storage, water recycling, and climate monitoring sensors—are directly applicable to solving terrestrial crises. The data harvested from space-based observation platforms is the primary source of information for climate scientists tracking the warming of the oceans and the degradation of the ozone layer. In this sense, the astronaut is not only an explorer of the cosmos but a vital monitor of Earth’s biological health.

Addressing the Fundamental Question: Are We Alone?

The dialogue inevitably touches upon the search for extraterrestrial intelligence (SETI) and the biological potential of the universe. Koch addresses the question—"Are we alone?"—not through the lens of science fiction, but through the lens of scientific humility. She emphasizes that the search for life is an ongoing, multi-generational effort that requires the refinement of remote sensing technology and the deployment of advanced observatories like the James Webb Space Telescope.

For future explorers, Koch offers a pragmatic, human-centric piece of advice: "Do what scares you." She suggests that the discomfort of the unknown is the primary driver of innovation. By embracing the fear of the unknown, the scientific community pushes the boundaries of what is technically possible, turning theoretical models into operational reality.

Broader Implications and Strategic Analysis

The partnership between NASA and organizations like Google—and the private aerospace sector at large—signals a new paradigm in global space policy. The collaboration is no longer limited to the manufacturing of hardware; it now encompasses the development of algorithmic solutions for complex mission planning.

From an analytical standpoint, the implications of this dialogue are twofold:

  1. Technological Acceleration: The integration of AI into mission-critical systems is essential for the scaling of lunar and Martian exploration. As missions become longer and more complex, human cognitive limits necessitate a partnership with autonomous systems that can process data faster than a human operator.
  2. Societal Impact: The narrative of space exploration is being reframed from a contest of national prestige to a collaborative effort focused on human survival and scientific advancement. By bringing leaders from the technology sector into the fold, NASA is effectively communicating the value proposition of space spending to a broader, more technology-literate public.

The conversation between Koch and Manyika underscores the reality that the future of discovery is not merely about how far we can travel, but how intelligently we can use the tools at our disposal. As Artemis II approaches, the focus remains on the synthesis of human resilience and technological precision.

Conclusion

The full dialogue provides a window into the mind of a modern astronaut and the ethos of the technology companies currently shaping the infrastructure of the future. As Christina Koch prepares for her journey around the Moon, the insights shared in this series serve as a roadmap for the next phase of human exploration. The challenges of deep space—the radiation, the isolation, and the technical complexity—will remain, but the partnership between the astronaut and the machine promises to make these challenges surmountable. Whether it is through the lens of climate science or the search for life elsewhere in the galaxy, the collaboration between human expertise and machine intelligence stands as the defining feature of 21st-century exploration.

September 21, 2026 0 comment
0 FacebookTwitterPinterestEmail
Newer Posts
Older Posts

Recent Posts

  • The Evolution of the Web3 Wallet: From Private-Key Vault to the Command Center of the Agentic Web
  • Ethereum Foundation Announces Annual Protocol AMA Session Scheduled for September 16
  • Kraken Expands Its Digital Asset Offerings with the Official Listing of Doppler Finance (Xdp)
  • CSD BR and Ripple Collaborate to Integrate XRP Ledger into Brazilian Financial Market Infrastructure
  • Web3 Venture Funding Surges to Record $22 Billion in Third Quarter 2025 Driven by Institutional Adoption

Recent Comments

No comments to show.
  • Facebook
  • Twitter

@2021 - All Right Reserved. Designed and Developed by PenciDesign


Back To Top
Dr Crypton
  • Home
  • About Us
  • Contact Us
  • Cookies Policy
  • Disclaimer
  • DMCA
  • Privacy Policy
  • Terms and Conditions

We are using cookies to give you the best experience on our website.

You can find out more about which cookies we are using or switch them off in .

Dr Crypton
Powered by  GDPR Cookie Compliance
Privacy Overview

This website uses cookies so that we can provide you with the best user experience possible. Cookie information is stored in your browser and performs functions such as recognising you when you return to our website and helping our team to understand which sections of the website you find most interesting and useful.

Strictly Necessary Cookies

Strictly Necessary Cookie should be enabled at all times so that we can save your preferences for cookie settings.