At 16:49:48 UTC on Friday, August 28, 2026, a Solana wallet—funded just three hours prior with 1.79 SOL derived from $190 in bridged USDC—began a systematic extraction of funds from card-balance accounts managed by Avici, a prominent Solana-based neobank. This event, which lasted roughly two and a half hours, served as a stark reminder of the underlying vulnerabilities within the rapidly expanding "non-custodial" crypto debit card sector. By the time the final transaction occurred at 19:18:52 UTC, 1,685 users had seen a combined $500,859.22 vanish from a smart contract infrastructure shared by several programs, including Avici and Tria.
The incident was not a result of compromised user keys or illicit wallet access. Rather, the vulnerability resided in the very architecture that proponents often cite as the hallmark of safety: a specialized smart contract designed for card collateral. These contracts, while ostensibly user-controlled, are frequently subject to administrative upgrade paths that rely on single signing keys. This centralized control, combined with a signature-verification flaw, allowed the attacker to grant themselves administrative privileges over individual user accounts, effectively bypassing the security models that users believed were protecting their assets.
The Chronology of the August 28 Exploit
The precision of the attack suggests a sophisticated understanding of the target’s technical debt. The attacker’s wallet, identified as FVNFzqAny8spWdPmYw6RQ9TkYa29ueFFiqCFD1gQnCEj, performed 21,405 transactions during the exploit window, with 17,500 succeeding. Each success followed a three-step sequence against a Rain-controlled Solana program: an initial SubmitSignatures call utilizing a native Ed25519 signature-verification instruction, followed by an AddCollateralAdmin call, and concluding with a WithdrawCollateralAsset command.
The critical failure involved a faulty verification instruction that directed signature and message offsets back at the initial call, allowing a single signature to satisfy a two-signature requirement. This oversight effectively turned the attacker into a "collateral admin" for thousands of accounts. By 19:03:18 UTC, while the exploit was ongoing, the attacker initiated a deBridge order to move over 1 million USDC from Solana to Ethereum, which was subsequently funneled through Tornado Cash in standard mixing increments.
Rain, the card-issuing infrastructure provider behind these programs, responded by patching the affected Solana programs between 19:18 UTC and 19:43 UTC. On September 5, 2026, Rain transitioned the upgrade authority for these programs to a Squads multisig vault, a critical security improvement that was not publicly announced but was verified via on-chain analysis on September 10.
The Scale of the Crypto Card Market
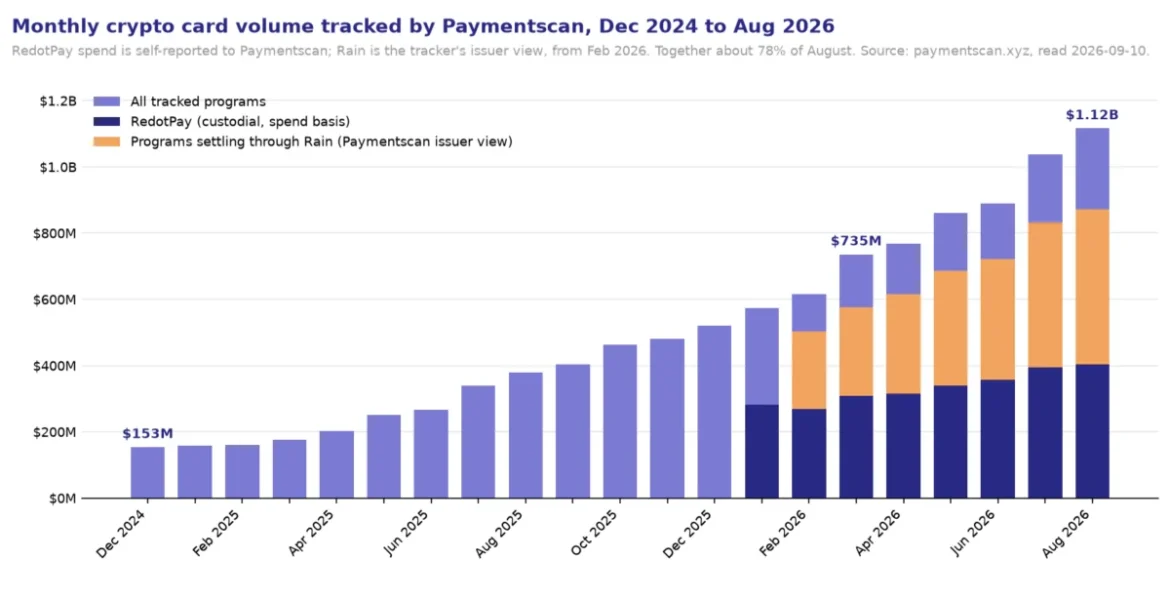
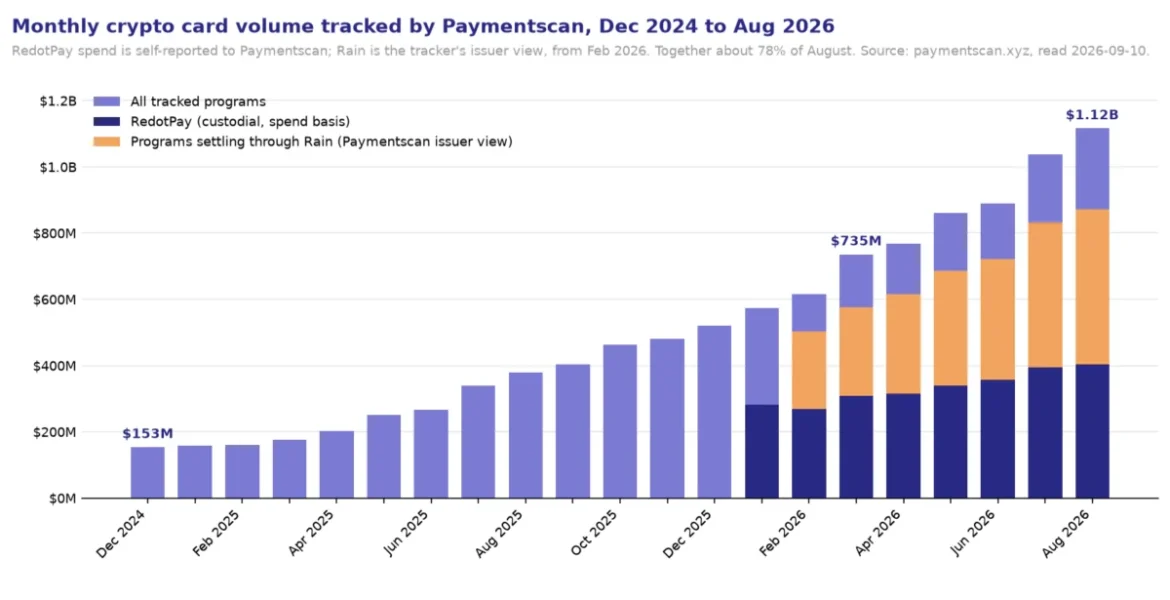
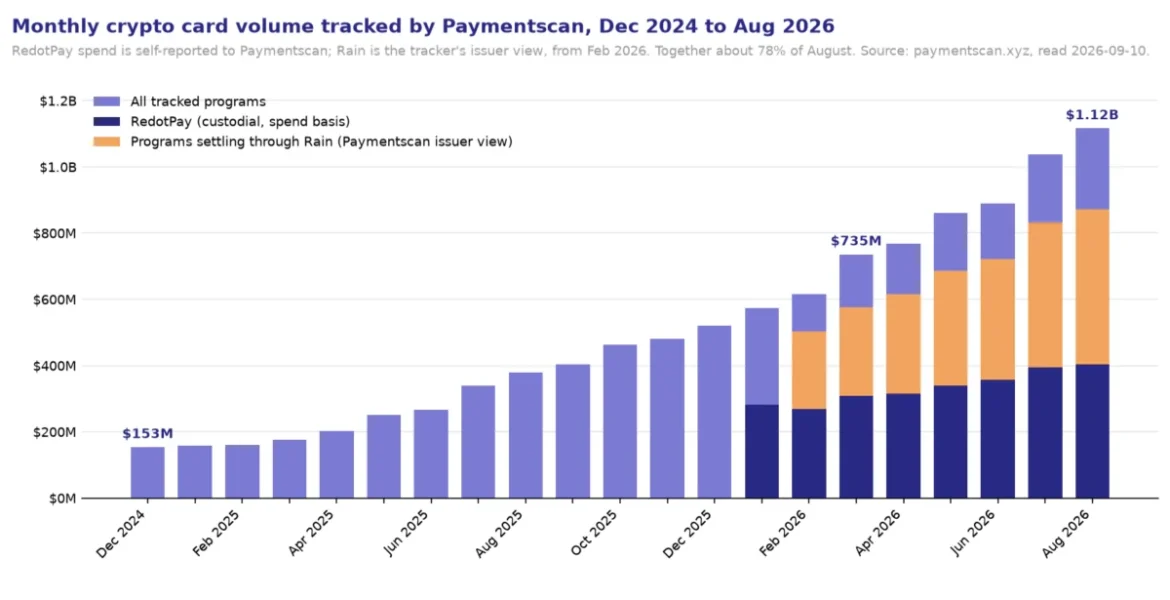
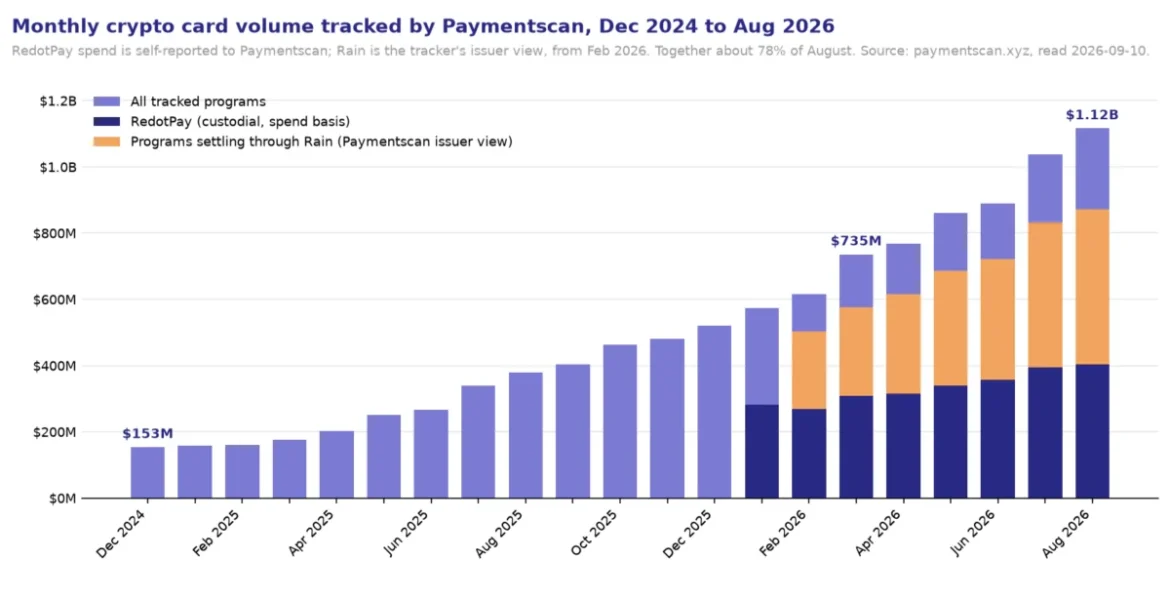
Data from Paymentscan indicates that the crypto card market has entered a period of hyper-growth, with August 2026 volume reaching $1.116 billion across 11 million transactions. This represents a significant shift from the $153 million recorded in December 2024. While these figures reflect a maturing industry, they also mask significant complexities regarding how funds are actually held.
Paymentscan identifies five distinct custody models, ranging from "Sold to the Operator"—where the user holds only a debt claim against the issuer—to "Your Own Vault," where funds remain in a self-custodial smart contract debited only at the moment of authorization. The industry remains highly concentrated; Rain alone facilitates settlement for roughly 42% of the market’s total volume. When combined with RedotPay’s self-reported figures, just two entities account for approximately 78% of the total tracked volume. This concentration creates a systemic risk profile where a single technical failure in a shared codebase can affect dozens of seemingly disparate brands simultaneously.
The Myth of Non-Custodial Security
The term "non-custodial" has become a marketing imperative in the crypto card space, yet its legal and technical definitions vary wildly. Avici’s terms of service, last updated in June 2025, assured users that the company would never hold custody of collateral. While legally accurate, this statement provided little comfort to the 1,685 users whose funds were drained due to a flaw in the underlying Rain-managed contract.

This gap between marketing and mechanism is exemplified by programs like Solayer, which markets its Emerald card as "fully on-chain" while its internal security documentation reveals the use of offline, multisig-protected cold storage. This is, by definition, a custodial arrangement. The industry’s reliance on "Third National"—a Puerto Rican money transmitter and Rain affiliate—as an issuer for seven major programs further highlights the distance between the "DeFi" ethos and the reality of traditional financial infrastructure. These cards are effectively charge cards financed by borrowed stablecoins, not the seamless, on-chain experiences often depicted in promotional materials.
Regulatory and Institutional Implications
The regulatory landscape is set to undergo a fundamental shift with the implementation of the EU’s Anti-Money Laundering Regulation (Regulation (EU) 2024/1624) in July 2027. This regulation will effectively prohibit anonymous crypto-asset accounts and bar EU acquirers from processing payments from anonymous prepaid cards issued in third-party jurisdictions. For the "no-KYC" card sector, this presents an existential threat. Currently, these services exploit the gap between "Know Your Business" (KYB) verification for the issuer and the lack of individual KYC for the cardholder.
Recent infrastructure failures—such as the collapse of the Kulipa program in July 2026, which abruptly ended services for Ready, Argent, and Solflare—demonstrate that the primary risk to users is often not a hack, but rather the fragility of the underlying business relationships. When issuers like Paytend have their licenses revoked or programs like Fiat24 pause operations to address compliance gaps, the brand the consumer interacts with is often left powerless to assist.
Official Responses and Remediation
The response to the August 28 exploit was swift, if opaque. Avici and Tria, recognizing the reputational damage at stake, opted to cover the losses out of their own balance sheets, with Avici explicitly stating that Rain funded the refunds. The total impact, approximately $1.1 million, was mitigated for the end-user within 24 hours. However, the incident highlighted a dangerous lack of transparency regarding pre-deployment audits. While Rain claims to use Sherlock for audits, the drained contracts were older versions that remained live—a classic "legacy code" vulnerability that audit-at-deployment models fail to address.
Ether.fi Cash remains a notable outlier in the category. By utilizing a public, address-verified vault on Optimism and maintaining clear documentation on its CashModule contract, it offers a level of transparency that is currently the exception, not the rule. The contrast between Ether.fi’s architecture and the shared, opaque collateral pools of other programs is a lesson in the importance of technical due diligence over marketing claims.
Moving Forward: What Users Should Analyze
For the end-user, the August 2026 events suggest five critical questions that must be addressed before depositing funds into any crypto-linked card:
- Custody Classification: Does the contract transfer ownership to the operator, or is it a true self-custodial vault?
- Issuer Identity: Is the issuer a chartered bank, an EMI, or an offshore money transmitter? If the issuer is not clearly named, the program should be viewed as high-risk.
- Insolvency Protection: What happens if the service provider goes bankrupt? If the terms do not explicitly address the status of user funds in an insolvency event, users should assume they are unsecured creditors.
- Upgrade Authority: Who holds the keys to upgrade the contract? If a single private key controls the contract, the "non-custodial" nature of the product is largely performative.
- Transparency of Metrics: Are volume and spend metrics verifiable on-chain, or are they self-reported numbers that lack independent oversight?
The rapid expansion of the crypto card market in 2026 has provided users with unprecedented convenience, but it has also introduced a level of technical and systemic risk that the current marketing landscape fails to articulate. While the August 28 exploit ended with users being made whole, the next failure may not be supported by a $338 million venture-backed balance sheet. As the industry approaches the 2027 regulatory deadline, the divergence between robust, transparent platforms and those relying on "nuanced loopholes" will likely accelerate, forcing a consolidation that favors transparency and structural integrity over the current proliferation of proprietary, black-box solutions.
The reliance on a single company to manage nearly half of the market’s settlement volume creates a "too-big-to-fail" scenario that contradicts the decentralization tenets of the blockchain ecosystem. Ultimately, the stability of the crypto card market in the coming years will depend less on the cleverness of its smart contract marketing and more on the regulatory and technical rigor of the institutions standing behind the cards. Until that time, the user is left to navigate a landscape where "non-custodial" is a description of the current state of a contract, rather than a guarantee of future security.