• Home
  • About Us
  • Contact Us
  • Cookies Policy
  • Disclaimer
  • DMCA
  • Privacy Policy
  • Terms and Conditions
Dr Crypton
Secure Your Future in Crypto
Artificial Intelligence & Tech

5 Free GitHub Zoomcamps to Learn Data Engineering, Machine Learning, MLOps, LLMs, and AI Development

by admin September 20, 2026
written by admin

The landscape of professional technical education is undergoing a profound transformation as community-driven initiatives challenge the dominance of traditional, high-cost bootcamps. DataTalks.Club, a global community of data professionals, has solidified its role in this shift by providing a series of open-access, project-based educational programs known as "Zoomcamps." These initiatives offer a structured, cohort-based curriculum covering the entire lifecycle of modern data and AI systems, ranging from infrastructure engineering to the deployment of large language model (LLM) applications.

The Evolution of Community-Driven Technical Education

Originating during the global pandemic as a response to the need for accessible remote learning, DataTalks.Club has maintained a commitment to zero-cost education. Unlike typical Massive Open Online Courses (MOOCs) that often suffer from high attrition rates due to isolation, the Zoomcamp model emphasizes synchronization. Participants are encouraged to join active cohorts, adhere to weekly deadlines, submit homework, and collaborate on final projects. This pedagogical structure mirrors the rigor of professional environments, providing accountability and networking opportunities that are often missing in self-paced learning models.

The success of this model is evidenced by the growing demand for "job-ready" skills. As of 2026, the technology sector continues to prioritize practical application over theoretical knowledge. Employers increasingly favor candidates who can demonstrate the ability to navigate the complexities of modern tech stacks—such as containerization, cloud orchestration, and model deployment—rather than those who only possess a foundational understanding of algorithms.

Data Engineering: The Foundation of the Modern Stack

The Data Engineering Zoomcamp represents a nine-week intensive journey into the architecture of data systems. In an era where data velocity and volume have reached unprecedented levels, the ability to build robust, scalable pipelines is a critical business asset. This course moves beyond basic SQL queries to cover the orchestration of complex workflows.

Students engage with a comprehensive technology stack, including Docker for environment consistency, PostgreSQL for transactional storage, and Apache Kafka for real-time streaming. The curriculum also incorporates modern workflow orchestration tools like Kestra and analytics engineering frameworks such as dbt. By the conclusion of the program, participants are expected to synthesize these components into an end-to-end pipeline, effectively simulating the work performed by data engineers in production environments. This focus on the "modern data stack" ensures that students are familiar with the industry-standard tools currently favored by high-growth startups and enterprise organizations alike.

Machine Learning Engineering: Beyond the Model

The transition from academic machine learning to applied machine learning engineering is a primary hurdle for many junior developers. The Machine Learning Zoomcamp addresses this gap by shifting the focus from model development to application lifecycle management. While the curriculum covers essential concepts such as regression, classification, and ensemble methods, the core value lies in the deployment phase.

By utilizing FastAPI, Kubernetes, and serverless architectures like AWS Lambda, students learn how to bridge the gap between a trained model and a functional, user-facing application. The importance of this approach cannot be overstated; the industry consensus is that a model’s value is zero until it is successfully integrated into a production system. With the next cohort scheduled for September 14, 2026, the program continues to provide a clear pathway for Python developers to advance into roles as Machine Learning Engineers.

MLOps: The Bridge to Production Reliability

While machine learning engineering focuses on deployment, the MLOps Zoomcamp addresses the operational complexities that arise once a model is live. In the professional world, maintaining a model’s performance over time—addressing data drift, ensuring reliability, and managing version control—is significantly more challenging than the initial training process.

The curriculum provides a deep dive into the "MLOps lifecycle," incorporating industry-standard tools such as MLflow for experiment tracking, and Prometheus and Grafana for system monitoring. By focusing on CI/CD pipelines and automated testing, the course teaches participants how to maintain a resilient machine learning system. This focus on reliability is crucial for organizations that depend on AI for core business processes, as it mitigates the risks associated with model decay and infrastructure failure.

LLM Application Development: Navigating the New Frontier

Perhaps the most contemporary addition to the DataTalks.Club repository is the LLM Zoomcamp. As generative AI continues to disrupt software development, the demand for developers who can integrate LLMs into existing products has surged. This 10-week course focuses on the architecture of LLM applications, specifically emphasizing Retrieval-Augmented Generation (RAG).

The curriculum moves well beyond simple prompt engineering. It covers vector search, embeddings, evaluation frameworks, and the construction of autonomous AI agents. By requiring participants to build a complete application, the course ensures that students understand the trade-offs between different search strategies and the necessity of monitoring LLM responses for accuracy and safety. This practical, system-level approach to AI development is highly sought after in the current job market, where businesses are rushing to implement proprietary LLM solutions.

AI-Assisted Development: The Changing Role of the Engineer

The AI Dev Tools Zoomcamp marks a shift in how software development is taught. Rather than focusing on how to build AI, this program instructs developers on how to use AI to build software more efficiently. This includes integrating AI coding assistants and agents into every stage of the development lifecycle, from planning and architecture to testing, security audits, and CI/CD deployment.

With the next cohort beginning on August 31, 2026, this course is designed for professionals looking to future-proof their careers. As tools like MCP (Model Context Protocol) and autonomous coding agents become standard, the ability to orchestrate these agents within a secure, professional workflow will be a defining skill for the next generation of software engineers. The focus here is not on replacing the developer, but on augmenting their capabilities while maintaining high standards of code quality and security.

Broader Implications for the Tech Industry

The persistence of the DataTalks.Club model suggests a shift in the perceived value of traditional higher education in the tech sector. By providing a free, peer-reviewed, and project-oriented curriculum, these Zoomcamps have effectively democratized access to high-level technical skills.

Data suggests that students who complete these programs often see tangible career benefits. Because the coursework is built upon the same tools and methodologies used by top-tier tech companies, the transition to the workforce is often smoother than that of graduates from purely theoretical academic programs. Furthermore, the community-driven nature of these courses provides a support system that fosters professional networking, mentorship, and knowledge sharing.

From an industry perspective, the availability of these resources reduces the "onboarding cost" for companies hiring junior talent. When an applicant has successfully completed a project-based course, the employer gains confidence that the candidate has already grappled with common production issues such as containerization, API design, and cloud deployment.

As the digital economy continues to prioritize agility and rapid skill acquisition, the model pioneered by DataTalks.Club serves as a blueprint for how technical communities can self-organize to solve the "skills gap." By keeping the barrier to entry low—requiring only time and dedication rather than significant financial investment—these Zoomcamps ensure that the next generation of AI and data professionals will be judged by the quality of their code and the robustness of their systems, rather than the prestige of their credentials.
September 20, 2026 0 comment
0 FacebookTwitterPinterestEmail
Artificial Intelligence & Tech

Recreating a 70-year love story frame by frame

by admin September 20, 2026
written by admin

The Genesis of a Digital Archive

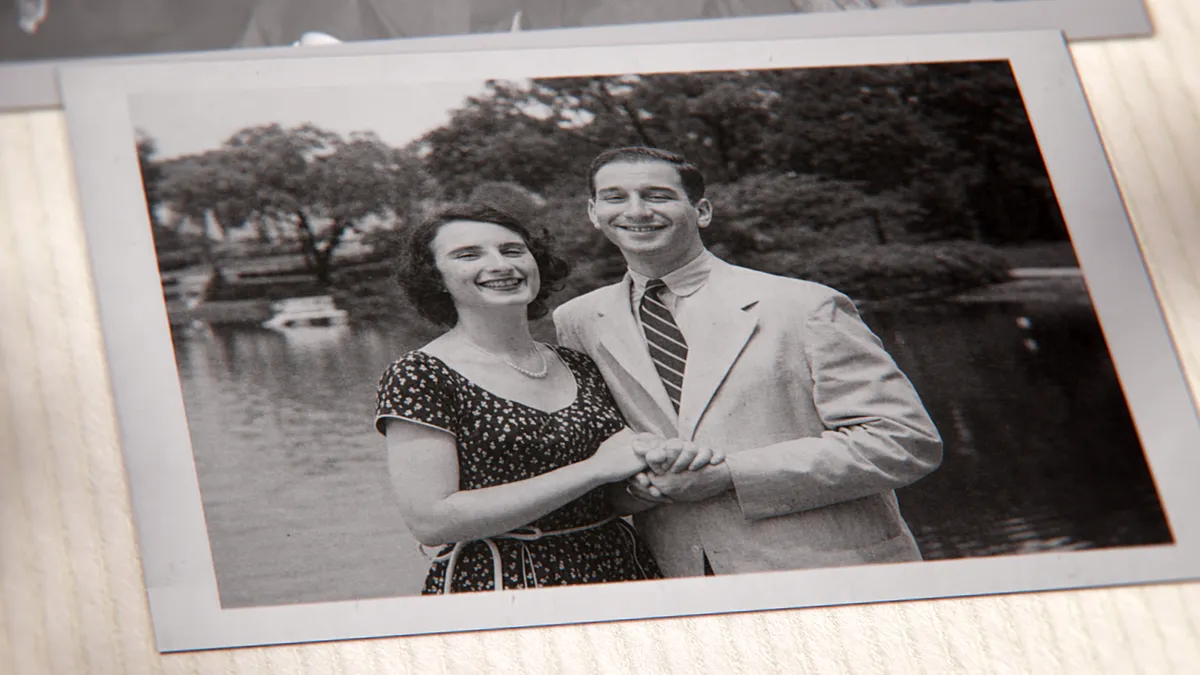
The narrative of Love, Rendered centers on a specific, unrecorded moment in the couple’s history: the day they first met at a student cooperative in Cleveland. Despite their long and shared life, this foundational event existed only in the abstract form of human memory, never captured by the lens of a camera or the permanence of film. For the filmmakers, including Academy Award-nominated director Liz Garbus and producers Dan Cogan and Darren Aronofsky, the challenge was to reconstruct this memory not as a historical reenactment, but as a collaborative synthesis of personal recollection and computational modeling.

The technical development of the film was led by Michael Chang, a Google DeepMind engineer whose own personal history with his grandfather’s struggle with memory loss served as a catalyst for the project. The production team utilized a hybrid methodology, merging archival restoration techniques with modern generative video models to visualize scenes that had long been lost to time.

The Science of Reminiscence Therapy

The conceptual framework for the film is rooted in the clinical practice of reminiscence therapy. This therapeutic approach is frequently employed in geriatric care to manage the symptoms of dementia and Alzheimer’s disease. By utilizing sensory stimuli—such as period-appropriate music, historical photographs, and guided storytelling—clinicians aim to trigger the neural pathways associated with long-term memory, thereby improving the emotional well-being of the patient.

Recreating a 70-year love story frame by frame

The filmmakers were heavily influenced by research into the resilience of memory. Liz Garbus, in her earlier work on the documentary Coma, observed the neurological response of patients in minimally conscious states when exposed to familiar auditory or visual cues. Similarly, the project drew inspiration from documented cases, such as the widely circulated footage of a former ballerina with Alzheimer’s who, upon hearing Tchaikovsky’s Swan Lake, was able to perform choreography from her youth.

In Love, Rendered, the technology functions as an extension of this therapy. Ethelle Shatz participated in the creative process as a primary source, working directly with engineers to refine the digital output. By providing granular feedback—such as correcting the curvature of a staircase or the specific style of a shoe heel—she helped anchor the AI’s generative output in factual, lived reality.

A Technical Chronology of Reconstruction

The production of the film followed a rigorous multi-stage workflow:

  1. Archival Assessment: The team began by digitizing existing family photos, providing the AI with the foundational aesthetic and physical characteristics of the couple in their youth.
  2. Generative Modeling: Engineers deployed video models to animate these still images, attempting to extrapolate movement and expression based on the identified visual patterns.
  3. Collaborative Iteration: The "human-in-the-loop" phase required the subjects to verify the accuracy of the AI-generated imagery. This ensured that the "memory" being created remained consistent with their subjective experience.
  4. Integration: The final film weaves these reconstructed moments with contemporary footage of the couple, creating a seamless narrative that bridges seven decades of history.

According to technical leads on the project, the primary challenge was not merely visual, but emotional. "Machine learning is a tool, much like a paintbrush or a hammer," notes Darren Aronofsky. "It does nothing until it is guided by human hands." The team’s objective was to ensure the AI did not hallucinate new, incorrect memories, but rather served as a conduit for the couple’s own latent recollections.

Recreating a 70-year love story frame by frame

Data and Implications for Generative AI

The use of AI in this context highlights a growing trend in the tech industry: the pivot from purely functional utility toward emotional and personal preservation. As generative models become more accessible, the capacity for individuals to perform their own "digital restoration" is expanding.

Google has integrated these capabilities into broader consumer-facing tools, such as the Gemini app, which now includes features for colorizing and restoring legacy photographs. However, the use of these tools for memory reconstruction raises important questions regarding the authenticity of digital records. While the filmmakers emphasize that the AI was used to guide the couple back to a moment, the reliance on algorithms to "fill in the blanks" suggests a future where our collective family history may become increasingly algorithmic.

Statistically, the demand for such technologies is likely to grow. The World Health Organization estimates that over 55 million people worldwide are living with dementia, a figure expected to rise to 139 million by 2050. As the demographic shift toward an aging population continues, the integration of technology into therapeutic care will become an increasingly vital area of interdisciplinary research.

Ethical Considerations and Future Outlook

While the reception to Love, Rendered has been positive, particularly regarding its focus on empathy, the film invites a broader conversation about the ethics of "synthetic memory." When an algorithm generates a missing visual, does it strengthen the human bond to the past, or does it risk substituting genuine, fading memories with an artificial approximation?

Recreating a 70-year love story frame by frame

The filmmakers maintain that the process was an exercise in agency. By involving the couple as co-creators, the production avoided the pitfalls of top-down digital reconstruction. The result is a documentary that functions less as a technical showcase and more as a proof-of-concept for how families might utilize AI to honor and preserve their shared history.

As the industry continues to refine video generation, the standard for "emotional truth" will be tested. Future iterations of this technology may allow for more immersive experiences, potentially incorporating audio synthesis or spatial computing to recreate environments that no longer exist. Whether these advancements will ultimately enhance our ability to cope with loss or fundamentally alter our relationship with reality remains a subject of ongoing debate within the fields of bioethics and digital media.

In the final assessment, Love, Rendered stands as a significant milestone in the evolution of AI-assisted storytelling. By focusing on the intimate details of a single couple’s life, the project provides a human-centric lens through which to view the rapid advancement of machine learning, suggesting that the most profound use of our most powerful technology may be the simple act of remembering.

September 20, 2026 0 comment
0 FacebookTwitterPinterestEmail
Cryptocurrency News

VanEck Spotlights Dilution Risks in Metaplanet Executive Compensation Structure Amid Aggressive Bitcoin Treasury Expansion

by admin September 20, 2026
written by admin

Japanese investment firm Metaplanet has rapidly ascended to become one of the most closely watched corporate Bitcoin holders outside of the United States, earning comparisons to American pioneers like MicroStrategy. However, a recent analysis by global asset manager VanEck has illuminated a critical financial dynamic that often escapes mainstream attention: the mechanics of executive compensation and share dilution underpinning Metaplanet’s aggressive treasury strategy. According to VanEck’s latest Bitcoin ChainCheck report, spearheaded by Head of Digital Assets Research Matthew Sigel, Metaplanet’s current executive stock-option structure carries potential dilution equivalent to roughly 22.4% of the company’s equity base.

While the headline-grabbing figures of Metaplanet’s expanding Bitcoin holdings continue to captivate retail and institutional investors alike, VanEck’s analysis serves as a stark reminder that corporate treasury strategies cannot be evaluated in a vacuum. For shareholders whose investment thesis hinges directly on increasing Bitcoin exposure on a per-share basis, the scale of potential equity dilution introduces a complex risk-reward equation that demands closer examination.

The Shift Toward Corporate Bitcoin Treasuries: A Global Phenomenon

To fully understand the gravity of VanEck’s observations, it is necessary to contextualize Metaplanet’s rise within the broader landscape of corporate finance. Over the past several years, a growing number of publicly traded companies have integrated digital assets into their balance sheets as a hedge against fiat currency devaluation, inflation, and macroeconomic volatility. Pioneered largely by Michael Saylor’s MicroStrategy (formerly MicroStrategy Inc.), this strategy involves leveraging the public equity markets—through secondary share offerings, convertible notes, and debt financing—to accumulate Bitcoin as a primary treasury reserve asset.

Metaplanet, listed on the Tokyo Stock Exchange, embraced this playbook with remarkable speed, positioning itself as Asia’s foremost corporate Bitcoin standard-bearer. By aggressively issuing equity and utilizing capital markets to fund continuous Bitcoin purchases, the company transformed its market identity from a struggling hotel and consulting business into a high-beta digital asset proxy.

Yet, this financial engineering relies heavily on a delicate balance: the value generated by acquiring appreciating digital assets must outpace the dilution inflicted upon existing shareholders through the issuance of new stock. When a corporation utilizes equity instruments not only to fund asset purchases but also to compensate its leadership team, the mechanics of per-share value creation become increasingly intricate.

Deconstructing the VanEck ChainCheck Report: The 22.4% Dilution Factor

VanEck’s mid-September Digital Assets ChainCheck report brought the spotlight squarely back to corporate governance and capital structure. While much of the financial media focuses exclusively on the total number of Bitcoins sitting in Metaplanet’s digital wallets, VanEck chose to scrutinize how management is being rewarded while building that very treasury.

The core finding of the report centers on Metaplanet’s executive stock-option framework. VanEck calculated that the company’s existing option capacity equates to approximately 22.4% potential dilution for current shareholders. To put this figure into perspective, a dilution rate of over one-fifth of the company’s equity represents a substantial transfer of potential future value from public shareholders to corporate insiders.

This revelation highlights a fundamental tension in corporate Bitcoin strategies. Publicly, Metaplanet’s leadership promotes a clear value proposition: increasing the amount of Bitcoin owned per share of common stock. However, if the share count expands significantly to accommodate executive incentives, the actual fractional ownership of those underlying treasury assets diminishes for retail and institutional investors who purchased shares on the open market. Consequently, an investor might find that while the company’s absolute Bitcoin balance is rising, their individual share of that treasury is effectively shrinking due to equity inflation.

Balancing Base Salaries and Equity Compensation

In defense of its compensation policies, Metaplanet has implemented measures intended to demonstrate fiscal restraint and alignment with shareholder interests. Most notably, the company reduced executive base salaries by approximately 15%, a move frequently cited by management to show solidarity with investors during periods of heavy capital expenditure and market volatility.

However, VanEck’s analysis points out that this nominal reduction in cash compensation sits alongside substantial equity-based remuneration. In the corporate governance landscape, stock options are a standard tool utilized to align the financial interests of executives with those of shareholders; when the stock price rises, both parties theoretically benefit.

The divergence in the case of Metaplanet lies in the sheer scale of the option pool relative to the size of the company and the specific nature of its investment thesis. When a corporation’s entire equity valuation is inextricably linked to a per-share metric—specifically, Bitcoin per share—any structural mechanism that inflates the denominator (the total number of shares) directly threatens the integrity of that metric.

It is important to clarify that VanEck’s report is not an indictment of Metaplanet’s underlying digital asset strategy. The company has not engaged in large-scale liquidations of its cryptocurrency holdings; its accumulation thesis remains firmly intact. Rather, the critique is structural, focusing on the capital architecture built around the treasury rather than the treasury itself.

The Evolution of Corporate Bitcoin Metrics

As the corporate adoption of Bitcoin matures from an experimental fringe strategy into an established institutional practice, the metrics by which these companies are evaluated are bound to evolve. Historically, market analysts and crypto enthusiasts tracked corporate treasuries based on a single metric: absolute Bitcoin volume. Companies were ranked simply by who held the most coins.

However, as VanEck’s commentary suggests, the future of corporate treasury analysis will likely demand a more sophisticated approach. Investors are beginning to realize that accumulating Bitcoin at any cost—particularly if achieved through highly dilutive equity issuances—may not always serve the best long-term interests of common shareholders.

Moving forward, market participants are expected to place greater emphasis on capital efficiency. Key questions will include:

  • How efficiently is a company accumulating Bitcoin on a per-share basis?
  • What is the net cost of acquisition when accounting for equity dilution, interest expenses on convertible debt, and administrative overhead?
  • Are executive compensation packages structured in a way that truly rewards per-share growth, or do they incentivize top-line asset accumulation at the expense of existing equity holders?

These considerations will likely differentiate successful, shareholder-friendly Bitcoin treasury companies from those that expand their balance sheets while eroding shareholder value through excessive dilution.

Broader Implications for the Asian Digital Asset Market

Metaplanet’s trajectory serves as a bellwether for the broader Asian corporate sector regarding the adoption of digital assets. Operating within a regulatory and financial environment historically more conservative toward cryptocurrencies than the United States, Metaplanet’s bold pivot captured global attention and inspired other regional firms to evaluate similar balance-sheet strategies.

At the same time, the scrutiny applied by major institutional asset managers like VanEck underscores the growing convergence between traditional equity research and digital asset analysis. As mainstream financial institutions integrate crypto-treasury companies into diversified portfolios, they bring rigorous traditional finance (TradFi) standards to bear on these firms. Corporate governance, executive compensation transparency, and capital allocation efficiency are no longer secondary concerns for crypto-focused equities; they are front-and-center evaluation criteria.

For Metaplanet, the challenge moving forward will involve maintaining its aggressive accumulation momentum while actively addressing investor concerns regarding equity dilution. Balancing executive incentive structures with the overarching promise of per-share Bitcoin accretion will be vital as the company seeks to retain the confidence of institutional shareholders.

Conclusion

Metaplanet remains a trailblazing entity in the corporate Bitcoin movement, demonstrating how non-American public companies can leverage capital markets to establish substantial digital asset reserves. Yet, as VanEck’s recent ChainCheck analysis demonstrates, the path of aggressive treasury accumulation is fraught with structural complexities.

With executive stock options representing a potential 22.4% dilution, shareholders are reminded that headline-grabbing Bitcoin balance sheets tell only half the story. As the market transitions toward a more nuanced evaluation of corporate digital asset strategies, capital efficiency, governance transparency, and per-share accretion metrics will ultimately determine which corporate treasuries deliver sustainable long-term value to their investors.

September 20, 2026 0 comment
0 FacebookTwitterPinterestEmail
Blockchain Technology

Global Regulatory Tensions Rise as Nations Move to Tax Digital Assets While Industry Pushes Back

by admin September 20, 2026
written by admin

The landscape of digital asset regulation is undergoing a seismic shift as major global economies intensify their efforts to bring cryptocurrency transactions under formal tax frameworks. From the European Union’s coordinated push for transparency to localized legislative battles in the United States, the coming years promise a fundamental change in how investors and corporations navigate the digital asset ecosystem. While European nations like Germany and Bulgaria are aligning their domestic laws with broader EU directives to capture revenue from a maturing market, major U.S. industry associations are fighting to halt state-level legislation they argue is both discriminatory and constitutionally unsound.

Germany’s Strategic Pivot Toward Capital-Income Taxation

Germany is currently at the forefront of this regulatory evolution. A draft bill emanating from the Federal Ministry of Finance, under the leadership of Finance Minister Lars Klingbeil, signals the end of a long-standing tax exemption for long-term crypto holdings. Historically, Germany has maintained a favorable stance toward private investors, where gains from digital assets were exempt from capital gains tax if the assets were held for more than one year.

Under the proposed reform, this tax-free threshold is set to vanish for assets acquired after December 31, 2026. The government intends to transition digital assets into the standard capital-income tax regime by 2028. This move would subject crypto gains to a flat 25% tax rate, supplemented by a 5.5% solidarity surcharge, resulting in an effective tax burden of 26.375%.

The Ministry of Finance justifies this move by citing the maturation of the crypto market. Finance Minister Klingbeil has characterized the previous tax-free treatment of speculative crypto gains as an unfair disparity when compared to the taxation of traditional "hard-earned" income and stock market investments. The economic projections associated with this shift are significant: the government estimates the policy will generate €160 million in revenue by 2028, scaling to €350 million by 2030.

While the proposal includes a €1,000 saver’s allowance—which may mitigate the impact for smaller retail investors—the removal of the one-year holding incentive marks a psychological and financial turning point for the German crypto community. Furthermore, the bill clarifies that staking and lending income will henceforth be classified as capital income, closing a loophole that previously left these passive income streams in a regulatory gray area. Certain assets, including specific stablecoins, security tokens, and real-world asset (RWA) tokens, may be exempt or subject to different classifications depending on their specific technical characteristics, a detail that industry analysts are watching closely as the bill moves through federal coordination.

Bulgaria and the Harmonization of EU Reporting Standards

While Germany focuses on internal revenue generation, Bulgaria is prioritizing the structural alignment of its financial reporting with European and global standards. On September 9, the Bulgarian National Assembly voted overwhelmingly to approve amendments to the "Tax and Social Security Procedure Code." This legislation transposes two critical European directives into national law, effectively integrating Bulgaria into the EU’s DAC8 (Directive on Administrative Cooperation) framework.

The urgency of this move is rooted in the broader EU mandate that required member states to transpose DAC8 by the end of 2025, with implementation effective from January 1, 2026. By passing these amendments, Bulgaria is ensuring that its domestic Crypto-Asset Service Providers (CASPs) are fully compliant with the Organization for Economic Co-operation and Development’s (OECD) Crypto-Asset Reporting Framework (CARF).

The implications for crypto users in Bulgaria are substantial. CASPs are now legally mandated to register with the National Revenue Agency (NRA) and disclose extensive user data. This includes personally identifiable information such as full names, residential addresses, tax identification numbers, and, crucially, granular transaction data. Providers must report the total gross amounts of transactions, the volume of units traded, and the specific frequency of purchases or sales against fiat currencies. This data will then be automatically exchanged between EU member states and participating global jurisdictions to combat cross-border tax evasion. With 47 jurisdictions, including Bulgaria, committed to the first round of automatic information exchange by 2027, the era of anonymous digital asset trading is effectively drawing to a close within the European bloc.

The U.S. Front: A Judicial Clash Over State-Level Taxation

In stark contrast to the European experience, where legislative harmonization is the primary driver, the United States is seeing a fragmented and highly contentious approach to crypto taxation. In June, Illinois made history by becoming the first U.S. state to enact the Digital Asset Tax Act (DATA), which imposes a 0.2% tax on the value of digital assets exchanged, transferred, or stored on behalf of Illinois customers.

The industry’s reaction was swift and litigious. The Blockchain Association and the Crypto Council for Innovation (CCI) have filed a formal motion for a preliminary injunction in the Circuit Court of Sangamon County, seeking to block the enforcement of the law before it takes effect on January 1, 2025. The core of their argument is that the law is "unlawful" and "unfairly targets" digital assets, creating a precedent that could be exploited by other states if left unchecked.

Arguments Against the Illinois Digital Asset Tax Act (DATA)

The trade associations highlight several points of contention in their legal filings:

  1. Unprecedented Scope: The Act taxes the act of transfer or storage, even if the asset holder realizes no gain, sells nothing, and merely moves an asset within a wallet.
  2. Discriminatory Treatment: Critics argue that the tax applies only to digital assets, while ignoring traditional assets like gold or fiat currency exchanges, violating the principle of equal protection under the law.
  3. Compliance Burdens: The registration and reporting requirements impose massive, multi-million dollar operational costs on firms, effectively forcing them to build infrastructure for a tax that may eventually be ruled unconstitutional.
  4. Criminal Liability: The threat of severe penalties, including fines up to $25,000 and imprisonment for up to five years, has created a climate of uncertainty for brokers operating in the state.

Ji Hun Kim, CEO of the Crypto Council for Innovation, noted that the state is forcing companies to divert critical resources toward an "unlawful tax" that violates constitutional rights. Summer Mersinger, CEO of the Blockchain Association, echoed these concerns, warning that if the Illinois law stands, it could trigger a "race to the bottom" where other states implement similar, potentially fragmenting, taxes that threaten the national market.

Chronology of Legislative Developments (2025–2027)

  • January 1, 2026: Deadline for EU member states to begin applying DAC8 provisions for automatic exchange of digital asset information.
  • June 2026: Illinois enacts the Digital Asset Tax Act (DATA), setting a precedent for transaction-based state taxes on crypto.
  • September 2026: Bulgaria’s National Assembly passes legislation to align with DAC8 and CARF standards.
  • December 31, 2026: Cut-off date for the current German crypto tax exemption for assets held longer than one year.
  • January 1, 2027: Scheduled effective date for the Illinois Digital Asset Tax Act (DATA).
  • 2028: Implementation of Germany’s 25% capital-income tax on crypto assets.

Broader Economic and Regulatory Implications

The divergence between the European and American approaches reflects a fundamental difference in how regulators view the role of digital assets. In Europe, the focus is on creating a comprehensive "regulatory perimeter." By treating crypto assets as financial instruments similar to stocks and bonds, EU regulators are essentially attempting to fold the industry into the traditional financial order, thereby providing clarity, albeit at the cost of the tax-free status that previously attracted early adopters.

Conversely, the U.S. landscape remains trapped in a state of jurisdictional competition. While federal bodies like the IRS continue to treat digital assets as property, state-level initiatives like those in Illinois threaten to create a "patchwork quilt" of regulations that could stifle innovation. The outcome of the legal challenge against the Illinois law will likely set a major precedent for whether states possess the authority to tax the underlying "activity" of digital assets in a manner that deviates from established federal property law.

As nations move toward 2027, the message to investors is clear: the period of regulatory ambiguity is ending. Whether through the administrative transparency of the EU or the litigious battles in the U.S., the digital asset market is being forced into a state of total integration with global fiscal systems. For firms and investors, the challenge will be to navigate a future where every transaction, transfer, and storage event is increasingly visible, measurable, and, ultimately, taxable.

September 20, 2026 0 comment
0 FacebookTwitterPinterestEmail
Blockchain Technology

Safari 27 integrates Model Context Protocol, creating a new security frontier for enterprise IT management

by admin September 20, 2026
written by admin

Safari 27 has officially integrated the Model Context Protocol (MCP) as a native server, marking a significant evolution in how consumer web browsers interact with artificial intelligence. By transforming the browser into a programmable interface for AI agents, Apple has effectively bridged the gap between niche developer utilities and mainstream desktop utility. However, this technical milestone has triggered an immediate alarm within enterprise security circles. While the protocol empowers users with unprecedented automation capabilities, the current iteration of Safari 27 lacks the Mobile Device Management (MDM) controls necessary for IT departments to programmatically disable these features, leaving organizations to navigate a complex new governance vacuum.

The Rise of the Programmable Browser

The Model Context Protocol, designed to standardize how AI models interact with data sources and tools, has transitioned rapidly from an experimental framework to a core infrastructure component. With its implementation in Safari 27, the browser no longer serves merely as a window to the internet but as a functional environment for autonomous agents. Any MCP-compliant client—ranging from industry-standard tools like Claude Code and Cursor to specialized developer environments like Codex CLI—can now interface directly with the browser.

This shift is significant because it democratizes high-level automation. An agent can now perform tasks that previously required human oversight or brittle, bespoke scripting. According to documentation provided by WebKit, the integration grants agents access to 17 distinct tools. These include granular control over Document Object Model (DOM) manipulation, real-time network visibility, runtime JavaScript evaluation, and the ability to capture high-fidelity screenshots of active sessions. By leveraging these tools, AI agents can navigate, interpret, and manipulate web content with a level of agility that mirrors human behavior.

Chronology of the MCP Deployment

The arrival of MCP in the consumer space follows a rapid development cycle. In early 2025, the industry began debating the "governance stack" for AI agents, as major tech players recognized that the next generation of productivity tools would require standardized access to local data. Throughout the middle of 2025, several enterprise vendors attempted to ship proprietary policy-enforcement layers, yet the market remained fragmented.

By the third quarter of 2025, the industry saw a surge in platform competition, with giants like Microsoft advocating for "distributed skills" architectures, effectively competing with the broader, open-standard approach of the Model Context Protocol. Apple’s decision to bake MCP directly into Safari 27, as detailed in the WebKit blog in late 2026, served as a decisive move to standardize this interaction. The release coincided with the rollout of macOS Golden Gate 27, which introduced several under-the-hood performance enhancements but, crucially, omitted the specific MDM payload keys that enterprise administrators had come to expect for managing new, high-privilege features.

Technical Safeguards and the Security Gap

Apple has implemented several security layers to mitigate the inherent risks of granting an AI agent control over a browser. The architecture operates entirely on a local basis, functioning as a stdio subprocess. This means the communication between the agent and the browser does not traverse the network, nor does it transmit telemetry or session data back to Apple’s servers.

Furthermore, the implementation utilizes a "sandbox-within-a-sandbox" approach. The AI agent operates within a dedicated automation window that is logically and technically isolated from the user’s primary browsing session. This separation ensures that the agent cannot access the user’s primary cache of cookies, saved passwords, AutoFill data, or sensitive browsing history. Apple has also opted for an explicit, two-step manual opt-in process, requiring users to navigate through the Advanced and Developer settings menus before the MCP server can be activated.

Despite these protections, the "enterprise gap" remains the primary point of contention. While Apple’s security model assumes that individual users will exercise discretion—noting, "As with any agent you give access to your browser, only use ones you trust"—corporate environments operate under a different mandate. In an enterprise, security is not a matter of individual trust but of policy enforcement. The current lack of MDM support means that an organization cannot prevent a savvy employee from enabling these tools, even if the organization’s internal cybersecurity policy explicitly forbids the use of unvetted AI agents for accessing corporate web portals.

The Governance Vacuum in the Enterprise

For IT security teams, the ability to enforce "least privilege" is the cornerstone of their infrastructure. The inability to disable the Safari MCP server via an MDM payload creates a notable compliance challenge. Currently, administrators can restrict Safari entirely on supervised iOS or iPadOS devices, but they lack the granular control required to manage the developer-facing aspects of the macOS environment.

This technical limitation forces a binary, often disruptive choice for CIOs and CISOs: either allow the deployment of Safari 27 across the fleet and accept the risk of unmanaged agent interaction, or block the browser entirely. In a modern workplace, where web-based applications form the backbone of daily operations, blocking Safari is often an untenable solution that impacts productivity and user experience.

The security implications are twofold. First, there is the risk of "shadow AI" deployment, where employees use powerful automation tools to interact with sensitive corporate data without IT’s knowledge. Second, there is the risk of supply chain attacks. If an agent with broad browser-manipulation capabilities is compromised, it could theoretically be used to scrape data or execute actions within authenticated sessions that the agent has been granted permission to access, bypassing traditional perimeter security.

Analyzing the Broader Impact

The integration of MCP into Safari 27 is a bellwether for the future of human-computer interaction. As browsers evolve into agent-friendly interfaces, the boundary between the user, the browser, and the agent becomes increasingly porous. This trend is expected to continue, with other major browsers likely to follow suit in an effort to maintain feature parity with Safari.

However, the industry reaction to this rollout suggests that the transition will be rocky. Security researchers and enterprise vendors have already begun calling for a standardized "AI Governance API" that would allow MDM platforms to toggle agent-related features as easily as they currently manage camera, microphone, or Bluetooth permissions. Without such a mechanism, the responsibility for security is unfairly shifted from the platform provider to the end-user.

In the coming months, it is highly probable that Apple will face pressure to update the macOS Golden Gate 27 enterprise framework to include the missing MDM keys. Until then, organizations are adopting temporary mitigation strategies. These include the use of endpoint detection and response (EDR) tools to monitor for the spawning of MCP-related subprocesses, as well as the implementation of strict user education programs designed to prevent the unauthorized activation of developer-grade browser features.

Moving Toward a Policy-Driven Future

The current situation highlights the tension between innovation and governance. Apple’s focus on the "prosumer" and individual privacy is evident in the robust, local-only design of the MCP implementation. However, the enterprise ecosystem requires a different set of priorities, centered on visibility, control, and auditability.

The arrival of native browser-based MCP support is not just a feature update; it is a fundamental shift in the browser’s threat model. As AI agents become more deeply embedded in our daily workflows, the need for a unified, policy-driven approach to AI governance will only become more acute. For now, IT leaders must bridge this gap through manual oversight and organizational policy, waiting for the necessary technical controls to be integrated into the operating system’s management stack.

As the industry moves forward, the success of MCP will likely be judged not only by the capabilities it provides to individual developers and power users but by its ability to integrate into the existing, rigorous security frameworks that define the modern enterprise. The Safari 27 rollout serves as an early, high-stakes test of that integration—a test that, as of today, remains in the early stages of resolution. The industry stands at a crossroads: either browsers must become manageable, enterprise-ready platforms for automation, or they will increasingly be viewed as a liability that must be restricted in professional environments.

September 20, 2026 0 comment
0 FacebookTwitterPinterestEmail
Blockchain Technology

Privacy-First, Uncensored AI Platform Venice AI Hits Unicorn Status With $65 Million Series A Funding Round

by admin September 20, 2026
written by admin

The generative artificial intelligence landscape has spent the past several years locked in a defensive posture. As mainstream tech companies grapple with escalating concerns regarding user mental health, personal safety, harassment, and the mass dissemination of disinformation, industry leaders have rushed to erect guardrails. These guardrails dictate rigid boundaries on what frontier AI models are permitted to process, generate, or discuss. Yet, a counter-movement is rapidly taking shape among consumers who resist what they view as paternalistic corporate censorship. Capitalizing on this tension, Venice AI—a privacy-focused startup championing "uncensored" artificial intelligence—has officially entered the unicorn club, securing a $65 million Series A funding round at a $1 billion valuation.

The milestone financing, announced on Wednesday, represents the company’s first-ever external fundraise. It was led by prominent crypto-focused venture capital firm Dragonfly, with strategic participation from Coinbase Ventures, North Island Ventures, and several other institutional investors. The heavy presence of crypto-native capital is no accident; it underscores the ideological intersection between Venice AI’s founding vision, its staunch defense of user privacy, and the decentralized philosophy championed by its veteran leadership.

A Rapid Ascent Driven by Uncompromising Demand

Founded just two years ago, Venice AI has charted a meteoric rise that defies traditional software-as-a-service growth trajectories. Despite operating in the shadow of heavily guarded giants like OpenAI and Anthropic, the platform has amassed over 850,000 unique website visitors, serves more than 3 million active users, and processes an average of 1.7 million API calls per day.

Crucially, the company has achieved financial sustainability faster than many of its peers. CEO Erik Voorhees confirmed in an exclusive interview that Venice AI is already profitable, boasting annualized run-rate revenues exceeding $70 million. This financial robustness, combined with surging consumer adoption, provided the foundation necessary to command a billion-dollar valuation during its maiden institutional funding round.

The core appeal of Venice AI lies in its hybrid architecture and its absolute refusal to implement conversational guardrails. The platform provides seamless access to more than 200 distinct AI models. It hosts "uncensored," open-source models directly on its proprietary data centers while intelligently routing user queries to closed-source commercial models, such as those developed by OpenAI and Anthropic, when appropriate.

Privacy, however, remains the startup’s primary technical selling point. All user input is encrypted and unencrypted client-side, then routed through an external proxy before being processed and returned. Venice AI explicitly maintains a strict zero-data-retention policy, ensuring that no user logs or chat histories are stored on its internal systems. For users seeking an extra layer of security, the platform also offers end-to-end encryption on select models, though this capability is gated behind a paid subscription tier.

The Ideology of the Neutral Protocol

The ethos driving Venice AI is inextricably linked to the background of its founder, Erik Voorhees. A pioneering figure in the cryptocurrency ecosystem, Voorhees has spent over a decade founding and advocating for decentralized, censorship-resistant technologies. His past ventures include Satoshi Dice, an early Bitcoin-based gambling platform, and ShapeShift, a cryptocurrency exchange designed to allow users to trade digital assets without registering personal identification.

Voorhees’ steadfast commitment to privacy has frequently courted regulatory scrutiny and public debate. Notably, during a 2018 Wall Street Journal investigation that criticized ShapeShift for processing millions in suspect funds due to its anonymous transaction model, Voorhees defended the platform’s architecture, stating publicly: "I don’t think people should have their identity recorded to catch an occasional criminal."

That same philosophical stance informs how Venice AI navigates the treacherous waters of generative AI safety. As regulatory bodies and grieving families point fingers at conversational agents for inciting psychological distress, self-harm, and dangerous delusions, Venice AI refuses to police user interactions. Voorhees explicitly rejects the notion that platform developers should act as arbiters of morality, choosing instead to frame Venice as a neutral technological utility.

"This is the same principle that you have in Bitcoin, where Bitcoin, as a neutral protocol, works the same way for all people," Voorhees explained during his interview with TechCrunch. "I think it’s actually quite dangerous from a safety perspective, for the world to enter this next phase and have everyone be constantly watched. To me that is actually much more dangerous than any particular person asking a controversial question or something that might be considered bad."

Instead of imposing top-down behavioral restrictions, Venice AI emphasizes user agency. The platform provides access to models capable of generating text, images, audio, and video across varying performance tiers. Users are given explicit freedom to customize AI "characters," adjust system prompts to encourage more direct and unvarnished responses, and interact with the technology entirely on their own terms.

"We’re optimizing for freedom and actually respecting users as adults, which is, I think, rare these days," Voorhees noted.

Bridging the Feature Gap and Integrating Crypto Economics

While ideological alignment and data privacy drew Venice AI its initial user base, Voorhees credits the company’s recent explosive growth to rapid technological catch-up. In its infancy, the platform lagged significantly behind the capabilities of market leaders like ChatGPT. However, as the engineering team integrated more sophisticated open-source and proprietary models, Venice closed that performance gap.

"When we launched, we were very far away from what ChatGPT could do, but people would use us because it was private," Voorhees observed. "And today, we’re very close to what ChatGPT can do […] so as we’ve closed that gap, it’s become an increasingly compelling alternative."

In keeping with the background of its founders and financial backers, Venice AI has also woven cryptocurrency infrastructure directly into its operational model. The platform launched a native utility token named "VVV" in early January, following the introduction of a secondary token, "DIEM," in August of the previous year. Users can purchase VVV tokens and stake them to mint DIEM, which automatically generates $1 worth of daily AI credits redeemable on the platform.

Despite this native Web3 integration, crypto payments remain a minority use case, accounting for roughly 8% of the platform’s total transactions. Nevertheless, the successful implementation of these tokens has fostered an active, dedicated community and aligned the startup with crypto-focused venture capital heavyweights.

Strategic Roadmap and Industry Implications

Armed with $65 million in fresh institutional capital, Venice AI is shifting its operational strategy to maximize profitability and infrastructure independence. Up to this point, the startup has relied heavily on leased computing power to serve millions of active users and API calls. A significant portion of the Series A proceeds will be dedicated to purchasing high-performance GPUs and constructing proprietary data centers. By moving away from rented infrastructure, Venice aims to drastically reduce operating overhead and expand its gross profit margins.

The rise of Venice AI highlights a profound ideological fracture within the broader artificial intelligence ecosystem. As major technology corporations face mounting pressure from governments, advocacy groups, and legal teams to sanitize AI interactions and mitigate real-world harms, a substantial segment of the user base is actively migrating toward platforms that prioritize autonomy and absolute data confidentiality.

Critics argue that platforms championing "uncensored" AI run the risk of facilitating dangerous behavior, generating harmful propaganda, or empowering malicious actors with unchecked generative capabilities. Conversely, proponents argue that corporate guardrails amount to insidious surveillance and unwarranted censorship, stifling creativity and robbing individuals of their digital agency.

As Venice AI accelerates its infrastructure expansion and solidifies its position as a billion-dollar enterprise, it serves as a powerful litmus test for the market. Its success suggests that a sizable population of digital consumers is willing to trade institutional safety nets for unfettered access, absolute privacy, and the freedom to explore the outer boundaries of artificial intelligence.

September 20, 2026 0 comment
0 FacebookTwitterPinterestEmail
Bitcoin & Altcoins

Platåberget: Introducing the Public Testing Ground for Ethereum’s Glamsterdam Upgrade

by admin September 20, 2026
written by admin

The Ethereum ecosystem has officially launched Platåberget, a new, short-term, public-facing testnet designed to serve as the primary sandbox for the upcoming Glamsterdam upgrade. Combining the nomenclature of "Gloas" and "Amsterdam," this development marks a critical juncture in the protocol’s evolution, introducing significant changes to both the consensus and execution layers. As developers and node operators prepare for this transition, the availability of Platåberget provides a vital environment for testing complex network modifications—specifically those concerning block building, gas dynamics, and validator workflows—before they are deployed to established testnets like Sepolia and Holesky.

The urgency for this testing phase is underscored by the scope of the Glamsterdam fork. Unlike routine maintenance updates, Glamsterdam introduces structural shifts that are expected to break legacy tooling. Consequently, the Ethereum development community is calling for widespread participation from wallet providers, indexer services, and gas estimation software developers to ensure system compatibility.

Understanding the Glamsterdam Architecture

The Glamsterdam upgrade represents a multifaceted shift in how Ethereum processes transactions and manages state. Central to this update is the implementation of ePBS (Enshrined Proposer-Builder Separation), a mechanism intended to decentralize the block-building process and mitigate the dominance of centralized relayers. By enshrining the builder-proposer relationship into the protocol itself, Ethereum aims to protect solo stakers and improve the overall security of the consensus layer.

However, the most far-reaching impact for the broader ecosystem lies in the gas repricing initiatives. EIP-7773 serves as the meta-EIP for the upgrade, coordinating a series of changes that fundamentally alter the cost structure of operations on the Ethereum Virtual Machine (EVM). Among these, EIP-8037 introduces a state-based gas dimension, moving away from a flat-fee model for simple transactions. Under the new paradigm, the cost of creating an account, deploying smart contract code, or writing to storage will be metered at a fixed Cost Per State Byte (CPSB), calculated at runtime.

This transition effectively renders the long-standing assumption of a flat 21,000 gas fee for ETH transfers obsolete. While existing accounts will continue to see predictable costs, transfers to non-existent accounts will now trigger dynamic state-access charges. For developers relying on hardcoded gas limits or legacy estimation algorithms, this necessitates a comprehensive audit of their backend infrastructure.

The Role of Platåberget in the Development Lifecycle

Platåberget is categorized as a "short-term, high-intensity" testnet. While previous iterations of Ethereum devnets were often ephemeral or restricted to core development teams, Platåberget represents a transition to a more inclusive, public-testing model. It is intended to run for several months, providing a stable platform for stress-testing the network under realistic, albeit simulated, conditions.

The testnet features a publicly joinable validator set, encouraging community members to test validator deposits and builder-deposit workflows. This inclusivity is vital for ensuring that Distributed Validator Technology (DVT) projects, solo stakers, and large-scale infrastructure providers are prepared for the transition. The scheduled fork date of August 20th provides a clear deadline for stakeholders to align their configurations, update their container images, and synchronize their nodes with the new network parameters.

For those looking to participate, the EthPandaOps initiative has streamlined the setup process. The Platåberget portal offers a one-click "Add Network" feature for client configuration, supplemented by a faucet that provides testnet ether to facilitate testing of deposits and gas-heavy transactions. The availability of container images for all major execution and consensus clients—including Geth, Besu, Reth, Lighthouse, and Prysm—ensures that participants can replicate production environments with minimal friction.

Chronology of the Glamsterdam Rollout

The deployment of the Glamsterdam upgrade follows a methodical, multi-phase roadmap designed to minimize risk to the Ethereum mainnet. The timeline is structured as follows:

  1. Specification and Research Phase (Completed): Core developers finalized the scope of the upgrade, culminating in the formalization of the meta-EIP-7773 and associated gas-related EIPs.
  2. Devnet 8/Platåberget Launch (Current): The deployment of the public testnet, scheduled to fork on August 20th. This phase focuses on identifying breaking changes in tooling and consensus edge cases.
  3. Pathological Testing (Upcoming): Once the current testnet is deemed stable, a specialized, non-finality devnet will be launched to test the protocol’s resilience against malicious or anomalous consensus scenarios.
  4. Long-lived Testnet Deployment: Following successful testing on Platåberget, the upgrade will be rolled out to public testnets, specifically Sepolia and Holesky. These environments provide the final barrier against potential mainnet vulnerabilities.
  5. Mainnet Activation: The final phase involves the coordinated upgrade of the Ethereum mainnet. This date remains contingent upon the stability and performance metrics gathered during the preceding testnet phases.

Implications for the Developer Ecosystem

The transition to Glamsterdam is being viewed by industry analysts as a turning point for Ethereum’s maturity. While the consensus-layer changes are aimed at decentralization, the execution-layer changes address the long-term sustainability of state management.

For application developers, the primary concern is the "breaking" nature of the gas repricing. Tools such as block explorers, wallet interfaces, and decentralized finance (DeFi) protocols that utilize automated transaction submission must be updated to account for the new state-access metrics. EIP-2780, which decomposes intrinsic costs, and EIP-8038, which addresses state-access increases, are the primary documentation sources for these updates. Developers are being urged to treat these changes as a mandatory migration rather than an optional optimization.

"The industry has historically relied on the simplicity of the 21,000 gas constant for native transfers," noted an infrastructure engineer familiar with the upgrade. "Moving to a runtime-calculated state gas cost requires a paradigm shift. If developers fail to adapt, we could see a surge in failed transactions and inaccurate fee estimations, which would ultimately degrade the user experience."

Official Response and Community Engagement

The Ethereum R&D community has established multiple channels for feedback, emphasizing the collaborative nature of the upgrade. The Ethereum R&D Discord remains the primary hub for technical discourse, while official repositories for consensus and execution specs serve as the source of truth for the protocol’s evolution.

Core developers have expressed optimism regarding the community’s engagement. By allowing for a sustained testing period, the risk of a "failed" upgrade is significantly reduced. "The goal of Platåberget is to find the breaking points," said a spokesperson for the testing initiative. "We want to see the system tested to its limits by the very people who will be using it. Whether it’s a new wallet developer or a veteran node operator, everyone has a role to play in ensuring the stability of the network."

Broader Economic and Technical Context

From a broader perspective, the Glamsterdam upgrade is a testament to Ethereum’s iterative development philosophy. By moving away from monolithic updates and embracing granular, spec-heavy forks, the network has demonstrated an ability to adapt to the increasing demands of a global decentralized finance ecosystem.

The introduction of ePBS is perhaps the most significant economic shift, as it addresses the "MEV (Maximal Extractable Value) problem" by preventing vertical integration between builders and proposers. This is expected to create a more competitive market for block production, potentially leading to lower transaction costs and more efficient resource allocation across the network.

However, the complexity of these changes cannot be overstated. As the protocol grows, the surface area for potential bugs increases. The rigorous testing schedule for Glamsterdam reflects a conservative approach to deployment, prioritizing the security of the billions of dollars currently locked in the Ethereum ecosystem.

As the August 20th fork date approaches, the focus of the community remains squarely on the data coming out of Platåberget. The success of the upgrade will be measured not just by the absence of network halts, but by the seamless integration of these complex changes into the daily operations of the Ethereum developer community. Those interested in following the progress are encouraged to monitor the All Core Dev calls and the Glamsterdam upgrade tracker, as the network prepares to enter its next chapter of scalability and efficiency.

September 20, 2026 0 comment
0 FacebookTwitterPinterestEmail
Bitcoin & Altcoins

Kraken Secures Official Launch Partnership for X Cashtags to Streamline US Cryptocurrency Trading

by admin September 20, 2026
written by admin

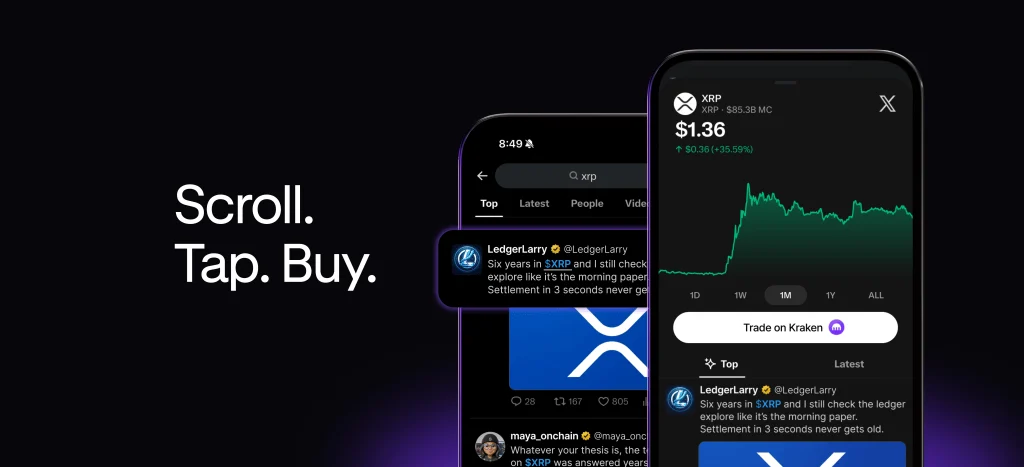
The intersection of social media and digital finance reached a significant milestone as cryptocurrency exchange Kraken announced its selection as an official launch partner for X Cashtags in the United States. This strategic integration is designed to bridge the gap between financial discourse and trade execution, allowing users of the social media platform X—formerly known as Twitter—to transition seamlessly from reading about digital assets to purchasing them without ever leaving their browsing thread.

Under the rollout, clicking or tapping on a supported ticker symbol preceded by a dollar sign—known on the platform as a cashtag—will present users with a direct trade option. Selecting this feature routes the user straight to Kraken to complete the transaction. The initiative eliminates the traditional friction points of copy-pasting ticker information between different applications, preserving the user’s exact place within a discussion thread.

Addressing the Friction of Modern Crypto Adoption

Industry data consistently demonstrates that user acquisition in the digital asset sector often suffers from high drop-off rates, largely attributable to the cumbersome onboarding and execution process. Historically, an interested investor might discover a promising asset through social commentary, research its background on an independent site, navigate to an exchange, create or log into an account, deposit fiat currency, and finally locate the correct trading pair. Each additional step introduces a probability of user abandonment.

Kamo Asatryan, Chief Data Officer of Payward and Global Head of Consumer at Kraken, emphasized the fundamental problem this partnership aims to solve. People are already interested in crypto, Asatryan noted, but the true obstacle lies in the multitude of steps required to progress from initial awareness to actual ownership. By integrating directly into the social media timeline via X Cashtags, the platform aims to reduce this journey to a matter of a few clicks, capturing user intent at the exact moment of inspiration.

Scope and Asset Availability

The collaboration leverages a vast array of financial instruments, with Kraken supporting cashtags across approximately 2,500 distinct assets. This comprehensive catalog spans both the company’s centralized exchange infrastructure and its decentralized exchange (DEX) offerings.

By providing access to such a wide breadth of assets, the partnership ensures that the specific token, stock, ETF, or cryptocurrency a user is researching in a social media discussion is the exact asset they can immediately act upon. This breadth of access is widely viewed by market analysts as critical for maintaining user engagement, as forcing a user to search for an obscure token on a separate platform often results in lost conversion opportunities.

The Evolution of Social Finance and Chronology of the Integration

The integration of financial tickers into social media is not entirely new, but the evolution toward direct, in-app trade execution represents a fundamental shift in how retail investors interact with markets. For years, platforms like Twitter and X have served as primary information hubs for financial discourse, hosting real-time commentary from retail traders, institutional analysts, project developers, and macroeconomic commentators.

The introduction of cashtags years prior provided users with clickable links that displayed real-time stock charts and crypto pricing data directly within search results. However, those earlier iterations stopped short of transactional capability. Users could view the data, but they still had to execute trades elsewhere.

By hand-selecting a group of premier financial platforms to serve as official execution partners for the US rollout, X has transformed its interface from an informational bulletin board into an active transactional portal. Kraken’s inclusion in this elite group places the exchange directly in front of one of the largest and most active financial communities on the internet, capturing user attention precisely when market sentiment peaks.

Strategic Implications for Kraken and the Broader Industry

From a strategic perspective, the partnership aligns with a broader industry trend toward embedded finance—the practice of integrating financial services into non-financial platforms, applications, and consumer touchpoints. Rather than requiring consumers to seek out financial service providers on their own, modern fintech and cryptocurrency companies are increasingly focusing on distribution strategies that meet users where they already spend their time.

Analysts observing the integration note that reducing the steps between discovery and execution could significantly increase trading volume for retail-focused assets, particularly during periods of high market volatility when speed and convenience are paramount. Furthermore, the inclusion of both centralized and decentralized assets within the cashtag framework highlights a maturing approach to multi-channel trading accessibility.

Regulatory and Operational Disclaimers

As with any financial service offering, the integration of trading capabilities via external platforms comes with standard regulatory disclosures and risk warnings. Kraken has emphasized that trading involves substantial risk and is not suitable for all investors. Cryptocurrency and digital asset holdings maintained on centralized exchanges are typically not protected by traditional banking insurance schemes such as the Federal Deposit Insurance Corporation (FDIC) or the Securities Investor Protection Corporation (SIPC).

Furthermore, availability of specific assets varies depending on the user’s geographic jurisdiction and local regulatory frameworks. Regarding decentralized exchange (DEX) trading, transactions occur via self-custodial wallets on decentralized protocols where Kraken does not hold user assets or private keys. DEX trading is generally unclassified as a traditional regulated financial product, and token prices can exhibit extreme volatility, potentially resulting in the loss of an entire investment. Execution is handled by third-party protocols independently of Kraken, which does not guarantee order fills, timing, or pricing.

Future Outlook and How to Participate

As the digital asset ecosystem continues to evolve, partnerships that blur the lines between social media and financial execution are expected to become increasingly common. For Kraken, the X Cashtag integration represents a major step forward in its ongoing mission to make digital asset ownership as frictionless as possible.

New users interested in utilizing the feature upon its rollout can sign up for a Kraken account in advance, ensuring they are fully verified and prepared to execute trades the next time a market trend or cashtag catches their attention on their social timeline. As the digital economy marches toward deeper integration with everyday communication tools, initiatives like this one signal a future where financial transactions are woven seamlessly into the fabric of daily digital life.

September 20, 2026 0 comment
0 FacebookTwitterPinterestEmail
Bitcoin & Altcoins

Bitcoin faces existential security debate as Silicon Valley and Ethereum leadership clash over AI and quantum threats

by admin September 20, 2026
written by admin

The long-term security architecture of Bitcoin, the world’s largest cryptocurrency by market capitalization, has become the subject of an intense intellectual standoff between Silicon Valley investor Liron Shapira and Ethereum co-founder Vitalik Buterin. The debate, which has played out primarily on social media platforms, centers on whether the rapid evolution of artificial intelligence and emerging quantum computing capabilities will render Bitcoin’s current cryptographic foundations obsolete, potentially triggering a significant market devaluation.

The discourse gained momentum when Shapira initially posited a 50% probability that Bitcoin’s price would suffer a catastrophic decline within a two-year timeframe. His thesis rested on the premise that advancements in AI could bypass the robustness assumptions currently shielding the Bitcoin network. Following feedback from Buterin and noted AI researcher Eliezer Yudkowsky, Shapira recalibrated his risk assessment to a 40% probability, though he maintained that the fundamental threats—specifically the vulnerability of the network to sophisticated technological breaches and the long-term decline of mining rewards—remain pressing concerns for institutional and retail investors alike.

The Anatomy of the Disagreement

At the core of the debate is a fundamental disagreement regarding the agility of decentralized systems. Shapira’s skepticism is rooted in the belief that the Bitcoin network’s decentralized governance model may be too slow to adapt when faced with an "AI-driven" security crisis. He argues that if a cryptographic vulnerability were to be exploited by a super-intelligent system, the time required to reach a broad social consensus for a hard fork or a system-wide upgrade might be insufficient to prevent a total loss of confidence in the asset.

Conversely, Vitalik Buterin has adopted a position of cautious optimism, directly challenging the notion that Bitcoin is fragile. Buterin contends that the network’s ability to evolve has been historically underestimated. He points out that many critical security enhancements—particularly those involving mining pool operations and client-side protocols—can be implemented as technical upgrades without the need for contentious, broad-based social consensus. For Buterin, the challenge is not the impossibility of defense, but the logistical and technical transition process during a potential period of instability. He remains largely dismissive of the idea that Bitcoin’s core proof-of-work (PoW) mechanism or its hash functions are on the verge of a total collapse.

Technological Headwinds: The AI and Quantum Front

The concerns raised by Shapira are symptomatic of a broader anxiety within the cybersecurity sector regarding the "quantum threat." As quantum computing transitions from a theoretical pursuit to an experimental reality, global regulatory bodies have begun to sound the alarm. The G7’s Cybersecurity Working Group recently issued a directive urging federal authorities to accelerate the adoption of post-quantum cryptography (PQC). The warning is explicit: current encryption standards, including the elliptic curve cryptography that secures Bitcoin private keys, may eventually become vulnerable to high-end quantum systems capable of solving the complex mathematical problems that underpin blockchain security.

The urgency of this issue is compounded by the existence of "legacy" Bitcoin addresses. It is estimated that approximately 6.9 million BTC—roughly one-third of the circulating supply—reside in addresses where public keys have been exposed, including the estimated 1.1 million BTC attributed to the network’s pseudonymous creator, Satoshi Nakamoto. Because these early addresses were often reused, they are theoretically more susceptible to quantum-assisted brute force attacks compared to modern "pay-to-script-hash" (P2SH) or SegWit addresses.

Proposals for Defensive Upgrades

In response to these identified risks, the Bitcoin developer community has been exploring proactive measures. One of the most prominent proposals is BIP-360, an initiative designed to implement a quantum-safe address system. This proposal, currently undergoing testing on a testnet, would allow users to transition their holdings to quantum-resistant addresses.

However, the path to implementation is fraught with political and ideological tension. Some proposals involve the potential "burning" or forced migration of dormant, vulnerable coins—a move that would affect long-held assets that have not moved in over a decade. Critics within the community have labeled such interventions as "authoritarian," arguing that the immutability of the blockchain is a core tenet of Bitcoin’s value proposition. This resistance highlights a critical paradox: the very decentralization that gives Bitcoin its trustless nature also creates the political friction that could hinder rapid responses to genuine technological emergencies.

Economic Factors: The Mining Reward Dilemma

Beyond the technical cryptographic risks, Shapira has highlighted the economic sustainability of the network as a secondary, yet vital, threat. As Bitcoin undergoes its periodic "halving" events, the block reward—the primary incentive for miners—decreases. Shapira argues that as mining rewards diminish, the security budget of the network becomes increasingly reliant on transaction fees. If fees do not scale sufficiently to compensate for the loss of block rewards, the total hash rate could decline, theoretically reducing the network’s cost to attack and making it more susceptible to coordinated malicious actions.

This economic pressure, combined with the technological threats, forms the basis of Shapira’s 40% crash forecast. He posits that the market may eventually price in these systemic risks, leading to a flight from the asset if it is perceived that the community cannot resolve these issues in a timely manner.

The Role of Institutional Oversight

The debate has moved beyond the fringes of crypto-Twitter and into the boardrooms of financial institutions. As Bitcoin becomes increasingly integrated into traditional finance through spot ETFs and institutional custody solutions, the "security of the network" has become a matter of macro-prudential concern. Institutional investors are increasingly scrutinizing the "governance risk" associated with Bitcoin’s development lifecycle.

The G7’s involvement signals that the transition to post-quantum cryptography is no longer a niche concern for cypherpunks; it is a global cybersecurity mandate. The collaboration between international government agencies and the private sector to develop standards for quantum-safe communication suggests that Bitcoin, as a major financial infrastructure, will eventually be forced to reckon with these standards to maintain its status as "digital gold."

Analytical Implications

The ongoing dialogue between Shapira and Buterin serves as a microcosm for the larger challenges facing decentralized finance. The implications of this debate can be summarized in three key areas:

  1. Governance Speed: Can a permissionless, decentralized system react to a "black swan" technological event as quickly as a centralized entity? The community’s ability to implement quantum-safe protocols without creating internal schisms will be the ultimate test of Bitcoin’s maturity.
  2. Cryptographic Evolution: The shift from current standards to post-quantum algorithms represents the most significant technical upgrade in the history of blockchain. It is a transition that requires not only technical ingenuity but also a consensus on the definition of a "hard fork" versus a "soft upgrade."
  3. Economic Resilience: The interplay between the diminishing block reward and the cost of network security remains the most significant long-term economic variable. If the network cannot maintain a sufficiently high hash rate to deter state-level actors, its security guarantees will be eroded, regardless of its cryptographic strength.

Conclusion

The disagreement between Liron Shapira and Vitalik Buterin is not merely a difference of opinion on market performance; it is a fundamental debate on the nature of digital resilience. While Shapira views the technological landscape as an accelerating threat that outpaces human consensus, Buterin views it as an environment that incentivizes innovation and adaptive defense.

As the crypto industry looks toward the next decade, the ability of Bitcoin to reconcile these two perspectives—by maintaining its core principles of decentralization while effectively addressing the looming threats posed by quantum computing and AI—will determine whether it remains a stable financial asset or becomes a relic of the early digital era. For now, the market remains in a state of vigilant observation, as the community prepares for the technical and political hurdles of the coming transition. The outcome of this debate will likely shape not just the price of Bitcoin, but the security architecture of the global financial system as it continues its migration onto distributed ledger technologies.

September 20, 2026 0 comment
0 FacebookTwitterPinterestEmail
Cryptography & Privacy

The Legacy Vulnerability Threatening Modern Enterprise Networks: A Deep Dive into Kerberoasting and Active Directory Security

by admin September 20, 2026
written by admin

The persistence of outdated cryptographic standards within enterprise infrastructure has once again been cast into the spotlight following major cyber incidents involving legacy Microsoft protocols. Central to these security concerns is Kerberoasting, a technique targeting Microsoft’s Active Directory (AD) that allows threat actors to compromise corporate networks through archaic encryption methods. Despite being documented for over a decade, this attack vector continues to facilitate high-impact breaches, including the high-profile ransomware attack on the Ascension Health hospital system in May 2024.

The mechanism behind the threat highlights a persistent challenge in enterprise cybersecurity: balancing backward compatibility with modern security posture. As organizations increasingly migrate to cloud environments and advanced perimeter defenses, foundational components like Active Directory often retain legacy elements introduced decades ago. This architectural reality creates critical blind spots that sophisticated threat actors routinely exploit to escalate privileges and execute widespread network disruptions.

Understanding Active Directory and the Roots of Kerberos Authentication

Active Directory serves as the cornerstone of access control for the vast majority of enterprise networks operating Windows environments. Functioning as a centralized directory service, AD manages user credentials, computer accounts, and security policies across the enterprise. When a user or workstation requests access to a network resource—such as a file server, database, or internal application—the system relies on authentication protocols to verify identity and authorize the connection.

The core protocol driving this authentication process within traditional Windows environments is Kerberos, a network authentication protocol originally developed at the Massachusetts Institute of Technology in the late 1980s. Microsoft integrated Kerberos into its architecture with the launch of Windows 2000 and Active Directory, establishing a ticket-based system designed to eliminate the need for clear-text password transmission over networks.

In a standard Kerberos exchange, a client requests a service ticket from a Key Distribution Center (KDC), which is a component of the Active Directory domain controller. The KDC issues a ticket encrypted with the long-term cryptographic key—essentially the password—of the target service. The client then presents this ticket to the service to establish a secure session.

While theoretically sound when configured with robust cryptographic keys, the architecture contains a structural vulnerability. Because Active Directory allows service accounts to be linked to user accounts managed by human administrators, these accounts are frequently secured using human-generated passwords rather than long, randomly rotated cryptographic keys.

The Mechanics of Kerberoasting

Kerberoasting takes advantage of the fundamental design of the Kerberos protocol, which permits any authenticated user within a domain to request a service ticket for virtually any registered service account. Crucially, the Active Directory domain controller does not verify whether the requesting user actually requires access to that specific service before issuing the ticket.

Once an attacker gains a foothold within a corporate network—often through routine initial access vectors such as phishing, compromised credentials, or malicious links—they can query the Active Directory to identify service principal names associated with user accounts. The attacker then requests service tickets for these accounts from the KDC.

Upon receiving the ticket, which is encrypted with the target service account’s password hash, the attacker can extract it from the local machine memory and export it out of the corporate network entirely. Because the decryption process occurs offline, the attacker faces no risk of detection by intrusion detection systems or network monitoring tools. Using specialized hardware arrays equipped with powerful graphics processing units, the attacker subjects the extracted ticket to intensive dictionary and brute-force cracking attempts until the underlying password is recovered.

Once the service account password is exposed, the attacker gains full administrative control over the associated service. In a poorly segmented enterprise network, these service accounts frequently possess elevated privileges across multiple systems, enabling lateral movement, domain dominance, and the deployment of ransomware.

The Escalation Risk of Legacy Cryptography: RC4 and MD4

The severity of Kerberoasting attacks is compounded exponentially by the continued support for obsolete cryptographic algorithms within Active Directory. While modern configurations utilize advanced encryption standards such as AES-128 and AES-256 combined with key derivation functions like PBKDF2, legacy fallback mechanisms often permit the use of older, structurally weaker ciphers.

Kerberoasting

Specifically, when an Active Directory environment retains backward compatibility for RC4 encryption and un-salted NT hashing algorithms—primarily derived from the legacy MD4 hash function—the computational barrier required to crack service tickets drops precipitously.

Benchmark data compiled by security researchers demonstrates the vast disparity in cracking speeds between modern and legacy cryptographic standards. Utilizing high-end consumer hardware such as an NVIDIA RTX 5090 GPU, an attacker attempting to crack service tickets encrypted with AES-128 and PBKDF2 can execute approximately 6.8 million password guesses per second. While substantial, this rate places practical limitations on the feasibility of cracking genuinely complex passwords.

In stark contrast, when a service defaults to RC4 encryption with un-salted NT hashes, the same hardware can execute approximately 4.18 billion password guesses per second. This represents an efficiency increase of roughly one thousand times, rendering human-generated passwords vulnerable to immediate compromise regardless of standard length or complexity.

Chronology of the Threat and Real-World Impact

The Kerberoasting attack vector is not a newly discovered phenomenon. The technique was formally researched, named, and publicly detailed by security researcher Tim Medin during a presentation at the DerbyCon security conference in September 2014. Despite extensive documentation within the cybersecurity community over the subsequent decade, organizations have been slow to audit and harden their Active Directory environments against the threat.

The practical consequences of neglecting these legacy vulnerabilities culminated in major enterprise security incidents throughout 2024. A notable example occurred in May 2024, when a severe ransomware attack targeted Ascension Health, one of the largest Catholic health systems in the United States. The attack caused widespread operational disruptions, forcing hospitals and care facilities to divert ambulances and delay patient procedures while systems were taken offline for remediation.

Subsequent investigations and regulatory inquiries highlighted the mechanics of the breach. In correspondence directed to federal regulators, lawmakers including Senator Ron Wyden emphasized that sophisticated ransomware syndicates actively leverage legacy Active Directory misconfigurations and Kerberoasting techniques to achieve lateral movement within critical infrastructure networks, underscoring the systemic risk posed by unmitigated technical debt in enterprise software.

Industry Response and Mitigation Strategies

In response to sustained pressure from lawmakers, cybersecurity agencies, and industry analysts, technology providers have intensified efforts to guide organizations toward more secure Active Directory configurations. In October 2024, Microsoft published updated security guidance aimed at helping enterprise administrators identify and mitigate Kerberoasting vulnerabilities within their networks.

The official mitigation recommendations focus on several core remediation steps:

  1. Automated Key Management: Transitioning service accounts to Group Managed Service Accounts (gMSAs), which automatically generate and regularly rotate complex, 240-character cryptographic passwords, eliminating human management entirely.
  2. Password Complexity: For services that cannot utilize gMSAs, administrators are urged to enforce exceptionally long, complex, and unpredictable passwords to increase the computational time required for offline brute-force attacks.
  3. Deprecation of Legacy Protocols: Actively disabling support for RC4 encryption across the domain to ensure that all Kerberos tickets are processed using secure AES standards.
  4. Continuous Auditing: Implementing continuous monitoring solutions to detect anomalous requests for service tickets, particularly high volumes of ticket requests originating from standard user accounts.

Broader Implications for Enterprise Security

The ongoing relevance of Kerberoasting highlights a deeper philosophical and operational challenge in software engineering and enterprise information technology: the friction between mandatory backward compatibility and absolute security.

Enterprise software vendors face immense commercial pressure to ensure that legacy applications, custom scripts, and older hardware systems continue functioning uninterrupted across successive operating system upgrades. Consequently, platforms like Active Directory maintain extensive fallback mechanisms to support deprecated protocols.

However, security analysts argue that the threshold for maintaining such legacy support has long been surpassed. As cyber threat actors increasingly automate the exploitation of known vulnerabilities using advanced computing hardware, the tolerance for unmitigated technical debt diminishes. The burden of security can no longer rest solely on under-resourced system administrators tasked with hardening complex environments manually. Instead, industry observers contend that platform developers must proactively deprecate and disable inherently unsafe cryptographic standards by default, forcing organizations to modernize their infrastructure rather than permitting insecure configurations to persist undetected.

Until such proactive measures become standard practice across all enterprise software ecosystems, vulnerabilities rooted in the technology of the 1980s and 1990s will continue to pose an outsized threat to modern organizational security.

September 20, 2026 0 comment
0 FacebookTwitterPinterestEmail
Newer Posts
Older Posts

Recent Posts

  • The Evolution of the Web3 Wallet: From Private-Key Vault to the Command Center of the Agentic Web
  • Ethereum Foundation Announces Annual Protocol AMA Session Scheduled for September 16
  • Kraken Expands Its Digital Asset Offerings with the Official Listing of Doppler Finance (Xdp)
  • CSD BR and Ripple Collaborate to Integrate XRP Ledger into Brazilian Financial Market Infrastructure
  • Web3 Venture Funding Surges to Record $22 Billion in Third Quarter 2025 Driven by Institutional Adoption

Recent Comments

No comments to show.
  • Facebook
  • Twitter

@2021 - All Right Reserved. Designed and Developed by PenciDesign


Back To Top
Dr Crypton
  • Home
  • About Us
  • Contact Us
  • Cookies Policy
  • Disclaimer
  • DMCA
  • Privacy Policy
  • Terms and Conditions

We are using cookies to give you the best experience on our website.

You can find out more about which cookies we are using or switch them off in .

Dr Crypton
Powered by  GDPR Cookie Compliance
Privacy Overview

This website uses cookies so that we can provide you with the best user experience possible. Cookie information is stored in your browser and performs functions such as recognising you when you return to our website and helping our team to understand which sections of the website you find most interesting and useful.

Strictly Necessary Cookies

Strictly Necessary Cookie should be enabled at all times so that we can save your preferences for cookie settings.